A vulnerability is where the fun starts. I want to know why it exists, what else it touches, and how far the system around it can be pushed, reconfigured, or pwned before something breaks.
My background is weird in the best possible way. I've worked in IT support and web development, built an online booking department, managed retail and food operations, owned two food businesses, produced a film, acted professionally, and published a cookbook. Technology was my best coworker and business partner through all of it.
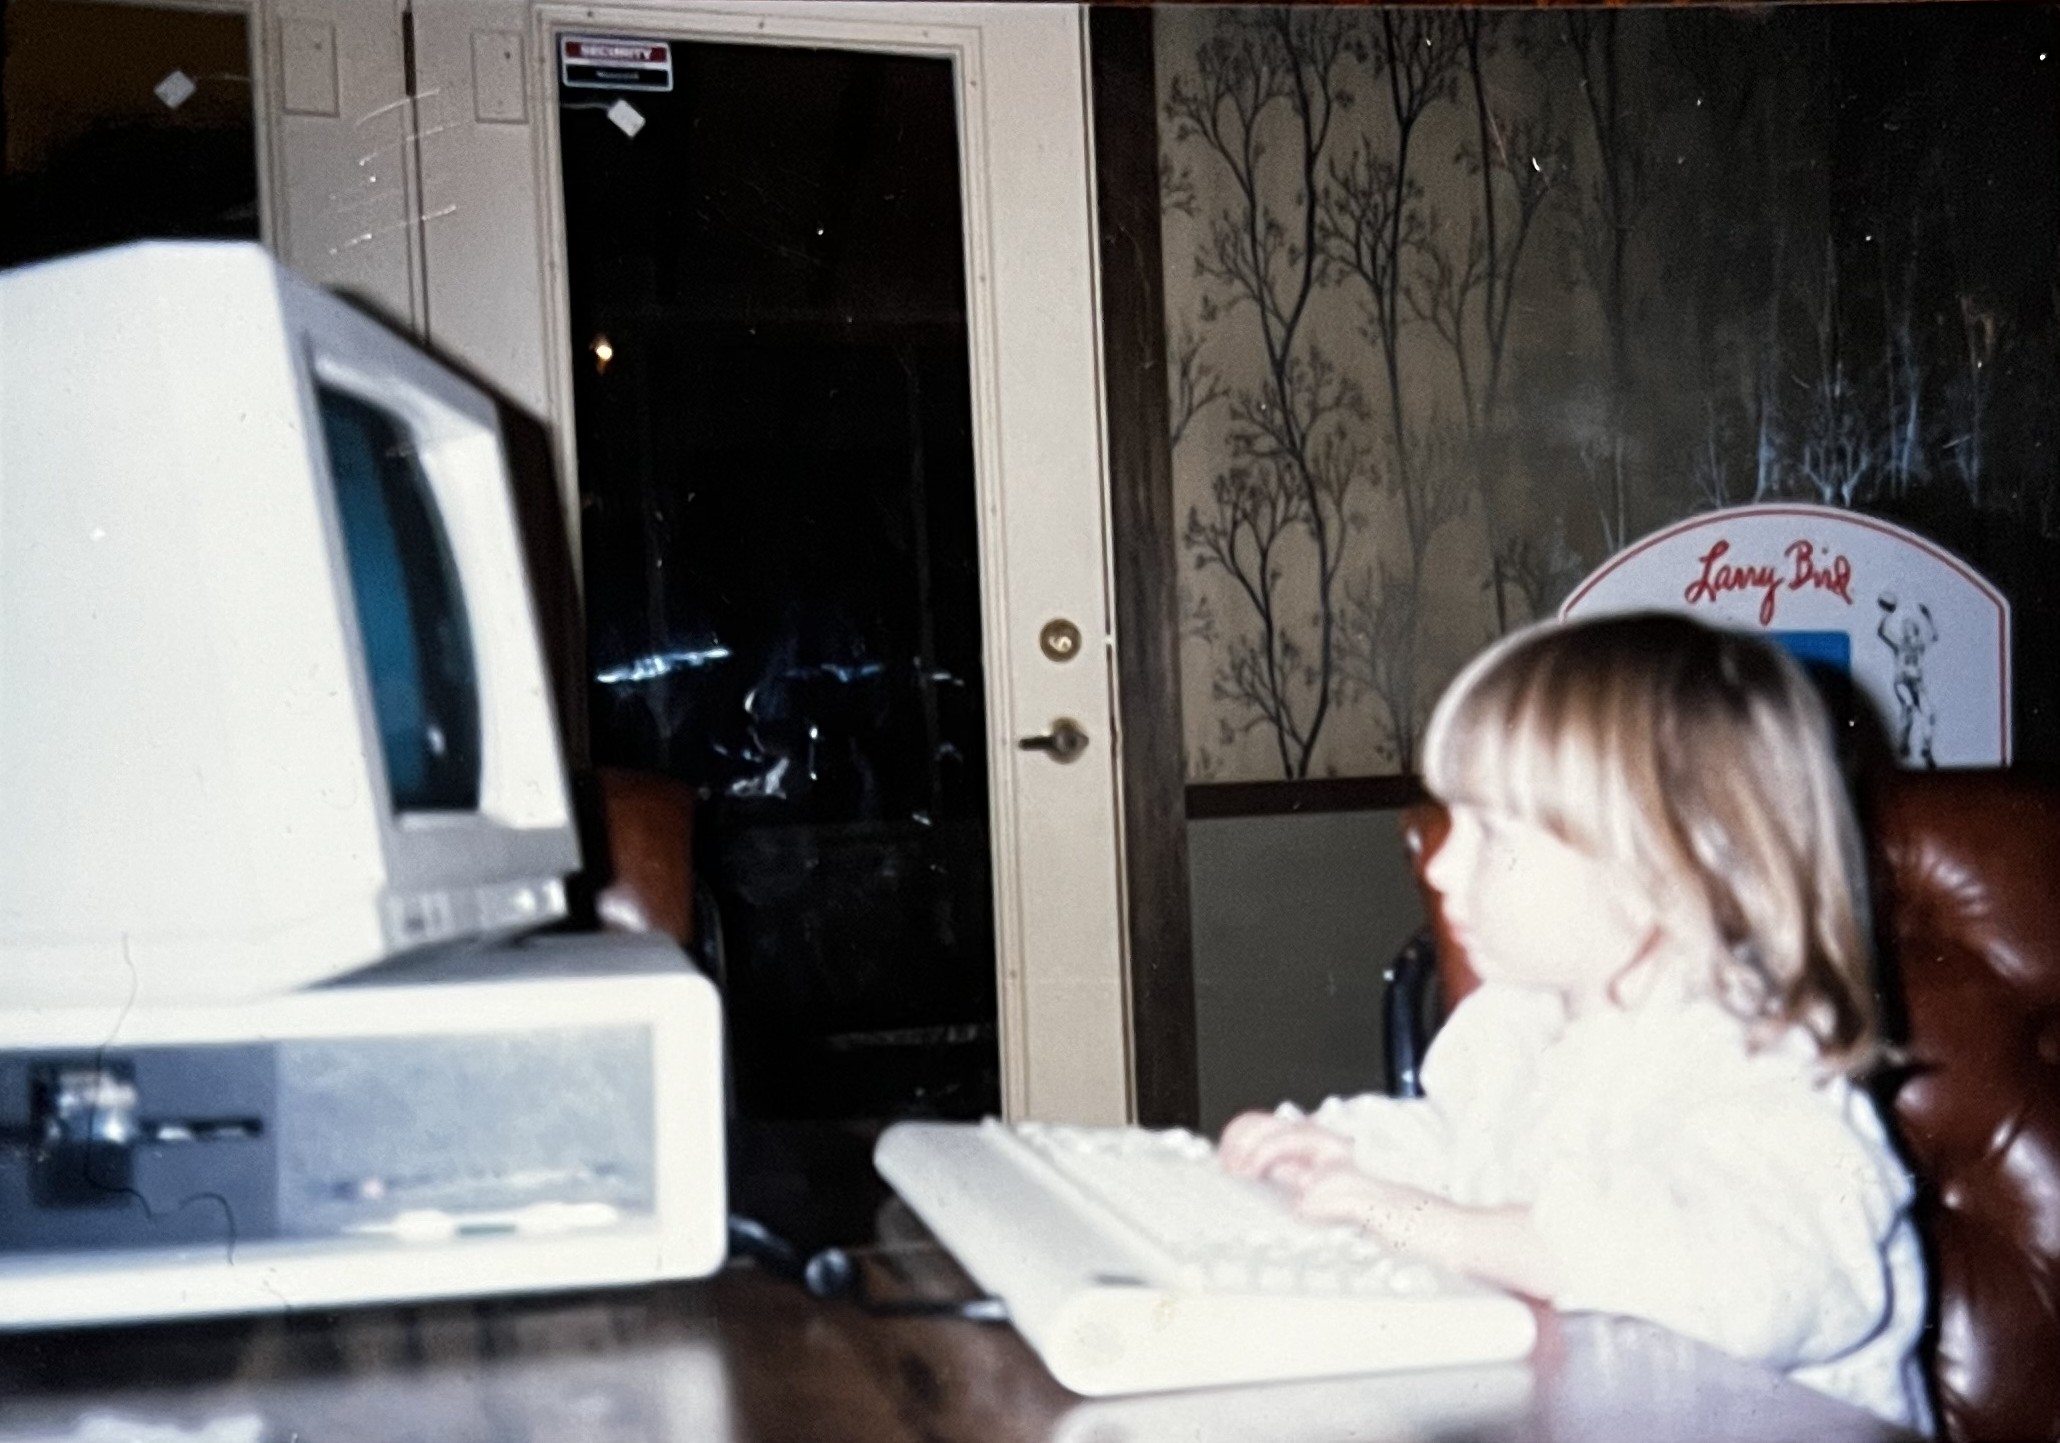
I started learning DOS commands at age 2, before I could read. By 13, I was building custom PCs with my Bat Mitzvah money. In high school, I customized Blogspot sites with hand-coded HTML and CSS. That work eventually became a popular vegan cooking blog and led to a published cookbook. In 2009, I learned mobile device repair during the early days of smartphone retail. I've been troubleshooting and rebuilding systems ever since.
In 2024, I enrolled at the California Institute of Applied Technology. I earned CompTIA A+, Network+, Security+, CIOS, CSIS, and ISC2 CC while maintaining a 4.0 GPA. In July 2026, I completed my A.A.S. in Computer Information Systems, Cybersecurity, Summa Cum Laude, and earned EC-Council's ADG Verified in Defend credential. I am enrolled in CIAT's applied bachelor's program, which begins in September 2026.
I've completed Red Siege's Penetration Testing: Beyond the Basics and Offense for Defense, AWS Academy Cloud Foundations, AI Cyber Defense Ops through Just Hacking Training and WiCyS, and Antisyphon's How to Build Pressure-Proof Pretexts workshop. I'm currently preparing for the PNPT and ACE-T Core while completing Cisco Ethical Hacker, CompTIA CyberDefense Pro, CompTIA AI Prompting Essentials, and Just Hacking's weekly Script-Based Malware Analysis course with John Hammond.
My current work includes penetration testing, vulnerability research, Active Directory, web applications and APIs, AI/ML security, malware analysis, detection engineering, and security tooling.
I conduct independent vulnerability research through authorized disclosure programs.
Recent work includes shipping Hayabusa MCP v0.1.0 and building a Fedora-based agentic security harness around CyberStrike. The harness now uses harness-controls v0.4.1 to keep Harnestia and STRIKER inside restricted case boundaries and out of trouble. That version passed 312 tests. Harnestia then completed an offline memory-forensics case through the CyberStrike TUI and recorded 12 answers from pinned evidence.
I conceived and co-founded CIAT's weekly Beginners CTF, which I co-lead with a CEH instructor. I teach sessions independently when needed, most recently guiding participants through TryHackMe's ContAInment AI-security challenge.
I was selected to speak at BSides Albuquerque 2026.
I co-founded Crumpled Thoughts, a nonprofit providing literacy and technology education to underrepresented communities. I advise on cybersecurity fundamentals, digital safety, and technical problem-solving. My wife teaches literacy and critical thinking. We work with people of color, LGBTQ+ people, immigrants, and low-income communities.
Contact
Email: jennshagrin@proton.me
LinkedIn: linkedin.com/in/jenn-shagrin
Portfolio: jennshaggy.github.io